# Welcome to CtrlOps Documentation (/docs)
**CtrlOps** is a powerful desktop application that makes managing your Linux servers incredibly easy. It gives you the speed and reliability of a desktop app, paired with a clean, modern interface that turns complex server tasks into simple clicks.
* **100% Local**: Your SSH keys, server IPs, and credentials never touch a cloud.
* **Zero Agents**: No need to install any software on your remote servers.
* **Lightning Fast**: Built on a high-performance native engine.
**Current Version**:
## How it Works [#how-it-works]
CtrlOps connects directly to your servers using standard, highly secure connections (like SSH). Everything runs locally on your machine - there is **nothing you need to install** on your servers to get started.
## Everything you need to manage servers [#everything-you-need-to-manage-servers]
One app. All your servers. No context switching.
***
## Need Help? [#need-help]
Can't find your answer in the docs? We're here to help you get unstuck.
* **Email Support**: [support@ctrlops.io](mailto:support@ctrlops.io)
* **Feature Requests**: Reach out if you have an idea that would make CtrlOps better!
* **Need more help?**: Join our [Discord community](https://discord.gg/JhRCp3hsT9)
# Permissions & Access Control (/docs/core/permissions)
Understanding Linux permissions and how to manage access to your servers effectively.
## Linux Permission Basics [#linux-permission-basics]
Every file and directory in Linux has three permission levels:
### Permission Types [#permission-types]
| Permission | Symbol | What It Means |
| ---------- | ------ | ---------------------------------------- |
| Read | `r` | View file contents / List directory |
| Write | `w` | Modify file / Create/delete in directory |
| Execute | `x` | Run file as program / Enter directory |
### Permission Levels [#permission-levels]
Permissions are set for three categories:
* **Owner** - The user who owns the file
* **Group** - Users in the same group
* **Others** - Everyone else
### Reading Permissions [#reading-permissions]
When you see `-rw-r--r--`, it breaks down as:
```
-rw-r--r--
| | |
| | └── Others: r-- (read only)
| └────── Group: r-- (read only)
└────────── Owner: rw- (read + write)
```
### Common Permission Numbers [#common-permission-numbers]
| Number | Permission | Use Case |
| ------ | ---------- | --------------------------------------- |
| 777 | rwxrwxrwx | Everyone can do everything (dangerous!) |
| 755 | rwxr-xr-x | Executable files, directories |
| 644 | rw-r--r-- | Regular files (documents, configs) |
| 600 | rw------- | Private files (SSH keys) |
| 400 | r-------- | Read-only sensitive files |
> **Tip:** Not sure what a mode maps to? The [chmod calculator](/tools/chmod-calculator) converts between octal (`755`) and symbolic (`rwxr-xr-x`) notation and gives you the exact `chmod` command to copy.
## Changing Permissions [#changing-permissions]
### Using `chmod` [#using-chmod]
```bash
# Make file executable
chmod +x script.sh
# Set specific permissions
chmod 755 myfile
# Recursive change
chmod -R 755 mydirectory/
```
### Changing Ownership [#changing-ownership]
```bash
# Change owner
chown username file.txt
# Change group
chown :groupname file.txt
# Change both
chown username:groupname file.txt
# Recursive
chown -R username:groupname directory/
```
## User Management in CtrlOps [#user-management-in-ctrlops]
### Adding Users to Your Server [#adding-users-to-your-server]
### Create the User [#create-the-user]
```bash
# Create user with home directory
sudo adduser john
# Set password
sudo passwd john
```
### Add to Sudo Group (Optional) [#add-to-sudo-group-optional]
```bash
# Grant admin privileges
sudo usermod -aG sudo john
```
### Set Up SSH Key [#set-up-ssh-key]
```bash
# Switch to new user
su - john
# Create SSH directory
mkdir ~/.ssh
chmod 700 ~/.ssh
# Add public key
echo "ssh-ed25519 AAAAC3..." >> ~/.ssh/authorized_keys
chmod 600 ~/.ssh/authorized_keys
```
### Managing Multiple Users [#managing-multiple-users]
Create different permission levels:
#### Admin Group [#admin-group]
```bash
# Create admin group
sudo groupadd admins
# Add users
sudo usermod -aG admins alice
sudo usermod -aG admins bob
```
#### Developer Group [#developer-group]
```bash
# Create developer group
sudo groupadd developers
# Set group ownership
sudo chown -R :developers /var/www/html
# Set permissions
sudo chmod 775 /var/www/html
```
## Directory Permissions [#directory-permissions]
### Web Server Example [#web-server-example]
```bash
# Typical web directory structure
/var/www/
├── html/ # Website files
│ ├── index.html
│ └── assets/
├── logs/ # Log files
└── config/ # Configuration
# Set permissions
sudo chown -R www-data:www-data /var/www/html
sudo chmod -R 755 /var/www/html
sudo chmod -R 750 /var/www/config
sudo chmod -R 755 /var/www/logs
```
### Home Directory Permissions [#home-directory-permissions]
Each user should only access their own home:
```bash
# Set correct home permissions
chmod 700 /home/username
```
## Special Permissions [#special-permissions]
### SUID (Set User ID) [#suid-set-user-id]
Allows executing a file with owner's permissions:
```bash
# Example: passwd command
-rwsr-xr-x 1 root root ... /usr/bin/passwd
```
### SGID (Set Group ID) [#sgid-set-group-id]
New files inherit directory's group:
```bash
# Set SGID on shared directory
chmod g+s /shared-folder
```
### Sticky Bit [#sticky-bit]
Prevents users from deleting others' files:
```bash
# Common on /tmp
chmod +t /shared-directory
```
## CtrlOps Permission Features [#ctrlops-permission-features]
### File Manager Permissions [#file-manager-permissions]
In CtrlOps File Manager, you can:
* **View permissions** at a glance (color-coded)
* **Edit permissions** with visual checkboxes
* **Bulk change** permissions on multiple files
* **See ownership** information
### Permission Warnings [#permission-warnings]
CtrlOps warns you when:
* Making files world-writable
* Changing permissions on sensitive files
* Removing execute permissions from scripts
### Best Practice Recommendations [#best-practice-recommendations]
When you select a file, CtrlOps suggests appropriate permissions:
* **SSH keys**: 600 (owner only)
* **Scripts**: 755 (executable by all)
* **Config files**: 644 (readable by all, writable by owner)
* **Log files**: 644 (readable by all)
## Security Checklist [#security-checklist]
Regularly audit your server permissions to maintain security.
### Monthly Review [#monthly-review]
```bash
# Find world-writable files
find /home -type f -perm -002
# Find files with no owner
find / -nouser -o -nogroup
# Check SSH directory permissions
ls -la ~/.ssh/
# Review sudo access
getent group sudo
```
### Principle of Least Privilege [#principle-of-least-privilege]
* **Give minimum permissions** needed for the job
* **Use groups** to manage permissions efficiently
* **Regular audits** of who has access to what
* **Remove access** when users no longer need it
## Common Issues [#common-issues]
### "Permission Denied" [#permission-denied]
* Check file permissions with `ls -la`
* Verify you're the owner or in the right group
* Check parent directory permissions
### "Operation not permitted" [#operation-not-permitted]
* You need sudo/root access
* File might be immutable (`chattr -i file`)
### Can't Enter Directory [#cant-enter-directory]
* Directory needs execute permission (`chmod +x dir`)
* Parent directories also need execute permission
## Summary [#summary]
* **rwx** = Read, Write, Execute
* **Owner, Group, Others** = Three permission levels
* **chmod** = Change permissions
* **chown** = Change ownership
* **Least privilege** = Give minimum necessary access
# Server Discovery & Setup (/docs/core/server-discovery)
CtrlOps provides several ways to add and manage your servers. This guide explains the actual workflows for setting up your infrastructure in the release.
## The SSH Setup Wizard [#the-ssh-setup-wizard]
If you are new to SSH or need to generate secure keys for your local workstation, CtrlOps provides a built-in **SSH Setup Wizard**.
### How to Access [#how-to-access]
* Open CtrlOps on your workstation.
* In the **left sidebar**, under **TOOLS**, click **SSH Setup**.
### What it Does [#what-it-does]
The wizard performs a three-step verify-and-secure process:
* **Installation Check**: Verifies that an SSH client is installed on your local machine (macOS, Windows, or Linux).
* **Key Detection**: Scans your local `~/.ssh` directory for existing keys and lists each one with a **Copy Key** button.
* **Key Generation**: Generates a modern **Ed25519** key pair for you in one click, or an **RSA** pair if your server only accepts older keys.
## Adding Servers Manually [#adding-servers-manually]
Once your local workstation is ready, you can add servers using the **New Connection** dashboard.
### New Connection Setup [#new-connection-setup]
* Click **"New Connection"** on the home screen.
* Enter your server's **IP Address** and **Username** (usually `root` or `ubuntu`).
* Select your authentication method:
* **SSH Key**: Browse for your private key file.
* **Password**: Enter your server password directly.
### Testing the Connection [#testing-the-connection]
Before saving, click **"Test Connection"**. CtrlOps will attempt a secure handshake and notify you via a toast message if the credentials are valid and the server is reachable.
### Organising by Environment [#organising-by-environment]
Give each server a **Tag** in the connection form - *Production*, *Staging*, or *Development* - and the funnel icon on the home screen narrows the list to just that environment. See [tag servers and filter by environment](/docs/modules/server-management#tag-servers-and-filter-by-environment) for the full walkthrough.
## Importing Infrastructure [#importing-infrastructure]
If you are migrating from another CtrlOps installation or have a pre-configured server list, use the **Import** feature:
* Click **"Import"** on the home screen.
* Select a valid **JSON configuration file**.
* CtrlOps will validate the structure and add the new servers to your dashboard instantly.
***
## Need Help? [#need-help]
Can't find your answer in the docs? We're here to help you get unstuck.
* **Email Support**: [support@ctrlops.io](mailto:support@ctrlops.io)
* **Feature Requests**: Reach out if you have an idea that would make CtrlOps better!
* **Need more help?**: Join our [Discord community](https://discord.gg/JhRCp3hsT9)
**Security Note**: CtrlOps version does not currently support automated network scanning. All servers must be added manually or via JSON import to ensure maximum security and privacy.
# SSH & Security (/docs/core/ssh-security)
This guide explains SSH (Secure Shell) in plain English - what it is, how it keeps you safe, and best practices for securing your servers.
## What is SSH? [#what-is-ssh]
SSH is like a secure phone call between your computer and your server. It:
* **Encrypts** all communication (nobody can listen in)
* **Authenticates** you (proves you are who you say you are)
* **Protects** your data from hackers and eavesdroppers
Think of it like this:
* Without SSH: Shouting your password across a crowded room
* With SSH: Whispering through a sealed, soundproof tube
## SSH Keys Explained [#ssh-keys-explained]
### The Two-Key System [#the-two-key-system]
SSH uses two keys that work together:
🔓 Public Key
• Goes on the server
• Can be shared freely
• Like a padlock that anyone can see
• File usually named:
id_rsa.pub
🔐 Private Key
• Stays on your computer
•
NEVER share this
• Like the key that opens the padlock
• File usually named:
id_rsa
or
.pem
**Critical**: Never share your private key. If someone gets it, they can access your server. It's like giving someone your house key.
Need a key pair to start with? Our [SSH key generator](/tools/ssh-key-generator) creates an Ed25519 or RSA pair right in your browser - nothing is uploaded - so you can drop the public half onto your server and keep the private key local.
## Where Does CtrlOps Store Keys? [#where-does-ctrlops-store-keys]
CtrlOps stores your SSH keys **securely on your local machine**:
* **Mac**: `~/Library/Application Support/CtrlOps/keys/`
* **Windows**: `%APPDATA%\CtrlOps\keys\`
* **Linux**: `~/.config/CtrlOps/keys/`
Keys are encrypted at rest and never leave your computer.
## Root vs Non-Root Access [#root-vs-non-root-access]
### What is Root? [#what-is-root]
`root` is the superuser account on Linux - it has unlimited power:
* Can delete any file
* Can install any software
* Can change any setting
* Can break the entire system
**Analogy**: Root is like having the master key to an entire building. Regular users only have keys to their own offices.
### When to Use Root [#when-to-use-root]
**Use root when you need to:**
* Install system-wide software
* Modify system configuration
* Manage other user accounts
* Access protected system files
**Don't use root when:**
* Running regular applications
* Editing your own project files
* Doing routine maintenance
### Best Practice: Create a Non-Root User [#best-practice-create-a-non-root-user]
For daily operations, create a regular user account:
```bash
# As root, create a new user
sudo adduser myusername
# Add user to sudo group for admin privileges
sudo usermod -aG sudo myusername
```
This way, you:
* Have daily access without risking accidental damage
* Can escalate to root when needed with `sudo`
* Limit the blast radius if credentials are compromised
## Security Best Practices [#security-best-practices]
The essentials are below; for the full fleet-level checklist (key rotation, per-user keys, audit trails, revocation), see our [14 SSH key management best practices](/blog/ssh-key-management-best-practices) guide.
To check a server against these practices instead of reading its config by hand, run the **SSH & Access** and **Firewall & Network** audits from the [Security Audit](/docs/modules/security-audit) tab. They report on root login, password authentication, the SSH port, idle timeout, `authorized_keys` permissions, firewall state, and open ports, then score the result.
### Disable Password Authentication [#disable-password-authentication]
Passwords can be guessed. Use SSH keys exclusively:
```bash
# Edit SSH config
sudo nano /etc/ssh/sshd_config
# Change these lines:
PasswordAuthentication no
PubkeyAuthentication yes
# Restart SSH
sudo systemctl restart sshd
```
### Use a Firewall [#use-a-firewall]
Only allow SSH from trusted IPs:
```bash
# Allow SSH only from your office IP
sudo ufw allow from 203.0.113.0/24 to any port 22
# Or block all incoming except SSH
sudo ufw default deny incoming
sudo ufw allow 22/tcp
sudo ufw enable
```
### Keep Software Updated [#keep-software-updated]
Security patches fix vulnerabilities:
```bash
# Ubuntu/Debian
sudo apt update && sudo apt upgrade
# CentOS/RHEL
sudo yum update
```
### Monitor Login Attempts [#monitor-login-attempts]
Check who's trying to access your server:
```bash
# See failed login attempts
sudo grep "Failed password" /var/log/auth.log
# See successful logins
sudo grep "Accepted" /var/log/auth.log
```
### Use Fail2Ban [#use-fail2ban]
Automatically block IPs with too many failed attempts:
```bash
# Install
sudo apt install fail2ban
# Enable
sudo systemctl enable fail2ban
sudo systemctl start fail2ban
```
## CtrlOps Security Features [#ctrlops-security-features]
CtrlOps adds additional security layers:
### Encrypted Storage [#encrypted-storage]
* All credentials encrypted with AES-256
* Keys stored in OS-level secure enclaves
* Automatic key rotation reminders
### Session Management [#session-management]
* Connections timeout after inactivity
* Automatic reconnection with fresh authentication
* Session logging for audit trails
### Approval-Based Execution [#approval-based-execution]
* High-risk commands require confirmation
* Dry-run mode for dangerous operations
* Rollback capabilities for mistakes
## What If My Key is Compromised? [#what-if-my-key-is-compromised]
If you think someone has your private key:
### Revoke the Key Immediately [#revoke-the-key-immediately]
Remove the public key from your server:
```bash
# On the server, edit authorized keys
nano ~/.ssh/authorized_keys
# Delete the line corresponding to the compromised key
```
### Generate a New Key Pair [#generate-a-new-key-pair]
```bash
# Generate new key
ssh-keygen -t ed25519 -C "your_email@yourdomain.com"
# Add new public key to server
ssh-copy-id -i ~/.ssh/id_ed25519.pub user@server
```
### Update CtrlOps [#update-ctrlops]
* Delete the old key in CtrlOps
* Upload the new private key
* Test the connection
### Review Server Logs [#review-server-logs]
Check for unauthorized access:
```bash
# See recent logins
last
# See failed attempts
sudo grep "Failed password" /var/log/auth.log
```
## Summary [#summary]
* **SSH** encrypts your connection to the server
* **Private keys** must be kept secret - never share them
* **Public keys** can be safely shared and go on the server
* **Root access** is powerful - use it sparingly
* **Regular updates** and **firewalls** keep you secure
## Related tools [#related-tools]
Free, browser-based tools for the tasks on this page. Nothing you paste into them is uploaded.
Questions about security? Contact our security team at [security@ctrlops.io](mailto:security@ctrlops.io)
# Download & Install (/docs/getting-started/download)
## System Requirements [#system-requirements]
Choose your platform below to get started:
### The macOS Flow [#the-macos-flow]
* **Execute Download**:
*
*
* Open the image and drag CtrlOps to your **Applications** folder.
* Launch **CtrlOps** to begin the License Activation.
**Security Note**: If macOS flags the developer as unidentified, navigate to **System Settings > Privacy & Security** and select **"Open Anyway"** to trust the local hub.
### The Windows Flow [#the-windows-flow]
* **Execute Download**:
*
* Follow the activation wizard to establish the local vault.
* Launch CtrlOps from your **Start Menu**.
### The Linux Flow [#the-linux-flow]
Paste this into your terminal (Ubuntu 22.04+ / Debian 12+, x86\_64):
```bash
curl -fsSL https://ctrlops.io/install.sh | sudo bash
```
It downloads the official CtrlOps package and installs it with its dependencies. Launch CtrlOps from your app menu, or run `ctrlops`.
**Prefer not to pipe a script?** Download the package and install it from the terminal — installing via `apt` (not by double-clicking the file) avoids the App Center warning and resolves dependencies automatically:
*
```bash
sudo apt install ./CtrlOps_1.1.0_linux_amd64.deb
```
You can verify the install script before running it against its [SHA-256 checksum](https://ctrlops.io/install.sh.sha256).
## The "After-Launch" Blueprint [#the-after-launch-blueprint]
Once installed, CtrlOps initializes its local data structure in your system's application support directory (`com.devopsflow`).
* **No Global Account**: You aren't signing into a cloud service.
* **License Activation**: You are activating your local instance to enable Agentic capabilities.
* **Data Sovereignty**: Your connection list and SSH keys stay in your vault.
* **Pricing**: $7/user/month or $70/user/year for unlimited servers, after a [1 month free trial](https://ctrlops.io/pricing) - no credit card required.
***
## Need Help? [#need-help]
Can't find your answer in the docs? We're here to help you get unstuck.
* **Email Support**: [support@ctrlops.io](mailto:support@ctrlops.io)
* **Feature Requests**: Reach out if you have an idea that would make CtrlOps better!
* **Need more help?**: Join our [Discord community](https://discord.gg/JhRCp3hsT9)
# Your First Connection (/docs/getting-started/first-connection)
Welcome to CtrlOps! Adding your first server connection is the gateway to streamlining your DevOps workflow. This guide walks you through the exact steps to securely connect your machine to your server.
## Prerequisites: SSH Setup Wizard [#prerequisites-ssh-setup-wizard]
Before adding a connection, your local machine needs to be properly configured for SSH. If you haven't done this before, CtrlOps includes a built-in **SSH Setup Wizard** to make the process effortless.
To access the wizard, look in the **left sidebar**, under **TOOLS**, and click **SSH Setup**. It opens in its own tab with a progress bar across the top.
The wizard will guide you through three critical steps:
* **SSH Installation:** Verifies that the OpenSSH client is installed on your OS.
* **SSH Keys:** Lists the keys already in `~/.ssh` and can generate a secure new one (Ed25519 recommended).
* **Server Setup:** Provides exact commands (like `ssh-copy-id`) to securely copy your public key to your target server.
For a screen-by-screen walkthrough of all three steps, see [Generate an SSH Key (GUI Wizard)](/docs/modules/ssh-management#generate-an-ssh-key-gui-wizard).
**Already have SSH keys set up?** You can skip the wizard and proceed directly to adding your connection! And if you also keep a hand-written `~/.ssh/config` for terminal use, our free [SSH config generator](/tools/ssh-config-generator) writes clean host blocks you can paste straight in.
## What You Need [#what-you-need]
Before proceeding, ensure you have the following details from your hosting provider (AWS, DigitalOcean, Hetzner, etc.):
* **IP Address** - Your server's public IP (e.g., `203.0.113.0`).
* **Port** - The SSH port. It defaults to `22`; you only need this if your server listens on a non-standard port.
* **Username** - Usually `root`, `ubuntu`, `ec2-user`, or your custom admin account.
* **Authentication** - Either your configured SSH key, a `.pem` file, or a password.
Already have a working SSH command? You don't have to fill anything in by hand. Paste your full connection string into **Quick Connect** at the top of the form and CtrlOps fills the details for you, see the next section.
## Connecting Step-by-Step [#connecting-step-by-step]
### Start a New Connection [#start-a-new-connection]
From the CtrlOps dashboard, click the green **New Connection** button at the top left, in the sidebar above the workspace list (or **Add First Connection** if your dashboard is empty).
### Quick Connect with a connection string (fastest) [#quick-connect-with-a-connection-string-fastest]
At the top of the form is the **Quick Connect via SSH String (Optional)** field. If you already have a working SSH command, paste it here and CtrlOps parses it to auto-fill the **IP Address**, **Username**, **Port**, and key path for you. It works on both authentication tabs.
Both common formats are recognized:
```bash
# Full ssh command with a key file and custom port
ssh -i ~/.ssh/mykey.pem user@192.168.1.1 -p 2222
# Simple user@host (great for AWS EC2 endpoints)
ubuntu@ec2-65-0-241-41.ap-south-1.compute.amazonaws.com
```
Once the fields populate, you can connect straight away or adjust anything before saving. Prefer to enter details by hand? Skip this field and use the next step instead.
### Fill in Server Details [#fill-in-server-details]
* **Server Name (optional)**: Give your connection a friendly, recognizable name (e.g., "Production Database").
* **IP Address**: Paste your server's public IP address or hostname.
* **Port**: The SSH port, pre-filled with `22`. Change it only if your server listens on a non-standard port.
* **Username**: Enter the exact SSH username.
### Choose Authentication Method [#choose-authentication-method]
Select the tab that matches your security setup:
By default, CtrlOps uses your system's standard SSH keys (like `~/.ssh/id_ed25519`).
**Using a password instead?**
Toggle the **Use password authentication** switch, enter your password, and optionally check **Remember password** for automatic future connections.
Passwords are convenient but less secure than SSH keys. We highly recommend using the SSH Setup Wizard to transition to key-based authentication.
Perfect for AWS EC2 or other cloud providers that give you a downloaded key file.
Click **Select .pem Key File** to browse your computer, or manually paste the absolute path to your `.pem` or `.key` file.
### Connect through a proxy or bastion (optional) [#connect-through-a-proxy-or-bastion-optional]
If your server isn't reachable directly and you have to hop through a jump host, expand **Advanced Settings** and fill in the **Proxy Command (Optional)** field. CtrlOps routes the connection through the host you specify.
```bash
ssh -W %h:%p user@bastion
```
Leave this empty for servers you can reach directly.
### Connect and Automate [#connect-and-automate]
Click **Connect SSH** (or **Connect with .pem**).
CtrlOps will automatically perform a pre-flight test to verify your credentials. Once successful, the connection is saved, and you will be immediately routed to your new instance dashboard!
## Connection Troubleshooting [#connection-troubleshooting]
If the connection fails, CtrlOps will display a specific error. Here is how to resolve the most common issues:
### "Authentication failed" / "Permission Denied" [#authentication-failed--permission-denied]
* Double-check your username (it is case-sensitive).
* If using a password, ensure it is typed correctly.
* If using a `.pem` file, ensure it has the correct permissions (`chmod 400 key.pem`).
* If using standard SSH keys, ensure your *public* key was properly added to the server's `~/.ssh/authorized_keys` file.
### "Cannot reach server" / "Connection Timed Out" [#cannot-reach-server--connection-timed-out]
* Verify the IP address is correct.
* Check that the server is currently powered on in your cloud provider's dashboard.
* Ensure port `22` (SSH) is open in your server's firewall/security groups.
### "Connection Refused" [#connection-refused]
* The server is online, but the SSH service is not running or is configured to use a non-standard port. If it uses a different port, set the **Port** field to match.
* If the server is only reachable through a jump host, add the bastion to the **Proxy Command** field under **Advanced Settings**.
### Windows: SSH Agent Not Running [#windows-ssh-agent-not-running]
If you are using standard SSH keys on Windows and connections fail, your Windows SSH Agent service might be stopped.
Run these commands in **PowerShell (as Administrator)**:
* **Set the service to start automatically**:
```powershell
Set-Service -Name ssh-agent -StartupType Automatic
```
* **Start the service now**:
```powershell
Start-Service ssh-agent
```
* **Add your private key** (replace `id_ed25519` with your filename if different):
```powershell
ssh-add $env:USERPROFILE\.ssh\id_ed25519
```
Restart CtrlOps and try connecting again.
## Next Steps [#next-steps]
Now that you're connected to your server, explore what CtrlOps can do:
* [Learn about the AI Terminal](/docs/modules/ai-terminal)
* [Explore the File Manager](/docs/modules/file-manager)
* [Set up automated backups](/docs/modules/backup)
## Need Help? [#need-help]
Can't find your answer in the docs? We're here to help you get unstuck.
* **Email Support**: [support@ctrlops.io](mailto:support@ctrlops.io)
* **Feature Requests**: Reach out if you have an idea that would make CtrlOps better!
* **Need more help?**: Join our [Discord community](https://discord.gg/JhRCp3hsT9)
# Migrate from Termius to CtrlOps (/docs/getting-started/migrate-from-termius)
Already using Termius? Moving your servers into CtrlOps takes about thirty seconds, and you will not have to re-enter a thing. CtrlOps has a built-in importer that reads your saved Termius hosts directly, so there is no export file to generate and no IPs or keys to copy across by hand.
## What comes over [#what-comes-over]
| From Termius | Into CtrlOps |
| :------------------------------ | :-------------------------------------------------- |
| Host name or label | The server name on your dashboard |
| Address or hostname | The server IP address |
| Port | The SSH port |
| Username | The SSH username |
| SSH key or agent authentication | The saved authentication method for that connection |
What does not come across: Termius snippets, port-forwarding rules, sync groups, and your Termius subscription. Those are Termius-specific features with no direct equivalent in the CtrlOps server list. Your connections are what move.
Everything is read locally on your machine. CtrlOps opens the Termius data already stored on this computer and writes it into your local CtrlOps server list. Nothing is uploaded.
## Before you start [#before-you-start]
* **CtrlOps installed and signed in.** If you have not installed it yet, start with the [Quick Start](/docs/getting-started/quick-start).
* **Termius installed on the same computer**, with your hosts visible in it. The importer reads local Termius data, so hosts that exist only in Termius cloud sync need to be synced down to this machine first.
* **Your computer login password.** Your operating system will ask for it once, to grant CtrlOps permission to read the credentials Termius has saved.
## Import your Termius servers [#import-your-termius-servers]
### Open the Termius importer [#open-the-termius-importer]
Open CtrlOps and go to **All Servers**. In the top right, click the **three-dot menu** next to the view switcher.
The menu has two groups. Under **SERVER LIST** you get **Import servers** and **Export servers**, which work with the standard CtrlOps JSON format. The one you want is under **MIGRATE**: click **Import from Termius**.
### Review what comes over [#review-what-comes-over]
A confirmation screen appears showing exactly what CtrlOps is about to read: your servers, ports, usernames, and SSH keys.
Read it, then click **Import Servers**.
### Unlock your saved Termius credentials [#unlock-your-saved-termius-credentials]
Termius stores its credentials in your operating system's secure credential store, so your OS asks you to approve access before CtrlOps can read them. This is your system granting permission, not CtrlOps asking you for a password it keeps.
macOS shows a dialog reading **"CtrlOps wants to use your confidential information stored in 'Termius' in your keychain."**
Enter your **login keychain password** - the same password you use to log into your Mac - and click **Allow**.
Click **Always Allow** instead if you would rather macOS stopped asking on future imports.
Windows may prompt you to confirm that CtrlOps can read the credentials Termius has saved on this machine. Approve the prompt to continue.
Depending on your desktop environment, your keyring (GNOME Keyring, KWallet, or similar) may ask you to unlock it before CtrlOps can read the saved Termius credentials. Enter your keyring password and allow access to continue.
CtrlOps then shows **"Reading your Termius servers..."** while it works through your saved hosts.
If you click **Deny**, the import stops and nothing is added. Open the three-dot menu and run **Import from Termius** again when you are ready.
### Pick the servers you want [#pick-the-servers-you-want]
CtrlOps lists everything it found, for example **"Found 4 servers"**, with a short summary above the list telling you how many are new and how many are already in your list.
Each row shows the server name, its `user@address`, and the authentication type it uses - **Key** for a saved SSH key, **Agent** for an SSH agent connection. Servers that are not already in CtrlOps carry a green **NEW** badge.
Everything is selected by default. Uncheck any server you do not want, or use **Deselect all** and pick just the ones you need. The running count on the right tells you how many are selected.
When the selection looks right, click **Import**.
### Connect to an imported server [#connect-to-an-imported-server]
A confirmation appears and your servers land on the **All Servers** dashboard, each showing its address and the authentication method it will use.
Click the **play button** on any server card to open a connection. No manual setup, no copying IPs and keys across one at a time.
## After the import [#after-the-import]
Your servers are in CtrlOps and ready to use. A few things worth doing next:
* **Connect to one server to confirm the credentials work.** If a connection fails, the [first connection troubleshooting guide](/docs/getting-started/first-connection#connection-troubleshooting) covers the common causes.
* **Run the SSH Setup Wizard** if you want to generate a fresh key or push a key to a server. See [SSH Management](/docs/modules/ssh-management).
* **Export a backup of your new server list.** Three-dot menu → **Export servers** writes a JSON file you can restore on another machine. See [Server Management](/docs/modules/server-management#backup-your-saved-servers).
* **Go beyond SSH.** Once connected you get the [AI Terminal](/docs/modules/ai-terminal), live [CPU, RAM, and disk monitoring](/docs/modules/infra-details), [log search](/docs/modules/log-management), and [one-click deployments](/docs/modules/deployment) from the same app.
## Troubleshooting [#troubleshooting]
The importer reads Termius data stored on the computer you are running CtrlOps on. If Termius is not installed on this machine, or your hosts live only in Termius cloud sync and have never been synced down locally, there is nothing for CtrlOps to read. Open Termius on this computer, confirm your hosts are visible there, then run the import again.
Nothing is imported if you deny the prompt. Open the three-dot menu again, choose **Import from Termius**, and approve the prompt this time. There is no limit on how often you can run the importer.
On macOS, click **Always Allow** instead of **Allow** on the keychain prompt. macOS then remembers the decision for CtrlOps and stops asking on future imports.
The import brings across the address, port, username, and key reference exactly as Termius had them, so a failure here is usually the same as any other SSH connection problem. Work through [Connection Troubleshooting](/docs/getting-started/first-connection#connection-troubleshooting) - it covers authentication failures, timeouts, refused connections, and the Windows SSH agent service.
No. CtrlOps reads the Termius data stored locally on your machine and writes it into your local CtrlOps server list. Nothing is uploaded, and your keys and credentials stay on the same computer they were already on. See [SSH Security](/docs/core/ssh-security) for how CtrlOps stores connection data.
Yes. The same three-dot menu has **Import servers** and **Export servers** under the **SERVER LIST** heading, which work with the standard CtrlOps JSON format. **Import from Termius** is a separate entry under **MIGRATE** that reads Termius data directly, with no export step in between. The [server discovery guide](/docs/core/server-discovery#importing-infrastructure) covers the JSON route.
## Next Steps [#next-steps]
* [Your First Connection](/docs/getting-started/first-connection) - the full connection form, authentication options, and proxy setup
* [Server Management](/docs/modules/server-management) - organise, back up, and manage your whole server list
* [AI Terminal](/docs/modules/ai-terminal) - describe what you need in plain English and get the command
* [CtrlOps vs Termius](/compare/ctrlops-vs-termius) - a feature-by-feature comparison if you are still deciding
* [Ughareja Infotech case study](/case-studies/ughareja-infotech) - how one team moved 6 servers off Termius in under 2 minutes
## Need Help? [#need-help]
Can't find your answer in the docs? We're here to help you get unstuck.
* **Email Support**: [support@ctrlops.io](mailto:support@ctrlops.io)
* **Feature Requests**: Reach out if you have an idea that would make CtrlOps better!
* **Need more help?**: Join our [Discord community](https://discord.gg/JhRCp3hsT9)
# Quick Start (/docs/getting-started/quick-start)
Welcome! This guide will get you from zero to managing your first server in under 5 minutes.
## Prerequisites [#prerequisites]
Before you begin, you'll need:
* A **Linux server** (Ubuntu 22.04+, CentOS Stream 9+, Debian 11+, or Fedora 38+)
* Your server's **IP address**
* **SSH access** to your server (username + password or SSH key)
* A **CtrlOps account** - every new account includes a [1 month free trial](https://ctrlops.io/pricing) with no credit card required, then $7/user/month for unlimited servers
Don't have a server yet? You can use:
* AWS EC2 (Amazon Linux 2023, Ubuntu 22.04/24.04)
* DigitalOcean Droplet (Ubuntu 22.04/24.04 LTS)
* Google Compute Engine (Debian 12, Ubuntu 22.04/24.04)
* Azure VMs (Ubuntu 22.04/24.04 LTS, CentOS Stream 9)
* Any cloud provider with Linux VMs
* A local VM (UTM for Mac, VirtualBox, VMware)
* Raspberry Pi 4/5 with Raspberry Pi OS or Ubuntu
## Guided Setup [#guided-setup]
### Download CtrlOps [#download-ctrlops]
Download the latest version for your platform:
[Download for Mac M1/M2/M3/M4](https://ctrlops.io)
[Download for Mac Intel](https://ctrlops.io)
[Download for Windows](https://ctrlops.io)
[Download for Linux](https://ctrlops.io)
### Install the Application [#install-the-application]
* **Mac**: Open the `.dmg` file and drag CtrlOps to Applications
* **Windows**: Run the installer and follow the prompts
* **Linux**: Extract the archive and run `./ctrlops`
### Launch and Connect [#launch-and-connect]
* Open CtrlOps
* Click **"Add Server"** in the top right
* Enter your server details:
* **Name**: My Server (any name you want)
* **IP Address**: Your server's IP
* **Username**: Usually `root` or your username
* Upload your SSH key or enter password
* Click **"Connect"**
### Start Managing! [#start-managing]
Once connected, you'll see:
* **Terminal**: Execute commands with AI assistance
* **File Manager**: Browse, upload, download, rename, and delete files visually
* **Monitoring**: Real-time CPU, RAM, and disk usage
* **Deployments**: Set up automated deployments
## What's Next? [#whats-next]
* [Learn about SSH and security](/docs/core/ssh-security)
* [Explore the AI Terminal](/docs/modules/ai-terminal)
* [Set up automated backups](/docs/modules/backup)
**The Human Element**: Once connected, you’ll see the **Agentic Persona** selector. This isn't just a chatbot; it's a senior engineer tuned to your specific task - be it a midnight outage or a security audit.
## Need Help? [#need-help]
Can't find your answer in the docs? We're here to help you get unstuck.
* **Email Support**: [support@ctrlops.io](mailto:support@ctrlops.io)
* **Feature Requests**: Reach out if you have an idea that would make CtrlOps better!
* **Need more help?**: Join our [Discord community](https://discord.gg/JhRCp3hsT9)
## Next Steps [#next-steps]
Now that you've established your first bridge, explore the **AI Terminal** to see how the system translates complex kernel states into plain, actionable engineering prose.
# Access Management (/docs/modules/access-management)
Managing who can log in to a single server is easy from the [SSH Management](/docs/modules/ssh-management) tab. But once you have 20 or 50 servers, it stops scaling: offboarding one teammate means opening every server, checking `authorized_keys`, and revoking their key one by one. Miss a single server and that person still has a way in. **Access** fixes this by scanning your whole fleet and showing you, in one screen, exactly who can reach which servers and what they can do once they're in. For an overview of how [server access control](/features/access-management) works across a fleet, see the feature page.
The access map is built and stored **locally** on your computer. CtrlOps reads the authorized users on each server during a scan and keeps the results on your machine. None of it is sent to CtrlOps or any third party.
## What Access does [#what-access-does]
* **Scan every server at once** and read who is authorized on each one.
* **See every person** across your fleet, with how many servers they can reach and how many give them sudo.
* **Remove a person from one server** without touching their access elsewhere.
* **Offboard a person from all servers** in a single action, with a type-to-confirm guard.
* **Onboard a new person to many servers** at once: paste their public key, pick the servers, and set a role per server.
* **Re-scan on demand** to refresh the picture after you change keys directly on a server.
* **Export an audit** snapshot of who can access what.
## Scan your servers for the first time [#scan-your-servers-for-the-first-time]
The first time you open Access, it's empty until you run a scan.
### Open Access [#open-access]
**Open app → Click Access (left sidebar, marked NEW)**
You'll see the empty state, *"Manage server access in one place"*, with a short summary of what a scan will do.
### Start the scan [#start-the-scan]
**Click Scan access**
CtrlOps connects to each saved server and reads its authorized users. A progress panel shows each server as it's checked, the running count of *"authorized users found"*, and which server is being read right now. Servers that aren't reachable are skipped.
### Review the results [#review-the-results]
When the scan finishes, you land on the **People** list, everyone who can log in to one or more of your servers, with stats across the top.
Scanning is read-only. It looks at your servers but changes nothing until you explicitly remove or add access. The empty state says it plainly: *"Read-only - nothing changes until you act."*
## Read the access list [#read-the-access-list]
The top of the screen has three stat cards, and below them is the searchable People list.
| Stat card | What it counts |
| :---------------- | :-------------------------------------------------------------------------------- |
| **People** | Unique users found across all scanned servers |
| **Servers** | Servers included in the scan |
| **Access grants** | Total authorized key-to-server grants (one person on five servers is five grants) |
Each row in the People list shows:
| Row element | What it shows |
| :-------------- | :--------------------------------------------------------------- |
| Avatar and name | The person's name or username |
| Key type badge | `SSH-ED25519` (secure) or `SSH-RSA` (standard) |
| Email / host | The key comment, e.g. `hiren@macmini` or an email address |
| Server chips | The first few servers this person can reach |
| Server count | Total servers, with a green shield count for how many grant sudo |
Use the **Search people** box to filter by name, and **Re-scan** (top right) to refresh the whole list.
## See one person's access [#see-one-persons-access]
**Click any person in the list**
A detail panel opens on the right. At the top it summarizes their reach, for example *"19 servers · 19 with sudo"*. Below that, **Active access** lists every server they can log in to, each showing:
* The server name and a **sudo** badge when that grant has elevated rights.
* The exact login target, e.g. `root@35.157.41.17` or `ubuntu@43.204.17.201`.
* A **Remove** button for that single grant.
At the bottom of the panel you can **Grant access to more servers**, **Rotate SSH key**, or **Remove from all servers**.
## Remove a person from one server [#remove-a-person-from-one-server]
When someone should keep most of their access but lose one server, you don't need to offboard them.
**Open the person's detail panel → Find the server → Click Remove**
CtrlOps revokes that person's authorized key for that one server. Their access to every other server is untouched.
## Offboard a person from all servers [#offboard-a-person-from-all-servers]
When a teammate leaves, remove them from everything in one step.
### Open the person and start the removal [#open-the-person-and-start-the-removal]
**Open the person's detail panel → Click Remove from all servers**
A confirmation dialog lists every server they'll lose access to.
### Confirm by typing their name [#confirm-by-typing-their-name]
The dialog asks you to **type the person's name to confirm**. This guard makes sure you're offboarding the right person and not removing access by accident.
**Type the name → Click Remove from all servers**
### Done [#done]
CtrlOps revokes every authorized key and account for that person across all servers. You don't have to open a single server by hand.
Removing from all servers is a fleet-wide revoke and takes effect right away. Double-check you have the right person, and that you aren't removing the key you're currently using to connect, before you confirm.
If you only want to invalidate a person's existing key without removing their access, use **Rotate SSH key** in the detail panel instead. This is handy when a key may have been exposed.
## Onboard a new user [#onboard-a-new-user]
When someone joins, give them access to many servers at once instead of editing each server's `authorized_keys` by hand.
### Open the Add user form [#open-the-add-user-form]
**Click Add user (top right)**
A modal opens titled *Add user*, *"Grant one person access to multiple servers at once."*
### Enter the name and public key [#enter-the-name-and-public-key]
| Field | What to enter |
| :----------------- | :-------------------------------------------------------------------- |
| **Name** | A friendly name, e.g. `Jane Doe` |
| **SSH public key** | Paste the user's public key, e.g. `ssh-ed25519 AAAAC3... jane@laptop` |
### Select servers [#select-servers]
Under **Select servers**, tick each server this person should reach. Use **Select all** to grab the whole fleet, and the counter (*"3 selected"*) tracks your choices.
### Set a role per server [#set-a-role-per-server]
For each selected server, set the **TARGET** login and role from the dropdown. You can mix roles across servers, root on one, a standard user on another.
| Role | Login | Rights |
| :----------- | :--------- | :---------------- |
| **root** | `root` | sudo (full admin) |
| **ubuntu** | `ubuntu` | standard user |
| **readonly** | `readonly` | read only |
### Grant access [#grant-access]
**Click Grant access to servers**
CtrlOps adds the public key to each selected server with the role you chose. The new person now appears in the People list.
Only paste the **public** half of a key pair (the part starting `ssh-ed25519` or `ssh-rsa`). Never paste a private key.
## Re-scan and export an audit [#re-scan-and-export-an-audit]
Access takes a snapshot when you scan; it doesn't watch your servers continuously.
* **Re-scan** (top right) rebuilds the People and server lists. Run it after you change keys directly on a server, add a new connection, or just want to confirm the current picture. The header shows when you *Last scanned*.
* **Export Audit** (top right) saves a snapshot of who can access what, useful for security reviews and compliance records.
Re-scan results and exported audits stay on your machine. CtrlOps never collects or transmits your access map.
This export answers *who can log in*. For *how the box itself is configured* - SSH hardening, firewall state, exposed ports, TLS, database and Docker settings - run a [Security Audit](/docs/modules/security-audit), which produces a hardening score and a PDF report per server.
## Tips [#tips]
Re-scan after anyone changes keys directly on a server (outside CtrlOps). Because Access stores a local snapshot, a manual change on the server won't show up until you scan again.
Offboard people from the Access screen rather than server by server. One confirmed *Remove from all servers* is faster and far less likely to leave a forgotten grant behind.
Use the **readonly** role when onboarding auditors or short-term contractors. They get in to look, without sudo.
Access is the fleet-wide view; the per-server [SSH Management](/docs/modules/ssh-management) tab is still the place for one-off key work on a single server. Use them together.
## Troubleshooting [#troubleshooting]
CtrlOps couldn't read that server's `authorized_keys`. This is the same cause as *"Access Denied"* on the SSH Management tab: the user it logged in as can't read the file. Reconnect as root, or as a user with passwordless sudo, then re-scan.
The server was unreachable when the scan ran, often a firewall blocking port 22, the machine being down, or a bad credential. Confirm you can connect to it from the Home page, then re-scan. Windows servers aren't supported and won't appear.
Removals you make inside CtrlOps update the list automatically, so the person should disappear right away. If they're still showing in the rare case it didn't refresh, click **Re-scan** to rebuild the list from the servers' current state.
Two common reasons: they had a separate key you didn't see (re-scan to confirm none remain), or they were already connected when you removed access, an existing SSH session stays open until it ends. New logins will be blocked.
Adds and removals you make inside CtrlOps update the counts automatically. Counts only fall behind when keys are changed directly on a server outside CtrlOps, click **Re-scan** to refresh every count.
That server likely rejected the write to `authorized_keys`, usually a permission issue (the login user lacks sudo) or the server was briefly unreachable. Fix access on that server, then add the user to just that one again.
# Backups (/docs/modules/backup)
Backups give you peace of mind. Set them up once, and CtrlOps will quietly copy your files to S3 on the schedule you pick. If something ever goes wrong on the server, you'll have a recent copy ready to go. For an overview of how [automated server backups](/features/backup) work, see the feature page.
## Create, schedule, and monitor backup jobs [#create-schedule-and-monitor-backup-jobs]
* Create backup jobs that copy a folder from your server to S3.
* Run a backup right now, or schedule it (daily, weekly, monthly, yearly, or a custom cron).
* Watch progress live, with speed, files transferred, and time remaining.
* Open the full log of any run to see exactly what happened.
* Edit, delete, or stop a backup that's already running.
Today CtrlOps backs up from your server to S3 (AWS, Cloudflare R2, Backblaze B2, Wasabi, MinIO, DigitalOcean Spaces). More destinations are on the way.
## Before you start [#before-you-start]
You'll need a few things in place. Don't worry, CtrlOps shows you a banner whenever something is missing and gives you a one-click install.
| Requirement | Why you need it | What to do if it's missing |
| :----------------------------- | :-------------------------------------------- | :------------------------------------------------------------------ |
| Active server connection | Backups run on the server you're connected to | Open the server from the Home page first |
| Rclone (on the server) | The tool that moves your files to S3 | Click **Install Rclone** in the yellow banner |
| Cron (only for scheduled jobs) | Triggers backups on a schedule | Click **Install Cron**, then **Start Cron Service** if it's stopped |
| S3 bucket and access keys | The destination for your files | Create them in your cloud provider's console |
If you only ever back up "right now" with one click, you can skip cron entirely. Cron is only required when you want backups to run on a schedule.
{/* screenshot: Rclone install banner and Cron status banner */}
## Set up your first backup job [#set-up-your-first-backup-job]
### Open the Backup tab [#open-the-backup-tab]
**Open app → Click your server → Click the Backup tab**
### Open the create form [#open-the-create-form]
**Click Create Job (top right of the Backup Configuration row)**
### Fill in the basics [#fill-in-the-basics]
In the *Basic Information* card, fill in these fields:
| Field | What to enter |
| :------------------- | :--------------------------------------------------------------------------------------------------------------------------------------- |
| **Job Name** | A name you'll recognise later, like `daily-website` or `mysql-monthly`. Letters, numbers, and underscores only. |
| **Source Path** | The folder on the server you want to back up, for example `/var/www/html` or `/home/user/documents`. |
| **Destination Type** | Select **S3-Compatible Storage**. |
| **Transfer Type** | **Sync** mirrors the source exactly (deletes anything at the destination that no longer exists at the source). **Copy** only adds files. |
{/* screenshot: New Backup Job form, Basic Information card */}
### Add your S3 details [#add-your-s3-details]
In the *Destination Configuration* card, fill in your S3 settings:
| Field | What to enter |
| :------------------ | :--------------------------------------------------------------------------------------------------- |
| **Provider** | The service you use: AWS S3, MinIO, Wasabi, DigitalOcean Spaces, Backblaze B2, or Cloudflare R2. |
| **Region** | Required for AWS (e.g. `us-east-1`). Optional for most other providers. |
| **Access Key** | Your S3 access key. Stored encrypted. |
| **Secret Key** | Your S3 secret key. Stored encrypted. |
| **Bucket Name** | The bucket your files will go into. |
| **Remote Path** | Optional. A folder inside the bucket, like `/server1/backups`. |
| **Custom Endpoint** | Only for providers that need it (MinIO, R2, etc.). Leave empty for AWS. |
| **Storage Class** | Optional. Use *Standard* for fast access, or *Glacier* / *Deep Archive* for cheap long-term storage. |
| **Use IAM Role** | Toggle on if your server already has IAM permissions, so you can skip Access Key and Secret Key. |
### Choose when it should run [#choose-when-it-should-run]
In the *Schedule Configuration* card, pick one option:
| Option | When to pick it |
| :----------- | :---------------------------------------------------------------------------------------------------------------------------- |
| **Manual** | Backups only run when you click *Run Backup*. No cron needed. |
| **Interval** | Recurring schedule. Pick how often (Daily, Weekly, Monthly, Yearly), the time of day, and the day if it applies. |
| **Custom** | Write your own cron expression (Minute, Hour, Day, Month, Weekday). Each field accepts a number, a range, or `*` for "every". |
Times use the **server's** timezone, not yours. Double-check the server time if a 2:00 AM backup needs to run at *your* 2 AM.
### (Optional) Tune the advanced options [#optional-tune-the-advanced-options]
You can skip this. The defaults work for most setups.
| Field | What it does | Default |
| :------------------ | :---------------------------------------------------------------------- | :------ |
| **Transfers** | How many files upload in parallel. Range 1 to 32. | 4 |
| **Checkers** | Threads used to verify files. Range 1 to 32. | 8 |
| **Bandwidth Limit** | Cap upload speed, e.g. `10M`, `100M`, `1G`. Leave empty for full speed. | (none) |
### Test the connection [#test-the-connection]
**Click Test Connection (bottom of the form)**
CtrlOps tries to reach your bucket with the keys you entered. If something is wrong, you'll see the error right away. Fix it before saving.
### Save the job [#save-the-job]
**Click Create**
Your new job appears in the table. It won't run yet unless you scheduled it or trigger it manually.
## Run a backup right now [#run-a-backup-right-now]
### Find your job [#find-your-job]
**Open the Backup tab → Locate the job in the table**
Each job has three round buttons on the right: **Run Backup** (play icon), **Edit** (pencil icon), **Delete** (trash icon).
### Trigger the run [#trigger-the-run]
**Click Run Backup (play icon)**
The status flips to **RUNNING** and a small progress bar appears. The job is now copying files in the background. You can switch tabs and come back.
### (Optional) Watch progress [#optional-watch-progress]
**Click the row to expand it**
A live panel slides open showing how much has been transferred, file count, current speed, and rough time remaining.
{/* screenshot: Expanded job row showing live progress panel */}
## Watch a backup in progress [#watch-a-backup-in-progress]
When you expand a running job, the *Backup Progress* panel updates in real time:
| Stat | What it shows |
| :-------------------- | :---------------------------------- |
| **Size Transferred** | How many MB or GB have moved so far |
| **Files Transferred** | Files done out of the total |
| **Transfer Speed** | Current rate, like `5.2 MB/s` |
| **ETA** | Rough time until finish |
| **Elapsed Time** | How long the run has been going |
If anything goes wrong mid-run, like a permission error on a single file, you'll see a red alert with the list of errors. No need to dig through logs to spot them.
To abort a running backup: **Expand the row → Click Kill This Process → Confirm**. The current run stops, the job stays in the list, and you can re-run it later.
## Open the log of a run [#open-the-log-of-a-run]
**Expand the job row → Click View Log**
A modal opens with the raw, terminal-style output from the backup engine. This is where to look when:
* A backup says it failed and you want to know why.
* You want to confirm a specific file was included.
* Something looks slow and you want to find the bottleneck.
The log is read-only. Scroll through it, and copy any text you need to share.
## Manage existing jobs [#manage-existing-jobs]
| Action | How |
| :---------- | :-------------------------------------------------------------------------------------------------------------- |
| **Edit** | Click the pencil icon on the job row. Useful for rotating credentials or moving the destination. |
| **Delete** | Click the trash icon and confirm. The job is removed. Existing backup files at the destination are not touched. |
| **Refresh** | Click *Refresh* at the top right of the table to re-pull the latest job statuses. |
You can't edit or delete a job while it's running. Stop it first with **Kill This Process**.
## Tips [#tips]
Name jobs by what they back up, not by the date. `daily-mysql-prod` ages well, `backup-april-2026` does not.
Test the connection before you save. A two-second test now beats discovering at 3 AM that a typo in your bucket name broke a week of backups.
Store backups somewhere far from your server. A local folder on the same disk as your data won't help if the disk dies. Pick a different cloud region, or a different provider entirely.
## Troubleshooting [#troubleshooting]
Click **Install Rclone** and wait. Installation can take a minute on slow servers. If it still fails, open the AI Terminal tab and check that the user has permission to install packages.
Cron isn't installed or isn't running. Look for the alert at the top of the Backup tab and click **Install Cron** or **Start Cron Service**.
Most often it's one of three things: wrong region, a typo in the bucket name, or the access key doesn't have permission to write to that bucket. Double-check those first.
Check the source path. A typo means rclone has nothing to copy, and that counts as a "successful" run of zero files. Open the log: if it says `Transferred: 0`, the source path is the culprit.
The cron service may have stopped. Open the Backup tab and look for a *"Cron service is not running"* alert at the top, then click **Start Cron Service**.
First, check the **Bandwidth Limit** field. If it's set, raise or remove it. Next, increase **Transfers** in Advanced Options to upload more files in parallel.
The user CtrlOps logs in as doesn't have read access to the source path, or write access to the destination. From the AI Terminal, run `ls -la ` to confirm permissions, and adjust with `chmod` or `chown` as needed.
# Application Deployment (/docs/modules/deployment)
CtrlOps takes a GitHub repository and turns it into a running app on your server. Connect your GitHub account once, pick a repo and branch from the list, choose a Node version, set your env variables, optionally add a domain with HTTPS, and click **Create**. CtrlOps clones the repo, installs dependencies, builds, starts the app under PM2, configures Nginx, and issues an SSL certificate. You watch the whole thing happen in a live progress modal. Once it is running, the [PM2 Process Manager](/docs/modules/pm2-process-manager) tab is where you restart, reload, or scale it. For a full hands-on walkthrough - the manual 13-step process versus one-click deployment - see [How to Deploy a Node.js App on a Linux VPS in 5 Minutes](/blog/deploy-nodejs-app-linux-vps), or the [one-click deployment](/features/deployment) feature page for the shorter overview.
## Deploy apps from GitHub, end to end [#deploy-apps-from-github-end-to-end]
* Connect your GitHub account once, then pick the repo and branch from a dropdown. Private repos included, no key setup.
* Deploy a Node.js, React, Next.js, or static "build folder" app from a GitHub repo.
* Pick the Node.js version (and install it on the fly if it's missing).
* Set environment variables one by one, or paste a whole `.env` block at once.
* Add one or more domains, with optional automatic SSL via certbot.
* Watch deployment progress live with command output and step status.
* Edit the app's `.env` later from the Folder Details page.
## Before you start [#before-you-start]
| Requirement | Why |
| :--------------------------------------------------------------------- | :--------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| **An active connection** to a Linux server | The deploy runs on whichever server you opened |
| **A GitHub repository** for the app | Connect your GitHub account and pick it from the list - this covers private repos with no extra setup. A public repo URL also works without connecting. |
| **Domain DNS already pointing at the server** (only if you'll use SSL) | Required so certbot can issue the certificate - a quick [DNS record lookup](/tools/dns-record-lookup) confirms the A record before you deploy. Once it is issued, the [SSL certificate decoder](/tools/ssl-certificate-decoder) shows the expiry and chain order |
| **PM2, Node, and Nginx** | CtrlOps installs whatever's missing as part of the deploy |
## Open the Add Application form [#open-the-add-application-form]
You can launch the form from a few places.
### From the Deployments tab [#from-the-deployments-tab]
**Open app → Click your server → Deployments tab → Click Add Application**
The Deployments tab is the dedicated home for your apps. This is the most common path.
### From the File Manager toolbar [#from-the-file-manager-toolbar]
**Open app → Click your server → File Manager tab → Click Add Application (top toolbar)**
The same form, reached from wherever you happen to be.
### From an existing app folder [#from-an-existing-app-folder]
**File Manager → Click into an app folder → The Folder Details page opens**
If the folder has a `package.json`, you'll see the technology badge (Next.js, React, Node.js) at the top, plus the *Files* and *Environment Variables* tabs. To add a new app, use the toolbar button above.
{/* screenshot: Add Application form, Basic Information card, showing the Connect GitHub button with the repo and branch dropdowns */}
## Set up your first deployment [#set-up-your-first-deployment]
The form is split into five cards. Fill them in top to bottom.
### Basic Information [#basic-information]
| Field | What to enter |
| :------------------- | :-------------------------------------------------------------------------------------- |
| **Application Name** | A friendly name like `My Node.js App`. The folder name preview appears below the field. |
| **Environment** | *Development*, *Staging*, or *Production*. Pick whichever fits. |
**GitHub Repository**
Two ways to point CtrlOps at your code.
**Connect your GitHub account (recommended)**
Click **Connect GitHub** and authorize CtrlOps in the browser that opens. Your repositories load into a dropdown - pick the one you want, then pick the branch from a second dropdown.
Private repos are included automatically. There's no key or token to set up.
Connecting is a one-time step. Every deploy after this one reuses the connection, so you go straight to picking a repo.
**Paste a repository URL**
Still supported if you'd rather not connect. Toggle between **HTTPS** and **SSH**, then paste the repo URL.
Two things to know about this path:
* **There's no branch picker.** CtrlOps deploys the repo's default branch.
* **Private repos over SSH still need a deploy key.** Add the server's public key to the repo on GitHub first, which you can grab from the [SSH Management](/docs/modules/ssh-management) tab. Over HTTPS, only public repos will clone.
Connecting your GitHub account removes the deploy-key step entirely and is the only way to choose a branch. The deploy-key requirement applies only to the paste-a-URL path with an SSH URL.
### Node.js Version [#nodejs-version]
Pick the Node version from the dropdown. Versions already installed on the server show a green checkmark. Versions not yet installed show a download icon, CtrlOps will install them as part of the deploy.
### Build Configuration [#build-configuration]
| Field | What to enter |
| :---------------------------- | :------------------------------------------------------------------------------------ |
| **Application Type** | *Node.js*, *React*, *Next.js*, or *Build Folder* |
| **Install Command** | Defaults to `npm install`. Change to `yarn install` or `pnpm install` if needed. |
| **Build Command** | Auto-fills with `npm run build` for React and Next.js. Leave empty for plain Node.js. |
| **Start Command** | Defaults to `npm start`. For static React, use `serve -s build -l `. |
| **Local Redis Server Needed** | Toggle on for Node.js apps that need Redis on the same machine |
### Environment Variables [#environment-variables]
Two ways to add them.
**One at a time**
Click **Add Environment Variable**. A new row appears with two inputs: *Key* and *Value*. Repeat for each variable.
**Paste a whole `.env` block**
Click **Bulk Paste Environment Variables**. A modal opens titled *Paste Environment Variables*. Paste the contents of your local `.env` file:
```
DATABASE_URL=postgres://user:pass@host:5432/db
API_KEY=sk_live_abc123
# Comments are fine, lines starting with # are ignored
```
Confirm. All variables are added to the list at once.
Quotes (`"` and `'`) and special characters in values are fully supported.
### Domains (optional) [#domains-optional]
Skip this card entirely if you don't need a domain yet, you can deploy and add one later.
| Field | What to enter |
| :----------------------------------------------------- | :-------------------------------------------------------------------------------------- |
| **Setup SSL certificates for domains (using Certbot)** | Toggle on to enable HTTPS automatically |
| **Port** | The port your app listens on, e.g. `3000`. Required when SSL is enabled. |
| **Add Domain** | Click to add a domain row. Enter a domain like `yoursite.com`. Click again to add more. |
When SSL is on, adding `yoursite.com` automatically also covers `www.yoursite.com`. You don't need to add both.
For SSL to succeed, your domain's DNS A record must already point to this server's public IP. If DNS isn't ready yet, deploy without SSL first, then add it once DNS resolves.
### Click Create [#click-create]
CtrlOps closes the form and opens the *Deployment Progress* modal. You'll see each step in a checklist (clone, install, build, start, configure Nginx, issue SSL) along with live terminal output.
### Watch the deployment [#watch-the-deployment]
Each step turns green when it succeeds, red if it fails. The terminal area shows exactly what the server is doing. When the last step finishes, you have a running app.
{/* screenshot: Deployment Progress modal with step checklist and live terminal */}
## Edit environment variables later [#edit-environment-variables-later]
Once the app is deployed, you can update its `.env` from the Folder Details page.
### Open the app folder [#open-the-app-folder]
**File Manager → Click into your app folder**
The Folder Details page opens, showing a technology badge (Next.js, React, Node.js) and version, plus two tabs.
### Switch to the Environment Variables tab [#switch-to-the-environment-variables-tab]
Existing variables are listed with key on the left and value on the right. If there are none yet, you'll see *"No environment variables found"*.
### Add a new variable [#add-a-new-variable]
Scroll past the list to the form at the bottom. Two inputs side by side:
| Field | What to enter |
| :---------------- | :------------------------------- |
| **Variable Name** | The key, e.g. `API_KEY` |
| **Value** | The value, e.g. `sk_live_abc123` |
**Click Add → The variable appears in the list above**
### Remove a variable [#remove-a-variable]
Click the red trash icon at the right of the row. The variable is removed from the `.env` file immediately.
Changing env variables doesn't restart the app automatically. After your edits, open the [PM2 Process Manager](/docs/modules/pm2-process-manager) tab and click restart on that process to pick up the new values.
## Re-deploy or pull the latest code [#re-deploy-or-pull-the-latest-code]
There's no built-in re-deploy button right now. To pull new commits and restart:
```bash
cd /home//
git pull
npm install
npm run build # only if you have a build step
pm2 restart
```
You can also wrap this in a [Script](/docs/modules/ai-terminal/scripts) so it's one click next time.
## Common PM2 commands [#common-pm2-commands]
PM2 is the process manager that keeps your app running.
You do not need any of these commands. The [PM2 Process Manager](/docs/modules/pm2-process-manager) tab lists every process with live CPU and memory, and restart, reload, stop, and delete are one click each. The commands below are here for when you would rather stay in a shell.
If you do want to run them by hand, use the AI Terminal.
You don't need `pm2 logs` to read your app's output. Every PM2 process's out and error logs are already listed in the [Logs](/docs/modules/log-management) tab, where you can search them, tail them live, or download them.
| Command | What it does |
| :----------------------- | :---------------------------------------------- |
| `pm2 list` | See all your running apps and their status |
| `pm2 logs ` | Tail the live logs for an app |
| `pm2 restart ` | Restart the app, picks up new env vars and code |
| `pm2 stop ` | Stop the app without removing it |
| `pm2 start ` | Start a stopped app |
| `pm2 delete ` | Remove the app from PM2 entirely |
## Tips [#tips]
Use **Bulk Paste Environment Variables** to copy from your local `.env` in one go. It saves a lot of clicking on a real-world app.
Deploy without SSL first if you're not sure DNS is ready. You can run certbot afterwards from the AI Terminal.
Watch the deployment progress modal end to end the first time. If something goes wrong, the failing step's terminal output usually points straight to the cause.
## Troubleshooting [#troubleshooting]
This only happens on the paste-a-URL path with an SSH URL. The simplest fix is to connect your GitHub account instead - click **Connect GitHub** in the form, authorize CtrlOps, and pick the repo from the list. Private repos then clone with no key setup at all.
If you'd rather stay on the SSH URL, add the server's public key as a deploy key on the GitHub repo. You can grab the server's key from the [SSH Management](/docs/modules/ssh-management) tab.
If the repo belongs to an organization, an org owner may need to approve CtrlOps' access before it shows up. If you created the repo after connecting, reconnect your GitHub account to refresh the list.
The user CtrlOps deploys as doesn't own the target folder. Pick a folder under `/home//`, where the user has write access, instead of `/var/www` or `/opt`.
The build is hitting the default Node memory limit. Add this env variable in Card 4 of the form: `NODE_OPTIONS=--max-old-space-size=4096` (adjust the number to fit your server's RAM).
Your app may be listening on `localhost` instead of `0.0.0.0`. Check your code's `app.listen()` call. Or, the firewall may be blocking the port, see the AI Terminal: `sudo ufw status`.
DNS isn't pointing to this server, or ports 80/443 are blocked.
Open the [PM2 Process Manager](/docs/modules/pm2-process-manager) tab, click the app, and switch to its **Logs** tab to watch its output live. The crash reason is almost always in the last few lines. Common causes: missing env variable, port already in use, database not reachable.
CtrlOps detects the tech from `package.json` dependencies (`next` for Next.js, `react` for React, `express` for Node.js). If your stack uses something else, the badge will be *"Unknown"*. The Folder Details page still works the same way.
# File Manager (/docs/modules/file-manager)
The File Manager turns your server's filesystem into something you can click through, just like Finder or Explorer. Upload a file with a click, double-click a folder to enter, edit a config file in place, and unzip an archive without typing a single command. If you would rather move files from a terminal, our [scp and rsync command builder](/tools/scp-rsync-command-builder) writes the exact command for you. For an overview of the [visual file manager](/features/file-manager) before you start, see the feature page.
## Browse, upload, edit, and manage server files [#browse-upload-edit-and-manage-server-files]
* Browse any folder on your server, all the way down to single files.
* Upload single files, multiple files, or whole folders.
* Download any file to your computer.
* Create new folders.
* Rename, delete, and copy the path of any item.
* Edit text files (configs, scripts, env files) right inside the app.
* Unzip `.zip` archives in place with one click.
* Search and filter the current folder.
## Open the File Manager [#open-the-file-manager]
**Open app → Click your server → File Manager tab (default tab when you connect)**
You land in the user's home directory. From there, navigate by clicking folders, using the breadcrumb at the top, or typing a path.
{/* screenshot: File Manager landing view with breadcrumb and file grid */}
## Tour the toolbar [#tour-the-toolbar]
The top of the File Manager has two rows of controls.
### Top row (display options) [#top-row-display-options]
| Control | What it does |
| :--------------------------------- | :--------------------------------------------------------------------------------------------------------------- |
| **Hidden Items** (eye icon toggle) | Show or hide dotfiles like `.env` or `.bashrc` |
| **Show Files** (file icon toggle) | Show files (on) or only show folders (off) |
| **Add Application** | Open the deploy form to create a new app folder. See the [Application Deployment](/docs/modules/deployment) page |
| **Refresh** | Reload the current folder |
### Second row (navigation) [#second-row-navigation]
| Control | What it does |
| :-------------- | :---------------------------------------------------------------------------- |
| **Go to Root** | Jump straight to `/` |
| Breadcrumb path | Click any segment to jump there. The current folder is highlighted in green |
| **Up arrow** | Go to the parent folder. Disabled when you're already at root |
| **Search** | Filter the current folder by filename. *"Items: N"* shows the live count |
| **Folder** | Create a new folder in the current path |
| **Upload** | Pick files from your computer to upload here |
| **Upload Dir** | Pick a folder from your computer to upload here, including its contents |
## Move around the filesystem [#move-around-the-filesystem]
A few ways to get where you need to go:
* **Click a folder** to open it.
* **Click a breadcrumb segment** at the top to jump back several levels in one click.
* **Click the up arrow** to step up one folder.
* **Click Go to Root** to jump to `/`.
## Upload files [#upload-files]
Use the **Upload** buttons in the toolbar to get files onto the server.
### Open the destination folder [#open-the-destination-folder]
Browse to the folder where you want the files to land.
### Click Upload (for files) or Upload Dir (for a whole folder) [#click-upload-for-files-or-upload-dir-for-a-whole-folder]
A native file picker opens.
### Pick what to upload [#pick-what-to-upload]
Select one or more files (or a folder) and confirm.
### Wait for the progress message [#wait-for-the-progress-message]
You'll see *"Uploading (1/3): filename.txt"* as each file moves across. When done, a toast shows *"Upload initiated for N item(s)"* and the file list refreshes automatically.
## Download a file [#download-a-file]
You can download from either the card view or the list view.
| View | How |
| :--------------- | :----------------------------------------------------------------------- |
| **Grid (cards)** | Hover over the file card, then click the **Download** icon in the footer |
| **List (table)** | Click the three-dot menu in the file's row, then choose **Download** |
| **Right-click** | Right-click the file, then choose **Download** from the context menu |
You'll be prompted by your browser or OS to choose where to save it.
## Create a folder [#create-a-folder]
### Open the parent folder [#open-the-parent-folder]
Browse to where you want the new folder to live.
### Click Folder [#click-folder]
A small modal opens with a single field labelled **Folder Name**.
### Name it and confirm [#name-it-and-confirm]
Type a name (no spaces or special characters in most server filesystems) and click the confirm button. The new folder appears immediately.
## Rename or delete [#rename-or-delete]
Each file or folder offers the same set of actions in the grid card footer, the list row, and the right-click menu.
| Action | What it does |
| :-------------------------- | :------------------------------------------------------------------------------------------ |
| **Rename** (pencil icon) | Opens a small modal with the current name pre-filled. Edit and confirm. |
| **Delete** (red trash icon) | Asks *"Delete ``? This action cannot be undone."* Click **OK** to remove it. |
| **Copy Path** | Copies the full server path to your clipboard. Useful for pasting into the AI Terminal. |
Delete is permanent. Files removed here are not sent to a trash folder, they are gone for good. If the file is important, download a copy first.
## Edit a text file [#edit-a-text-file]
Use this for config files, env files, scripts, or anything else you want to tweak without leaving the app.
### Open the file's menu [#open-the-files-menu]
In list view, click the three-dot menu in the file's row. In grid view, the same option is available via right-click.
### Click Edit Content [#click-edit-content]
A modal opens titled *Editing: filename*. The full file contents load in a dark, monospaced text area.
### Make your changes [#make-your-changes]
Edit the text directly. The footer has three buttons:
| Button | What it does |
| :--------- | :--------------------------------------------------------- |
| **Reload** | Discard your changes and re-fetch the file from the server |
| **Cancel** | Close the modal without saving |
| **Save** | Save your changes and close the modal |
### Click Save [#click-save]
A toast confirms *"File saved successfully"*. If something goes wrong, you'll see *"Failed to save file: ..."* with the error.
For a syntax-highlighted experience on big files, you may prefer to download, edit locally, and re-upload. The built-in editor is meant for quick tweaks.
## Unzip a `.zip` archive [#unzip-a-zip-archive]
### Find the archive [#find-the-archive]
Browse to the folder containing the `.zip` file. The blue *Expand ZIP* icon appears in the card footer for any `.zip` file.
### Click Expand ZIP [#click-expand-zip]
The icon spins while the archive is being extracted. The contents land in a new folder named after the zip (without the `.zip` extension).
### Wait for the toast [#wait-for-the-toast]
A success toast confirms *"Expanded filename.zip"*. The file list refreshes to show the new folder.
## Search and sort [#search-and-sort]
* **Search**: type any part of a filename in the search box. Matches update live, and *"Items: N"* shows the count of visible files.
* **Sort**: folders always appear first, followed by files in alphabetical order. There is no manual sort selector.
## Tips [#tips]
Toggle **Hidden Items** on when you need to edit `.env` files or `.bashrc`. Off by default to keep the view clean.
**Copy Path** is your shortcut to the AI Terminal. Copy a file's path here, then paste it after `cat`, `tail -f`, or `vi` in the terminal.
Big folder uploads can take a while. Keep the tab open until the success toast appears, otherwise the upload may be cut short.
## Troubleshooting [#troubleshooting]
The **Hidden Items** toggle in the top toolbar is off. Click the eye icon to turn it on.
The user you're connected as doesn't own that file. You can either reconnect as a user with the right permissions, or use the AI Terminal with `sudo` to remove it.
Network blips and very large files are the usual causes. Click **Refresh** to see what made it across, then re-upload only the missing items. If it keeps failing, the destination folder may be out of space, check the [Infrastructure Details](/docs/modules/infra-details) tab.
The user doesn't have write permission on that file, or the disk is full. Use the AI Terminal to run `ls -la ` and confirm permissions, or check the disk in the Infrastructure Details tab.
The unzip command needs the `unzip` package on the server. If it's missing, open the AI Terminal and run `sudo apt install unzip` (or `sudo yum install unzip`), then try again.
The user CtrlOps is logged in as may not have read permission for some files. Folders and files you can't read are simply hidden from the list, no error is shown.
# Monitor Linux Server: Real-Time Infrastructure Dashboard (/docs/modules/infra-details)
Open the tab on any connected server to see whether it is busy, running low on memory, or close to filling up the disk. Metrics auto-refresh every 2 seconds, so the numbers are always current. Color-coded gauges turn from green to red as usage climbs, making it easy to spot bottlenecks before they cause downtime.
For deeper diagnostics, use the [AI Terminal](/docs/modules/ai-terminal) to ask questions like 'Why is my server slow?' and get AI-generated commands with human approval. Once a gauge tells you *something* is wrong, the [Logs](/docs/modules/log-management) tab is usually where you find out *what*. For an overview of [real-time server monitoring](/features/infra-monitoring) across your fleet, see the feature page.
## What You Can Monitor on a Linux Server with CtrlOps [#what-you-can-monitor-on-a-linux-server-with-ctrlops]
* See live CPU, memory, and disk usage at a glance - the same data you would get from running `top`, `free -h`, and `df -h`, presented visually
* Spot the top 10 processes consuming the most CPU or memory
* End a runaway process from its row in the table, without typing a `kill` command
* Free up cached memory in one click
* Clean out old logs and temp files to reclaim disk space (replaces manual `find` and `rm` commands)
* Refresh all metrics manually or let auto-refresh update every 2 seconds
## How to Monitor a Linux Server in CtrlOps [#how-to-monitor-a-linux-server-in-ctrlops]
**Open app → Click your server → Click the Infrastructure Details tab**
You will see three circular gauges at the top - one each for CPU, memory, and disk - followed by a process table below. Metrics auto-refresh every 2 seconds while the tab is open, so you are always looking at live server health data.
## Understanding CPU, Memory, and Disk Usage Gauges [#understanding-cpu-memory-and-disk-usage-gauges]
Each gauge uses a color-coded threshold system to help you monitor server health at a glance: green (0-60%), yellow (60-80%), orange (80-90%), and red (90%+). When a gauge turns red, it indicates a resource bottleneck that needs immediate attention.
| Card | What it shows | Extra info below the gauge |
| :------------ | :----------------------------- | :------------------------------------------------- |
| **Processor** | CPU load as a percentage | System uptime and number of CPU cores |
| **Memory** | RAM in use as a percentage | Used GB out of total, available memory, swap usage |
| **Storage** | Root disk used as a percentage | Used out of total size, available space |
## Monitor Top Processes by CPU and Memory Usage [#monitor-top-processes-by-cpu-and-memory-usage]
Below the gauges, the *Top Processes* table lists the 10 heaviest processes running right now.
| Column | What it shows |
| :----------- | :---------------------------------------------------------------------------------------------------------------------- |
| **PID** | The process ID number |
| **Process** | The command or program name |
| **CPU %** | CPU usage. On multi-core servers this can go above 100% (100% means one full core) |
| **Memory %** | RAM usage as a percentage of total |
| **Actions** | A red trash icon that ends the process. See [Kill a Runaway Process](#kill-a-runaway-process-from-the-dashboard) below. |
Click any column header to sort by that field. The table holds the top 10 only, so very small background tasks don't appear.
## Refresh the numbers [#refresh-the-numbers]
Numbers refresh on their own every 2 seconds. If you want to force an immediate update:
**Click Refresh Metrics (top right of the tab)**
You'll see a brief spinner on the button, then the gauges and process list update.
## Clear Linux Buffer/Cache Memory in One Click [#clear-linux-buffercache-memory-in-one-click]
When the Memory card is high but you suspect a lot of it is just cached data Linux is hanging on to, you can release it.
### Find the Clear Buffer/Cache icon [#find-the-clear-buffercache-icon]
**Memory card → Top right corner → Trash icon (purple)**
Hover over it to see the tooltip *"Clear Buffer/Cache"*.
### Click the icon [#click-the-icon]
A toast pops up at the bottom saying *"Clearing buffer/cache memory..."* with a spinner. There is no confirmation dialog, the action runs immediately.
### Wait for the result [#wait-for-the-result]
When it finishes you'll see *"Buffer/cache memory cleared successfully"*. The Memory gauge updates to reflect the freed-up space.
Clearing the cache is safe. Linux uses spare RAM to speed up file reads, and it gives that memory back the moment a real program needs it. This action just releases the cache early.
## Clean Disk Space on Linux Server - Remove Old Logs and Temp Files [#clean-disk-space-on-linux-server---remove-old-logs-and-temp-files]
When the Storage card is creeping into orange or red, you can wipe out old logs and temp files.
### Find the Clean Disk Space icon [#find-the-clean-disk-space-icon]
**Storage card → Top right corner → Trash icon (orange)**
Hover for the tooltip *"Clean Disk Space (Remove old logs & temp files)"*.
### Click the icon [#click-the-icon-1]
A toast appears: *"Cleaning disk space..."* with a spinner. Like cache clearing, this runs straight away with no confirmation.
### Wait for the result [#wait-for-the-result-1]
When it finishes you'll see *"Disk space cleaned successfully"*. The Storage gauge drops by however much was reclaimed.
What this action removes:
* Log files older than 2 days
* Compressed log archives (`.gz`)
* Systemd journal entries older than 3 days
* Temporary files in `/tmp` and `/var/tmp`
* Package manager caches (`apt-get clean` or `yum clean all`, depending on your OS)
This permanently deletes the files listed above. If you need to keep older logs for audit or compliance reasons, copy them somewhere safe before running this.
## Kill a Runaway Process from the Dashboard [#kill-a-runaway-process-from-the-dashboard]
Clearing cache and disk space frees up resources a process has already used. When a process is the problem itself, pinning a core or eating the RAM, you can end it from the same *Top Processes* table you spotted it in. No copying the PID into a terminal, no `kill` command to remember.
### Find the process [#find-the-process]
**Click the CPU % or Memory % header to sort**
The heaviest process moves to the top. Check the **Process** name and **PID** before you act, PIDs get reused, and the table reorders itself every 2 seconds as the numbers move.
### Click the red trash icon [#click-the-red-trash-icon]
**Top Processes row → Right-hand column → Trash icon (red)**
A confirmation dialog opens naming the process and its PID, so you can catch a misclick before anything happens.
### Confirm and watch the table [#confirm-and-watch-the-table]
**Click to confirm**
CtrlOps sends the process a SIGTERM, the standard "please exit" signal. A toast reports whether it worked, and the process drops off the table on the next 2-second refresh.
SIGTERM asks a process to shut down, it doesn't force it. A process that ignores the signal stays in the table, in which case open the AI Terminal and run `kill -9 ` to force it. Also worth knowing: ending a service process stops the service. For anything supervised by systemd or [PM2](/docs/modules/pm2-process-manager), restart it through its manager instead, otherwise the supervisor just starts it again and the kill looks like it silently failed.
## Why Monitor a Linux Server with a GUI Dashboard Instead of CLI? [#why-monitor-a-linux-server-with-a-gui-dashboard-instead-of-cli]
Most Linux server monitoring guides recommend command-line tools like `top`, `htop`, `vmstat`, `iostat`, and `free`. These tools are powerful, but they require memorizing syntax, reading raw terminal output, and SSH-ing into each server individually.
CtrlOps replaces this workflow with a visual dashboard that runs locally on your desktop. Here is how the two approaches compare:
| Task | CLI Approach | CtrlOps Approach |
| :---------------------------- | :---------------------------------------------- | :------------------------------------------- |
| Check CPU usage | Run `top` or `htop` via SSH | Open Infra Details tab - see CPU gauge |
| Check memory usage | Run `free -h` via SSH | See Memory gauge with used/total/swap |
| Check disk usage | Run `df -h` via SSH | See Storage gauge with used/available |
| Find resource-heavy processes | Run `ps aux --sort=-%cpu` | View Top Processes table - click to sort |
| Clear buffer/cache | Run `echo 3 > /proc/sys/vm/drop_caches` as root | Click the Clear Buffer/Cache icon |
| Clean old logs | Write and run a `find` + `rm` script | Click the Clean Disk Space icon |
| Monitor during deployment | Keep SSH session open with `watch` | Keep Infra Details tab open - auto-refreshes |
For file-level operations on your server, the built-in [File Manager](/docs/modules/file-manager) provides a visual interface for browsing, uploading, and editing files over SSH.
This is not a replacement for enterprise monitoring platforms like Prometheus, Grafana, or Zabbix - those are designed for large-scale distributed infrastructure with alerting, historical data, and dashboards across hundreds of servers. CtrlOps is purpose-built for solo developers and small teams (2-10 people) who manage a handful of Linux servers and need a fast, visual way to check server health without deep CLI expertise.
## Linux Server Monitoring Tips [#linux-server-monitoring-tips]
Keep the Infrastructure Details tab open in a separate window during deploys or migrations. You'll spot a CPU or memory spike the moment it happens.
If a process is stuck consuming 100% CPU, end it straight from the table with the red trash icon in its row. Only fall back to the AI Terminal and `kill -9 ` when the process ignores the polite signal the button sends.
When the Storage card hits 90% red, clean the disk first. If it's still high, check the AI Terminal with `du -sh /* 2>/dev/null | sort -h` to find the biggest folders.
## Troubleshooting [#troubleshooting]
The connection to the server may have dropped. Look for a red banner at the top of the tab. If you see one, click **Reconnect** and the metrics will start flowing again. If there's no banner but numbers still won't move, click **Refresh Metrics** once.
The user CtrlOps logs in as needs sudo permission to drop caches. Open the AI Terminal and run `sudo -v` to confirm. If sudo asks for a password every time, ask your sysadmin to enable NOPASSWD for this user, or log in as a user with full root access.
Same root cause as above: this action runs commands like `journalctl --vacuum-time` and `apt-get clean` that need sudo. Confirm sudo works in the AI Terminal first.
Sort the *Top Processes* table by Memory %. If the heaviest processes still don't account for the usage, much of it is likely cache. Click **Clear Buffer/Cache** to confirm.
The tab polls every 2 seconds. On a slow or distant server the round trip can add visible lag. Switch to another tab and back, or click **Refresh Metrics** to force a fresh fetch.
Two likely causes.
The process ignored **SIGTERM**, which is the signal the trash icon sends. Open the AI Terminal and run `kill -9 ` to force it.
Or the process is supervised by systemd or [PM2](/docs/modules/pm2-process-manager), which restarted it immediately under a new PID. Stop or disable it through its manager instead of killing it, otherwise every kill looks like it silently failed.
## Frequently Asked Questions [#frequently-asked-questions]
### How do I monitor a Linux server without using the command line? [#how-do-i-monitor-a-linux-server-without-using-the-command-line]
CtrlOps provides a visual Infrastructure Details dashboard that shows live CPU, memory, and disk usage on any connected Linux server. Open the app, click your server, and go to the Infra Details tab. You see color-coded gauges and a process table - no terminal commands required. CtrlOps runs on Mac, Windows, and Linux.
### What metrics can I monitor on a Linux server with CtrlOps? [#what-metrics-can-i-monitor-on-a-linux-server-with-ctrlops]
CtrlOps monitors CPU load percentage (with uptime and core count), RAM usage (used/total in GB, available memory, swap), root disk storage (used/total, available space), and the top 10 processes sorted by CPU and memory consumption. Metrics auto-refresh every 2 seconds.
### Can I clear server cache and clean disk space from CtrlOps? [#can-i-clear-server-cache-and-clean-disk-space-from-ctrlops]
Yes. The Infrastructure Details tab has one-click actions for both. The Clear Buffer/Cache button releases cached memory that Linux holds for file read acceleration. The Clean Disk Space button removes log files older than 2 days, compressed archives, systemd journal entries older than 3 days, temp files, and package manager caches.
### Can I kill a process on a Linux server without using the terminal? [#can-i-kill-a-process-on-a-linux-server-without-using-the-terminal]
Yes. Every row in the *Top Processes* table has a red trash icon. Click it, confirm the process name and PID in the dialog, and CtrlOps sends the process a SIGTERM over SSH. The table refreshes on its next 2-second poll. If the process ignores SIGTERM, run `kill -9 ` in the AI Terminal to force it.
### Does CtrlOps require installing an agent on my Linux server? [#does-ctrlops-require-installing-an-agent-on-my-linux-server]
No. CtrlOps connects via SSH and fetches metrics directly from your server. There is no server-side agent, daemon, or cloud sync. All data stays on your local machine, encrypted with AES-256.
### How much does CtrlOps cost for server monitoring? [#how-much-does-ctrlops-cost-for-server-monitoring]
CtrlOps is $7/month per user (monthly) or $70/year per user (yearly). Every new account includes a 1 month free trial - no credit card required.
# Log Management: Read Linux Server Logs Without SSH (/docs/modules/log-management)
Checking server logs usually means the same ritual every time. SSH into the box, hunt down the right file path, then `tail` or `grep` your way through walls of text just to find one line.
The Logs tab replaces that. Connect to a server and CtrlOps scans it on its own, finds the log files, and groups them for you - Nginx access and error logs, PM2 process logs from your [deployed apps](/docs/modules/deployment), whatever else is running. Click one and read it. Search it, tail it live, download it, or clear it. When a log points at a real problem, take it to the [AI Terminal](/docs/modules/ai-terminal) and ask what the error means, or check [Infrastructure Details](/docs/modules/infra-details) to see whether the server was under load at the time. For a tour of what the [server log viewer](/features/log-management) does before you set it up, see the feature page.
## What you can do in the Logs tab [#what-you-can-do-in-the-logs-tab]
* See every log file CtrlOps finds on the server, grouped by what produced it - no digging for file paths.
* Add a log file auto-discovery missed by pasting its path once.
* Read any log file in a built-in viewer, without opening an SSH session.
* Search inside a log instead of scrolling through thousands of lines by eye.
* Pull up the last 200, 500, 1000, or 5000 lines.
* Refresh on demand to pull in the latest lines.
* Follow a log live and watch new lines stream in as they happen.
* Download the whole file to your machine in one click.
* Clear a log file to reclaim space, with a confirmation step first.
## Why a Logs tab instead of ssh and tail [#why-a-logs-tab-instead-of-ssh-and-tail]
| Doing it by hand | Doing it in CtrlOps |
| :------------------------------------------------------------------------------------- | :--------------------------------------------------- |
| `ssh user@host`, then remember which server this app runs on | Click the server, click the Logs tab |
| Remember or hunt for the path: `/var/log/nginx/access.log`? `~/.pm2/logs/app-out.log`? | Every log file is already listed and grouped for you |
| `tail -n 200 `, then `tail -n 500` when 200 was not enough | Pick 200, 500, 1000, or 5000 from a dropdown |
| `grep ` and re-run it as the pattern changes | Type in the search box |
| `tail -f ` and leave the session open | Click **Follow** |
| `scp user@host: .` to get a copy | Click **download** |
| `truncate -s 0 ` and hope you got the path right | Click **Clear** and confirm |
## Open the Logs tab [#open-the-logs-tab]
**Open app → Click your server → Click the Logs tab**
The tab sits in the left sidebar, below SSH Management. CtrlOps starts scanning the moment you open it.
## How CtrlOps finds your log files [#how-ctrlops-finds-your-log-files]
You do not point CtrlOps at anything. It scans the server itself and fills in the **Log Sources** list on the left, already grouped by what produced each file:
* **Web Servers** - your Nginx access and error logs.
* **Runtime & Apps** - the out and error logs for every PM2 process running on the box. To act on those processes rather than read them, use the [PM2 Process Manager](/docs/modules/pm2-process-manager) tab.
Each source shows two things under its name: the **file size** and **how long ago it was last written to** - `472 KB · 45s` for a log that is actively being appended to, `356 KB · 177d` for one that has been quiet for half a year. That is usually enough to tell which log is worth opening.
If the list is long, use the **Search log files** box above it to filter by name.
The count next to the *Log Sources* heading is the total number of files CtrlOps found, and each group carries its own count. On a busy server this is routinely 20 or more.
## Add a log file CtrlOps did not find [#add-a-log-file-ctrlops-did-not-find]
Auto-discovery covers the common locations. If an app writes somewhere unusual, add the path yourself.
### Find the input at the bottom of the sources list [#find-the-input-at-the-bottom-of-the-sources-list]
Below the log sources you will see a text input with the placeholder `/var/log/app.log`, and a green plus button next to it.
### Paste the full path [#paste-the-full-path]
Type or paste the absolute path to the log file, for example `/var/log/myapp/worker.log`.
### Click the plus button [#click-the-plus-button]
The file is added to the list and opens like any other source.
This is a one-time step. The path is saved, so the file appears alongside the auto-discovered sources every time you come back to this server.
## Read a log file [#read-a-log-file]
### Click a source in the list [#click-a-source-in-the-list]
The file's contents load into the viewer on the right. The header shows the friendly name, like *Nginx · access*.
### Check the path at the bottom [#check-the-path-at-the-bottom]
The footer shows the real file path the viewer is reading, for example `/var/log/nginx/access.log`, along with how many lines are currently loaded.
### Search inside the log [#search-inside-the-log]
Use the **Search logs...** box at the top of the viewer to filter down to the lines you care about. This is the replacement for piping the file through `grep`.
## Control how much history you see [#control-how-much-history-you-see]
The viewer loads the last **200 lines** by default, which is enough for most "what just happened" checks.
Need more history? The line-count dropdown in the toolbar takes you up to **500**, **1000**, or **5000** lines.
Right next to it, the **refresh** button pulls in the latest lines whenever you want them, without reloading the tab.
## Follow logs in real time [#follow-logs-in-real-time]
Click **Follow** and the viewer switches to **Live**. New lines stream in as your server writes them.
This is the one to reach for when you are reproducing a bug: start following, trigger the request, and watch the error land. You are catching it as it actually goes wrong, rather than refreshing afterwards and reading the aftermath.
Click again to stop following and go back to a static view.
Follow is the GUI equivalent of `tail -f`, except you do not have to keep an SSH session open to hold onto it.
## Download a log file [#download-a-log-file]
Click the **download** button in the toolbar and the whole file is saved to your machine.
Worth knowing: this downloads the **entire file**, not just the lines currently on screen. Handy when you want to hand a log to a teammate, attach it to a bug report, or dig through it in your own editor.
## Clear a log file [#clear-a-log-file]
A log file that has been growing for months can eat real disk space. Click **Clear** to truncate it on the server. CtrlOps asks you to confirm first, then empties the file.
Clearing a log file is permanent. The contents are gone from the server and cannot be recovered. If there is any chance you will want them, click **download** first, then clear.
{/* screenshot: Clear log file confirmation dialog */}
## Tips [#tips]
Sort your attention by the age shown under each source. A log that was written to `45s` ago is where your problem is. One that has not moved in `177d` almost certainly is not.
Deployed an app and it will not start? Its PM2 out and error logs are already in the list under *Runtime & Apps*. That is faster than running `pm2 logs` in a terminal, and the error log is usually the one you want. To restart it once you have found the problem, use the [PM2 Process Manager](/docs/modules/pm2-process-manager) tab.
Copy the error line out of a log and paste it into the [AI Terminal](/docs/modules/ai-terminal). Explaining a stack trace and suggesting the fix is exactly what it is good at.
## Troubleshooting [#troubleshooting]
The user CtrlOps logs in as may not have permission to read that file. Many logs under `/var/log` are owned by root. Open the [AI Terminal](/docs/modules/ai-terminal) and run `ls -l ` to check the ownership, or connect as a user with the access you need.
Auto-discovery covers the common locations, so an app writing to a custom directory may not show up. Paste the full path into the input at the bottom of the log sources list and click the plus button to add it manually.
The viewer holds a static snapshot until you ask for more. Click **refresh** to pull the latest lines, or click **Follow** to switch to Live and have new lines stream in on their own.
Clear truncates the file on the server and cannot be undone. Going forward, download a file before clearing it if there is any chance you will want the contents.
Search only looks at the lines currently loaded in the viewer. If you are on the default 200 lines and the line you want is older, raise the line count to 500, 1000, or 5000 first, then search again.
## Frequently Asked Questions [#frequently-asked-questions]
### How do I view Linux server logs without using SSH? [#how-do-i-view-linux-server-logs-without-using-ssh]
Open CtrlOps, click your server, and go to the Logs tab. CtrlOps scans the server, finds the log files on it, and groups them under headings like *Web Servers* and *Runtime & Apps*. Click any file to read it. There is no SSH session to open and no file path to remember.
### How does CtrlOps find my log files? [#how-does-ctrlops-find-my-log-files]
When you open the Logs tab, CtrlOps scans the server on its own and pulls in the log files it finds, already grouped. Nginx access and error logs land under *Web Servers*, PM2 process logs under *Runtime & Apps*. Each source shows its file size and how long ago it was last written to, so you can tell at a glance which logs are still active.
### What if CtrlOps does not find one of my log files? [#what-if-ctrlops-does-not-find-one-of-my-log-files]
Paste the full path into the input at the bottom of the log sources list, for example `/var/log/app.log`, and click the plus button. The file is added to the list. It is a one-time step - the path is saved and appears alongside the auto-discovered sources every time you come back.
### How many lines of a log file can I see at once? [#how-many-lines-of-a-log-file-can-i-see-at-once]
The viewer shows the last 200 lines by default. Use the line-count dropdown in the toolbar to raise that to 500, 1000, or 5000 lines.
### Can I watch logs update in real time? [#can-i-watch-logs-update-in-real-time]
Yes. Click **Follow** and the viewer switches to **Live**. New lines stream in as your server writes them, so you can watch something as it is actually going wrong instead of refreshing after the fact. Click again to stop following.
### Can I download a server log file to my machine? [#can-i-download-a-server-log-file-to-my-machine]
Yes. Click the download button in the toolbar and the whole file is saved to your local machine - not just the lines currently on screen.
### Does clearing a log file in CtrlOps delete it permanently? [#does-clearing-a-log-file-in-ctrlops-delete-it-permanently]
Clear truncates the file on the server, and it cannot be undone. CtrlOps always asks you to confirm before it happens. If you want to keep the contents, download the file first, then clear it.
# PM2 Process Manager: Manage PM2 Without the Command Line (/docs/modules/pm2-process-manager)
If you run Node apps on a server, you already know the loop. SSH into the box, run `pm2 list` to see what is alive, squint at the table, run `pm2 restart `, then `pm2 logs ` to find out whether that actually fixed anything. Every check is a command, and every command needs a shell.
The PM2 tab replaces that loop. Connect to a server and every process PM2 keeps alive is listed for you, with live CPU, memory, and restart counts. Restart, reload, start, stop, or delete any of them with one click. Click a process and you get its metrics, its Node.js runtime internals, and a live log stream in the same panel. Apps you shipped through [Deployments](/docs/modules/deployment) run under PM2, so they show up here automatically. For whole log files rather than one process's output, use the [Logs](/docs/modules/log-management) tab, and for server-wide CPU and memory see [Infrastructure Details](/docs/modules/infra-details).
## What you can do in the PM2 tab [#what-you-can-do-in-the-pm2-tab]
* See every process PM2 is managing on the server, with live status, CPU, memory, and restart count.
* Read totals for online, errored, and stopped processes at a glance, plus total CPU and memory.
* Restart, reload, start, stop, or delete any process with one click.
* Restart every process on the server at once.
* Save the current process list so it survives a reboot.
* Install PM2 on a server that does not have it, without opening a shell.
* Open any process to see CPU, memory, event loop lag, heap usage, restarts, and uptime.
* Check Node.js runtime internals like active handles, heap size, and event loop latency p95.
* See the auto-restart rules a process is running under.
* Stream a single process's logs live, and filter them as they arrive.
* Expand a cluster to see and manage each of its instances individually.
## Why a PM2 tab instead of pm2 commands [#why-a-pm2-tab-instead-of-pm2-commands]
| Doing it by hand | Doing it in CtrlOps |
| :-------------------------------------------------------- | :------------------------------------------- |
| `ssh user@host`, then `pm2 list` to see what is running | Click the server, click the PM2 tab |
| Count the online and errored rows yourself | The summary cards do it for you |
| `pm2 restart ` | Click the restart button on the row |
| `pm2 reload ` | Click the reload button on the row |
| `pm2 stop ` and `pm2 start ` are two commands | One button that flips with the process state |
| `pm2 delete ` | Click the trash icon |
| `pm2 restart all` | Click **Restart all** |
| `pm2 save` | Click **Save list** |
| `pm2 monit`, which holds the terminal hostage | Live metric cards you can leave open |
| `pm2 logs ` in a second SSH session | Open the process and switch to its Logs tab |
| `pm2 describe ` and read a wall of text | The Overview tab, laid out and labelled |
## Open the PM2 tab [#open-the-pm2-tab]
### Connect to your server [#connect-to-your-server]
Open CtrlOps and click the server you want to manage. Wait for the header to show **Connected**.
### Click the PM2 tab [#click-the-pm2-tab]
In the left sidebar, click **PM2**. It sits between *AI Terminal* and *Infra Details*.
### Read the process list [#read-the-process-list]
Every process PM2 is managing appears in the table, with the summary cards above it showing how many are online, errored, and stopped.
The panel header confirms the state of PM2 itself, showing `PM2 · running` next to the title once CtrlOps has found the binary and talked to the daemon.
## If PM2 is not installed [#if-pm2-is-not-installed]
Not every server has PM2 on it. If CtrlOps cannot find a `pm2` binary, the tab shows **PM2 is not installed** instead of a process list, and offers to install it for you.
### Open the PM2 tab on that server [#open-the-pm2-tab-on-that-server]
Click your server, then click **PM2** in the left sidebar. If no `pm2` binary is found, CtrlOps shows the *PM2 is not installed* screen.
### Click Install PM2 [#click-install-pm2]
Click the green **Install PM2** button in the middle of the panel. CtrlOps installs PM2 globally on the server.
### Wait for the process list to appear [#wait-for-the-process-list-to-appear]
When the install finishes, the empty state is replaced by the process list. On a fresh install the list is empty until you start something.
PM2 needs Node.js on the server. If the install does not complete, open the [AI Terminal](/docs/modules/ai-terminal) and run `node -v` to confirm Node is there first.
## Read the summary bar [#read-the-summary-bar]
Five cards sit above the process list. They are the fastest way to tell whether the server is healthy before you read a single row.
| Card | What it tells you |
| :------------ | :------------------------------------------------------------------------------ |
| **Online** | How many processes are running right now. |
| **Errored** | How many have crashed or failed to start. Anything above zero is worth opening. |
| **Stopped** | How many are registered with PM2 but deliberately not running. |
| **Total CPU** | Combined CPU across every PM2 process on the server. |
| **Total Mem** | Combined memory across every PM2 process on the server. |
Total CPU and Total Mem cover PM2 processes only, not the whole machine. For server-wide load, use [Infrastructure Details](/docs/modules/infra-details).
## The process list [#the-process-list]
Each row is one process PM2 is managing.
| Column | What it shows |
| :---------- | :------------------------------------------------------------------------------------------------ |
| **ID** | The PM2 process id, the same number `pm2 list` prints. |
| **Name** | The process name, with the script it runs underneath it, such as `app.js`, `index.js`, or `bash`. |
| **Status** | `ONLINE`, `ERRORED`, or `STOPPED`, with a coloured dot. |
| **Mode** | `fork ×1` for a single process, `cluster ×4` for a clustered app and its instance count. |
| **CPU** | Live CPU use for that process. |
| **Memory** | Live memory use for that process. |
| **↺** | How many times PM2 has restarted it. Colour-coded, so a high count stands out. |
| **Actions** | Restart, reload, start or stop, and delete. |
The restart count is the single most useful column on this page. A process sitting at `120` restarts is not healthy just because it currently reads `ONLINE` - PM2 has simply caught it 120 times. Open it and read its logs.
## Act on a process from the list [#act-on-a-process-from-the-list]
### Find the process in the list [#find-the-process-in-the-list]
Scan the **Name** column for your app. The script file it runs, such as `app.js` or `index.js`, is shown underneath the name.
### Pick an action from the Actions column [#pick-an-action-from-the-actions-column]
Each row ends with restart, reload, start or stop, and delete buttons. Click the one you want.
### Watch the row update [#watch-the-row-update]
The row updates in place with the new status, CPU, memory, and restart count, so you can confirm the action took effect without leaving the tab.
The four buttons, left to right:
| Button | Equivalent command | What it does |
| :----------- | :----------------------- | :---------------------------------------------------------------------------------------------------------- |
| Restart | `pm2 restart ` | Stops the process and starts it again. Brief downtime. |
| Reload | `pm2 reload ` | Replaces the process without dropping requests. |
| Start / Stop | `pm2 start` / `pm2 stop` | One button that flips with the state. A stopped or errored process offers start, a running one offers stop. |
| Delete | `pm2 delete ` | Removes the process from PM2 entirely. |
**Restart or reload?** Restart kills the process and brings it back, so there is a short window where it serves nothing. Reload swaps it out while it keeps serving. Reload only genuinely avoids downtime in cluster mode, where PM2 has other instances to hold the traffic. On a `fork ×1` process there is only one worker, so reload behaves much like a restart.
Delete removes the process from PM2's list. The app stops and PM2 forgets about it, so it will not come back on reboot. Your files on disk are untouched, but you will need to start it again yourself.
## Restart every process at once [#restart-every-process-at-once]
The green **Restart all** button at the top right restarts every process PM2 is managing on that server. It is the equivalent of `pm2 restart all`.
This hits everything on the box, not just the app you were looking at. On a server running several apps, restarting one from its own row is almost always what you want instead.
## Save the process list [#save-the-process-list]
**Save list** writes the current set of processes to PM2's saved process list, the same thing `pm2 save` does. PM2 restores that list when the server reboots.
Click it after you add or remove a process. If you never save, a reboot brings back whatever was saved last, which may not match what is running now.
## Inspect one process [#inspect-one-process]
Click any row and a detail panel opens on the right. The header shows the process name and status, along with its `id`, `pid`, mode, and how long it has been up.
The same actions are repeated at the top of the panel as full buttons - **Restart**, **Reload**, **Stop**, and delete - so you do not have to close the panel to act on what you are looking at. Under them sit quick chips for CPU, memory, and restart count.
The panel has two tabs: **Overview** and **Logs**.
### Overview tab [#overview-tab]
Six cards across the top, each with a live sparkline so you can see the trend rather than just the current number:
| Metric | Why it matters |
| :----------------- | :-------------------------------------------------------------------------------------------- |
| **CPU** | Sustained high CPU on a Node process usually means a blocking loop, not real work. |
| **Memory** | Resident memory. A number that only ever climbs is the classic leak signature. |
| **Event loop lag** | How long the event loop is delayed. This is the number that actually predicts slow responses. |
| **Heap usage** | How full the V8 heap is as a percentage. Near 100% and climbing means a crash is coming. |
| **Restarts** | How many times PM2 has had to bring this process back. |
| **Uptime** | How long it has been up since the last restart. |
Event loop lag is the metric worth learning. CPU and memory tell you the process is busy; event loop lag tells you it has stopped being responsive. A healthy Node process sits under a millisecond. Once lag climbs into the hundreds, requests are queueing behind synchronous work even though CPU may look fine.
Below the cards, **Node.js runtime** reports what the process looks like from inside V8, with the Node version it is running on:
* **Active handles** and **active requests** - open sockets, timers, and file operations the process is holding.
* **Heap size**, **used heap size**, and **heap usage** - how much memory V8 has claimed and how much of it is actually in use.
* **Event loop latency** and **event loop latency p95** - the typical delay, and the delay at the bad tail. The p95 is the one your slowest users feel.
Then **Auto-restart rules** shows the conditions PM2 will act on for this process:
* **Max memory restart** - the memory ceiling that triggers an automatic restart, or `not set`.
* **Watch & reload** - whether PM2 restarts the process when its files change.
* **Autorestart** - whether PM2 brings it back when it exits.
* **Last exit code** - how it ended last time. `0` is a clean exit; anything else is a crash worth reading the logs for.
{/* screenshot: process detail panel showing the Overview tab with metric cards and the Node.js runtime table */}
### Logs tab [#logs-tab]
Switch to **Logs** and that single process's output streams in live. A *streaming* indicator confirms the feed is running.
This is scoped to the one process you opened, which is the difference between it and the [Logs](/docs/modules/log-management) tab. Here you are watching one app's output as it happens. There you are reading whole log files on disk, with history, download, and search across everything on the server.
* **Filter log lines** narrows the stream to what you are looking for as it arrives.
* **Flush** clears the view so the next lines land against a clean screen. Useful right before you reproduce a bug.
Reproducing something intermittent? Open the process, switch to Logs, click **Flush**, then trigger the behaviour. Whatever appears is entirely from your attempt, with no scrollback to wade through.
## Manage a cluster [#manage-a-cluster]
An app running in cluster mode appears as a single row with its instance count under the name, for example `4 instances · index.js`, and `cluster ×4` in the Mode column. The CPU and memory on that row are the totals across every instance.
Click the chevron at the left of the row to expand it. Each instance is then listed on its own line with its own PM2 id, status, CPU, memory, and restart count, plus its own restart and stop buttons and an arrow to open its detail panel.
That split matters when only one worker is misbehaving. Instead of reloading the whole cluster, expand it, find the instance eating memory or racking up restarts, and restart just that one.
The parent row keeps its own controls, so you can still act on the cluster as a whole, and carries an extra settings button for cluster-level configuration.
Use **reload** rather than restart on a cluster. PM2 replaces the instances one at a time and the remaining workers keep serving requests, so the app never goes dark.
## Tips [#tips]
Read the restart column before anything else. A process with a three-digit restart count has been crash-looping, and PM2 has been quietly papering over it. That is where your problem is, even if the status currently says `ONLINE`.
Deployed an app through [Deployments](/docs/modules/deployment) and it will not come up? It is already here under its deployment name. Open it and go straight to the Logs tab - the reason is almost always in the last few lines.
Changed environment variables in the [File Manager](/docs/modules/file-manager)? The app will not pick them up on its own. Come back here and click restart on that process instead of running `pm2 restart` in a terminal.
## Troubleshooting [#troubleshooting]
CtrlOps looked for a `pm2` binary on that server and did not find one. Click **Install PM2** and CtrlOps installs it globally for you.
PM2 needs Node.js on the server. If the install does not complete, open the [AI Terminal](/docs/modules/ai-terminal) and run `node -v` to check that Node is present.
A high number in the restart column means PM2 has been crash-looping it. Click the process and open its **Logs** tab. The reason is almost always in the last lines before each restart - commonly a missing environment variable, a port already in use, or a database it cannot reach.
If the logs are not enough, the **Last exit code** under *Auto-restart rules* tells you how it died.
PM2 keeps a separate process list per Linux user. If your apps were started by a different user than the one CtrlOps connects as, that user's processes will not show up here.
Reconnect to the server as the user that started the apps. You can check which user you are connected as in the header next to the server name.
PM2 only restores processes that were saved to its process list. Click **Save list** after you add or remove a process so the current set is written to disk. If nothing was ever saved, PM2 has nothing to restore on boot.
Reload only genuinely avoids downtime in cluster mode, where PM2 has other instances to carry the traffic while one is replaced. On a `fork ×1` process there is a single worker, so reload behaves much like a restart. If zero-downtime restarts matter for an app, run it in cluster mode.
## Frequently Asked Questions [#frequently-asked-questions]
### How do I manage PM2 processes without the command line? [#how-do-i-manage-pm2-processes-without-the-command-line]
Open CtrlOps, click your server, and go to the **PM2** tab. Every process PM2 keeps alive on that server is listed with its status, mode, CPU, memory, and restart count. Each row has buttons for restart, reload, start or stop, and delete, so every action is a single click instead of a `pm2` command typed into a shell.
### What is the difference between restart and reload in PM2? [#what-is-the-difference-between-restart-and-reload-in-pm2]
Restart kills the process and starts it again, so there is a short window where it serves nothing. Reload replaces workers one at a time and keeps serving requests throughout, which is why it is called a zero-downtime restart. Reload only truly avoids downtime in cluster mode - on a `fork ×1` process it behaves much like a restart.
### Can I restart all my PM2 processes at once? [#can-i-restart-all-my-pm2-processes-at-once]
Yes. Click the green **Restart all** button at the top right of the PM2 tab. It restarts every process PM2 is managing on that server, the equivalent of `pm2 restart all`. It affects everything on the box, so use it when you mean the whole server, not one app.
### How do I see how much CPU and memory a PM2 process is using? [#how-do-i-see-how-much-cpu-and-memory-a-pm2-process-is-using]
The process list shows live CPU and memory for every process, and the summary cards at the top add up total CPU and total memory across all of them. Click any process to open its detail panel, where CPU, memory, event loop lag, heap usage, restarts, and uptime each get their own card with a live sparkline.
### Can I view PM2 logs for a single process live? [#can-i-view-pm2-logs-for-a-single-process-live]
Yes. Click a process, then open the **Logs** tab in its detail panel. Lines stream in as the process writes them and a *streaming* indicator confirms the feed is live. You can filter the lines with the search box, and **Flush** clears what is on screen so the next lines arrive against a clean view.
### Does CtrlOps work with PM2 cluster mode? [#does-ctrlops-work-with-pm2-cluster-mode]
Yes. A clustered app appears as a single row showing the instance count and combined CPU and memory. Expand it with the chevron and every instance is listed separately with its own id, CPU, memory, and restart controls. You can act on one misbehaving instance or on the whole cluster from the parent row.
### What does Save list do? [#what-does-save-list-do]
**Save list** writes the current set of running processes to PM2's saved process list, the same thing `pm2 save` does. PM2 restores that saved list when the server reboots, so anything you started or deleted survives a restart. Without saving, a reboot brings back whatever was saved last.
# Security Audit: Scan and Harden Your Linux Servers (/docs/modules/security-audit)
## What you can do in the Audit tab [#what-you-can-do-in-the-audit-tab]
* Run any of 25 predefined audits, grouped into Server, Database, Web Servers, and Docker. Filter the catalog by category or search it by name.
* Check what an audit looks at, how long it takes, and whether it needs sudo, before you run it.
* Pick exactly which checks run. Every check is a checkbox and all of them start ticked.
* Watch the run live, with the log streaming and real-time progress.
* Read a hardening score out of 100, a findings-by-severity breakdown, and a pass, warn, fail, and skip tally.
* Sort and filter the findings table, and see the reason a check could not answer instead of having it silently dropped.
* Download any run as a PDF, and reopen or download past runs from the Reports tab.
* Hand selected findings to the [AI Terminal](/docs/modules/ai-terminal) as a ready-made prompt, then approve each fix command yourself.
* Run the same audit across many servers at once from the workspace-level Audit Reports screen.
## Watch it run [#watch-it-run]
The whole flow in under three minutes - pick an audit, scope the checks, read the report, and fix a finding. Every step is written out below too, so you can skip straight to [running your first audit](#run-your-first-audit).
The Audit tab checks how a server is **configured**, from the inside, over an authenticated SSH session. If you want a quick look at a server from the **outside** with nothing to install and no account, the free [VPS Security Scanner](/tools/vps-security-scanner) probes open ports, TLS, and HTTP headers from the public internet. They answer different questions and are worth running together.
## Why an audit tab instead of a manual checklist [#why-an-audit-tab-instead-of-a-manual-checklist]
| Doing it by hand | Doing it in CtrlOps |
| :------------------------------------------------------------------------------------ | :-------------------------------------------------------- |
| `ssh user@host`, then remember which questions to ask | Click the server, click **Audit**, pick from the catalog |
| `grep -E 'PermitRootLogin\|PasswordAuthentication' /etc/ssh/sshd_config` | Part of the SSH & Access audit |
| `ufw status verbose`, then check `iptables` because the box uses that instead | Firewall & Network detects which one is in use |
| `ss -tulpn \| grep LISTEN` and read the output yourself | Open Ports and External Listeners, each with a verdict |
| `find / -perm -4000 -type f 2>/dev/null` | SUID/SGID Files |
| `openssl x509 -enddate -noout -in /etc/letsencrypt/live/*/cert.pem` | SSL Certificate Expiry, plus whether renewal is automated |
| `curl -sI https://example.com \| grep -i strict-transport`, six times for six headers | The Security Headers audit, all six at once |
| Decide for yourself whether each answer is bad | Every check returns a status and a severity |
| Write the findings up by hand afterwards | A report with a score, a severity split, and a PDF |
| Repeat all of it on the next server | Run on N servers from Audit Reports |
## Open the Audit tab [#open-the-audit-tab]
### Connect to your server [#connect-to-your-server]
Open CtrlOps and click the server you want to audit. Wait for the header to show **Connected**.
### Click Audit in the sidebar [#click-audit-in-the-sidebar]
**Audit** sits at the bottom of the left sidebar, under Logs. It only appears once a connection is established, because the audits run over that session.
### Read the catalog [#read-the-catalog]
The catalog opens on all 25 audits. The pills across the top filter it to **Server**, **Database**, **Web Servers**, or **Docker**, and the search box filters by name. The toggle at the right switches between grid and list.
Each card tells you what you need before you commit to a run: the audit name, a one-line description of what it looks at, how many checks it contains, roughly how long it takes, and a **sudo required** badge when full coverage needs elevated access. The **i** button opens the detail for that audit.
Every audit and the checks inside it are listed in [the audit catalog](#the-audit-catalog) further down, if you would rather read the whole set before you run anything.
## Run your first audit [#run-your-first-audit]
### Filter to the category you care about [#filter-to-the-category-you-care-about]
If you are auditing a plain application server, **Server** is the place to start, and **SSH & Access** is the audit most likely to find something. A box running Nginx and MySQL is worth auditing in all three relevant categories rather than one.
### Click Generate [#click-generate]
The green **Generate** button on the card starts the flow. Nothing has run on the server yet.
### Choose which checks to include [#choose-which-checks-to-include]
A picker opens listing every check in that audit, all of them ticked. Untick anything that does not apply to this host, and use the search box if the list is long. The footer counts what is selected, and **Clear all** empties the list if you would rather tick a handful.
This step is the answer to "I do not want it poking at my database". Nothing outside your selection runs.
### Click Continue [#click-continue]
CtrlOps runs the selected checks over your SSH session. The log streams live and progress updates as each check resolves, so a slow check is visible rather than a frozen screen. When the run finishes, the report opens.
Audits are read-only. Every check inspects configuration, file permissions, and process state. None of them change anything on the server, so running one on production is safe.
## Read the report [#read-the-report]
The report header carries the audit name, a status pill, and a line identifying the run: server name, address, date, time, and audit version. That line is what makes a downloaded PDF meaningful three months later.
### Findings by severity [#findings-by-severity]
A donut and a count for **Critical**, **High**, **Medium**, and **Low**. This is the triage view: it answers "how bad is it" before you read a single finding.
### Hardening score [#hardening-score]
A score out of 100 with a plain-language label, plus a note about the run. On a first scan it says a baseline was saved for trend, so the next run on the same server can be compared against it.
Under the score sits the coverage note. If checks were skipped because they needed elevated access, the card says so in amber with the percentage that actually ran. See [Coverage and sudo](#coverage-and-sudo) below.
### Checks run [#checks-run]
The tally: how many checks **passed**, how many raised **warnings**, how many **failed**, and how many were **skipped**. Skipped is not a failure and it is not a pass, which is why it gets its own number rather than being folded into either.
### Findings and recommendations [#findings-and-recommendations]
A table with four columns:
| Column | What it holds |
| :----------- | :--------------------------------------------------------------- |
| **Type** | The check that produced the finding |
| **Finding** | The check number, its name, and the recommendation in a sentence |
| **Status** | `PASSED`, `WARNING`, `FAILED`, or `SKIPPED` |
| **Severity** | `CRITICAL`, `HIGH`, `MEDIUM`, or `LOW` |
Status and Severity are both sortable and filterable, so you can pull every failed high-severity finding to the top and work down from there.
The recommendation is written to be actionable rather than diagnostic. A real one reads:
> **SSL Certificate Expiry** - SKIPPED - HIGH
> No `/etc/letsencrypt/live` directory - if TLS terminates elsewhere, check that platform
That is the shape of every finding: what was looked at, what was found, and what to do about it.
## Statuses and severities [#statuses-and-severities]
Every check returns exactly one status and one severity.
| Status | Meaning |
| :---------- | :--------------------------------------------------------------------------------------------------------------------------- |
| **PASSED** | The check ran and the configuration is what it should be. |
| **WARNING** | The check ran and found something worth changing, but it is not immediately dangerous on its own. |
| **FAILED** | The check ran and found a real problem. |
| **SKIPPED** | The check could not answer, and the message says why. Usually the software is not installed, or reading the file needs root. |
| Severity | Meaning |
| :----------- | :------------------------------------------------------------- |
| **CRITICAL** | Exploitable now, or exposes the whole host. |
| **HIGH** | A serious weakness that materially widens your attack surface. |
| **MEDIUM** | Worth fixing, and usually cheap to fix. |
| **LOW** | Hygiene and defence in depth. |
Severity describes how much the check matters, not how bad this particular server is. A `SKIPPED` finding can still carry `HIGH` severity: the check is important and it could not be answered, which is exactly the pair you want to know about.
## Coverage and sudo [#coverage-and-sudo]
Audits run as the SSH user you connected with, and a large share of the checks read files that only root can open, such as `mongod.conf`, `redis.conf`, database sockets, and certificate directories. Rather than guessing or silently dropping those checks, CtrlOps reports them as skipped with the real reason:
* `MySQL not accessible - server down, or root/sudo needed for socket auth`
* `Root or sudo required to read mongod.conf`
* `Root or sudo required to scan backup paths`
* `Need root to read certificates`
The score card then shows the coverage percentage for the run, so a report built from half the checks is never presented as a clean bill of health.
Connect as a user with sudo, or as root, before you run an audit you intend to act on or send to someone. A run at low coverage is still useful for a first look, but it is not the report you want in an email.
The **sudo required** badge on a card tells you in advance which audits are affected. Database and Docker audits are the ones that lean on it hardest.
## Fix a finding with AI [#fix-a-finding-with-ai]
This is the part that separates the Audit tab from a scanner. A scanner ends at a list of problems; here the list is the input to the fix.
### Select the findings you want to fix [#select-the-findings-you-want-to-fix]
Tick the checkbox at the start of each row in the findings table. Start with a single finding so you can see the whole loop before you batch them.
### Click Fix selected findings [#click-fix-selected-findings]
The bar above the summary cards becomes the action. Clicking it builds a prompt from the findings you selected and **copies it to your clipboard**. Nothing has been sent anywhere and nothing has run on the server.
### Paste it into the AI Terminal [#paste-it-into-the-ai-terminal]
Open the [AI Terminal](/docs/modules/ai-terminal) on the same server, paste the prompt into the assistant, and press Enter. It reads the findings and works out what needs to change.
### Read the command, then run it [#read-the-command-then-run-it]
Each command arrives in an approval card marked **Awaiting approval**, with the command itself and a **Why this command** explanation of what it does and why the assistant chose it. Read it. Then click **Run** to execute it, or **Cancel** to skip it and move on.
Nothing is remediated automatically, ever. The assistant proposes and explains; you approve. A command you cancel leaves the server exactly as it was. This is the same approval boundary that governs every command in the AI Terminal.
When you have worked through the findings, run the same audit again. The new run is scored against the same checks, so the score moving is a real measurement rather than a claim, and the first run is kept as the baseline to compare against.
## Download or revisit a report [#download-or-revisit-a-report]
### Open the report [#open-the-report]
Either use the report that opened when the audit finished, or click **Reports** at the top of the Audit tab. The badge on that button counts how many saved runs that server has.
### Click the download icon [#click-the-download-icon]
The download button sits at the top right of the report. It writes the whole report to your machine as a PDF: the score, the severity split, and every finding with its status and message.
### Check the header before you send it [#check-the-header-before-you-send-it]
The header line carries the server name, address, date, time, and audit version, so whoever opens the PDF knows exactly which host was scanned, when, and with which version of the checks.
## Run an audit on many servers [#run-an-audit-on-many-servers]
The per-server Audit tab audits the server you are connected to. To audit several at once, use the workspace-level version instead.
### Open Audit Reports from the Home screen [#open-audit-reports-from-the-home-screen]
Go to the **Home** tab and click **Audit Reports** under Tools in the left sidebar. The catalog is identical.
### Click Generate and pick your checks [#click-generate-and-pick-your-checks]
Same flow as a single server: choose the audit, tick the checks to include, and continue.
### Select the servers [#select-the-servers]
The picker lists every saved server with a checkbox and a search box for name or address. Tick the hosts you want and click **Run on N servers**. Each server is audited separately and gets its own report under Reports.
Running one audit across a fleet is what makes the results comparable. The same checks with the same thresholds on every host means a difference in the score is a difference in the servers, not a difference in how carefully somebody looked.
## The audit catalog [#the-audit-catalog]
The full reference: all 25 audits and every named check inside them, so you can work out which ones apply to a given server without opening the app. Approximate times are for a single server on a normal connection.
Checks for software that is not installed report as skipped, so an audit aimed at the wrong server is harmless, just not useful. Pick by what the box actually runs.
### Server [#server]
| Audit | Approx | Checks it runs |
| :----------------------- | :----- | :-------------------------------------------------------------------------------------------------------------------------------------- |
| **SSH & Access** | \~14s | SSH Root Login, SSH Password Auth, SSH Port, SSH Idle Timeout, Authorized Keys, UID 0 Accounts, Sudo Group Members, Sudo NOPASSWD |
| **Firewall & Network** | \~14s | Firewall State, Firewall Rules Audit, Docker Port Exposure, Open Ports, Exposed Database Ports, IPv6 Firewall Coverage, Outbound Policy |
| **Services & Processes** | \~11s | Unneeded Services, Running Services, External Listeners, Cron Jobs, Systemd Timers |
| **File System** | \~10s | World-Writable Files, SUID/SGID Files, /tmp Permissions, Log File Permissions |
| **Application Security** | \~10s | SSL Certificate Expiry, Certificate Auto-Renewal, Application Versions, Database Access, Resource Isolation |
| **Logging & Monitoring** | \~9s | Fail2ban, Log Rotation, Failed SSH Logins |
| **System Updates** | \~8s | Pending Updates, Unattended Upgrades, Kernel Version, Reboot Required |
### Database [#database]
Covers MySQL and MariaDB, PostgreSQL, MongoDB, and Redis.
| Audit | Approx | Checks it runs |
| :------------------------------ | :----- | :-------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| **Authentication** | \~14s | MySQL Root Password, MySQL Anonymous Users, MySQL Passwordless Accounts, MySQL Remote Root, PostgreSQL Auth Methods, PostgreSQL Password Hashing, MongoDB Authorization, Redis Authentication |
| **Network Isolation** | \~12s | Database Engines, MySQL Network Binding, PostgreSQL Network Binding, MongoDB Network Binding, Redis Network Binding, Exposed Database Ports, Web DB Admin Tools |
| **Least-Privilege Permissions** | \~12s | MySQL Wildcard Hosts, MySQL FILE Privilege, MySQL File Access, MySQL Admin Accounts, PostgreSQL Superusers, PostgreSQL Allowed Hosts |
| **Configuration & Hardening** | \~19s | Service User, Default Databases, Database Patches, Transaction Log Placement, Database Backups, Backup File Permissions |
| **Transport Encryption** | \~11s | MySQL TLS Enforcement, MySQL Certificate, PostgreSQL TLS, PostgreSQL Certificate, MongoDB TLS |
| **Credential Storage** | \~10s | Config Files In Web Root, Config File Permissions, Git In Web Root, Client Credential Files |
### Web Servers [#web-servers]
Covers Nginx and Apache.
| Audit | Approx | Checks it runs |
| :---------------------------- | :----- | :------------------------------------------------------------------------------------------------------------------------ |
| **Content Exposure** | \~14s | Directory Listing, Hidden File Exposure, Backup Files, HTTP Methods, Status Endpoints, Default Pages |
| **TLS Configuration** | \~12s | HTTPS Enabled, TLS Protocols, TLS Ciphers, Certificate Expiry, HTTPS Redirect, OCSP Stapling |
| **Logging & Monitoring** | \~12s | Access Logging, Error Logging, Log File Permissions, Log Rotation, Web Application Firewall |
| **Configuration Hardening** | \~11s | Config File Permissions, Web Root Ownership, Request Size Limits, Connection Timeouts, Rate Limiting, Unnecessary Modules |
| **Security Headers** | \~10s | HSTS, Content Type Options, Frame Protection, Content Security Policy, Referrer Policy, Permissions Policy |
| **Identification & Patching** | \~9s | Web Server Inventory, Version Disclosure, Worker User, Web Server Updates, Config Syntax |
### Docker [#docker]
| Audit | Approx | Checks it runs |
| :------------------------- | :----- | :----------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| **Image Vulnerabilities** | \~16s | Image Vulnerability Scan, Base Image Security, Image Secrets Scan, Image Configuration Review, Image Signature Verification, End-of-Life Base Image, Image Best Practices, Software Bill of Materials (SBOM) |
| **Volume Permissions** | \~13s | Sensitive Host Path Mounts, Volume Read/Write Access, World-Writable Volumes, Volume Ownership, Volume Permissions, Anonymous/Dangling Volumes, Read-Only Volume Enforcement |
| **Daemon & Socket** | \~12s | Docker Inventory, Docker TCP Socket, Socket In Containers, Docker Group Members, Daemon Log Level, Rootless Mode |
| **Network & Supply Chain** | \~12s | Port Publishing, Inter-Container Connectivity, Secrets In Env, Engine Updates, Image Hygiene |
| **Container Hardening** | \~10s | Privileged Containers, No New Privileges, Container User, Capabilities, Read-Only Filesystem, Sensitive Bind Mounts |
| **Runtime & Resources** | \~10s | Seccomp Profile, MAC Confinement, Memory Limits, CPU Limits, PID Limits, Restart Policy |
The scripts behind these audits are plain POSIX `sh` and detect the distribution and package manager themselves, so the same audit runs on Ubuntu, Debian, RHEL, Rocky, AlmaLinux, Amazon Linux, Fedora, Oracle Linux, SUSE, and Alpine without you picking a variant.
## What the audit does not do [#what-the-audit-does-not-do]
Owning the boundary is more useful than implying a wider one. Four things this is not:
**It is not a vulnerability scanner.** There is no CVE feed, no exploit testing, and it never probes hosts you do not already have SSH access to. It reads how a machine is configured. The Docker audit named *Image Vulnerabilities* checks image hygiene, such as base image age, mutable tags, embedded secrets, signature verification, and whether an SBOM exists, rather than querying a vulnerability database. For CVE scanning, use Trivy, Grype, or a commercial scanner.
**It is not continuous monitoring.** There is no schedule, no daemon, and no agent installed on the server. Every audit is a run you start, and nothing watches the box between runs. If you need continuous detection and alerting, that is a host intrusion detection system such as Wazuh or Falco.
**It is not a compliance certification.** The checks are not mapped to CIS Benchmark or STIG control identifiers, and the reports are not attested evidence for SOC 2, ISO 27001, PCI, or HIPAA. They are a hardening record: useful internally, useful to hand a client, not something an auditor will accept as a control matrix. For that path, use a compliance platform such as Vanta or Drata, or OpenSCAP with a certified SCAP profile.
**It does not fix anything by itself.** Findings become a prompt, the AI writes a command, and you approve it. There is no background remediation and no auto-apply.
Everything runs inside the SSH session you already opened. Nothing is installed on the server, no credential leaves your machine, and the report is written to your own disk. See [SSH and Security](/docs/core/ssh-security) for how the connection is handled, [Access Management](/docs/modules/access-management) for auditing *who can log in*, which is a separate question from how the box is configured, or the [Security Audit feature page](/features/security-audit) for a shorter overview of what the module is for.
## Tips [#tips]
Run **SSH & Access** first on any server you have just inherited. It is fast, it needs the least privilege of the server audits, and root login plus password authentication left on is the single most common real finding.
Use the check picker rather than skipping an audit entirely. If a Database audit is mostly irrelevant because the box only runs Postgres, untick the MySQL, MongoDB, and Redis checks and you get a short, fully relevant run instead of a wall of skips.
Fix one finding at a time on your first pass through the AI loop. Reading a single approval card teaches you what the assistant does with an audit prompt, and batching is much less nerve-racking once you have seen it work.
## Troubleshooting [#troubleshooting]
A skip means the check could not answer, and the message on the row says why. There are two common causes.
The first is that the software is not on the server. Running a Database audit on a web-only box skips almost everything, correctly. Filter the catalog to the categories that match what the server actually runs.
The second is privilege. Many checks read root-only files, so connecting as an unprivileged user skips them. Reconnect as root or as a user with sudo and run the audit again. The coverage percentage on the score card tells you how much of the audit actually ran.
Audits run over the same SSH session as everything else, so anything that breaks the connection breaks the run. Check the header still shows **Connected** and reconnect if it does not.
A run that dies partway through does not leave anything behind on the server. The checks are read-only and independent, so re-running the audit is safe and starts clean.
If the session drops repeatedly on long audits, the server may be closing idle connections. That is itself a finding: **SSH Idle Timeout** in the SSH & Access audit reports the `ClientAliveInterval` setting.
The Findings and recommendations table can be filtered, and it does not show every check by default. Clear the status filter to see passed and skipped checks alongside the open ones.
Skipped checks also matter here. The score reflects what could actually be verified, so a run at partial coverage will not reach 100 even with nothing failing. The coverage note under the score says how much of the audit ran.
The download button writes the file through your operating system's normal save path, so a blocked download is usually a permissions or disk problem on your machine rather than anything to do with the server.
Check that the report finished. A run still in progress has nothing complete to export. If the report is open and the button does nothing, close and reopen it from the **Reports** tab, which reloads the saved run from disk.
Nothing breaks. Every check detects whether the software is present and reports a skip with the reason if it is not, so running a Docker audit on a server with no Docker is harmless. It is simply not useful, and it will drag the coverage percentage down for no reason.
Use the category pills to run only what applies, or untick the irrelevant checks in the picker before you continue.
## Frequently Asked Questions [#frequently-asked-questions]
### How do I run a security audit on a Linux server? [#how-do-i-run-a-security-audit-on-a-linux-server]
Connect the server in CtrlOps and click Audit in the left sidebar. Pick an audit from the catalog, click Generate, tick the checks you want to include, and click Continue. CtrlOps runs the checks over the SSH session you already have open, streams the log live, and hands you a report with a hardening score and a downloadable PDF. Nothing is installed on the server.
### What does a CtrlOps security audit check? [#what-does-a-ctrlops-security-audit-check]
There are 25 audits across four categories. Server audits cover SSH and access, firewall and network, system updates, file system permissions, services and processes, application security, and logging. Database audits cover authentication, network isolation, least-privilege permissions, transport encryption, credential storage, and configuration hardening for MySQL, PostgreSQL, MongoDB, and Redis. Docker audits cover container hardening, the daemon and socket, image hygiene, volume permissions, runtime limits, and network exposure. Web server audits cover security headers, TLS configuration, content exposure, configuration hardening, logging, and version disclosure.
### Do I need root or sudo to run a security audit? [#do-i-need-root-or-sudo-to-run-a-security-audit]
No. Audits run as the SSH user you connected with. Many checks read files that only root can open, and those checks report SKIP with the reason rather than guessing. The score card shows a coverage percentage so a partial run is never mistaken for a clean one. Connect as a user with sudo, or as root, to get full coverage.
### Can I get a PDF security report to send to a client? [#can-i-get-a-pdf-security-report-to-send-to-a-client]
Yes. Every audit run produces a report you can download as a PDF from the download button at the top right of the result panel. It contains the hardening score, the severity breakdown, and every finding with its status and message. Past runs are kept under the Reports tab, so you can download an older one at any time.
### Is CtrlOps Audit a vulnerability scanner? [#is-ctrlops-audit-a-vulnerability-scanner]
No. It is a configuration audit. There is no CVE feed, no exploit testing, and it never probes hosts you do not have SSH access to. The Docker audit named Image Vulnerabilities checks image hygiene such as base image age, mutable tags, embedded secrets, and signature verification, rather than querying a vulnerability database. For CVE scanning use a dedicated scanner such as Trivy, Grype, or Nessus.
### Does CtrlOps run security audits on a schedule? [#does-ctrlops-run-security-audits-on-a-schedule]
No. There is no schedule, no daemon, and no agent on the server. Every audit is a run you start yourself, and nothing watches the server between runs. If you need continuous detection, that is a host intrusion detection system such as Wazuh or Falco.
### Can I use CtrlOps audit reports for SOC 2, ISO 27001, or CIS compliance? [#can-i-use-ctrlops-audit-reports-for-soc-2-iso-27001-or-cis-compliance]
Not as attested evidence. The checks are not mapped to CIS Benchmark or STIG control identifiers and the reports are not audit evidence for a certification. They are a hardening record you can act on and hand to a client. For a certification path use a compliance platform such as Vanta or Drata, or OpenSCAP with a certified SCAP profile.
### Does the AI fix security audit findings automatically? [#does-the-ai-fix-security-audit-findings-automatically]
No. Selecting findings and clicking Fix selected findings copies a prompt to your clipboard. You paste it into the AI Terminal, the assistant writes the command and explains why, and then it waits. Nothing runs on the server until you read the command and click Run. Findings are fixed one at a time with you approving each step.
### Can I run the same audit on more than one server at once? [#can-i-run-the-same-audit-on-more-than-one-server-at-once]
Yes. Open Audit Reports from the Home screen instead of the per-server Audit tab, click Generate on the audit you want, and the server picker lists every saved server with a checkbox. Select the servers and click Run on N servers. Each host is audited separately and gets its own report.
# Server Management (/docs/modules/server-management)
The CtrlOps **Home** page is where you add servers and manage every saved connection, all without remembering an `ssh` command. Once you're connected, head to [SSH Key Management](/docs/modules/ssh-management) to control who can log in to a server, or to [Access Management](/docs/modules/access-management) for the fleet-wide view of who can reach what. For an overview of the [server management dashboard](/features/multi-server-management) itself, see the feature page.
## Add servers and manage your connections [#add-servers-and-manage-your-connections]
* Add a new server with a password or a `.pem` key.
* Paste a full SSH connection string and let CtrlOps fill the form for you.
* Set a custom port or route through a bastion with a proxy command.
* Generate an SSH key pair on your local machine with the setup wizard.
* Edit, reconnect, or delete saved servers from their cards.
* Favorite the servers you use most and reach them from the Favorites tab.
* Tag servers by environment and filter the Home page down to one environment at a time.
* Test connections before saving.
* Import or export your saved server list as a JSON backup.
## Add a new server connection [#add-a-new-server-connection]
This is what you do the very first time, on the Home page.
### Open the Add Connection form [#open-the-add-connection-form]
**Open app → Click New Connection (top left of the sidebar)**
A modal opens with two tabs: **SSH-based Connection** and **.pem Key-based Connection**.
At the top is a **Quick Connect via SSH String** field. If you already have a working SSH command, paste it here (e.g. `ssh -i ~/.ssh/mykey.pem user@192.168.1.1 -p 2222`, or a plain `ubuntu@host`) and CtrlOps auto-fills the IP, Username, Port, and key path on either tab. Skip it if you'd rather type the details in by hand.
### Fill in the basics (both tabs) [#fill-in-the-basics-both-tabs]
| Field | What to enter |
| :------------------------- | :--------------------------------------------------------------------------------------------------------------------------------------------------------- |
| **Server Name (optional)** | A friendly name like `Production API`. Helps when you have many servers. |
| **Tag (optional)** | Mark the server as `Production`, `Staging`, or `Development`. Servers with no tag stay in the **Untagged** group. Used by the tag filter on the Home page. |
| **IP Address** | The server's IP or hostname, e.g. `192.168.1.10` or `api.yoursite.com` |
| **Port** | The SSH port. Defaults to `22`; change it only if your server uses a non-standard port. |
| **Username** | The Linux user to log in as, e.g. `ubuntu`, `root`, `ec2-user` |
### Pick your auth method [#pick-your-auth-method]
**For password-based servers:**
Stay on the *SSH-based Connection* tab. Toggle on **Use password authentication**. A password field appears.
| Field | What to enter |
| :-------------------- | :--------------------------------------------------------------------------------------- |
| **Password** | Your SSH password. Click the eye icon to confirm what you typed. |
| **Remember password** | Check it to save the password (encrypted). Leave it unchecked to be prompted every time. |
**For key-based servers (most cloud VMs):**
Switch to the *.pem Key-based Connection* tab.
| Action | What it does |
| :----------------------- | :-------------------------------------------------------------------------------- |
| **Select .pem Key File** | Opens a file picker. Pick the private key file you downloaded from AWS, GCP, etc. |
| Manual path input | Or paste the full path to the key file if you know it. |
### Connect through a proxy (optional) [#connect-through-a-proxy-optional]
If the server is only reachable through a bastion or jump host, expand **Advanced Settings** and fill in the **Proxy Command** field, e.g. `ssh -W %h:%p user@bastion`. Leave it empty for servers you can reach directly.
### Test and save [#test-and-save]
**Click Connect SSH (or Connect with .pem)**
A spinner shows *"Connecting to server..."*. CtrlOps tries to actually log in. After 5 seconds, you'll see a *"Taking longer than usual"* note if the server is slow.
If the connection works, the server is saved and you land in **Instance Details** straight away. If something fails, you'll see *"Connection Failed"* with the error and a list of things to check, fix the input and try again.
Windows servers are not supported. If you point CtrlOps at a Windows machine, you'll see *"Windows Server Not Supported"* with the list of OSes that work (Ubuntu, Debian, CentOS, RHEL, Fedora, Amazon Linux).
## Manage your saved servers [#manage-your-saved-servers]
Each saved server appears as a card on the Home page.
| Card element | What it shows / does |
| :-------------------------- | :------------------------------------------------------------------------------------------------------- |
| Server name | Bold heading. If you didn't set a name, the IP shows here. |
| Username and IP | Gray text in the form `username@ip` |
| Last connected | Small timestamp |
| Tag badge | The server's environment, shown as a coloured badge when you've set one. Untagged servers show no badge. |
| **Favorite** (star icon) | Click to mark the server as a favorite. It then appears under the **Favorites** tab for quick access. |
| **Connect** (play icon) | Tests the connection then opens **Instance Details** |
| **Edit** (pencil icon) | Opens the same form pre-filled, so you can change details |
| **Delete** (red trash icon) | Asks *"Are you sure to delete this connection?"*. Click **Yes** to remove it. |
## Favorite your most-used servers [#favorite-your-most-used-servers]
When you have a long list of servers, favorites keep the ones you reach for most just a click away, no scrolling or searching through the full list.
### Mark a server as a favorite [#mark-a-server-as-a-favorite]
**Click the star icon on the server's card** (bottom row, next to Edit and Delete)
The star fills in to show it's a favorite. Click it again any time to remove the favorite.
### Open the Favorites tab [#open-the-favorites-tab]
**Click Favorites in the left sidebar** (under Workspace)
You'll see only your favorited servers, with the same Connect, Edit, and Delete actions as the main list. The sidebar shows a count next to **Favorites** so you know how many you've pinned.
Favorite the handful of servers you connect to every day. With 50 servers in your workspace, jumping straight to the Favorites tab is far faster than filtering the full list each time.
## Tag servers and filter by environment [#tag-servers-and-filter-by-environment]
Favorites cover the handful of servers you touch daily. Tags handle the other problem, telling production apart from staging when the list gets long, so you can narrow the Home page to one environment before you start working.
### Tag a server [#tag-a-server]
**Click Edit on the server's card → Pick a tag → Save**
The **Tag** field offers three environments: *Production*, *Staging*, and *Development*. You can also set it when you first add the server, on either the SSH-based or `.pem` tab. Leave it empty and the server lands in **Untagged**, which is a real filter option rather than a hidden bucket.
### Open the tag filter [#open-the-tag-filter]
**Click the funnel icon** (top right of the server list, next to the view switcher)
A dropdown opens with a *Search in filters* box at the top, a **Select all items** row, one row per tag with its colour dot, and a **Reset** link at the bottom.
### Filter to one or more environments [#filter-to-one-or-more-environments]
**Tick the tags you want to see**
The list narrows as you tick. Ticking is additive, so **Production** and **Staging** together shows both. Tick **Untagged** on its own to find the servers you added quickly and never labelled.
### Clear the filter [#clear-the-filter]
**Click Reset** (bottom of the dropdown)
The full list comes back. **Select all items** does the same thing in one click when you have several tags ticked.
Filter to **Production** before a deploy or a restart. When the list only holds production servers, you can't fire a command at a staging box by mistake, which is the failure mode a long unfiltered list invites.
## Connect with a "remember password" off [#connect-with-a-remember-password-off]
If you saved a connection without ticking *Remember password*, CtrlOps prompts you each time.
**Click the server card → Password modal opens → Type the password → Click Connect**
You'll see the server name at the top of the modal so you know which password is being asked for. Tick **Remember password** in this modal if you want to skip it next time.
## Set up SSH keys for the first time (the wizard) [#set-up-ssh-keys-for-the-first-time-the-wizard]
If you've never used SSH before, the wizard walks you through generating a key on your computer and copying the public part onto the server.
### Open the wizard [#open-the-wizard]
**In the left sidebar, under TOOLS, click SSH Setup**
The wizard opens in its own tab with three steps - *SSH Installation*, *SSH Keys*, and *Server Setup* - and a progress indicator at the top.
### SSH installation check [#ssh-installation-check]
CtrlOps checks if `ssh` is installed on your computer. If yes, you'll see the version and path. If no, you'll see install instructions for Mac, Windows, and Linux. Follow them, then click **Check Again**.
When SSH is found, click **Next**.
### SSH key setup [#ssh-key-setup]
The **Your SSH keys** card lists every public key found in `~/.ssh` with its bit size and a **Copy Key** button. If a key is already there, skip ahead.
If you don't have keys, use the **Generate another key** card. There's no form to fill in, just one of two buttons:
| Button | When to use it |
| :----------------------- | :---------------------------------------------------- |
| **Generate Ed25519 Key** | The default choice. Smaller and more secure than RSA. |
| **Generate RSA Key** | Only when your server can't accept Ed25519 keys. |
**Wait for the success toast** and the new key appears in the list above.
The key is saved on your computer in the standard location (`~/.ssh/`). Click **Next**.
### Add the public key to the server [#add-the-public-key-to-the-server]
The **Your public keys** card repeats your keys with a **Copy Key** button, plus a **Refresh** button if you generated a key elsewhere. Below it, three methods are shown.
| Method | When to use it |
| :---------------------------------------------------------------------------------- | :------------------------------------------ |
| **Method 1 (Recommended)**: Run `ssh-copy-id username@server-ip` from your terminal | When you can already log in with a password |
| **Method 2**: Manually append to `~/.ssh/authorized_keys` | When you have shell access via another tool |
| **Method 3**: Add through your cloud provider dashboard | First-time setup on AWS, GCP, etc. |
A **Detailed setup instructions** section expands to show the exact commands, each with its own **Copy** button - the `ssh-copy-id` one-liner, then a six-command **Manual method** covering `mkdir -p ~/.ssh`, appending to `authorized_keys`, and the `chmod 600` / `chmod 700` permissions. Click **Copy Key** to copy the public key to your clipboard, then paste it wherever the method needs it.
**Click Complete setup** to close the wizard. You can now use the key when adding a connection.
## Backup your saved servers [#backup-your-saved-servers]
Useful when you switch computers or want a backup.
### Export [#export]
**Open app → Click the three-dot menu (top right) → Export**
A save dialog opens with the default name `ctrlops_servers_backup_YYYY-MM-DD.json`. The file contains all your saved connections, including any saved passwords and key paths.
The export includes saved passwords. Treat the JSON file like a password file: store it securely.
### Import [#import]
**Three-dot menu → Import → Pick a JSON file**
CtrlOps adds new connections and skips duplicates (matched by username, IP, port). You'll see a toast like *"Import complete! Added 5 new servers, 2 duplicates skipped"*.
## Tips [#tips]
Prefer Ed25519 keys for new setups. They're shorter, faster, and at least as secure as RSA 4096.
Add a meaningful comment when generating a key (the *Email* field). When you have keys from several machines on a server, the comment is the only way to tell them apart.
## Troubleshooting [#troubleshooting]
The error message includes the cause. Common ones: wrong username (try `ubuntu` for AWS Ubuntu, `ec2-user` for Amazon Linux, `root` for many VPS providers), firewall blocking port 22, or the `.pem` key has wrong permissions on your local machine. For permission issues, run `chmod 600 yourkey.pem` in your local terminal.
The server is slow to respond, often because it's far away or under load. Wait up to 30 seconds. If it still fails, the server may be unreachable, check the IP and that any cloud security group allows port 22 from your IP.
The JSON file is corrupt or wasn't an export from CtrlOps. Open it in a text editor and confirm it starts with `[` and contains an array of server objects.
# SSH Key Management (/docs/modules/ssh-management)
Once you're connected to a server, the **SSH Management** tab is where you control who can log in: add an authorized key, see every key on the server, and revoke access in one click, all without editing `authorized_keys` by hand. You can also create system users with their own access level, so you can grant least-privilege access (read-only or read/write) without handing anyone full root. To add or connect servers in the first place, see [Server Management](/docs/modules/server-management); to manage access across your whole fleet from one screen, see [Access Management](/docs/modules/access-management). For an overview of the [SSH key manager](/features/ssh-management) before you dive in, see the feature page.
## What You Can Do - Manage SSH Keys Visually [#what-you-can-do---manage-ssh-keys-visually]
* Generate an SSH key pair (Ed25519 or RSA 4096) from a built-in GUI wizard - no terminal commands needed.
* Add your SSH key to a server using ssh-copy-id, manual append, or cloud provider dashboard, with step-by-step instructions inside the app.
* See every authorized key on a connected server in a visual registry.
* Add one or more public keys at once.
* Create custom system users with read/write or read-only access.
* Target a key to a specific system user when you add it.
* Filter the registry by system user to see who has which access.
* Copy a key to reuse it on another server.
* Revoke a key to remove that person's access immediately.
## Generate an SSH Key (GUI Wizard) [#generate-an-ssh-key-gui-wizard]
If you don't have SSH keys yet, CtrlOps includes a built-in wizard that generates them for you - no terminal commands required. This is the fastest way to generate an SSH key using a GUI on Mac, Windows, or Linux. (Just need a quick key in the browser without installing anything? Our free [SSH key generator](/tools/ssh-key-generator) covers that, and the [SSH key management best practices guide](/blog/ssh-key-management-best-practices) explains how to look after keys across a whole fleet.)
### Open the SSH Setup Wizard [#open-the-ssh-setup-wizard]
**In the left sidebar, under TOOLS, click SSH Setup**
The wizard opens in its own tab and runs through three steps - *SSH Installation*, *SSH Keys*, and *Server Setup* - with a progress bar at the top.
### Step 1 - SSH Installation Check [#step-1---ssh-installation-check]
CtrlOps checks if SSH is installed on your computer. If it's found, you'll see the version and path. If not, you'll see platform-specific install instructions for Mac, Windows, and Linux. Follow them, then click **Check Again**.
When SSH is detected, click **Next**.
### Step 2 - Generate or View Your SSH Keys [#step-2---generate-or-view-your-ssh-keys]
The **Your SSH keys** card lists every public key found in `~/.ssh`, with a *keys found* count on the right. Each key shows its name, its bit size (for example *256 bits* for Ed25519), the full public key in a read-only field, and a **Copy Key** button. If a key is already listed, you can skip ahead to Step 3.
If you don't have a key yet, use the **Generate another key** card below. There's no form to fill in - just pick a type:
| Button | When to use it |
| :----------------------- | :---------------------------------------------------- |
| **Generate Ed25519 Key** | The default choice. Smaller and more secure than RSA. |
| **Generate RSA Key** | Only when your server can't accept Ed25519 keys. |
Wait for the success toast. The key pair is saved in your computer's standard SSH directory (`~/.ssh/`) and appears in the list above. Click **Next**.
### Step 3 - Add Your SSH Key to the Server [#step-3---add-your-ssh-key-to-the-server]
The **Your public keys** card at the top repeats your keys with a **Copy Key** button, plus a **Refresh** button if you generated a key in another window. Below it, three methods are provided. Pick whichever fits your setup:
| Method | When to use |
| :---------------------------------------------------------------------------------- | :----------------------------------------------- |
| **Method 1 (Recommended):** Run `ssh-copy-id username@server-ip` from your terminal | When you can already log in with a password |
| **Method 2:** Manually append to `~/.ssh/authorized_keys` | When you have shell access through another tool |
| **Method 3:** Add through your cloud provider dashboard | First-time setup on AWS, DigitalOcean, GCP, etc. |
A **Detailed setup instructions** section expands with pre-filled commands, each with its own **Copy** button. It opens with the one-line `ssh-copy-id username@your-server-ip`, then a **Manual method** for when that isn't available:
1. Copy the public key (use the **Copy Key** button)
2. Connect to your server: `ssh username@your-server-ip`
3. Create the SSH directory: `mkdir -p ~/.ssh`
4. Append the key: `echo "YOUR_PUBLIC_KEY" >> ~/.ssh/authorized_keys`
5. Set file permissions: `chmod 600 ~/.ssh/authorized_keys`
6. Set directory permissions: `chmod 700 ~/.ssh`
A **Cloud provider dashboards** note closes the section: most providers (AWS, DigitalOcean, Linode) let you paste the key into an *SSH Keys* or *Security* screen instead.
Click **Complete setup** to close the wizard. Your new key is ready to use when adding server connections.
## Manage SSH Keys on a Server (SSH Management tab) [#manage-ssh-keys-on-a-server-ssh-management-tab]
Inside a connected server, the SSH Management tab is where you control who can log in.
**Open app → Click your server → Click the SSH Management tab**
You'll see a stat row at the top with four counters: *Registry* (total), *ED25519* (secure), *RSA* (standard), *Access* (other types). Below that is the *Registry Governance* card with an **Active System User** dropdown at the top right and the keys table, which includes a **System User** column showing what each key can log in as.
{/* screenshot: SSH Management tab with stats row and authorized keys table */}
## System Users and Roles [#system-users-and-roles]
A server can have several system users, each with its own access level. The **Active System User** dropdown at the top of Registry Governance lets you switch between them and create new ones.
The dropdown lists:
* **All Users** (default) - every key on the server.
* Each existing system user with its level badge, e.g. `root` (**SUDO**), `ubuntu` (**STANDARD**), plus any custom roles you create.
* **+ Create User** - opens the form to add a new system user (see below).
**Filter the registry by system user.** Pick a system user from the dropdown to show only the keys that can log in as that user. For example, choose `ubuntu` to see just the keys with ubuntu access. Switch back to **All Users** to clear the filter. The **System User** column in the table shows the same information per key as ROOT, UBUNTU, or custom-role badges.
Each access level grants different rights:
| System user / role | Rights |
| :-------------------- | :------------------------------------------------------------- |
| **root** | sudo - full admin (read, write, update, delete, run anything) |
| **ubuntu** (standard) | read, write, update, and delete |
| Custom **read/write** | read and write, but cannot delete |
| Custom **read-only** | read only - no add, edit, delete, or running arbitrary scripts |
## Create a Custom User Role [#create-a-custom-user-role]
Instead of giving everyone the same access you have, you can create a system user with exactly the rights you want and authorize keys against it.
### Open the Create User form [#open-the-create-user-form]
**Open the Active System User dropdown → Click + Create User**
A modal opens titled *Create User*, *"Create a new Linux system user."*
### Enter a username [#enter-a-username]
Type a **Username** for the new system user, e.g. `jsmith`.
### Pick the access level [#pick-the-access-level]
Choose one:
| Option | What it grants |
| :---------------------- | :-------------------------------------------------------------------------------------------------------- |
| **Read / Write Access** | Standard interactive user with write permissions. They can read and work on the server but cannot delete. |
| **Read Only Access** | Restricted shell access. They can read the server but cannot write, delete, or run arbitrary scripts. |
### Create [#create]
**Click Create User (or press Enter)**
The new system user is created on the server and appears in both the **Active System User** and **Target System User** dropdowns, ready to authorize keys against.
Use **Read Only Access** for auditors or contractors who should look but never change anything, and **Read / Write Access** to let someone work without delete rights or sudo. Reserve `root` for people who genuinely need full admin.
## Add an SSH Key to a Server [#add-an-ssh-key-to-a-server]
### Open the Add Key form [#open-the-add-key-form]
**Click Add Key (top right of the Registry Governance section)**
A modal opens titled *Add SSH Key*, *"Securely import keys to your registry."*
### Choose the target system user [#choose-the-target-system-user]
Pick the **Target System User** from the dropdown, `root`, `ubuntu`, or any custom role you created (such as `readwrite`). This decides which system user the key can log in as, and so what access the key holder gets.
### Paste the public key [#paste-the-public-key]
Paste the contents of a `.pub` file. You can paste several keys at once, press Enter for a new line to add multiple keys in one go. A pulse-dot indicator shows *"N Keys Detected, all will be added"* as you paste.
### Save [#save]
**Click Import Key**
A toast confirms *"Key added"*. The new key appears in the table immediately with a *"SYNCING"* label until the server confirms.
Only the **public** half of a key pair goes here. It's the file ending in `.pub`. Never paste a private key into this field.
## View and Audit Your SSH Keys [#view-and-audit-your-ssh-keys]
This table audits the keys themselves. To audit the SSH *configuration* they log in through - root login, password authentication, port, idle timeout, `authorized_keys` permissions, UID 0 accounts, and sudo rules - run the **SSH & Access** audit from the [Security Audit](/docs/modules/security-audit) tab.
The keys table has five columns:
| Column | What it shows |
| :---------------------- | :---------------------------------------------------------------------------------------------------------- |
| **Name / Identity** | The key's comment or *"Unnamed Signature"* if blank |
| **Signature** | Type badge (ED25519 in green, RSA in blue) |
| **Public Key Identity** | The key string, blurred by default. Hover for the *"CLICK TO REVEAL"* tooltip, click to show full key. |
| **System User** | Badges (ROOT, UBUNTU, or a custom role) for the system user(s) this key can log in as |
| **Actions** | Copy and Revoke buttons |
## Copy a Key [#copy-a-key]
**Click the Copy icon in the Actions column**
A toast confirms *"Key copied to clipboard"*. Useful when you want to add the same key to another server.
## Revoke an SSH Key (Remove Access) [#revoke-an-ssh-key-remove-access]
### Click Revoke (red trash icon) on the row [#click-revoke-red-trash-icon-on-the-row]
A confirmation pops up titled *"Revoke Key Access?"* with the warning *"This will immediately terminate target login signature."*
### Confirm [#confirm]
**Click Revoke Now**
The key is removed from the server's `authorized_keys` file immediately. The user with that key can no longer log in.
Revoking takes effect right away. Make sure you still have at least one other working key, or password access, before revoking the key you're currently using to connect, otherwise you'll lock yourself out.
## Tips [#tips]
Always test a new key by opening a fresh CtrlOps connection in another window before revoking the one you're using. If something is wrong, you still have a way in.
Prefer Ed25519 keys for new setups. They're shorter, faster, and at least as secure as RSA 4096.
Add a meaningful comment (the Email field in the wizard) when generating a key. When you have keys from multiple machines on a server, the comment is the only way to tell them apart in the registry.
## Troubleshooting [#troubleshooting]
The user CtrlOps logged in as can't read or write `~/.ssh/authorized_keys`. The tab needs root or sudo with NOPASSWD. Reconnect as root, or have your sysadmin enable NOPASSWD for your user.
Same problem as above with a different message. CtrlOps can't run sudo because the server still asks for a password. Either log in as a user with passwordless sudo, or as root directly.
Three things to check, in order:
* The server's `~/.ssh/authorized_keys` permissions must be `600`, and `~/.ssh` must be `700`. Run `ls -la ~/.ssh` in the AI Terminal.
* SELinux on RHEL/CentOS can block keys. Run `restorecon -R -v ~/.ssh` to fix labels.
* Make sure you're connecting as the right user, the key only authorises one specific Linux user.
That exact public key is already in `authorized_keys`. Either it's already authorised, or another row has the same key under a different comment. Look for it in the table.
Creating a system user writes to the server, so it needs root or sudo. If you connected as a read-only system user (or a user without sudo), the **+ Create User** action can't complete. Reconnect as `root` or a read/write (sudo) user and try again.
Same cause: a read-only system user can't modify `authorized_keys` or delete users. Revoking and removing need root or a read/write (sudo) system user. Reconnect with the right access and the Revoke and delete actions become available.
## Related tools [#related-tools]
Free, browser-based tools for the key work described above. Nothing you paste into them is uploaded.
# AI Not Responding (/docs/troubleshooting/ai-not-responding)
The AI Assistant is the panel that slides in on the right of the AI Terminal tab. It needs one AI provider connected to work - a ChatGPT account, an OpenRouter account, or your own API key - and it talks to that provider directly. Most AI problems boil down to a credential issue, a network issue, or a provider issue.
CtrlOps doesn't run its own AI service. You connect your own provider account or API key, and CtrlOps stores the credential locally on your computer. Costs for AI usage are paid directly to your provider, not to CtrlOps.
## Why the AI Terminal Stops Responding [#why-the-ai-terminal-stops-responding]
* Fixing the *"AI Not Configured"* empty state.
* *"Unauthorized"* and *"Invalid API key"* errors.
* Models dropdown stuck on *"Loading models..."*.
* Slow responses, timeouts, and rate limits.
* AI suggesting wrong or unsafe commands.
* Auto-Run not behaving the way you expected.
## Common problems and fixes [#common-problems-and-fixes]
No AI provider is connected yet. Open **AI Keys** from the left sidebar, under **TOOLS**, then pick one of three ways to connect:
* **Sign in with ChatGPT:** on the first **Quick connect** card, if you already have a ChatGPT account. No API key.
* **Connect with OpenRouter:** on the second card. A free OpenRouter account is enough - CtrlOps picks a free model for you.
* **Add credential:** in the **API credentials** section, to use your own key from OpenAI, Anthropic, Google, or a custom OpenAI-compatible endpoint.
See the [AI Terminal page](/docs/modules/ai-terminal#add-an-ai-key-one-time-setup) for the full walkthrough.
The API key isn't being accepted by the provider. Causes, in order of likelihood:
* **The key was copied with extra whitespace.** Re-copy from your provider's dashboard and re-paste.
* **The key was revoked or rotated.** Generate a new one in the provider's console.
* **The key has the wrong permissions / scope.** OpenAI keys need access to chat completions. Anthropic keys need messages access. Most personal keys have everything by default.
* **You're out of credits.** Many providers freeze keys when the prepaid balance hits zero.
**Fix:** Left sidebar → TOOLS → AI Keys → click **Edit** on the credential → paste the new key → click **Test connection** before saving.
The provider's API isn't returning a list of models. Three things to check:
* **API key first.** A wrong key shows the same symptom. Click **Test connection**, if it says *Unauthorized*, fix the key.
* **For OpenAI Compatible providers:** the *Base URL* is required and must include the version path, for example `https://api.your-provider.com/v1`, not just `https://api.your-provider.com`.
* **Network issues** between you and the provider. Check by visiting the provider's dashboard in a browser, if that loads, the network is fine.
You've sent more requests in a short window than the provider allows. The fix depends on your provider:
| Provider | What to do |
| :------------ | :----------------------------------------------------------------------------------------------------------------------------------------------- |
| OpenAI | Visit the [OpenAI usage page](https://platform.openai.com/account/usage) to see your tier limits. Wait a minute and retry, or upgrade your tier. |
| Anthropic | Free-tier accounts have low rate limits. Add credits to move into a higher tier. |
| Google Gemini | Free tier has strict per-minute limits. Wait, or switch to a paid model. |
Switching to a cheaper model from the dropdown also helps, because cheaper models often have higher rate limits.
A few things to try, in order:
* **Switch to a faster model** from the dropdown at the bottom-left of the AI panel. Try `claude-haiku`, `gpt-4o-mini`, or `gemini-flash`.
* **Reduce the conversation length.** Click **New** in the AI panel header to start a fresh chat. Long histories make every response slower.
* **Lower the Max AI reasoning steps** in the panel footer. The AI may be running many internal steps before answering. Try 20 to 50.
* **Check the provider's status page** if responses are abnormally slow across many sessions.
The AI hit the Max AI reasoning steps cap mid-task. Two fixes:
* **Raise the cap.** The slider in the AI panel footer goes up to 200. Bump it for complex tasks.
* **Break the task in half.** "Set up nginx + issue an SSL cert + start the app" is three tasks. Ask each one separately, then chain them.
A few things sharpen the responses:
* **Be specific.** *"Apache shows 'Address already in use' on port 80"* gets a better answer than *"my server is broken"*.
* **Paste the exact error.** The AI is excellent at decoding cryptic error text but can only do that if it sees the text.
* **Mention the OS.** Ubuntu, CentOS, Amazon Linux, all have slightly different commands. Saying so up front avoids generic guesses.
* **Start a new conversation** when you switch topics. Long conversations drift.
* **Try a stronger model** (`claude-opus`, `gpt-4o`, `gemini-pro`) for hard or unusual problems.
The terminal session may have disconnected. Look at the bottom-left for a *"Disconnected"* alert, click **Reconnect**, then ask the AI to retry.
If the terminal is connected but Run still does nothing, switch to another tab and back to refresh the panel. As a last resort, right-click the terminal and choose **Reset Session**.
**Auto-Run** only auto-approves commands the AI proposed itself in the same conversation. Some safety-critical commands, particularly those that delete files or stop services, may still surface a confirmation. That's intentional.
If you want zero prompts at all, the AI panel's Auto-Run toggle is the only switch, there is no separate *"safety level"* setting in the product today.
Leave Auto-Run off until you've used the AI for a while. Once it's on, every command runs the moment the AI suggests it, and reading mistakes get expensive fast.
Reset by switching tabs:
* Click the **File Manager** tab, then back to **AI Terminal**.
* Click **AI Assistant** (robot icon) in the header.
If it's still stuck, restart the app. The chat history is preserved as long as you don't click **New**.
A few common cost traps:
* **Heavy models on every question.** GPT-4 Opus / Claude Opus / Gemini Pro are 5 to 20 times more expensive per token than their smaller siblings. Switch to a small model for routine questions and reserve the big ones for hard problems.
* **Auto-Run on with chains of commands.** Each command's output gets fed back to the AI, which decides on the next command. Twenty hops add up.
* **Web Search on by default.** Web search adds tokens. Toggle it off when you don't need it.
* **Long-running conversations.** Old messages in the same conversation are re-sent on every new question. Click **New** when starting a different topic.
You can see exact costs in your provider's dashboard. Set a monthly budget cap there if you want a hard limit.
The AI sometimes returns plain code without specifying a language. To force highlighting, ask it to *"format the answer as bash"* (or python, sql, nginx, etc.). The next response will use that language hint.
Highlighting is supported for: bash, javascript, typescript, python, php, sql, yaml, json, nginx, and most other common languages.
## When all else fails: gather details and ask [#when-all-else-fails-gather-details-and-ask]
Before reaching out, collect:
| Info | Where to find it |
| :------------------------------------------------- | :----------------------------------------------------- |
| The exact error text | From the AI panel chat or the toast |
| Which provider and model you're using | From the dropdown at the bottom-left of the AI panel |
| The status of *Test connection* on your credential | Left sidebar → TOOLS → AI Keys → click your credential |
| A screenshot of the panel | Whole AI panel, including the footer |
Then bring it to:
* **Discord community:** [Join Discord](https://discord.gg/JhRCp3hsT9)
* **The AI itself**, ironically. Paste the error you saw and ask the AI to explain the cause. Often it can.
AI is a fast assistant, not an oracle. Read every command before you click **Run**, especially anything that deletes files, stops services, or rewrites configs.
# Backup Not Running (/docs/troubleshooting/backup-not-running)
A backup job that doesn't run is worse than no backup, you think you're covered, but you aren't. This page walks through the symptoms you'll see in the **Backup** tab, and the exact fix for each one.
CtrlOps backs up from your server to S3-compatible storage today (AWS, Cloudflare R2, Backblaze B2, Wasabi, MinIO, DigitalOcean Spaces). SFTP and Local destinations are not supported in the current release.
## Why Backup Jobs Fail and How to Fix Them [#why-backup-jobs-fail-and-how-to-fix-them]
* Banners at the top of the tab (rclone, cron, shell) and what each one means.
* *"Test Connection"* failures and how to read them.
* Backups that succeed but copy zero files.
* Scheduled backups that never trigger.
* Live runs that stall, fail mid-way, or run too slowly.
## First, scan the top of the Backup tab [#first-scan-the-top-of-the-backup-tab]
Whenever something breaks, the Backup tab shows you why. Before opening any specific job, look for one of these alert banners:
| Banner | What it means | One-click fix |
| :--------------------------------------------------- | :------------------------------------------------- | :--------------------------- |
| *"Rclone Not Installed"* (yellow) | The tool that copies files isn't on the server | Click **Install Rclone** |
| *"Cron is required for scheduled backups..."* | Cron isn't installed; only manual backups will run | Click **Install Cron** |
| *"Cron is installed but the service is not running"* | Cron exists but is stopped | Click **Start Cron Service** |
| *"Backup Shell Disconnected"* | The session managing backups dropped | Click **Reconnect** |
If a banner is showing, fix it first. Most "backup didn't run" cases are one of these four.
## Common problems and fixes [#common-problems-and-fixes]
You filled in the form, clicked **Test Connection**, and got an error. The four most common causes, in order:
* **Wrong region.** AWS strictly requires the region to match the bucket. Look up the bucket in the S3 console and copy the region exactly (e.g. `us-east-1`).
* **Typo in bucket name.** Bucket names are case-sensitive on most providers. Re-paste from the provider's console.
* **Access key without permission to write.** The IAM policy on the access key needs at least `s3:PutObject`, `s3:GetObject`, `s3:ListBucket`, and `s3:DeleteObject` for the bucket.
* **Custom endpoint missing or wrong.** For Cloudflare R2, MinIO, Wasabi, and other S3-compatible providers, the *Custom Endpoint* field is required. Leave it empty for AWS.
Fix the field, click **Test Connection** again before saving.
The job didn't fail, it just had nothing to copy. This almost always means the **Source Path** is wrong or empty.
**Open the View Log modal** (expand the job → click **View Log**). Look for the line:
```
Transferred: 0 B / 0 B, -, 0 B/s, ETA -
```
If you see `Transferred: 0`, the source path is the culprit.
Common causes:
* A typo, like `/var/wwww` instead of `/var/www`.
* The path exists but the user CtrlOps logs in as can't read it (try `ls -la ` from the AI Terminal).
* The folder is empty.
Fix: click **Edit** on the job, correct the **Source Path**, save, and run again.
You set a schedule (Interval or Custom), but nothing has run automatically.
**Check, in order:**
* **Is cron running?** Open the Backup tab and look for the *"Cron service is not running"* alert. Click **Start Cron Service**.
* **Did you save the schedule?** Click **Edit** on the job and confirm the *Schedule Type* is *Interval* or *Custom*, not *Manual*.
* **Is the time correct in the server's timezone?** The job runs on the server's clock, not yours. From the AI Terminal:
```bash
date
timedatectl
```
If the timezone is wrong, fix it: `sudo timedatectl set-timezone Asia/Kolkata` (or whichever zone is correct).
* **Is the cron expression valid?** For *Custom* schedules, a typo in any field breaks the whole job. Stick to digits, ranges, or `*` per field.
Two cases are easy to miss:
**'Permission denied' on the source:** the user doesn't have read access to part of the source. Pick a subdirectory the user owns, or in the AI Terminal:
```bash
sudo chown -R : /path/to/source
```
**Disk full on the source:** rclone needs a tiny amount of working space, and a 100% full disk breaks it. Open the [Infrastructure Details](/docs/modules/infra-details) tab and check the Storage card. If it's red, click **Clean Disk Space** and retry the backup.
Two settings to tune in the *Advanced Options* card of the job form:
* **Bandwidth Limit**, if it's set, raise it or remove it. Empty means full speed.
* **Transfers**, how many files upload in parallel. Default is `4`. Bump to `8` or `16` for many small files; lower if your provider is throttling.
Other common causes:
* **The provider is rate-limiting your account.** S3 throughput is generous but capped. Check the provider's docs.
* **Your server's outbound bandwidth is small.** Run `speedtest-cli` from the AI Terminal to measure. A 10 Mbps server can't push backups at 100 MB/s no matter the settings.
* **Many tiny files.** Backing up `node_modules` is slow because rclone has to handshake on every file. If you don't need them, exclude them from the source path.
A run that's been *RUNNING* for far longer than it should can be killed.
**Expand the job row → Click Kill This Process → Confirm**
The current run stops, the job stays in the table, and you can re-run it. If kill doesn't work because the shell session is gone, look for the *"Backup Shell Disconnected"* banner and click **Reconnect**.
If the same job hangs every time, the issue is usually network: a dead route to the bucket, a misbehaving proxy, or DNS resolving to the wrong endpoint. Test from the AI Terminal:
```bash
curl -v https://your-bucket.s3.your-region.amazonaws.com/
```
You should see a quick HTTP response (any status code is fine, even 403 means the network works).
The View Log shows exactly what was transferred. Expand the job → click **View Log** → look for the summary lines at the bottom:
```
Transferred: 2.345 GiB / 2.345 GiB, 100%, 12.345 MiB/s, ETA 0s
Errors: 0
Checks: 423 / 423, 100%
Transferred: 87 / 87, 100%
Elapsed time: 3m12.4s
```
A clean run shows zero errors and matching counts. If `Errors:` is non-zero, the same number of files failed and the log lists each one earlier.
For peace of mind on critical data, run a small test restore once a month: download a few files from the bucket using your provider's console and confirm they open.
The job definition is gone, but **the backup files at the destination are not touched** when you delete a job. Your data in S3 is safe.
To re-create the job, click **Create Job** again with the same source path, destination, and credentials. The next run will sync against the existing backup files (with *Sync*) or add to them (with *Copy*).
The job is currently running. You can't edit a running job; stop it first:
**Expand the row → Click Kill This Process → Confirm**
After the run stops, **Edit** and **Delete** become available again.
The shell session may have dropped. Look for the *"Backup Shell Disconnected"* alert at the top of the tab and click **Reconnect**. Then click **Refresh** again.
If the alert isn't showing but **Refresh** still shows stale data, switch to another tab and back; the stat cards reload on tab focus.
## Quick checks before you ask for help [#quick-checks-before-you-ask-for-help]
Most "the backup didn't run" reports turn out to be one of these:
| Symptom | Quick check |
| :----------------------------- | :---------------------------------------------- |
| Nothing has run automatically | Cron alert at the top of the tab |
| One job fails, others succeed | Click the failing job and **View Log** |
| Test Connection fails | Region, bucket name, access key permissions |
| Backup ran but bucket is empty | Source path typo; log shows `Transferred: 0` |
| Job hangs forever | **Kill This Process**, then check network to S3 |
## When all else fails: gather details and ask [#when-all-else-fails-gather-details-and-ask]
Before you reach out, collect:
| Info | Where to find it |
| :-------------------------------------- | :-------------------------------------------- |
| Job name and the failing run's log | Expand the row → **View Log** → copy the text |
| Destination type and provider | The job's *Destination Configuration* card |
| Approximate timestamp of the failure | From the row's status |
| Server's date / timezone output | From the AI Terminal: `timedatectl` |
| Any banner currently showing on the tab | Top of the Backup tab |
Then bring it to:
* **Discord community:** [Join Discord](https://discord.gg/JhRCp3hsT9)
* **AI Assistant inside CtrlOps**, paste the log and ask *"why did this fail?"*. Rclone messages are dense but well-structured, the AI is good at translating them.
A failed backup is the same as no backup. Don't ignore the red status indicator, fix the cause and verify with a manual run before going back to your day.
# Connection Issues (/docs/troubleshooting/connection-issues)
You hit **New Connection**, fill in the form, click **Connect SSH**, and instead of landing in your server you see *"Connection Failed"* or *"Taking longer than usual"*. This page walks through the most common causes and exact fixes.
## How to Diagnose SSH Connection Failures [#how-to-diagnose-ssh-connection-failures]
* Why a *"Connection failed"* error appears and how to read every row of the modal.
* Copying the full error report to share with support or the AI Assistant.
* Fixing wrong username, wrong key, or wrong IP.
* Firewall and security group fixes for AWS, GCP, Azure, DigitalOcean.
* What to do when CtrlOps says *"Windows Server Not Supported"*.
* When to use the SSH Setup Wizard.
## First, find the exact error [#first-find-the-exact-error]
When a connection fails, CtrlOps opens a *Connection failed* modal that breaks the failure down rather than dumping a raw SSH string at you. Read it top to bottom:
| Row | What it tells you |
| :------------ | :----------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| **Server** | The saved connection name, so you know which server this is about |
| **Address** | The `user@ip:port` CtrlOps actually dialled. Check this first, a typo here explains a surprising share of failures |
| **Failed at** | The stage that broke, e.g. *Dialling (TCP + SSH handshake)*. This alone splits network problems from auth problems |
| **Took** | How long it tried before giving up. A full 45 seconds points at a firewall silently dropping packets; a failure in under a second points at auth or a refused port |
| **Error** | A `category / code` pair such as `network / PreflightTimeout` |
Under that, **What happened** is a timestamped timeline of the attempt, marking which lines came from the app and which from SSH, so you can see exactly where it stalled. Three buttons sit at the bottom: **Close**, **Try again**, and **Copy report**.
The error wording still matters most. Scan the table below to find your case:
| What the error says | Most likely cause |
| :------------------------------------------ | :-------------------------------------------------------- |
| *"Connection timed out"* | Firewall or security group blocking port 22 |
| *"Connection refused"* | SSH service isn't running on the server |
| *"Permission denied (publickey, password)"* | Wrong username, wrong password, or wrong key |
| *"Host key verification failed"* | Server's identity changed since you last connected |
| *"Network unreachable"* | DNS or routing problem |
| *"Taking longer than usual"* | Slow server, slow network, or wrong IP |
| *"Windows Server Not Supported"* | The server is running Windows; use a Linux server instead |
## Copy the full error report [#copy-the-full-error-report]
**Click Copy report** (bottom right of the *Connection failed* modal)
This puts the whole failure on your clipboard as plain text: the server name, the address dialled, the stage it failed at, how long it took, the error category and code, and the complete **What happened** timeline. Paste it straight into Discord, an email, or the AI Assistant instead of retyping an error message from memory or a screenshot.
The report is safe to share. It carries the address CtrlOps dialled and the trace of what happened, never your password or the contents of your private key.
## Common problems and fixes [#common-problems-and-fixes]
The whole failure, as plain text: the server name, the `user@ip:port` CtrlOps dialled, the stage it failed at, how long it tried, the error category and code, and the full *What happened* timeline.
Paste it into Discord, an email, or the CtrlOps AI Assistant instead of retyping the error or attaching a screenshot. It contains the address and the failure trace only, never your password or private key.
This is the most common error. CtrlOps reached the server, but the username, password, or key was rejected.
**Check the username first.** Different distros use different defaults:
| Server type | Default username |
| :------------------------- | :----------------- |
| Ubuntu (AWS, DigitalOcean) | `ubuntu` |
| Amazon Linux (AWS) | `ec2-user` |
| Debian | `debian` |
| CentOS / Rocky / AlmaLinux | `centos` or `root` |
| Most VPS providers | `root` |
**If you're using a `.pem` key:** make sure permissions on your local machine are tight. From your local terminal:
```bash
chmod 600 ~/path/to/yourkey.pem
```
**If you're using a password:** confirm password authentication is enabled on the server. SSH into it another way and check `/etc/ssh/sshd_config` for `PasswordAuthentication yes`.
**Click Edit on the connection card → Fix the username or re-pick the key → Click Connect again.**
The server isn't responding on port 22 within 30 seconds. The cause is almost always a firewall.
**Check your cloud provider's security group:**
| Provider | Where to look |
| :----------- | :------------------------------------------------------------------------ |
| AWS | EC2 Console → Security Groups → Inbound rules → allow TCP 22 from your IP |
| DigitalOcean | Networking → Cloud Firewalls → Inbound Rules → allow SSH |
| GCP | VPC Network → Firewall → allow `tcp:22` |
| Azure | Network Security Group → Inbound security rules → allow SSH |
**Check the server-side firewall** by SSHing in another way (cloud console, mobile hotspot, or the provider's web shell):
```bash
sudo ufw status
sudo ufw allow 22/tcp
sudo ufw reload
```
**If your office network blocks port 22**, try a mobile hotspot or VPN to confirm. Some corporate networks block outbound SSH.
The server is reachable but the SSH service isn't accepting connections. This means SSH is stopped, crashed, or listening on a different port.
**Get into the server through your cloud provider's web console** (the "in-browser shell" most providers offer), then check SSH:
```bash
sudo systemctl status ssh
sudo systemctl start ssh
sudo systemctl enable ssh
```
If SSH is running on a non-standard port (some hardened servers use `2222` or `8022`), CtrlOps doesn't have a port field today, so port 22 is assumed. Either move SSH back to 22, or open a port-forward via the AI Terminal once you're in.
The server's identity has changed since the last time your computer talked to it. This is a security warning, not necessarily an attack.
**Legitimate reasons this happens:**
* The server was rebuilt or reinstalled.
* The IP got reassigned to a different machine.
* The OS was reinstalled on the same disk.
**Fix on your local machine** (open Terminal on Mac/Linux or PowerShell on Windows):
```bash
ssh-keygen -R
```
Then try **Connect** again in CtrlOps.
Only clear the host key if you actually expected the server to change. If the IP wasn't supposed to change, investigate before clearing.
Your computer can't find a route to the server.
**If you're using a hostname** (like `api.yoursite.com`), check DNS:
```bash
dig api.yoursite.com +short
```
If the IP is wrong or empty, fix the A record at your DNS provider and wait 5 to 30 minutes for propagation. No terminal handy? Our free [DNS record lookup](/tools/dns-record-lookup) runs the same check in the browser.
**If a recent DNS change isn't sticking**, try with the raw IP address as a workaround.
CtrlOps only works with Linux servers. The supported list:
* Ubuntu, Debian
* CentOS, RHEL, Rocky, AlmaLinux, Fedora
* Amazon Linux
* Other mainstream Linux distributions
If you pointed at a Windows server by mistake, double-check the IP. If you genuinely need to manage Windows, that's outside CtrlOps' scope today.
You probably saved the connection without checking **Remember password**. Two options:
* **For one server:** Open the password modal next time and tick **Remember password**.
* **Switch to key-based auth:** Use the [SSH Setup Wizard](/docs/modules/server-management) on the Home page to generate a key, copy the public part to `~/.ssh/authorized_keys` on the server, then re-add the connection on the *.pem Key-based Connection* tab.
Two common causes:
* **The server's IP changed.** Cloud VMs with dynamic IPs lose their address on stop/start. Confirm in your provider's console, then click **Edit** on the connection card to update the IP.
* **The key file moved or got new permissions.** Confirm the path still exists, and re-run `chmod 600 yourkey.pem`.
The user account on the server may have a non-interactive shell (like `/usr/sbin/nologin`), or the home directory is missing.
Get in through the cloud console and check:
```bash
grep /etc/passwd
```
The shell at the end of the line should be `/bin/bash` or `/bin/sh`. If it's `/bin/false` or `/usr/sbin/nologin`, fix it:
```bash
sudo usermod -s /bin/bash
```
Your local SSH agent is offering too many keys before getting to the right one. Two fixes:
**Tell SSH to only use one specific key.** Open `~/.ssh/config` on your computer and add:
```
Host my-server
HostName 1.2.3.4
User ubuntu
IdentityFile ~/.ssh/specific_key.pem
IdentitiesOnly yes
```
Or, in CtrlOps, switch to the *.pem Key-based Connection* tab and pick the exact key file. CtrlOps then uses only that key.
## When all else fails: gather details and ask [#when-all-else-fails-gather-details-and-ask]
Before you reach out for help, collect:
| Info | Where to find it |
| :---------------------------------------------------- | :------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------ |
| Everything about the failure itself | Click **Copy report** in the *Connection failed* modal. It captures the server, the address dialled, the stage it failed at, the timing, the error code, and the full timeline in one paste |
| Auth method | Password, `.pem` key, or SSH Agent |
| Cloud provider | AWS, GCP, DigitalOcean, etc. |
| Output of `ssh -vvv user@ip` from your local terminal | Run on your local machine to capture verbose SSH logs |
Then bring it to:
* **Discord community:** [Join Discord](https://discord.gg/JhRCp3hsT9)
* **AI Assistant inside CtrlOps**, paste the copied report and ask for a translation. It's surprisingly good at decoding SSH error messages.
Always keep a fallback way into your server, your cloud provider's web console, a second user, or a different SSH key on a different machine. The day your only SSH key stops working is not the day you want to be locked out.
# AI SSH Terminal (/docs/modules/ai-terminal)
The AI Terminal is the same SSH terminal you'd use anywhere, with two side panels you can pop open: an **AI Assistant** that turns plain English into commands and explains output, and a **Scripts** library where you keep the commands you run all the time. Type a command yourself, ask the AI to figure one out, or run a saved script in one click. For an overview of the [AI-powered terminal](/features/ai-terminal) before you set it up, see the feature page.
## What is an AI terminal? [#what-is-an-ai-terminal]
An AI terminal is a command-line interface enhanced with artificial intelligence. Instead of memorizing Linux commands, you describe what you need in plain English - the AI generates the correct command, explains what it does, and executes it with your approval.
Traditional SSH terminals require you to know exact syntax. An AI terminal assistant bridges that gap: it understands context, reads server output, chains multiple commands, and provides human-readable summaries of results.
CtrlOps takes this further by combining a full SSH session with an AI assistant panel side-by-side. You can type commands manually when you know them, or ask the AI when you don't - all in one window, connected to your live Linux server. No server-side agent required.
## What you can do with the AI SSH terminal [#what-you-can-do-with-the-ai-ssh-terminal]
* Type any Linux command and see the output, just like a regular SSH terminal.
* Get command suggestions as you type, with a one-line description of what each one does.
* Ask the AI plain-English questions ("what services are running?", "why is the disk full?").
* Have the AI run commands for you, with your approval before each one.
* Connect a ChatGPT or OpenRouter account in one click, or bring your own OpenAI, Anthropic, or Gemini key, and switch between them mid-conversation.
* Save commonly-used commands as Scripts and re-run them with one click.
* Let the AI search the web for current docs, error messages, and package versions.
* Use AI as your Linux terminal assistant - debug errors, optimize configs, and manage services without memorizing commands.
* Works with any Linux server you connect via SSH - Ubuntu, Debian, CentOS, AlmaLinux, and more.
## Open the AI SSH terminal [#open-the-ai-ssh-terminal]
**Open app → Click your server → Click the AI Terminal tab**
You'll land in a dark terminal taking up most of the screen. The header has a green title *"Terminal"* on the left, with two toggle buttons on the right: **AI Assistant** (robot icon) and **Scripts** (file icon). Both panels are collapsed by default.
{/* screenshot: AI Terminal landing view with header buttons */}
## Use the terminal directly [#use-the-terminal-directly]
Click anywhere in the dark area and start typing. It works exactly like an SSH session:
* Hit Enter to run a command.
* Tab to autocomplete file names.
* Up arrow to repeat the previous command.
* Scroll wheel to look at history (5,000 line buffer).
* Ctrl+C / Cmd+C copies selected text.
* Ctrl+F / Cmd+F opens a search overlay.
* Right-click for **Copy**, **Paste**, **Clear Buffer**, **Reset Session**.
If your connection drops, you'll see a *"Disconnected"* alert in the bottom-left with a **Reconnect** button.
### Command suggestions as you type [#command-suggestions-as-you-type]
Start typing and CtrlOps suggests the rest. A small dropdown appears above the cursor with matching commands, subcommands, and flags - each with a one-line description of what it does. Type `pm2 l` and you'll see `list`, `logs`, `logrotate`, `login`, and `link` side by side with what each one actually does, so you no longer have to remember the full syntax for the commands you only run once a month.
| Key | What it does |
| :------------------- | :----------------------------------- |
| **↑ / ↓** | Move through the suggestions |
| **Tab** or **Enter** | Accept the highlighted suggestion |
| **Esc** | Dismiss the dropdown and keep typing |
The suggestions narrow as you type, so you can keep going and ignore them entirely if you already know the command. This is plain autocomplete and it costs you nothing - it doesn't call the AI, doesn't need an API key, and works whether or not the AI Assistant panel is open.
{/* screenshot: terminal with the command suggestion dropdown open on `pm2 l` */}
## Add an AI key (one-time setup) [#add-an-ai-key-one-time-setup]
The AI Assistant needs one AI provider connected before it can answer anything. There are three ways to do that, and **two of them need no API key at all**. All three start on the same screen: in the left sidebar, under **TOOLS**, click **AI Keys**.
| Your situation | Use this | What you need |
| :----------------------------------------------------------- | :----------------------------------------------------------- | :--------------------------------------------------------------- |
| You already have a ChatGPT account | [**Sign in with ChatGPT**](#sign-in-with-chatgpt) | Your ChatGPT login. No API key. |
| You don't pay for any AI service | [**Connect with OpenRouter**](#connect-with-openrouter-free) | A free OpenRouter account. CtrlOps picks a free model for you. |
| You want a specific provider or model, or already hold a key | [**Add credential**](#add-your-own-api-key) | An API key from OpenAI, Anthropic, Google, or a custom endpoint. |
The top of the AI Keys page is **Quick connect**, with the ChatGPT and OpenRouter cards side by side. Below it is **API credentials**, where your own keys live.
### Sign in with ChatGPT [#sign-in-with-chatgpt]
Pick this if you already have a ChatGPT account. CtrlOps signs in through OpenAI, so there is no API key to generate, copy, or paste.
**Open the AI Keys page**
In the left sidebar, under **TOOLS**, click **AI Keys**.
**Click Sign in with ChatGPT**
It's the button on the first **Quick connect** card, labelled *ChatGPT account*.
**Approve the sign-in in your browser**
CtrlOps opens your browser. Sign in to your OpenAI account, approve access, and the browser hands you back to the app.
**Check the card**
The ChatGPT card now shows your connected account and a sign-out icon, and the model is selectable from the AI Assistant dropdown straight away.
This path runs on the ChatGPT plan you already pay for, so there's no per-token API bill and no key to store or rotate. To disconnect, click the sign-out icon on the ChatGPT card.
### Connect with OpenRouter (free) [#connect-with-openrouter-free]
Pick this if you don't pay for ChatGPT. [OpenRouter](https://openrouter.ai) is one account in front of hundreds of models, and it serves a set of them free. You do **not** need a paid OpenRouter key: when you connect, CtrlOps picks the best free model available and selects it for you.
**Open the AI Keys page**
In the left sidebar, under **TOOLS**, click **AI Keys**.
**Click Connect with OpenRouter**
It's the button on the second **Quick connect** card, labelled *OpenRouter account*.
**Approve the connection in your browser**
Sign in to OpenRouter, or create an account if you don't have one, then authorise CtrlOps. Creating the account is free and doesn't need a card.
**Let CtrlOps pick the model**
Back in the app, the OpenRouter card shows a **MODEL** dropdown already set to a free model. Leave it as it is, or open the dropdown to switch to a different one at any time - there's nothing to reconnect.
{/* screenshot: connected OpenRouter card with the MODEL dropdown showing the auto-selected free model */}
Free models are served by third-party providers who **may log your prompts and responses**, and they're rate-limited. Don't paste secrets, credentials, or confidential server output into a chat backed by a free model.
Free models are ideal for learning your way around the AI Terminal. For real server work - running commands, debugging incidents, touching infrastructure - a high-capability model like Claude Opus, Gemini 2.5 Pro, or GPT-5 earns its cost, because smaller models are more likely to suggest commands that misfire.
### Add your own API key [#add-your-own-api-key]
Pick this when you already hold a key from a provider, or you need a specific model that the two Quick connect options don't give you. It works with OpenAI, Anthropic, Google, and any OpenAI-compatible endpoint.
**Open the AI Keys page**
In the left sidebar, under **TOOLS**, click **AI Keys**.
**Click Add credential**
The button sits at the top right of the **API credentials** section. If you have no credentials yet, the same button is in the empty state, under *Connect your first AI provider*.
**Fill in the Add AI credential form**
| Field | What to enter |
| :----------------------------------- | :-------------------------------------------------------------------------------------------------------------- |
| **Name (identifier)** | A label for you, like `Prod LLM` or `Personal Key`. Up to 50 characters. |
| **Provider** | Defaults to *OpenAI*. Switch it to Anthropic, Google, or a custom OpenAI-compatible endpoint. |
| **API key** | Paste the key from your provider's console. The eye icon reveals it so you can check the paste. |
| **Model** | Reads *Enter credentials to load models* until the key is accepted, then fills with your provider's model list. |
| **Base URL** (custom endpoints only) | The endpoint URL including the version path, e.g. `https://api.your-provider.com/v1` - not just the host. |
**Click Test connection**
CtrlOps makes a tiny test call. You'll see a success toast or a specific error.
**Click Save credential**
The key is stored locally on your computer and encrypted at rest, never on a CtrlOps server. Saving runs the test again automatically; the credential saves either way, marked as *error* status if the test failed.
You can add as many credentials as you want. The AI panel lets you switch between them, and between the Quick connect providers, mid-conversation.
## Open the AI Assistant panel [#open-the-ai-assistant-panel]
**In the AI Terminal header → Click AI Assistant (robot icon)**
A 450px panel slides in from the right with the chat history (empty at first), an input box at the bottom, and a green circular send button.
If you haven't connected an AI provider yet, you'll see *"AI Not Configured"* with a button that takes you to the AI Keys page.
{/* screenshot: AI Terminal with AI Assistant panel open and a sample conversation */}
## Ask the AI a question [#ask-the-ai-a-question]
The AI terminal assistant understands natural language. Describe your problem or goal, and it generates the right Linux commands for your server.
### Pick which key to use (optional) [#pick-which-key-to-use-optional]
At the bottom-left of the AI panel, a dropdown shows the currently selected key. Click it to switch to a different provider or model. The next message you send uses the new key.
### Type your question [#type-your-question]
Use plain English in the input box at the bottom. Examples:
* *"What services are running on this server?"*
* *"Why is `/var/log` so big?"*
* *"Set up a daily cron job that runs my-script.sh at 2am"*
### Send it [#send-it]
**Press Enter, or click the green send arrow**
(Use *Shift+Enter* for a newline if you want a multi-line prompt.)
### Approve any commands the AI wants to run [#approve-any-commands-the-ai-wants-to-run]
If the AI suggests a command, it appears as a card with the command in a code block, an explanation, and two buttons:
| Button | What it does |
| :------------------------ | :--------------------------------------------------------------------------- |
| **Run** (green play icon) | Runs the command in the terminal. Output is captured and sent back to the AI |
| **Cancel** (red X) | Rejects the command. The AI may suggest something else |
The AI may chain several commands in a row, asking for approval each time, until it has enough information to give you an answer.
Always read the command before clicking **Run**. The AI is helpful but it's not infallible. If a suggested command would touch important files or stop a running service, double-check first.
## Tweak how the AI behaves [#tweak-how-the-ai-behaves]
The AI panel has a few controls in the footer.
| Control | What it does |
| :----------------------------------------------- | :------------------------------------------------------------------------------------------------------------------------------------------------ |
| **Max AI reasoning steps** (number field, 1-200) | Caps how many back-and-forth steps the AI takes per question. Default is fine for most. |
| **Auto-Run** (switch) | Skip the manual approval step and run AI commands automatically. Convenient but riskier. |
| **Web Search** (pill + toggle) | Let the AI look things up online for current docs, error messages, package versions, etc. See [Web search](/docs/modules/ai-terminal/web-search). |
| **New** (header button) | Start a fresh conversation, useful when context gets stale |
| **Export** (header button) | Save the chat as a file for sharing or notes |
| **Stop** (red X, only while running) | Interrupt the AI mid-thought |
| **Close** (X) | Collapse the panel |
Leave **Auto-Run** off until you've used the AI for a while and trust the kind of commands it suggests. With Auto-Run on, every command runs immediately with no approval step.
## Go deeper [#go-deeper]
## Tips [#tips]
When something is broken, paste the exact error into the AI Assistant and ask *"why?"*. The AI is excellent at decoding cryptic error messages.
When the AI keeps suggesting wrong commands, click **New** in the panel header to start a fresh conversation. Long contexts can drift.
Keep two AI keys configured: one fast and cheap (Haiku, GPT-4o-mini, Gemini Flash) for quick lookups, one heavy (Opus, GPT-4o, Gemini Pro) for hard debugging. Switch between them from the dropdown.
The AI SSH terminal works best when you give it context. Instead of "fix nginx", try "nginx is returning 502 after I updated the config - check the error log and suggest a fix." More context = better commands.
## Why use an AI-powered Linux terminal? [#why-use-an-ai-powered-linux-terminal]
Managing Linux servers through a traditional SSH terminal means memorizing hundreds of commands, parsing cryptic error messages, and spending time searching documentation. An AI-powered Linux terminal assistant handles this for you:
* **Diagnose server issues in seconds:** paste an error, get the fix.
* **No command memorization:** describe what you need, the AI writes the command.
* **Approve before execution:** every AI-generated command requires your approval (unless you enable Auto-Run).
* **Switch AI providers freely:** sign in with ChatGPT or connect OpenRouter in one click, or use OpenAI, Anthropic Claude, Google Gemini, or any OpenAI-compatible provider with your own API key, stored locally with AES-256 encryption.
* **Secure SSH connections:** connect to your Linux server via SSH with no server-side agent needed. Manage your credentials and keys from the [SSH Key Management](/docs/modules/ssh-management) module.
* **Go beyond debugging:** once you've diagnosed and fixed an issue, deploy updates with [one-click deployment](/docs/modules/deployment) without leaving CtrlOps.
Whether you're a solo developer managing multiple client servers or a startup CTO without a dedicated DevOps team, the AI SSH terminal turns server management from a specialized skill into a conversation. It is also one of the key differentiators that makes CtrlOps the [best Termius alternative for AI-powered server management](/blog/termius-alternatives).
## Troubleshooting [#troubleshooting]
No AI provider is connected yet. Open **AI Keys** from the left sidebar, under **TOOLS**. Under **Quick connect**, click **Sign in with ChatGPT** if you have a ChatGPT account, or **Connect with OpenRouter** to use a free model with no API key at all. To bring your own provider key instead, click **Add credential** in the **API credentials** section. See "Add an AI key" above.
The API key is wrong, expired, or doesn't have permission. Open the AI Keys page, click **Edit** on the credential, paste a fresh key, and click **Test connection** before saving.
The provider's API isn't returning a model list. Most often this means the API key is wrong, or your provider needs a custom Base URL. Double-check both, then click **Test connection** again.
The terminal session may have disconnected. Look for a *"Disconnected"* alert at the bottom-left, and click **Reconnect**. Then ask the AI to retry.
The session may be hung. Right-click and choose **Reset Session**, then **Reconnect** if needed. Your scrollback is preserved.
The conversation hit the *Max AI reasoning steps* cap before finishing. Increase the cap in the panel footer (default 200 is plenty for most). For very complex tasks, break them into smaller questions instead.
Switch to a cheaper model from the dropdown for everyday questions, and reserve the heavy models for hard problems. **Auto-Run** can also rack up costs by encouraging long chains of commands, leave it off when you're being mindful of usage.
# MCP Servers (/docs/modules/ai-terminal/mcps)
MCP stands for **Model Context Protocol**. In plain terms: it lets the AI Assistant talk to outside tools - like a documentation search engine, your GitHub account, or a folder on your computer - so it can give you answers grounded in your actual context instead of relying on training data alone.
When you connect an MCP server, its tools become available to the AI automatically. Ask *"search my repo for auth-related code"* and the AI will reach through the GitHub MCP server, not guess.
The MCP badge in the AI Terminal toolbar shows how many tools are currently active (e.g. *"5 tools"*). Click it to open the MCP Manager.
{/* screenshot: AI Terminal header showing MCP badge with active tool count */}
## What comes built-in [#what-comes-built-in]
CtrlOps ships with three default servers. They appear in the MCP Manager automatically, but they start turned off until you choose to enable them.
| Server | What it does | What you need |
| :------------- | :------------------------------------------------------------------------------------------------- | :----------------------------------------------------------------------------------------------------------------------------------------------------------- |
| **Context7** | Looks up up-to-date documentation for libraries, frameworks, and APIs. Great for coding questions. | A Context7 API Key (starts with `ctx7sk-…`). Get one free at [context7.com](https://context7.com). |
| **GitHub** | Repository operations, issue and pull request management, code search. | A GitHub Personal Access Token (starts with `ghp_…` or `github_pat_…`). Create one in [GitHub settings](https://github.com/settings/personal-access-tokens). |
| **Filesystem** | Read and write files inside one folder you choose on your local computer. | Node.js installed (gives you `npx`). Pick a folder when you turn it on. |
If you delete a default server, it won't come back. You can always add it again manually.
## Connect your first MCP server [#connect-your-first-mcp-server]
The fastest path is enabling one of the defaults. Here's Context7 as an example - the steps are the same shape for the others.
### Open the MCP Manager [#open-the-mcp-manager]
**In the AI Terminal → Click the MCP badge in the toolbar**
A right-side panel slides out listing all configured servers.
### Turn the server on [#turn-the-server-on]
Find the **Context7** card and flip its toggle switch to **ON**.
Because the server has no API key yet, a **Secrets** modal pops up automatically asking for your credentials.
### Enter the API key [#enter-the-api-key]
Paste your Context7 API Key (starts with `ctx7sk-…`) into the input field and click **Save & Connect**.
CtrlOps validates the format immediately. If the key looks wrong, you'll see a message telling you what format is expected.
### Check the status [#check-the-status]
The card updates: a green dot means connected, and you'll see a tool count like *"4 tools"*. The AI can now use Context7 whenever it thinks docs would help.
You can add as many servers as you want, but the AI can only use **20 tools at a time** across all connected servers. If you hit the limit, CtrlOps auto-disables excess tools with a *"LIMIT REACHED"* badge. Click a tool to manually re-enable it after freeing up slots elsewhere.
## How the AI uses MCP tools [#how-the-ai-uses-mcp-tools]
You don't tell the AI to use MCP. You just ask your question naturally, and the AI decides whether a connected server can help.
### What you see [#what-you-see]
1. **You ask:** *"What changed in the auth middleware since last week?"*
2. **The AI emits an MCP request** - you'll see a small inline panel appear in the chat showing which server is being used and what it's doing.
3. **The Subagent runs** - CtrlOps spins up an isolated AI loop (called a Subagent) that figures out the exact tool names and arguments, executes them, and collects results.
4. **Result appears** - the final answer lands back in your chat, citing what it found.
The Subagent panel shows each "turn" live: thinking step → tool call → result. It caps at 10 turns. If something goes wrong, you see the error right there instead of a silent failure.
The main chat only sees the final summary. The full tool-call history stays inside the Subagent panel, keeping your conversation clean.
## Manage servers and tools [#manage-servers-and-tools]
### The MCP Manager drawer [#the-mcp-manager-drawer]
Click the MCP badge anytime to reopen the drawer. Each server card shows:
* **Status dot** - green (connected), amber (connecting), red (error)
* **Tool count** - total tools vs. active tools (e.g. *"8 tools (6 active)")*
* **Toggle** - turn the whole server on or off
* **Test** - ping the server and refresh the tool list
* **Edit** - change name, description, URL, headers, or command
* **Delete** - remove permanently (asks for confirmation)
If a server errors, its toggle turns into a **RETRY** button in red. Click it to attempt reconnection.
### Enable or disable individual tools [#enable-or-disable-individual-tools]
Click the **"X tools (Y active)"** line on a connected card to expand the tool list. Each tool has its own switch. Disabled tools won't be offered to the AI, which is useful when a server has many tools and you only need a few.
### Add a custom server [#add-a-custom-server]
Beyond the defaults, you can connect any MCP-compatible server.
Best when you know the server details and want guided fields.
**In the MCP Manager → Click Add New Server → Manual Entry tab**
Fill in:
| Field | What to enter |
| :--------------------- | :------------------------------------------------------------------------------------------------------------- |
| **Server Name** | Unique identifier. Letters, numbers, hyphens, underscores only. No spaces. 2 - 50 characters. |
| **Description** | Required. Tell the AI what this server does (10 - 200 characters). The AI uses this to decide when to call it. |
| **Connection Type** | **HTTP** (remote API), **SSE** (legacy streaming), or **Stdio** (local process like `npx` or `python`). |
| **URL** (HTTP/SSE) | Must start with `http://` or `https://` and have a valid domain. |
| **Command** (Stdio) | The executable to run, e.g. `npx`, `node`, `python`. Must be a known executable or absolute path. |
| **Arguments** (Stdio) | Comma-separated arguments passed to the command. |
| **Headers / Env Vars** | Optional key-value pairs for authentication or configuration. |
Live validation runs as you type. Whitespace-only input is rejected everywhere, and URLs must look like real URLs. If you select Stdio, the command is checked against a whitelist of safe executables.
Click **Save & Connect** when ready. If credentials are missing, the Secrets modal will prompt you before the connection attempt.
Best when you have a standard `mcpServers` config block from the server's documentation.
**In the MCP Manager → Click Add New Server → Paste JSON Config tab**
Paste your JSON into the editor. You get:
* **Monaco Editor** - syntax highlighting, real-time error squiggles, fold/unfold, auto-format (`Alt+Shift+F`)
* **Visual Tree View** - a collapsible structure of your JSON on the right
* **Real-time validation** - checks for missing keys, invalid names, undeclared `${input:...}` placeholders, and malformed JSON with exact line numbers
Example:
```json
{
"mcpServers": {
"my-docs": {
"type": "http",
"url": "https://docs-api.example.com/mcp",
"description": "Internal company documentation",
"headers": {
"Authorization": "Bearer ${input:api_key}"
}
}
},
"inputs": [
{ "id": "api_key", "description": "API Key", "password": true }
]
}
```
If you use `${input:id}` placeholders, a modal will ask for the values before saving. Click **Save & Connect** when the editor shows no errors.
## Security [#security]
**Keys stay on your machine.** API keys, tokens, and secrets are stored in browser localStorage alongside your other AI credentials. They are never sent to the AI model or to any CtrlOps server. Password fields are masked in the UI.
**Validation guards in place:**
* URLs must start with `http://` or `https://` and have a valid domain with a TLD
* HTTP URLs that aren't localhost trigger a security warning
* Stdio commands are checked against a whitelist of known executables (`npx`, `node`, `python`, `docker`, `uvx`, etc.)
* Secret formats are enforced by regex - e.g., Context7 keys must start with `ctx7sk-`, GitHub tokens with `ghp_` or `github_pat_`
* Whitespace-only submissions are rejected everywhere
* All connections time out after 120 seconds
* Server management is disabled while the AI is running to prevent conflicts
## Troubleshooting [#troubleshooting]
The connection failed. Common causes: wrong API key, the server is down, or your network can't reach the URL. Click the card's **Test** button to see the exact error. Double-check your credentials and try again.
You've hit the global cap of 20 active tools across all MCP servers. Disable tools or turn off entire servers you aren't using. The badge disappears automatically when slots free up, and you can manually re-enable the tools you need.
The AI decides when a tool is relevant based on the server's description and your question. Try phrasing your question around the server's domain - e.g., for GitHub, ask *"search my repo for…"* or for Context7, ask *"look up the docs for…"*. Also make sure the server is toggled ON and has active tools.
The Filesystem server runs via `npx`, which comes with Node.js. Make sure Node.js is installed on your computer. Open a terminal and run `npx --version`. If it fails, install Node.js from [nodejs.org](https://nodejs.org).
Extra whitespace on paste is a common culprit. Re-open the Secrets modal, delete the key, re-paste it carefully, and save again. If it still fails, click **Test** on the card to see the raw server response.
The Subagent tried to use a tool but something went wrong (bad arguments, permission denied, server hiccup). The main chat still proceeds - usually the AI will tell you it couldn't fetch something and suggest next steps. Expand the Subagent panel to see the exact error and which turn it failed on.
## Go deeper [#go-deeper]
## Tips [#tips]
Start with one MCP server and get comfortable before stacking more. Context7 is the easiest - just a free API key and you're querying live docs in minutes.
The AI uses the server's **description** to decide when to call it. Write descriptions that clearly say what the server can do. "GitHub repo search and issue management" is better than "My GitHub tools."
Don't paste secrets into the AI chat itself. Keys belong in the MCP Secrets modal, not in conversation prompts. Even though CtrlOps is local-only, it's good hygiene.
# Script Directory (/docs/modules/ai-terminal/scripts)
Scripts are your personal library of shell commands. Save the things you run all the time (restart nginx, tail an error log, check disk usage) and run them with one click on any server. Scripts live on your computer, not the server, so they follow you around to every connection. For an overview of the [script directory](/features/script-directory) before you build your library, see the feature page.
## Open the Scripts panel [#open-the-scripts-panel]
**In the AI Terminal header → Click Scripts (file icon)**
A panel slides in showing your saved scripts with a search box at the top. Scripts are stored on your computer and available across every server you connect to.
If you have none yet, you'll see *"No scripts yet"* with a *"Create your first script"* link.
## Create a script [#create-a-script]
### Open the new-script form [#open-the-new-script-form]
**In the Scripts panel header → Click + (New script icon)**
The script editor opens.
### Fill in the basics [#fill-in-the-basics]
| Field | What to enter |
| :-------------- | :---------------------------------------------------------- |
| **Name** | A short name like `restart-nginx` or `tail-error-logs` |
| **Description** | Optional. A line about what the script does. |
| **Tags** | Optional. Comma-separated, helps you filter the list later. |
| **Color** | Pick a card colour for visual grouping. |
### Write the script [#write-the-script]
In the content area, write your commands. Use `{{variable_name}}` placeholders for anything you want to be prompted for at run time:
```bash
sudo tail -f /var/log/{{service}}/error.log
```
### Save [#save]
The script appears in the Scripts panel list immediately. It's available across every server, so you only have to write it once.
## Run a saved script [#run-a-saved-script]
### Find the script [#find-the-script]
In the Scripts panel, scroll or use the search box to find it.
### Click the Run icon (play) [#click-the-run-icon-play]
If the script has no variables, it runs immediately in the terminal. You'll see a success toast when it finishes.
### Fill in variables (if any) [#fill-in-variables-if-any]
If the script uses `{{variable}}` placeholders, a **Run** modal opens with a text input for each one. As you type, the **WILL RUN** panel underneath shows the exact command that's about to execute, with your values substituted in - read it before you commit. Fill the inputs in and click **Run in terminal**.
### See the output [#see-the-output]
The command runs in the terminal area. Output appears live. A success toast confirms `" completed"`. If it fails, the toast says *"Script failed, check terminal output"*.
## Tips [#tips]
Save your three most-used troubleshooting commands as Scripts (`tail -f` your app log, `pm2 restart`, `df -h`). One click beats typing them out every time. For PM2 specifically, the [PM2 Process Manager](/docs/modules/pm2-process-manager) tab already gives you restart, reload, and stop as buttons, so save Scripts for the things it does not cover.
Use tags to group scripts by domain (`nginx`, `db`, `monitoring`) and filter the list with the search box when you have a lot of them.
Use `{{variable}}` placeholders liberally. A single `tail-log` script with a `{{service}}` variable beats writing one script per service.
## Troubleshooting [#troubleshooting]
Scripts run on whichever server you currently have open. Check the connection name in the header. To run a script on a different server, switch to that server's tab first.
Look for a *"Script failed, check terminal output"* toast at the top of the screen. The actual error is printed in the terminal area, scroll up if it's already gone past.
Scripts are stored locally in the app's data directory. Reinstalling without exporting first will wipe them. There's no cloud sync today, so back them up by copying the file from the app's data folder.
# Web Search (/docs/modules/ai-terminal/web-search)
The AI Assistant can search the web mid-conversation when you enable it, useful for looking up current documentation, recent CVEs, error messages, or package versions the model may not have in its training data.
The web search control sits at the bottom-right of the AI panel as a pill with a globe icon and a small toggle switch.
## What the pill tells you [#what-the-pill-tells-you]
| Pill state | Meaning |
| :-------------------------------------- | :---------------------------------------------------------------------------------- |
| **Web off** (gray) | Web search is disabled. The AI works from its own knowledge only. |
| **Setup needed** (amber) | Web search is on, but the selected provider needs an API key you haven't added yet. |
| **tavily / brave / duckduckgo** (green) | Web search is on and ready. |
## Enable web search [#enable-web-search]
### Open the settings popover [#open-the-settings-popover]
**Click the pill label** (the globe + provider name), not the toggle switch.
A small popover slides out with provider options and an API key field.
### Pick a provider [#pick-a-provider]
| Provider | Notes |
| :----------------------------------- | :---------------------------------------------------------------------------------------------------------------------------------------------- |
| **Tavily** *(recommended)* | Purpose-built for AI agents, fast and reliable. Needs a free Tavily API key (`tvly-…`). |
| **Brave** | Independent index, good privacy posture. Needs a Brave Search API key (`BSA…`). |
| **DuckDuckGo** | Works with no API key, but is frequently rate-limited or bot-blocked. Use for casual lookups; switch to Tavily or Brave for anything important. |
Each provider keeps its own key: switching tabs in the popover won't wipe out the other provider's key.
### Paste the API key (if the provider needs one) [#paste-the-api-key-if-the-provider-needs-one]
The key is stored locally with your other AI credentials and is never sent to the model, only to the search provider when a search is performed.
### Close the popover and flip the toggle [#close-the-popover-and-flip-the-toggle]
Click outside the popover (or hit Escape) to close it, then click the small switch on the pill to turn web search **on**. The pill turns green when ready.
Once enabled, the AI decides on its own when a question is worth a web lookup, you don't have to ask it to search. Search results appear inline in the chat as small favicon "chips" with the source URL, so you can click through to the original page.
Tavily's free tier is generous (1,000 searches/month at the time of writing) and is by far the most reliable of the three for AI workflows. If you only set up one, set up Tavily.
## When to leave web search on [#when-to-leave-web-search-on]
* Debugging a fresh stack-trace or error message you've never seen before.
* Working with a library you've recently upgraded: the AI's training data may be a version behind.
* Looking up CVEs, package vulnerabilities, or release notes.
* Asking about recent CLI flags, config options, or breaking changes.
## When to leave it off [#when-to-leave-it-off]
* Pure-shell tasks (`grep`, `awk`, `find`, file moves), the model knows these cold.
* Anything where you don't want the AI fanning out to external services.
* Tight loops where the extra search latency adds up.
## Troubleshooting [#troubleshooting]
The selected provider needs an API key you haven't added. Click the pill label, paste the key, and the pill should switch to the provider's name in green. DuckDuckGo doesn't need a key, so switching to it is another way to clear this state.
DuckDuckGo aggressively rate-limits and bot-blocks automated traffic. This is expected. For reliable results, switch to Tavily or Brave, both have free tiers.
The model decides when a search is worth it. If you're asking questions it can answer from training data, it won't search. To force a lookup, phrase your question around recency, e.g. *"search the web for the latest…"* or *"check current docs for…"*.
Test the key directly against the provider's API (Tavily and Brave both have docs with curl examples). If it works there but not here, open the settings popover and re-paste it, since extra whitespace on paste can break authentication.
---
# 7 Best aaPanel Alternatives for Developers (2026) (/blog/aapanel-alternatives)
Author: Hiren Kalariya | Role: Co-Founder & CEO, TST Technology | Published: 2026-07-21 | Tags: aaPanel alternatives, hosting control panel, server management panel, VPS management, aaPanel vs CtrlOps | Reading Time: 14 min read
> aaPanel's free tier locks you to one admin and Pro costs $28.80/mo per server. We compared 7 alternatives on pricing, team access and data privacy.
The best aaPanel alternatives in 2026 are **CtrlOps** (desktop app with an approval-gated AI terminal, $7/user/month with a 1 month free trial), **HestiaCP** (free full hosting stack with email), **CloudPanel** (fastest free PHP panel), **CyberPanel** (OpenLiteSpeed speed), **Coolify** (self-hosted PaaS), **RunCloud** (managed SaaS), and **Webmin + Virtualmin** (deepest control). The right pick depends on your stack, team size, and where your credentials are allowed to live.
## Top 7 aaPanel Alternatives for Developers in 2026 [#top-7-aapanel-alternatives-for-developers-in-2026]
We tested 7 aaPanel alternatives across real deployment tasks, security models, and pricing structures to find which ones actually solve the problems aaPanel creates.
| Tool | Type | Price | AI Terminal | Team Access | Data Privacy |
| ------------------- | ---------------- | ----------------------------------------- | -------------------- | ----------------------- | ------------------------------------------------------ |
| aaPanel (baseline) | Web panel | Free (1 admin) / Pro $28.80/mo per server | No | Free: single admin only | Self-hosted (international version of BT Panel, China) |
| CtrlOps | Desktop app | $7/user/mo (1-month free trial) | Yes (approval-gated) | Unlimited | Local-only |
| CloudPanel | Web panel | Free | No | Limited | Self-hosted |
| HestiaCP | Web panel | Free | No | Multi-user | Self-hosted |
| CyberPanel | Web panel | Free | No | Multi-level | Self-hosted |
| Coolify | Self-hosted PaaS | Free | No | Unlimited | Self-hosted |
| RunCloud | Managed SaaS | From $9/month | No | Yes | Cloud (RunCloud servers) |
| Webmin + Virtualmin | Web panel | Free | No | Multi-user | Self-hosted |
*Pricing from vendor sites as of July 2026. aaPanel Pro is priced per server; CtrlOps is priced per user with unlimited servers.*
***
## 1. CtrlOps [#1-ctrlops]
[CtrlOps](/) is a desktop application for macOS, Windows, and Linux. It connects to your servers over standard SSH - no agent installed, no web panel exposed on the server.

### Key Features [#key-features]
* **[AI Terminal](/docs/modules/ai-terminal):** Describe the problem in plain English. CtrlOps generates diagnostic commands and waits for your approval before running anything.
* **[One-click deployment](/docs/modules/deployment):** Paste a GitHub repo URL, select your framework. CtrlOps handles git clone, npm install, PM2, Nginx, and SSL. Reduces deployment from 30 - 45 minutes to under 5.
* **[GUI file manager](/docs/modules/file-manager):** Drag-and-drop uploads, in-app editing. No separate SFTP tool needed.
* **[Real-time monitoring](/docs/modules/infra-details):** Live CPU, RAM, disk, and top processes for every connected server.
* **[Script Directory](/docs/modules/ai-terminal/scripts):** Save command sequences as reusable one-click scripts with `{{variable}}` placeholders. Run the same script across multiple servers.
* **Log management:** Auto-discovers every log file on your server, grouped by service. Search, tail live, or download without touching the terminal.
* **Local-first security:** All credentials stored on your machine with AES-256 encryption. Nothing syncs to the cloud. aaPanel runs on your server and exposes a web interface to the internet.
**Bottom line:**
CtrlOps includes more beyond this list - SSH key management, access management, automated backups, and MCP server integration. See the
[full feature list](/features)
.
Spirex Infoways ran exactly the setup this guide describes: aaPanel installed separately on all six of its servers, which meant six logins and no single view of the fleet. [Their multi-server changes went from two hours to under ten minutes](/case-studies/spirex-infoways) once every server ran from one dashboard.
### Pricing [#pricing]
* Free trial: [1 month free](/pricing), no credit card required
* Monthly: $7/user/month (unlimited servers)
* Yearly: $70/user/year (save 16.7%)
### Best For [#best-for]
* Developers managing 3-20 VPS servers
* Small teams that need AI-assisted diagnostics and deployment automation
* Anyone who requires local-first credential storage (NDAs, data residency)
* Freelancers replacing 4+ separate tools (SSH client, SFTP, monitoring, terminal)
### Limitations [#limitations]
* No mobile app.
* No serverless support (Lambda, Cloud Functions).
* No Kubernetes or container orchestration.
***
## 2. CloudPanel [#2-cloudpanel]
[CloudPanel](https://www.cloudpanel.io/) is a free, open-source web hosting panel built on NGINX and PHP-FPM. It installs on Debian or Ubuntu and strips everything to the essentials - lighter and faster than aaPanel on the same hardware.

### Key Features [#key-features-1]
* **NGINX-native stack:** No Apache fallback. PHP-FPM, MySQL, Redis, and Node.js all configured out of the box.
* **Cloud provider integrations:** Built-in support for AWS, DigitalOcean, Hetzner, Google Cloud, Vultr, and Azure. Auto-configures firewalls and DNS for each provider.
* **Site isolation:** Each website runs under its own Linux user. One compromised site cannot access another.
* **Free SSL via Let's Encrypt:** Automatic certificate provisioning and renewal.
* **Vhost templates:** Pre-built configs for WordPress, Laravel, Drupal, and other PHP frameworks.
### Pricing [#pricing-1]
* Free forever, open-source (BSD license)
* No paid plans or premium tiers
* All features included at no cost
### Best For [#best-for-1]
* Developers hosting 5-15 PHP or Node.js sites on a single server
* Teams that want a lightweight, NGINX-native panel with minimal resource overhead
* Projects that do not need a built-in email server
### Limitations [#limitations-1]
* No built-in email server.
* No GUI file manager inside the panel.
* Smaller community than HestiaCP or CyberPanel.
**Bottom line:**
CloudPanel trades aaPanel's feature count for raw performance. If you host 5-15 PHP sites and don't need a built-in mail server, CloudPanel runs leaner on the same hardware.
***
## 3. HestiaCP [#3-hestiacp]
[HestiaCP](https://hestiacp.com/) is a free, open-source control panel forked from VestaCP. It provides a full hosting stack in a single install: web server, email, DNS, databases, and backups - plus a properly integrated mail server that aaPanel lacks.

### Key Features [#key-features-2]
* **Full hosting stack:** NGINX + Apache or NGINX + PHP-FPM, Exim mail server, Dovecot, Roundcube webmail, PowerDNS, and MariaDB/MySQL. All configured during installation.
* **Multi-user support:** Create separate accounts with their own domains, databases, and email. aaPanel free limits you to one admin.
* **Multi-PHP:** Run PHP 5.6 through 8.2 simultaneously. Assign different PHP versions per site.
* **Automated backups:** Schedule backups to local storage or 50+ cloud destinations.
* **One-click CMS installs:** WordPress, Drupal, Laravel, NextCloud, PrestaShop, and more.
### Pricing [#pricing-2]
* Free forever, open-source (GPLv3 license)
* No paid plans or premium tiers
* All features included at no cost
### Best For [#best-for-2]
* Freelancers and small agencies hosting client sites with email
* Teams that need multi-user accounts, DNS management, and automated backups at zero cost
* WordPress and PHP sites that require a full hosting stack (web server, mail, DNS, databases) in one install
### Limitations [#limitations-2]
* Supports only Debian and Ubuntu.
* UI is functional but dated.
* No Docker management.
***
## 4. CyberPanel [#4-cyberpanel]
[CyberPanel](https://cyberpanel.net/) is a free hosting panel built on [OpenLiteSpeed](https://openlitespeed.org/), the open-source edition of LiteSpeed Web Server. If page speed matters for your WordPress sites, CyberPanel's OpenLiteSpeed stack is the biggest differentiator over aaPanel.

### Pricing [#pricing-3]
* Core panel: Free forever (OpenLiteSpeed)
* .htaccess Module: $59/year or $199 lifetime
* CyberPanel Add-ons bundle (all 6 premium add-ons): $59/year with 7-day free trial
* LiteSpeed Enterprise bundles: separate pricing via LiteSpeed store (starts higher)
### Best For [#best-for-3]
* WordPress-heavy hosting where page load speed is the top priority
* Developers who want OpenLiteSpeed's built-in caching for PHP workloads
* Teams comfortable troubleshooting occasional panel quirks in exchange for raw speed
### Key Features [#key-features-3]
* **OpenLiteSpeed built-in:** Up to 10x faster than Apache for PHP workloads, according to LiteSpeed's [own benchmarks](https://www.litespeedtech.com/benchmarks). LiteSpeed Cache for WordPress is included.
* **Docker manager:** Deploy containerized apps alongside traditional PHP hosting from the same panel.
* **Email server:** Postfix + Dovecot with Rspamd spam filtering, DKIM, SPF, and DMARC.
* **One-click installs:** WordPress, Redis, MongoDB, n8n, and 20+ applications.
* **Multi-user levels:** Admin, reseller, and user roles for hosting businesses.
### Limitations [#limitations-3]
* Premium add-ons cost $59/year each.
* Community support can be slow.
* User reviews report occasional backup and SSL failures under production load.
***
## 5. Coolify [#5-coolify]
[Coolify](https://coolify.io/) is an open-source, self-hosted PaaS. Instead of managing Apache configs and PHP versions like aaPanel, you push code to Git and Coolify handles the rest. Think self-managed Heroku.

### Key Features [#key-features-4]
* **Git-push deployments:** Connect your GitHub, GitLab, or Bitbucket repo. Push to deploy. Automatic SSL, preview deployments, and rollbacks.
* **280+ one-click templates:** Deploy databases (PostgreSQL, MySQL, Redis), workflow tools (n8n), CMS platforms, and AI inference engines.
* **No per-user fees:** Unlimited team members on the self-hosted version. No feature gates.
* **Multi-server support:** Manage multiple VPS instances from one Coolify dashboard.
* **Docker Compose native:** Bring your own `docker-compose.yml` and deploy.
### Pricing [#pricing-4]
* Self-hosted: free forever (Apache 2.0 license), no feature limits, no user caps
* Coolify Cloud: $5/month for 2 servers, $3/month per additional server
* Coolify Cloud annual: 20% discount (\~$4/month)
* No per-user fees on any plan
### Best For [#best-for-4]
* Developers deploying Node.js, Python, Go, or containerized apps
* Teams that want Heroku-like Git-push workflows on their own servers
* Projects using Docker Compose that need automatic SSL, preview deployments, and rollbacks
### Limitations [#limitations-4]
* Requires Docker knowledge.
* Scaling stops at Docker Swarm. No Kubernetes.
* Needs a dedicated VPS for the Coolify management layer.
* Documentation gaps for complex multi-server setups.
***
## 6. RunCloud [#6-runcloud]
[RunCloud](https://runcloud.io/) is a managed SaaS panel. You connect your VPS to RunCloud's dashboard, and it handles stack configuration, deployments, SSL, and monitoring - no panel installed on your server, but an agent is required.

### Key Features [#key-features-5]
* **Web-based dashboard:** Manage servers from any browser. No SSH needed for most tasks.
* **Atomic deployments:** Git-based deploys with zero-downtime switching for PHP apps.
* **Automated backups:** Scheduled server and database backups with one-click restore.
* **Team management:** Role-based access and shared server management across team members.
* **WordPress toolkit:** One-click staging, cloning, and automatic updates for WordPress sites.
* **Integrations:** Slack, Telegram, GitHub, Cloudflare DNS, and more.
### Pricing [#pricing-5]
* 5-day free trial (no free plan)
* Essentials: $8/month (1 server, unlimited web apps, 2GB backup storage)
* Professional: $19/month (up to 50 servers, 10GB backup, staging, app cloning)
* Business: $49/month (up to 100 servers, 30GB backup, atomic deployment, 10 team seats, API access)
* Enterprise: $399/month (up to 500 servers, 50 team seats, high-volume API)
* Annual billing available on all plans.
### Best For [#best-for-5]
* Agencies managing multiple client WordPress and PHP sites
* Developers who want a managed SaaS experience without maintaining panel software
* Teams that need atomic (zero-downtime) deployments and role-based access (Business plan and above)
### Limitations [#limitations-5]
* No free plan. 5-day trial only.
* Pricing is per server. Scales fast with multiple servers.
* PHP-focused. Limited non-PHP stack support.
* Agent-based. Installs software on your server.
* Best features locked behind higher tiers.
***
## 7. Webmin + Virtualmin [#7-webmin--virtualmin]
[Webmin](https://webmin.com/) is a free, open-source web interface for Linux system administration. [Virtualmin](https://www.virtualmin.com/) is a plugin that adds web hosting features (virtual hosts, DNS, email, databases) on top of Webmin.
Together, they form the most configurable alternative to aaPanel. Every server setting is exposed. Every config file is editable through the GUI.

### Key Features [#key-features-6]
* **Full system administration:** Manage users, firewall rules, cron jobs, services, packages, disk quotas, and network config. Goes far deeper than any hosting panel.
* **Virtualmin hosting stack:** Apache or NGINX, BIND DNS, Postfix mail, MySQL/MariaDB. Full multi-domain hosting with per-user isolation.
* **100+ modules:** Extend Webmin with modules for Samba, Squid, LDAP, Fail2ban, and nearly any Linux service.
* **Supports most Linux distros:** Debian, Ubuntu, CentOS, AlmaLinux, Rocky Linux, RHEL, and more.
* **Long track record:** Webmin has been actively developed since 1997. Massive documentation and community.
### Pricing [#pricing-6]
* Webmin: free, open-source
* Virtualmin GPL: free, unlimited domains
* Virtualmin Pro: from $7.50/month or $75/year (10 domains), scales with domain count
* Virtualmin Pro adds: script installers, reseller features, spam/virus filtering, mobile access, priority support
### Best For [#best-for-6]
* Experienced Linux sysadmins who want granular control over every server setting
* Teams managing multi-domain hosting with per-user isolation, email, and DNS
* Environments that need 100+ Webmin modules (Samba, LDAP, Fail2ban, Squid, and more)
### Limitations [#limitations-6]
* Steep learning curve with hundreds of options.
* Interface looks dated.
* No one-click app deployment.
* No Docker integration in the base install.
***
## Feature and Capability Comparison [#feature-and-capability-comparison]
These tables compare all 7 aaPanel alternatives across the capabilities that matter for daily server management - not marketing bullet points.
### Hosting Stack and Web Server [#hosting-stack-and-web-server]
| Tool | Web Server | PHP Support | Node.js Support | Built-in Email | DNS Management | Database GUI |
| ------------------- | ----------------------- | ----------------- | -------------------- | --------------------- | ---------------------- | -------------- |
| aaPanel (baseline) | Apache + NGINX | ✓ (multi-version) | ✓ | ✗ | ✗ | ✓ (phpMyAdmin) |
| CtrlOps | N/A (connects over SSH) | N/A | ✓ (one-click deploy) | N/A | N/A | ✗ |
| CloudPanel | NGINX only | ✓ (PHP-FPM) | ✓ | ✗ | ✗ | ✓ (phpMyAdmin) |
| HestiaCP | NGINX + Apache | ✓ (multi-version) | ✗ | ✓ (Exim + Dovecot) | ✓ (PowerDNS) | ✓ |
| CyberPanel | OpenLiteSpeed | ✓ | ✗ | ✓ (Postfix + Dovecot) | ✓ | ✓ |
| Coolify | Docker-based | Via container | ✓ (Git deploy) | Via container | ✗ | Via container |
| RunCloud | NGINX + Apache | ✓ | ✓ (limited) | ✗ | Cloudflare integration | ✓ |
| Webmin + Virtualmin | Apache or NGINX | ✓ | ✗ | ✓ (Postfix) | ✓ (BIND) | ✓ |
### Deployment and Automation [#deployment-and-automation]
| Tool | One-Click App Deploy | Git-Based Deploy | Docker Support | Deployment Templates | CI/CD Integration |
| ------------------- | -------------------- | ----------------- | -------------- | -------------------- | ---------------------- |
| aaPanel | ✓ (limited) | ✗ | Basic | ✗ | ✗ |
| CtrlOps | ✓ | ✓ (GitHub URL) | ✗ | ✓ (Script Directory) | ✗ |
| CloudPanel | ✓ (PHP frameworks) | ✗ | ✗ | ✓ (vhost templates) | ✗ |
| HestiaCP | ✓ (CMS installs) | ✗ | ✗ | ✗ | ✗ |
| CyberPanel | ✓ (20+ apps) | ✗ | ✓ | ✗ | ✗ |
| Coolify | ✓ (280+ templates) | ✓ (Git-push) | ✓ (native) | ✓ (Docker Compose) | ✓ (webhooks) |
| RunCloud | ✓ (WordPress) | ✓ (atomic deploy) | ✗ | ✗ | ✓ (GitHub integration) |
| Webmin + Virtualmin | ✗ | ✗ | ✗ | ✗ | ✗ |
### Team Access and Security [#team-access-and-security]
| Tool | Multi-User Access | Role-Based Permissions | Credential Storage | Agent on Server | Exposed Web Port |
| ------------------- | ------------------ | --------------------------- | -------------------- | ------------------ | ---------------- |
| aaPanel | Free: 1 admin only | Pro only | Server-side | ✗ (is the server) | ✓ (port 8888) |
| CtrlOps | Unlimited | ✓ (root/standard/read-only) | Local only (AES-256) | ✗ | ✗ |
| CloudPanel | Limited | Basic | Server-side | ✗ (is the server) | ✓ (port 8443) |
| HestiaCP | ✓ (multi-user) | ✓ (admin/user) | Server-side | ✗ (is the server) | ✓ (port 8083) |
| CyberPanel | ✓ (multi-level) | ✓ (admin/reseller/user) | Server-side | ✗ (is the server) | ✓ (port 8090) |
| Coolify | Unlimited | ✓ | Server-side | ✗ (is the server) | ✓ |
| RunCloud | ✓ | ✓ (role-based) | Cloud (RunCloud) | ✓ (agent required) | ✗ |
| Webmin + Virtualmin | ✓ (multi-user) | ✓ (granular ACLs) | Server-side | ✗ (is the server) | ✓ (port 10000) |
### Monitoring and AI Features [#monitoring-and-ai-features]
| Tool | Live Metrics Dashboard | Log Viewer | AI Command Generation | AI Approval Gate | Process Manager GUI |
| ------------------- | -------------------------- | ------------------ | --------------------- | ---------------- | ------------------- |
| aaPanel | Basic | ✓ | ✗ | N/A | ✗ |
| CtrlOps | ✓ (CPU/RAM/disk/processes) | ✓ (auto-discovery) | ✓ | ✓ | ✓ |
| CloudPanel | Basic | ✗ | ✗ | N/A | ✗ |
| HestiaCP | Basic | ✗ | ✗ | N/A | ✗ |
| CyberPanel | Basic | ✗ | ✗ | N/A | ✗ |
| Coolify | ✓ | ✓ | ✗ | N/A | ✗ |
| RunCloud | ✓ | ✓ | ✗ | N/A | ✗ |
| Webmin + Virtualmin | ✓ (detailed) | ✓ | ✗ | N/A | ✓ |
***
## Why Are Developers Switching Away from aaPanel? [#why-are-developers-switching-away-from-aapanel]
**Single-user limit on the free tier:** aaPanel free supports one admin account. If you manage client servers with a teammate, or hand off access to a contractor, there's no built-in way to do it without sharing the root login. HestiaCP, CtrlOps, and Coolify all support multiple users at no cost.
**Pricing jumps quickly on Pro:** aaPanel Pro costs [$28.80/month](https://www.aapanel.com/new/pricing.html) (monthly), $198/year, or $699 lifetime. Each license covers one server. Managing 3 servers on Pro costs $86.40/month or $594/year. CtrlOps covers unlimited servers for $7/user/month or $70/user/year.
**No deployment automation or AI:** aaPanel provides a file manager, database tools, and a terminal emulator. It does not generate commands, diagnose errors, or deploy apps from a Git repo. Every task beyond basic hosting is manual terminal work.
### The Data Privacy Question Nobody Wants to Ignore [#the-data-privacy-question-nobody-wants-to-ignore]
aaPanel is the international version of BT Panel, a Chinese server management panel. This is public information listed in aaPanel's own documentation.
A [June 2026 Trustpilot review](https://au.trustpilot.com/review/aapanel.com) captures the concern directly: the reviewer questioned whether server data, domains, or usage information managed through aaPanel could be monitored or accessed under Chinese data regulations.
If your clients require data sovereignty guarantees or your contracts include data residency clauses, a locally installed alternative (CtrlOps, HestiaCP, CloudPanel) or a self-hosted platform (Coolify) removes this variable entirely.
**Bottom line:**
aaPanel hasn't been proven to mishandle data. But a hosting panel has root-level access to your server. For developers managing client projects under NDAs, the origin of the software running on their servers is a reasonable factor in tool selection.
***
## How to Choose the Right aaPanel Alternative for Your Stack [#how-to-choose-the-right-aapanel-alternative-for-your-stack]
The right tool depends on what you're hosting, how many servers you manage, and whether you need team access.
**You host PHP/WordPress sites and want a free panel:** CloudPanel (performance-focused, no email) or HestiaCP (full stack with email and DNS). Both are self-hosted, open-source, and replace aaPanel feature-for-feature.
**You host PHP sites and page speed is critical:** CyberPanel. OpenLiteSpeed's built-in caching gives a measurable edge for WordPress. Accept the trade-off of occasional stability issues.
**You deploy Node.js, Python, or Docker apps:** Coolify. Git-push deploys and 280+ templates make it the best PaaS alternative. aaPanel's app deployment for non-PHP stacks is basic at best.
**You manage 3+ servers and want AI assistance:** [CtrlOps](/). The AI terminal diagnoses issues, the file manager replaces SFTP, and the monitoring dashboard replaces `htop`. Our [CtrlOps vs aaPanel](/compare/ctrlops-vs-aapanel) breakdown covers the trade-off feature by feature.
**You want a managed service with no self-hosting:** RunCloud. You trade local control for convenience. Good for agencies that want to [manage multiple servers](/blog/manage-multiple-servers-without-losing-control) without maintaining panel software.
**You need full system administration control:** Webmin + Virtualmin. More powerful than any panel on this list. Also more complex. Best for experienced Linux admins.
| Your Situation | Best Pick | Runner-Up |
| -------------------------------- | ------------------- | ---------- |
| WordPress hosting, zero budget | HestiaCP | CyberPanel |
| PHP sites, max performance | CyberPanel | CloudPanel |
| Node.js / Docker deployments | Coolify | CtrlOps |
| 5+ servers, team access, AI | CtrlOps | RunCloud |
| Managed SaaS, no self-hosting | RunCloud | CtrlOps |
| Full Linux admin control | Webmin + Virtualmin | HestiaCP |
| Data privacy / local credentials | CtrlOps | CloudPanel |
## Conclusion [#conclusion]
The best aaPanel alternative depends on what broke for you.
If aaPanel's single-user limit and lack of AI assistance are costing you time, CtrlOps replaces the entire workflow with a desktop app that handles SSH, file management, monitoring, and deployment at $7/month per user, free for the first month. That is the same shift developers describe after switching:
> Honestly didn't expect much. But my DevOps workflow has genuinely shifted... I'm doing in 10 minutes what used to take an hour. If you manage servers, just try it.
>
> * **Chintan Poriya**, Co-founder & CEO of [BytezTech](https://byteztech.com), in a [public LinkedIn review](https://www.linkedin.com/posts/chintan-poriya_product-review-started-using-ctrlopsai-activity-7467179106200260609-Uoht)
More developer feedback is collected on the [CtrlOps reviews page](/reviews), where every quote links back to its original public post.
If you want a free browser-based panel with email support, HestiaCP is the most complete. If you deploy Docker apps, Coolify is purpose-built for that workflow.
Every tool on this list solves a specific problem aaPanel doesn't. Match the tool to your stack, test it on a staging server, and switch when you're confident.
If you're also evaluating SSH clients alongside server panels, the [best SSH client for Mac](/blog/best-ssh-client-mac-2026) and [PuTTY, Webmin, and ServerPilot alternatives](/blog/putty-webmin-serverpilot-alternatives) guides cover the terminal side of the equation.
***
## Frequently Asked Questions [#frequently-asked-questions]
HestiaCP is the most complete free alternative. It includes web hosting, email server, DNS management, multi-user accounts, and automated backups. CloudPanel is a better choice if you only need PHP/Node.js hosting without email. Both are open-source and self-hosted.
aaPanel functions as a capable server management panel. The safety concern relates to its origin as BT Panel, a Chinese company, and whether Chinese data regulations could theoretically apply to data managed through the panel. No public evidence of data misuse exists, but developers handling client data under NDAs or data residency contracts should evaluate this risk. Self-hosted alternatives like HestiaCP, CloudPanel, or a local-first tool like CtrlOps remove this variable.
Yes, for most developer workflows. CtrlOps replaces aaPanel's file manager, terminal, and monitoring with a desktop app that adds AI-assisted diagnostics, one-click deployment, and local-first credential storage. It does not include a built-in web hosting panel with Apache/NGINX vhost management the way aaPanel does. CtrlOps handles deployment and server operations. For traditional shared hosting panel features (email, DNS zones, PHP version management per site), pair it with CloudPanel or HestiaCP.
CtrlOps at $7/month per user includes unlimited users and unlimited servers, and starts with a 1 month free trial. HestiaCP and Coolify both offer multi-user access for free. aaPanel free only supports one admin account, and aaPanel Pro starts at $28.80/month per server for team features.
CloudPanel is lighter and faster for PHP hosting. Its NGINX-native stack uses fewer server resources than aaPanel's heavier setup. CloudPanel lacks a built-in email server and has a smaller app marketplace. Choose CloudPanel for lean PHP hosting. Choose aaPanel if you need email, a large plugin ecosystem, and don't mind the heavier resource footprint.
CtrlOps is a desktop app available on macOS (Apple Silicon and Intel), Windows, and Linux. It connects to your servers over SSH without installing anything on the server. All other alternatives on this list (CloudPanel, HestiaCP, CyberPanel, RunCloud, Webmin) are web-based panels that run on the server and are accessed through a browser. The same desktop-versus-browser trade-off applies to SSH itself, which we break down in [web-based vs. local SSH clients](/blog/web-based-vs-local-ssh-client).
Coolify is a stronger choice than aaPanel for Docker-based workflows. It provides Git-push deployments, automatic SSL, 280+ one-click service templates, and Docker Compose support. aaPanel has basic Docker management but is not designed for container-first deployment workflows.
Stay with aaPanel if you're a solo developer hosting WordPress sites, you don't need team access, your clients have no data residency requirements, and you're comfortable with aaPanel's Pro pricing for advanced features. Switching panels requires migration effort and learning time. If aaPanel isn't blocking your workflow, the switch may not be worth the cost.
Web panels like aaPanel, CloudPanel, and HestiaCP install on your server and run as a web application you access through a browser. They expose a port on your server. Desktop server managers like CtrlOps install on your local machine and connect to servers over SSH. No panel software runs on the server, and no extra ports are exposed.
RunCloud replaces aaPanel's core hosting features with a managed SaaS approach. You don't install panel software on your server. RunCloud handles stack configuration, deployments, SSL, and monitoring through its cloud dashboard. The trade-off is per-server pricing (starting at $9/month), no free tier, and an agent installed on your server that communicates with RunCloud's infrastructure.
---
# AI in DevOps: Replacing Manual Server Management (2026) (/blog/ai-in-devops)
Author: Hiren Kalariya | Role: Co-Founder & CEO, TST Technology | Published: 2026-04-08 | Updated: 2026-06-11 | Tags: AI DevOps, AI DevOps tools, AI terminal, server automation, server management | Reading Time: 25 min read
> How AI in DevOps replaces manual server work with AI terminals, approval-based commands, and real-time monitoring. Before-vs-after workflows saving 80% time.
## Key Takeaways [#key-takeaways]
AI in DevOps means using AI to replace the *manual parts* of server work - diagnostics, command generation, file operations, and routine maintenance - while engineers review and approve every action. It is not about replacing DevOps engineers. Teams that move from manual terminal workflows to AI-assisted operations report roughly 80-85% time savings on routine server tasks, and the production-safe model in 2026 is approval-gated assistance, not autonomous agents: the AI generates the commands, a human approves them before anything runs.
* **AI Terminal with approval gates** - describe the problem in English, review the generated commands, click to run
* **Centralized server access** - one dashboard, no scattered IPs or SSH keys
* **Real-time monitoring** - CPU, memory, disk visible at a glance, no SSH-and-htop ritual
* **Local-first security** - credentials never leave your machine, no cloud sync
* **Measurable time savings** - routine daily server operations drop from 75-135 minutes to 14-19 minutes
* **Lower bus factor** - non-DevOps developers can debug, deploy, and resolve incidents with approval-gated AI guidance
| Tool | Category | Approval Gate |
| ---------------------------- | ------------------------------ | ------------------------ |
| CtrlOps | AI server management workspace | ✓ Approve-before-execute |
| Warp | AI terminal | ✗ Auto-run by default |
| GitHub Copilot | Code assistant | n/a - no server access |
| Datadog / New Relic | AI monitoring | n/a - observability only |
| GitLab Duo / AWS DevOps Guru | Platform-specific AI | Platform-dependent |
Prefer to watch instead? Here is how AI replaces the manual server work while you keep control - in under 4 minutes:
***
## The Shift From Manual Server Work to AI-Assisted DevOps [#the-shift-from-manual-server-work-to-ai-assisted-devops]
If you are still managing servers the way you did three years ago, SSH-ing in, running commands from memory, switching between five tools just to check if something is working, you are not alone. However, you are also not operating the way your team needs you to.
The gap between what infrastructure demands and what manual workflows can deliver has grown too wide. 90% of tech professionals now use AI as part of their work, according to [Google's 2025 DORA report](https://dora.dev/dora-report-2025/). However, in DevOps, most teams still handle server operations the old way: terminal windows, guesswork, and hoping the one person who knows the commands is online.
This is not about AI replacing DevOps engineers. It is about AI replacing the *manual parts* - the repetitive commands, the diagnostic guesswork, and the context-switching between tools - so that engineers can focus on architecture and strategy instead of firefighting.
***
## Why Manual Server Management Is Breaking Modern DevOps Workflows [#why-manual-server-management-is-breaking-modern-devops-workflows]
Three things have changed that make manual server management unsustainable:\
Infrastructure has multiplied. A startup that ran one server in 2022 now manages production, staging, databases, caching, and background workers each on separate machines, often across multiple cloud providers.
Teams have not scaled proportionally. Most SMBs cannot justify a full-time DevOps hire. 33% of organizations cite skills shortage as their top challenge, according to [Puppet's 2021 State of DevOps Report, via Octopus](https://octopus.com/devops/metrics/devops-statistics/). The work grows, but the people do not.\
The cognitive load is crushing. Remembering IPs, SSH keys, command flags, config file paths, and which tool does what is not expertise;
It is memorization that could be handled better by a system - the kind of overhead that quietly eats a full day of every engineer's week.
Manual workflows worked when you had three servers and one person managing them. They break when you have [twelve servers across three cloud providers](/blog/manage-multiple-servers-without-losing-control), and a team that needs self-serve access.
**Bottom line:** Manual server workflows scale linearly. AI-assisted workflows scale exponentially. The moment your fleet grows past five servers - or your team grows past two engineers - manual stops being a workflow and becomes a daily tax on focus.
### The Rise of AI in DevOps and Automation [#the-rise-of-ai-in-devops-and-automation]
The shift is not hypothetical. 86% of tech professionals say using AI in core development tasks increases productivity ([DORA 2025](https://dora.dev/dora-report-2025/)), and 68% of developers save at least 10 hours a week with AI tools ([Atlassian 2025 Developer Experience Report](https://www.atlassian.com/blog/developer/developer-experience-report-2025)).
However, here is the nuance most articles miss: 61% of professionals have never used agentic AI workflows at all, and more autonomous agent modes sit at only around 25% adoption ([DORA 2025](https://dora.dev/dora-report-2025/)). The adoption is real, but it is cautious. Teams want AI assistance, not full autonomy.
This is the key insight driving the current wave of AI in DevOps: tools that help you work faster *with your approval*, not tools that run commands on your servers without asking. The future is not autonomous infrastructure. It is an augmented infrastructure where intelligent automation handles the tedious parts, and humans make the decisions.
**Reality check:** Auto-executing AI on a production server is one wrong command away from an incident. Every reputable AI DevOps tool in 2026 ships with an approval gate - and most engineers refuse to use the ones that don't. If a tool runs commands without asking, it's a demo, not a production system.
That is what the rest of this article covers: what AI-driven DevOps actually looks like in practice, how it replaces manual work, and what measurable improvements teams are seeing.
## Why DevOps Teams Are Moving to AI in 2026? [#why-devops-teams-are-moving-to-ai-in-2026]

The move to AI in DevOps is not driven by hype. It is driven by pain. The math is simple: the work keeps growing, the people don't, and something has to give.
### The Cost of Manual Server Management (Time, Errors, Context Switching) [#the-cost-of-manual-server-management-time-errors-context-switching]
Manual server management has three hidden costs that compound over time:\
Time. A typical DevOps engineer spends 1-3 hours daily on repetitive tasks: checking server health, deploying updates, reviewing logs, and restarting services. That is 5-15 hours per week on work that adds no strategic value. 50% of developers lose 10+ hours a week to inefficiencies like tracking down information ([Atlassian 2025 Developer Experience Report](https://www.atlassian.com/blog/developer/developer-experience-report-2025)).
Errors. Manual commands are fragile. A wrong flag, a mistyped path, or running a command on the wrong server, the consequences range from minor inconvenience to production outage. 44% of organizations experience 1-5 application failures per month ([JFrog 2025, via Appfire](https://appfire.com/resources/blog/devop-statistics)).
Context switching. Switching between the terminal, the SFTP client, the monitoring dashboard, and ChatGPT is not just annoying; it kills focus. Each context switch takes 5-10 minutes of recovery time. Over a day, that adds up to hours of lost productivity.
### How AI Is Changing the DevOps Workflow? [#how-ai-is-changing-the-devops-workflow]
AI does not replace the workflow. It changes the interface.\
Instead of:
* Memorizing commands → you describe what you need in plain English
* Switching between tools → one interface handles access, files, monitoring, and debugging
* Running commands unthinkingly → AI generates them, you approve before execution
* Guessing at root causes → AI analyzes server state and suggests diagnostics
The workflow stays the same (connect, diagnose, fix, verify), but each step takes less time and carries less risk.
### What "AI-Driven DevOps" Really Means in 2026? [#what-ai-driven-devops-really-means-in-2026]
Let us clear up the confusion. "AI-driven DevOps" does not mean:
❌ AI runs your infrastructure autonomously\
❌ AI replaces DevOps engineers\
❌ You stop understanding what happens on your servers
It means:\
✅ AI generates commands you review and approve\
✅ AI diagnoses issues faster than manual troubleshooting\
✅ AI handles routine tasks so engineers focus on strategic work\
✅ AI provides context-aware suggestions based on actual server state
The [DORA 2025 report](https://dora.dev/dora-report-2025/) found that more autonomous AI features, like agent modes, have slower adoption at around 25% - and 30% of professionals report little or no trust in AI-generated code. This tells us something important: teams want AI assistance *with human supervision*, not AI running on autopilot.
The right model for DevOps is not autonomous AI. It is human-in-the-loop AI, where the system does the heavy lifting and the human makes the call.
For more context on how automation is reshaping DevOps workflows, see our guide on the [best DevOps automation tools for small teams](/blog/devops-automation-tools).
## AI DevOps Tools That Are Shaping 2026 [#ai-devops-tools-that-are-shaping-2026]
The AI DevOps tool landscape is still maturing, but the categories are becoming clear. Here is where things stand.
### Top AI DevOps Tools Overview (CtrlOps First, Followed by Other Tools) [#top-ai-devops-tools-overview-ctrlops-first-followed-by-other-tools]
**CtrlOps - AI-assisted server management workspace**\
CtrlOps combines a centralized server dashboard, a [visual file manager](/docs/modules/file-manager), [real-time monitoring](/docs/modules/infra-details), and an [AI terminal](/docs/modules/ai-terminal) that generates commands with your approval. It is built for SMBs and teams that do not have a dedicated DevOps person but need to manage multiple servers efficiently. Local-first security model means credentials never leave your machine. Pricing: $7/month/user for unlimited servers, after a [1 month free trial](/pricing) with no credit card required.
| Feature | CtrlOps |
| ------------------------- | ---------------------------------- |
| AI Terminal | ✅ With human approval gates |
| File Manager GUI | ✅ Full visual browser |
| Infrastructure Monitoring | ✅ Built-in real-time dashboard |
| One-Click Deploy | ✅ Node.js, React, Next.js |
| Local-First Security | ✅ No cloud sync |
| Multi-Server Directory | ✅ Named servers, one-click connect |
**Warp - AI-powered terminal**\
Warp is a modern Rust-based terminal with AI command generation - we've tested it hands-on in our [best SSH client for Mac](/blog/best-ssh-client-mac-2026) comparison. Strong for developers who live in a terminal, but it is not a server management tool - no file manager, no monitoring dashboard, no multi-server directory - and it auto-runs by default, which is faster but riskier for production environments.
**GitHub Copilot - Code and configuration assistance**\
Copilot excels at generating code, but it does not connect to your servers or understand your infrastructure state. Useful for writing scripts, not for managing live environments.
**Datadog / New Relic - AI-powered monitoring**\
These platforms offer intelligent anomaly detection and alerting. Powerful for observability, but they do not provide server access, file management, or command execution. They tell you something is wrong; they do not help you fix it directly.
**GitLab Duo / AWS DevOps Guru - Platform-specific AI**\
Tied to specific ecosystems. Useful if you are all-in on one platform, less helpful for multi-cloud teams managing servers across providers.
### Where AI Terminal Assistants Fit In Modern Workflows? [#where-ai-terminal-assistants-fit-in-modern-workflows]
AI terminal assistants solve a specific problem: the gap between "I know what is wrong" and "I know the exact commands to fix it."
Traditional workflow:
1. Notice a problem
2. Google the error message
3. Find a Stack Overflow answer from 2021
4. Adapt the command for your environment
5. Hope it works
6. If it does not, repeat
AI terminal workflow:
1. Describe the problem: "Why is my API returning 502 errors?"
2. The assistant generates diagnostic commands based on your server's actual state
3. You review and approve
4. Commands execute
5. The assistant summarizes the results in plain language
The difference is not just speed in context. A generic AI chatbot does not know your server's CPU load, disk usage, or running processes. An AI terminal assistant connected to your server does. Where that assistant actually runs matters too - we compared [three AI terminal approaches for server management](/blog/ai-terminal-tools-server-management) (in-session suggestions, an agent on the server, and desktop-first with approval gates).
### How AI Server Management Tools Reduce Operational Toil? [#how-ai-server-management-tools-reduce-operational-toil]
Operational toil is the work that has to get done but does not move the business forward. AI reduces it in three ways:
Automated diagnostics. Instead of running top, df -h, free -m, and journalctl manually, the assistant runs the right combination based on the symptom you describe.
Guided remediation. The system suggests fixes with explanations, so even engineers unfamiliar with a specific issue can resolve it confidently.
Proactive monitoring. Real-time dashboards with smart alerts catch problems before they become incidents.
For a deeper comparison of available solutions, check our guide on [DevOps management tools](https://tsttechnology.io/blog/devops-management-tool).
## We Replaced Manual Server Work with AI: Here is What Actually Changed [#we-replaced-manual-server-work-with-ai-here-is-what-actually-changed]

This section is not theoretical. It is based on what actually happens when teams move from manual terminal workflows to AI-assisted operations using CtrlOps.
### Before vs After: Life Without CtrlOps [#before-vs-after-life-without-ctrlops]
#### What Server Operations Looked Like Before AI [#what-server-operations-looked-like-before-ai]
The morning routine:
1. Open terminal, SSH into production server (IP from spreadsheet)
2. Run htop to check CPU, free -h for memory, and df -h for disk
3. Run pm2 status to check if the app is running
4. Open a browser tab with the Grafana dashboard
5. Open ChatGPT in another tab for debugging help
6. Check Slack for any reported issues
The deployment ritual:
1. SSH into the server
2. cd /var/www/myapp
3. git pull origin main
4. npm install --production
5. pm2 restart myapp
6. pm2 logs myapp --lines 50 (verify it started)
7. Check Nginx: sudo nginx -t && sudo systemctl reload nginx
8. Cross fingers
The incident response:
1. Get a Slack alert at 11 PM
2. SSH into the server
3. Run various diagnostic commands
4. Google error messages
5. Try fixes one by one
6. Hope you did not make it worse
7. Resolution time: 30-90 minutes
#### What Server Operations Look Like with CtrlOps (AI + UI + Centralization)? [#what-server-operations-look-like-with-ctrlops-ai--ui--centralization]
The morning routine:
1. Open CtrlOps
2. See all servers with health status at a glance
3. Click server → Infra Details shows CPU, memory, disk in real-time
4. Done in 30 seconds
The deployment:
1. Open CtrlOps, click server
2. Click "Add Application" → paste GitHub URL, select framework
3. Add environment variables, domain, and toggle SSL
4. Click Create
5. Done in 5 minutes
The incident response:
1. Open CtrlOps, connect to the server
2. Type in AI Terminal: "Why is my API returning 502 errors?"
3. The assistant runs diagnostics, returns: "Nginx cannot reach Node.js app. App crashed due to memory limits. Memory at 94%."
4. Review suggested fix commands, click "Run."
5. Resolution time: 5-10 minutes
### Time Saved with AI in DevOps [#time-saved-with-ai-in-devops]
#### Typical Daily Tasks Before AI (Manual Steps, Time Consumption) [#typical-daily-tasks-before-ai-manual-steps-time-consumption]
| Task | Manual Steps | Time |
| ------------------------------- | ------------------------------------------ | ---------- |
| Check server health (3 servers) | SSH into each, run 3-4 commands per server | 15-20 min |
| Deploy update | SSH, pull, install, restart, verify logs | 15-30 min |
| Debug error | Search logs, Google error, try fixes | 30-60 min |
| Update the config file | SSH, navigate, vim, save, reload service | 10-15 min |
| Transfer the file to the server | Open SFTP, connect, navigate, upload | 5-10 min |
| Daily total | | 75-135 min |
#### Tasks After AI (Automation, Suggestions, Faster Execution) [#tasks-after-ai-automation-suggestions-faster-execution]
| Task | AI-Assisted Steps | Time |
| --------------------------- | --------------------------------------------------------------- | --------- |
| Check server health | Open the dashboard, view all servers | 1 min |
| Deploy update | Guided wizard → click Create | 5 min |
| Debug error | Describe the problem to the assistant, review & approve the fix | 5-10 min |
| Update the config file | File Manager → click, edit, save | 2 min |
| Transfer file to the server | File Manager → upload | 1 min |
| Daily total | | 14-19 min |
That is roughly 80-85% time savings on routine server operations. Over a month, that is 20-40 hours given back to the team.
### Mistakes Reduced Thanks to AI Controls [#mistakes-reduced-thanks-to-ai-controls]
#### Common Manual Errors in Server Management (Wrong Commands, Misconfigurations) [#common-manual-errors-in-server-management-wrong-commands-misconfigurations]
* Running commands on the wrong server (terminal windows look identical)
* Typos in commands (rm -rf in the wrong directory)
* Forgetting steps in the deployment sequence (install before restart)
* Editing config files with syntax errors
* Leaving stale SSH keys on servers after team members leave
These are not rare incidents. They happen because humans are asked to do repetitive, precise work under pressure, often at odd hours. The stale-key problem in particular has a dedicated fix - the [14 SSH key management best practices](/blog/ssh-key-management-best-practices) cover revocation and auditing end to end.
#### How CtrlOps Prevents Accidental Execution with Approval-Based Commands? [#how-ctrlops-prevents-accidental-execution-with-approval-based-commands]
CtrlOps takes a different approach from AI tools that auto-execute:
Every AI-generated command needs your approval. You review it before it runs.
This is the "approve-before-execute" model, and it matters for three reasons:
1. You stay in control. No AI runs commands on your production server without your explicit say-so.
2. You learn as you go. Seeing the generated commands teaches you what each one does, building knowledge instead of creating dependency.
3. You catch mistakes before they happen. If the assistant suggests something unexpected, you can modify or reject it.
The market is clearly saying: help me, but do not run things without asking. CtrlOps was built around that principle.
### Real Use Cases of AI in Server Management [#real-use-cases-of-ai-in-server-management]
#### Use Case 1 - AI Terminal Assistant for Faster Debugging and Diagnostics [#use-case-1---ai-terminal-assistant-for-faster-debugging-and-diagnostics]
**Scenario:** API server starts returning 502 errors at 2 AM.\
**Without AI:** The engineer wakes up, SSHs in, runs 5-10 diagnostic commands over 30 minutes, and eventually finds the issue.\
**With CtrlOps AI:** Engineer types "Why is my API returning 502 errors?" The assistant runs diagnostics, identifies the root cause (disk full, service crashed, memory limit), and suggests a fix. Engineer approves. Resolved in 5 minutes.
#### Use Case 2 - Centralized Multi-Server Monitoring and Alerts [#use-case-2---centralized-multi-server-monitoring-and-alerts]
**Scenario:** Managing 8 servers across 2 cloud providers.\
**Without AI:** Check each server individually via SSH or separate monitoring tabs. Problems are discovered reactively after users complain.\
**With CtrlOps**, a single dashboard shows all 8 servers with real-time metrics. Unusual patterns surface immediately. You spot the disk filling up before it hits 100%.
#### Use Case 3 - UI-Based File Management Without CLI Dependency [#use-case-3---ui-based-file-management-without-cli-dependency]
**Scenario:** A frontend developer needs to update an Nginx config file.\
**Without AI:** Must know SSH, terminal navigation, and Vim. Likely needs help from a DevOps person. Takes 15 minutes if they know what they are doing, much longer if they do not.\
**With CtrlOps:** Open File Manager, navigate visually to /etc/nginx/, click the config file, edit in UI, save. Takes 2 minutes. No terminal knowledge needed.
## Advantages of AI in DevOps for Modern Teams [#advantages-of-ai-in-devops-for-modern-teams]
The advantages of AI in DevOps go beyond "saving time." They reshape how teams operate, who can participate, and how reliably infrastructure runs.
### Centralization of Server Access and Operations [#centralization-of-server-access-and-operations]
When server access, monitoring, file management, and troubleshooting live in one place, everything changes:
* No more scattered credentials. SSH keys, server IPs, and connection details live in one encrypted, local store, not in spreadsheets, Slack messages, or sticky notes.
* No more "which tool do I use for this?" One application handles everything from connecting to deploying to debugging.
* No more information silos. Everyone on the team sees the same server status, the same metrics, the same access points.
Teams with easy access to self-serve information are 4.9x more effective ([Atlassian 2025, via Appfire](https://appfire.com/resources/blog/devop-statistics)). Centralization makes that possible.
### Security-First Design with User-Approved Commands [#security-first-design-with-user-approved-commands]
AI in DevOps raises a legitimate concern: what if the AI runs something destructive?\
The answer is approval-based execution. Every AI-generated command in CtrlOps goes through a human review gate. You see the exact command, understand what it does, and choose whether to run it.
This matters because 57% of professionals say AI introduces new security risks, but 63% also believe it helps write more secure code ([Black Duck Global State of DevSecOps 2025](https://www.blackduck.com/resources/analyst-reports/state-of-devsecops.html)). The tension is real: the technology can help, but only when it is designed with safety boundaries.
CtrlOps addresses this with:
* Approve-before-execute: No command runs without your click
* Local-only storage: Credentials never leave your machine
* No cloud sync: No third-party servers ever see your SSH keys
* AES-256 encryption: All stored data is encrypted at rest
This is the specific reason Ughareja Infotech left Termius: its AI routed commands through the cloud, with no option to bring your own key. [The founder now runs the AI terminal locally on his own key](/case-studies/ughareja-infotech), with every command described and approved before it executes. For developers looking for a [Termius alternative with built-in AI](/blog/termius-alternatives), the landscape has shifted significantly in 2026.
**Bottom line:** If your AI DevOps tool syncs SSH keys to the cloud, your security perimeter just grew to include a third party's infrastructure. Local-first credential storage isn't a feature - it's a baseline requirement for any team with SOC2, HIPAA, or client-contract obligations.
### Faster Incident Response with Real-Time Insights [#faster-incident-response-with-real-time-insights]
73% of teams take several hours to resolve production issues ([Logz.io DevOps Pulse 2023](https://logz.io/devops-pulse-2023/)). The bottleneck is not fixing the problem, but finding it.
AI accelerates incident response by:
* Connecting symptoms to causes faster than manual log diving
* Providing context-aware suggestions based on actual server state
* Summarizing diagnostic output in plain language instead of raw terminal output
The result: incidents that took 30-90 minutes now take 5-10 minutes.
### Reduced Dependency on Pure Terminal Expertise [#reduced-dependency-on-pure-terminal-expertise]
46% of organizations still use manual security processes, and 49% say these processes severely slow development ([Black Duck Global State of DevSecOps 2025](https://www.blackduck.com/resources/analyst-reports/state-of-devsecops.html)). The same applies to server operations.
When only one person on the team knows the right commands, two things happen:
1. That person becomes a bottleneck
2. Everyone else is afraid to touch the servers
AI-assisted tools break this dependency. A frontend developer can debug a production issue. A startup founder can deploy their app. A junior engineer can resolve an incident at 2 AM. Not because they have memorized Linux commands, but because the assistant generates the right commands and they approve them.
### Improved Productivity Across DevOps Teams [#improved-productivity-across-devops-teams]
The productivity gains are measurable:
| Metric | Before AI | With AI Assistance |
| ---------------------- | ------------ | ------------------ |
| Daily server ops time | 75-135 min | 14-19 min |
| Deployment time | 15-30 min | 5 min |
| Incident resolution | 30-90 min | 5-10 min |
| Onboarding new dev | 2-3 hours | 30 min |
| Wrong-server incidents | 2-3 per year | 0 |
For DevOps teams specifically, the time savings come from eliminating the diagnostic and command-memorization overhead that dominates manual workflows.
## How CtrlOps Fits Into the AI in DevOps Ecosystem? [#how-ctrlops-fits-into-the-ai-in-devops-ecosystem]

CtrlOps is not trying to be everything for everyone. It solves a specific problem: helping teams without dedicated DevOps expertise manage servers efficiently using AI assistance.
### CtrlOps as an AI-Powered DevOps Workspace [#ctrlops-as-an-ai-powered-devops-workspace]
Think of CtrlOps as three things combined:
1. **A server directory** - for all your servers, named and organized, with one click to connect
2. **An operations workspace** - file management, monitoring, and deployment in one UI
3. **An AI assistant** - terminal commands generated from natural language, with your approval
No other tool combines all three with a local-first security model.
**Where AI-assisted DevOps tools don't fit (yet):**
No tool replaces every part of your DevOps stack. CtrlOps focuses on the human-in-the-loop server operations layer - connecting, deploying, debugging, monitoring. It doesn't replace CI/CD pipelines (GitHub Actions, GitLab CI, Jenkins), it doesn't run autonomous Kubernetes operators, and it doesn't replicate the alerting depth of dedicated observability platforms like Datadog or New Relic. Pair it with those for full coverage - or use those instead if your stack runs primarily on serverless or container orchestration.
### What AI in DevOps Looks Like With CtrlOps [#what-ai-in-devops-looks-like-with-ctrlops]
This is not a feature list. It is what actually happens when you open the app and use it.
#### AI Terminal with Approve-Before-Execute [#ai-terminal-with-approve-before-execute]
The [AI Terminal](/features/ai-terminal) is built around one principle: the AI generates, you decide.
Here is the exact flow:
1. You type a request in plain English: *"Why is my API returning 502 errors?"*
2. The AI reads your server's live state - running processes, memory load, active services - via the live SSH session
3. It generates the appropriate diagnostic or fix commands, grounded in your actual server context, not a generic answer
4. Commands appear with a **Run** button. Nothing executes until you click it.
5. Output returns. The AI summarizes it in plain language.
6. Full command history stays in the panel with execution time and status.
This is what using generative AI in DevOps looks like in practice - not a chatbot you describe your server to, but an assistant that already knows your server state and generates commands specific to it.
**Quick action suggestions built in:**
* "Why is my server slow?"
* "Check memory and CPU"
* "Show recent error logs"
* "List running services"
* "Check disk space"
* "Restart crashed service"
**Bring your own AI:** Connect OpenAI, Google Gemini, Anthropic Claude, or any OpenAI-compatible provider. Your keys, your costs, your data - stored locally, never sent to CtrlOps servers.
**Auto-Run exists, but think before enabling it in production.** CtrlOps includes an Auto-Run toggle for power users who want to skip the approval gate for routine diagnostic sequences. For production servers, keep it off. The approve-before-execute model is what makes AI safe in live environments - and it is why agent modes sit at only \~25% adoption while 30% of professionals report little or no trust in AI-generated code (DORA 2025).
#### Web Search: Commands Based on Today's Docs, Not Last Year's Training Data [#web-search-commands-based-on-todays-docs-not-last-years-training-data]
Every AI model has a training cutoff. Ask it to install a recently released tool, and it may generate commands based on outdated documentation - wrong flags, deprecated methods, failed installs.
CtrlOps solves this with built-in web search inside the AI Terminal.
**How it works:**
* Enable the **Web** toggle in the AI Assistant panel
* Choose a search provider: Tavily (recommended), Brave, or DuckDuckGo (no API key required)
* Ask your question as normal
The AI searches the web in real time, reads the relevant documentation, shows you the sources it used, and then generates the command - still with the human approval gate in place. Web search does not bypass safety; it improves accuracy.
**What this changes in practice:**
| Without Web Search | With Web Search |
| ------------------------------------------------- | ----------------------------------------------- |
| Commands based on model's last training date | Commands based on live, current documentation |
| May suggest deprecated flags or install methods | Reads the official source before generating |
| Requires you to Google separately and cross-check | Sources shown inline - click through to verify |
| Breaks on recently released packages or CVEs | Handles new tools, breaking changes, fresh CVEs |
This is the layer that makes the AI Terminal genuinely reliable for production work, not just a fast shortcut.
#### Real-Time Infrastructure Monitoring Dashboard [#real-time-infrastructure-monitoring-dashboard]
No more running `htop`, `free -h`, and `df -h` in separate terminal windows.
The Infra Details tab shows:
| Metric | What You See |
| --------- | ------------------------------- |
| CPU | Live load %, uptime, core count |
| Memory | Used/total GB, available, swap |
| Disk | Used/total space, available % |
| Processes | PID, name, CPU%, Memory% |
One-click actions: refresh metrics, clean cache, clear old buffers.
This makes [server health monitoring](/features/infra-monitoring) accessible to everyone on the team, not just the person who knows what `free -h` output means.
#### UI-Based File Management vs Manual SSH + CLI [#ui-based-file-management-vs-manual-ssh--cli]
File operations are the most common server tasks that should not require terminal expertise.
Manual SSH + CLI approach:
* Navigate directories with `cd`
* List files with `ls -la`
* Edit with Vim or nano
* Transfer with `scp` or a separate SFTP tool
CtrlOps File Manager:
* Browse the directory tree visually
* Click to edit files
* Drag to upload/download
* Search by filename
The terminal is always available for complex operations. For the 80% of routine file tasks, the UI is faster and less error-prone.
#### Centralized Server Management from One Dashboard [#centralized-server-management-from-one-dashboard]
The foundation: a server directory where every server has a name, status, and one-click access.
This eliminates three chronic problems:
1. **"What is the IP again?"** - Servers are named, not numbered
2. **"Which server am I on?"** - Status and name visible at all times
3. **"How do I connect?"** - One click, no credential hunting
Import/export server lists for team sharing. SSH Setup Wizard for guided onboarding. Works with any SSH-accessible server across any cloud provider.
***
### For Non-DevOps Developers: The CtrlOps Difference [#for-non-devops-developers-the-ctrlops-difference]
Every AI DevOps tool on the market is built assuming the user knows Linux. CtrlOps is the one tool built for the developer who does not want to become a Linux expert just to manage a production server.
This is the gap no competitor owns and where CtrlOps delivers the most distinct value.
**What changes for a non-DevOps developer:**
**Debugging a production error at 2 AM**
Without CtrlOps: SSH in, run five commands from memory, Google the output, guess at the fix.
With CtrlOps: Type "Why is my server returning 500 errors?" The AI reads the live server state, runs diagnostics, and returns a plain-language summary. You review the fix command and click Run. Done in 5 minutes.
**Deploying an update**
Without CtrlOps: Remember the right directory, `git pull`, `npm install`, `pm2 restart`, verify logs, check Nginx. One wrong command breaks production.
With CtrlOps: Click Add Application → paste GitHub URL → select framework → add `.env` → toggle SSL → click Create. No sequence to memorize. No commands to type.
**Installing a tool you have never used**
Without CtrlOps: Google the tool, read the docs, find the install command, SSH in, paste it, hope the version matches.
With CtrlOps: Enable Web Search in the AI Terminal. Type the request. The AI reads the current official documentation and generates the exact correct install command. You approve. It runs.
**Updating a config file**
Without CtrlOps: SSH in, navigate to the right directory, open Vim, edit, save (if you remember the Vim commands), reload the service.
With CtrlOps: Open File Manager → navigate visually → click the file → edit in UI → save. Two minutes. No Vim required.
**The approval gate is the safety net for non-DevOps users.** When you are not certain what a command does, seeing it written out before it executes is what builds confidence and competence. Teams using CtrlOps consistently report that junior developers and non-DevOps team members become genuinely self-sufficient within a few weeks, not because the AI does everything for them, but because reviewing approved commands teaches them what each one does.
The result: a frontend developer can resolve a production incident. A startup founder can deploy a hotfix. A junior engineer can debug at 2 AM - without paging the senior DevOps person. The "bus factor" problem disappears.
## AI in DevOps vs AI-Powered Server Management: What's the Difference? [#ai-in-devops-vs-ai-powered-server-management-whats-the-difference]
When teams start using AI in DevOps, they quickly run into a terminology problem. "AI in DevOps" and "AI-powered server management" are often used interchangeably, but they describe very different things, targeting very different teams.
The distinction matters because it determines which tool actually fits your workflow.
### AI in DevOps: The Enterprise Definition [#ai-in-devops-the-enterprise-definition]
In enterprise engineering, AI in DevOps refers to AI embedded across the entire software delivery lifecycle:
* **AI-assisted code review** integrated into CI/CD pipelines
* **Predictive anomaly detection** across distributed Kubernetes clusters
* **Automated incident correlation** across hundreds of microservices
* **AI-generated runbooks** from observability data at scale
Tools like Datadog, GitLab Duo, and AWS DevOps Guru operate in this space. They are built for teams with dedicated platform engineers, SRE functions, and infrastructure running across multiple regions.
These tools solve real problems but they are designed for organizations with a DevOps team already in place.
### AI-Powered Server Management: The SMB Reality [#ai-powered-server-management-the-smb-reality]
AI-powered server management targets a different problem entirely: *what happens when a small team needs to manage production servers without a dedicated DevOps engineer?*
The challenges here are not about Kubernetes orchestration or distributed tracing. They are about:
* Remembering the right SSH command at 2 AM
* Deploying an update without breaking production
* Knowing whether a server is healthy without running four manual commands
* Giving a junior developer enough context to resolve an incident independently
This is where generative AI in DevOps delivers immediate, measurable value not by replacing a DevOps platform, but by replacing the *manual parts* of server work that consume hours every week.
### How CtrlOps Fits: The Line Between Both Worlds [#how-ctrlops-fits-the-line-between-both-worlds]
| | Enterprise AI in DevOps | AI-Powered Server Management (CtrlOps) |
| ------------------------ | ------------------------------------------------ | ------------------------------------------------------------- |
| **Target user** | Dedicated DevOps/SRE teams | Developers, founders, small teams |
| **Infrastructure scale** | 100s of services, Kubernetes, multi-region | 1 - 50 SSH-accessible servers |
| **AI role** | Autonomous anomaly detection, runbook generation | Command generation with human approval |
| **Deployment model** | SaaS, cloud-native | Local-first desktop app |
| **Credential storage** | Cloud | Local only, AES-256 encrypted |
| **Learning curve** | Weeks to onboard | Under 5 minutes to first connection |
| **Replaces** | Manual observability, ticket routing | Manual terminal work, SFTP clients, SSH credential management |
| **Pricing** | $20 - $50+ per seat/month | $7/month, unlimited servers (1 month free) |
Neither category is wrong. They solve different problems for different teams.
If you are running a distributed system with a platform engineering team, you need enterprise DevOps tooling. If you are a developer or small team managing VPS servers and spending hours a week on manual terminal work, AI-powered server management is what actually moves the needle.
If you want to understand how to use AI in DevOps for your day-to-day server operations rather than enterprise infrastructure management, the [Practical Next Steps](#practical-next-steps-for-your-team) section below covers exactly that.
## Practical Next Steps for Your Team [#practical-next-steps-for-your-team]
Knowing AI in DevOps works is different from making it work for your team. Here is how to start.
### How to Start Replacing Manual Server Work with AI? [#how-to-start-replacing-manual-server-work-with-ai]
Start small. Do not try to AI-ify your entire DevOps workflow at once. Pick one high-friction area:
* **Debugging and diagnostics:** This is where AI delivers the most immediate value. Instead of running 10 commands manually, describe the problem and let the assistant generate the diagnostic sequence.
* **File operations:** If your team currently uses a separate SFTP tool or manual scp commands, moving to a visual file manager is a quick win.
* **Monitoring:** Replacing manual htop checks with a real-time dashboard saves time every day.
Measure before and after. Track how long common tasks take now, then compare after adopting AI-assisted tools. The numbers tell the story.
### What to Look for in an AI DevOps & Server Management Tool? [#what-to-look-for-in-an-ai-devops--server-management-tool]
Not all AI DevOps tools are built the same. Here is what matters:
| Criteria | What to Check | Why It Matters |
| -------------------- | ----------------------------------------------- | ------------------------------- |
| Approval gates | Does the assistant ask before executing? | Production safety |
| Local-first security | Are credentials stored locally only? | Compliance and client contracts |
| Multi-server support | Can you manage all servers from one view? | Eliminates context switching |
| File management | Is there a GUI, or only SFTP? | Non-DevOps team members |
| Monitoring | Built-in, or separate tool? | Consolidation vs fragmentation |
| AI provider choice | Locked to one provider, or bring your own? | Cost and data control |
| No server agents | Does it require installing software on servers? | Deployment friction |
| Pricing | Per-user or flat rate? | Team scaling costs |
### How to Implement AI Safely in Existing DevOps Workflows [#how-to-implement-ai-safely-in-existing-devops-workflows]
**Rule 1:** Never auto-execute in production. AI should suggest, humans should approve. This is non-negotiable for production environments.
**Rule 2:** Start with non-destructive operations. Use AI for diagnostics and monitoring first. Move to remediation commands only after your team trusts the tool.
**Rule 3:** Keep credentials local. If a tool syncs your SSH keys to the cloud, it creates a security surface you do not control. Local-first is not just a feature; it is a compliance requirement for many teams.
**Rule 4:** Train your team. AI-assisted tools only work if people use them. Spend 30 minutes walking the team through the AI terminal, file manager, and monitoring dashboard. The ROI comes from adoption, not just installation.
**Rule 5:** Keep the terminal available. Intelligent assistance is for the routine. The terminal is for the complex. Your tool should offer both.
### Getting Started with CtrlOps in Your DevOps Stack [#getting-started-with-ctrlops-in-your-devops-stack]
Prefer to watch the walkthrough? Here is the full setup - download, activation, adding your first server, and running your first AI-assisted command - in under three minutes:
Or follow the written steps below:
### Download CtrlOps [#download-ctrlops]
Download from [ctrlops.io](https://ctrlops.io/), available for Mac, Windows, and Linux.
### Activate Account [#activate-account]
Activate with your license key ([1 month free trial](/pricing), no credit card required).
### Add Your Server [#add-your-server]
Add your server name, enter the IP, and choose your SSH key or upload a `.pem` file.
### Connect AI Provider [#connect-ai-provider]
Connect your AI provider and add your OpenAI, Gemini, or Claude API key for context-aware assistance.
### Start Troubleshooting [#start-troubleshooting]
Try the AI Terminal with a simple question: "Check my server health."
From download to first AI-assisted operation: under 5 minutes. For a broader context on industry trends driving this shift, see our collection of [DevOps statistics and trends](https://tsttechnology.io/blog/devops-statistics).
## Future of AI in DevOps [#future-of-ai-in-devops]

AI in DevOps is still in its early chapters. Here is where it is heading and what your team should prepare for.
### From Assistance to Autonomous DevOps Systems [#from-assistance-to-autonomous-devops-systems]
Today's AI in DevOps is firmly in the "assistance" phase: the system generates commands, humans approve. This model works because it balances speed with safety.\
The next phase is supervised autonomy: AI handles routine operations (restarts, scaling, log cleanup) within pre-defined boundaries, escalating only when it encounters something unexpected.
Full autonomy AI managing infrastructure without human involvement is not coming soon, and for good reason. Infrastructure decisions carry business risk. The [DORA 2025 data](https://dora.dev/dora-report-2025/) confirms this: only about a quarter of professionals use AI agent modes, and 61% have never interacted with agentic workflows at all. The industry wants help, not replacement.
### Rise of AI-Native Infrastructure Management Platforms [#rise-of-ai-native-infrastructure-management-platforms]
The current generation of DevOps tools added AI as a feature. The next generation will be built AI-first.
What this means:
* Natural language is the primary interface. Instead of learning a tool's UI, you describe what you need.
* Context-aware operations. AI that understands your entire infrastructure, not just one server at a time.
* Predictive rather than reactive. "Your API cluster will need scaling in 3 days based on traffic patterns" instead of "CPU at 95%."
* Integrated workflows. Monitoring, diagnostics, and remediation in one smooth flow, not three separate tools.
45% of organizations are already investing in new DevOps tools ([JFrog 2025, via Appfire](https://appfire.com/resources/blog/devop-statistics)). The demand for better tooling is there. The AI-native platforms that combine safety with intelligence will win.
### What Teams Should Prepare for Next? [#what-teams-should-prepare-for-next]
Three things to start thinking about now:
1. Skill evolution, not skill replacement. AI will not replace DevOps engineers. They will evolve from command executors to infrastructure strategists. The value shifts from "knowing the commands" to "knowing what needs to happen and verifying the system does it right."
2. Security standards for AI in production. As AI takes on more operational responsibility, security reviews need to include AI tool evaluation. Does it auto-execute? Where are credentials stored? What audit trail exists?
3. Data governance. When you connect an AI to your servers, what data does it see? Where does it go? Local-first tools that keep data processing on your machine (or through your own API keys) minimize exposure.
The teams that adopt AI-assisted DevOps now, while keeping humans in the loop, will be best positioned for whatever comes next. They will have the workflows, the trust, and the experience to take advantage of each new capability as it emerges.
## Conclusion [#conclusion]
The shift from manual server management to AI-assisted DevOps is not a trend you can afford to watch from the sidelines. The data is clear: adoption is near-universal across tech, productivity gains are measurable, and weekly time savings stack up fast for teams using AI tools.
However, the real story is not in the statistics. It is in the daily experience of teams that stopped running htop in five terminal windows and started asking an AI assistant, "What is wrong with my server?" It is the frontend developer who resolved a production incident at 2 AM without calling the DevOps lead. It is the startup founder who deployed their app in 5 minutes instead of 45.
The teams thriving in 2026 are not the ones with the most DevOps engineers. They are the ones with the best tools that centralize access, provide AI assistance with human oversight, and make server operations visible and manageable for everyone on the team.
AI has already changed DevOps. The real question is whether your team adopts it now or waits for a 3 AM incident to force the shift.
## Frequently Asked Questions (FAQs) [#frequently-asked-questions-faqs]
AI in DevOps means using **artificial intelligence** to assist with server management tasks, diagnostics, deployment, monitoring, and troubleshooting, while **keeping humans in the decision loop**. It matters in 2026 because infrastructure complexity has outpaced team capacity. Adoption is now the norm across the tech industry, and teams that do not build AI-assisted workflows fall behind in **speed and reliability**.
The five key advantages:
1. **Faster incident resolution** (from hours to minutes)
2. **Reduced manual errors** through approval-based command execution
3. **Centralized visibility** across all servers
4. **Lower dependency on terminal expertise**
5. **Significant time savings** (roughly 10+ hours back per developer each week)
An AI terminal assistant lets you describe server problems or tasks in **plain English** and generates the appropriate shell commands. Unlike auto-running AI agents, it **shows you what it will execute before it runs**. This helps DevOps engineers diagnose issues faster, run complex command sequences without memorizing flags, and enables non-expert team members to **troubleshoot independently**.
AI reduces errors in three ways. First, it **eliminates typos** by generating correct commands automatically. Second, **approval gates** let you review commands before execution, catching mistakes before they happen. Third, **centralized dashboards** prevent wrong-server incidents because servers are clearly named and identified.
**No.** AI in DevOps replaces manual tasks, **not people**. It handles repetitive operations, diagnostics, routine commands, and monitoring, so engineers focus on **strategic decisions**. Industry data consistently shows professionals want AI assistance with **human judgment**, not autonomous execution.
CtrlOps uses an **approve-before-execute model**: AI generates commands, but **nothing runs without your click**. All credentials are stored locally with **AES-256 encryption**, no cloud sync, no third-party access. This **local-first approach** meets strict compliance requirements, including **SOC2 and HIPAA**.
Based on typical workflows, teams save **80-85%** on daily server operations. Checking health drops from 15-20 minutes to **1 minute**. Deployments drop from 15-30 minutes to **5 minutes**. Incident resolution drops from 30-90 minutes to **5-10 minutes**. Across a month, this translates to **20-40 hours saved** per team member.
Yes, when implemented correctly. The critical safety measure is the **approval gates**. AI should **suggest commands, not auto-execute them**. **Local-first credential storage** prevents third-party breaches. Encrypted data at rest (**AES-256**) protects against local compromise.
A small but growing group. The bring-your-own-key model means **you** pay your AI provider directly (OpenAI, Anthropic, Google Gemini, or any OpenAI-compatible endpoint), the tool **routes through your account**, and your prompts and server context never train someone else's model.
CtrlOps is one of the few AI DevOps tools built this way - connect any OpenAI-compatible provider and you control the model, the cost, and the data residency. Warp also supports BYO key on its paid tiers. GitHub Copilot and most enterprise SaaS platforms (Datadog, GitLab Duo) do **not** offer BYO - you use their backend and pay per seat.
Why this matters for production teams: BYO keys let you stay inside an existing SOC2 / HIPAA / DPA boundary instead of adding a new vendor relationship for every AI feature you adopt.
GitHub Copilot and ChatGPT are **code assistants**. They generate code in your editor, answer questions in a browser tab, and never connect to your servers. They don't know your CPU load, disk usage, or running processes - which means every suggestion is generic.
CtrlOps is a **server operations assistant**. The AI Terminal connects to a live SSH session, reads the actual server state, and generates commands grounded in that context. You still review and approve before anything runs, but the suggestions are specific to *your* server, not the average internet server.
Use Copilot or ChatGPT to write a deployment script. Use CtrlOps to run it, monitor it, and debug it when it fails at 2 AM.
That's actually the strongest use case. Small teams without a dedicated DevOps engineer are exactly who get hit hardest by manual server work - and who benefit most when AI handles the diagnostic and command-generation overhead.
What changes for a small team:
* **Frontend developers** can debug a production 502 without paging anyone
* **Founders** can deploy a hotfix in 5 minutes without remembering Linux flags
* **Junior engineers** can resolve incidents at 2 AM with approval-gated guidance
The approval gate is the safety net: the AI generates the commands, the human approves them, and learning happens on every run. Over a few weeks, the team builds genuine server fluency instead of staying dependent on one senior engineer.
---
# 3 AI Terminal Approaches for Server Management Compared (2026) (/blog/ai-terminal-tools-server-management)
Author: Daxesh Italiya | Published: 2026-07-25 | Tags: AI Terminal, Server Management, Termius AI, Kiro CLI, AI Terminal Comparison | Reading Time: 9 min read
> We tested Termius AI, Kiro CLI, and CtrlOps for server management. See which AI terminal keeps servers clean with approval-gated, desktop-first automation.
Three AI terminal tools now handle server management through natural language: Termius AI suggests commands inside your SSH session, Kiro CLI runs as an autonomous agent on the server, and CtrlOps runs AI on your desktop and sends only approved commands to the server.
The key difference is where the AI runs. That decision affects your security footprint, compliance posture, and how much manual work remains. Here is how all three compare across real deployment tasks.
## AI Terminal Approaches for Server Management [#ai-terminal-approaches-for-server-management]
Three AI terminals, three different architectures. The right choice depends on how much automation you need and where you want the AI to run.
| Capability | Termius AI | Kiro CLI | CtrlOps |
| ---------------------------------------- | ----------------------------------------- | -------------------------------------- | --------------------- |
| Command generation from natural language | Yes | Yes | Yes |
| Multi-step autonomous execution | No (beta only) | Yes | Yes |
| Runs outside the server | No | No | **Yes** |
| Live web search for current docs/CVEs | No | No | **Yes** |
| No software installed on server | Yes | No | **Yes** |
| Step-by-step approval with explanations | No | No | **Yes** |
| Post-execution summary | No | No | **Yes** |
| BYOK AI model | No | No | **Yes** |
| MCP server integration | No | Yes | **Yes** |
| Mobile access | Yes | No | No |
| **Pricing** | **Free AI autocomplete; Pro from $10/mo** | **Free tier (50 credits); Pro $20/mo** | **$7/mo, Free trial** |
Prefer to watch instead? We ran all three side by side on real server tasks - the full comparison in under 7 minutes:
***
## How Does Termius AI Handle Server Management? [#how-does-termius-ai-handle-server-management]
[Termius AI](https://termius.com/index.html) converts plain English into shell commands inside an active SSH session. Type "show me nginx logs" and Termius generates the right command instantly.
No syntax memorization needed for tools like `grep`, `find`, or `journalctl`.

The suggestion appears inline with a risk label and a run count, but you still press enter yourself and you still run the next command yourself.
### What works well: [#what-works-well]
* Converts plain English to terminal commands inside the active session
* Works on desktop and mobile with credential sync across devices
* No additional software installed on your servers
* Trusted SSH client with years of stability
### Where it falls short for server management: [#where-it-falls-short-for-server-management]
1. No error recovery.
2. Single-command only.
3. No live web search.
4. AI Agent not publicly available yet.
***
## How Does Kiro CLI Handle Server Management? [#how-does-kiro-cli-handle-server-management]
[Kiro CLI](https://kiro.dev/cli/) takes a different approach entirely. Instead of suggesting commands, it acts as a full AI agent that executes entire workflows from a single prompt.
A request like "Install Docker first, then run Nginx using Docker" triggers the complete process automatically.
Kiro asks for permission before each critical operation, then handles sub-steps on its own. If a permission error occurs, it adds `sudo` and retries without asking.

A single "install nginx" prompt becomes a chain of shell calls. Kiro notices the stale package list, runs `apt-get update` first, and reports back that nginx 1.28.3 is installed and enabled on boot. Fast, but every one of those commands ran on the server before you saw it.
Kiro is built and operated by AWS. The CLI brings agentic AI into the terminal with support for custom agents, MCP servers, and tools like bash execution, file system access, and AWS service integration. You can create specialized agents for different workflows: DevOps, code review, or debugging.
### What works well: [#what-works-well-1]
* Executes complete multi-step workflows from a single prompt
* Asks permission before critical operations (installing packages, running containers)
* Handles permission errors automatically by adding `sudo` and retrying
* Custom agent configurations for scoped tool access and permissions
* MCP server support for external integrations (AWS Terraform MCP, EKS MCP)
* Automates infrastructure-as-code generation, CI/CD pipelines, and Kubernetes deployments
### Where it falls short for server management: [#where-it-falls-short-for-server-management-1]
1. Runs directly on the server.
2. Requires AWS CLI, Python, Terraform, and kubectl installed on the server.
3. Permission without explanation.
4. No live web search.
**Reality check:**
Running an AI agent directly on production means the agent has the same access as your SSH session. Every dependency installed for the agent increases the attack surface. If your organization has compliance requirements around server-side software, agent-on-server architectures need additional security review.
***
## How Does CtrlOps Handle Server Management? [#how-does-ctrlops-handle-server-management]
[CtrlOps](https://ctrlops.io/) runs as a desktop application on your machine, not on the server. The AI processes requests locally and sends only approved commands through your SSH connection.
No AI runtime, no dependency stack, no agent software on production servers.

Ask "check memory and CPU" and the AI plans the steps. Every command stops at an approval gate first, showing a read/write indicator and a plain-English reason for why it is needed. Nothing touches the server until you approve it.
CtrlOps costs $7/month per user with unlimited servers. Every account starts with a [1 month free trial, no credit card required](https://ctrlops.io/pricing). It supports macOS (Apple Silicon + Intel), Windows, and Linux.
### What works well: [#what-works-well-2]
* Each command shows the exact code, read/write indicator, and plain-English explanation. You approve each step individually.
* Post-execution summary after completing all steps
* Live [web search](https://ctrlops.io/docs/modules/ai-terminal/web-search) through Tavily, Brave, or DuckDuckGo for current CVEs, package versions, and security advisories
* [MCP server integration](https://ctrlops.io/docs/modules/ai-terminal/mcps) with Context7, GitHub, Filesystem, and custom servers
* [Node.js deployment](https://ctrlops.io/blog/deploy-nodejs-app-linux-vps) drops from 30-45 minutes to 5 minutes
### Where it falls short for server management: [#where-it-falls-short-for-server-management-2]
1. No mobile app.
2. No Kubernetes or container orchestration.
3. No serverless support.
**Bottom line:**
CtrlOps is the strongest option for teams that want full AI automation without installing anything on production servers. Every command is explained and approved individually. But if you need mobile access or Kubernetes orchestration, pair it with a mobile SSH client or use Kiro CLI for container workflows.
***
## What Does an AI Terminal for Server Management Need? [#what-does-an-ai-terminal-for-server-management-need]
An AI terminal for server management needs five things to be production-ready: natural language command generation, multi-step workflow execution, operation outside the server's attack surface, pre-execution transparency, and access to live security advisories.
Most tools in 2026 nail the first capability. The real differences show up in the other four.
The [2025 Verizon DBIR](https://www.verizon.com/business/resources/reports/2025-dbir-data-breach-investigations-report.pdf) found that vulnerability exploitation as an initial access vector grew 34% year-over-year. Unnecessary server-side software is a measurable risk, not a theoretical one.
***
## Why Does It Matter Where the AI Runs? [#why-does-it-matter-where-the-ai-runs]
Where the AI runs determines your security footprint and blast radius. A desktop-first architecture keeps AI off production servers. An agent-on-server approach gives the AI the same access level as your SSH session.
When AI runs on the server, it has access to files, environment variables, secrets, and services. Every dependency (CLI tools, runtimes, libraries) widens the attack surface. When AI runs on your desktop, the server receives only the commands you approve.
For freelancers managing client servers under NDAs, agencies handling production across multiple clients, and startups where the same person writes code and manages servers, this distinction directly affects what you can promise clients about infrastructure security.
Ughareja Infotech chose on exactly that basis. Running six servers for ecommerce clients, its founder moved off Termius because AI commands left his machine at all - [the migration took under two minutes](/case-studies/ughareja-infotech), and the AI now runs locally on his own key.
***
## Which AI Terminal Approach Should You Choose? [#which-ai-terminal-approach-should-you-choose]
**Choose Termius AI if** you want AI command suggestions inside a familiar SSH client.
You already know what to do and want faster syntax generation. You value mobile access and cross-device credential sync. Termius fits engineers who prefer full manual control.
**Choose Kiro CLI if** you need full agent automation and are comfortable with AI running on your infrastructure.
You are in the AWS ecosystem and want agents that generate Terraform scripts, manage EKS clusters, and automate CI/CD pipelines. The server-side dependency footprint is acceptable for your use case.
**Choose CtrlOps if** you want end-to-end automation that keeps servers clean.
You need every command explained with individual step-by-step approval, live web search for current security advisories, and local-only credential storage.
You [manage multiple servers without losing control](https://ctrlops.io/blog/manage-multiple-servers-without-losing-control) and value transparency without sacrificing speed.
***
## Conclusion [#conclusion]
AI is becoming essential for server management in 2026. But when it interacts with production infrastructure, automation without visibility becomes a liability.
Termius AI keeps things safe with single-command generation. Kiro CLI delivers powerful agent automation at the cost of a server-side software footprint. CtrlOps combines multi-step automation with a desktop-first architecture that requires individual approval for every command and checks current security advisories through live web search.
If your team values keeping AI off production servers while maintaining human oversight, a desktop-first architecture offers the strongest balance between automation and control.
***
An AI terminal for server management lets you manage remote servers using natural language instead of memorized shell commands. You describe what you need ("install Nginx and configure it as a reverse proxy") and the AI generates the commands. Some tools only suggest commands. Others execute complete multi-step workflows automatically.
Safety depends on the architecture. Tools that run AI agents directly on the server give the agent the same access as your SSH session, increasing the attack surface. Desktop-first tools like CtrlOps run the AI locally on your machine, sending only the commands you approve through the SSH connection. No AI runtime or dependencies are installed on the server.
CtrlOps runs as a desktop application on macOS, Windows, or Linux. The AI processes your request locally, generates a step-by-step execution plan, and waits for approval on each step. Only approved commands travel to the server through the SSH connection. No AI software or credentials are installed on or synced to the server.
Termius announced an AI Agent in May 2026 that can connect to infrastructure and execute commands across multiple terminals. This feature is in closed beta. Termius also offers Gloria, a cloud-based DevOps agent for infrastructure tasks. The publicly available AI feature is Autocomplete, which suggests commands but does not execute multi-step workflows.
Kiro CLI is an AI-powered terminal tool built by AWS. It brings agentic AI into the terminal with support for custom agents, MCP servers, and bash execution. The agent runs directly on the server where Kiro is installed, requiring dependencies like AWS CLI, Python, and Terraform on the infrastructure.
Yes. CtrlOps includes live web search with Tavily, Brave, and DuckDuckGo. Ask the AI to check whether the software version you are installing has known CVEs. It searches current security advisories before continuing. Server commands still go through the approval gate regardless of search results.
CtrlOps costs $7/month per user with unlimited servers, with a 1 month free trial and no credit card required. Termius offers free AI autocomplete with Pro plans starting at $10/month (billed annually). Kiro CLI offers a free tier with 50 credits and Pro starting at $20/month.
Skip AI terminals if you manage a single personal server with occasional updates. The overhead is not worth it. Also skip them for container orchestration (use kubectl or Lens), serverless deployments (use provider CLIs), or if your workflow is entirely infrastructure-as-code with tools like Terraform or Pulumi.
Yes. Kiro CLI and its dependencies (AWS CLI, Python, Terraform, kubectl) need to be installed on each server you manage. This gives the agent deep access to the server's files, software, and system resources. Some teams are not comfortable with this level of access on production servers.
---
# 8 Best SSH Clients for Linux in 2026 (Free & Paid) (/blog/best-ssh-client-linux)
Author: Hiren Kalariya | Role: Co-Founder & CEO, TST Technology | Published: 2026-06-18 | Updated: 2026-07-26 | Tags: SSH client for Linux, OpenSSH alternatives, Linux terminal, server management, AI terminal | Reading Time: 26 min read
> We tested 8 SSH clients for Linux across real workflows - OpenSSH, Termius, Tabby, Warp, and CtrlOps. Compare features, security, and pricing for 2026.
The best SSH client for Linux in 2026 is **CtrlOps** for anyone managing more than one server - it's the only tool on this list that combines SSH, a GUI file manager, live infrastructure monitoring, AI diagnostics, and one-click deployment in a single desktop app ($7/user/mo). For a free CLI-first workflow, **OpenSSH** (pre-installed on most distros) is still the default. For cross-device credential sync, choose **Termius**. For an open-source modern terminal, choose **Tabby**. For AI-assisted local coding, choose **Warp**.
## 8 Best SSH Clients for Linux in 2026 [#8-best-ssh-clients-for-linux-in-2026]
The 8 best SSH clients for Linux in 2026 are CtrlOps (all-in-one server management), OpenSSH (pre-installed CLI), Termius (cross-device sync), Tabby (open-source modern terminal), Warp (AI-first coding terminal), Remmina (multi-protocol), PuTTY (lightweight legacy), and SecureCRT (enterprise compliance).
Here's how each handles real server tasks:
| Tool | Best For | Price | AI | File Manager | Local Credentials |
| ----------- | -------------------------------- | ---------------------------- | ---------------------- | --------------------- | ----------------- |
| **CtrlOps** | **All-in-one server management** | **$7/user/mo (1 mo free)** | **✓ Approval-gated** | **✓ Full GUI** | **✓ Local-only** |
| OpenSSH | CLI-first SSH access | Free (usually pre-installed) | ✗ | ✗ | ✓ Local |
| Termius | Cross-device sync | $10/user/mo | Partial (autocomplete) | ✓ SFTP | ✗ Cloud |
| Tabby | Open-source modern terminal | Free | ✗ | ✓ SFTP/Zmodem | ✓ Local |
| Warp | AI-first coding terminal | $20/mo | ✓ Auto-run | ✗ | ✗ Cloud |
| Remmina | Multi-protocol (RDP + VNC + SSH) | Free | ✗ | ✗ | ✓ Local |
| PuTTY | Lightweight legacy client | Free | ✗ | ✗ | ✓ Local |
| SecureCRT | Enterprise compliance | \~$119/license | ✗ | ✗ (SecureFX separate) | ✓ Local |
Prefer to watch instead? The full comparison - all eight tools, the deploy race, and the SSH key security question - in about 7 minutes:
### 1. CtrlOps: Best for AI-Powered Server Management [#1-ctrlops-best-for-ai-powered-server-management]
[CtrlOps](https://ctrlops.io/) takes a fundamentally different approach from every other tool on this list.

Instead of being a better terminal, it replaces your entire server management stack: terminal, file manager, monitoring dashboard, and deployment system. All-in-one desktop app.
**Pros of CtrlOps:**
* **Named server cards:** Connect to "Prod-Backend" or "Client-XYZ-Staging" instead of grepping through `~/.ssh/config`. One click, you're in.
* **Full [GUI file manager](https://ctrlops.io/docs/modules/file-manager):** Upload, download, edit, and delete remote files without `scp` commands or a separate SFTP tool. Drag-and-drop works.
* **Approval-gated AI terminal:** Type "why is my server slow?" and get diagnostic commands shown before anything runs. You review, approve, then execute. No auto-run.
* **Streamlined [application deployment](https://ctrlops.io/docs/modules/deployment):** Pick your stack (React, Next.js, Node.js), link GitHub, set environment variables. CtrlOps handles cloning, dependencies, PM2, Nginx, and Certbot SSL automatically.
* **Instant infrastructure monitoring:** CPU, RAM, disk, and running processes visible inside the app. No more `htop` in a separate window.
* **Local-first security:** Credentials, SSH keys, and server configs stay on your machine. AES-256 encrypted. No cloud sync.
* **[Script Directory](https://ctrlops.io/docs/modules/ai-terminal/scripts):** Save reusable scripts with `{{variable}}` placeholders. One click runs them across every server.
* **MCP Server integration.** Connect Context7, GitHub, Filesystem, or custom MCP servers via JSON config. The AI reads your actual codebase before generating commands.
**CtrlOps Limitations:**
* No mobile app
* No serverless or Kubernetes support
* No push notifications yet (on roadmap)
**Pricing:** $7/user/month or $70/user/year (unlimited servers). [1 month free trial](https://ctrlops.io/pricing), no credit card required.
**Platforms:** Linux (Ubuntu, Fedora, Debian, Arch), macOS (Apple Silicon + Intel), Windows.
Softnoesis runs its older DevOps servers exactly this way, reaching fifteen to twenty of them from one platform with per-server CPU and RAM visibility - [a setup its founder finished in about six minutes](/case-studies/softnoesis).
> "The fact that i dont need to install any agent on my servers sold me immediately. Got it running on our staging env and already caught 2 issues before they became outages. will be moving prod over soon."
>
> * Srushti Vasani, [Product Hunt review](https://www.producthunt.com/products/ctrlops?comment=5382621)
**Bottom line:** For teams that also need Windows coverage, check our [best SSH clients for Windows](https://ctrlops.io/blog/best-ssh-clients-windows) guide.
***
### 2. OpenSSH: Best Pre-Installed CLI Client [#2-openssh-best-pre-installed-cli-client]
[OpenSSH](https://www.openssh.com/) is likely already on your machine. Most major desktop Linux distributions ship it by default (requiring no download or setup).

For CLI-first developers who live in the terminal, OpenSSH is the foundation every other tool builds on.
**Pros of OpenSSH:**
* **Pre-installed** on most desktop distributions (Ubuntu, Fedora, Debian); on minimal installs like Arch, you add it via your package manager.
* **`~/.ssh/config` file:** define named hosts, custom ports, and identity files for one-command connections
* **Rock-solid security:** 25+ years of community audits, constant patches, the protocol standard itself
* **Scriptable:** pipes, aliases, `ssh-agent`, ProxyJump. Automate anything in bash
* **Port forwarding and tunneling:** local, remote, dynamic SOCKS proxying built in (don't have the flags memorized? Our free [SSH tunnel generator](/tools/ssh-tunnel-generator) writes the exact command)
* **Zero overhead:** no GUI, no Electron, no RAM footprint beyond the connection
**OpenSSH Limitations:**
* **No GUI.** Everything is command-line. File transfers mean `scp` or `rsync` in a separate command.
* **No server directory.** You maintain `~/.ssh/config` by hand. No visual grouping, no search.
* **No AI.** Blank cursor, blank screen, your knowledge or nothing.
* **No monitoring dashboard.** Run `htop`, `df -h`, `free -m` one at a time.
* **No deployment automation.** Every `git pull` and `pm2 restart` is manual.
* **Config syntax errors are silent.** A typo in `~/.ssh/config` fails without a useful error message.
**Pricing:** Free, open-source (BSD license).
**Platforms:** Pre-installed on most desktop Linux distributions. Also available on macOS, Windows, and BSD.
OpenSSH is the right baseline for 1 - 2 servers with a scripting-first workflow. At 5+ servers with daily file transfers and production debugging, the config overhead outweighs the simplicity.
**Bottom line:** OpenSSH does one thing perfectly: secure shell connections. But most developers who "use OpenSSH" are actually using OpenSSH plus `scp` plus `htop` plus a notes file plus a cloud dashboard. Five tools duct-taped together. That's the stack a purpose-built client replaces.
***
### 3. Termius: Best for Cross-Platform Teams [#3-termius-best-for-cross-platform-teams]
[Termius](https://termius.com/) is the most polished dedicated SSH client on the market.

It syncs servers, credentials, and snippets across Mac, Windows, Linux, iOS, and Android. The only tool on this list with full-featured mobile apps.
**Pros of Termius:**
* **Cross-device sync:** servers and credentials follow you everywhere, E2E encrypted
* **Clean UI:** named hosts, groups, tags, one-click connect
* **Built-in SFTP:** file transfers without a separate tool
* **AI-powered autocomplete:** suggests commands as you type
* **Mobile apps:** SSH from your phone during a production incident
* **Team vault:** shared server access with role-based controls
* **Linux support:** fully compatible via native .deb, Snap, and AppImage installations.
**Termius Limitations:**
* **SSH keys sync to Termius's cloud.** E2E encrypted, yes, but they live on third-party infrastructure. Some client contracts prohibit this.
* **No infrastructure monitoring.** You SSH in and run `htop` manually.
* **No one-click deployment.** Manual repo clones, PM2, Nginx setup.
* **AI is autocomplete, not diagnostics.** Suggests completions, doesn't understand server state.
* **Pricing scales per user.** Pro: $10/user/month. Team: $20/user/month. 5-person Team plan costs $100/month ($1,200/year).
**Pricing:** Free (Starter, local vault only). Pro: $10/user/month. Team: $20/user/month. Business: $30/user/month (all when billed annually).
**Platforms:** Linux, macOS, Windows, iOS, Android.
Termius wins if you need the same SSH setup on every device, including your phone. The trade-off: cloud credential storage and per-user pricing that gets expensive at team scale. See [CtrlOps vs Termius](https://ctrlops.io/compare/ctrlops-vs-termius) for a direct comparison. If you're exploring [alternatives to Termius](/blog/termius-alternatives), we've compared the top options across all platforms.
***
### 4. Tabby: Best Open-Source Modern Terminal [#4-tabby-best-open-source-modern-terminal]
[Tabby](https://tabby.sh/) is a cross-platform, open-source terminal that modernizes SSH with tabs, split panes, a plugin ecosystem, and a built-in connection manager.

No subscription. No account required.
**Pros of Tabby:**
* **Free and open-source** (MIT license), no feature gates, no accounts
* **Cross-platform:** Linux, macOS, Windows with an identical interface
* **Built-in SSH client** with profiles, SFTP, Zmodem transfers, key management
* **Plugin ecosystem:** extend with community-built plugins
* **Split panes and workspaces:** save complex layouts as profiles
* **Encrypted credential storage:** local vault with master passphrase
* **Modern UI:** themes, ligatures, GPU-accelerated rendering
* **Linux-native packages:** .deb, .rpm, AppImage, Snap
**Tabby Limitations:**
* **Resource-heavy.** Electron-based, uses more RAM than OpenSSH or a native terminal.
* **No AI features.** No command generation, no diagnostics.
* **No monitoring or deployment.**
* **Learning curve.** Extensive config options: strength for power users, barrier for beginners.
* **Occasional stability issues** with certain plugin combinations.
**Pricing:** Free, open-source (MIT license).
**Platforms:** Linux, macOS, Windows.
Best choice for developers who want open-source with no vendor lock-in.
Significantly more capable than PuTTY on Linux. The trade-off is higher memory usage and zero AI or server management features.
***
### 5. Warp: Best AI-First Coding Terminal [#5-warp-best-ai-first-coding-terminal]
[Warp](https://www.warp.dev/) is the most well-funded AI terminal on the market. Backed by Sequoia Capital with [$73M+ in funding](https://sacra.com/c/warp/), built in Rust.

Block-based output, IDE-like editing, and AI Agent Mode that converts natural language into shell commands.
**Pros of Warp:**
* **AI Agent Mode:** type natural language, get shell commands generated and executed
* **Block-based output:** each command result is a selectable, searchable block
* **IDE-like editing:** select, copy, edit previous commands like text
* **Rust-based performance:** GPU-accelerated, no Electron lag
* **Warp Drive:** save and share command sequences across teams
* **BYOK support:** bring your own OpenAI, Anthropic, or Google API key
* **Linux support:** native .deb and .rpm packages
**Warp Limitations:**
* **It's a coding terminal, not a server manager.** No server directory, no file manager, no monitoring, no deployment.
* **AI auto-runs commands by default.** On production, one misinterpreted prompt can cause real damage. No approval gate.
* **Cloud account required.** Can't use Warp without signing in.
* **Free tier is limited.** 150 AI credits for 2 months, then 75/month. Build plan: $20/month with 1,500 credits.
* **Not designed for multi-server fleet management.**
**Pricing:** Free (75 - 150 AI credits/month). Build: $20/month. Business: $50/user/month.
**Platforms:** Linux, macOS, Windows.
Warp is the best terminal on Linux for local development. For remote server management, Warp's AI lacks server context and auto-executes without review. See [CtrlOps vs Warp](https://ctrlops.io/compare/ctrlops-vs-warp) for a direct comparison.
**Reality check:** Any AI terminal that auto-runs commands without a review step is a developer-machine feature, not a server-management feature. On a production server with real traffic, the approval gate in CtrlOps stops 2 AM mistakes from becoming outages.
> "The approve before execute thing is what sold me. Every other AI tool just runs stuff, and you find out what happened after."
>
> * Bhautik Kapadiya, [Product Hunt review](https://www.producthunt.com/products/ctrlops?comment=5381266)
***
### 6. Remmina: Best Multi-Protocol Client for Linux [#6-remmina-best-multi-protocol-client-for-linux]
[Remmina](https://remmina.org/) is a Linux-native remote desktop client that supports SSH alongside RDP, VNC, SPICE, and NX in one tabbed interface.

Pre-installed on many Ubuntu and GNOME-based distributions. Built for sysadmins who manage mixed environments.
**Pros of Remmina:**
* **Multi-protocol in one app:** SSH, RDP, VNC, SPICE, NX, XDMCP
* **Pre-installed on Ubuntu** and many GNOME-based distributions
* **Tabbed interface:** multiple connections in one window
* **Connection profiles:** save and organize servers with groups and folders
* **Plugin architecture:** extend protocol support via community plugins
* **Free and open-source** (GPL-2.0)
* **GTK-native:** no Electron, lightweight on Linux
**Remmina Limitations:**
* **SSH is secondary.** It's a remote desktop client first. SSH terminal is basic.
* **No AI features.** Manual command execution only.
* **No file manager.** No SFTP browser, no drag-and-drop transfers.
* **No monitoring or deployment.**
* **No cloud sync.** Connection profiles are local, no cross-device sharing.
* **Linux-only in practice** - macOS support is experimental and unofficial; no real Windows version.
**Pricing:** Free, open-source (GPL-2.0).
**Platforms:** Linux (macOS support is experimental/unofficial; Windows is not supported).
The right pick for sysadmins who need RDP, VNC, and SSH in one app on Linux.
Not the right pick if SSH is your primary use case. The terminal experience is basic compared to dedicated SSH clients.
***
### 7. PuTTY: Best Lightweight Legacy Client [#7-putty-best-lightweight-legacy-client]
[PuTTY](https://www.chiark.greenend.org.uk/~sgtatham/putty/latest.html) has been available since 1999. While it's best known as a Windows SSH client, it runs on Linux too, installable via `apt` or `dnf`.

For a quick GUI-based SSH connection without configuring `~/.ssh/config`, PuTTY is the simplest graphical option.
**Pros of PuTTY:**
* Quick graphical SSH client with zero learning curve: enter an IP, connect
* Supports SSH, Telnet, SCP, and raw serial connections
* Tiny footprint, lightweight on system resources
* 25+ years of security audits and community trust
* Completely free, open-source
* Available in most Linux package managers (`apt install putty`)
**PuTTY Limitations:**
* **No named server directory.** Sessions stored individually, no grouping or search.
* **No file transfer.** Upload a config? Open a second terminal and `scp` it.
* **No AI, no monitoring, no deployment.** You're alone with a blank terminal.
* **No tabs.** Each server is a separate PuTTY window.
* **Minimal advantage over OpenSSH on Linux.** Most Linux developers already have a better terminal built in.
* **UI feels dated.** The GTK port looks like 2005.
**Pricing:** Free, open-source (MIT).
**Platforms:** Linux, macOS, Windows (primary).
PuTTY makes more sense on Windows, where it dominated for two decades. On Linux, OpenSSH is pre-installed and more capable. For modern options, see [PuTTY alternatives for Windows](https://ctrlops.io/blog/putty-alternatives-windows).
The only reason to use PuTTY on Linux: you want a GUI for SSH without learning `~/.ssh/config` syntax. If you want the head-to-head [CtrlOps vs PuTTY](https://ctrlops.io/compare/ctrlops-vs-putty) comparison, we break down where each one fits.
**Bottom line:** On Linux, PuTTY solves a problem that doesn't exist. OpenSSH is pre-installed, Tabby and Termius offer better GUIs. PuTTY stays relevant on Windows. On Linux, it's a nostalgia pick. See [modern PuTTY, Webmin, and ServerPilot alternatives](https://ctrlops.io/blog/putty-webmin-serverpilot-alternatives).
***
### 8. SecureCRT: Best for Enterprise & Compliance [#8-securecrt-best-for-enterprise--compliance]
[SecureCRT](https://www.vandyke.com/products/securecrt/) by VanDyke Software has been the enterprise SSH client since 1995.

FIPS 140-2 validated. Advanced scripting in Python, VBScript, and Perl. Likely already on your organization's approved software list in government, defense, or healthcare IT.
**Pros of SecureCRT:**
* **31 years of reliability:** enterprise trust built over decades
* **FIPS 140-2 compliance:** meets government security requirements
* **Advanced scripting:** automate workflows with Python, VBScript, Perl
* **Multi-protocol:** SSH, Telnet, Serial
* **Session management:** tabbed sessions, saved layouts, detailed logging
* **Smart card and PKI support:** hardware-based authentication
* **Linux support:** native .deb and .rpm packages
**SecureCRT Limitations:**
* **No AI features.** Manual command execution only.
* **Legacy UI.** Functional but dated.
* **Expensive for small teams.** \~$119/license one-time, plus optional annual maintenance. SecureFX (file transfer) sold separately.
* **No monitoring, no deployment.**
* **Overkill for most developers.** If you don't need FIPS or scripting, you're paying for unused features.
**Pricing:** \~$119/license one-time (includes 1 year of updates).
**Platforms:** Linux, macOS, Windows.
The right tool if your organization requires FIPS 140-2 or advanced scripting.
For freelancers and startups, you're paying enterprise prices for unused features. See [CtrlOps vs SecureCRT](https://ctrlops.io/compare/ctrlops-vs-securecrt) for a comparison.
***
## How Do All 8 SSH Clients Compare Feature-by-Feature? [#how-do-all-8-ssh-clients-compare-feature-by-feature]
Across 11 capabilities, CtrlOps is the only SSH client that combines a [named server directory](/features/multi-server-management), a full GUI file manager, infrastructure monitoring, approval-gated AI, and one-click deployment in one app. OpenSSH, Tabby, Remmina, and PuTTY are free but cover only the terminal; Termius adds SFTP and cloud sync at $10/user/month; Warp adds auto-run AI at $20/month.
Here's the full side-by-side across every capability that matters for daily server management on Linux.
Not marketing features. Things you actually do.
| Feature | CtrlOps | OpenSSH | Termius | Tabby | Warp | Remmina | PuTTY | SecureCRT |
| ------------------------- | ---------------- | --------------- | --------- | ----------- | ---------- | ------------- | ----------- | ------------------- |
| Named server directory | ✓ | Via config file | ✓ | ✓ | ✗ | ✓ | Partial | ✓ |
| One-click connect | ✓ | ✗ | ✓ | ✓ | ✗ | ✓ | ✓ | ✓ |
| Built-in file manager | ✓ Full GUI | ✗ | ✓ SFTP | ✓ SFTP | ✗ | ✗ | ✗ | ✗ |
| Infrastructure monitoring | ✓ Dashboard | ✗ | ✗ | ✗ | ✗ | ✗ | ✗ | ✗ |
| AI command generation | ✓ Approval-gated | ✗ | Partial | ✗ | ✓ Auto-run | ✗ | ✗ | ✗ |
| One-click deployment | ✓ | ✗ | ✗ | ✗ | ✗ | ✗ | ✗ | ✗ |
| Local credential storage | ✓ AES-256 | ✓ | ✗ Cloud | ✓ | ✗ Cloud | ✓ | ✓ | ✓ |
| Multi-protocol | SSH | SSH | SSH, Mosh | SSH, Serial | SSH | SSH, RDP, VNC | SSH, Telnet | SSH, Telnet, Serial |
| Mobile app | ✗ | ✗ | ✓ | ✗ | ✗ | ✗ | ✗ | ✗ |
| Price (individual/mo) | $7 (1 mo free) | Free | $10 | Free | $20 | Free | Free | \~$119 one-time |
| 5-user team (monthly) | $35 | $0 | $100 | $0 | $100 | $0 | $0 | \~$580 one-time |
*Team pricing based on each vendor's standard team tier as of June 2026: Termius Team at $20/user, Warp Build at $20/user (Warp Business is $50/user).*
The pricing difference matters at team scale.
**Termius and Warp charge per user.** Costs grow linearly with headcount.
**CtrlOps is $7/user/month (or $70/user/year) after a 1 month free trial**, a lower per-seat price that includes monitoring, deployment, and file management you'd otherwise build from separate tools.
**Free tools (OpenSSH, Tabby, Remmina, PuTTY)** cost $0 upfront but add 30 - 40 minutes of daily tool-switching overhead that compounds into real cost.
***
## How We Evaluated 8 SSH Clients for Linux? [#how-we-evaluated-8-ssh-clients-for-linux]
We evaluated 8 SSH clients for Linux across four real-world tasks: connecting to a 5-server fleet on Ubuntu 24.04 and Fedora 40, deploying Node.js apps, debugging a production incident, and transferring config files mid-session. Scored on task performance, not marketing claims.
You're managing five client servers from your Ubuntu workstation. It's 2 AM. A production Node.js app is throwing 502 errors.
You open a terminal tab. Run `ssh root@167.71...` but which IP was the production box again?
You check your notes file. Connect. Run a few diagnostic commands from memory. The config file needs updating.
So you open a second terminal, `scp` the file over, fat-finger the path, retry. Then you open a browser tab to check DigitalOcean's dashboard for CPU spikes.
Three tools. Four context switches. Twenty-five minutes. The client is still calling.
If you're a **freelance developer juggling client servers**, a **startup CTO tired of 45-minute deployments**, or an **agency engineer managing staging and production across projects**: you've lived this.
We compared 8 of the **best SSH clients for Linux** across the same real-world tasks:
* Connecting to a 5-server fleet on Ubuntu 24.04 LTS and Fedora 40
* Setting up and deploying Node.js apps on a DigitalOcean droplet
* Debugging a production incident under time pressure
* Transferring config files mid-session without opening a second tool
***
## What Makes a Great SSH Client for Linux in 2026? [#what-makes-a-great-ssh-client-for-linux-in-2026]
A great SSH client for Linux consolidates your workflow. It minimizes the tabs and tools needed to manage live servers while maintaining strict security standards.

Six criteria separate a useful Linux SSH client from another terminal tab:
**1. Multi-server organization.**
Find and connect to the right server in under 10 seconds. Named hosts, one-click connect, visual grouping by environment. Not raw IPs in a text file or a cluttered `~/.ssh/config`.
**2. Integrated file management.**
Uploading a config shouldn't require a second terminal running `scp` or `rsync`. A built-in file browser eliminates one full context switch per session. (Terminal users: our [scp / rsync command builder](/tools/scp-rsync-command-builder) assembles the exact flags.)
> "The file manager feature is the one nobody talks about, but everyone needs. separate SFTP client is such a pain when you just want to edit one config file."
>
> * Abhishek Akbari, Senior Full-Stack Developer at Torinit, [Product Hunt review](https://www.producthunt.com/products/ctrlops?comment=5381385)
**3. Credential security.**
Where do your SSH keys live: on your machine or a vendor's cloud? For client work and regulated industries, the answer matters. Good [SSH key management](https://ctrlops.io/docs/core/ssh-security) is essential.
**4. AI assistance.**
AI that drafts diagnostic commands can save nearly an hour on unfamiliar environments.
Key distinction: does it auto-run commands or show them for approval first?
**5. Deployment and automation.**
If you manually run `git pull`, `npm install`, `pm2 restart`, and configure Nginx every time you deploy, your SSH client isn't doing enough.
**6. Real price transparency.**
Per-user pricing adds up fast. A $10/user/month tool costs $600/year for a 5-person team. Know the true cost at your team size before committing.
**Bottom line:** The best SSH clients for Linux in 2026 are not just terminals. They're server management tools. Evaluating them purely on "can it open an SSH connection?" solves the wrong problem: your default terminal already does that.
***
## How to Choose the Right SSH Client for Linux? [#how-to-choose-the-right-ssh-client-for-linux]
Choosing the ideal SSH client for Linux comes down to your specific daily tasks and workflow requirements.

No single tool wins every scenario. Here's a decision framework by role and friction.
**You're a developer managing client servers and deploying apps:**
CtrlOps.
Named servers keep client environments organized. Local credentials satisfy NDAs. One-click deployment cuts a 45-minute process to 5 minutes. $7/user/month, see broader [DevOps automation tools](https://ctrlops.io/blog/devops-automation-tools) comparison.
**You're a CLI-first developer who lives in the terminal:**
OpenSSH.
Pre-installed on most distributions. Scriptable. Pairs with `tmux` and `~/.ssh/config` for a zero-overhead workflow. When you outgrow manual config management, look at GUI-based options.
**Your team needs the same setup on every device:**
Termius.
Cross-device sync across Linux, Mac, Windows, iOS, Android. Accept the cloud credential trade-off or verify compatibility with your security requirements first.
**You want open-source with no vendor lock-in:**
Tabby.
Free, MIT-licensed, cross-platform, plugin ecosystem. Heavier on RAM, but far more capable than PuTTY or a default terminal emulator.
**You live in the terminal writing code locally:**
Warp.
AI agent features and IDE-like editing are the best available for local development. Be careful with Agent Mode on production.
**You manage mixed environments (RDP + VNC + SSH):**
Remmina.
One app for every protocol. Pre-installed on Ubuntu. SSH is basic, but the multi-protocol convenience is unmatched on Linux.
**You need enterprise compliance certifications:**
SecureCRT.
FIPS 140-2 validated, advanced scripting, 31 years of enterprise trust.
| Your Situation | Best Pick | Runner-Up |
| --------------------------------- | --------- | ---------------- |
| Freelancer, 5 - 15 client servers | CtrlOps | Termius |
| CLI-first, 1 - 2 servers | OpenSSH | Tabby |
| Cross-platform team | Termius | CtrlOps |
| Open-source advocate | Tabby | Remmina |
| AI-first terminal power user | Warp | CtrlOps |
| Mixed protocol sysadmin | Remmina | SecureCRT |
| Enterprise/compliance | SecureCRT | Termius Business |
| Learning SSH for the first time | OpenSSH | PuTTY |
***
## Why Does the AI Terminal Gap Matter on Linux? [#why-does-the-ai-terminal-gap-matter-on-linux]
The AI terminal gap matters on Linux because the bottleneck was never opening the connection - it's the 20 - 40 minutes you lose Googling errors and copy-pasting commands once you're in. Of the 8 clients here, only CtrlOps and Warp close that gap, and only CtrlOps shows each generated command for approval before it runs.
Linux users already have the most powerful CLI available. That's exactly why this gap is easy to overlook.

The real bottleneck: Googling error messages, reading Stack Overflow posts from 2019, hoping commands still work on your kernel version. Of 8 tools tested, only CtrlOps and Warp help after you're connected.
**With OpenSSH or PuTTY:**
Open a browser. Google the error. Find a Stack Overflow post from 2019. Try a command. Hope it works on Ubuntu 24.04. That loop takes 20 - 40 minutes on a good night.
**With Warp:**
Type the problem in Agent Mode. It generates commands, but auto-runs them. When debugging a live production server late at night, a single mistyped or misunderstood command can easily escalate a minor issue into a major outage.
**With CtrlOps:**
Type the problem in the [AI Terminal](https://ctrlops.io/docs/modules/ai-terminal). It reads your server's current context: CPU, memory, running processes, recent logs.
It generates the right diagnostic commands.
It shows them before anything executes.
You review. Approve. The fix runs.
The difference isn't convenience. It's the 35 minutes between "my client is down" and "my client is fixed."
### A real example: a client server pinned at 100% CPU [#a-real-example-a-client-server-pinned-at-100-cpu]
Here's what that looks like in practice. A while back, one of the client servers we manage started alerting: CPU stuck at 100%, the Node.js app was crawling, and nothing in the application logs to explain it.
Instead of opening five terminal tabs and a browser, we connected to the server card and asked the AI Terminal in plain English: *"CPU is maxed out but the app isn't under load. What's eating it?"*
1. It read the live server context (top processes, CPU, memory) and proposed a few read-only diagnostic commands: list the top processes by CPU, check what was actually running, and look at recent scheduled jobs. We reviewed them, approved them, and they ran.
2. The output surfaced the culprit immediately: an unfamiliar binary running out of `/tmp` under a random name, eating 98% of the CPU. A crypto-miner had slipped onto the box through an exposed service.
3. We asked the AI how it was persisting. It proposed checking the cron entries and systemd units, read-only again, approved, ran. It found a cron job re-downloading the miner every few minutes, which is exactly why a naive "just kill it" would not have stuck.
4. Only then did anything destructive run. The AI laid out the cleanup, stop the process, remove the binary, strip out the cron persistence, and showed each command before execution. We approved them one at a time.
Total time: under ten minutes, on a server none of us had touched in weeks.
The point isn't that the AI is magic. It's that every command was shown before it ran. On a compromised production box, that approval gate is the whole difference between fixing the problem and making it worse with a command copy-pasted from a 2019 forum thread. With an auto-run tool, step 4 executes before you've even finished reading it.
For a deeper look at how [AI changes DevOps workflows](https://ctrlops.io/blog/ai-in-devops), we break down the full approval-gated model.
***
## What Does a Real Deployment Look Like: OpenSSH vs a Modern SSH Client? [#what-does-a-real-deployment-look-like-openssh-vs-a-modern-ssh-client]
A real Node.js deployment takes 19 - 35 minutes with OpenSSH plus scp plus a browser dashboard - three tools and four context switches - versus 4 - 5 minutes in CtrlOps, where named server cards, a drag-and-drop file manager, an approval-gated AI terminal, and a built-in monitoring dashboard live in one app.
Feature tables are useful. But the real question: how much time do you lose on tasks that should be automatic?
Same deployment. Two approaches.
### Deploying with OpenSSH + scp + a browser dashboard [#deploying-with-openssh--scp--a-browser-dashboard]
1. Check your notes for the right server IP. (2 - 3 minutes)
2. Run `ssh root@ip`. Authenticate with the right key file. (1 - 2 minutes)
3. `cd /var/www/app && git pull`. Something breaks. Google the error. (10 - 20 minutes)
4. Config file needs updating. Open a new terminal tab, `scp` the file over. (3 - 5 minutes)
5. `npm install && pm2 restart app`. Check the browser dashboard for CPU spikes. (3 - 5 minutes)
**Total: 19 - 35 minutes.** Three tools. Two terminal tabs. Four context switches.
### The same deployment in CtrlOps [#the-same-deployment-in-ctrlops]
1. Click the "Prod-Backend" server card. Connected instantly. (10 seconds)
2. Open File Manager. Upload the updated config with drag and drop. (1 minute)
3. Open AI Terminal. Type: "pull latest, rebuild, restart PM2." Approve the commands. (2 minutes)
4. Check infrastructure dashboard: CPU normal, no error spike. (30 seconds)
**Total: 4 - 5 minutes.** One app. Zero context switches.
> "Deployments are no longer a source of anxiety for me, which is a massive relief. The process is incredibly simple - just paste the repository, set up the environment variables, enable SSL, and you're good to go. Since making the switch, I haven't run into a single deployment failure."
>
> * Bhavesh, [Product Hunt review](https://www.producthunt.com/products/ctrlops?comment=5380604)
Every tool you eliminate doesn't just save the time of opening it. It saves the recovery time afterward. If you manage a larger fleet, our guide on [managing multiple servers without losing control](https://ctrlops.io/blog/manage-multiple-servers-without-losing-control) digs into the organizational side.
***
## Conclusion [#conclusion]
The **best SSH clients for Linux** in 2026 are the ones that consolidate workflows into fewer tools.
Linux already gives you the most powerful CLI available. The question is whether you want to spend your time configuring it or managing servers.
For a raw terminal, OpenSSH is unbeatable. For cross-device sync, Termius leads. For an open-source GUI, Tabby is the strongest free option.
For teams that need SSH, file management, monitoring, deployment, and AI diagnostics in one local-first app: CtrlOps does that. $7/user/month (or $70/user/year) with a 1-month free trial. The workflow speaks for itself: the first time you deploy in 5 minutes instead of 35.
Pick the tool that matches your biggest pain point today. Switch if it stops fitting.
The best SSH client is the one you actually use without fighting it.
***
## Frequently Asked Questions [#frequently-asked-questions]
An SSH client is software that uses the Secure Shell (SSH) protocol to create encrypted connections to remote servers. On Linux, OpenSSH comes pre-installed as the default SSH client. You connect by running `ssh user@hostname` in any terminal. GUI-based SSH clients like Termius, CtrlOps, and Tabby add visual server directories, file managers, and saved credential management on top of this core protocol.
It depends on your workflow. For managing multiple servers with file transfers, monitoring, and deployments in one app, **CtrlOps** is the most complete option at $7/user/month (or $70/user/year). For cross-device sync, **Termius** is the most mature. For CLI-first simplicity, **OpenSSH** is pre-installed on most distributions. For a modern open-source GUI, **Tabby** is the strongest free option.
For 1 - 2 servers with simple SSH access, yes. For managing 5+ servers daily (deploying code, transferring files, monitoring resources, debugging incidents) OpenSSH alone requires 3 - 4 additional tools: `scp`, `htop`, cloud dashboards, and a notes file for IPs. Purpose-built clients like CtrlOps or Termius consolidate that stack into one interface.
**OpenSSH** is the best free CLI client: pre-installed on most distributions, scriptable, and rock-solid. **Tabby** is the best free GUI client: open-source, cross-platform, with built-in SFTP and a plugin ecosystem. **Remmina** is the best free option if you also need RDP and VNC alongside SSH.
Yes. Termius offers native Linux packages via .deb download, Snap Store, and AppImage. It supports Ubuntu, Fedora, Debian, and most major distributions. The Free Starter plan includes SSH, SFTP, local vault, and AI-powered autocomplete. Pro features like cloud sync, snippets, and mobile sync require $10/user/month (billed annually).
No. MobaXterm is a Windows-only application. There is no native Linux version, no .deb or .rpm package, and no Flatpak or Snap. On Linux, the closest multi-protocol alternatives are **Remmina** (SSH, RDP, VNC) or **CtrlOps** (SSH with AI, file manager, and monitoring). MobaXterm's X11 server feature is unnecessary on Linux since X11 runs natively.
Two tools offer AI in the terminal on Linux: **CtrlOps** and **Warp**. CtrlOps uses an approval-gated model: it shows generated commands before execution so you review them first. Warp uses an auto-run model where AI commands execute immediately. For production servers, the approval gate is the safer approach. Both support BYOK (bring your own API key from OpenAI, Anthropic, or Google).
On Linux, PuTTY solves a problem that doesn't exist. OpenSSH is pre-installed on most distributions and more capable. Tabby offers a better GUI. PuTTY's main value is on Windows, where no native SSH client existed until Windows 10. On Linux, the only reason to install PuTTY is if you specifically want a GUI for entering IPs without learning `~/.ssh/config` syntax.
Skip GUI clients if you manage 1 - 2 servers, prefer scripting everything in bash, already have a solid `~/.ssh/config` and `tmux` workflow, or work on headless Linux servers without a desktop environment. In those cases, OpenSSH plus `tmux` is lighter, faster, and sufficient. GUI clients add value when you manage 5+ servers, transfer files frequently, or need visual monitoring.
Yes. CtrlOps runs natively on Ubuntu (20.04+), Fedora, Debian, Arch Linux, macOS (Apple Silicon and Intel), and Windows. It connects to servers over standard SSH, no agents or plugins needed on your servers. If you can SSH into a server from your Linux machine, CtrlOps can manage it. It costs $7/user/month or $70/user/year. Download from [ctrlops.io](https://ctrlops.io/).
Free options with file transfer: **Tabby** (built-in SFTP, open-source) and **OpenSSH** (via `scp`/`rsync` commands, no GUI). Among paid tools with a full GUI file manager: **CtrlOps** at $7/user/month is the lowest-cost option that includes drag-and-drop file management, AI terminal, and monitoring. **Termius Pro** at $10/user/month offers SFTP but no monitoring or deployment.
Both run natively on Linux with .deb and Snap support. Termius excels at cross-device credential sync and has mobile apps for iOS and Android. CtrlOps excels at server operations: full GUI file manager, real-time infrastructure monitoring, one-click deployment, and approval-gated AI commands. Termius stores credentials in the cloud (E2E encrypted). CtrlOps stores everything locally. For a detailed comparison, see [CtrlOps vs Termius](https://ctrlops.io/compare/ctrlops-vs-termius).
---
# Best SSH Client for Mac 2026: What Actually Works (/blog/best-ssh-client-mac-2026)
Author: Hiren Kalariya | Role: Co-Founder & CEO, TST Technology | Published: 2026-05-02 | Updated: 2026-08-12 | Tags: ssh client, mac, terminal, devops, server management | Reading Time: 35 min read
> Honest comparison of 6 SSH clients on Mac across real workflows: iTerm2, Termius, Warp, OpenSSH, and CtrlOps - features, security, and pricing for 2026.
The best SSH client for Mac in 2026 is **CtrlOps** for anyone managing more than one server - it's the only tool on this list that combines SSH, a GUI file manager, live infrastructure monitoring, AI diagnostics, and one-click deployment in a single desktop app ($7/user/mo). For a free terminal, **iTerm2** is the strongest option. For cross-device sync, choose **Termius**. For an AI-first coding terminal, choose **Warp**. For a fully scriptable, no-install setup, **OpenSSH** is built into macOS.
## 6 Best SSH Clients for Mac in 2026 [#6-best-ssh-clients-for-mac-in-2026]
The 6 best SSH clients for Mac in 2026 are CtrlOps (all-in-one server management), macOS Terminal (built-in baseline), iTerm2 (free power terminal), Termius (cross-device sync), Warp (AI-first coding terminal), and OpenSSH + custom setup (full terminal control). We tested each against the same real-world scenarios.
| Tool | Best For | Price | AI | File Manager | Local Credentials |
| ---------------- | -------------------------------- | -------------------------- | ---------------------- | -------------- | ----------------- |
| **CtrlOps** | **All-in-one server management** | **$7/user/mo (1 mo free)** | **✓ Approval-gated** | **✓ Full GUI** | **✓ Local-only** |
| macOS Terminal | Single-server basics | Free (built-in) | ✗ | ✗ | ✓ Local |
| iTerm2 | Power terminal users | Free | ✗ | ✗ | ✓ Local |
| Termius | Cross-device sync | $10/user/mo | Partial (autocomplete) | ✓ SFTP | ✗ Cloud |
| Warp | AI-first coding terminal | $20/mo | ✓ Auto-run | ✗ | ✗ Cloud |
| OpenSSH + Custom | Full terminal control | Free (built-in) | ✗ | ✗ | ✓ Local |
*Full breakdown with real workflow comparisons, security analysis, and pricing details below.*
Prefer to watch instead? The full comparison - all six tools, the deploy race, and the SSH key security question - in about 6 minutes:
***
### 1. CtrlOps: Best for AI-Powered Server Management [#1-ctrlops-best-for-ai-powered-server-management]
CtrlOps takes a fundamentally different approach from every other tool on this list.
Instead of being a better terminal, it replaces your entire server management stack: terminal, file manager, monitoring dashboard, and deployment system. All-in-one desktop app.
**Pros of CtrlOps:**
* **Named server cards:** Connect to "Prod-Backend" or "Client-XYZ-Staging" instead of grepping through `~/.ssh/config`. One click, you're in.
* **Full [GUI file manager](/docs/modules/file-manager):** Upload, download, edit, and delete remote files without `scp` commands or a separate SFTP tool. Drag-and-drop works.
* **Approval-gated [AI terminal](/docs/modules/ai-terminal):** Type "why is my server slow?" and get diagnostic commands shown before anything runs. You review, approve, then execute. No auto-run.
* **Streamlined [application deployment](/docs/modules/deployment):** Pick your stack (React, Next.js, Node.js), link GitHub, set environment variables. CtrlOps handles cloning, dependencies, PM2, Nginx, and Certbot SSL automatically.
* **Instant infrastructure monitoring:** CPU, RAM, disk, and running processes visible inside the app. No more `htop` in a separate window.
* **Local-first security:** Credentials, SSH keys, and server configs stay on your machine. AES-256 encrypted. No cloud sync.
* **[Script Directory](/docs/modules/ai-terminal/scripts):** Save reusable scripts with `{{variable}}` placeholders. One click runs them across every server.
* **MCP Server integration.** Connect Context7, GitHub, Filesystem, or custom MCP servers via JSON config. The AI reads your actual codebase before generating commands.
**Explore all features:** Beyond these capabilities, CtrlOps provides many other features like a PM2 process manager, a Visual File Manager, and more. If you want information about all the features, please visit the [CtrlOps features page](/features).
**CtrlOps Limitations:**
* No mobile app
* No serverless or Kubernetes support
* No push notifications yet (on roadmap)
**Pricing:** $7/user/month or $70/user/year (unlimited servers). [1 month free trial](/pricing), no credit card required.
**Platforms:** macOS (Apple Silicon + Intel), Windows, Linux.
### 2. macOS Terminal (Baseline) [#2-macos-terminal-baseline]
macOS Terminal is already on your Mac. For quick one-off connections, `ssh user@ip` and you're in.
**Pros of macOS Terminal:**
* **Already on your machine.** Open Terminal, type `ssh user@ip`, done.
* **Scriptable:** pipes, aliases, `ssh-agent`, pairs with `tmux` for session management
* **Zero overhead:** no download, no account, no RAM footprint beyond the connection
**macOS Terminal Limitations:**
* **No server directory.** You memorize IPs or keep a notes file open.
* **No file transfer GUI.** SCP commands with exact paths every time.
* **No monitoring.** You run `htop`, `df -h`, `free -m` manually.
* **No AI.** You Google errors or paste them into ChatGPT in a separate tab.
* **No session persistence.** Close the window and everything's gone.
**Pricing:** Free (built into macOS).
**Platforms:** macOS only.
The right choice if you manage 1 - 2 servers and don't want to install anything. Beyond that, you'll end up supplementing it with 3 - 4 other tools.
### 3. iTerm2: Best Free Power Terminal [#3-iterm2-best-free-power-terminal]
[iTerm2](https://iterm2.com/) is the most popular terminal replacement on Mac. Split panes, hotkey windows, search, autocomplete, triggers, and profiles.
**Pros of iTerm2:**
* **Free and mature** with 20+ years of development
* **Split panes:** monitor multiple servers side by side
* **Hotkey window:** drop into a terminal from anywhere with one shortcut
* **Profiles:** save connection details and terminal preferences per server
* **Search and autocomplete:** find output instantly, complete commands faster
* **GPU-accelerated rendering:** fast and responsive
**iTerm2 Limitations:**
* **No file manager.** SCP commands or a separate SFTP tool for every file transfer.
* **No server directory.** Profiles help, but no visual fleet view or one-click connect.
* **No AI.** No command generation, no diagnostics.
* **No monitoring or deployment.**
* **Steep learning curve.** Extensive config options that most developers never fully use.
**Pricing:** Free, open-source.
**Platforms:** macOS only.
iTerm2 is the best terminal emulator on Mac. But it's still just a terminal. If your problems involve file management, monitoring, and multi-server organization, iTerm2 doesn't solve them.
### 4. Termius: Best for Cross-Platform Teams [#4-termius-best-for-cross-platform-teams]
[Termius](https://termius.com/) is the most polished [dedicated SSH client](/blog/putty-webmin-serverpilot-alternatives) on the market. It syncs servers, credentials, and snippets across Mac, Windows, Linux, iOS, and Android. The only tool on this list with full-featured mobile apps.
**Pros of Termius:**
* **Cross-device sync:** servers and credentials follow you everywhere, E2E encrypted
* **Clean UI:** named hosts, groups, tags, one-click connect
* **Built-in SFTP:** file transfers without a separate tool
* **AI-powered autocomplete:** suggests commands as you type
* **Mobile apps:** SSH from your phone during a production incident
* **Team vault:** shared server access with role-based controls
**Termius Limitations:**
* **SSH keys sync to Termius's cloud.** E2E encrypted, yes, but they live on third-party infrastructure. Some client contracts prohibit this.
* **No infrastructure monitoring.** You SSH in and run `htop` manually.
* **No one-click deployment.** Manual repo clones, PM2, Nginx setup.
* **AI is autocomplete, not diagnostics.** Suggests completions, doesn't understand server state.
* **Pricing scales per user.** Pro: $10/user/month. Team: $20/user/month. 5-person Team plan costs $100/month ($1,200/year).
**Pricing:** Free (Starter, local vault only). Pro: $10/user/month. Team: $20/user/month. Business: $30/user/month (all when billed annually).
**Platforms:** macOS, Windows, Linux, iOS, Android.
Termius wins if you need the same SSH setup on every device, including your phone. The trade-off: cloud credential storage and per-user pricing that gets expensive at team scale. See [CtrlOps vs Termius](/compare/ctrlops-vs-termius) for a direct comparison. If the cloud storage is a dealbreaker, see [best Termius alternatives](/blog/termius-alternatives) across all platforms or the [Mac-specific breakdown](/blog/termius-alternatives-mac).
### 5. Warp: Best AI-First Coding Terminal [#5-warp-best-ai-first-coding-terminal]
[Warp](https://www.warp.dev/) is the most well-funded AI terminal on the market. Backed by Sequoia Capital with [$73M+ in funding](https://sacra.com/c/warp/), built in Rust. Block-based output, IDE-like editing, and AI Agent Mode that converts natural language into shell commands.
**Pros of Warp:**
* **AI Agent Mode:** type natural language, get shell commands generated and executed
* **Block-based output:** each command result is a selectable, searchable block
* **IDE-like editing:** select, copy, edit previous commands like text
* **Rust-based performance:** GPU-accelerated, no Electron lag
* **Warp Drive:** save and share command sequences across teams
* **BYOK support:** bring your own OpenAI, Anthropic, or Google API key
**Warp Limitations:**
* **It's a coding terminal, not a server manager.** No server directory, no file manager, no monitoring, no deployment.
* **AI auto-runs commands by default.** On production, one misinterpreted prompt can cause real damage. No approval gate.
* **Cloud account required.** Can't use Warp without signing in.
* **Free tier is limited.** 150 AI credits for 2 months, then 75/month. Build plan: $20/month with 1,500 credits.
* **Not designed for multi-server fleet management.**
**Pricing:** Free (75 - 150 AI credits/month). Build: $20/month. Business: $50/user/month.
**Platforms:** macOS, Windows, Linux.
Warp is the best terminal on Mac for local development. For remote server management, Warp's AI lacks server context and auto-executes without review. See [CtrlOps vs Warp](/compare/ctrlops-vs-warp) for a direct comparison.
### 6. OpenSSH + Custom: Best for Full Terminal Control [#6-openssh--custom-best-for-full-terminal-control]
OpenSSH is built into macOS. Combined with `~/.ssh/config`, bash aliases, and tmux, it gives you a free, fully scriptable SSH workflow with zero vendor lock-in.
**Pros of OpenSSH + Custom:**
* **Pre-installed** on macOS. No download, no account.
* **`~/.ssh/config` file:** define named hosts, custom ports, and identity files for one-command connections
* **Total control:** shell scripts, aliases, tmux layouts, anything you can script
* **Rock-solid security:** 25+ years of community audits, the protocol standard itself
* **Zero overhead:** no GUI, no Electron, no RAM footprint beyond the connection
**OpenSSH Limitations:**
* **4 - 8 hours of initial setup.** SSH config, bash aliases, tmux layouts, deployment scripts.
* **No GUI.** Everything is command-line. File transfers mean `scp` or `rsync` in a separate command.
* **No server directory.** You maintain `~/.ssh/config` by hand. No visual grouping, no search.
* **No AI, no monitoring, no deployment automation.**
* **Not shareable.** Onboarding a new team member means walking them through your entire configuration.
**Pricing:** Free, open-source (BSD license).
**Platforms:** Pre-installed on macOS. Also available on Linux and Windows.
The custom setup works for senior engineers who love the terminal. For teams, junior developers, and agencies, the maintenance overhead outweighs the flexibility.
***
## How We Compared the 6 Best SSH Clients for Mac? [#how-we-compared-the-6-best-ssh-clients-for-mac]
We compared 6 SSH clients for Mac across four real-world tasks: connecting to a 5-server fleet, deploying a Next.js app, debugging a production issue under time pressure, and transferring config files mid-session. Scored on task performance, not marketing claims.
You're managing five client servers from your MacBook. A production Node.js app is throwing 502 errors.
You open Terminal, dig through a notes file for the IP, connect. The config file needs updating, so you open Cyberduck, re-enter the same credentials. Then you check a browser tab for CPU spikes.
Three tools. Four context switches. Twenty-five minutes. The client is still calling.
If you're a **freelance developer juggling client servers**, a **startup CTO tired of 45-minute deployments**, or an **agency engineer managing staging and production across projects**: you've lived this.
***
## What Makes a Great SSH Client for Mac in 2026? [#what-makes-a-great-ssh-client-for-mac-in-2026]
A great SSH client for Mac consolidates your workflow. It minimizes the tabs and tools needed to manage live servers while maintaining strict security standards.
Six criteria separate a useful Mac SSH client from another terminal tab:
**1. Multi-server organization.**
Find and connect to the right server in under 10 seconds. Named hosts, one-click connect, visual grouping by environment. Not raw IPs in a text file.
**2. Integrated file management.**
Uploading a config shouldn't require opening Cyberduck in a separate window. A built-in file browser eliminates one full context switch per session.
**3. Credential security.**
Where do your SSH keys live: on your machine or a vendor's cloud? For client work and regulated industries, the answer matters.
**4. AI assistance.**
AI that drafts diagnostic commands can save nearly an hour on unfamiliar environments. Key distinction: does it auto-run commands or show them for approval first? A [built-in AI that can see live server metrics](/blog/ai-in-devops) is a different tool from a chatbot in a browser tab.
**5. Deployment and automation.**
If you manually run `git pull`, `npm install`, `pm2 restart`, and configure Nginx every time you deploy, your SSH client isn't doing enough.
**6. Real price transparency.**
Per-user pricing adds up fast. A $10/user/month tool costs $600/year for a 5-person team. Know the true cost at your team size before committing.
**Bottom line:** The best SSH clients for Mac in 2026 are not just terminals. They're server management tools. Evaluating them purely on "can it open an SSH connection?" solves the wrong problem: your default terminal already does that.
***
## Why Most SSH Clients on Mac Fail in Real Workflows [#why-most-ssh-clients-on-mac-fail-in-real-workflows]
Most SSH clients on Mac fail in real workflows because they only solve the connection - not the job around it. The moment you manage more than one server, you bolt on a separate SFTP app for files, a browser dashboard for monitoring, and ChatGPT for debugging, cobbling together 4 - 6 disconnected tools. macOS Terminal, iTerm2, Termius, and Warp each cover only a slice of that workflow.
When you're actually managing servers - deploying at midnight, debugging under pressure, juggling five different machines - the cracks show fast.
### The hidden cost of switching between terminal, FTP, and monitoring tools [#the-hidden-cost-of-switching-between-terminal-ftp-and-monitoring-tools]
Every tool you add to a server workflow carries a tax that never shows up on the invoice: the seconds lost re-authenticating, re-navigating, and rebuilding focus each time you switch windows.
Here's what a typical server management session looks like for most developers:
1. Open Terminal to SSH into the server
2. Open a separate SFTP client (Cyberduck, Transmit, WinSCP) to upload a config file
3. Switch to a browser tab to check server metrics on a cloud dashboard
4. Open ChatGPT in another tab to ask about an error message
5. Copy-paste the error back into Terminal
6. Repeat steps 1 - 5 for the next server
That's not a workflow. That's a scavenger hunt. And the cost is real: **task-switching research shows the mental blocks created by shifting between tasks can cost up to 40% of someone's productive time** ([American Psychological Association](https://www.apa.org/research/action/multitask)), and UC Irvine research found it takes an average of 23 minutes to fully refocus after an interruption ([Mark et al., The Cost of Interrupted Work](https://www.ics.uci.edu/~gmark/chi08-mark.pdf)).
If you manage multiple servers daily, you're not just losing time - you're burning mental energy on tool management instead of actual problem-solving. The average knowledge worker toggles between applications over 1,200 times per day, according to [Harvard Business Review research](https://hbr.org/2022/08/how-much-time-and-energy-do-we-waste-toggling-between-applications). For developers managing infrastructure, that number is likely higher.
**Bottom line:** Tool fragmentation isn't a productivity problem - it's a focus problem. Each context switch resets your working memory; do it 100+ times a day and you're operating at a fraction of your capacity even when you "feel productive." The real fix isn't faster tools; it's fewer tools doing more.
### Where macOS Terminal breaks in production use [#where-macos-terminal-breaks-in-production-use]
macOS Terminal (or even iTerm2) works fine when you're connecting to a single server, running a few commands, and logging out. But real production use exposes three critical gaps:
#### Multi-server handling, file transfers, debugging limitations [#multi-server-handling-file-transfers-debugging-limitations]
**Multi-server management doesn't exist.** Terminal gives you tabs. That's it. No server directory, no named aliases, no visual status indicators. When you have 8 servers across staging and production, you're relying on memory or a sticky note to know which tab is which. One wrong command on the wrong server can mean downtime.
**File transfers require a separate tool.** Need to upload an Nginx config file? You can't do it in Terminal without SCP commands and exact paths. So you open Cyberduck or FileZilla, re-enter the same credentials, navigate to the right directory, and transfer. That's a 5-minute detour for a 10-second task.
**Debugging is manual and slow.** When something breaks at 2AM, you're running `top`, `df -h`, `journalctl`, `tail -f` - one command at a time, interpreting raw output, with no context about what changed since last time. There's no dashboard. No history. No AI to ask "why is this server slow?" - just you and a blinking cursor.
The result? Most developers cobble together a patchwork of 4 - 6 tools just to manage their servers. And they accept this as normal. It isn't.
***
## AI-Powered SSH Clients for Mac: What's Actually Different in 2026 [#ai-powered-ssh-clients-for-mac-whats-actually-different-in-2026]
What's actually different in 2026 is that AI terminals split into two models: AI that auto-runs commands (Warp's Agent Mode) and AI that shows commands for approval before running (CtrlOps' [AI Terminal](/features/ai-terminal)). On a production server, that difference matters more than the branding - one misread prompt with auto-run has no undo, while an approval gate stops 2 AM mistakes before they execute.
"AI terminal" has become a marketing phrase that gets slapped on anything with an autocomplete suggestion. In practice, AI SSH clients split into two models:
**Model 1: AI that executes for you (Warp Agent Mode)**
Type "deploy my Next.js app" and Warp figures out the commands and runs them. No confirmation step. Fast. Convenient on your local machine. On a production server, a single misread prompt can trigger `pm2 delete all` or worse. There's no undo.
**Model 2: AI that shows and asks (CtrlOps AI Terminal)**
Type "why is my server slow?" and CtrlOps generates the diagnostic commands - then shows them to you before anything runs. You review, click Run, and it executes. Slower by one click. Safer by an order of magnitude when you're on live infrastructure.
This is the difference that most "AI SSH client" comparisons miss entirely.
### How Each SSH Client Handles AI [#how-each-ssh-client-handles-ai]
| SSH Client | AI Feature | Auto-Executes? | Server Context Aware? | Approval Gate | AI Provider |
| ---------------- | ----------------------------- | -------------- | --------------------- | -------------- | ----------------------------------------- |
| macOS Terminal | ✗ None | - | - | - | - |
| iTerm2 | ✗ None | - | - | - | - |
| Termius | Partial (Gloria autocomplete) | ✗ | ✗ | N/A | Proprietary |
| Warp | ✓ Agent Mode | ✓ Yes | ✗ | ✗ None | Warp AI |
| OpenSSH + Custom | ✗ None | - | - | - | - |
| **CtrlOps** | **✓ AI Terminal** | **✗ No** | **✓ Live metrics** | **✓ Built-in** | **OpenAI / Gemini / Claude / OpenRouter** |
### Why CtrlOps Is the AI-Native Option [#why-ctrlops-is-the-ai-native-option]
Most ssh clients for mac bolt AI on top of an existing terminal. CtrlOps built AI around server operations from the start. The distinction shows in three places:
**1. Live server context.** When you ask "check memory and CPU," CtrlOps' AI already knows what server you're connected to, its current state, and the last commands run in the session. ChatGPT in a browser tab knows none of this.
**2. Pre-built server operations.** The AI panel ships with quick-action prompts mapped to the actual tasks you do daily: "Why is my server slow?", "Show recent error logs", "Restart crashed service", "Check disk space." These aren't generic prompts - they're tuned for Linux server ops.
**3. Bring your own AI key.** OpenAI, Anthropic Claude, Google Gemini, or any OpenRouter-compatible model. Your API key is stored locally on your machine - never on CtrlOps servers. This also means you're not locked into one model's quality ceiling.
> "What stands out from an engineering perspective is the approval gate on the AI terminal. Most AI tooling here either runs blind or needs too much manual intervention to be useful. This sits in the right place: the AI does the thinking, the engineer makes the call."
>
> * **Drijesh P.**, [Engineering Manager at IBM](https://drijeshppatel.in) ([original post on LinkedIn](https://www.linkedin.com/posts/drijesh_ctrlops-deploy-debug-manage-linux-servers-activity-7462442711686651904-gb4r))
**The production server rule:** Any AI that auto-runs commands without a review step is a developer-machine feature, not a server management feature. Warp's Agent Mode is excellent when you're building locally. On a production server with real traffic and real data, the one-click approval gate in CtrlOps is the feature that stops 2 AM mistakes from becoming incidents.
***
## Real Workflow Comparison (What Changes in Practice) [#real-workflow-comparison-what-changes-in-practice]
In practice, the same Next.js deployment takes 25 - 50 minutes with macOS Terminal plus a separate SFTP client, a browser dashboard, and ChatGPT - four to five tool switches - versus 5 - 8 minutes in CtrlOps, where named server cards, a GUI file manager, one-click deployment, a live monitoring dashboard, and approval-gated AI all live in one window.
Feature lists don't tell you how a tool feels in daily use. Workflow comparisons do. Let's walk through the same task - deploying a Next.js app to a production server - using both approaches.
### Traditional Workflow [#traditional-workflow]
This is what most developers do today. If you're using Terminal + separate tools, here's your deployment:
#### Terminal + SFTP + monitoring tools + manual steps [#terminal--sftp--monitoring-tools--manual-steps]
1. **Find the server IP** from your notes or spreadsheet (2 minutes)
2. **Open Terminal**, type `ssh user@ip`, enter password or key path (1 minute)
3. **Pull the latest code:** `git pull origin main` (2 minutes)
4. **Install dependencies:** `npm install` (3 - 5 minutes, depending on project size)
5. **Build the application:** `npm run build` (2 - 3 minutes)
6. **Restart the process:** `pm2 restart app` (30 seconds)
7. **Open SFTP tool** (Cyberduck/FileZilla), reconnect to the same server (2 minutes)
8. **Upload updated config file** if needed (1 minute)
9. **Switch to browser**, check cloud dashboard or run `htop` to verify server health (2 minutes)
10. **Check logs:** `pm2 logs` or `tail -f /var/log/nginx/error.log` (1 - 2 minutes)
11. **If something breaks**, Google the error, paste it into ChatGPT, try the suggested fix (10 - 30 minutes)
**Total time: 25 - 50 minutes** per deployment, with 4 - 5 tool switches and multiple context jumps.
### Unified Workflow (CtrlOps) [#unified-workflow-ctrlops]
Here's the same [Next.js deployment to a production server](/blog/deploy-nextjs-app-linux-vps), this time using a unified tool (CtrlOps in this example):
#### Unified interface + automation + reduced context switching [#unified-interface--automation--reduced-context-switching]
1. **Open CtrlOps**, click the named server card for "prod-frontend" (10 seconds)
2. **Click "Add Application"** in the File Manager (5 seconds)
3. **Fill in the form:** paste GitHub repo URL, select Next.js, paste `.env` variables (bulk), add domain, toggle SSL (2 minutes)
4. **Click Create.** CtrlOps handles git clone, npm install, npm build, PM2 setup, Nginx configuration, and Certbot SSL - automatically (3 - 5 minutes)
5. **Check Infra Details** tab - live CPU, RAM, disk metrics, no commands needed (30 seconds)
6. **Check logs** in the Console tab if needed (30 seconds)
7. **If something breaks**, type "why is my server slow?" in the AI panel - it runs diagnostics and shows results before executing (2 - 3 minutes)
**Total time: 5 - 8 minutes** per deployment, zero tool switches, everything in one window.
### Time and cognitive load comparison [#time-and-cognitive-load-comparison]
| Task | Traditional Setup | Unified Tool (CtrlOps) | Time Saved |
| ------------------------ | ------------------------------ | ------------------------ | ------------ |
| Find & connect to server | 2 - 3 min (IP lookup + SSH) | 10 sec (one-click) | \~2.5 min |
| Deploy a Next.js app | 30 - 45 min (manual steps) | 5 min (guided form) | \~35 min |
| Upload a config file | 5 min (open SFTP + navigate) | 30 sec (File Manager) | \~4.5 min |
| Check server health | 3 - 5 min (run htop, df, free) | 30 sec (dashboard) | \~4 min |
| Debug a production issue | 30 - 60 min (manual + ChatGPT) | 5 - 10 min (AI terminal) | \~40 min |
| **Per-deployment total** | **45 - 80 min** | **8 - 15 min** | **\~50 min** |
The difference isn't just time. It's the mental energy spent context-switching between tools, re-entering credentials, and trying to remember which window has which server. A unified workflow means you stay focused on the problem instead of managing the tools.
Research confirms this: context switching costs developers an average of 2 - 3 hours of productivity daily ([Atlassian: The Cost of Context Switching](https://www.atlassian.com/blog/productivity/context-switching)). Every tool switch is a potential task abandonment.
## Best FREE SSH Clients for Mac [#best-free-ssh-clients-for-mac]
The best free SSH client for Mac depends on what "free" actually costs you in time.
Free SSH clients for Mac range from zero-setup to fully customized, but none replace the full server management stack without trade-offs.
| Tool | Price | File Transfer | AI Help | Multi-Server View | Local Credentials |
| ---------------- | ------------------ | ------------- | ------------------ | ----------------- | ----------------- |
| macOS Terminal | Free | SCP (manual) | ✗ | ✗ | ✓ |
| iTerm2 | Free | SCP (manual) | ✗ | Tabs only | ✓ |
| OpenSSH + Custom | Free | rsync/SCP | ✗ | SSH config | ✓ |
| CtrlOps | 1-month free trial | ✓ GUI | ✓ (approval-gated) | ✓ Fleet view | ✓ |
**iTerm2** is the strongest free option for most developers. It upgrades the default Terminal with split panes, search, and connection profiles - no cost, no account, no cloud dependency. Your SSH keys stay on your machine.
**macOS Terminal** is already on your Mac and handles one-off connections without installing anything. That's its ceiling.
**OpenSSH + a custom SSH config file** gives you named hosts and one-click-style aliases, but requires manual setup. Nobody sets this up because they enjoy it - they do it because they need it.
**CtrlOps** is not permanently free, but the one-month free trial (no credit card required) gives you enough runway to validate whether unified server management is worth $7/user/month. For most developers managing 3+ servers, the answer is yes after the first deployment.
**Bottom line:** For zero cost, iTerm2 is the best free SSH client on Mac. It beats macOS Terminal in every way that matters and costs nothing. If your work involves more than SSH - file transfers, monitoring, deployments - the CtrlOps free trial is worth running before you commit to any paid tool.
***
## Best GUI SSH Clients for Mac [#best-gui-ssh-clients-for-mac]
A GUI SSH client saves the most time on tasks that are hard to do in plain text: navigating remote directories, monitoring live server metrics, and configuring deployments without memorizing every flag.
The best GUI SSH clients for Mac reduce the time spent on file transfers, server health checks, and deployments from minutes to seconds.
| Tool | GUI File Manager | Live Server Metrics | One-Click Deploy | Server Directory | Price |
| -------------- | ---------------- | ------------------- | ---------------- | ---------------- | -------------- |
| Termius | ✓ SFTP | ✗ | ✗ | ✓ | $10/mo |
| **CtrlOps** | **✓ Full GUI** | **✓ CPU/RAM/Disk** | **✓** | **✓** | **$7/user/mo** |
| macOS Terminal | ✗ | ✗ | ✗ | ✗ | Free |
| iTerm2 | ✗ | ✗ | ✗ | ✗ | Free |
| Warp | ✗ | ✗ | ✗ | ✗ | $20/mo |
**Termius** has the most polished GUI SSH experience for pure connection management. The server directory is clean, the SFTP file browser works well, and the interface is the same on Mac, Windows, iOS, and Android. If you need cross-device access with a GUI, Termius is the benchmark.
**CtrlOps** goes further. The GUI covers the full workflow: connect to a named server, open the [file manager](/features/file-manager), check live CPU and disk metrics, and deploy a Node.js or Next.js app - all inside one window. No terminal-to-SFTP-to-browser round trip.
For developers who spend time daily on file transfers, health checks, and deployments, that consolidation is the practical difference between a 30-minute task and a 5-minute one.
Terminal and Warp are CLI-first tools. They have no GUI file manager and no visual monitoring - not because it's technically impossible, but because that's not what they're built for.
**Reality check:** GUI does not mean "no terminal access." Both Termius and CtrlOps give you a full terminal alongside the GUI features. The value of a GUI SSH client is not that it hides the command line - it's that you stop being *forced* into the command line for tasks where clicking is faster.
***
## Feature & Capability Comparison Table [#feature--capability-comparison-table]
Here's the full breakdown across every capability that matters for real server management. Not marketing features - actual things you do daily.
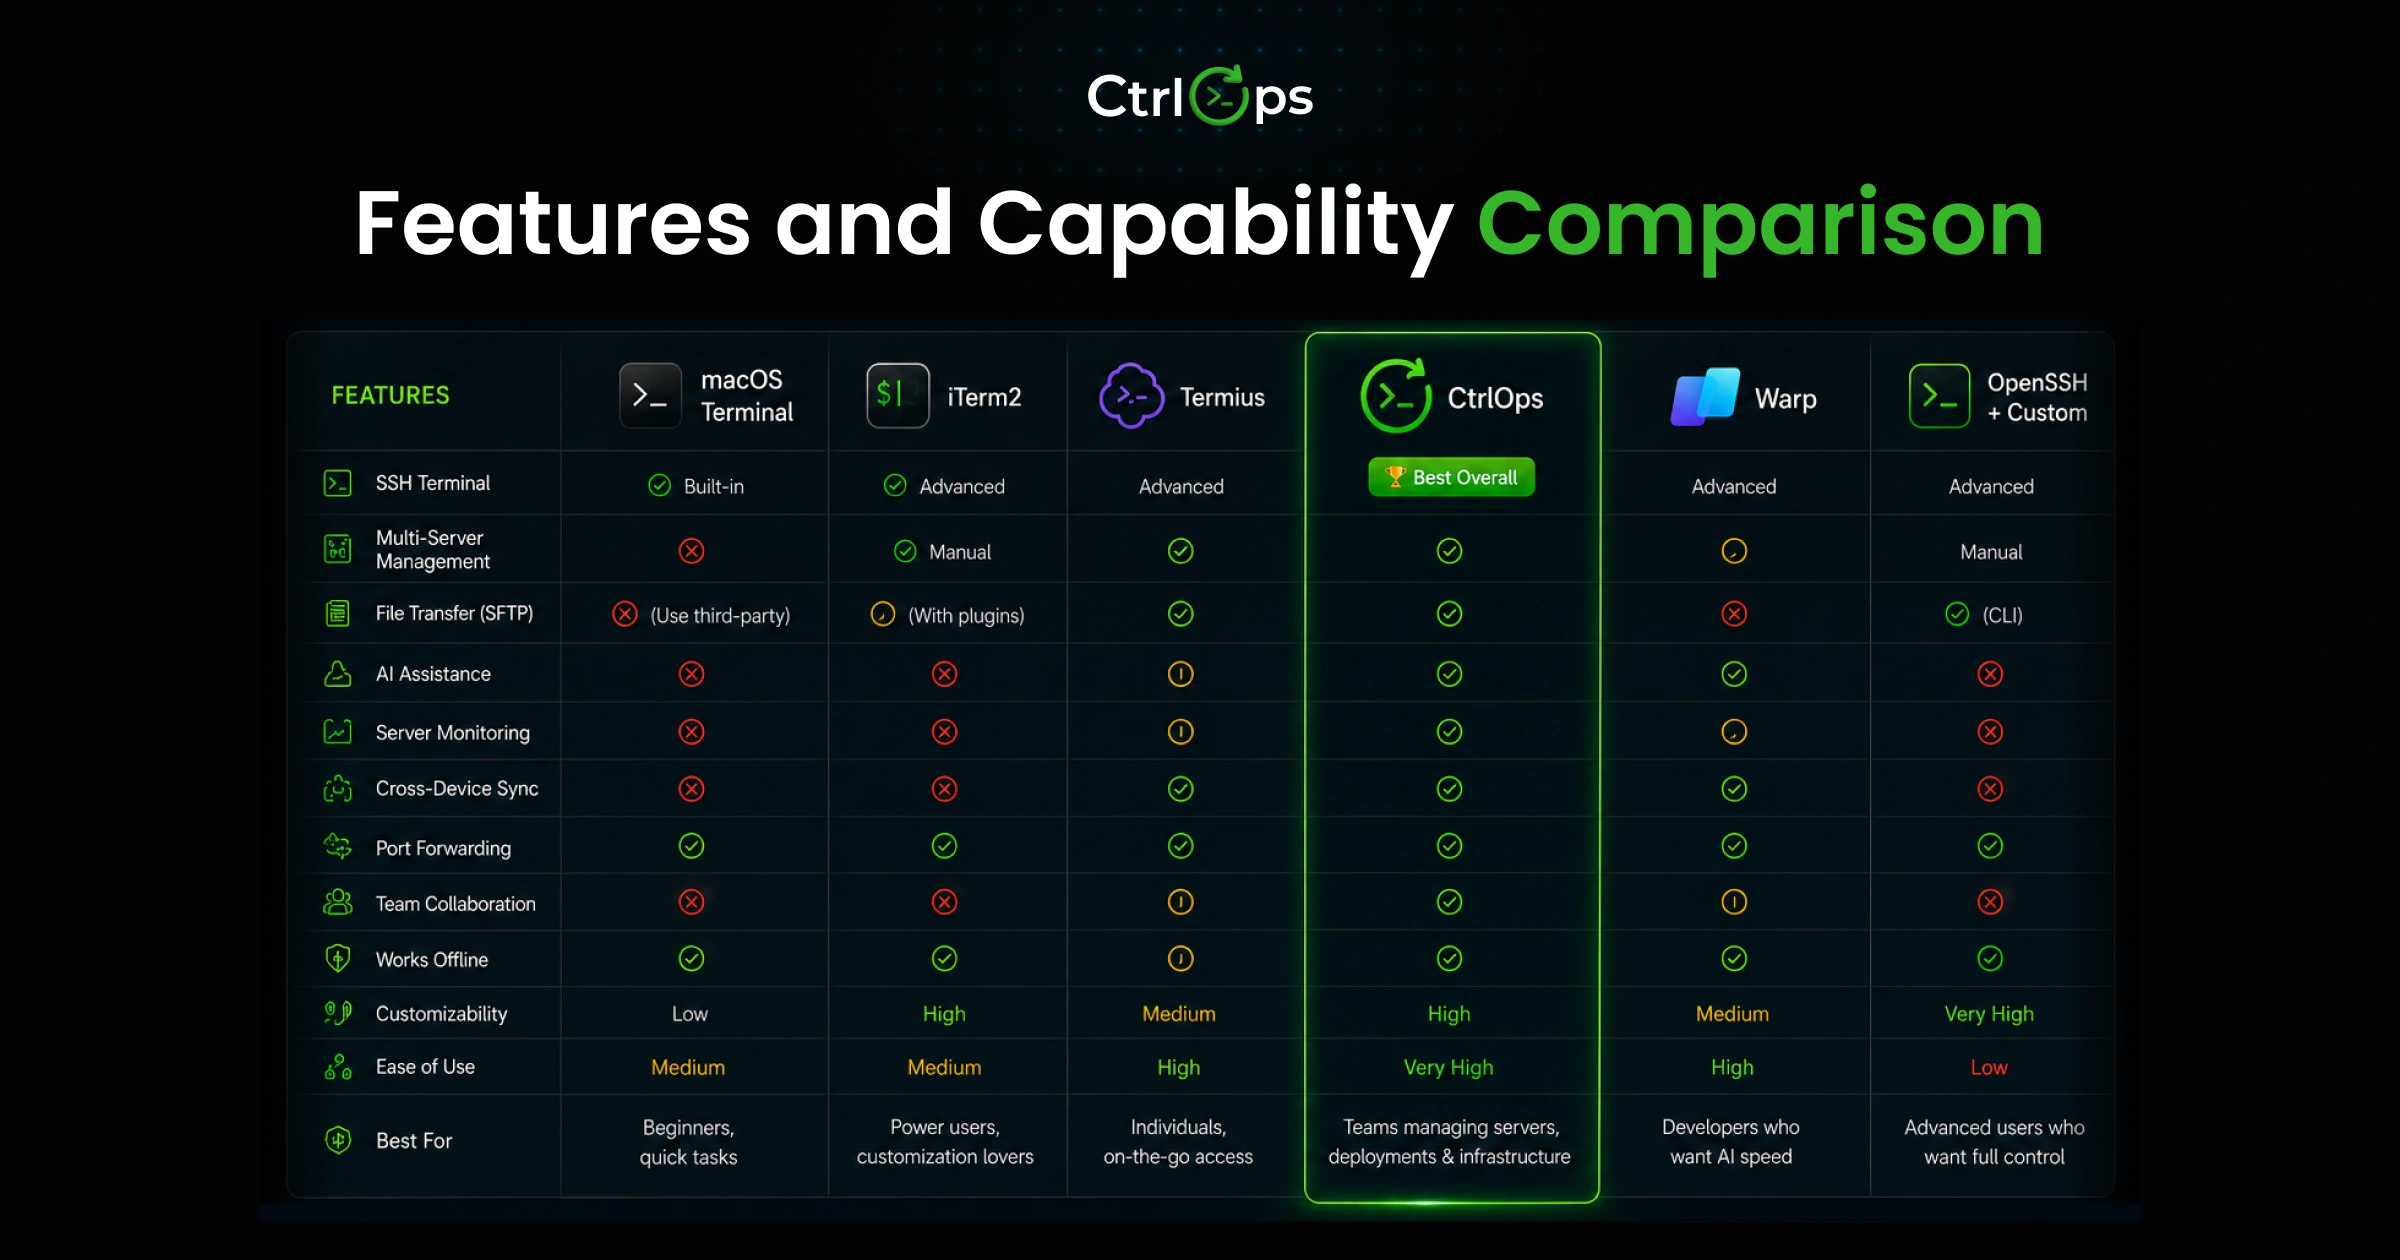
### Multi-server handling [#multi-server-handling]
If you manage more than 2 servers, this is where most tools fall apart. Only Termius and CtrlOps offer a proper server directory with one-click connections. iTerm2 and Warp give you tabs, but you're still memorizing IPs or maintaining SSH config files manually.
| Tool | Server Directory | Named Hosts | One-Click Connect | Fleet Overview | Group by Environment |
| ---------------- | -------------------- | ----------- | ----------------- | -------------- | -------------------- |
| macOS Terminal | ✗ | ✗ | ✗ | ✗ | ✗ |
| iTerm2 | ✗ (profiles only) | Partial | ✗ | ✗ | ✗ |
| Termius | ✓ | ✓ | ✓ | ✗ | ✓ |
| Warp | ✗ | ✗ | ✗ | ✗ | ✗ |
| OpenSSH + Custom | Partial (SSH config) | ✓ (manual) | ✗ | ✗ | ✗ (manual) |
| CtrlOps | ✓ | ✓ | ✓ | ✓ | ✓ |
### File management & GUI support [#file-management--gui-support]
This is the biggest gap in most "best SSH client" comparisons. Moving files is something you do constantly - and most tools force you to open a separate application for it.
| Tool | Built-in File Manager | Upload/Download | Edit Remote Files | Directory Upload | Drag & Drop |
| ---------------- | --------------------- | --------------- | ----------------- | ---------------- | ----------- |
| macOS Terminal | ✗ (SCP only) | SCP commands | ✗ | ✗ | ✗ |
| iTerm2 | ✗ | SCP commands | ✗ | ✗ | ✗ |
| Termius | ✓ (SFTP) | ✓ | ✗ | ✗ | ✗ |
| Warp | ✗ | SCP commands | ✗ | ✗ | ✗ |
| OpenSSH + Custom | ✗ (SCP/rsync) | CLI only | ✗ | rsync | ✗ |
| CtrlOps | ✓ | ✓ | ✓ | ✓ | ✓ |
### Monitoring & debugging [#monitoring--debugging]
Running `htop` and `df -h` isn't monitoring - it's checking. Real monitoring means a visual dashboard that shows you server health without typing commands. Only CtrlOps offers this natively.
| Tool | Live Metrics Dashboard | Process Management | Log Viewer | One-Click Cache Clear | AI Diagnostics |
| ---------------- | ---------------------- | ------------------ | ------------ | --------------------- | ---------------------- |
| macOS Terminal | ✗ | `top`/`htop` | `tail -f` | ✗ | ✗ |
| iTerm2 | ✗ | `top`/`htop` | `tail -f` | ✗ | ✗ |
| Termius | ✗ | SSH commands | SSH commands | ✗ | Partial (autocomplete) |
| Warp | ✗ | SSH commands | SSH commands | ✗ | ✓ (Agent Mode) |
| OpenSSH + Custom | ✗ | Scripts | Scripts | Scripts | ✗ |
| CtrlOps | ✓ | ✓ | ✓ | ✓ | ✓ (with approval) |
### Automation & AI support [#automation--ai-support]
Warp has the strongest AI but auto-runs commands. CtrlOps has approval-gated AI. Termius has basic autocomplete. The rest have none.
| Tool | AI Command Generation | AI Auto-Execute | Human Approval Gate | One-Click Deploy | Deployment Templates |
| ---------------- | --------------------- | --------------- | ------------------- | ---------------- | -------------------- |
| macOS Terminal | ✗ | ✗ | N/A | ✗ | ✗ |
| iTerm2 | ✗ | ✗ | N/A | ✗ | ✗ |
| Termius | Partial (Gloria) | ✗ | N/A | ✗ | ✗ |
| Warp | ✓ (Agent Mode) | ✓ | ✗ | ✗ | ✓ (Workflows) |
| OpenSSH + Custom | ✗ | ✗ | N/A | Scripts | Scripts |
| CtrlOps | ✓ | ✗ | ✓ | ✓ | ✓ |
### Pricing comparison [#pricing-comparison]
Price matters - especially when you're paying per user for a team. Here's what you actually pay annually.
| Tool | Free Tier | Individual/Month | Annual Cost (Individual) | Team (5 users/month) | Cloud Account Required |
| ---------------- | ------------- | ---------------- | --------------------------- | -------------------- | ---------------------- |
| macOS Terminal | ✓ Free | $0 | $0 | $0 | ✗ |
| iTerm2 | ✓ Free | $0 | $0 | $0 | ✗ |
| Termius | Limited | $10 | $120 | $100 ($20/user) | ✓ |
| Warp | Limited | $20 | $240 ($216 billed annually) | $100 ($20/user) | ✓ |
| OpenSSH + Custom | ✓ Free | $0 | $0 | $0 | ✗ |
| CtrlOps | 1-month trial | $7 | $84 | $35 ($7/user) | ✗ |
The per-seat difference adds up fast: **Termius and Warp team plans are $20/user**, so a 5-person team costs $100/month on either. **CtrlOps is $7/user/month** with unlimited servers, so the same team costs $35/month - roughly a third of the price.
One important note on pricing: free tools (Terminal, iTerm2, OpenSSH) are genuinely free, but they come with a hidden cost - the time you spend managing workarounds, maintaining scripts, and switching between supplementary tools. That time has a real dollar value, especially for freelancers and agencies billing by the hour.
### Head-to-Head: Termius vs iTerm2 vs Warp vs CtrlOps [#head-to-head-termius-vs-iterm2-vs-warp-vs-ctrlops]
If you're choosing between the four main options that come up in every "best ssh client for mac" search, here's the no-fluff breakdown of what each one actually does - and where it stops.
| | **iTerm2** | **Termius** | **Warp** | **CtrlOps** |
| ----------------------------- | -------------------- | ----------------------- | -------------------- | ---------------------------- |
| **Best for** | Terminal power users | Cross-device SSH sync | AI-first terminal | All-in-one server management |
| **Price** | Free | $10/mo per user | $20/mo per user | $7/mo per user |
| **Multi-server directory** | ✗ | ✓ | ✗ | ✓ |
| **One-click connect** | ✗ | ✓ | ✗ | ✓ |
| **File manager (GUI)** | ✗ | ✓ (SFTP) | ✗ | ✓ (full GUI) |
| **Infrastructure monitoring** | ✗ | ✗ | ✗ | ✓ (live CPU/RAM/disk) |
| **One-click app deployment** | ✗ | ✗ | ✗ | ✓ |
| **AI terminal** | ✗ | Partial (autocomplete) | ✓ (auto-executes) | ✓ (approval-gated) |
| **AI approval gate** | N/A | N/A | ✗ | ✓ |
| **Cloud account required** | ✗ | ✓ | ✓ | ✗ |
| **SSH keys stored** | Local | Cloud (Termius servers) | Cloud (Warp servers) | Local only |
| **Mobile app** | ✗ | ✓ (iOS + Android) | ✗ | ✗ |
| **Team pricing** | Free | $20/user/mo | $20/user/mo | $7/user/mo |
**The honest summary:**
* **iTerm2** wins if you want the best free terminal emulator and nothing else. It doesn't manage servers - it gives you a better window to manage them yourself.
* **Termius** wins if you need the same SSH setup on your laptop, desktop, and phone. The cross-device sync is genuinely useful. Cloud credential storage is the trade-off.
* **Warp** wins if you live in the terminal all day and want AI that moves at your speed. Keep it off production servers unless you're comfortable with auto-execute.
* **CtrlOps** wins if your daily work involves more than SSH - file transfers, deployments, monitoring, debugging under pressure. It's the only tool in this table that replaces 4+ apps.
No single tool is best for every developer. The question is which column matches how you actually spend your time.
***
## GUI vs Terminal: What Actually Works [#gui-vs-terminal-what-actually-works]
There's a strange tribalism around this topic. Some developers treat GUI tools as a sign of weakness. Others can't imagine typing `scp -r user@server:/var/www/html/config /tmp/backup` by hand. The truth is simpler: **each has a place, and knowing when to use which matters more than picking a side.**
### When CLI is faster and more flexible [#when-cli-is-faster-and-more-flexible]
The terminal wins when you know exactly what you want to do and how to do it:
* **Quick one-off commands.** `systemctl restart nginx` is faster to type than navigating a UI.
* **Scripting and automation.** Bash scripts, cron jobs, CI/CD pipelines - all CLI. No GUI can replace this.
* **Piping and chaining.** `cat access.log | grep "404" | sort | uniq -c | sort -rn | head -20` - try that in a GUI.
* **Batch operations.** Running the same command across 10 servers with a for-loop beats clicking through 10 GUI screens.
* **SSH tunnels and port forwarding.** The `-L` and `-R` flags are second nature for anyone who's used them before.
If you're a senior engineer who lives in the terminal, CLI is always going to feel more natural. And that's fine - most SSH clients (including CtrlOps and Termius) still give you a full terminal alongside their GUI features.
### When GUI saves hours of effort [#when-gui-saves-hours-of-effort]
The GUI wins when the task involves visual navigation, multi-step processes, or information that's hard to parse as raw text:
* **Finding and uploading files.** Navigating a remote directory tree in a GUI file manager takes seconds. Doing the same with `ls`, `cd`, and `scp` takes minutes - and you need to remember exact paths.
* **Monitoring multiple servers.** A dashboard showing CPU, RAM, and disk for 10 servers at a glance vs. opening 10 terminal tabs and running `htop` in each one. There's no comparison.
* **Onboarding new team members.** Teaching a junior developer to use a GUI is a 30-minute conversation. Teaching them bash, SSH config, and deployment scripts is a 2-week process.
* **Deployment configuration.** Filling in a form with your repo URL, environment variables, domain, and SSL toggle vs. writing and debugging a deployment script from scratch.
#### Real examples from deployments and debugging [#real-examples-from-deployments-and-debugging]
**The deployment example:** You need to deploy a Next.js app to a fresh VPS. With CLI, you're running 12+ commands manually - `git clone`, `npm install`, `npm run build`, `pm2 start`, `ecosystem.config.js` setup, Nginx configuration, Certbot SSL. Miss one step and nothing works. With CtrlOps's GUI, you fill in a form and click Create. The same steps happen, but you don't have to remember them.
**The debugging example:** Your production server is slow at 2AM. With CLI, you run `top`, `df -h`, `free -m`, `pm2 logs`, and `nginx -t` - five separate commands, each giving you a piece of the puzzle. You connect the dots in your head. With a GUI dashboard, you see CPU at 94%, disk at 91%, and a spike in error logs - all on one screen in two seconds.
**The verdict:** Use both. A good SSH client gives you a terminal when you want it and a GUI when you need it. The problem with macOS Terminal and iTerm2 isn't that they're CLI - it's that they're *only* CLI. The problem with some GUI tools isn't the GUI - it's that they hide the terminal entirely.
***
## Security Breakdown (What Most Developers Ignore) [#security-breakdown-what-most-developers-ignore]
Most SSH client comparisons barely mention security. They'll note "supports SSH key authentication" and move on. But how your SSH client handles credentials - where keys are stored, who can access them, what happens during a breach - is arguably the most important factor in your choice. Especially if you manage servers for clients or employers.
### Local vs cloud-based SSH key storage [#local-vs-cloud-based-ssh-key-storage]
This is the single biggest security distinction between SSH clients, and most developers don't think about it until a client or auditor asks.
**Cloud-based storage (Termius, Warp):** Your SSH keys and server credentials sync to the vendor's cloud servers. This enables cross-device access - your phone, your laptop, your desktop all have the same connections. It's convenient. It also means your keys exist on someone else's infrastructure.
**Local-only storage (CtrlOps, iTerm2, OpenSSH):** Your credentials stay on your machine. No cloud sync. No third-party server holding your keys. You can't access them from another device, but nobody else can either.
Here's why this matters more than you think:
| Factor | Cloud Storage | Local-Only Storage |
| --------------------------- | ------------------------------------------------- | ------------------------------------------------------ |
| **Third-party breach risk** | If vendor is breached, your keys could be exposed | No third-party exposure - keys don't leave your device |
| **Compliance** | May violate client contracts, GDPR, HIPAA | Easier to comply - data never leaves your machine |
| **Audit questions** | "On a third-party server" | "On our local machine" |
| **Cross-device access** | ✓ Access from any device | ✗ Only from your machine |
| **Account dependency** | ✗ If vendor shuts down, access may be lost | ✓ Your data, your control |
**Bottom line on storage:** For internal projects with no compliance pressure, cloud storage is a fair convenience trade. For client work, regulated industries (SOC2, HIPAA, PCI), or any contract that mentions "third-party data handling" - local-only credential storage isn't a feature, it's a baseline requirement. Picking the wrong tool here turns into a contract violation discovered during an audit, not a security incident you can fix later.
#### Risks in client and production environments [#risks-in-client-and-production-environments]
If you're a freelancer or agency managing servers for clients, cloud-based key storage isn't just a theoretical risk - it can be a **contract violation**. Many enterprise clients explicitly forbid third-party credential storage.
If a client asks "where are our SSH keys stored?" and your answer is "on Termius's servers," you've got a problem.
The numbers back this up. Stolen credentials were involved in 16 - 20% of confirmed data breaches in 2024 - 2025 ([Verizon DBIR](https://www.verizon.com/business/resources/reports/dbir/)). And per the [IBM Cost of a Data Breach Report 2024](https://www.ibm.com/reports/data-breach), the average breach now costs $4.88 million.
Even if the breach doesn't happen through your SSH client, having credentials on a third-party server expands your attack surface.
For startup CTOs, there's another angle: **offboarding**. When a developer leaves, how quickly can you revoke their SSH access? With cloud-based tools, their account may still have access until you manually remove them - and their locally cached keys may persist even after removal. With local-only tools, credentials exist only on specific devices you control.
### Credential management best practices [#credential-management-best-practices]
Regardless of which SSH client you choose, follow these rules:
1. **Never store private keys in cloud-synced directories.** Not iCloud, not Dropbox, not Google Drive. If it syncs, it can leak.
2. **Use SSH key passphrases.** An unencrypted private key on a stolen laptop is an open door. A passphrase-encrypted key buys you time.
3. **Rotate keys when team members leave.** This should take minutes, not weeks. If your SSH client makes rotation hard, that's a problem.
4. **Audit who has access to what.** If you can't answer "which developers have SSH access to the production database server?" in under 60 seconds, you have a visibility problem.
5. **Prefer tools that keep credentials local.** This isn't paranoia - it's risk reduction. Every third party you add to your credential chain is another potential failure point.
6. **Use different keys for different servers.** One key for everything means one compromise breaks everything. Yes, it's more to manage. That's the trade-off.
The security choice isn't about being paranoid. It's about being able to answer hard questions from clients, auditors, and your own team - without guessing. For the complete key lifecycle - generation, passphrases, rotation, and revocation - the [SSH key management best practices](/blog/ssh-key-management-best-practices) guide goes deeper on every rule above.
***
## Real Use Cases (Where Tools Succeed or Fail) [#real-use-cases-where-tools-succeed-or-fail]
The real test of any SSH client is what happens in a specific scenario - not what its feature table says. Here are three real workflows where tools either save you or slow you down.
### Managing multiple servers (5 - 20 servers) [#managing-multiple-servers-5---20-servers]
**The scenario:** You manage 12 servers across staging, production, and three client projects. You need to connect to the right server quickly, check its status, and move on.
**macOS Terminal / iTerm2:** You've got 12 tabs open, each labeled with an IP address you can't remember. You keep a notes file with the mapping. Half the time, you connect to the wrong server first. When a client asks "what's the disk status on our production server?", you SSH in, run `df -h`, and report back - 3 minutes per server.
**Termius:** Better. Named servers in folders, one-click connect. But no fleet view - to check disk on 12 servers, you still connect to each one individually. You can't see all server statuses at a glance.
**CtrlOps:** All 12 servers as cards in one view. Live CPU, RAM, and disk metrics visible without connecting. Click into any server for details. One-click cache clear. The difference between "3 minutes per server" and "3 seconds per server" adds up fast when you do this daily.
**Winner for multi-server:** CtrlOps > Termius > iTerm2 > Terminal
### Deploying applications quickly [#deploying-applications-quickly]
**The scenario:** You need to deploy a Next.js app with environment variables, PM2 process management, Nginx reverse proxy, and SSL certificate.
**macOS Terminal / iTerm2:** You follow a [13-step deployment checklist](/blog/deploy-nodejs-app-linux-vps) (or a blog post). 12+ commands, each with potential failure points. If you miss the PM2 ecosystem config, your app restarts on reboot. If you skip the Nginx config, your domain doesn't resolve. If you forget Certbot, no HTTPS. Total time: 30 - 45 minutes if everything goes right. Much longer if something breaks.
**Termius:** Same manual process. Termius gives you a nicer connection experience but doesn't automate deployment. You're still running the same commands.
**Warp:** The AI can generate deployment commands for you, which saves looking them up. But it auto-runs them - and on production, that's risky. One misread prompt and you've overwritten the wrong config.
**CtrlOps:** Fill in a form - repo URL, framework, env variables, domain, SSL toggle. Click Create. CtrlOps handles git clone, build, PM2 setup, Nginx config, and Certbot. Total time: 5 minutes.
**Winner for deployment:** CtrlOps >> Warp > iTerm2 = Terminal = Termius
### Debugging production issues under pressure [#debugging-production-issues-under-pressure]
**The scenario:** It's 2AM. Your production server is down. You're half awake, on your laptop, trying to figure out what happened.
**macOS Terminal / iTerm2:** Find the server IP (where did you save it?), SSH in, run `htop`, `df -h`, `pm2 logs`, `nginx -t`, `journalctl -u nginx`. Read raw output. Try to remember what the numbers should be. Google error messages. Paste into ChatGPT. Try the fix. Hope it works.
**Termius:** Same debugging process. Named servers help you connect faster, but the investigation is still manual commands and raw output.
**Warp:** AI Agent Mode is actually helpful here. Type "production server is down, check what's wrong" and Warp generates diagnostic commands. But it auto-runs them - and at 2AM, auto-running commands on production is the last thing you want.
**CtrlOps:** Open the app, see the server card showing disk at 94% and CPU spiking. Click in, see the top processes and recent log errors in the Console tab. Ask the AI "why is this server slow?" - it generates diagnostic commands, but shows them to you first. You approve, then it runs. You stay in control.
#### Which tools hold up in real scenarios [#which-tools-hold-up-in-real-scenarios]
| Scenario | Best Tool | Why |
| ---------------------------------------- | ------------------ | ----------------------------------------------- |
| Quick one-off command on a single server | iTerm2 or Terminal | Fast, no overhead, you know the command |
| Managing 5+ servers daily | CtrlOps | Fleet view, one-click access, live metrics |
| First-time deployment of a web app | CtrlOps | Guided form replaces 12+ manual commands |
| Debugging at 2AM with pressure | CtrlOps | Dashboard + AI with approval gates |
| Team collaboration on server access | Termius or CtrlOps | Shared server directories, team features |
| Pure terminal power user workflow | iTerm2 + Warp | Best terminal experiences available |
| Maximum security, no third-party cloud | CtrlOps or OpenSSH | Credentials stay local, no vendor cloud account |
| Mobile SSH access | Termius | Only tool with mature iOS/Android apps |
No single tool wins every scenario. That's the point. The "best" SSH client for Mac depends on which of these scenarios you face most often.
***
## What Actually Works (Direct Recommendations) [#what-actually-works-direct-recommendations]
Here are direct recommendations for each developer type - no hedging, no "it depends on your needs" cop-outs.
### Best for beginners [#best-for-beginners]
**iTerm2.** If you're new to server management and just need to connect, run commands, and learn the ropes, iTerm2 gives you a better terminal than macOS Terminal without overwhelming you with options. It's free, it works, and you won't outgrow it in a month.
Skip macOS Terminal - the lack of split panes and search makes learning harder than it needs to be. Skip the paid tools until you understand what you're missing. Once you're managing 3+ servers and opening Cyberduck for file transfers, it's time to upgrade.
### Best for power users [#best-for-power-users]
**Warp + iTerm2 as backup.** If you live in the terminal all day, every day, Warp's AI-powered command generation and IDE-like editing are genuinely useful. The speed is real (Rust-based, no Electron lag), and the AI saves you from Googling syntax you've used a hundred times.
But keep iTerm2 as your fallback. Warp is tied to a cloud account and their service. When their login or service has an outage - and outages happen - you need a terminal that doesn't depend on a vendor. iTerm2 is that backup.
One caveat: if you ever run commands on production servers, be careful with Warp's auto-execute AI. It's fast but unforgiving. There's no undo on `rm -rf`.
**Reality check on auto-running AI in production:** Speed is a feature in development. It's a liability in production. Any AI terminal that runs commands without an approval gate is one misinterpreted prompt away from an incident. If a tool's selling point is "the AI just does it," that's a developer-machine feature - not a server-management feature. Always verify there's a review step before commands hit a live server.
### Best for teams [#best-for-teams]
**Termius.** The team features - shared server vaults, role-based access, and cross-platform sync - make it the most mature option for team SSH management. Every team member gets the same server list on every device. Onboarding a new developer takes minutes, not hours.
The trade-off is cloud credential storage. If your team handles sensitive client data or operates under compliance requirements (GDPR, HIPAA, SOC 2), storing SSH keys on Termius's servers may not be acceptable. For internal infrastructure with lower compliance sensitivity, Termius works well.
For teams that need local-first security, CtrlOps is the alternative - same organizational benefits, but credentials never leave team members' machines.
### Best all-in-one solution [#best-all-in-one-solution]
**CtrlOps.** This is the only tool that replaces your terminal, file manager, monitoring dashboard, and deployment scripts in one app. If your current setup involves switching between 3 - 5 tools for server management, CtrlOps eliminates that switching.
At $7/user/month with unlimited servers, it's also structurally cheaper than running Termius Pro per-seat for SSH + a separate monitoring tool + the time cost of manual deployments. The 1-month free trial lets you validate the workflow before committing.
⚠️
**Where CtrlOps doesn't fit (yet):**
No tool wins everywhere. CtrlOps has no mobile app - if you need to SSH from your phone, Termius is the only real option in 2026. It's also a newer product, so the community resources, third-party integrations, and accumulated Stack Overflow answers are thinner than for iTerm2 or Termius. And if your stack runs primarily on serverless (Lambda, Cloud Functions) or container orchestration (Kubernetes), CtrlOps' SSH-based model isn't the right shape for those environments.
**Bottom line:** If your daily work involves managing multiple servers, deploying applications, and debugging production issues - and you're tired of juggling tools - CtrlOps is the most complete answer available on Mac right now.
***
## Final Verdict: Which SSH Client Should You Use? [#final-verdict-which-ssh-client-should-you-use]
There's no single "best SSH client for Mac" - only the best one for your situation. Use these three questions to cut through the noise.
### Decision framework based on real use cases [#decision-framework-based-on-real-use-cases]
Ask yourself these three questions:
**1. How many servers do you manage?**
* **1 - 2 servers:** macOS Terminal or iTerm2 is enough. Don't over-tool a simple problem.
* **3 - 10 servers:** You need organization. Termius or CtrlOps - both give you named hosts and one-click connections.
* **10+ servers:** You need fleet visibility. CtrlOps is the only tool that shows live metrics for all servers at a glance without connecting individually.
**2. What's your biggest daily friction?**
* **Remembering server details and connecting:** Any dedicated SSH client (Termius, CtrlOps) solves this.
* **Transferring files:** You need built-in SFTP. Termius and CtrlOps have it; Terminal and Warp don't.
* **Deploying applications:** You need automation. CtrlOps is the only tool with one-click deployment.
* **Debugging under pressure:** You need monitoring + AI help. CtrlOps (dashboard + approved AI) or Warp (auto-run AI, riskier).
* **Context switching between tools:** You need consolidation. CtrlOps replaces terminal + SFTP + monitoring + deployment scripts.
**3. What are your security requirements?**
* **Internal projects, no compliance pressure:** Any tool works. Cloud sync (Termius, Warp) is convenient.
* **Client projects or compliance requirements:** Local-only storage is non-negotiable. CtrlOps or OpenSSH setups.
* **Locked-down environments where no third-party service is allowed:** OpenSSH is the only fully self-contained choice. CtrlOps keeps credentials local but the app itself needs internet access; Termius and Warp additionally require vendor cloud accounts.
### Quick decision table [#quick-decision-table]
| You Are | Your Priority | Best Pick | Backup |
| --------------------------------- | ----------------------------- | --------- | ----------------------- |
| Solo dev, 1 - 2 servers | Keep it simple | iTerm2 | macOS Terminal |
| Freelancer, 5 - 15 client servers | Organization + security | CtrlOps | Termius |
| Power user, terminal-first | Speed + AI | Warp | iTerm2 |
| Startup CTO, team of 5 - 15 | Visibility + control | CtrlOps | Termius (if cloud OK) |
| Agency, rotating clients | Security + consolidation | CtrlOps | OpenSSH + custom |
| Student, learning SSH | Free + beginner-friendly | iTerm2 | macOS Terminal |
| DevOps engineer, 20+ servers | Fleet management + automation | CtrlOps | iTerm2 + custom scripts |
One last thing: don't let tool choice become procrastination. The difference between any SSH client on this list and no SSH client is huge. The difference between the "perfect" SSH client and a "good enough" one is small. Pick one that fits your biggest pain point today, and switch if it stops fitting. The best tool is the one you actually use, consistently, without fighting it. Everything else is just another tab to manage.
Not on a Mac all day? We've run the same real-workflow tests for the [best SSH clients for Windows](/blog/best-ssh-clients-windows) and the [best SSH clients for Linux](/blog/best-ssh-client-linux), so you can keep a consistent setup across machines.
***
## Frequently Asked Questions (FAQs) [#frequently-asked-questions-faqs]
It depends on your workflow. For managing multiple servers with file transfers, monitoring, and deployments, **CtrlOps** is the most complete option. For pure terminal power users, **Warp** offers the best AI-enhanced experience. For team SSH management with cross-device sync, **Termius** is the most mature choice. For free, lightweight use, **iTerm2** beats macOS Terminal in every way that matters. There's no single winner - only the right tool for how you work.
Not always. If you manage 1 - 2 servers and know your way around the command line, iTerm2 or macOS Terminal works fine. But if you regularly transfer files, check server health across multiple machines, or deploy applications, a GUI saves 15 - 30 minutes per session. The question isn't "is GUI better than CLI?" - it's "does my workflow involve tasks that GUI handles faster?" For most developers managing 3+ servers, the answer is yes.
Termius is a well-built product from a reputable company, and it encrypts your credentials in transit and at rest. However, it **syncs your SSH keys to their cloud servers** by design. This is a feature, not a bug - it enables cross-device access. But it also means your credentials exist on third-party infrastructure. For internal projects, this is usually fine. For client work with compliance requirements, it may not be acceptable. The security concern isn't about Termius's competence - it's about where your keys live.
Almost everything on this list. **iTerm2** is the most direct upgrade - same terminal experience with split panes, search, and profiles, still free. If you want a modern SSH client with a server directory and file transfers, **Termius** is the most popular choice. If you want AI-assisted commands, **Warp** leads. If you want an all-in-one tool that replaces your entire server management stack, **CtrlOps** is the only option that covers SSH, file management, monitoring, and deployment in one app.
For server management, yes - by a wide margin. **iTerm2 adds split panes, search, profiles, triggers, and autocomplete** without changing the underlying terminal experience. It's still free, still local-only, and runs on the same Mac you already have. The one reason to stick with Terminal: you want the absolute minimum tool footprint and don't need any of iTerm2's features. For everyone else managing more than one server, iTerm2 is the strict upgrade.
**Use it with caution.** Warp's standout feature is AI Agent Mode, which generates and auto-executes commands from natural language requests. On a development machine, that speed is a feature. On a production server, it's a risk - there's no approval gate before commands run, so one misinterpreted prompt can do real damage. For production work, either disable Agent Mode and use Warp as a regular terminal, or pick a tool with an approval gate (CtrlOps shows generated commands before executing).
A few defaults that cover most teams: **keep private keys in `~/.ssh/` with permissions `600`** (the OS won't accept anything looser), **always set a passphrase** on private keys so a stolen laptop isn't an open door, **never store keys in cloud-synced folders** (iCloud, Dropbox, Google Drive), and **prefer SSH clients with local-only credential storage** for client work - cloud-sync tools like Termius and Warp move your keys to third-party servers. Rotate keys when team members leave and use different keys for different environments.
**SSH (Secure Shell) gives you a remote terminal** - you run commands on the server as if you were sitting at its keyboard. **SFTP (Secure File Transfer Protocol) gives you remote file access** - upload, download, navigate directories. Both use the same SSH connection underneath. Some tools do one well (PuTTY for SSH, Cyberduck for SFTP). Modern SSH clients like Termius and CtrlOps include both in one app, so you don't switch tools mid-task.
No. **MobaXterm does not work on Mac** - it is Windows-only software. MobaXterm is a popular all-in-one terminal for Windows users that bundles SSH, X server, RDP, VNC, and SFTP into one app. It has no macOS version and no announced plans to build one. If you're looking for an ssh client for mac like PuTTY or MobaXterm - tools that combine SSH with file transfer and multi-protocol support - the closest Mac equivalents are **Termius** (cross-platform, polished UI, built-in SFTP) or **CtrlOps** (SSH + file manager + monitoring + deployment in one local-first app). For pure terminal experience closest to MobaXterm's tab-based layout, **iTerm2** with split panes is the free starting point. Mac developers generally don't need MobaXterm's X11 server, which was its biggest differentiator on Windows - macOS handles Unix tools natively via Terminal. For a full breakdown of the five strongest options, see our guide to the [best MobaXterm alternatives for Mac](/blog/mobaxterm-alternatives-mac).
**Yes.** macOS ships with [OpenSSH](https://www.openssh.com/) pre-installed - that's what powers the `ssh` command in Terminal. It's the reference implementation of the SSH protocol and works for any server you have access to. The question isn't whether macOS has SSH (it does); it's whether the default `ssh user@ip` workflow scales when you manage multiple servers, transfer files, and want monitoring. For most developers managing 3+ servers, the answer is no - you'll want an SSH client with a server directory and file manager on top of OpenSSH.
They solve different problems, so the comparison depends on what you need. iTerm2 is a free, powerful terminal emulator - it gives you split panes, search, and profiles, but no server directory, no file transfers, and no cross-device sync. Termius is a dedicated SSH client with a polished server directory, built-in SFTP, and cross-platform sync across Mac, Windows, iOS, and Android. If you manage multiple servers and want named connections with one-click access, Termius does things iTerm2 simply can't. If you want the best free terminal experience and handle your own SSH config, iTerm2 wins. They are not direct competitors - iTerm2 is a terminal; Termius is a server management tool.
iTerm2 is the best free SSH client for Mac beginners. It is already designed for macOS, installs in minutes, and adds split panes, search, and connection profiles on top of the built-in terminal - all at no cost. macOS Terminal works but lacks the quality-of-life features that make learning easier. For beginners who quickly outgrow basic SSH and start transferring files or managing 3+ servers, CtrlOps offers a one-month free trial with a GUI that removes the need to memorize commands from day one.
Free options with file transfer: **OpenSSH** (via `scp`/`rsync` commands, no GUI). Among paid tools with a full GUI file manager: **CtrlOps** at $7/user/month is the lowest-cost option that includes drag-and-drop file management, AI terminal, and monitoring. **Termius Pro** at $10/user/month offers SFTP but no monitoring or deployment.
---
# 9 Best SSH Clients for Windows in 2026 (Free & Paid) (/blog/best-ssh-clients-windows)
Author: Hiren Kalariya | Role: Co-Founder & CEO, TST Technology | Published: 2026-06-16 | Updated: 2026-07-27 | Tags: SSH client for Windows, PuTTY alternatives, Windows terminal, server management, AI terminal | Reading Time: 24 min read
> We tested 9 SSH clients for Windows across real workflows - PuTTY, MobaXterm, Termius, Warp, and CtrlOps. Compare features, security, and pricing for 2026.
The best SSH client for Windows in 2026 is **CtrlOps** for anyone managing more than one server - it combines SSH, a GUI file manager, live monitoring, approval-gated AI, and one-click deployment at $7/user/month. **PuTTY** is the lightest free option, **MobaXterm** the best free all-in-one toolkit, **Termius** the pick for cross-device sync, and **Warp** the strongest AI-first terminal.
## 9 Best SSH Clients for Windows in 2026 [#9-best-ssh-clients-for-windows-in-2026]
The 9 best SSH clients for Windows in 2026 are CtrlOps (all-in-one server management), PuTTY (free lightweight), MobaXterm (Windows power users), Windows Terminal + OpenSSH (built-in), Termius (cross-device sync), Bitvise (free SFTP), Tabby (open-source), SecureCRT (enterprise compliance), and Warp (AI-first terminal). We tested each against the same real-world scenarios.
| Tool | Best For | Price | AI | File Manager | Local Credentials |
| -------------------------- | -------------------------------- | ------------------- | ---------------------- | --------------------- | ----------------- |
| **CtrlOps** | **All-in-one server management** | **$7/user/mo** | **✓ Approval-gated** | **✓ Full GUI** | **✓ Local-only** |
| PuTTY | Lightweight SSH basics | Free | ✗ | ✗ | ✓ Local |
| MobaXterm | Windows power users | Free / $69 one-time | ✗ | ✓ Basic SFTP | ✓ Local |
| Windows Terminal + OpenSSH | No-install SSH | Free (built-in) | ✗ | ✗ | ✓ Local |
| Termius | Cross-device sync | $10/user/mo | Partial (autocomplete) | ✓ SFTP | ✗ Cloud |
| Bitvise | Free SSH + SFTP | Free | ✗ | ✓ SFTP GUI | ✓ Local |
| Tabby | Open-source terminal | Free | ✗ | ✓ SFTP/Zmodem | ✓ Local |
| SecureCRT | Enterprise compliance | \~$119/license | ✗ | ✗ (SecureFX separate) | ✓ Local |
| Warp | AI-first coding terminal | $20/mo | ✓ Auto-run | ✗ | ✗ Cloud |
Prefer to watch instead? The full comparison - all nine tools, the deploy race, and the SSH key security question - in under 8 minutes:
***
### 1. CtrlOps: Best for AI-Powered Server Management [#1-ctrlops-best-for-ai-powered-server-management]
[CtrlOps](https://ctrlops.io/) takes a fundamentally different approach from every other tool on this list.
Instead of being a better terminal, it replaces your entire server management stack: terminal, file manager, monitoring dashboard, and deployment system, all in one desktop app.

**Pros of CtrlOps:**
* **Named server cards.** Connect to "Prod-Backend" or "Client-XYZ-Staging" in one click instead of remembering raw IPs.
* **Full [GUI file manager](https://ctrlops.io/docs/modules/file-manager).** Upload, download, edit remote files with drag-and-drop. No SCP commands, no separate SFTP tool.
* **Approval-gated [AI terminal](https://ctrlops.io/docs/modules/ai-terminal).** Ask "why is my server slow?" and get diagnostic commands shown before execution. You approve, then it runs.
* **One-click [app deployment](https://ctrlops.io/docs/modules/deployment).** Pick your framework, paste GitHub repo, add env variables. CtrlOps handles git clone, npm install, PM2, Nginx, and SSL.
* **[Infrastructure monitoring](https://ctrlops.io/docs/modules/infra-details) + [Script Directory](https://ctrlops.io/docs/modules/ai-terminal/scripts).** Live CPU, RAM, disk for every server. Save reusable command scripts with `{{variable_name}}` placeholders. Local-first security with AES-256 encryption, no cloud sync.
**CtrlOps Limitations:**
* No mobile app, Termius wins for phone-based SSH
* No serverless or Kubernetes support
**Pricing:** $7/user/month (unlimited servers). [1 month free trial](https://ctrlops.io/pricing), no credit card required.
**Platforms:** Windows, macOS (Apple Silicon + Intel), Linux.
***
### 2. PuTTY: Best Free Lightweight SSH Client [#2-putty-best-free-lightweight-ssh-client]
[PuTTY](https://www.chiark.greenend.org.uk/~sgtatham/putty/latest.html) has been the default SSH client for Windows since 1999. It does exactly one thing well: opens SSH connections.
For quick one-off connections to a single server, nothing is faster to download and use.

**Pros of PuTTY:**
* Quick download with zero learning curve - just grab the .exe, enter an IP, and connect
* Supports SSH, Telnet, SCP, and raw serial connections
* Tiny footprint, runs from a single executable, no install required
* 25+ years of security audits and community trust
* Completely free, open-source
**PuTTY Limitations:**
* **No named server directory.** Sessions stored by raw IP in the Windows registry, in plain text. No aliases, no grouping.
* **No file transfer.** Upload a config? Open WinSCP separately, re-enter credentials.
* **No AI, no monitoring, no deployment.** You're alone with a blank terminal.
* **No tabs.** Each server is a separate PuTTY window. Five servers means five windows.
* **Registry storage is a security risk.** Session data lives in `HKEY_CURRENT_USER\Software\SimonTatham\PuTTY\Sessions`, unencrypted, accessible to any process on the machine.
**Pricing:** Free, open-source.
**Platforms:** Windows (primary), with unofficial Unix ports.
PuTTY is a reliable SSH client for Windows if you only need a free, no-frills connection and nothing else.
It's the wrong tool if you manage more than 2 servers or transfer files regularly.
Most developers who still use PuTTY in 2026 have outgrown it. They just haven't switched yet. See the full [CtrlOps vs PuTTY](https://ctrlops.io/compare/ctrlops-vs-putty) comparison or browse [PuTTY, Webmin, and ServerPilot alternatives](https://ctrlops.io/blog/putty-webmin-serverpilot-alternatives).
Migrating? Convert `.ppk` keys to OpenSSH format with our browser-based [PPK to OpenSSH converter](/tools/ppk-to-openssh-converter).
**Reality check:** PuTTY saves your sessions, including server addresses and usernames, in the Windows registry in plain text. That data is accessible to any process or user on your machine. For developers handling client servers or regulated data, this is a compliance concern, not just an inconvenience.
***
### 3. MobaXterm: Best All-in-One Windows Toolkit [#3-mobaxterm-best-all-in-one-windows-toolkit]
[MobaXterm](https://mobaxterm.mobatek.net/) is PuTTY with everything Windows administrators actually need bolted on.
One executable. No installation. SSH, RDP, VNC, FTP, SFTP browser, X11 server, and a built-in Unix terminal, all included.

**Pros of MobaXterm:**
* **Tabbed sessions:** manage multiple connections in one window
* **Built-in SFTP browser:** opens automatically alongside your SSH session
* **Embedded X11 server:** run graphical Linux applications remotely (unique on Windows)
* **Multi-protocol:** SSH, RDP, VNC, FTP, SFTP, Telnet, serial in one app
* **Portable mode:** runs from a USB drive
* **Macro recording:** automate repetitive command sequences
**MobaXterm Limitations:**
* **Windows only.** One Mac user on the team creates tool fragmentation.
* **No AI features.** You type every command manually.
* **No cloud sync or team collaboration.**
* **No infrastructure monitoring.** You run `htop` manually.
* **No one-click deployment.**
* **Free edition limits to 12 sessions:** enough for solo work, tight for teams.
**Pricing:** Free (Home edition, 12 sessions max). Professional: $69/user one-time.
**Platforms:** Windows only.
MobaXterm is the best free upgrade from PuTTY on Windows.
Tabbed interface, built-in SFTP, and X11 server solve real problems without spending a dollar.
Hard to beat at $0 for Windows-only shops.
**Comparing CtrlOps vs MobaXterm?**
Read our detailed feature comparison:
[CtrlOps vs MobaXterm](https://ctrlops.io/compare/ctrlops-vs-mobaxterm)
.
***
### 4. Windows Terminal + OpenSSH: Best Built-In Option [#4-windows-terminal--openssh-best-built-in-option]
Windows 10 and 11 ship with OpenSSH pre-installed. Combined with Windows Terminal, Microsoft's modern tab-based console, it serves as a built-in SSH terminal without requiring any third-party downloads.

**Pros of Windows Terminal:**
* **Already on your machine.** Open Terminal, type `ssh user@ip`, done.
* **Tabs and profiles:** multiple connections, split panes, custom styling
* **SSH config file:** save named hosts in `~/.ssh/config` for one-command connections
* **GPU-accelerated rendering:** Windows Terminal is fast and modern
* **WSL integration:** full Linux shell alongside SSH connections (if you live inside WSL or dual-boot, our [best SSH clients for Linux](/blog/best-ssh-client-linux) roundup covers that side too)
**Windows Terminal Limitations:**
* **No GUI file manager.** SCP or rsync commands only.
* **No server directory.** You maintain SSH config manually.
* **No AI.** Same blank-cursor experience as PuTTY in a nicer window.
* **No monitoring dashboard.** Diagnostic commands one at a time.
* **No deployment automation.**
**Pricing:** Free (built into Windows 10/11).
**Platforms:** Windows only.
The right choice if you don't want to install anything.
Surprisingly capable, better than PuTTY in many ways. But still just a terminal.
Managing 5+ servers and transferring files daily will push you toward additional tools.
***
### 5. Termius: Best for Cross-Platform Teams [#5-termius-best-for-cross-platform-teams]
[Termius](https://termius.com/index.html) is the most polished dedicated SSH client on the market.
It syncs your servers, credentials, and command snippets across Mac, Windows, Linux, iOS, and Android. It's the only tool on this list with genuinely usable mobile apps.

**Pros of Termius:**
* **Cross-device sync:** servers and credentials follow you everywhere, E2E encrypted
* **Clean UI:** named hosts, groups, tags, one-click connect
* **Built-in SFTP:** file transfers without a separate tool
* **AI-powered autocomplete:** suggests commands as you type
* **Mobile apps:** SSH from your phone during a production incident
* **Team vault:** shared server access with role-based controls
**Termius Limitations:**
* **SSH keys sync to Termius's cloud.** E2E encrypted, yes, but they live on third-party infrastructure. Some client contracts prohibit this.
* **No infrastructure monitoring.** You SSH in and run `htop` manually.
* **No one-click deployment.** Manual repo clones, PM2, Nginx setup.
* **AI is autocomplete, not diagnostics.** Suggests completions, doesn't understand server state.
* **Pricing scales per user.** Pro: $10/user/month. Team: $20/user/month. 5-person Team plan costs $100/month ($1,200/year).
**Pricing:** Free (Starter, local vault only). Pro: $10/user/month. Team: $20/user/month. Business: $30/user/month.
**Platforms:** Windows, macOS, Linux, iOS, Android.
Termius wins if you need the same SSH setup on every device. Mac users on the team can also check the [best SSH clients for Mac](https://ctrlops.io/blog/best-ssh-client-mac-2026) for a deeper comparison - and if the cloud key storage is what's pushing you away, we've rounded up the [best Termius alternatives for 2026](/blog/termius-alternatives) separately.
The trade-off is cloud credential storage and per-user pricing that gets expensive at team scale.
**Comparing CtrlOps vs Termius?**
Read our detailed breakdown of features, security, and pricing:
[CtrlOps vs Termius](https://ctrlops.io/compare/ctrlops-vs-termius)
.
***
### 6. Bitvise: Best Free SFTP + SSH Combo [#6-bitvise-best-free-sftp--ssh-combo]
[Bitvise](https://www.bitvise.com/) is a Windows-native SSH and SFTP client that's been quietly excellent for years.
Free for all use: personal, commercial, enterprise. No session limits. No feature gates. No per-user pricing.

**Pros of Bitvise:**
* **Completely free:** personal and commercial use, no restrictions
* **Graphical SFTP browser:** split-pane file transfer view alongside your terminal
* **Strong tunneling:** SSH port forwarding, SOCKS proxy, FTP-to-SFTP bridge
* **Windows-native:** not Electron. Fast and lightweight.
* **Automatic reconnection:** reconnects after dropped connections
**Bitvise Limitations:**
* **Windows only.** No Mac, Linux, or mobile.
* **No AI features.** Terminal only.
* **No server directory.** Connection profiles exist, but no fleet view.
* **No monitoring, no deployment, no automation.**
* **UI feels dated.** Functional, not modern.
**Pricing:** Free (SSH Client). SSH Server: paid separately.
**Platforms:** Windows only.
The best free SSH client for Windows if file transfers are core to your workflow.
The graphical SFTP browser eliminates WinSCP from your toolchain entirely.
***
### 7. Tabby: Best Open-Source Modern Terminal [#7-tabby-best-open-source-modern-terminal]
[Tabby](https://tabby.sh/) is a cross-platform, open-source terminal that modernizes SSH with tabs, split panes, a plugin ecosystem, and a built-in connection manager.
No subscription. No account required.

**Pros of Tabby:**
* **Free and open-source** (MIT license), no feature gates, no accounts
* **Cross-platform:** Windows, macOS, Linux with identical interface
* **Built-in SSH client** with profiles, SFTP, Zmodem transfers, key management
* **Plugin ecosystem:** extend with community-built plugins
* **Split panes and workspaces:** save complex layouts as profiles
* **Encrypted password manager:** local storage with master passphrase
* **Modern UI:** themes, ligatures, GPU-accelerated rendering
**Tabby Limitations:**
* **Resource-heavy.** Electron-based, uses more RAM than PuTTY or Bitvise.
* **No AI features.** No command generation, no diagnostics.
* **No monitoring or deployment.**
* **Learning curve.** Extensive config options, strength for power users, barrier for beginners.
* **Occasional stability issues** with certain plugin combinations.
**Pricing:** Free, open-source (MIT license).
**Platforms:** Windows, macOS, Linux.
Best choice for developers who want open-source with no vendor lock-in.
Significantly more capable than PuTTY. The trade-off is higher memory usage and zero AI or server management features.
***
### 8. SecureCRT: Best for Enterprise & Compliance [#8-securecrt-best-for-enterprise--compliance]
[SecureCRT](https://www.vandyke.com/products/securecrt/) by VanDyke Software has been the enterprise SSH client since 1995.
FIPS 140-2 validated. Advanced scripting in Python, VBScript, and Perl. Likely already on your organization's approved software list if you work in government, defense, or healthcare IT.

**Pros of SecureCRT:**
* **31 years of reliability:** enterprise trust built over decades
* **FIPS 140-2 compliance:** meets government security requirements
* **Advanced scripting:** automate workflows with Python, VBScript, Perl
* **Multi-protocol:** SSH, Telnet, Serial, RDP
* **Session management:** tabbed sessions, saved layouts, detailed logging
* **Smart card and PKI support:** hardware-based authentication
**SecureCRT Limitations:**
* **No AI features.** Manual command execution only.
* **Legacy UI.** Functional but dated.
* **Expensive for small teams.** \~$119/license one-time, plus optional annual maintenance. SecureFX (file transfer) sold separately.
* **No monitoring, no deployment.**
* **Overkill for most developers.** If you don't need FIPS or scripting, you're paying for unused features.
**Pricing:** \~$119/license one-time (includes 1 year of updates).
**Platforms:** Windows, macOS, Linux.
The right tool if your organization requires FIPS 140-2 or advanced scripting.
For freelancers and startup CTOs, you're paying enterprise prices for enterprise features you won't use.
**Comparing CtrlOps vs SecureCRT?**
Read our head-to-head analysis of enterprise capabilities vs modern server management:
[CtrlOps vs SecureCRT](https://ctrlops.io/compare/ctrlops-vs-securecrt)
.
***
### 9. Warp: Best AI-First Coding Terminal [#9-warp-best-ai-first-coding-terminal]
[Warp](https://www.warp.dev/) is the most well-funded AI terminal in the market. Backed by Sequoia Capital with [$73M+ in funding](https://sacra.com/c/warp/), built in Rust.
It reimagines the terminal with block-based output, IDE-like editing, and an AI Agent Mode that converts natural language into shell commands.

**Pros of Warp:**
* **AI Agent Mode:** type natural language, get shell commands generated and executed
* **Block-based output:** each command is a selectable, searchable block
* **IDE-like editing:** select, copy, edit previous commands like text
* **Rust-based performance:** GPU-accelerated, no Electron lag
* **Warp Drive:** save and share command sequences across teams
* **BYOK support:** bring your own OpenAI, Anthropic, or Google API key
**Warp Limitations:**
* **It's a coding terminal, not a server manager.** No server directory, no file manager, no monitoring, no deployment.
* **AI auto-runs commands by default.** On production, one misinterpreted prompt can cause real damage. No approval gate.
* **Cloud account required.** Can't use Warp without signing in.
* **Free tier is limited.** 150 AI credits for 2 months, then 75/month. Build plan: $20/month.
* **Not designed for multi-server fleet management.**
**Pricing:** Free (75 - 150 AI credits/month). Build: $20/month. Business: $50/user/month.
**Platforms:** Windows, macOS, Linux.
Warp is the best terminal experience on Windows, for local development.
The AI and editing features are excellent for writing and running code. For managing remote servers, Warp's AI doesn't have your server's context. And auto-executing commands on production is a risk most teams shouldn't take.
**Reality check:** Any AI terminal that auto-runs commands without a review step is a developer-machine feature, not a server-management feature. On a production server with real traffic, CtrlOps acts as a safety gate: its AI analyzes server logs and resource usage to generate the exact commands you need, but **nothing runs until you manually review and click approve**. This human-in-the-loop approach keeps you in full control, preventing accidental keystrokes or 2 AM debugging mistakes from turning into site-wide incidents.
> "The approve before execute thing is what sold me. Every other AI tool just runs stuff, and you find out what happened after."
>
> * Bhautik Kapadiya, [Product Hunt review](https://www.producthunt.com/products/ctrlops?comment=5381266)
***
## How Do All 9 SSH Clients Compare Feature-by-Feature? [#how-do-all-9-ssh-clients-compare-feature-by-feature]
CtrlOps is the only SSH client for Windows that includes a GUI file manager, infrastructure monitoring, AI command generation, and one-click deployment in one app. PuTTY and Windows Terminal handle basic SSH only. Termius and Warp add AI features but lack monitoring and deployment.
| Feature | CtrlOps | PuTTY | MobaXterm | Win Terminal | Termius | Bitvise | Tabby | SecureCRT | Warp |
| ------------------------- | ---------------- | ------------ | --------- | ------------ | ------------ | ------- | ------------- | --------------- | ------------- |
| Named server directory | ✓ | ✗ | Partial | ✗ | ✓ | Partial | ✓ | ✓ | ✗ |
| One-click connect | ✓ | ✗ | ✓ | ✗ | ✓ | ✓ | ✓ | ✓ | ✗ |
| Built-in file manager | ✓ Full GUI | ✗ | ✓ SFTP | ✗ | ✓ SFTP | ✓ SFTP | ✓ SFTP | ✗ | ✗ |
| Infrastructure monitoring | ✓ Dashboard | ✗ | ✗ | ✗ | ✗ | ✗ | ✗ | ✗ | ✗ |
| AI command generation | ✓ Approval-gated | ✗ | ✗ | ✗ | Partial | ✗ | ✗ | ✗ | ✓ Auto-run |
| One-click deployment | ✓ | ✗ | ✗ | ✗ | ✗ | ✗ | ✗ | ✗ | ✗ |
| Local credential storage | ✓ | ✓ (registry) | ✓ | ✓ | ✗ Cloud | ✓ | ✓ | ✓ | ✗ Cloud |
| Cross-platform | ✓ Win/Mac/Linux | Windows | Windows | Windows | All + Mobile | Windows | Win/Mac/Linux | Win/Mac/Linux | Win/Mac/Linux |
| Mobile app | ✗ | ✗ | ✗ | ✗ | ✓ | ✗ | ✗ | ✗ | ✗ |
| Price (individual/mo) | $7 | Free | Free | Free | $10 | Free | Free | \~$119 one-time | $20 |
| 5-user team (monthly) | $35 | $0 | $0 | $0 | $100 | $0 | $0 | \~$580 one-time | $100 |
*Team pricing based on each vendor's standard team tier as of June 2026: Termius Team at $20/user, Warp Build at $20/user (Warp Business is $50/user).*
The pricing difference compounds at team scale. Termius jumps from $10 to $20/user on Team tiers. Warp jumps from $20 to $50/user on Business. CtrlOps stays at $7/month/user with no team markups.
***
## How We Evaluated 9 SSH Clients for Windows [#how-we-evaluated-9-ssh-clients-for-windows]
We tested 9 SSH clients for Windows against four real-world tasks: connecting to a 5-server fleet, deploying a Node.js app, debugging a production incident, and transferring config files mid-session. This guide covers how each tool performed, not what the marketing page promises.
You're managing six client servers from your Windows laptop. It's 11 PM. A staging server is returning 502 errors.
You open PuTTY, dig through a notepad for the IP, connect, realize you need to upload a config fix. So you open WinSCP, re-enter the same credentials. Then you check a browser tab for CPU spikes.
Three tools. Four context switches. Twenty minutes. The actual problem is still unfixed.
If you're a **freelance developer juggling client servers**, a **startup CTO tired of 45-minute deployments**, or an **agency engineer managing staging and production across projects:** you've lived this.
We compared each tool across those four tasks. Here's what we found.
***
## What Makes a Great SSH Client for Windows in 2026? [#what-makes-a-great-ssh-client-for-windows-in-2026]
When evaluating different SSH tools for Windows, a great client does more than open a secure shell connection. It reduces the total number of tools you need to manage production servers, without creating new security problems.

Six criteria separate a useful SSH client from another window on your taskbar:
**1. Multi-server organization.**
Find and connect to the right server in under 10 seconds. Named hosts, one-click connect, visual grouping by environment, not raw IPs in a text file.
**2. Integrated file management.**
Uploading a config file shouldn't require opening WinSCP in a separate window. A built-in file browser eliminates one full tool from your stack.
> "the file manager feature is the one nobody talks about but everyone needs. separate SFTP client is such a pain when you just want to edit one config file."
>
> * Abhishek Akbari, Senior Full-Stack Developer at Torinit, [Product Hunt review](https://www.producthunt.com/products/ctrlops?comment=5381385)
**3. Credential security.**
Where do your SSH keys live? On your machine, or on a vendor's cloud server? For client work and regulated industries, the answer matters.
**4. AI assistance.**
Something that generates diagnostic commands on an unfamiliar stack saves 20 - 40 minutes per incident. Critical question: does the AI auto-run commands or show them first for approval?
**5. Deployment and automation.**
If you manually run `git pull`, `npm install`, `pm2 restart`, and configure Nginx every time you deploy, your SSH client isn't doing enough.
**6. Real price transparency.**
Per-user pricing adds up fast. A $10/user/month tool costs $600/year for a 5-person team. Know the true cost at your team size before committing.
**Bottom line:** The best SSH clients for Windows in 2026 are not just SSH clients. They're server management tools. Evaluating them purely on "can it open an SSH connection?" solves the wrong problem.
***
## How to Choose the Right SSH Client for Windows? [#how-to-choose-the-right-ssh-client-for-windows]
The "best SSH client for Windows" depends entirely on what you actually need to do with it.
No single tool wins every scenario. Here's a decision framework by role and friction.

**You're a developer managing client servers and deploying apps:**
CtrlOps.
Named servers keep client environments organized. Local credentials satisfy NDAs. The AI terminal diagnoses unfamiliar stacks without Googling.
One-click deployment replaces 12 manual commands with a single form. If you're evaluating broader [DevOps automation tools](https://ctrlops.io/blog/devops-automation-tools), CtrlOps fits as the deployment and monitoring layer.
**You're a beginner learning SSH:**
PuTTY.
Free, simple, 25 years of tutorials. When you start managing 3+ servers and opening separate tools for file transfers, it's time to upgrade.
**You're a Windows power user or sysadmin:**
MobaXterm.
SSH, RDP, VNC, X11, SFTP in one app. Free Home edition handles 12 sessions. $69 one-time Pro removes that limit.
**You don't want to install anything:**
Windows Terminal + OpenSSH.
Already on your machine. Add an SSH config file for named hosts and you've got a respectable setup with zero downloads.
**Your team needs the same setup on every device:**
Termius.
Cross-device sync across Mac, Windows, Linux, iOS, Android. Accept the cloud credential trade-off or verify compatibility with your security requirements first.
**You need enterprise compliance certifications:**
SecureCRT.
FIPS 140-2 validated, advanced scripting, 31 years of enterprise trust.
**You want open-source with no vendor lock-in:**
Tabby.
Free, MIT-licensed, cross-platform, plugin ecosystem. Heavier on RAM, but far more capable than PuTTY.
**You live in the terminal writing code locally:**
Warp.
AI agent features and IDE-like editing are the best available, for local development. Be careful with Agent Mode on production.
| Your Situation | Best Pick | Runner-Up |
| --------------------------------- | --------- | ---------------- |
| Freelancer, 5 - 15 client servers | CtrlOps | Termius |
| Beginner, 1 - 2 servers | PuTTY | Windows Terminal |
| Windows-only sysadmin | MobaXterm | Bitvise |
| Cross-platform team | Termius | CtrlOps |
| Open-source advocate | Tabby | Windows Terminal |
| Enterprise/compliance | SecureCRT | Termius Business |
| AI-first terminal power user | Warp | CtrlOps |
| Free SSH + SFTP | Bitvise | MobaXterm |
***
## Why Does the AI Terminal Gap Matter? [#why-does-the-ai-terminal-gap-matter]
Every SSH client for Windows focuses on tabs, SFTP, and session management. But they all ignore the ultimate test: **what happens when something goes completely wrong and you don't know what to do next?**

To see why this gap matters, look at what happened to me recently:
I was out of the office, visiting a friend's wedding, when I suddenly got a call from a client. The entire application was taking too long to load. Everything had been working fine the day before, so I was shocked.
I immediately called my DevOps guy and asked him to investigate, thinking it might be a memory leak or a hung server. After 50 minutes, he called me back, completely helpless - he couldn't identify the exact problem.
At that point, I opened my laptop, launched CtrlOps, and opened the AI Terminal. I asked it to check for slowness and analyze all processes. Within a few minutes, it identified something shocking: **a crypto miner was running on my server.**
Here is where the gap between traditional terminals and CtrlOps became a lifesaver:
* **With PuTTY or MobaXterm:** I would have logged into a blank prompt, run standard diagnostic commands from memory, and likely ended up googling CPU usage metrics on my phone while sitting at a wedding reception. My DevOps guy and I would have lost hours to downtime.
* **With Warp:** I could have asked its AI, but auto-running generated commands on a slow, compromised server in production is incredibly risky. One wrong execution could have corrupted active databases or logs.
* **With CtrlOps:** I didn't know the exact commands to safely clean a compromised server, so I asked the AI Terminal to remove the miner and release the server load. It generated 3 - 4 cleanup commands. I reviewed them, clicked **Approve**, and the miner was completely removed.
Next, I needed to investigate the root cause. I asked the AI Terminal: *"I didn't install this miner. Check who did this and how they got access."*
The AI Terminal ran multiple system audits and provided a detailed report showing:
* The exact SSH session that was activated.
* The timestamps of when the miner was installed.
* When the session logged out.
**The root cause:** My DevOps guy had mistakenly added a GitLab public SSH key directly inside the server to run CI/CD, and hackers took advantage of this exposed key.
If I hadn't had the approval-gated AI Terminal with me, there is zero chance I could have investigated, resolved, and secured my server so quickly.
CtrlOps' AI Terminal also connects to [real-time web search](https://ctrlops.io/docs/modules/ai-terminal/web-search) to read the latest documentation before suggesting commands. This helps when you're debugging a framework version that shipped after the AI model's knowledge cutoff.
***
## Conclusion [#conclusion]
The **best SSH clients for Windows** in 2026 are the ones that consolidate workflows into fewer tools.
CtrlOps does that at $7/user/month with a 1-month free trial. The workflow speaks for itself the first time you deploy in 5 minutes instead of 45.
Pick the tool that matches your biggest pain point today. Switch if it stops fitting.
The best SSH client is the one you actually use without fighting it.
> "After using CtrlOps for the past few months, troubleshooting and managing servers has become much faster. I spend less time hunting for issues and more time on development. If you're a developer who also handles DevOps work, give CtrlOps a try - it quietly saves hours without you realizing it."
>
> * Amit Khichar, [LinkedIn](https://www.linkedin.com/posts/amit-khichar_ctrlops-saas-buildinpublic-share-7469630283689074689-G04H/)
***
## Frequently Asked Questions [#frequently-asked-questions]
It depends on your workflow. For managing multiple servers with file transfers, monitoring, and deployments in one app, **CtrlOps** is the most complete option at $7/user/month. For cross-device sync, **Termius** is the most mature. For free and no-install, **Windows Terminal + OpenSSH** is already on your machine. For the lightest free download, **PuTTY** remains reliable.
Yes, several strong options. **PuTTY** is the most well-known, lightweight and reliable. **MobaXterm Home** bundles SSH, SFTP, RDP, and X11 free (12 session limit). **Bitvise SSH Client** is free for all use with a graphical SFTP browser. **Tabby** is free and open-source with a modern UI. **Windows Terminal + OpenSSH** requires no download. It's built into Windows 10 and 11.
PuTTY still works reliably as a basic SSH client. But it hasn't evolved meaningfully in over a decade. No tabs, no file manager, no AI, no monitoring. Sessions stored in the Windows registry in plain text. For connecting to one server occasionally, it's fine. For managing 3+ servers daily, modern alternatives like MobaXterm, Termius, or CtrlOps solve problems PuTTY doesn't acknowledge.
Yes, but quality varies by tool. **PuTTY** stores sessions by IP, no grouping, no overview. **Termius** and **CtrlOps** offer named server directories with one-click connect and environment grouping. **CtrlOps** adds a fleet view showing live CPU, RAM, and disk for all servers without connecting individually. For 5+ servers, a proper directory saves roughly 10 minutes of daily connection overhead.
Yes. Both Windows 10 and 11 include OpenSSH Client pre-installed. Verify by opening Terminal and typing `ssh`. If missing, enable via Settings → Apps → Optional Features → OpenSSH Client. Combined with Windows Terminal, you get tabs, profiles, and a functional SSH workflow with zero downloads.
CtrlOps is a desktop app for Windows, macOS, and Linux that combines SSH access, a GUI file manager, real-time infrastructure monitoring, an approval-gated AI terminal, and one-click deployment in one local-first app. Unlike pure SSH clients (PuTTY, Termius), it replaces 3 - 4 separate tools. Unlike Warp, it shows every command before execution, nothing runs without approval. All credentials stay local with AES-256 encryption. $7/user/month, 1 month free trial, no credit card.
Yes. CtrlOps runs natively on Windows, macOS (Apple Silicon and Intel), and Linux. It connects to servers over standard SSH, no agents or plugins needed on your servers. If you can SSH into a server from your Windows machine, CtrlOps can manage it.
**CtrlOps** stores all credentials locally with AES-256 encryption. **Tabby** uses a local vault with a master passphrase. **SecureCRT** stores sessions locally. **PuTTY** stores in Windows registry in plain text. **Termius** and **Warp** sync to cloud servers (E2E encrypted for Termius). For maximum security, choose local-only encrypted storage.
Yes, MobaXterm is a direct and significant upgrade. It adds tabbed sessions, built-in SFTP browser, X11 server, RDP/VNC support, macro recording, and portable mode, all free. The main limitation: MobaXterm is Windows-only. If your team includes Mac or Linux users, it creates fragmentation. For Windows-only environments, MobaXterm replaces PuTTY and WinSCP in one App.
---
# How to Deploy a Next.js App on a Linux VPS in 5 Minutes (2026) (/blog/deploy-nextjs-app-linux-vps)
Author: Daxesh Italiya | Published: 2026-07-10 | Tags: deploy nextjs app on vps, nextjs vps deployment, self-host nextjs, nextjs pm2 nginx ssl, one-click deployment | Reading Time: 26 min read
> Deploy a Next.js app on a Linux VPS in 13 steps or under 5 minutes with one-click deployment. Covers the build step, NEXT_PUBLIC_ vars, PM2, Nginx, and SSL.
Next.js apps need a running Node.js server for SSR, API routes, and middleware. Unlike [static React builds](/blog/deploy-react-app-linux-vps), you cannot just upload files to a web server. Deploying Next.js on a Linux VPS requires building the production bundle, configuring a process manager, setting up a reverse proxy, and handling environment variables that behave differently at build time versus runtime. CtrlOps [one-click deployment](/features/deployment) automates this entire stack in under 5 minutes.
***
## Key Takeaways [#key-takeaways]
Deploying a Next.js application on a Linux VPS in 2026 involves 13 manual steps and at least one gotcha that does not exist in plain Node.js deployments: the production build step. Miss it, and your app serves development code to real users. Get `NEXT_PUBLIC_` variables wrong, and your frontend silently uses stale values baked in at build time.
**Manual deployment (all 13 steps)** is the right choice when you need a custom Nginx configuration, want to learn the full deployment stack, or run a non-standard Next.js setup with Docker or a monorepo. Total time: 30-45 minutes.
**CtrlOps one-click deployment** handles the repetition when you deploy Next.js apps from GitHub regularly. You fill a form, select Next.js as the application type, and click Deploy. The dependency installation, build, PM2, Nginx, and SSL are configured automatically. Total time: under 5 minutes.
| Step | Manual Process | With CtrlOps |
| --------------------- | --------------------------------------------------- | ----------------------------- |
| Install Node.js | Run NodeSource setup script | Select version from dropdown |
| Clone repo | `git clone` via terminal | Paste GitHub URL in form |
| Environment variables | Create `.env` manually via `nano` | Bulk paste entire `.env` file |
| Install dependencies | `npm install` via terminal | Auto-runs during deploy |
| Production build | Run `npm run build` manually | Auto-runs during deploy |
| PM2 setup | Install, configure, set startup script | Handled automatically |
| Nginx reverse proxy | Write config file, test, reload | Handled automatically |
| DNS setup | Update A record at registrar | Update A record at registrar |
| SSL certificate | Install Certbot, run CLI commands | Toggle on, auto-configured |
| **Total time** | **30-45 minutes** | **Under 5 minutes** |
| **Tools required** | **5+ (terminal, editor, browser, DNS panel, docs)** | **1 (CtrlOps)** |
***
## Why Is Next.js Harder to Deploy Than Plain Node.js? [#why-is-nextjs-harder-to-deploy-than-plain-nodejs]
Deploying Next.js on a VPS stacks three extra requirements on top of standard Node.js infrastructure: a mandatory `npm run build` compilation step, a split between build-time and runtime environment variables, and a persistent Node.js process that renders pages on every request.
A plain Node.js app runs with `npm start`. Next.js needs `npm run build` first, which compiles React Server Components, generates static pages, optimizes images, and bundles JavaScript. On a 1 GB VPS, this build step alone can consume all available memory and crash with a `Killed` error.
Then there is the environment variable split. Variables prefixed with `NEXT_PUBLIC_` get embedded into the JavaScript bundle during `npm run build`. Change them after the build, and nothing happens. Your frontend keeps using the old values. This catches developers who treat `.env` changes the same way they would in Express, where a restart picks up new values immediately.
If you have deployed a Node.js app to a VPS before, you already know 80% of the process. The extra 20% is Next.js-specific, and this guide covers every part of it.
**Bottom line:** Apps without SSR or API routes can skip the process manager entirely by setting `output: 'export'` in `next.config.js` and serving the generated HTML through Nginx alone. This guide assumes your app uses server-side rendering, which is the case for most production Next.js projects.
***
## What Do You Need Before Deploying Next.js on a VPS? [#what-do-you-need-before-deploying-nextjs-on-a-vps]
Every Next.js VPS deployment starts with the same prerequisites as needed which we follow while [deploying nodejs on linux server](/blog/deploy-nodejs-app-linux-vps). Get these ready first to avoid mid-deployment blockers that cost you 20 minutes of debugging.
* **A Linux VPS** running Ubuntu 22.04 or 24.04 LTS with at least 2 GB of RAM. The production build step is memory-intensive. A 1 GB server works but needs a swap file (covered in Step 5).
* **SSH access** to your server. You should be able to run `ssh user@your-server-ip` from your local terminal.
* **Your Next.js app in a GitHub repository.** Public repos work immediately. Private repos need a deploy key or a GitHub personal access token.
* **A domain name** (optional but recommended). Point the DNS A record to your server's public IP address before starting the SSL step.
* **A successful local build.** Run `npm run build` on your local machine first. If it fails locally, it will fail on the server with less helpful error output.
**Reality check:** Next.js recommends 2 GB of RAM minimum for production builds. If you are on a 1 GB VPS from DigitalOcean, Hetzner, or AWS Lightsail, create a 2 GB swap file before running `npm run build`. Without it, the Linux OOM killer will terminate the build process silently. Step 5 shows you how.
***
## How to Deploy Next.js on a VPS Manually: The Full 13-Step Process [#how-to-deploy-nextjs-on-a-vps-manually-the-full-13-step-process]
Manual Next.js deployment on a Linux VPS involves 13 steps across server preparation, application setup, production builds, process management, reverse proxy configuration, and SSL. An experienced developer finishes in 30-45 minutes. First-timers should block 60-90 minutes to account for debugging DNS, firewall rules, and environment variable mismatches.

Every step below includes the exact commands. If you have done this before, skip the explanations and copy the commands directly.
### Step 1: Update Server Packages (2 Minutes) [#step-1-update-server-packages-2-minutes]
Update your server to get the latest security patches and package versions before installing anything.
```bash
sudo apt update && sudo apt upgrade -y
```
Skipping this step is how you end up with dependency conflicts 20 minutes into the process.
### Step 2: Install Node.js and Git (3 Minutes) [#step-2-install-nodejs-and-git-3-minutes]
Install Node.js using the [NodeSource](https://github.com/nodesource/distributions) repository. This gives you the LTS version instead of the outdated version in Ubuntu's default repos.
```bash
curl -fsSL https://deb.nodesource.com/setup_24.x | sudo -E bash -
sudo apt install -y nodejs git
```
Verify the installation:
```bash
node --version
npm --version
git --version
```
Node.js 24 LTS is the recommended version for production deployments in 2026. [Node.js 24 LTS](https://nodejs.org/en/blog/release/v24.0.0) (codename Krypton) entered Long-Term Support in October 2025 and is supported through April 2028.
### Step 3: Clone Your Next.js Project (1 Minute) [#step-3-clone-your-nextjs-project-1-minute]
Clone your application code from GitHub.
```bash
git clone https://github.com/your-username/your-app.git
```
Move into the project directory:
```bash
cd your-app
```
For private repos, use a GitHub personal access token:
```bash
git clone https://@github.com/your-username/your-app.git
```
### Step 4: Configure Environment Variables (3-5 Minutes) [#step-4-configure-environment-variables-3-5-minutes]
Create a `.env` file with your application's required variables.
```bash
nano .env
```
Add your variables:
```
DATABASE_URL=postgres://user:pass@host:5432/db
NEXTAUTH_URL=https://example.com
NEXTAUTH_SECRET=your-secret
NODE_ENV=production
PORT=3000
```
Save and exit (`Ctrl+X`, then `Y`, then `Enter`).
This is where most deployments slow down. You need to find the right variable names, copy values from your local setup, and make sure nothing has quotes that break the parsing. One missing variable means a startup crash that takes 10 minutes to debug.
**Reality check:** Next.js treats environment variables differently from standard Node.js apps. Variables starting with `NEXT_PUBLIC_` are embedded into the JavaScript bundle at build time. If you change a `NEXT_PUBLIC_` variable after running `npm run build`, the frontend will keep using the old value until you rebuild. Server-only variables (without the prefix) are read at runtime and update on restart.
### Step 5: Install Project Dependencies (2-4 Minutes) [#step-5-install-project-dependencies-2-4-minutes]
```bash
npm install
```
On servers with 1 GB of RAM, `npm install` can fail with a single-word error: `Killed`. That is the Linux OOM killer stopping the process when memory runs out. A 2 GB swap file fixes it:
```bash
sudo fallocate -l 2G /swapfile
sudo chmod 600 /swapfile
sudo mkswap /swapfile
sudo swapon /swapfile
echo '/swapfile none swap sw 0 0' | sudo tee -a /etc/fstab
```
The last command keeps the swap active after reboots. Set it up once. It costs nothing and prevents the most common install failure on entry-level VPS plans.
### Step 6: Build the Next.js Application (1-3 Minutes) [#step-6-build-the-nextjs-application-1-3-minutes]
This is the step that does not exist in plain Node.js deployments. Create an optimized production build:
```bash
npm run build
```
If the build completes successfully, Next.js generates the `.next` directory containing your production application. Fix any build errors before moving to the next step.
The build step compiles React Server Components, pre-renders static pages, and bundles client-side JavaScript. On a 2 GB VPS, expect this to take 1-3 minutes depending on the size of your app. Large apps with hundreds of pages can take 5-10 minutes.
**Bottom line:** If your build fails with `JavaScript heap out of memory`, increase the Node.js memory limit: `NODE_OPTIONS="--max-old-space-size=1536" npm run build`. This allocates 1.5 GB of heap memory to the build process. On a 2 GB VPS with swap enabled, this is enough for most Next.js apps.
### Step 7: Open Firewall Ports (1 Minute) [#step-7-open-firewall-ports-1-minute]
Configure UFW to allow SSH, HTTP, and HTTPS traffic.
```bash
sudo ufw allow OpenSSH
sudo ufw allow 80/tcp
sudo ufw allow 443/tcp
sudo ufw enable
```
Type `y` to confirm.
**Reality check:** If you enable the firewall without allowing OpenSSH first, you will lock yourself out of your own server. Always run `sudo ufw allow OpenSSH` before `sudo ufw enable`. Recovering from this mistake requires a provider console or VNC session.
### Step 8: Test the Application on the Server (1 Minute) [#step-8-test-the-application-on-the-server-1-minute]
Start the app to verify everything works before configuring PM2 and Nginx.
```bash
npm start
```
Visit `http://your-server-ip:3000` in a browser. If it loads, your app is working. Press `Ctrl+C` to stop it.
If it crashes, check the error output. The most common issues with Next.js: missing `NEXTAUTH_SECRET`, a `DATABASE_URL` that points to localhost instead of your production database, or a build step that was skipped entirely (the `.next` directory does not exist).
### Step 9: Install and Configure PM2 (3 Minutes) [#step-9-install-and-configure-pm2-3-minutes]
PM2 keeps your app running in the background, restarts it on crashes, and ensures it starts after a server reboot.
```bash
sudo npm install -g pm2
pm2 start npm --name "your-app" -- start
pm2 save
pm2 startup
```
PM2 outputs a command after `pm2 startup`. Copy and run it exactly as shown.
Verify it is running:
```bash
pm2 list
```
Your app should show as `online`.
### Step 10: Install and Configure Nginx (5-8 Minutes) [#step-10-install-and-configure-nginx-5-8-minutes]
Nginx acts as a reverse proxy. It listens on port 80 and 443, then forwards traffic to your Next.js app running on port 3000.
```bash
sudo apt install nginx -y
```
Create a new Nginx config file:
```bash
sudo nano /etc/nginx/sites-available/your-app
```
Paste this configuration:
```nginx
server {
listen 80;
server_name yourdomain.com www.yourdomain.com;
location / {
proxy_pass http://127.0.0.1:3000;
proxy_http_version 1.1;
proxy_set_header Upgrade $http_upgrade;
proxy_set_header Connection 'upgrade';
proxy_set_header Host $host;
proxy_set_header X-Real-IP $remote_addr;
proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
proxy_set_header X-Forwarded-Proto $scheme;
proxy_cache_bypass $http_upgrade;
}
}
```
Enable the config and test it:
```bash
sudo ln -s /etc/nginx/sites-available/your-app /etc/nginx/sites-enabled/
sudo nginx -t
sudo systemctl reload nginx
```
Next.js handles its own image optimization through the built-in `` component. Nginx does not need special configuration for this. The image optimization pipeline runs inside the Node.js process and caches results in `.next/cache/images`. If you want to offload static asset serving, you can add a `location /_next/static/` block that serves files directly from disk, but it is not required for most deployments.
If you prefer to generate the Nginx config visually instead of writing it by hand, the [CtrlOps Nginx Config Generator](/tools/nginx-config-generator) creates a ready-to-use reverse proxy configuration in seconds.
### Step 11: Connect Your Domain to the VPS (2-5 Minutes) [#step-11-connect-your-domain-to-the-vps-2-5-minutes]
Go to your domain registrar (Namecheap, Cloudflare, GoDaddy) and update the DNS A record.
| Record Type | Host | Value |
| ----------- | ---- | -------------- |
| A | @ | your-server-ip |
| A | www | your-server-ip |
DNS propagation can take a few minutes to several hours. Check progress with:
```bash
dig yourdomain.com +short
```
### Step 12: Install Certbot and Generate SSL (2-3 Minutes) [#step-12-install-certbot-and-generate-ssl-2-3-minutes]
Use Certbot to get a free SSL certificate from Let's Encrypt.
```bash
sudo apt install certbot python3-certbot-nginx -y
sudo certbot --nginx -d yourdomain.com -d www.yourdomain.com
```
Certbot automatically updates your Nginx config for HTTPS and sets up HTTP-to-HTTPS redirects.
Test auto-renewal:
```bash
sudo certbot renew --dry-run
```
### Step 13: Verify the Deployment (1 Minute) [#step-13-verify-the-deployment-1-minute]
Open `https://yourdomain.com` in your browser. Your Next.js app should load with a valid SSL certificate.
Final check:
```bash
pm2 list
```
Your app should be `online`, Nginx proxying traffic, and SSL active. And you are done!
***
## Where Do Next.js VPS Deployments Break? [#where-do-nextjs-vps-deployments-break]
The 13 steps above work. But Next.js introduces failure points that plain Node.js apps do not have. These are the issues that send you back to Stack Overflow or search on Google and AI Tool to find the solution.
### The Build Fails Silently on Low-Memory Servers [#the-build-fails-silently-on-low-memory-servers]
Next.js production builds are memory-intensive. The framework compiles React Server Components, generates static pages, traces file dependencies, and bundles JavaScript in parallel. On a 1 GB VPS without swap, the Linux OOM killer terminates the build process. The only output you see is `Killed`. No error message, no stack trace, no hint about what went wrong.
The [State of Frontend 2024 report](https://tsh.io/state-of-frontend) found that Next.js remains the most widely adopted meta-framework, used by 52.9% of surveyed developers. Many of those developers deploy to entry-level VPS plans with 1 GB of RAM, where the build step is the first thing that fails.
### NEXT\_PUBLIC Variables Do Not Update on Restart [#next_public-variables-do-not-update-on-restart]
Standard Node.js apps read `.env` values at startup. Change a variable, restart the process, done. Next.js splits environment variables into two categories. Variables starting with `NEXT_PUBLIC_` are inlined into the client-side JavaScript bundle during `npm run build`. Variables without the prefix are read at runtime by server-side code.
If you change `NEXT_PUBLIC_API_URL` after deployment and only restart PM2, the frontend keeps hitting the old API endpoint. You need to rebuild (`npm run build`) and then restart. This catches every developer at least once.
### SSR Memory Usage Grows Over Time [#ssr-memory-usage-grows-over-time]
Server-side rendering keeps the Node.js process alive and working on every request. Unlike a static site where Nginx serves files from disk, SSR means your Next.js process compiles and renders HTML for each page view. Memory usage creeps upward over hours and days.
Without PM2's `max_memory_restart` setting, a Next.js app on a 2 GB VPS can eventually consume all available memory and freeze. Setting `pm2 start npm --name "your-app" --max-memory-restart 1G -- start` automatically restarts the process before it starves the server.
**Bottom line:** Next.js VPS deployments require more RAM than equivalent Node.js apps. Budget 2 GB minimum for a small-to-medium Next.js app with SSR. If you run a database on the same server, 4 GB is the safe starting point.
***
## How Does CtrlOps One-Click Deployment Handle Next.js? [#how-does-ctrlops-one-click-deployment-handle-nextjs]
CtrlOps reduces the 13-step manual process to a single form. You select Next.js as the application type, paste your GitHub URL, and click Deploy. CtrlOps handles the build, dependency installation, PM2 configuration, Nginx reverse proxy, and SSL certificate generation automatically. Total time: under 5 minutes.
Here is the exact process:
**1. Open the deployment form:** Connect to your server in CtrlOps. Go to [File Manager](/docs/modules/file-manager) and click **Add Application** in the toolbar.

**2. Fill in basic information:** Enter an application name (e.g., "My Next.js App"). Select the environment: Development, Staging, or Production. Choose GitHub auth method (HTTPS or SSH) and paste your repo URL.

**3. Select Node.js version:** Pick from the dropdown. A green checkmark flags Node versions that already exist on the server. Any version you select without a checkmark gets installed as part of the deployment sequence.
**4. Choose Next.js as the application type:** This is the critical step that differs from a plain Node.js deployment. When you select Next.js, CtrlOps automatically runs the build step (`npm run build`) before starting the app. The install command auto-fills as `npm install`. Toggle on Local Redis if your app needs it.
**5. Add environment variables:** Two options: add them one at a time (Key + Value fields) or click **Bulk Paste** and paste your entire `.env` file at once. CtrlOps sets these before the build runs, so `NEXT_PUBLIC_` variables are correctly embedded.
**6. Set up the domain and SSL:** Toggle on **Setup SSL certificates for domains (using Certbot)**. Enter the port your app listens on (e.g., 3000). Add your domain.
**7. Click Deploy:** CtrlOps opens a live deployment progress modal. A live progress modal shows terminal output for every phase: repo clone, dependency install, production build, PM2 startup, reverse proxy config, and certificate generation. Each phase flips green on success.
### What CtrlOps Handles Behind the Scenes [#what-ctrlops-handles-behind-the-scenes]
When you click Deploy with Next.js selected, CtrlOps runs these steps in sequence:
1. Clones the repo from GitHub
2. Installs the selected Node.js version if not already on the server
3. Runs `npm install` (or your custom install command)
4. Runs `npm run build` to create the production bundle
5. Starts the app under PM2 with auto-restart and startup scripts
6. Configures Nginx as a reverse proxy
7. Runs Certbot for SSL (if toggled on)
Every step shows live terminal output. If the build fails because of a missing environment variable or a TypeScript error, the failing step turns red. You see the exact error message from `npm run build`, not a generic "deployment failed" dialog.
**Reality check:** DNS must already point to your server before SSL can work. If your domain's A record is not set up yet, deploy without SSL first. You can add it later from the [AI Terminal](/docs/modules/ai-terminal) by asking CtrlOps to run Certbot manually.
***
## Vercel vs VPS: When Does Self-Hosting Next.js Save Money? [#vercel-vs-vps-when-does-self-hosting-nextjs-save-money]
Vercel is the default hosting platform for Next.js. It is built by the same company that builds Next.js, and the deployment experience is excellent. But Vercel's pricing scales with traffic, team size, and usage. A VPS has a fixed monthly cost regardless of how many visitors hit your site.
The Vercel Pro plan costs $20 per seat per month with 1 TB of bandwidth included. Bandwidth overages cost $40 per 100 GB. A 3-person startup on Vercel Pro pays at least $60/month before any overages. Add a traffic spike from a successful Product Hunt launch, and the bill can jump to $200-500 in a single month.
A VPS from Hetzner ($4-7/month), DigitalOcean ($6-12/month), or AWS Lightsail ($5-10/month) has a fixed price. Traffic spikes do not change your hosting bill. A $7/month VPS with 2 GB RAM handles 100,000+ page views per month for a typical Next.js app with SSR.
| Factor | Vercel Pro | VPS + CtrlOps |
| ----------------------------- | ---------------------------------------- | ------------------------------------ |
| Monthly cost (solo developer) | $20/month + usage | $7/month VPS + $7/user/month CtrlOps |
| Monthly cost (3-person team) | $60/month + usage | $7/month VPS + $21/month CtrlOps |
| Bandwidth overage | $40 per 100 GB over 1 TB | Not applicable (fixed price) |
| Traffic spike risk | Bill increases with traffic | Fixed cost regardless |
| SSR cold starts | Yes (serverless) | No (always-on process) |
| Full server access | No | Full root SSH access |
| Deployment time | \~2 minutes | \~5 minutes |
| Vendor lock-in | Moderate (Vercel-specific optimizations) | None (standard VPS) |
Vercel wins for solo developers who want zero infrastructure management, teams that need preview deployments on every pull request, and apps that benefit from Vercel's global edge network.
Self-hosting on a VPS wins for teams that need predictable costs, apps with consistent traffic that would generate overages on Vercel, projects that require full server access for custom configurations, and developers who manage multiple apps on the same server.
**Bottom line:** If your monthly Vercel bill exceeds $50 and your traffic is predictable, self-hosting on a VPS saves money within the first month. The break-even point is roughly 2-3 months of Vercel Pro versus a year of VPS hosting. CtrlOps eliminates the DevOps overhead that usually makes self-hosting impractical for small teams.
***
## How Do You Update Your Next.js App After Deployment? [#how-do-you-update-your-nextjs-app-after-deployment]
Deploying is the first time. Every code change after that needs a redeployment. Next.js redeployments have an extra step that plain Node.js apps do not: you must rebuild the production bundle every time.
### Manual Update Process [#manual-update-process]
```bash
ssh user@your-server-ip
cd /home/user/your-app
git pull origin main
npm install --omit=dev
npm run build
pm2 restart your-app
```
Six commands, every time. Forgetting `npm run build` is the most common mistake. Your app keeps serving the old version because PM2 restarted the process using the existing `.next` directory from the previous build.
For apps with live traffic, use `pm2 reload your-app` instead of `pm2 restart`. Restart kills the process and relaunches it, dropping active connections for a few seconds. Reload replaces processes one at a time (in cluster mode), so the app never goes fully offline.
### Updating with CtrlOps [#updating-with-ctrlops]
CtrlOps does not have a built-in re-deploy button yet. But you can create a reusable **Script** in the [Script Directory](/docs/modules/ai-terminal/scripts):
```bash
cd /home/user/{{app_name}}
git pull origin main
npm install --omit=dev
npm run build
pm2 reload {{app_name}}
```
Save it once. Run it on any server with one click. The `{{app_name}}` placeholder lets you reuse the same script for different Next.js projects.
Alternatively, describe the task in plain English inside the AI Terminal: "pull latest changes, run the build, and reload PM2." CtrlOps translates that into the correct command sequence and waits for your approval before executing.
> "The preview step is the whole game when AI touches live infra. CtrlOps gets it right: ask in plain English, see the exact command before it runs, approve."
>
> * **Vivek Chand**, verified review on [Product Hunt](https://www.producthunt.com/products/ctrlops?comment=5381393)
### Useful PM2 Commands for Next.js Apps [#useful-pm2-commands-for-nextjs-apps]
| Command | What It Does |
| ------------------------------------------------------------- | -------------------------------------------------------- |
| `pm2 list` | See all running apps and their status |
| `pm2 logs your-app` | Tail live logs for debugging SSR errors |
| `pm2 restart your-app` | Full restart (picks up new env vars and rebuilt code) |
| `pm2 reload your-app` | Zero-downtime restart in cluster mode |
| `pm2 monit` | Real-time dashboard showing CPU and memory per process |
| `pm2 start npm --name "app" --max-memory-restart 1G -- start` | Auto-restart when memory exceeds 1 GB (critical for SSR) |
**Bottom line:** After updating `NEXT_PUBLIC_` environment variables, you must rebuild (`npm run build`) and then restart PM2. A restart alone does not update client-side values. For server-only variables (without the `NEXT_PUBLIC_` prefix), `pm2 restart your-app` is sufficient.
***
## What Happens After Your Next.js App Is Live? [#what-happens-after-your-nextjs-app-is-live]
Deploying is step one. Keeping the server healthy is everything after that. Once your Next.js app is running, you need visibility into CPU, RAM, and disk usage - especially because SSR workloads consume more resources than static sites and memory usage creeps upward over days.
Manually, you SSH in and run `htop`, `df -h`, and `free -m` across each server. With three or more servers, this becomes a daily time sink.
CtrlOps gives you a real-time [infrastructure dashboard](/docs/modules/infra-details) for every connected server. CPU load, memory usage, disk space, and running processes are visible without typing a single command. When your Next.js app's SSR process starts eating more RAM than expected, you see it before it crashes - not after.
Beyond monitoring, server access also needs management. If a contractor needs temporary SSH access to your staging server, or a junior developer should only connect to the dev environment, you need per-server user and key controls. The CtrlOps [Access Management](/docs/modules/access-management) module lets you create SSH users, assign permissions, and manage keys visually - no `adduser` or `sshd_config` editing required.
**Bottom line:** Deployment is a one-time event. Server monitoring and access control are ongoing. CtrlOps handles both from the same interface you used to deploy, so you do not need to switch between tools for different server tasks.
***
## When Does Manual Next.js Deployment Stop Scaling? [#when-does-manual-nextjs-deployment-stop-scaling]
Manual deployment works for your first server. It breaks down when you manage three or more Next.js apps across different VPS instances.
A freelance developer managing 5 client Next.js apps deploys the same way each time: SSH in, pull, install, build, restart. That is 6 commands multiplied by 5 servers: roughly 2.5 to 4 hours of pure deployment work per update cycle. Each server has slightly different Node versions, different `.env` files, different Nginx configs. Keeping track of what is where becomes its own job.
An indie SaaS founder who deploys staging and production separately runs through 12 commands per code change (6 for staging, 6 for production). Each deploy takes 15-20 minutes including the build step. Over a month of daily deployments, that is 7.5-10 hours of repetitive terminal work.
Research by [Gloria Mark at UC Irvine](https://ics.uci.edu/~gmark/chi08-mark.pdf) found that it takes an average of 23 minutes to refocus after a context switch. During a manual deployment, you switch between terminal, text editor, browser, DNS panel, and documentation at least 6 times. The cumulative recovery time often exceeds the deployment time itself.
CtrlOps eliminates this scaling problem. Every deployment is identical: fill the form, click Deploy. The fifth deployment takes the same 5 minutes as the first. No accumulated config drift across servers. No forgotten build steps on server number 4.
Spirex Infoways saw the same curve flatten on real client work. A change that needed applying in three or four places used to take up to two hours, and now [runs across the whole fleet in under ten minutes](/case-studies/spirex-infoways).
> "Started using CtrlOps a few weeks ago, honestly didn't expect much. But my DevOps workflow has genuinely shifted - AI Terminal that understands plain English, server management without SSH juggling, backups, deployments, and file manager all in one place. I'm doing in 10 minutes what used to take an hour. If you manage servers, just try it."
>
> * **Chintan Poriya**, [Co-founder & CEO of BytezTech](https://byteztech.com) ([original post on LinkedIn](https://www.linkedin.com/posts/chintan-poriya_product-review-started-using-ctrlopsai-activity-7467179106200260609-Uoht))
### How Does CtrlOps Compare to Other Next.js Deployment Options? [#how-does-ctrlops-compare-to-other-nextjs-deployment-options]
| Approach | Deploy Time | Monthly Cost | Best For |
| --------------------------- | ------------------------------ | ------------------------------------ | ---------------------------------------------- |
| **Vercel** | 1-2 min | Free tier, then $20+/seat | Teams wanting zero infrastructure management |
| **CtrlOps** | Under 5 min | $7/user/month (1 mo free) + VPS cost | Teams managing 1-25 servers, predictable costs |
| **Manual (SSH + terminal)** | 30-45 min | VPS cost only | Learning, custom setups, one-off deployments |
| **Coolify / Dokploy** | 5-10 min setup | Free (self-hosted) + VPS | Docker-first teams, open source preference |
| **GitHub Actions CI/CD** | 5-10 min setup, then automatic | Free tier (2,000 min/month) | Teams with existing CI/CD experience |
CtrlOps sits between "deploy manually every time" and "run a full PaaS." You keep your own VPS, your own pricing, and full server access. CtrlOps automates the repetitive build-install-configure cycle without locking you into a platform.
The key differentiator: CtrlOps [deploys from GitHub](/docs/modules/deployment) with automatic build execution, Nginx, PM2, and SSL setup. No agents are installed on your server. No cloud sync of credentials. Everything stays local on your machine.
For a broader look at where CtrlOps fits alongside CI/CD tools and monitoring platforms, we covered [15 DevOps automation tools](/blog/devops-automation-tools) with real workflow comparisons.
***
## When Should You Deploy Next.js Manually Instead? [#when-should-you-deploy-nextjs-manually-instead]
CtrlOps one-click deployment covers Next.js apps deployed from GitHub with standard `npm run build` and `npm start` commands. For specific situations, manual deployment is still the right choice.
**Docker-based deployments:** If your setup uses Docker Compose with `output: 'standalone'` in `next.config.js`, you need a Dockerfile and manual orchestration. CtrlOps does not handle container builds. The standalone output mode creates a self-contained `.next/standalone` directory that reduces deployment size by 60-80%, but it requires copying static assets separately (`cp -r .next/static .next/standalone/.next/static`) and running `node server.js` instead of `npm start`.
**Monorepo setups:** If your Next.js app lives inside a Turborepo or Nx monorepo with custom build pipelines, the standard `npm run build` command may not work as expected. Manual configuration or a dedicated CI/CD pipeline gives you the control needed for these setups.
**Non-standard server configurations:** Custom Nginx caching rules for ISR (Incremental Static Regeneration), WebSocket proxy configuration for real-time features, or multi-app setups with different domains on the same server all need manual Nginx config editing.
**Learning purposes:** If you are deploying Next.js to a VPS for the first time, walk through all 13 steps manually at least once. Understanding the relationship between the build output, PM2, and Nginx makes you a better developer. Then automate the repetition.
***
## Best Practice: Create a Non-Root Deploy User [#best-practice-create-a-non-root-deploy-user]
Every command in this guide works as root, but running your Next.js app as root means one compromised npm package owns your entire server. Create a dedicated deploy user once, and every deployment on that server is safer.
```bash
adduser deploy
usermod -aG sudo deploy
```
Copy your SSH key to the new user and test the login:
```bash
ssh-copy-id deploy@your-server-ip
ssh deploy@your-server-ip
```
Once key-based login works, disable password authentication. Open the SSH config:
```bash
sudo nano /etc/ssh/sshd_config
```
Set `PasswordAuthentication no`, save, then restart SSH:
```bash
sudo systemctl restart ssh
```
**Reality check:** Test the key-based login in a second terminal before closing your current SSH session. If the key setup failed and password login is already disabled, you are locked out. Recovery means a provider console session.
This takes 5 minutes and you do it once per server. Skip it on a throwaway test box. Never skip it on a server that holds user data or client applications.
**Skip the SSH commands:** CtrlOps handles SSH user setup visually. Open your server, go to **SSH Management**, and create a custom user with the permissions you need. The [Access Management guide](/docs/modules/access-management) walks through every option.
***
## Conclusion [#conclusion]
Deploying a Next.js app on a Linux VPS requires 13 steps and one extra gotcha that plain Node.js apps do not have: the mandatory production build. Miss `npm run build`, and your app serves development code. Get `NEXT_PUBLIC_` variables wrong, and your frontend silently ignores your changes. The manual process takes 30-45 minutes and has not changed in years.
CtrlOps reduces this to one form and one click. Paste your GitHub URL, select Next.js as the application type, bulk-paste env variables, add a domain, and toggle on SSL. Click Deploy. The build, PM2, Nginx, and SSL are configured automatically. Total time: under 5 minutes.
If you are migrating from Vercel to cut costs, the manual route works but demands 30-45 minutes per server and deep familiarity with PM2, Nginx, and Certbot. CtrlOps gives you the fixed-cost predictability of a VPS with a deployment experience that takes minutes, not hours.
The manual process is worth learning once. The repetition is not.
***
Manual deployment on a Linux VPS takes 30-45 minutes for an experienced developer. This includes server updates, Node.js installation, cloning the repo, setting environment variables, running the production build, configuring PM2, Nginx as a reverse proxy, and SSL via Certbot. CtrlOps one-click deployment reduces this to under 5 minutes by automating the build step, PM2, Nginx, and SSL configuration through a guided form.
It depends on your app's features. If you use SSR, API routes, middleware, or Incremental Static Regeneration, you need a running Node.js process managed by PM2 or systemd. If your app is purely static with no server-side logic, you can set `output: 'export'` in `next.config.js`, run `npm run build`, and serve the generated `out` folder with Nginx directly. Most production Next.js apps require SSR.
The `Killed` message means the Linux OOM (Out of Memory) killer terminated the build process because the server ran out of RAM. Next.js production builds are memory-intensive. Fix this by creating a 2 GB swap file: `sudo fallocate -l 2G /swapfile && sudo chmod 600 /swapfile && sudo mkswap /swapfile && sudo swapon /swapfile`. For persistent swap, add it to `/etc/fstab`.
Variables prefixed with `NEXT_PUBLIC_` are embedded into the JavaScript bundle during `npm run build`. They become part of the client-side code. If you change a `NEXT_PUBLIC_` variable after building, you must run `npm run build` again and restart PM2 for the change to take effect. Server-only variables (without the prefix) are read at runtime and update with a simple `pm2 restart`.
For solo developers with low traffic, Vercel's free Hobby plan is cheaper. For teams of 2+ or apps with predictable traffic, a VPS is significantly cheaper. Vercel Pro costs $20 per seat per month plus bandwidth overages ($40 per 100 GB over 1 TB). A 2 GB VPS costs $4-12/month with no traffic-based pricing. A 3-person team on Vercel Pro pays at least $60/month; the same team on a VPS pays $7-12/month for hosting plus $21/month for CtrlOps.
When you select Next.js as the application type in CtrlOps, it automatically adds the `npm run build` step between dependency installation and app startup. For plain Node.js apps, this build step is skipped. CtrlOps also sets environment variables before the build runs, which ensures that `NEXT_PUBLIC_` variables are correctly embedded in the client-side bundle.
Standalone mode (`output: 'standalone'` in `next.config.js`) creates a self-contained `.next/standalone` directory with only the files needed to run your app. It eliminates the need for `node_modules` at runtime and reduces deployment size by 60-80%. It is useful for Docker deployments. For standard VPS deployment with PM2 and `npm start`, standalone mode is optional. CtrlOps does not require it.
A small Next.js app with SSR uses 150-300 MB of RAM at runtime. The production build step needs more, roughly 1-2 GB during compilation. A 2 GB VPS is the practical minimum for running one Next.js app. If you also run a database (PostgreSQL, MySQL) on the same server, start with 4 GB. PM2's `max-memory-restart` flag prevents memory leaks from crashing the server.
Yes. You can run multiple Next.js apps on the same server by deploying each one through the Add Application form with a different app name and domain. Each app runs on its own port under PM2, and CtrlOps configures separate Nginx server blocks for each domain. A 4 GB VPS comfortably handles 2-3 small Next.js apps simultaneously.
SSH into your server, pull the latest code with `git pull`, run `npm install --omit=dev`, then `npm run build`, and finally `pm2 reload your-app` for zero-downtime restarts. With CtrlOps, you can save these 5 commands as a reusable Script in the Script Directory and run it with one click on any server, or type the request in plain English in the AI Terminal and approve the generated commands.
---
# How to Deploy a Node.js App on a Linux VPS in 5 Minutes (2026) (/blog/deploy-nodejs-app-linux-vps)
Author: Daxesh Italiya | Published: 2026-07-07 | Tags: deploy nodejs app on vps, nodejs vps deployment, deploy nodejs linux server, pm2 nginx ssl setup, one-click deployment | Reading Time: 22 min read
> Deploy a Node.js app on a Linux VPS in 13 steps or under 5 minutes with one-click deployment. Covers PM2, Nginx, SSL, env variables, and automation.
Deploying a Node.js app on a Linux VPS manually requires 13 steps: updating server packages, installing Node.js, cloning your repo, configuring environment variables, installing dependencies, setting firewall rules, testing, configuring PM2, setting up Nginx as a reverse proxy, connecting a domain, generating an SSL certificate with Certbot, and verifying.
The full process takes 30-45 minutes for experienced developers and over an hour for first-timers. CtrlOps one-click deployment reduces these 13 steps to [a single form and one click](/features/deployment), handling Node.js installation, PM2, Nginx, environment variables, and SSL automatically in under 5 minutes.
***
## Key Takeaways [#key-takeaways]
Deploying a Node.js application on a Linux VPS in 2026 still means running 13 manual commands across 5 different tools. The process is reliable but repetitive.
**Manual deployment (all 13 steps)** is the right choice when you are learning VPS deployment for the first time, need a custom server configuration, or work with non-Node.js frameworks. Total time: 30-45 minutes.
**CtrlOps one-click deployment** eliminates the repetition when you deploy Node.js, React, or Next.js apps from GitHub regularly. You fill a form and click Deploy. PM2, Nginx, and SSL are configured automatically. Total time: under 5 minutes.
| Step | Manual Process | With CtrlOps |
| --------------------- | --------------------------------------------------- | ----------------------------- |
| Install Node.js | Run NodeSource setup script | Select version from dropdown |
| Clone repo | `git clone` via terminal | Paste GitHub URL in form |
| Environment variables | Create `.env` manually via `nano` | Bulk paste entire `.env` file |
| Install dependencies | `npm install` via terminal | Auto-runs during deploy |
| PM2 setup | Install, configure, set startup script | Handled automatically |
| Nginx reverse proxy | Write config file, test, reload | Handled automatically |
| DNS setup | Update A record at registrar | Update A record at registrar |
| SSL certificate | Install Certbot, run CLI commands | Toggle on, auto-configured |
| **Total time** | **30-45 minutes** | **Under 5 minutes** |
| **Tools required** | **5+ (terminal, editor, browser, DNS panel, docs)** | **1 (CtrlOps)** |
***
## Why Is Deploying Node.js on a VPS Still a 13-Step Process? [#why-is-deploying-nodejs-on-a-vps-still-a-13-step-process]
You finished building your Node.js app. It runs perfectly on `localhost:3000`. Now you need it live on a VPS with HTTPS, auto-restarts, and a real domain.
So you open a terminal, SSH into your server, and start searching.
A few minutes later, you are six browser tabs deep. One tutorial covers Node installation. Another explains PM2. A third shows the Nginx reverse proxy config. None of them matches your exact setup. You copy-paste an Nginx block, get a 502 error, and spend another 20 minutes realizing it was a missing semicolon.
If you are a **freelance developer** shipping a client project, a **startup founder** getting your MVP live, or an **agency developer** deploying to staging for the third time this week, you know this scenario.
The manual process has not changed in years. It still takes 13 steps, 30-45 minutes, and working knowledge of five different tools. We walked through the full 13-step manual deployment and timed each step. Then we did the same deployment using [CtrlOps one-click deployment](/docs/modules/deployment).
This guide covers both approaches. You will learn every manual step so you understand what actually happens on your server. Then you will see how to skip most of it.
***
## What Do You Need Before Deploying Node.js on a VPS? [#what-do-you-need-before-deploying-nodejs-on-a-vps]
Every Node.js VPS deployment starts with the same prerequisites, whether you deploy manually or use a tool. Get these ready first to avoid mid-deployment blockers.
* **A Linux VPS** running Ubuntu 22.04 or 24.04 LTS with at least 1 GB of RAM. Providers like DigitalOcean, Linode, Hetzner, or AWS Lightsail all work.
* **SSH access** to your server. You should be able to run `ssh user@your-server-ip` from your local terminal.
* **Your Node.js app in a GitHub repository.** Public repos work immediately. Private repos need a deploy key or a GitHub personal access token.
* **A domain name** (optional but recommended). Point the DNS A record to your server's public IP before starting the SSL step.
**Bottom line:** Ubuntu 24.04 LTS is the most commonly used OS for Node.js VPS hosting in 2026. If your provider gives you a choice, pick it. Every command in this guide is written for Ubuntu/Debian-based systems.
***
## How to Deploy Node.js on a VPS Manually: The Full 13-Step Process [#how-to-deploy-nodejs-on-a-vps-manually-the-full-13-step-process]
Manual Node.js deployment on a Linux VPS involves 13 steps across server preparation, application setup, process management, reverse proxy configuration, and SSL. An experienced developer finishes in 30-45 minutes. Someone doing it for the first time should expect over an hour.

Every step below includes the exact commands. If you have done this before, skip the explanations and copy the commands directly.
### Step 1: Update Server Packages (2 Minutes) [#step-1-update-server-packages-2-minutes]
Update your server to get the latest security patches and package versions before installing anything.
```bash
sudo apt update && sudo apt upgrade -y
```
Skipping this step is how you end up with dependency conflicts 20 minutes into the process.
### Step 2: Install Node.js and Git (3 Minutes) [#step-2-install-nodejs-and-git-3-minutes]
Install Node.js using the [NodeSource](https://github.com/nodesource/distributions) repository. This gives you the LTS version instead of the outdated version in Ubuntu's default repos.
```bash
curl -fsSL https://deb.nodesource.com/setup_24.x | sudo -E bash -
sudo apt install -y nodejs git
```
Verify the installation:
```bash
node --version
npm --version
git --version
```
Node.js 24 LTS is the recommended version for production deployments in 2026. [Node.js 24 LTS](https://nodejs.org/en/blog/release/v24.0.0) (codename Krypton) entered Long-Term Support in October 2025 and is supported through April 2028.
### Step 3: Clone Your Node.js Project (1 Minute) [#step-3-clone-your-nodejs-project-1-minute]
Clone your application code from GitHub.
```bash
git clone https://github.com/your-username/your-app.git
```
For private repos, use a GitHub personal access token:
```bash
git clone https://@github.com/your-username/your-app.git
```
### Step 4: Navigate to the Project Directory (10 Seconds) [#step-4-navigate-to-the-project-directory-10-seconds]
```bash
cd your-app
```
If you manage multiple apps on the same server, keep a clean directory structure. Use `/home/deploy/your-app` or `/var/www/your-app` as a consistent convention.
### Step 5: Configure Environment Variables (3-5 Minutes) [#step-5-configure-environment-variables-3-5-minutes]
Create a `.env` file with your application's required variables.
```bash
nano .env
```
Add your variables:
```
DATABASE_URL=postgres://user:pass@host:5432/db
API_KEY=sk_live_abc123
NODE_ENV=production
PORT=3000
```
Save and exit (`Ctrl+X`, then `Y`, then `Enter`).
This is where most deployments slow down. You need to find the right variable names, copy values from your local setup, and make sure nothing has quotes that break the parsing. One missing variable means a startup crash that takes 10 minutes to debug.
### Step 6: Install Project Dependencies (2-4 Minutes) [#step-6-install-project-dependencies-2-4-minutes]
```bash
npm install
```
On servers with 1 GB of RAM, `npm install` can fail with a single-word error: `Killed`. That is the Linux OOM killer stopping the process when memory runs out. A 2 GB swap file fixes it:
```bash
sudo fallocate -l 2G /swapfile
sudo chmod 600 /swapfile
sudo mkswap /swapfile
sudo swapon /swapfile
echo '/swapfile none swap sw 0 0' | sudo tee -a /etc/fstab
```
The last command keeps the swap active after reboots. Set it up once. It costs nothing and prevents the most common install failure on entry-level VPS plans.
### Step 7: Open Firewall Ports (1 Minute) [#step-7-open-firewall-ports-1-minute]
Configure UFW to allow SSH, HTTP, and HTTPS traffic.
```bash
sudo ufw allow OpenSSH
sudo ufw allow 80/tcp
sudo ufw allow 443/tcp
sudo ufw enable
```
Type `y` to confirm.
**Reality check:** If you enable the firewall without allowing OpenSSH first, you will lock yourself out of your own server. Always run `sudo ufw allow OpenSSH` before `sudo ufw enable`. Recovering from this mistake requires a provider console or VNC session.
### Step 8: Test the Application on the Server (1 Minute) [#step-8-test-the-application-on-the-server-1-minute]
Start the app to verify everything works before configuring PM2 and Nginx.
```bash
npm start
```
Visit `http://your-server-ip:3000` in a browser. If it loads, your app is working. Press `Ctrl+C` to stop it.
If it crashes, check the error output. The most common issues: missing environment variables, wrong Node.js version, or a dependency that did not install correctly.
### Step 9: Install and Configure PM2 (3 Minutes) [#step-9-install-and-configure-pm2-3-minutes]
PM2 keeps your app running in the background, restarts it on crashes, and ensures it starts after a server reboot.
```bash
sudo npm install -g pm2
pm2 start npm --name "your-app" -- start
pm2 save
pm2 startup
```
PM2 outputs a command after `pm2 startup`. Copy and run it exactly as shown.
Verify it is running:
```bash
pm2 list
```
Your app should show as `online`.
That `pm2 startup` command registers a systemd unit, so your app is now one more service on a host that already runs a couple of dozen. The [services and processes audit checklist](/security-checklist/vps/services-processes) covers what to check as that list grows: which processes listen on public ports and under which user, how many daemons are running, and whether anything scheduled itself in cron without you.
### Step 10: Install and Configure Nginx (5-8 Minutes) [#step-10-install-and-configure-nginx-5-8-minutes]
Nginx acts as a reverse proxy. It listens on port 80 and 443, then forwards traffic to your Node.js app running on port 3000.
```bash
sudo apt install nginx -y
```
Create a new Nginx config file:
```bash
sudo nano /etc/nginx/sites-available/your-app
```
Paste this configuration:
```nginx
server {
listen 80;
server_name yourdomain.com www.yourdomain.com;
location / {
proxy_pass http://127.0.0.1:3000;
proxy_http_version 1.1;
proxy_set_header Upgrade $http_upgrade;
proxy_set_header Connection 'upgrade';
proxy_set_header Host $host;
proxy_set_header X-Real-IP $remote_addr;
proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
proxy_set_header X-Forwarded-Proto $scheme;
proxy_cache_bypass $http_upgrade;
}
}
```
Enable the config and test it:
```bash
sudo ln -s /etc/nginx/sites-available/your-app /etc/nginx/sites-enabled/
sudo nginx -t
sudo systemctl reload nginx
```
**Tip:** If Nginx fails to reload or you see an error, check your syntax with `sudo nginx -t` to pinpoint the issue.
### Step 11: Connect Your Domain to the VPS (2-5 Minutes) [#step-11-connect-your-domain-to-the-vps-2-5-minutes]
Go to your domain registrar (Namecheap, Cloudflare, GoDaddy) and update the DNS A record.
| Record Type | Host | Value |
| ----------- | ---- | -------------- |
| A | @ | your-server-ip |
| A | www | your-server-ip |
DNS propagation can take a few minutes to several hours. Check progress with:
```bash
dig yourdomain.com +short
```
### Step 12: Install Certbot and Generate SSL (2-3 Minutes) [#step-12-install-certbot-and-generate-ssl-2-3-minutes]
Use Certbot to get a free SSL certificate from Let's Encrypt.
```bash
sudo apt install certbot python3-certbot-nginx -y
sudo certbot --nginx -d yourdomain.com -d www.yourdomain.com
```
Certbot automatically updates your Nginx config for HTTPS and sets up HTTP-to-HTTPS redirects.
Test auto-renewal:
```bash
sudo certbot renew --dry-run
```
A dry run that passes today is not a guarantee for the next 90 days. The [application security audit checklist](/security-checklist/vps/application-security) covers what to re-check later: whether the renewal timer is still active, whether any certificate has slipped inside the 30-day window, and whether the Node version you installed here has since gone end-of-life.
### Step 13: Verify the Deployment (1 Minute) [#step-13-verify-the-deployment-1-minute]
Open `https://yourdomain.com` in your browser. Your Node.js app should load with a valid SSL certificate.
Final check:
```bash
pm2 list
```
Your app should be `online`, Nginx proxying traffic, and SSL active.
And you are done!
***
## What Goes Wrong During Manual Node.js Deployment? [#what-goes-wrong-during-manual-nodejs-deployment]
The 13 steps above look clean on paper. In practice, manual Node.js VPS deployment breaks in predictable ways that add 30-45 minutes to every deployment.
### You Context-Switch Between 5+ Tools Constantly [#you-context-switch-between-5-tools-constantly]
A manual deployment requires your terminal, a text editor (nano or vim), a browser for documentation, your DNS provider's dashboard, and often ChatGPT or Stack Overflow for troubleshooting.
Research from [UC Irvine](https://ics.uci.edu/~gmark/chi08-mark.pdf) shows every context switch costs an average of 23 minutes to fully refocus. During a deployment, you switch contexts 6-8 times minimum.
### The Nginx Config Is a Silent Failure Point [#the-nginx-config-is-a-silent-failure-point]
Nginx configuration causes more deployment failures than any other step. A missing semicolon, a wrong port number, or an incorrect `server_name` produces a 502 Bad Gateway error with no helpful error message.
You run `nginx -t`, read the output, guess what is wrong, edit the file, and test again. For developers who deploy once a month, this means re-learning the config syntax every single time.
### Environment Variables Get Lost in Transit [#environment-variables-get-lost-in-transit]
Copying `.env` values from your local machine to the server via `nano` is error-prone. A missing quote, an extra space, or a forgotten variable causes a startup crash. The error message rarely says "missing env variable." It says something like `Cannot read properties of undefined`.
### Every Deployment Is the Same 13 Steps, Every Time [#every-deployment-is-the-same-13-steps-every-time]
The steps do not change between deployments. Server update, Node install, clone, env setup, PM2, Nginx, SSL.
For a freelancer deploying client apps to new VPS instances, or a startup deploying to staging three times a week, this repetition adds up. A developer deploying weekly spends 24-36 hours per year on the same 13 steps.
**Bottom line:** The manual process works. It is reliable and gives you full control. But for developers who deploy more than once a month, the 30-45 minutes per deployment quietly becomes one of the biggest time sinks in the workflow. [According to the Node.js Survey](https://nodejs.org/static/documents/2018-survey-report.pdf#Business-Impact), 68% of developers report that Node.js increases their productivity, largely due to using full-stack JavaScript. But that productivity gain disappears when the deployment process itself is the bottleneck.
***
## How Does CtrlOps One-Click Deployment Work? [#how-does-ctrlops-one-click-deployment-work]
CtrlOps reduces the 13-step manual process to a single form. You fill in your app details, click Deploy, and CtrlOps handles Node.js installation, dependency setup, PM2 configuration, Nginx reverse proxy, and SSL certificate generation automatically. Total time: under 5 minutes.
Here is the exact process:
**1. Open the deployment form.**
Connect to your server in CtrlOps. Go to [File Manager](/docs/modules/file-manager) and click **Add Application** in the toolbar.

If you need help connecting your server to CtrlOps, you can refer to the [First Connection Guide](/docs/getting-started/first-connection) for a step-by-step walkthrough.
**2. Fill in basic information.**
Enter an Application Name (e.g., "My Node.js App"). Select the Environment: Development, Staging, or Production. Choose GitHub auth method (HTTPS or SSH) and paste your repo URL.

**3. Select Node.js version.**
Pick from the dropdown. Versions already installed on the server show a green checkmark. Missing versions get installed automatically during deployment.
**4. Configure the build.**
Select **Node.js** as the Application Type. The install command auto-fills as `npm install` (change to `yarn install` or `pnpm install` if needed). Enter the start command (e.g., `npm start`). Toggle on Local Redis if your app needs it.
**5. Add environment variables.**
Two options: add them one at a time (Key + Value fields) or click **Bulk Paste** and paste your entire `.env` file at once. No more typing variables into `nano` line by line.
**6. Set up the domain and SSL.**
Toggle on **Setup SSL certificates for domains (using Certbot)**. Enter the port your app listens on (e.g., 3000). Add your domain. Adding `yourdomain.com` automatically covers `www.yourdomain.com`.
**7. Click Deploy.**
CtrlOps opens a live [deployment progress](/docs/modules/deployment) modal. You watch each step complete in real-time: clone, install, build, start, Nginx config, SSL certificate. When the last step turns green, your app is live.
### What CtrlOps Handles Behind the Scenes [#what-ctrlops-handles-behind-the-scenes]
When you click Deploy, CtrlOps runs the same steps you would run manually. It is not magic. It is automation of a known, repeatable process:
1. Clones the repo from GitHub
2. Installs the selected Node.js version if not already on the server
3. Runs `npm install` (or your custom install command)
4. Runs the build command (for React/Next.js apps)
5. Starts the app under PM2 with auto-restart and startup scripts
6. Configures Nginx as a reverse proxy
7. Runs Certbot for SSL (if toggled on)
Every step shows live terminal output. If something fails, the failing step turns red, and you can see exactly which command errored.
**Reality check:** DNS must already point to your server before SSL can work. If your domain's A record is not set up yet, deploy without SSL first. You can add it later from the [AI Terminal](/docs/modules/ai-terminal) by asking CtrlOps to run Certbot manually.
> "Deployments don't stress me out anymore, and that feels weird to say. Paste repo, fill env, toggle SSL, done. Genuinely cannot remember the last time something broke mid-deploy since switching to this."
>
> * **Bhavesh**, verified review on [Product Hunt](https://www.producthunt.com/products/ctrlops?comment=5380604)
***
## Best Practice Tip: Create a Non-Root Deploy User [#best-practice-tip-create-a-non-root-deploy-user]
Every command in this guide works as root, but running your app as root means one compromised npm package owns your entire server. Create a dedicated deploy user once, and every deployment on that server is safer.
```bash
adduser deploy
usermod -aG sudo deploy
```
Copy your SSH key to the new user and test the login:
```bash
ssh-copy-id deploy@your-server-ip
ssh deploy@your-server-ip
```
Once key-based login works, disable password authentication. Open the SSH config:
```bash
sudo nano /etc/ssh/sshd_config
```
Set `PasswordAuthentication no`, save, then restart SSH:
```bash
sudo systemctl restart ssh
```
**Reality check:** Test the key-based login in a second terminal before closing your current SSH session. If the key setup failed and password login is already disabled, you are locked out, and recovery means a provider console session.
This takes 5 minutes and you do it once per server. Skip it on a throwaway test box. Never skip it on a server that holds client data.
**Skip the commands entirely:** CtrlOps handles this whole setup visually. Open your server, go to **SSH Management**, and create a custom user with the permissions you need - without writing a single command. The [Access Management guide](/docs/modules/access-management) covers every option, and this [video walkthrough](https://youtu.be/MKyuJv4c56U) shows the full flow step by step.
***
## How Do You Update Your Node.js App After Deployment? [#how-do-you-update-your-nodejs-app-after-deployment]
Deploying is the first time. Every code change after that needs a redeployment. Here is how updates work with both approaches.
### Manual Update Process [#manual-update-process]
```bash
ssh user@your-server-ip
cd /home/user/your-app
git pull origin main
npm install --omit=dev
npm run build # if you have a build step
pm2 restart your-app
```
Five commands, every time. Forgetting `npm install` after adding a new dependency causes a crash. Forgetting `npm run build` for a [Next.js app](/blog/deploy-nextjs-app-linux-vps) serves stale code.
One upgrade for apps with live traffic: use `pm2 reload your-app` instead of `pm2 restart`. Restart kills the process and relaunches it, dropping active connections for a few seconds. Reload replaces processes one at a time (in cluster mode), so the app never goes fully offline. For a side project the difference is invisible. For a client's production app, it is a zero-downtime deploy.
### Updating with CtrlOps [#updating-with-ctrlops]
CtrlOps does not have a built-in re-deploy button yet. But you can create a reusable **Script** in the [Script Directory](/docs/modules/ai-terminal/scripts):
```bash
cd /home/user/your-app
git pull origin main
npm install --omit=dev
npm run build
pm2 restart your-app
```
Save it once. Run it on any server with one click. Add variable placeholders like `{{app_name}}` for different projects.
Or use the AI Terminal: type "pull latest code and restart my app." CtrlOps generates the exact commands. You approve before anything runs.
### Useful PM2 Commands for Ongoing Management [#useful-pm2-commands-for-ongoing-management]
| Command | What It Does |
| ---------------------- | ---------------------------------------------------------------------------------------------- |
| `pm2 list` | See all running apps and their status |
| `pm2 logs your-app` | Tail live logs for debugging |
| `pm2 restart your-app` | Restart the app (picks up new env vars and code) |
| `pm2 reload your-app` | Zero-downtime restart; replaces processes one at a time in cluster mode |
| `pm2 stop your-app` | Stop without removing from PM2 |
| `pm2 delete your-app` | Remove the app from PM2 entirely |
| `pm2 monit` | Real-time dashboard showing CPU and memory per process |
| `pm2 save` | Save the current PM2 process list so applications automatically restart after a server reboot. |
| `pm2 startup` | Generate and configure the startup script to launch PM2 automatically when the server boots. |
**Bottom line:** Changing environment variables does not restart the app automatically. After editing `.env` values, either manually or through CtrlOps File Manager, run `pm2 restart your-app` to pick up the new values.
***
## Why Does Manual Deployment Stop Working at Scale? [#why-does-manual-deployment-stop-working-at-scale]
Manual deployment works fine for your first server. It breaks down at three or more.
A freelance developer managing 8 client servers deploys the same way each time. That is 13 steps multiplied by 8 servers: roughly 4-6 hours of pure deployment work per cycle. Each server has slightly different Node versions, different Nginx configs, different SSL setups. Keeping track of what is where becomes its own job.
A startup that deploys to its staging environment three times a week typically spends 90-135 minutes on deployment tasks each week. Over a month, that's 6-9 hours that could be invested in building new features instead.
Research by [Gloria Mark at UC Irvine](https://ics.uci.edu/~gmark/chi08-mark.pdf) found that it takes an average of 23 minutes to refocus after a context switch. For developers, this disruption is particularly costly because programming requires maintaining complex mental models that collapse when jumping between tools. During a manual deployment, you switch between terminal, text editor, browser, DNS panel, and documentation at least 6 times. The cumulative recovery time often exceeds the deployment time itself.
CtrlOps eliminates the scaling problem. Every deployment is identical: fill the form, click Deploy. The tenth deployment takes the same 4-5 minutes as the first. No accumulated config drift across servers. No forgotten PM2 startup scripts on server number 6.
> "For months, deployments terrified me - I'm not a DevOps guy. Every push to production made my stomach drop, so I delayed, avoided, and shipped less. Now I manage every deployment myself. No hiring, no favors, no waiting on someone else's calendar. The thing I was most scared of became the thing I do without thinking."
>
> * **Niraj Sheladiya**, [Co-founder of AutoReels](https://autoreels.in) ([original post on X](https://x.com/nirajsheladiya/status/2061782511622279460))
### How Does CtrlOps Compare to Other Deployment Options? [#how-does-ctrlops-compare-to-other-deployment-options]
| Approach | Deploy Time | Cost | Best For |
| --------------------------- | ------------------------------ | --------------------------- | ----------------------------------------------- |
| **Manual (SSH + terminal)** | 30-45 min | Free | Learning, custom setups, non-Node frameworks |
| **CtrlOps** | Under 5 min | $7/user/month (1 mo free) | Teams managing 1-25 servers, repeat deployments |
| **Vercel/Netlify** | 2-3 min | Free tier, then $20+/month | Frontend/JAMstack, serverless functions |
| **GitHub Actions CI/CD** | 5-10 min setup, then automatic | Free tier (2,000 min/month) | Teams with existing CI/CD experience |
| **Forge/RunCloud** | 5-10 min | $12-19/month | PHP/Laravel-focused teams |
CtrlOps sits between "do everything manually" and "use a full PaaS." You keep your own VPS, your own pricing, and full control. CtrlOps automates the repetitive configuration without locking you into a platform.
The key differentiator: CtrlOps [deploys from GitHub](/docs/modules/deployment) with automatic Nginx, PM2, and SSL setup. No agents are installed on your server. No cloud sync of credentials. Everything stays local on your machine.
For a broader comparison of where CtrlOps fits alongside CI/CD tools, IaC, and monitoring, we covered [15 DevOps automation tools](/blog/devops-automation-tools) with real workflow comparisons.
***
## When Should You Deploy Manually Instead? [#when-should-you-deploy-manually-instead]
CtrlOps one-click deployment covers Node.js, [React](/blog/deploy-react-app-linux-vps), Next.js, and static build-folder apps deployed from GitHub. For specific situations, manual deployment is still the right choice.
**Custom server architectures:** If your setup requires Docker Compose, Kubernetes, or multi-container orchestration, you need manual control or a dedicated CI/CD pipeline. CtrlOps does not handle container orchestration.
**Non-Node.js applications:** Python/Django, Go, Ruby on Rails, or PHP apps sit outside the one-click deployment scope. You can still use the [AI Terminal](/docs/modules/ai-terminal) to assist with manual deployment of these frameworks.
**Air-gapped or restricted environments:** Some compliance setups restrict what tools can run on servers. In these cases, scripted manual deployment through SSH is the standard approach.
**Learning purposes:** If you are deploying for the first time, walk through all 13 steps manually at least once. Understanding what PM2, Nginx, and Certbot actually do makes you a better developer. Then automate the repetition.
***
## Conclusion [#conclusion]
Deploying a Node.js app on a Linux VPS requires 13 steps. Server updates, Node installation, repo cloning, environment variables, dependency installation, firewall rules, PM2 setup, Nginx configuration, domain DNS, SSL certificates, and verification. The process takes 30-45 minutes manually and has not changed in years.
Every step is well-documented and reliable. But reliable does not mean efficient. When you deploy to multiple servers, deploy weekly, or deploy without deep Linux experience, the manual process becomes the bottleneck.
CtrlOps reduces this to one form and one click. Paste your GitHub URL, select a Node version, bulk-paste env variables, add a domain, and toggle on SSL. Click Deploy. PM2, Nginx, and SSL are configured automatically. Total time: under 5 minutes.
> "I'm a designer, I don't write code. Deployment was always my wall - I'd wait on a friend to handle the server stuff. But I opened CtrlOps, asked the AI Terminal in plain English what to do, and it walked me through everything step by step. I deployed my website. By myself. For the first time."
>
> * **Urvesh Kavar**, [UI/UX Product Designer](https://dribbble.com/Urvesh_7970) ([original post on LinkedIn](https://www.linkedin.com/posts/uiuxdesigner-urvesh-kavar_design-nocode-webdeployment-share-7467076744877862912-GL8W/))
The manual process is worth learning. The repetition is not.
***
Manual deployment on a Linux VPS takes 30-45 minutes for an experienced developer. This includes server updates, Node.js installation, cloning the repo, setting environment variables, configuring PM2, Nginx as a reverse proxy, and SSL via Certbot. CtrlOps one-click deployment reduces this to under 5 minutes by automating PM2, Nginx, and SSL configuration through a guided form.
Ubuntu 24.04 LTS is the most widely used Linux distribution for Node.js VPS hosting in 2026. It offers long-term security support until April 2029, broad package compatibility, and the largest community of deployment tutorials. Ubuntu 22.04 LTS is also a solid choice if your provider does not offer 24.04 yet.
Technically, no. Your Node.js app can serve traffic directly on port 3000. But for production use, Nginx is strongly recommended. It handles SSL termination, serves static files faster than Node, provides basic load balancing, and lets you run multiple apps on the same server with different domains. CtrlOps configures Nginx automatically during one-click deployment.
Without a process manager, Node.js runs in the foreground. Closing your SSH session kills the process. PM2 solves this by running your app in the background, restarting it on crashes, and starting it after server reboots. Run `pm2 start npm --name your-app -- start`, then `pm2 save` and `pm2 startup` to persist it.
CtrlOps provides a deployment form inside its File Manager. You enter your GitHub repo URL, select the Node.js version, paste environment variables (individually or bulk), add a domain, and toggle on SSL. Click Deploy, and CtrlOps clones the repo, installs dependencies, starts the app under PM2, configures Nginx as a reverse proxy, and runs Certbot for HTTPS. All steps show live progress. Pricing is $7/user/month with a 1 month free trial.
PM2 is a production process manager for Node.js. It keeps your app running in the background, auto-restarts it on crashes, supports cluster mode for multi-core CPUs, manages logs, and starts the app after server reboots. Without PM2, your Node.js app stops the moment your SSH session ends or the process crashes.
CtrlOps is a desktop application, not a hosting provider. You use your own VPS from any provider: DigitalOcean, AWS, Hetzner, Linode, or any server you can SSH into. CtrlOps connects via SSH and provides a visual interface for deployment, file management, monitoring, and AI-assisted operations. All credentials and data stay on your local machine.
CtrlOps deploys to one server at a time through the Add Application form. However, you can use the Script Directory to save deployment commands as reusable scripts with variable placeholders. Run the same script across any server with one click, changing only the app name or environment variables per server. This makes repeat deployments across a fleet consistent and fast.
---
# How to Deploy a React App on a Linux VPS in 5 Minutes (2026) (/blog/deploy-react-app-linux-vps)
Author: Daxesh Italiya | Published: 2026-07-14 | Tags: deploy react app on vps, react vps deployment, react nginx spa routing, vite build deployment, one-click deployment | Reading Time: 22 min read
> Deploy a React app on a Linux VPS in 12 steps or under 5 minutes with one-click deployment. Covers the production build, Nginx SPA routing, env vars, and SSL.
To deploy a React app on a Linux VPS manually, you run `npm run build` to generate static files, copy the output to a web directory, configure Nginx with an SPA routing fallback (`try_files $uri $uri/ /index.html`), and secure it with Certbot SSL. Total time: 20-30 minutes manually, or under 5 minutes with [CtrlOps one-click deployment](/docs/modules/deployment).
A production React build is not a running program. It is a folder of pre-built files. Deployed by hand, that means there is no process to keep alive and no port to proxy: the entire job is building the files correctly and telling Nginx how to serve them.
***
## Key Takeaways [#key-takeaways]
Deploying a React app on a Linux VPS in 2026 is simpler than [deploying Node.js](/blog/deploy-nodejs-app-linux-vps) or [Next.js](/blog/deploy-nextjs-app-linux-vps), but it has its own trap: client-side routing. Get the Nginx config wrong, and refreshing any page other than the homepage throws a 404. Get the environment variable prefix wrong, and your production build silently ships `undefined` instead of your API URL.
**Manual deployment (all 12 steps)** is the right choice when you want full control over caching headers, need a non-standard Nginx setup, or are deploying for the first time and want to understand what actually happens to your files. Total time: 20-30 minutes.
**CtrlOps one-click deployment** removes the repetition when you [deploy React apps from GitHub](/features/deployment) regularly. We tested both approaches on a fresh 1 GB DigitalOcean droplet running Ubuntu 24.04: the manual process took 20 to 30 minutes end-to-end, while CtrlOps finished in 5 minutes. You fill a form, select React as the application type, and click Create. The build, the start command, Nginx, and SSL are handled from there.
| Step | Manual Process | With CtrlOps |
| --------------------- | --------------------------------------------------- | ---------------------------------------- |
| Install Node.js | Run NodeSource setup script | Select version from dropdown |
| Clone repo | `git clone` via terminal | Pick the repo and branch from a dropdown |
| Environment variables | Create `.env` manually via `nano` | Bulk paste entire `.env` file |
| Install dependencies | `npm install` via terminal | Auto-runs during deploy |
| Production build | Run `npm run build` manually | Auto-runs during deploy |
| Serve the built files | Configure Nginx `root` and SPA fallback by hand | Set once in the Start Command field |
| Nginx | Write config file, test, reload | Handled automatically |
| DNS setup | Update A record at registrar | Update A record at registrar |
| SSL certificate | Install Certbot, run CLI commands | Toggle on, auto-configured |
| **Total time** | **20-30 minutes** | **Under 5 minutes** |
| **Tools required** | **5+ (terminal, editor, browser, DNS panel, docs)** | **1 (CtrlOps)** |
***
## Why Is React Deployment Different from Node.js or Next.js? [#why-is-react-deployment-different-from-nodejs-or-nextjs]
A React app compiled for production is not a running program. It is a folder of pre-built assets, usually named `dist` (Vite) or `build` (Create React App), that any web server can serve without executing a single line of JavaScript on the server. There is no `npm start` in the sense a Node.js app means it, and nothing has to stay resident in memory to render a page.
**Client-side routing needs a fallback rule.** If your app uses React Router, a URL like `/dashboard/settings` does not exist as a real file on disk. Whatever serves your files has to be told to return `index.html` for any path it cannot find, so React Router can take over and render the right screen in the browser. Skip this, and every direct link or page refresh outside the homepage returns a 404.
**Environment variables are baked in at build time, permanently.** Unlike a Node.js server that reads `.env` on every restart, a React build inlines environment variables directly into the JavaScript bundle the moment you run the build command. Change a variable after building, and nothing happens until you rebuild from scratch. This is documented behavior in the Create React App and Vite docs, not a bug: the variables are substituted as literal strings during compilation, so there is no runtime left to re-read them.
**Bottom line:** Create React App (CRA) was officially deprecated by the React team in February 2025 ([React docs: Creating a React App](https://react.dev/learn/creating-a-react-app)) and now runs in maintenance mode only, with no new features or performance work. Vite has become the standard build tool for React SPAs in 2026, and this guide covers commands for both, noting where they differ.
***
## What Do You Need Before Deploying React on a VPS? [#what-do-you-need-before-deploying-react-on-a-vps]
* **A Linux VPS** running Ubuntu 22.04 or 24.04 LTS with at least 1 GB of RAM. Static builds are far lighter on resources than Next.js SSR builds, so an entry-level VPS is usually enough.
* **SSH access** to your server. You should be able to run `ssh user@your-server-ip` from your local terminal.
* **Your React app in a GitHub repository.** Public repos work immediately. Private repos need a deploy key or a GitHub personal access token.
* **A domain name** (optional but recommended). Point the DNS A record to your server's public IP before starting the SSL step.
* **A successful local build.** Run `npm run build` on your machine first. If it fails locally, it fails on the server too, with less helpful output.
**Reality check:** Check your `package.json` before you start. Vite projects output to a `dist/` folder; Create React App projects output to `build/`. Using the wrong folder name is one of the most common reasons a fresh deployment shows a blank white screen.
***
## How to Deploy a React App on a VPS Manually: The Full 12-Step Process [#how-to-deploy-a-react-app-on-a-vps-manually-the-full-12-step-process]
Manual React deployment on a Linux VPS involves server preparation, building the static bundle, and configuring Nginx to serve it correctly, including the SPA routing fallback. An experienced developer finishes in 20-30 minutes.
### Step 1: Update Server Packages (2 Minutes) [#step-1-update-server-packages-2-minutes]
```bash
sudo apt update && sudo apt upgrade -y
```
### Step 2: Install Node.js and Git (3 Minutes) [#step-2-install-nodejs-and-git-3-minutes]
You only need Node.js to run the build. It does not need to stay running afterward.
```bash
curl -fsSL https://deb.nodesource.com/setup_24.x | sudo -E bash -
sudo apt install -y nodejs git
```
Verify:
```bash
node --version
npm --version
git --version
```
Node.js 24 LTS is the recommended version for production builds in 2026. [Node.js 24 LTS](https://nodejs.org/en/blog/release/v24.0.0) (codename Krypton) entered Long-Term Support in October 2025 and is supported through April 2028.
### Step 3: Clone Your React Project (1 Minute) [#step-3-clone-your-react-project-1-minute]
```bash
git clone https://github.com/your-username/your-app.git
cd your-app
```
For private repos:
```bash
git clone https://@github.com/your-username/your-app.git
```
### Step 4: Configure Environment Variables (3-5 Minutes) [#step-4-configure-environment-variables-3-5-minutes]
```bash
nano .env
```
For a Vite project, prefix every variable your frontend code reads with `VITE_`:
```
VITE_API_URL=https://api.yourdomain.com
VITE_ANALYTICS_KEY=abc123
```
For a Create React App project, the prefix is `REACT_APP_` instead:
```
REACT_APP_API_URL=https://api.yourdomain.com
REACT_APP_ANALYTICS_KEY=abc123
```
Save and exit (`Ctrl+X`, then `Y`, then `Enter`).
**Reality check:** Every variable your React code reads gets compiled directly into the JavaScript bundle and shipped to every visitor's browser. Never put secrets, database credentials, or private API keys in a React `.env` file. Anything prefixed `VITE_` or `REACT_APP_` is public the moment you build.
### Step 5: Install Project Dependencies (2-4 Minutes) [#step-5-install-project-dependencies-2-4-minutes]
```bash
npm install
```
On a 1 GB VPS, `npm install` can fail with a bare `Killed` message if memory runs out. A 2 GB swap file fixes it:
```bash
sudo fallocate -l 2G /swapfile
sudo chmod 600 /swapfile
sudo mkswap /swapfile
sudo swapon /swapfile
echo '/swapfile none swap sw 0 0' | sudo tee -a /etc/fstab
```
### Step 6: Build the Production Version (1-2 Minutes) [#step-6-build-the-production-version-1-2-minutes]
The command is the same for both build tools. Only the output folder differs.
```bash
npm run build
```
Vite generates a `dist/` folder. Create React App generates `build/`. Either way you get minified HTML, CSS, and JavaScript, with content-hashed filenames for cache busting.
**Bottom line:** React production builds are far lighter than Next.js builds since there is no server-side rendering to pre-compute. Most small-to-medium React apps build in under a minute, even on a 1 GB VPS.
### Step 7: Create a Web Directory (30 Seconds) [#step-7-create-a-web-directory-30-seconds]
Static files should live outside your home directory, in a location Nginx can read regardless of which system user owns it.
```bash
sudo mkdir -p /var/www/your-app
```
### Step 8: Copy the Build Files (30 Seconds) [#step-8-copy-the-build-files-30-seconds]
Copy the contents of your build output (not the folder itself) into the web directory.
For Vite:
```bash
sudo cp -r dist/* /var/www/your-app/
```
For Create React App:
```bash
sudo cp -r build/* /var/www/your-app/
```
Set correct ownership so Nginx can read the files:
```bash
sudo chown -R www-data:www-data /var/www/your-app
```
### Step 9: Install and Configure Nginx (5-8 Minutes) [#step-9-install-and-configure-nginx-5-8-minutes]
```bash
sudo apt install nginx -y
```
Create a new site config:
```bash
sudo nano /etc/nginx/sites-available/your-app
```
Paste this configuration:
```nginx
server {
listen 80;
server_name yourdomain.com www.yourdomain.com;
root /var/www/your-app;
index index.html;
location / {
try_files $uri $uri/ /index.html;
}
location ~* \.(js|css|png|jpg|jpeg|gif|svg|woff2?|ttf|eot)$ {
expires 30d;
add_header Cache-Control "public, immutable";
}
}
```
The `try_files $uri $uri/ /index.html;` line is the piece that makes client-side routing work. Nginx checks for a matching file, then a matching directory, and falls back to `index.html` if neither exists, letting React Router handle the path in the browser.
Enable the config and test it:
```bash
sudo ln -s /etc/nginx/sites-available/your-app /etc/nginx/sites-enabled/
sudo nginx -t
sudo systemctl reload nginx
```
If you would rather generate the config visually than write it by hand, the free [CtrlOps Nginx Config Generator](/tools/nginx-config-generator) produces a ready-to-use static site block in seconds.
**Reality check:** Without the `try_files` fallback, your homepage will load fine, but refreshing `/dashboard` or sharing a direct link to `/settings` returns a plain Nginx 404 page. This is the single most common React-on-VPS bug, and it has nothing to do with your React code.
### Step 10: Connect Your Domain to the VPS (2-5 Minutes) [#step-10-connect-your-domain-to-the-vps-2-5-minutes]
Update the DNS A record at your registrar (Namecheap, Cloudflare, GoDaddy):
| Record Type | Host | Value |
| ----------- | ---- | -------------- |
| A | @ | your-server-ip |
| A | www | your-server-ip |
Check propagation with `dig yourdomain.com +short`, or confirm the record from the browser with the free [DNS record lookup](/tools/dns-record-lookup) tool before you attempt SSL.
### Step 11: Install Certbot and Generate SSL (2-3 Minutes) [#step-11-install-certbot-and-generate-ssl-2-3-minutes]
```bash
sudo apt install certbot python3-certbot-nginx -y
sudo certbot --nginx -d yourdomain.com -d www.yourdomain.com
```
Test auto-renewal:
```bash
sudo certbot renew --dry-run
```
### Step 12: Verify the Deployment (1 Minute) [#step-12-verify-the-deployment-1-minute]
Open `https://yourdomain.com`. Confirm the homepage loads, then manually navigate to a nested route (like `/about` or `/dashboard`) and refresh the page. If it still loads instead of showing a 404, your SPA fallback is working correctly.
***
## Where Do React VPS Deployments Break? [#where-do-react-vps-deployments-break]
React deployments have fewer failure points than Node.js or Next.js, since there is no long-running server process to babysit. But the failures that do happen tend to be confusing precisely because everything looks fine on the surface.
### The Blank White Screen [#the-blank-white-screen]
The most common React deployment failure is an entirely blank page with no error visible anywhere in the UI. The usual causes: the build output was copied from the wrong folder (`build/` instead of `dist/`, or vice versa), the Nginx `root` directive points somewhere that does not match where the files actually live, or an absolute asset path in `index.html` does not match your domain structure. Opening the browser console almost always reveals a 404 for a `.js` or `.css` file, which points straight at the mismatch.
### Refreshing Any Route Except the Homepage 404s [#refreshing-any-route-except-the-homepage-404s]
Without the `try_files $uri $uri/ /index.html;` fallback in your Nginx config, only the exact homepage URL works. Every other client-side route returns a 404 the moment someone refreshes or shares a direct link. This is the single most-searched React-on-VPS deployment problem.
### Environment Variables That "Don't Update" [#environment-variables-that-dont-update]
A developer changes an API URL in `.env`, refreshes the browser, and sees the old value. Unlike a Node.js server, a React SPA has no runtime to restart. The old value is permanently compiled into the JavaScript bundle sitting in `/var/www/your-app`. The only fix is rebuilding (`npm run build`) and re-copying the output.
### Stale Browser Caching After Deploys [#stale-browser-caching-after-deploys]
Because static assets are often cached aggressively for performance (see the `expires 30d` rule above), returning visitors sometimes load an old version of your app after a deploy. Build tools like Vite solve this automatically by content-hashing filenames (`index-a1b2c3.js`), so a new build always has new filenames and old cached files are simply ignored. Make sure your `index.html` itself is never cached, only the hashed asset files, or visitors will keep loading a stale reference to old bundles.
### The Build Runs Out of Memory [#the-build-runs-out-of-memory]
On a 1 GB VPS, a large React build can die with `JavaScript heap out of memory` before it finishes. Raising Node's heap limit fixes it without resizing the server:
```bash
NODE_OPTIONS=--max-old-space-size=4096 npm run build
```
**Bottom line:** Nearly every React deployment issue traces back to one of two things: the wrong build folder being served, or a missing SPA fallback rule. Check those two first before assuming your React code is broken.
***
## How Does CtrlOps One-Click Deployment Handle React? [#how-does-ctrlops-one-click-deployment-handle-react]
CtrlOps reduces the manual build-and-serve process to a single form. You select React as the application type, pick your GitHub repo, and click Create. CtrlOps clones the repo, installs dependencies, runs the build, starts the app, configures Nginx, and issues the SSL certificate, streaming live terminal output for every phase. Total time: under 5 minutes.
The form is split into five cards. Here is the exact process:
**1. Open the Add Application form:** Connect to your server in CtrlOps, open the **Deployments** tab (or the [File Manager](/docs/modules/file-manager) toolbar), and click **Add Application**.

**2. Fill in basic information:** Name the app something recognizable ("Marketing Site", "Client Dashboard") and choose Development, Staging, or Production. Then point CtrlOps at your code: click **Connect GitHub** to authorize once and pick the repo and branch from a dropdown (private repos included, no deploy key needed), or paste a repository URL directly.
**3. Select the Node.js version:** Pick from the dropdown. Versions already on the server show a green checkmark; anything else shows a download icon and gets installed as part of the deploy.
**4. Choose React as the application type, and set the start command:** Selecting React auto-fills the Build Command as `npm run build`. The Start Command is the field that matters for a React app. A static build needs something to serve it on a port, so set it to match your build folder:
```bash
# Vite (dist/ folder)
serve -s dist -l 3000
# Create React App (build/ folder)
serve -s build -l 3000
```
The `-s` flag is the important part. It is short for "single page app", and it makes `serve` return `index.html` for any path it cannot find on disk. That is the same job the `try_files` rule does in the manual Nginx config, which is why client-side routing keeps working without you writing a fallback rule yourself.
**5. Add environment variables:** Add them one at a time (Key and Value fields), or click **Bulk Paste Environment Variables** and drop in your entire `.env` file at once. CtrlOps sets these before the build runs, so `VITE_` and `REACT_APP_` variables are correctly baked into the bundle.
**6. Configure the domain and SSL, then click Create:** Enter the port your start command listens on (3000 in the example above), add your domain, and toggle on **Setup SSL certificates for domains (using Certbot)**. Adding `yoursite.com` automatically covers `www.yoursite.com` too.
CtrlOps then opens a live Deployment Progress modal with a checklist: clone, install, build, start, configure Nginx, issue SSL. Each step turns green on success and red on failure, with the real terminal output underneath, so a failed build shows you the actual error from `npm run build` rather than a generic "deployment failed" dialog.
### What CtrlOps Handles Behind the Scenes [#what-ctrlops-handles-behind-the-scenes]
1. Clones the repo from GitHub
2. Installs the selected Node.js version if it is not already present
3. Runs `npm install` (or your custom install command)
4. Runs `npm run build` to produce the static bundle
5. Starts your start command under PM2, so the static server comes back up after a crash or reboot
6. Configures Nginx to route your domain to that port
7. Runs Certbot for SSL, if toggled on
**Bottom line:** The manual path and the CtrlOps path solve SPA routing differently. Manually, Nginx serves the files off disk and `try_files` provides the fallback. With CtrlOps, `serve -s` provides the fallback and Nginx routes to it. Same result for your users, and in both cases you still have to point at the right build folder (`dist` for Vite, `build` for CRA).
**Reality check:** DNS must already point to your server before SSL can succeed. If your domain is not pointed yet, deploy without SSL first and add it later from the [AI Terminal](/docs/modules/ai-terminal).
***
## React SPA on a VPS vs. Netlify, Vercel, and Cloudflare Pages [#react-spa-on-a-vps-vs-netlify-vercel-and-cloudflare-pages]
React apps are static files, which means they can be hosted almost anywhere: a VPS, Netlify, Vercel, Cloudflare Pages, or an S3 bucket behind a CDN. Each option trades convenience for cost and control differently.
| Approach | Deploy Time | Monthly Cost | Best For |
| ---------------------------------------- | --------------- | -------------------------------------------- | ----------------------------------------------------- |
| **Netlify / Cloudflare Pages free tier** | 1-2 min | Free, then usage-based | Personal projects, low traffic, zero infra |
| **Vercel** | 1-2 min | Free tier, then $20+/seat | Teams already on the Vercel ecosystem |
| **CtrlOps** | Under 5 min | $7/user/month (1 mo free) + VPS cost | Teams managing several apps/servers, predictable cost |
| **Manual (SSH + Nginx)** | 20-30 min | VPS cost only | Learning, custom Nginx rules, one-off projects |
| **S3 + CloudFront** | 15-20 min setup | Pay-per-request, usually a few dollars/month | High-traffic static sites needing global CDN |
A VPS starts making sense when your React frontend is one of several apps you manage, alongside an API, a database, or an admin panel, and you want everything on infrastructure you control at a flat monthly price. For a standalone portfolio or marketing page with no backend, a free static host like Netlify or Cloudflare Pages is the simpler choice.
**Bottom line:** If your React app is a standalone marketing site with no backend to manage, a free static host is usually the simpler choice. If it is one piece of a larger stack you are already running on a VPS, alongside an API, a database, or other apps, deploying it to the same server keeps everything under one roof.
***
## How Do You Update Your React App After Deployment? [#how-do-you-update-your-react-app-after-deployment]
Every code change needs a rebuild. What happens next depends on how you deployed.
### Manual Update Process [#manual-update-process]
Rebuild and re-copy the static files. There is no process to restart, because nothing is running.
```bash
ssh user@your-server-ip
cd /home/user/your-app
git pull origin main
npm install
npm run build
sudo rm -rf /var/www/your-app/*
sudo cp -r dist/* /var/www/your-app/
sudo chown -R www-data:www-data /var/www/your-app
```
(Swap `dist/*` for `build/*` if you are on Create React App.) Nginx serves whatever files are currently sitting in the web directory, so the moment the new files are copied in, the new version is live.
### Updating with CtrlOps [#updating-with-ctrlops]
Save this sequence once as a reusable **Script** in the [Script Directory](/docs/modules/ai-terminal/scripts), with `{{app_name}}` as a placeholder for reuse across projects:
```bash
cd /home/user/{{app_name}}
git pull origin main
npm install
npm run build
pm2 restart {{app_name}}
```
Because CtrlOps runs your static server under PM2, the restart picks up the freshly built folder. You only write that script once - [it is then one click on every server you connect to](/features/script-directory), and the placeholder is filled in at run time. Or type it in plain English in the [AI Terminal](/docs/modules/ai-terminal): "pull the latest code, rebuild, and restart the app." CtrlOps generates the exact command sequence and waits for your approval before running anything.
**Bottom line:** A rebuild is mandatory on every deploy, because your environment variables and your entire app are compiled into the bundle. There is no "just restart it and pick up the new config" shortcut like there is with a Node.js API.
***
## When Should You Deploy React Manually Instead? [#when-should-you-deploy-react-manually-instead]
Deploy React manually instead of using one-click tools when:
**Custom caching or CDN rules:** You need fine-grained cache-control headers per route, edge-side includes, or a CDN layered in front of Nginx.
**Multi-app Nginx setups with shared infrastructure:** Your React app shares a server with an API and needs a specific location block routing `/api/` to a backend on a different port.
**Monorepo builds:** Your React app lives inside a Turborepo or Nx monorepo with a non-standard build pipeline where the default `npm run build` does not apply.
**Learning purposes:** Walking through the manual process once (build, copy, configure Nginx, add the SPA fallback) makes the "why" behind each automation step obvious when something breaks.
***
## Best Practice: Create a Non-Root Deploy User [#best-practice-create-a-non-root-deploy-user]
Every command in this guide works as root, but building a React app as root means one compromised npm package owns your entire server. A production build runs `npm install`, and `npm install` runs whatever `postinstall` scripts your dependency tree brings with it. That is a lot of third-party code to hand root to. Create a dedicated deploy user once, and every deployment on that server is safer.
```bash
adduser deploy
usermod -aG sudo deploy
```
Copy your SSH key to the new user and test the login:
```bash
ssh-copy-id deploy@your-server-ip
ssh deploy@your-server-ip
```
Once key-based login works, disable password authentication. Open the SSH config:
```bash
sudo nano /etc/ssh/sshd_config
```
Set `PasswordAuthentication no`, save, then restart SSH:
```bash
sudo systemctl restart ssh
```
**Reality check:** Test the key-based login in a second terminal before closing your current SSH session. If the key setup failed and password login is already disabled, you are locked out. Recovery means a provider console session.
This split also maps cleanly onto how a React deploy actually works. Clone and build inside the deploy user's own home directory (`/home/deploy/your-app`), where it owns every file and `npm install` never hits a permission error. Only the final copy into `/var/www/your-app` needs `sudo`, because that directory belongs to `www-data`. If you try to run the whole thing out of `/var/www`, `npm install` will fail with `EACCES` permission errors, which is a confusing way to learn this lesson.
It takes 5 minutes and you do it once per server. Skip it on a throwaway test box. Never skip it on a server that holds user data or client applications.
**Skip the SSH commands:** CtrlOps handles SSH user setup visually. Open your server, go to **SSH Management**, and create a custom user with the permissions you need. The [Access Management guide](/docs/modules/access-management) walks through every option, and this [video walkthrough](https://youtu.be/MKyuJv4c56U) shows the full flow step by step.
***
## Conclusion [#conclusion]
Deploying a React app to a Linux VPS is lighter than deploying Node.js or Next.js, since a production build is just files. But it has its own sharp edges: copying the wrong build folder, forgetting the SPA routing fallback, or assuming environment variables update without a rebuild. None of these show up as an obvious server crash. They show up as a blank screen or a confusing 404, which makes them harder to debug than a process that simply refuses to start.
CtrlOps runs the build, starts your static server under PM2, wires up Nginx, and issues SSL, all from one form. For teams managing multiple apps across several servers, it fits into a broader [DevOps automation workflow](/blog/devops-automation-tools) without adding tool sprawl.
***
Manual deployment takes 20-30 minutes for an experienced developer, covering server setup, the production build, copying static files, configuring Nginx with SPA routing, and SSL via Certbot. CtrlOps one-click deployment reduces this to under 5 minutes by automating the build, the start command, the Nginx config, and the certificate.
Not if you serve the files straight off disk. A React production build is a folder of static HTML, CSS, and JavaScript, and Nginx can serve it with no process manager involved at all. You only need PM2 if you choose to serve the build through a static server like `serve` on a port, which is the approach CtrlOps uses so the app survives a crash or a reboot.
Whatever serves your files is not configured with a fallback for client-side routes. If Nginx serves the files directly, add `try_files $uri $uri/ /index.html;` inside your `location /` block. If you serve the build through the `serve` package, use the `-s` flag (`serve -s dist`), which does the same thing. Either way, any path that does not match a real file falls back to `index.html` so React Router can handle it.
Vite. Create React App was officially deprecated by the React team in February 2025 and now runs in maintenance mode with no new features or performance improvements. Vite offers substantially faster builds and is the build tool the React team currently points new projects toward.
React environment variables are compiled directly into the JavaScript bundle at build time, not read at runtime like a Node.js server would. Changing a value in `.env` has no effect until you run `npm run build` again and redeploy the new output.
Vite outputs to a `dist/` folder by default. Create React App outputs to a `build/` folder. Point your Nginx `root` directive, your start command, and your deployment scripts at whichever one matches your project's build tool, since using the wrong folder name is a common cause of a blank page after deployment.
No. Every environment variable your React code reads gets bundled into the client-side JavaScript and shipped to every visitor's browser. Anything prefixed `VITE_` or `REACT_APP_` should be treated as public information, never API secrets, database credentials, or private keys.
The pipeline is the same shape (clone, install, build, start, Nginx, SSL), but the Start Command is what changes. A Node.js or Next.js app starts its own server with `npm start`. A React build has no server, so you point the Start Command at a static server instead: `serve -s dist -l 3000` for Vite, or `serve -s build -l 3000` for Create React App. The `-s` flag handles SPA routing, and Nginx routes your domain to that port.
The build ran out of RAM. On a 1 GB VPS, add a 2 GB swap file, or raise Node's heap limit by setting `NODE_OPTIONS=--max-old-space-size=4096` as an environment variable before the build runs. In CtrlOps, add that as an environment variable in the deployment form and the build step picks it up.
---
# 15 Best AI DevOps Tools for Small Teams in 2026 (/blog/devops-automation-tools)
Author: Hiren Kalariya | Role: Co-Founder & CEO, TST Technology | Published: 2026-05-18 | Updated: 2026-06-11 | Tags: devops automation tools, ci/cd automation, infrastructure automation, server management, devops tools | Reading Time: 28 min read
> The 15 best DevOps automation tools in 2026: real workflow comparisons, a phased automation roadmap, and the server ops layer every other guide misses.
## Key Takeaways [#key-takeaways]
The best DevOps automation tools for small teams in 2026 are **GitHub Actions** (CI/CD), **Docker** (containers), **Terraform** or **Ansible** (infrastructure as code), **Prometheus + Grafana** (monitoring), and **CtrlOps** (server operations). A team managing 1 - 25 servers can cover roughly 80% of its automation needs for about [$7/month per user](/pricing) - and CtrlOps starts with a 1 month free trial - with CtrlOps + GitHub Actions + Docker - and should skip Kubernetes, Chef, and enterprise monitoring until it genuinely outgrows what's simpler.
Automation isn't just faster: automated pipelines run a 5 - 15% change failure rate versus 30 - 46% for heavily manual processes ([DORA research](https://dora.dev/research/)).
| Category | Top Pick | Runner-Up | Free Tier? | Best For |
| -------------- | ------------------------------ | -------------- | ---------- | ----------------------------------------------------- |
| CI/CD | GitHub Actions | GitLab CI/CD | ✅ Both | Push-to-deploy pipelines |
| IaC | Terraform | Ansible | ✅ Both | Provisioning & config management |
| Containers | Docker | Docker Compose | ✅ Both | Consistent app environments |
| Orchestration | Kubernetes | ArgoCD | ✅ Both | 50+ containers (skip if under 50) |
| Monitoring | Prometheus + Grafana | Datadog | ✅ / ❌ | Metrics, alerting, observability |
| **Server Ops** | **CtrlOps ($7/mo, 1 mo free)** | Portainer | ✅ Both | **Best AI DevOps tool for small teams & freelancers** |
**The four layers every team needs to automate - in this order:**
1. **Server access** - Replace IP spreadsheets and scattered SSH keys with a named directory (Day 1)
2. **Deployments** - One-click or push-triggered, verified, and done in under 5 minutes (Week 1)
3. **Monitoring and backups** - Automated health checks, alerts, and database backups (Week 2 - 4)
4. **AI-assisted debugging** - Natural language commands with live server context, not generic ChatGPT advice (Month 2+)
**The uncomfortable truth:** Every DevOps guide covers layers 1 - 3. None of them covers layer 4 - the server operations layer, where you spend 60%+ of your actual time. CI/CD deploys the code. Server management keeps it running. This guide covers both.
***
## Why Small Teams Need a Different DevOps Automation Stack [#why-small-teams-need-a-different-devops-automation-stack]
You're four tools deep into a deployment at 11 PM.
Terminal open. File manager in another window. Monitoring dashboard on a third screen. Notes app with the server IPs that might or might not be current. And a ChatGPT tab where you're pasting error logs, hoping for a clue - from an AI that has never seen your actual server.
Every solo DevOps freelancer and startup CTO I talk to describes the same chaos. Managing 12 client servers with nothing but SSH and a spreadsheet. Wasting 30 minutes on deployments that should take 5. Living with the constant fear of running a command on the wrong production server at midnight.
According to [The Business Research Company](https://www.thebusinessresearchcompany.com/report/devops-global-market-report), the global DevOps automation tools market is growing from **$14.95 billion in 2025 to $18.77 billion in 2026** - a **25.6% CAGR** - but most of that money flows to enterprise teams with dedicated DevOps departments. What about you? The freelancer. The startup CTO. The small teams. The developer who builds software but never wanted to become a Linux expert just to keep it running.
This guide is for you.
You'll get a practical breakdown of 15 DevOps automation tools with real workflow comparisons, actual time numbers, a phased roadmap telling you what to automate on Day 1 versus Month 1, honest assessments of what's overkill for small teams, and - critically - the layer nobody else covers: what actually happens after your deployment pipeline finishes.
***
## What Are DevOps Automation Tools? [#what-are-devops-automation-tools]
### The Real Definition (Not the Textbook One) [#the-real-definition-not-the-textbook-one]
Textbooks define DevOps automation tools as "software solutions that automate processes between software development and IT operations." That's technically accurate and practically useless.
Here's the real version: **DevOps automation tools remove you as the bottleneck between writing code and running it reliably in production.**
Without automation, every deployment needs you. Every server configuration needs you. Every 2 AM incident needs you. With automation, those things happen without your hands on a keyboard - or with your hands on a keyboard for 5 minutes instead of 45. For small teams, the right AI DevOps tools don't just speed up processes - they replace the need for a dedicated DevOps hire entirely.
The difference that matters isn't the definition - it's understanding that "automation" in DevOps covers four distinct layers, and most teams only automate two of them.
### The 4 Layers of DevOps Automation Every Team Needs [#the-4-layers-of-devops-automation-every-team-needs]
#### CI/CD Pipeline Automation (Build, Test, Deploy) [#cicd-pipeline-automation-build-test-deploy]
The most-discussed layer. When you push code, automated pipelines run tests, build artifacts, and deploy to your servers. If you've ever manually run `npm install` on a production server, you know exactly why this matters. **Tools:** Jenkins, GitHub Actions, GitLab CI/CD, CircleCI.
#### Infrastructure as Code (Provision and Configure) [#infrastructure-as-code-provision-and-configure]
Describing your servers and cloud resources as code files so they're reproducible and version-controlled. When a server dies, you don't spend a half-day rebuilding it from memory - you run your IaC config and get an identical replacement. **Tools:** Terraform, Ansible, Pulumi.
#### Container Orchestration (Run and Scale) [#container-orchestration-run-and-scale]
Managing containerized applications across clusters - handling deployment, scaling, networking, and self-healing automatically. **Tools:** Kubernetes, Docker Swarm, ArgoCD. Small teams that want push-to-deploy without standing up Kubernetes often reach for a self-hosted PaaS instead - see [CtrlOps vs Dokploy](https://ctrlops.io/compare/ctrlops-vs-dokploy) for how that trade-off looks.
#### Server Operations and Management (The Layer Everyone Forgets) [#server-operations-and-management-the-layer-everyone-forgets]
This is the 40% of DevOps work that falls between your CI/CD pipeline and your IaC templates. File edits on a running server. Disk space checks at 9 PM Friday. Revoking SSH access after a team member departs. Debugging why a service throws 500s twenty minutes *after* a perfectly successful automated deploy.
No CI/CD pipeline covers this. No Terraform template handles it. And if you're managing 5 - 25 servers, you're doing most of it manually - right now.
**The four-layer reality:** Most DevOps guides cover layers 1 - 3 in depth and treat layer 4 as "just use SSH." For teams under 25 people, layer 4 is where the most time gets lost - and where the most outages originate. This guide covers all four.
***
## Why Most Teams Stay Manual (And What It Costs Them) [#why-most-teams-stay-manual-and-what-it-costs-them]
The DevOps automation market is growing at **25.6% annually**, yet most small teams are still doing the majority of their operations work manually. Not because they're careless. Because every piece of automation advice assumes you have a dedicated DevOps team, an existing Kubernetes cluster, and an enterprise budget.
Here's what staying manual actually costs - in time, money, and risk.
### The 30-Minute Deployment That Should Take 5 Minutes [#the-30-minute-deployment-that-should-take-5-minutes]
A real [manual deployment for a Node.js application on a VPS](/blog/deploy-nodejs-app-linux-vps), step by step:
| Step | What You Do | Time |
| ---- | ------------------------------------------- | ----------- |
| 1 | Find server IP in your spreadsheet | 2 min |
| 2 | SSH into the correct server (first try?) | 1 - 2 min |
| 3 | Navigate to the project directory | 1 min |
| 4 | Pull the latest code from Git | 2 - 3 min |
| 5 | Install dependencies | 3 - 5 min |
| 6 | Build the application | 2 - 3 min |
| 7 | Restart services in the right order | 1 - 2 min |
| 8 | Verify the app is actually responding | 5 min |
| 9 | Check logs for errors you might have missed | 5 - 10 min |
| 10 | Fix anything that comes up | 10 - 30 min |
**Total: 30 - 45 minutes** if nothing breaks. When something does - wrong branch, dependency conflict, failed migration - you're looking at 60+ minutes.
The worst part isn't the time. It's the uncertainty. After step 9, you *think* the deployment worked. But did you verify all endpoints? Did the migration run? Did the background worker restart? Manual verification means checking a few things and hoping the rest is fine. That "hope" is where production incidents are born.
### The Spreadsheet Full of Server IPs That Nobody Updates [#the-spreadsheet-full-of-server-ips-that-nobody-updates]
Every team that hasn't automated server access management has one. Columns for IP, hostname, SSH user, purpose, and "notes." The notes column has "PRODUCTION - be careful" in red, written 8 months ago.
The problem: it's always wrong. IPs change when servers get reprovisioned. New servers get added by whoever provisioned them. Old servers get decommissioned but stay in the sheet for months. According to [StrongDM's DevOps Statistics research](https://www.strongdm.com/blog/devops-statistics), **over 50% of organizations struggle with assigning, rotating, and tracking credentials**. When your server directory lives in a Google Sheet, you're part of that statistic.
### Bus Factor of 1: When Only One Person Can Deploy [#bus-factor-of-1-when-only-one-person-can-deploy]
In a 6-person startup, Sarah knows how to deploy. Not because she was elected - because she set it up originally and it lives in her head. When Sarah is sick, nothing ships. When Sarah takes a vacation, releases get scheduled around her PTO.
**[50% of organizations](https://www.strongdm.com/blog/devops-statistics)** report that access requests take hours, days, or even weeks because deployment knowledge is concentrated in a single person. This isn't a people problem. It's a documentation and automation problem. The fix starts with [centralizing how you manage multiple servers](/blog/manage-multiple-servers-without-losing-control) - so the knowledge lives in a system, not a person. And it's completely invisible until Sarah announces she's leaving.
Spirex Infoways lived this with a nine-person team: one person carried the entire DevOps load, and a fix that needed repeating across three or four servers ate up to two hours. [Centralizing the fleet removed the bottleneck](/case-studies/spirex-infoways) and took those changes under ten minutes.
### The DevOps Tool for Freelancers Problem: 12 Clients, Zero Consistency [#the-devops-tool-for-freelancers-problem-12-clients-zero-consistency]
Freelancers face a different version of the same chaos. You're not managing one team's servers - you're managing 8 - 12 clients' servers across different stacks, different providers, and different deployment expectations.
Each client has their own SSH credentials, their own deployment process, and their own "notes" document that lives somewhere in your Downloads folder. When something breaks at 9 PM on a Friday, you're not just debugging a server - you're first spending 10 minutes finding *which* server.
The DevOps tool for freelancers needs to solve organization first, automation second. Because no CI/CD pipeline helps you when you can't remember which IP belongs to which client in under 30 seconds.
What freelancers actually need:
* A named server directory that's always current
* Deployments that work identically across every client environment
* Monitoring that covers all clients from one view - not 12 separate dashboards
* Local credential storage that doesn't put client SSH keys on a third-party cloud
### SSH Key Sprawl After Team Members Leave [#ssh-key-sprawl-after-team-members-leave]
Most teams have an offboarding checklist for email, GitHub, and Notion. Almost none have one for SSH access. When someone leaves, their email gets disabled the same day - but their SSH key sits in `~/.ssh/authorized_keys` on every production server they ever touched, and nobody owns the task of removing it. Without a documented process, that access stays live indefinitely.
**The credentials time bomb:** Every engineer who leaves without proper offboarding leaves SSH keys sitting on your production servers. According to [StrongDM's DevOps Statistics research](https://www.strongdm.com/blog/devops-statistics), **42% of organizations use shared SSH keys** and **65% use team or shared logins**. When someone leaves, their access doesn't. Those credentials are still on their laptop, in their backup, and potentially in their personal password manager - indefinitely.
For freelancers and agencies managing client infrastructure, this isn't just a security risk. It's a contract liability. Most client agreements include security clauses. If a breach occurs because a stale SSH key was never removed, the exposure is yours.
#### Real Security Exposure from Stale Credentials on Production Servers [#real-security-exposure-from-stale-credentials-on-production-servers]
A former team member's compromised laptop gives an attacker direct root access to your production servers. No brute force. No exploit. Just an old key that nobody removed. Gartner estimates the average cost of IT downtime at **$5,600 per minute** - and [ITIC's 2024 Hourly Cost of Downtime Survey](https://itic-corp.com/itic-2024-hourly-cost-of-downtime-part-2/) corroborates this: 97% of enterprises report a single hour of downtime costs over $100,000. Stale credentials aren't a theoretical risk - they're an open door with a known price tag.
***
## Manual vs Automated DevOps: A Real Workflow Comparison [#manual-vs-automated-devops-a-real-workflow-comparison]
### Manual Deployment Workflow (30 - 45 Minutes Per Deploy) [#manual-deployment-workflow-30---45-minutes-per-deploy]
For freelancers and small teams, the gap between manual and automated isn't just measured in minutes. It's measured in how many clients you can realistically manage, how confidently you can onboard a second team member, and whether you can actually take a weekend off without a deployment hanging over you.
#### SSH in, Pull Code, Install Deps, Restart Services, Verify Manually, Hope Nothing Broke [#ssh-in-pull-code-install-deps-restart-services-verify-manually-hope-nothing-broke]
| Step | Manual Time | Failure Points |
| ----------------------- | --------------- | -------------------------------------- |
| Find server credentials | 2 - 5 min | Wrong IP, outdated notes |
| SSH into correct server | 1 - 3 min | SSH into staging instead of prod |
| Git pull correct branch | 2 - 4 min | Wrong branch, merge conflicts |
| Install dependencies | 3 - 8 min | Package conflicts, registry timeouts |
| Run migrations | 2 - 5 min | Migration failures that corrupt the DB |
| Restart services | 1 - 2 min | Wrong restart order, missed a service |
| Review logs | 3 - 5 min | Log too long to spot the actual error |
| Functional verification | 2 - 5 min | Checked the wrong environment |
| **Total** | **16 - 37 min** | **7+ failure points every deploy** |
### Automated Deployment Workflow (Under 5 Minutes) [#automated-deployment-workflow-under-5-minutes]
#### One-Click or Push-Triggered With Built-In Verification and Automatic Rollback [#one-click-or-push-triggered-with-built-in-verification-and-automatic-rollback]
| Step | Automated Time | Failure Points |
| --------------------------- | -------------- | --------------------------------------- |
| Push to main / click Deploy | 0 min | None |
| Pipeline: test + build | 1 - 2 min | Tests catch code issues before prod |
| Deploy to correct server | 1 min | Pre-configured, can't misroute |
| Run migrations | Automatic | Automatic rollback on failure |
| Health check verification | Automatic | Fails fast with a clear, specific error |
| Notify team via Slack/email | Automatic | Everyone knows status without asking |
| **Total** | **2 - 5 min** | **1 failure point: your code** |
The key difference isn't just speed. It's **certainty**. You go from "I think it worked" to "the pipeline confirmed it worked" in the time it takes to grab coffee.
### Time Savings Breakdown Across 10 Deployments Per Week [#time-savings-breakdown-across-10-deployments-per-week]
| Metric | Manual | Automated | Savings |
| -------------------- | --------------- | ------------- | ----------------------------- |
| Time per deployment | 30 - 45 min | 3 - 5 min | 25 - 40 min |
| Weekly (10 deploys) | 5 - 7.5 hours | 30 - 50 min | \~4 - 6.5 hours |
| Monthly (40 deploys) | 20 - 30 hours | 2 - 3.5 hours | \~18 - 26 hours |
| Annual (480 deploys) | 240 - 360 hours | 24 - 42 hours | **200 - 320 hours recovered** |
200 - 320 hours per year - 5 to 8 full work weeks - from automating deployments alone.
### Error Rate Comparison: Manual vs Automated Deployments [#error-rate-comparison-manual-vs-automated-deployments]
According to the [DORA State of DevOps Research](https://dora.dev/research/), elite-performing teams with automated CI/CD pipelines achieve a **Change Failure Rate of 5 - 15%**, while low-performing teams relying on heavily manual processes report rates **above 30 - 46%**. Manual deployments fail or cause a notable issue roughly 1 in every 3 - 5 times. Automated pipelines: closer to 1 in every 7 - 20.
**Why the gap is bigger than the numbers suggest:** Automated failures are caught within minutes by the pipeline. Manual failures often go undetected for hours until a user reports them. The real cost difference isn't just failure frequency - it's detection speed and mean time to recovery.
***
## 15 Best DevOps Automation Tools in 2026 [#15-best-devops-automation-tools-in-2026]
This isn't a padded list with one-line tool descriptions. These are the 15 AI DevOps tools that actually matter for small teams in 2026 - with honest notes on when each makes sense and when it's overkill for your headcount. Every tool has been evaluated specifically for teams managing 1 - 25 servers, not enterprise deployments with dedicated SRE teams.
### CI/CD Pipeline Automation Tools [#cicd-pipeline-automation-tools]
#### 1. Jenkins - Self-Hosted CI/CD With 1,800+ Plugins [#1-jenkins---self-hosted-cicd-with-1800-plugins]
Open source, self-hosted, and infinitely extensible with over 1,800 plugins. If you can imagine a build or deployment workflow, [Jenkins](https://www.jenkins.io/) can run it.
**Best for:** Teams that need maximum pipeline customization and are comfortable managing the Jenkins server itself.
**Real talk:** Jenkins requires dedicated maintenance. You're managing CI/CD infrastructure *on top of* your application servers. For teams under 10 people, this overhead frequently outweighs the flexibility. GitHub Actions is faster to start with, no server to maintain.
**Pricing:** Free (open source). You pay for the server it runs on.
***
#### 2. GitHub Actions - CI/CD Built Into Your Repository [#2-github-actions---cicd-built-into-your-repository]
[GitHub Actions](https://github.com/features/actions) workflows live as YAML files in your repo. Triggers are git events (push, PR, release). Free tier covers 2,000 minutes/month for private repos. No separate CI server. No infrastructure to maintain.
**Best for:** Teams already on GitHub who want working CI/CD without managing additional infrastructure.
**Real talk:** The YAML syntax is learnable in a day. A working test-build-deploy pipeline is realistic by the end of the week. The marketplace has 15,000+ pre-built actions for almost any integration. And when a pipeline fails on a cryptic indentation error, pasting the file into a [YAML validator](/tools/yaml-validator) finds it faster than re-reading it line by line.
**Pricing:** Free for public repos. 2,000 min/month free for private repos, then \~$0.008/minute.
***
#### 3. GitLab CI/CD - All-in-One DevOps Platform [#3-gitlab-cicd---all-in-one-devops-platform]
[GitLab](https://about.gitlab.com/) bundles code hosting, CI/CD, container registry, security scanning, and project management in one platform. If you're tired of stitching together GitHub + CircleCI + Artifactory + Jira, GitLab's consolidation is genuinely compelling.
**Best for:** Teams that want a single platform for the entire software delivery lifecycle with no cross-tool integration headaches.
**Pricing:** Free tier available. Paid plans from $29/user/month.
***
#### 4. CircleCI - Managed CI/CD Without Self-Hosting [#4-circleci---managed-cicd-without-self-hosting]
[CircleCI](https://circleci.com/) delivers fast, managed CI/CD with Docker support, parallelism, and build caching built in. Integrates with GitHub, GitLab, and Bitbucket without ecosystem lock-in.
**Best for:** Teams that want hosted CI/CD and flexibility beyond any single platform's native tooling.
**Pricing:** Free tier (6,000 build minutes/month). Performance plan from $15/month.
***
### Infrastructure as Code Tools [#infrastructure-as-code-tools]
#### 5. Terraform - Multi-Cloud Infrastructure Provisioning [#5-terraform---multi-cloud-infrastructure-provisioning]
[Terraform](https://www.terraform.io/) lets you define your entire infrastructure - servers, databases, networks, DNS, load balancers - in code. Run `terraform apply` and it provisions everything. Run it again when something changes, and it modifies only what's different. No manual tracking, no configuration drift.
**Best for:** Teams managing infrastructure across multiple cloud providers (AWS + GCP + Azure).
**Real talk:** Terraform state management adds real complexity. For a solo freelancer managing 5 DigitalOcean droplets, Terraform may be more overhead than it saves. Use remote state storage from day one, or the `.tfstate` file becomes a headache of its own.
**Pricing:** CLI is open source (free). Terraform Cloud: free up to 5 users, then $20/user/month.
***
#### 6. Ansible - Configuration Management and Deployment [#6-ansible---configuration-management-and-deployment]
[Ansible](https://www.ansible.com/) is agentless - no software to install on target servers. Runs over SSH. Writes automation in YAML playbooks that any engineer can read without certification. Idempotent: run the same playbook 10 times, get the same result.
**Best for:** Teams managing server configuration without containers, or supplementing Terraform with post-provision setup.
**Real talk:** Ansible is the most approachable IaC tool for teams coming from manual SSH workflows. Know Linux and YAML? Useful playbooks in a day.
**Pricing:** Open source (free). Red Hat Ansible Automation Platform: enterprise pricing.
***
#### 7. Pulumi - IaC Using Python, TypeScript, or Go [#7-pulumi---iac-using-python-typescript-or-go]
[Pulumi](https://www.pulumi.com/) does what Terraform does but replaces HCL with real programming languages - Python, TypeScript, Go, or C#. Real languages mean loops, conditionals, functions, and your existing package ecosystem - no separate DSL to learn.
**Best for:** Developer-heavy teams where infrastructure code should feel like application code.
**Pricing:** Open source (free). Pulumi Cloud: free for individuals; team plans from $50/month.
***
#### 8. Chef - Policy-Driven Infrastructure Automation [#8-chef---policy-driven-infrastructure-automation]
Ruby-based "recipes" and "cookbooks." Mature, enterprise-grade, used at thousands of nodes under strict compliance requirements.
**Best for:** Large enterprises with complex compliance environments.
**Real talk:** Chef's learning curve and Ruby dependency are hard to justify for teams under 50 people. Ansible handles 95% of the same use cases with a fraction of the complexity. On this list because it genuinely matters at enterprise scale - not because you should use it.
***
### Container Orchestration Tools [#container-orchestration-tools]
#### 9. Docker - Package and Run Applications Consistently [#9-docker---package-and-run-applications-consistently]
[Docker](https://www.docker.com/) packages your application and all its runtime dependencies into a container that runs identically everywhere - your laptop, staging, production. Eliminates "works on my machine" definitively.
**Best for:** Every team deploying applications. Docker is table stakes in 2026, not optional.
**Real talk:** The learning curve is a weekend. The payoff starts immediately. If you're not containerizing yet, start here - before anything else in this list.
**Pricing:** Free (Docker Engine). Docker Desktop free for small businesses.
***
#### 10. Kubernetes - Orchestrate Containers at Scale [#10-kubernetes---orchestrate-containers-at-scale]
[Kubernetes](https://kubernetes.io/) manages containerized applications across clusters - auto-scaling, self-healing, rolling updates, service discovery - everything for running containers at genuine scale.
**Best for:** Teams running 50+ containers across multiple services with traffic variability requiring auto-scaling.
**Kubernetes reality check:** K8s is genuinely necessary at scale - and genuinely punishing below it. The learning curve is steep. Day-2 operations (monitoring, logging, security, upgrades) require significant expertise. Teams under 10 people with fewer than 20 services almost always find the operational overhead exceeds the benefits. Start with Docker Compose. Migrate when you actually outgrow it - not because a job posting listed K8s as a requirement.
**Pricing:** Free (open source). Managed K8s (EKS, GKE, AKS) charges for worker node compute.
***
#### 11. ArgoCD - GitOps for Kubernetes Deployments [#11-argocd---gitops-for-kubernetes-deployments]
Your desired cluster state lives in Git. [ArgoCD](https://argo-cd.readthedocs.io) continuously ensures your running cluster matches it. Configuration drift gets detected and corrected automatically.
**Best for:** Teams already running Kubernetes who want declarative, Git-driven deployments with automatic drift correction.
**Real talk:** Only useful if you're already running K8s. Don't adopt Kubernetes just to use ArgoCD.
**Pricing:** Free (open source).
***
### Monitoring and Observability Tools [#monitoring-and-observability-tools]
#### 12. Prometheus - Metrics Collection and Alerting [#12-prometheus---metrics-collection-and-alerting]
[Prometheus](https://prometheus.io/) scrapes metrics from your services and infrastructure on a defined interval, stores them in a time-series database, and evaluates alerting rules you define. Pair with [Grafana](https://grafana.com/) for dashboards that actually tell you something.
**Best for:** Teams running self-hosted infrastructure who want powerful, customizable monitoring without SaaS subscription costs.
**Pricing:** Open source (free). Requires hosting and configuration overhead.
***
#### 13. Datadog - Full-Stack Monitoring and APM [#13-datadog---full-stack-monitoring-and-apm]
[Datadog](https://www.datadoghq.com/) combines infrastructure monitoring, APM, log management, and synthetic testing in one SaaS platform. An agent install takes 5 minutes and data flows immediately - no Prometheus configuration, no Grafana dashboards to build from scratch.
**Best for:** Teams that want comprehensive observability without maintaining their own monitoring stack.
**Real talk:** Datadog gets expensive fast. At $23/host/month for infrastructure monitoring alone, a 25-server setup is $575/month. Model the actual cost before committing.
**Pricing:** Free tier (5 hosts). Pro from $23/host/month.
***
## The Missing Layer: Server Management & AI Automation Tools [#the-missing-layer-server-management--ai-automation-tools]
### Why CI/CD and IaC Don't Cover Your Day-to-Day Server Operations [#why-cicd-and-iac-dont-cover-your-day-to-day-server-operations]
You've set up GitHub Actions. You have Terraform templates. Your deployments are mostly automated.
And yet - you still spend 10 - 15 hours a week on things none of those tools handle:
* Editing an Nginx config that came out wrong after a deploy
* Checking why a server's disk is at 94% on a Friday evening
* Revoking SSH access for the developer who left last week
* Debugging why a service throws 500s twenty minutes *after* a successful deploy
* Transferring a 2GB log file from production to analyze locally
* Running a one-off database query to verify a migration applied correctly
This is the **server operations layer**. The daily, unglamorous work of keeping production running. And there's no well-known tool category that explicitly owns it.
### The Gap Between Your Deployment Pipeline and Production Reality [#the-gap-between-your-deployment-pipeline-and-production-reality]
Your CI/CD pipeline is like a delivery truck. It gets the package to the door. But someone still needs to open it, put things in the right place, verify everything works, and handle anything unexpected.
That someone is you. Every time. With:
* **SSH client** (iTerm2, Termius, PuTTY) - for connecting
* **File manager** (Cyberduck, WinSCP) - for file transfers
* **Monitoring dashboard** (Datadog, Grafana) - for metrics
* **Notes app** (Notion, Obsidian) - for server IPs and docs
* **AI chat** (ChatGPT) - for errors that don't know your server's actual state
Five tools. Three windows open simultaneously. Zero integration between any of them.
**The tool-switching cost:** If context-switching between 5 tools costs 3 minutes per task, and you perform 20 server-related tasks per day, that's 60 minutes of daily friction from switching alone. Across a 5-person team, that's 5 hours per day - invisible, constant, and completely fixable.
#### What Happens After the Deploy: Debugging, File Edits, Health Checks, Backups [#what-happens-after-the-deploy-debugging-file-edits-health-checks-backups]
**Debugging** - CPU spiking. A service won't start. You SSH in, run `top`, scan logs, paste errors into ChatGPT, get generic advice that doesn't account for your stack, try more commands. 30 - 90 minutes later, you find it.
**File edits** - Update an Nginx config, change an environment variable, modify a cron job. One typo can take down a production site. `vim` under pressure at midnight is a skill nobody should need to optimize.
**Health checks** - Is the app responding? Is the database connected? Is disk usage creeping up? Check manually, one server at a time. With 12 client servers, that's 12 SSH sessions before you have a full picture.
**Backups** - You should be running automated backups. But writing backup scripts with retention policies and verification logic is tedious, so it stays in the backlog. Until the day you actually need a restore.
### 14. CtrlOps - AI-Powered Server Management Platform [#14-ctrlops---ai-powered-server-management-platform]
CtrlOps fills this exact gap. It's not a CI/CD tool. It's not IaC. It's a **server management tool for startups and freelancers** - a category that handles what happens between and after deployments, replacing the 4 - 6 tool sprawl with one local-first desktop application. It's the AI DevOps tool built specifically for small teams: no enterprise procurement, no cloud-synced credentials, no six-month onboarding process.
#### SSH Management With Named Server Directory [#ssh-management-with-named-server-directory]
Replace the IP spreadsheet with an organized, named server directory. Connect to "prod-web-1" instead of typing `192.168.1.143` for the fifteenth time this week. Share the directory with your team without emailing credentials.
#### AI Terminal: Plain English to Shell Commands - With Human Approval [#ai-terminal-plain-english-to-shell-commands---with-human-approval]
[Describe what you need in plain English](/features/ai-terminal) - "check which process is using the most memory" or "find all log files larger than 500MB" - and get the correct shell command generated for your specific server's context. Every command requires explicit approval before execution.
This is fundamentally different from pasting an error into ChatGPT. ChatGPT doesn't know your server runs Ubuntu 22.04, uses Node 18, has PM2 managing three processes, and has a disk that's 78% full. CtrlOps does - and generates commands that account for your actual environment.
Where the AI itself runs is the other half of the decision. We compared [Termius AI, Kiro CLI, and CtrlOps](/blog/ai-terminal-tools-server-management) on execution model, approval controls, and how much software each one leaves behind on the server.
**Real example - Docker config debugging:** A misconfigured Docker Compose file was causing intermittent service crashes. Manually tracing the root cause took 2 days of log reading and Stack Overflow rabbit holes. With CtrlOps [AI Terminal](/docs/modules/ai-terminal), the relevant context surfaced in 10 minutes and the correct fix was generated immediately - because the AI had simultaneous visibility into the container configuration, runtime logs, and the host's resource constraints.
#### One-Click Application Deployment [#one-click-application-deployment]
[Deploy Node.js, React, Next.js, and other applications](/docs/modules/deployment) from GitHub in under 5 minutes. CtrlOps handles the git pull, dependency installation, environment variable injection, service restart, and post-deploy health check - no CLI scripting required. Configure once; every subsequent deploy is a single button click.
Compared to doing this manually: 30 - 60 minutes down to under 5. Compared to configuring GitHub Actions for the same workflow: CtrlOps works without touching your repository structure or writing YAML.
#### Infrastructure Monitoring Built In [#infrastructure-monitoring-built-in]
CPU, memory, disk, and network metrics for all your servers in one view - without installing Prometheus and building Grafana dashboards from scratch. Set alert thresholds and get notified before users discover the problem.
**The disk space trap:** Disk filling up is the #1 preventable cause of outages in small teams. It's slow, predictable, and entirely avoidable - but only if you're watching. Most teams find out when the database stops writing, and everything grinds to a halt. Monitoring disk across all servers from one dashboard makes this a 20-minute maintenance task instead of a midnight incident.
#### Backup Automation [#backup-automation]
[Schedule database backups](/docs/modules/backup) with retention policies from the same interface where you manage everything else. No cron job scripting. No "did the backup actually run?" anxiety on Monday morning.
#### 100% Local Security - No Cloud Sync [#100-local-security---no-cloud-sync]
Your SSH keys and server credentials never leave your machine. CtrlOps stores everything in encrypted local storage. No third-party cloud server holds your production credentials.
Cloud-synced SSH clients (Termius's default mode) create a single point of compromise across all your clients' servers. For freelancers managing client infrastructure, having production credentials sync to a third-party cloud service frequently violates client contracts.
#### Pricing [#pricing]
Free trial available. **$7/month** - designed for startup budgets, not enterprise procurement cycles.
CtrlOps **complements** your CI/CD stack - it doesn't replace GitHub Actions or Terraform. It handles everything between "deploy finished" and "everything is confirmed healthy."
**Where CtrlOps doesn't fit (yet):** No tool works everywhere, and being honest about this matters. The platform is built for traditional server infrastructure - VMs, VPS, and dedicated machines. If your stack runs entirely on **serverless** (AWS Lambda, Google Cloud Functions) or you're deep into **container orchestration** (Kubernetes, ECS Fargate), this isn't the right fit - the server operations layer it solves doesn't exist in the same way there. Also worth knowing: real-time metrics show on the dashboard today, but **push-based alerting** (Slack, email notifications) is currently on the roadmap, not yet shipped. For teams that need proactive alerts firing now, pairing with UptimeRobot or a dedicated monitoring tool fills the gap in the meantime. And if you're promising clients a specific uptime target, run it through our [uptime SLA calculator](/tools/uptime-sla-calculator) first - the difference between 99.9% and 99.99% is about 43 minutes of allowed downtime a month.
If you're still using PuTTY, Webmin, or ServerPilot for day-to-day server work, [this comparison of modern alternatives](/blog/putty-webmin-serverpilot-alternatives) lays out exactly what you're leaving on the table.
***
### 15. Portainer - Visual Management for Docker and Kubernetes [#15-portainer---visual-management-for-docker-and-kubernetes]
A web-based GUI for managing Docker containers, images, volumes, and networks - extending to Kubernetes cluster management. If your team runs Docker but finds the CLI a barrier for non-DevOps members, Portainer makes container operations accessible without a terminal.
**Best for:** Teams running Docker or Kubernetes who want a visual interface for day-to-day container operations.
**Pricing:** Free Community Edition. Business Edition from $7/node/month.
***
## What to Automate First: A Prioritized Roadmap [#what-to-automate-first-a-prioritized-roadmap]
Every DevOps automation article lists tools. None of them tell you the order. And almost none of them are written for small teams - the 3-person startup, the solo freelancer, the agency managing 15 client servers without a dedicated DevOps engineer.
Here's the sequence that makes the most sense for AI DevOps tools adoption in small teams managing 5 - 25 servers - based on effort required versus time recovered.
### Phase 1: Server Access and Connection Management (Day 1) [#phase-1-server-access-and-connection-management-day-1]
#### Replace IP Spreadsheets With a Named Server Directory [#replace-ip-spreadsheets-with-a-named-server-directory]
Before automating anything else, organize your servers. Meaningful names. Documented purpose, region, and access notes in one authoritative location. This takes 2 hours and reduces cognitive overhead for every task that follows for years.
#### Centralize SSH Key Storage and Access [#centralize-ssh-key-storage-and-access]
Audit which SSH keys exist on each production server. Remove keys belonging to anyone who has left. Establish a documented, repeatable process for key rotation when the next person departs.
**Quick audit command:** Run `cat ~/.ssh/authorized_keys` on each production server to see every key with current access. Most teams are surprised by what they find - and how many entries they can't attribute to anyone currently on the team.
### Phase 2: Application Deployments (Week 1) [#phase-2-application-deployments-week-1]
#### Automate git pull, Dependency Install, Service Restart, and Verification [#automate-git-pull-dependency-install-service-restart-and-verification]
Before a full CI/CD pipeline, collapse your 10-step manual deployment into a single triggered action. The goal is to eliminate the 7+ failure points, not to build a perfect infrastructure.
#### Set Up One-Click Deployment or Push-Triggered Pipelines [#set-up-one-click-deployment-or-push-triggered-pipelines]
GitHub Actions takes roughly half a day to configure for a basic deploy workflow. CtrlOps one-click deployment is under an hour and requires no YAML. Pick the approach that matches your team's current depth - the right answer is whichever one you actually finish setting up this week.
### Phase 3: Health Checks and Monitoring (Week 2) [#phase-3-health-checks-and-monitoring-week-2]
#### Automated CPU, Memory, Disk, and Process Monitoring [#automated-cpu-memory-disk-and-process-monitoring]
Set up monitoring across all servers with threshold alerts: disk > 85%, CPU sustained above 90%, memory > 95%. These three metrics catch the vast majority of preventable incidents before they become customer-facing outages.
#### Alert on Anomalies Before Users Report Issues [#alert-on-anomalies-before-users-report-issues]
A notification at 8 AM that the disk is at 87% is a 20-minute maintenance task. Finding out at 11 PM when the database has stopped writing is a full incident with customer impact. The only difference is whether you were watching.
### Phase 4: Backup and Maintenance Scripts (Month 1) [#phase-4-backup-and-maintenance-scripts-month-1]
#### Automated Database Backups and Retention Policies [#automated-database-backups-and-retention-policies]
Manual backups don't happen consistently. Automated backups do. Implement [daily database backups with 30-day retention](/features/backup) - and actually verify monthly that your restore process works on real data. A backup that's never been tested is an assumption, not a safety net.
#### Scheduled Maintenance Tasks (Log Rotation, Certificate Renewal) [#scheduled-maintenance-tasks-log-rotation-certificate-renewal]
`certbot renew` in a cron job. Log rotation via `logrotate`. Small tasks that cause large outages when forgotten. Automate them in Month 1 and never think about them again. (Getting the schedule syntax right is its own small hurdle - our free [cron expression generator](/tools/cron-expression-generator) builds and explains the expression for you.)
### Phase 5: AI-Assisted Debugging and Incident Response (Month 2+) [#phase-5-ai-assisted-debugging-and-incident-response-month-2]
#### AI Terminal for Faster Root Cause Analysis [#ai-terminal-for-faster-root-cause-analysis]
With foundational automation in place, AI-assisted debugging becomes a force multiplier. Instead of spending 45 minutes tracing a memory leak through raw logs, describe the symptoms and get guided investigation steps with your server's actual context - not generic Stack Overflow advice.
#### Natural Language Commands for Common Operations [#natural-language-commands-for-common-operations]
"Find all files modified in the last 24 hours in the application directory." Small savings per instance. Meaningful across a week of operations.
**The roadmap isn't strictly linear.** If you're drowning in manual deployments, start with Phase 2. If you just lost data because of a missing backup, start with Phase 4. Fix the biggest current pain first - then work forward.
***
## AI DevOps Tools for Small Teams: What Nobody Tells You [#ai-devops-tools-for-small-teams-what-nobody-tells-you]
### You Don't Need a Full CI/CD Pipeline on Day One [#you-dont-need-a-full-cicd-pipeline-on-day-one]
Most DevOps content is written for teams with a dedicated DevOps engineer, a Kubernetes cluster, and a $2,000/month tooling budget. If that's not you - if you're a founder, a freelancer, or a small team CTO making decisions with real budget constraints - this section is the one that actually applies.
CI/CD pipelines are valuable. They're also complex to configure correctly, require ongoing maintenance, and can become their own operational burden. For a team of 3 - 5 deploying one application twice a week, a reliable one-click deployment is often the right starting point. It ships in a day instead of a week.
Automate the most painful thing first. For most small teams, that's deployment reliability or server access chaos - not pipeline infrastructure.
### Start With Server Management, Not Kubernetes [#start-with-server-management-not-kubernetes]
The number of small teams that adopted Kubernetes because blog posts said they should - and spent months maintaining K8s instead of building a product - is a real pattern.
Kubernetes solves problems you develop at genuine scale. At 5 - 15 servers, the operational overhead almost always exceeds the benefits. Start with Docker Compose. Migrate when you actually outgrow it.
### The Tools That Are Overkill for Teams Under 10 People [#the-tools-that-are-overkill-for-teams-under-10-people]
| Tool | Why It's Overkill | What to Use Instead |
| ---------- | --------------------------------------------------------- | --------------------------------------------------- |
| Kubernetes | Complexity doesn't justify benefit for \<50 containers | Docker Compose or direct deployment |
| Chef | Enterprise-focused, Ruby-based, steep learning curve | Ansible or CtrlOps for server management |
| Datadog | $23+/host/month adds up to thousands annually | Prometheus + Grafana or CtrlOps built-in monitoring |
| Jenkins | You're maintaining a CI server on top of your app servers | GitHub Actions - managed, no infrastructure |
| Terraform | State management overhead for \<10 servers | Direct provisioning or simple scripts to start |
### What a Solo DevOps Freelancer Actually Automates vs What Blog Posts Say You Should [#what-a-solo-devops-freelancer-actually-automates-vs-what-blog-posts-say-you-should]
Blog posts say you should automate: infrastructure provisioning, container orchestration, multi-region failover, compliance scanning, and chaos engineering.
A solo freelancer managing 12 client servers actually automates: **deployments, backups, monitoring, and SSH access.**
Four things. Those four things solve 80% of the operational pain. If you're building your own DevOps tools list, start there - not with the enterprise DevOps automation examples that assume a full-time SRE team.
#### Real DevOps Automation Examples: Managing 12 Client Servers With Consistent Processes [#real-devops-automation-examples-managing-12-client-servers-with-consistent-processes]
A freelance DevOps engineer manages 12 client servers across 9 clients: different stacks (Node.js, Python, PHP), different hosting providers (DigitalOcean, AWS, Hetzner), and different deployment requirements.
**Before automation:**
* Deployments: 30 - 45 minutes per server (up to 9 hours total when updating all clients)
* Server directory: a spreadsheet that was wrong 50% of the time
* Monitoring: zero - issues discovered when clients complained
* Backups: manual when remembered
**After implementing CtrlOps with one-click deployment, centralized monitoring, and automated backups:**
* Deployments: 3 - 5 minutes per server (under 60 minutes total for all 12 when needed)
* Server directory: named, current, shared with clients who need read access
* Monitoring: automated alerts catch issues before clients notice
* Backups: daily, automated, with tested restore procedures
**Total time saved: 5 - 7 hours per week.** For a freelancer billing by the hour, that's direct revenue recovery - not a theoretical benefit.
***
## AI-Powered DevOps Automation: What's New in 2026 [#ai-powered-devops-automation-whats-new-in-2026]
### How AI Is Changing Server Management [#how-ai-is-changing-server-management]
The AI wave hit developer tooling first - code completion, PR reviews, documentation generation. AI-assisted server management with real infrastructure context has been slower to arrive, but the gap is closing fast in 2026.
The core problem with generic AI assistants for server debugging: they give generic answers. "My Node.js service is crashing" into ChatGPT yields generic Node.js debugging advice. The same question asked with your actual server logs, running process list, memory stats, OS version, and deployment history yields targeted, actionable commands in seconds.
#### Natural Language to Infrastructure Commands [#natural-language-to-infrastructure-commands]
The gap between "I know what I want to do" and "I know the exact command to do it" is real and constant. `find / -name "*.log" -mtime +30 -size +100M` is not something most engineers have memorized. Getting that command generated from a plain English description - then approving it before it runs - is the practical value of AI in server operations today.
#### AI-Assisted Debugging With Live Server Context (Not Generic ChatGPT Answers) [#ai-assisted-debugging-with-live-server-context-not-generic-chatgpt-answers]
Debugging with a generic AI assistant has a hard ceiling: it can only see what you paste into the chat box. It doesn't know your Node version, which processes are currently running, what your last deploy changed, or whether disk usage spiked an hour ago. So it offers advice that *might* apply - and you spend the next 20 minutes figuring out whether any of it actually fits your situation.
An AI with live server context skips that translation step. It reads the running process list, recent log entries, active network connections, and scheduled cron jobs in the same query - then correlates those signals into a focused hypothesis instead of a generic checklist. The difference shows up most clearly during real incidents.
**Real example - Crypto miner detection:** Unusual CPU spikes on a client VPS triggered an investigation. Without AI assistance, isolating the cause means manual process inspection, network analysis, and log review - typically 1 - 2 hours of focused work. With CtrlOps AI Terminal that had simultaneous visibility into running processes, network connections, and cron jobs, the cryptominer was identified in under 15 minutes. The AI flagged an unfamiliar process, traced it to a compromised package dependency, and suggested both the immediate remediation and security hardening steps to prevent recurrence.
### The Approve-Before-Execute Model: AI Suggests, Humans Decide [#the-approve-before-execute-model-ai-suggests-humans-decide]
The appropriate model for AI in production server management is not autonomous execution. It's: AI generates the command with explanation, human reviews and approves, then it runs. This preserves AI's speed benefit - the right command in seconds instead of a 5 - 10 minute Google session - while maintaining human control over what actually executes on production systems.
### When to Trust AI Automation vs When to Keep Manual Control [#when-to-trust-ai-automation-vs-when-to-keep-manual-control]
**Safe to fully automate:**
* Monitoring metrics collection and threshold alerting
* Backup scheduling and execution
* SSL certificate renewal
* Log rotation
* Uptime health checks
**Human-gated - automate the process, require human trigger:**
* Production deployments
* Credential rotation and SSH key changes
* Database schema migrations
* Server scaling or termination events
* Any destructive filesystem operations
### AI Tools That Can Automate DevOps Workflows: Current Capabilities and Limitations [#ai-tools-that-can-automate-devops-workflows-current-capabilities-and-limitations]
**What AI does well in DevOps right now:**
* Generating infrastructure commands from natural language descriptions
* Debugging production issues with live server context
* Suggesting configuration changes based on error patterns
* Detecting anomalies in monitoring data before they become incidents
* Scaffolding IaC templates and CI/CD workflow files
**What AI cannot reliably do yet:**
* Make production readiness judgment calls
* Understand business context (is 3 AM on a Saturday a safe deploy window for *this* client?)
* Replace deep system knowledge and operational experience
* Handle novel failure modes it hasn't encountered before
* Make architectural decisions with long-term consequences
***
## Security Considerations for DevOps Automation [#security-considerations-for-devops-automation]
### Where Are Your SSH Keys Stored? (Cloud Sync vs Local-Only) [#where-are-your-ssh-keys-stored-cloud-sync-vs-local-only]
When an SSH client syncs credentials to the cloud by default, your server access keys exist on that vendor's servers. A vendor breach exposes your production credentials. A vendor policy change affects your compliance posture. You no longer fully own the security perimeter around your clients' infrastructure.
Local-only storage means SSH keys live on your machine, encrypted, under your control. The tradeoff is no automatic cross-device sync - but for production server credentials, that tradeoff is almost always the right one.
### SSH Key Sprawl: The Hidden Security Problem After Team Members Leave [#ssh-key-sprawl-the-hidden-security-problem-after-team-members-leave]
The responsible process for any departure:
1. Maintain a registry of which keys have access to which servers
2. Within 24 hours of departure: audit and remove their key from `~/.ssh/authorized_keys` on every server they accessed
3. Rotate any shared keys or passwords they had access to
Without this process documented and repeatable, unauthorized access accumulates with every departure. And without centralized credential management, executing this audit means individual SSH sessions into every server - which is exactly why most teams skip it. The complete process - generation, rotation, audit, and revocation - is covered in our [SSH key management best practices guide](/blog/ssh-key-management-best-practices).
### Why Cloud-Synced Credentials Violate Most Client Contracts [#why-cloud-synced-credentials-violate-most-client-contracts]
If you manage client infrastructure, read your service agreements. Most include language about data residency, third-party access restrictions, and who can hold access credentials. Storing client SSH keys on a third-party cloud service may put you in breach - even if both parties have never thought about it.
Local-only credential storage eliminates this exposure entirely.
### Automating Security Checks Into Your Deployment Pipeline [#automating-security-checks-into-your-deployment-pipeline]
#### Secret Scanning, Vulnerability Detection, Compliance Enforcement [#secret-scanning-vulnerability-detection-compliance-enforcement]
* **Secret scanning** - GitHub's native secret scanning detects accidentally committed API keys and tokens in real time. Free. Takes 10 minutes to enable.
* **Dependency vulnerability scanning** - Snyk or Dependabot scan your dependencies for known CVEs before every deploy.
* **Container image scanning** - Trivy scans container images for vulnerabilities before they reach production.
**One leaked API key in a public commit can compromise your entire infrastructure.** GitHub secret scanning is free and takes 10 minutes to enable. There is no justification for running production repositories without it.
***
## How to Choose the Right DevOps Automation Tools [#how-to-choose-the-right-devops-automation-tools]
### Best AI DevOps Tools for Freelancers (1 - 5 Servers) [#best-ai-devops-tools-for-freelancers-1---5-servers]
#### Focus on: Server Management, One-Click Deploy, AI-Assisted Debugging [#focus-on-server-management-one-click-deploy-ai-assisted-debugging]
| Need | Tool | Why |
| ----------------- | ------------------------- | ---------------------------------------------------------- |
| Server management | CtrlOps | Named servers, file manager, monitoring, backups - one app |
| Deployments | CtrlOps or GitHub Actions | One-click deploy or push-triggered pipeline |
| AI debugging | CtrlOps AI Terminal | Live server context, approve-before-execute |
| Monitoring | CtrlOps built-in | Simple, requires no separate infrastructure |
**Monthly cost:** Under $20 for most solo setups. Skip Terraform, Kubernetes, Jenkins, and Datadog until you genuinely need them.
***
### Best Server Management Tool for Startups (5 - 25 Servers) [#best-server-management-tool-for-startups-5---25-servers]
#### Add: CI/CD Pipeline, Infrastructure Monitoring, Team Access Control [#add-cicd-pipeline-infrastructure-monitoring-team-access-control]
| Need | Tool | Why |
| ----------------- | ---------------------------- | --------------------------------------------------- |
| CI/CD | GitHub Actions or GitLab CI | Managed, no server to maintain |
| Server management | CtrlOps | Team-shared directory with local credential storage |
| Monitoring | CtrlOps + Prometheus/Grafana | More metrics depth as you scale |
| Configuration | Ansible | Simple YAML playbooks for repeatable server setup |
| Containers | Docker + Docker Compose | Consistent environments without K8s complexity |
**Monthly cost:** $100 - $500 depending on server count and monitoring tier.
***
### For Growing Teams (25+ Servers) [#for-growing-teams-25-servers]
#### Add: IaC, Container Orchestration, Multi-Cloud Management [#add-iac-container-orchestration-multi-cloud-management]
| Need | Tool | Why |
| ------------- | --------------------- | ------------------------------------------------------------ |
| IaC | Terraform | Multi-cloud provisioning now justifies the complexity |
| Orchestration | Kubernetes | Auto-scaling and self-healing worth the operational overhead |
| CI/CD | GitLab CI or CircleCI | More pipeline control and customization |
| Monitoring | Datadog | Full observability without self-hosting burden |
| GitOps | ArgoCD | Automated K8s deployments from Git |
| Server ops | CtrlOps | Still handles the operations layer CI/CD doesn't cover |
**Monthly cost:** $500 - $3,000+ depending on scale and provider.
***
### Integration Check: Do Your Tools Talk to Each Other? [#integration-check-do-your-tools-talk-to-each-other]
Before committing to any tool, verify three things:
1. Does it connect natively to what you already use - GitHub, your cloud provider, Slack?
2. Can it be triggered from your existing workflows without custom glue code?
3. Will it create a new information silo that nobody checks regularly?
Tools that don't integrate create the same friction as tools you never adopted. The best stack flows end to end - not the one that looks best in a comparison table.
***
## Conclusion: Start With the Biggest Pain, Not the Most Impressive Tool [#conclusion-start-with-the-biggest-pain-not-the-most-impressive-tool]
The DevOps automation journey doesn't start with Kubernetes. It starts with the problem costing you the most time and stress right now.
For most teams managing 5 - 25 servers, that's one of three things:
1. Manual deployments that take 30 minutes and occasionally break production at midnight
2. Server access chaos - the spreadsheet, the SSH into staging instead of prod, the departed engineer who still has root access
3. Finding out about server problems from clients instead of your own monitoring
Fix the biggest pain first. The tools exist, work well, and for most use cases cost less than $40/month combined.
If you already have CI/CD running and your infrastructure is in code, but still spend hours weekly on SSH chaos and post-deploy debugging - that's the server operations layer. Fourteen of the fifteen tools on this list don't cover it. The fifteenth one does.
**The practical starting point for most small teams:** Get server access organized (Day 1). Automate your most common deployment (Week 1). Set up disk and memory alerts (Week 2). Schedule database backups (Month 1). That four-step sequence solves 80% of the operational pain that most small teams quietly accept as normal - and perpetually live with.
The best DevOps automation stack isn't the theoretically correct one that's been sitting in a backlog ticket for three months. It's the one actually running today.
Pick one thing. Finish it. Then pick the next.
***
## FAQs [#faqs]
DevOps automation tools are software that replaces manual, repetitive tasks across software delivery and infrastructure management. They cover CI/CD pipelines (automated build, test, deploy), infrastructure as code (programmatic server provisioning), container orchestration (running and scaling containerized apps), monitoring (automated health checks and alerting), and server operations (SSH management, file transfers, deployment automation, and day-to-day maintenance).
Most guides cover the first three layers. The server operations layer - where small teams spend 40 - 60% of their actual time - is the one everyone skips. That's the gap this guide addresses.
For teams managing 2 - 15 servers, a practical starting stack:
| Tool | Monthly Cost | What It Covers |
| -------------------- | ---------------- | -------------------------------------------------------- |
| CtrlOps | $7 | Server management, one-click deploy, monitoring, backups |
| GitHub Actions | $0 (free tier) | CI/CD pipelines |
| Docker | $0 | Consistent application environments |
| Ansible | $0 | Server configuration when needed |
| Prometheus + Grafana | $0 (self-hosted) | Additional monitoring (or use CtrlOps built-in) |
| **Total** | **\~$7/month** | Complete small-team automation stack |
Skip Kubernetes, Chef, Jenkins, and Datadog until you genuinely outgrow the above.
Yes - and the category matured significantly in 2025 - 2026. AI DevOps tools fall into a few areas:
* **AI server terminals** (CtrlOps AI Terminal) - generate shell commands from plain English with live server context, require human approval before execution
* **AI code assistants** (GitHub Copilot, Cursor) - help write deployment scripts and IaC templates
* **AI in CI/CD** (GitHub Copilot for Actions) - suggest pipeline configurations and diagnose build failures
* **AI observability** (Datadog AI) - anomaly detection and alert noise reduction
The most practical capability for small teams: an AI terminal that knows your specific server's state and generates the correct command for your actual environment - not generic advice that might apply to someone else's server.
In priority order:
1. **Day 1** - Server access management (named directory, centralized SSH keys)
2. **Week 1** - Application deployments (one-click or push-triggered, verified under 5 minutes)
3. **Week 2** - Infrastructure monitoring (CPU, disk, memory alerts across all servers)
4. **Month 1** - Backup automation (daily database backups with tested restore process)
5. **Month 1** - Security gates (secret scanning in CI, automated SSL renewal)
6. **Month 2+** - AI-assisted operations (AI terminal for debugging and routine commands)
If your biggest risk today is data loss, start with Month 1. If you're losing 6 hours per week to manual deployments, start with Week 1. Fix the biggest current pain first.
CI/CD tools (Jenkins, GitHub Actions, CircleCI) automate one specific layer: the build-test-deploy pipeline. They handle the journey from `git push` to running code in production.
DevOps automation tools is the broader category encompassing CI/CD plus infrastructure as code, container orchestration, monitoring, server operations, security scanning, and backup automation. CI/CD delivers your code. DevOps automation provisions, deploys, monitors, secures, and maintains everything that code runs on.
A complete automation stack for a 5 - 10 person startup managing 10 - 15 servers:
| Tool | Monthly Cost | Purpose |
| -------------------- | -------------------- | -------------------------------------------------- |
| CtrlOps | $7 | Server management, deployment, monitoring, backups |
| GitHub Actions | $0 - $30 | CI/CD (free tier covers most small teams) |
| Docker | $0 | Container runtime |
| Ansible | $0 | Configuration management |
| Prometheus + Grafana | $0 (self-hosted) | Monitoring (or use CtrlOps built-in) |
| **Total** | **\~$7 - $37/month** | Full automation coverage |
Compare to enterprise stacks running $500 - $2,000/month. Small teams can achieve complete automation coverage for less than most SaaS tool subscriptions - and the time ROI is measured in days, not quarters.
The best AI DevOps tools for small teams are the ones that eliminate manual work without requiring a dedicated DevOps engineer to set them up and maintain them.
For most teams managing under 25 servers, the practical AI DevOps stack looks like this:
| Tool | What It Solves |
| -------------- | ------------------------------------------------------------------------------------------ |
| CtrlOps | AI terminal with live server context, one-click deployments, monitoring, backup automation |
| GitHub Actions | Push-triggered CI/CD pipelines with no server to maintain |
| Docker | Consistent environments across dev and production |
What makes CtrlOps specifically an AI DevOps tool for small teams: the AI Terminal generates shell commands with awareness of your actual server state - OS version, running processes, disk usage, recent logs. Not generic advice from an AI that's never seen your infrastructure.
The 2026 answer is no longer "you need a DevOps engineer." It's "you need the right tool stack." For most small teams, that's under $40/month total.
Partially. CI/CD pipelines require the internet (they're web-based services). Infrastructure provisioning requires the internet to call the cloud provider APIs.
For CtrlOps specifically: accessing the app and your server dashboard requires internet. Your SSH keys and server credentials are stored locally in encrypted storage - they're not cloud-synced - but active management sessions still need network access to reach the servers themselves (via internet, LAN, or VPN). This is an important distinction: **local credential storage ≠ offline operation**. The benefit of local storage is security and privacy, not offline capability.
Database automation in DevOps covers three distinct areas:
**Schema migration automation:** Flyway and Liquibase manage database schema changes as versioned migration files applied automatically during deployments. No more "don't forget to run the migration" in the deploy runbook.
**Backup automation:** Scheduled database dumps with retention policies and verified restore processes. CtrlOps handles backup scheduling directly from its interface. pgBackRest and Barman provide dedicated PostgreSQL backup management for larger setups.
**Database provisioning:** Terraform provisions managed database instances (RDS, Cloud SQL, Supabase) as part of IaC workflows. Ansible playbooks handle installation and configuration for self-hosted databases.
The most neglected piece across all three: **automated restore testing**. A backup that's never been tested is an assumption, not a safety net. Schedule a monthly restore test to staging and verify your backups actually work before you need them at 2 AM.
---
# 13 Linux Server Management Best Practices (2026) (/blog/linux-server-management-best-practices)
Author: Daxesh Italiya | Role: CTO | Published: 2026-08-04 | Tags: linux server management, linux server security, ssh hardening, sysadmin best practices, devops | Reading Time: 25 min read
> 13 Linux server management best practices for 2026 - SSH hardening, firewall setup, monitoring, backups, and systemd, with real commands for Ubuntu and RHEL.
The 13 most important Linux server management best practices in 2026 are: creating individual user accounts with least-privilege sudo access, setting correct file permissions (never `chmod 777`), disabling root SSH login and switching to key-based authentication, configuring firewalls with deny-by-default rules, automating security updates, managing services with systemd, centralizing monitoring and alerting, testing backup restores monthly, automating repetitive tasks with cron or systemd timers, managing disk and storage proactively, knowing core networking diagnostics, tuning performance baselines, and following a structured troubleshooting checklist.
These practices apply to any Linux distribution - Ubuntu, Debian, RHEL, CentOS, or Fedora - and cover the full lifecycle from initial setup to ongoing maintenance.
## Overview of Best Practices of Linux Server Management [#overview-of-best-practices-of-linux-server-management]
Before deep-diving into each recommendation, here is a high-level summary of the essential rules for modern sysadmins. The table below lists each practice in order of priority, along with the key commands and the consequences of neglecting them.
| Practice | Priority | Key Command/Action | What Goes Wrong Without It |
| -------------------------- | ---------- | ---------------------------------------------- | ------------------------------------------------------- |
| Individual user accounts | Day 1 | `useradd -m -s /bin/bash` | Lost audit trail, shared root passwords |
| File permissions | Day 1 | `chmod 644` / `chmod 755` | Malicious script uploads via `777` |
| SSH hardening | Day 1 | `PermitRootLogin no` + key auth | Brute-force compromise through port 22 |
| Firewall (deny-by-default) | Day 1 | `ufw default deny incoming` | Every open port is an attack surface |
| Automated updates | Week 1 | `unattended-upgrades` | Known CVEs exploited months after patches |
| systemd management | Week 1 | `systemctl status/restart` | Stale services, missed boot starts |
| Monitoring and logging | Week 1 | `journalctl` + alerting stack | Disk fills to 100%, users find the problem first |
| **Tested backups** | **Week 1** | **rsync/restic + monthly restore test** | **Corrupted backup discovered during an actual outage** |
| Cron / systemd timers | Month 1 | `crontab -e` or `.timer` units | Manual tasks skipped, log rotation forgotten |
| Disk management | Ongoing | `df -h` + `du -sh` + logrotate | Services crash from full disk at midnight |
| Network diagnostics | As needed | `ip addr`, `ss -tulnp`, `dig` | Chasing the wrong problem for hours |
| Performance tuning | As needed | `vm.swappiness`, file limits | Unnecessary swapping, connection drops |
| Troubleshooting checklist | As needed | Logs > resources > service > network > changes | Random fixes that create new problems |
***
## The 13 Linux Server Management Best Practices [#the-13-linux-server-management-best-practices]
Let's explore all 13 Linux server management best practices one by one.
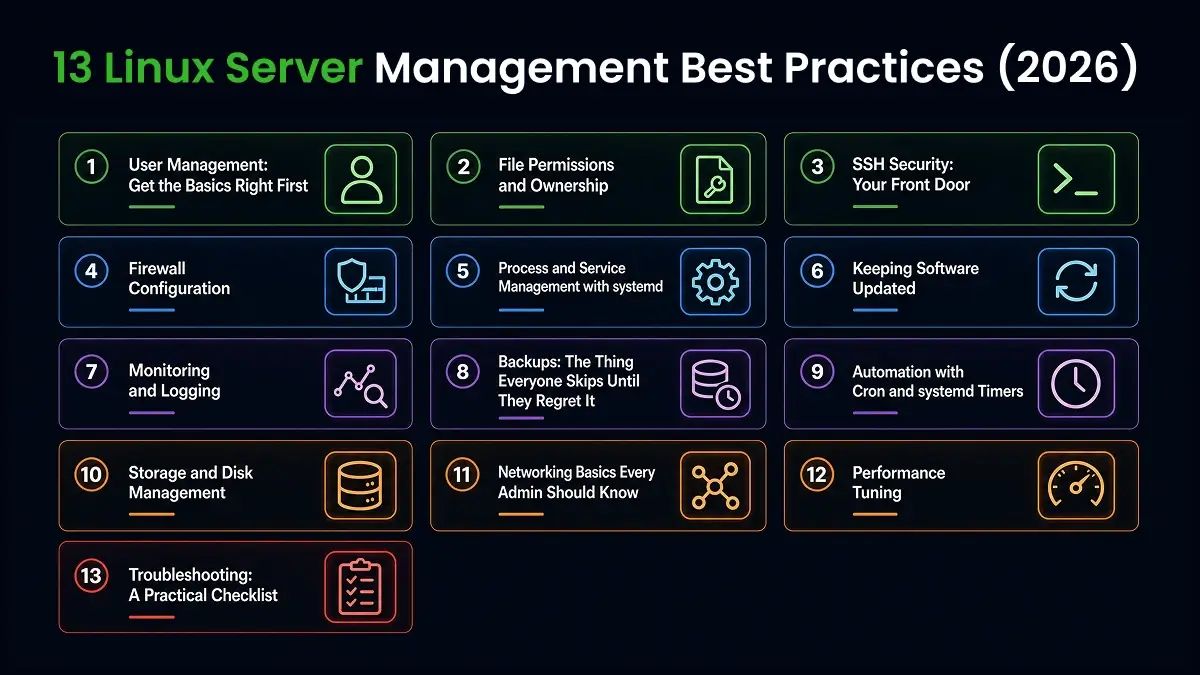
### 1. User Management: Get the Basics Right First [#1-user-management-get-the-basics-right-first]
Before you even think about hardening SSH or configuring a firewall, get your user accounts in order.
A huge chunk of server compromises happen not because of some exotic zero-day, but because of sloppy account hygiene - shared root passwords, ex-employees who still have access, or a service account with way more privilege than it needs.
#### Create individual accounts, not shared logins [#create-individual-accounts-not-shared-logins]
Every person (and every application, where practical) should have their own account. Shared logins destroy your audit trail - if three people share one account and something breaks, you have no idea who did it.
```bash
# Create a new user with a home directory
sudo useradd -m -s /bin/bash username
# Set a password for them
sudo passwd username
```
`-m` creates the home directory, `-s /bin/bash` sets their default shell. If you skip `-m`, the user won't get a home directory, which trips people up more often than you'd expect.
#### Grant sudo instead of handing out root [#grant-sudo-instead-of-handing-out-root]
Add trusted users to the sudo (Debian/Ubuntu) or wheel (RHEL/CentOS/Fedora) group instead of giving them the root password.
```bash
sudo usermod -aG sudo username # Debian/Ubuntu
sudo usermod -aG wheel username # RHEL/CentOS
```
For finer control, edit sudoers with `visudo` (never edit `/etc/sudoers` directly - a syntax error there can lock everyone out):
```bash
sudo visudo
```
You can restrict a user to specific commands only:
```
username ALL=(ALL) NOPASSWD: /usr/bin/systemctl restart nginx
```
This lets username restart nginx without a password, but nothing else. This is the kind of least-privilege thinking that should run through everything you do as an admin - give people exactly what they need, no more.
#### Clean up after people leave [#clean-up-after-people-leave]
This one's overlooked constantly. When someone leaves the team, lock or delete their account the same day.
To temporarily or permanently lock access without deleting their data:
```bash
sudo usermod -L username # Disables password login
sudo usermod -s /usr/sbin/nologin username # Disables SSH shell access
sudo mv /home/username/.ssh/authorized_keys /home/username/.ssh/authorized_keys.bak # Disables active SSH keys
```
To delete the user and their home directory (and thus all SSH keys) entirely:
```bash
sudo userdel -r username
```
Before deleting, check for cron jobs or running processes tied to that user (`crontab -u username -l`, `ps -u username`), so you don't accidentally kill something important.
**Bottom line:** For teams managing multiple servers, keeping track of who has access to what becomes exponentially harder as you add servers. A centralized server directory with [access management](/docs/modules/access-management) replaces the manual `authorized_keys` audit on every individual machine.
***
### 2. File Permissions and Ownership [#2-file-permissions-and-ownership]
Linux permissions trip up beginners constantly, but they're really not that complicated once they click.
#### The permission model [#the-permission-model]
Every file has three permission sets: owner, group, and others. Each set can have read (r), write (w), and execute (x).
```bash
ls -l /var/www/html/index.html
```
```
-rw-r--r-- 1 www-data www-data 1024 Jul 10 09:15 index.html
```
Reading left to right: it's a regular file (`-`), the owner can read/write, the group can read, and everyone else can read.
#### Changing ownership and permissions [#changing-ownership-and-permissions]
```bash
sudo chown www-data:www-data /var/www/html/index.html # change owner:group
sudo chmod 644 /var/www/html/index.html # rw- r-- r--
sudo chmod 755 /usr/local/bin/deploy.sh # rwx r-x r-x (executable script)
```
A quick way to think about numeric permissions: 4 = read, 2 = write, 1 = execute. Add them up per group. 644 means owner gets 6 (4+2 = read+write), group and others get 4 (read only).
#### Avoid the temptation of chmod 777 [#avoid-the-temptation-of-chmod-777]
If you've ever hit a permission error and just thrown `chmod -R 777` at the problem to make it go away - you're not alone, but stop doing that. 777 means anyone on the system can read, write, and execute the file.
On a web server, that's practically an invitation for someone to upload a malicious script. Figure out the actual owner/group mismatch instead.
#### Special permissions worth knowing [#special-permissions-worth-knowing]
**SUID** (`chmod u+s`): runs a file with the owner's privileges rather than the caller's. `passwd` uses this so regular users can update their password, which touches root-owned files.
**SGID** (`chmod g+s`): on directories, new files inherit the directory's group - handy for shared team folders.
**Sticky bit** (`chmod +t`): on directories like `/tmp`, it means only the file's owner can delete it, even if others have write access to the directory.
```bash
chmod +t /shared/uploads
```
***
### 3. SSH Security: Your Front Door [#3-ssh-security-your-front-door]
SSH is how you access almost everything on a remote Linux server, which makes it the single most important thing to lock down. Most automated attacks against Linux servers are just bots hammering port 22 with common username/password combinations.
#### Disable root login over SSH [#disable-root-login-over-ssh]
Nobody should be able to SSH in directly as root. Force people to log in as themselves and use sudo.
Edit `/etc/ssh/sshd_config`:
```
PermitRootLogin no
```
#### Switch to SSH key authentication [#switch-to-ssh-key-authentication]
Passwords can be guessed or brute-forced. Key pairs are far harder to crack - a typical RSA or ed25519 key is effectively unguessable.
Generate a key pair on your local machine:
```bash
ssh-keygen -t ed25519 -C "username@work-laptop"
```
Copy it to the server:
```bash
ssh-copy-id username@your-server-ip
```
Then disable password authentication entirely on the server side, in `/etc/ssh/sshd_config`:
```
PasswordAuthentication no
PubkeyAuthentication yes
```
Don't restart SSH yet - apply the remaining hardening steps below first, then restart once at the end.
#### Other SSH hardening steps [#other-ssh-hardening-steps]
Limit who can connect:
```
AllowUsers username
```
Use fail2ban to automatically ban IPs after repeated failed login attempts:
```bash
# Debian/Ubuntu
sudo apt install fail2ban -y
# RHEL/CentOS/Fedora (needs EPEL first)
sudo dnf install epel-release -y
sudo dnf install fail2ban -y
sudo systemctl enable --now fail2ban
```
Installing it is not the same as it working. A running Fail2Ban with an empty jail list reports itself healthy and blocks nothing, which is one of the cases the [logging and monitoring audit checklist](/security-checklist/vps/logging-monitoring) checks for, alongside log rotation health and the failed-login count that tells you whether the bans are keeping up.
Set idle timeouts so forgotten sessions don't stay open forever:
```
ClientAliveInterval 300
ClientAliveCountMax 2
```
Now restart SSH to apply all the changes above:
```bash
sudo systemctl restart sshd
```
**Reality check:** Test your key-based login in a second terminal window before closing your current session. If something's misconfigured and you lock yourself out, you'll be glad you kept the original session open.
**Optional:**
Change the default SSH port. Some admins move SSH off port 22 to reduce automated scan noise (bots hammering 22 with credential-stuffing attempts).
This is "security through obscurity"; it doesn't stop a targeted attacker, only cuts down junk traffic, and it adds setup steps: on RHEL/CentOS/Fedora with SELinux enforcing, you'll need `sudo semanage port -a -t ssh_port_t -p tcp `, your firewall rules need updating, and fail2ban needs its jail's port value changed to match.
Skip this unless you specifically want the reduced noise; the practices above (key-only auth, fail2ban, deny-by-default firewall) already cover the real security.
For a deeper walkthrough of key generation, rotation, and revocation across a multi-server fleet, read our [SSH key management best practices](/blog/ssh-key-management-best-practices), or compare the [best SSH clients for Mac](/blog/best-ssh-client-mac-2026) and the [best SSH clients for Linux](/blog/best-ssh-client-linux) to see how they handle key management.
***
### 4. Firewall Configuration [#4-firewall-configuration]
A firewall is your gatekeeper - it decides what traffic is even allowed to reach your server in the first place.
#### UFW (Uncomplicated Firewall) - Debian/Ubuntu [#ufw-uncomplicated-firewall---debianubuntu]
```bash
sudo ufw allow 22/tcp # allow your custom SSH port
sudo ufw allow 80/tcp # HTTP
sudo ufw allow 443/tcp # HTTPS
sudo ufw enable
sudo ufw status verbose
```
Example output:
```
Status: active
To Action From
-- ------ ----
22/tcp ALLOW Anywhere
80/tcp ALLOW Anywhere
443/tcp ALLOW Anywhere
```
#### firewalld - RHEL/CentOS/Fedora [#firewalld---rhelcentosfedora]
```bash
sudo firewall-cmd --permanent --add-service=ssh
sudo firewall-cmd --permanent --add-service=http
sudo firewall-cmd --permanent --add-service=https
sudo firewall-cmd --reload
sudo firewall-cmd --list-all
```
If you changed SSH to a custom port, replace `--add-service=ssh` with `--add-port=/tcp`; the ssh service definition only opens port 22.
#### The golden rule: deny by default [#the-golden-rule-deny-by-default]
Only open ports you actually need. If you're not running a mail server, there's no reason port 25 should be open. Every open port is one more thing an attacker can probe.
Getting the rules right on day one is the easy half. The [network security audit checklist](/security-checklist/vps/firewall-network) covers what to re-check later, including the one gap these commands cannot close: a Docker container publishing on `0.0.0.0` reaches the internet regardless of what `ufw status` says.
```bash
sudo ufw default deny incoming
sudo ufw default allow outgoing
```
**Bottom line:** A properly configured firewall combined with SSH key auth eliminates the overwhelming majority of automated attack attempts. Together, these two practices are the highest-ROI security steps for any Linux server.
***
### 5. Keeping Software Updated [#5-keeping-software-updated]
Unpatched software is one of the most common ways servers get compromised - often through vulnerabilities that were publicly disclosed and patched months earlier.
#### Debian/Ubuntu [#debianubuntu]
```bash
sudo apt update # refresh package index
sudo apt upgrade -y # install available updates
sudo apt autoremove -y # clean up unused dependencies
```
#### RHEL/CentOS/Fedora [#rhelcentosfedora]
```bash
sudo dnf check-update
sudo dnf upgrade -y
```
#### Automate security updates [#automate-security-updates]
You shouldn't need to remember to patch every server manually. On Ubuntu, `unattended-upgrades` handles this for you:
```bash
sudo apt install unattended-upgrades
sudo dpkg-reconfigure --priority=low unattended-upgrades
```
On RHEL-based systems, `dnf-automatic` does the same job:
```bash
sudo dnf install dnf-automatic
sudo systemctl enable --now dnf-automatic.timer
```
For production systems, consider applying security patches automatically but holding off on full version upgrades until you've tested them in staging. A patched CVE protects you immediately. A kernel upgrade that breaks your application creates a new incident.
Installing the tool is not the same as it running. The [system updates audit checklist](/security-checklist/vps/system-updates) covers what to verify afterwards: whether the periodic run is actually switched on, whether `dnf-automatic` is set to install rather than just notify, and whether the kernel you patched has been rebooted into yet.
#### Reduce your attack surface [#reduce-your-attack-surface]
Uninstall anything you're not using. That old FTP server nobody remembers installing three years ago is still a door into your system.
```bash
# List installed packages
dpkg -l # Debian/Ubuntu
rpm -qa # RHEL/CentOS
# Remove something you don't need
sudo apt purge telnet
```
Also check which services are actually listening:
```bash
sudo ss -tulnp
```
This shows every listening port and the process behind it - a good way to spot something that shouldn't be running.
***
### 6. Process and Service Management with systemd [#6-process-and-service-management-with-systemd]
Almost all modern distributions use systemd to manage services. Getting comfortable with `systemctl` and `journalctl` will save you a lot of guesswork.
```bash
sudo systemctl status nginx # check if a service is running
sudo systemctl start nginx
sudo systemctl stop nginx
sudo systemctl restart nginx
sudo systemctl enable nginx # start automatically on boot
sudo systemctl disable nginx
```
Example status output:
```
● nginx.service - A high performance web server
Loaded: loaded (/lib/systemd/system/nginx.service; enabled)
Active: active (running) since Thu 2026-07-30 08:12:03 UTC; 2h ago
```
#### Checking processes and resource hogs [#checking-processes-and-resource-hogs]
```bash
top # live view of CPU/memory usage
htop # nicer, interactive version (install separately)
ps aux | grep nginx # find a specific process
```
If a process is misbehaving and won't respond to a normal stop:
```bash
sudo kill -15 # graceful shutdown request
sudo kill -9 # force kill, last resort
```
Always try `-15` (SIGTERM) before `-9` (SIGKILL) - it gives the process a chance to close files and clean up properly instead of dying mid-write.
***
### 7. Monitoring and Logging [#7-monitoring-and-logging]
You can't fix what you don't know is broken. Monitoring isn't optional - it's how you catch problems before your users do.
#### Watching resource usage [#watching-resource-usage]
```bash
df -h # disk space by filesystem
du -sh /var/log # size of a specific directory
free -h # memory usage
uptime # load average over 1, 5, 15 minutes
```
Example `df -h` output:
```
Filesystem Size Used Avail Use% Mounted on
/dev/sda1 50G 38G 10G 80% /
```
At 80% usage, it's time to start paying attention. Waiting until you hit 100% means services start crashing.
#### Centralize and review your logs [#centralize-and-review-your-logs]
Most system logs live in `/var/log`, and `journalctl` gives you a unified view for systemd-managed services:
```bash
sudo journalctl -u sshd --since "1 hour ago"
sudo tail -f /var/log/auth.log # watch authentication attempts live
```
Watching `auth.log` (Debian/Ubuntu) or `/var/log/secure` (RHEL) for repeated failed login attempts is one of the simplest ways to catch a brute-force attempt in progress.
#### Set up real alerting [#set-up-real-alerting]
Manually checking logs doesn't scale. For anything beyond a couple of servers, use a monitoring stack - something like Prometheus + Grafana, Netdata, or Zabbix - so you get alerted the moment CPU spikes, disk fills up, or a service goes down, instead of finding out from an angry customer.
Set alert thresholds before the problem becomes critical. An alert at 90% disk usage is useful. An alert at 100% is just a postmortem.
**Reality check:** Most small teams skip monitoring because setting up Prometheus + Grafana feels like a project in itself. The result is finding out about disk at 100% from a customer ticket, not from your own systems. If you're [managing multiple servers](/blog/manage-multiple-servers-without-losing-control), a built-in monitoring dashboard eliminates the setup overhead entirely.
***
### 8. Backups: The Thing Everyone Skips Until They Regret It [#8-backups-the-thing-everyone-skips-until-they-regret-it]
If there's one practice that separates a professional setup from an amateur one, it's backups that are actually tested. A backup you've never tried restoring is a backup you don't actually have.
The other failure mode is a backup that depends on someone remembering to run it. At Olbuz, a developer had to be pinged every time one was due, until [scheduling took the person out of the loop entirely](/case-studies/olbuz).
#### The 3-2-1 rule [#the-3-2-1-rule]
Keep 3 copies of your data, on 2 different types of storage, with 1 copy off-site. This protects you against hardware failure, ransomware, and simple human error (like an accidental `rm -rf`).
#### The difference between syncing and backing up [#the-difference-between-syncing-and-backing-up]
A common mistake is using a simple mirror as a backup. For example:
```bash
# WARNING: This is a mirror, not a true backup!
rsync -avz --delete /var/www/ backup-server:/backups/www/
```
`-a` preserves permissions and timestamps, `-v` is verbose, `-z` compresses during transfer, and `--delete` removes files on the destination that no longer exist on the source.
While this mirrors the live data, **it does not protect against ransomware or accidental deletion (`rm -rf`)**. If your files are encrypted by ransomware or deleted, the next run of this command will faithfully delete or overwrite the healthy backups on the destination.
#### Implementing versioned backups [#implementing-versioned-backups]
To be truly protected, your backups must be versioned (containing point-in-time snapshots). Here are two ways to achieve this:
##### Option A: Versioned rsync with `--backup-dir` [#option-a-versioned-rsync-with---backup-dir]
You can tell `rsync` to move deleted or modified files into a dated directory instead of deleting them:
```bash
# Get the current date
CURRENT_DATE=$(date +%Y-%m-%d_%H-%M-%S)
# Sync to the main folder, moving any changed/deleted files to a dated archive
rsync -avz --delete --backup --backup-dir=/backups/archive/$CURRENT_DATE /var/www/ backup-server:/backups/current/
```
This ensures you can always recover older versions of modified or deleted files from the dated archive directories.
##### Option B: Dedicated backup tools (Restic/Borg) [#option-b-dedicated-backup-tools-resticborg]
For production environments, use dedicated backup tools that support deduplication, encryption, and native snapshotting. For example, using **Restic**:
```bash
# Initialize a restic repository
restic init --repo /srv/restic-repo
# Create a snapshot backup
restic -r /srv/restic-repo backup /var/www
# List snapshots (points in time you can restore)
restic -r /srv/restic-repo snapshots
```
#### Database backups [#database-backups]
```bash
mysqldump -u root -p mydatabase > mydatabase_backup.sql
pg_dump mydatabase > mydatabase_backup.sql # for PostgreSQL
```
#### Automate it and actually test restores [#automate-it-and-actually-test-restores]
Schedule backups with cron (more on that below), but the part people skip is verifying the backup actually works. Once a month, pull a backup and restore it somewhere isolated. It's uncomfortable to spend time on something that "should just work," but discovering a corrupted backup during an actual outage is far worse.
**Bottom line:** Writing backup scripts with retention policies and verification logic is tedious, which is exactly why it stays in the backlog until data is lost. Tools that handle [automated backup scheduling](/docs/modules/backup) with configurable retention remove the friction that keeps teams from doing this on Day 1.
***
### 9. Automation with Cron and systemd Timers [#9-automation-with-cron-and-systemd-timers]
Manual, repetitive tasks are where mistakes creep in. Automate anything you do more than a couple of times.
#### Cron [#cron]
```bash
crontab -e
```
Example: run a backup script every night at 2 AM:
```
0 2 * * * /usr/local/bin/backup.sh >> /var/log/backup.log 2>&1
```
The five fields are minute, hour, day-of-month, month, and day-of-week. `2>&1` redirects errors into the same log file, which is easy to forget and annoying to debug later if you do.
#### systemd timers (the modern alternative) [#systemd-timers-the-modern-alternative]
Timers give you better logging (via `journalctl`) and dependency handling than cron. A simple timer setup involves two files:
`/etc/systemd/system/backup.service`:
```ini
[Unit]
Description=Run backup script
[Service]
ExecStart=/usr/local/bin/backup.sh
```
`/etc/systemd/system/backup.timer`:
```ini
[Unit]
Description=Run backup daily at 2AM
[Timer]
OnCalendar=*-*-* 02:00:00
Persistent=true
[Install]
WantedBy=timers.target
```
Enable it:
```bash
sudo systemctl enable --now backup.timer
sudo systemctl list-timers # see all scheduled timers
```
`Persistent=true` is a nice touch - it makes sure a missed run (say, the server was down at 2 AM) gets triggered as soon as the system comes back up.
***
### 10. Storage and Disk Management [#10-storage-and-disk-management]
#### Checking and managing disk usage [#checking-and-managing-disk-usage]
```bash
lsblk # list block devices
df -h # filesystem-level usage
du -sh /* 2>/dev/null | sort -rh | head -10 # find your biggest directories
```
That last command is one of the most useful one-liners in a sysadmin's toolkit - it'll quickly tell you what's eating your disk space.
#### Logical Volume Management (LVM) [#logical-volume-management-lvm]
If your server uses LVM, you can resize partitions without downtime - a big advantage over fixed partitions.
```bash
sudo lvextend -L +10G /dev/mapper/vg-root
sudo resize2fs /dev/mapper/vg-root # for ext4
sudo xfs_growfs / # for XFS
```
#### Clean up log bloat [#clean-up-log-bloat]
Logs are a common, quiet source of disk exhaustion. `logrotate` handles this automatically on most distributions, but it's worth checking your configuration in `/etc/logrotate.d/` to make sure old logs actually get compressed or deleted rather than piling up indefinitely.
***
### 11. Networking Basics Every Admin Should Know [#11-networking-basics-every-admin-should-know]
```bash
ip addr show # view network interfaces and IPs
ip route show # view routing table
ping -c 4 google.com # test connectivity
traceroute google.com # trace the path packets take
ss -tulnp # view listening ports and associated processes
dig example.com # DNS lookup
```
When something "isn't working," these commands are usually your first stop: is the server even reachable, is the right port open, is DNS resolving correctly. Working through them in order saves you from chasing the wrong problem.
***
### 12. Performance Tuning [#12-performance-tuning]
Once the basics are solid, you can start squeezing more reliability and speed out of your servers.
Check load average with `uptime` - a load average consistently higher than your CPU core count means the system is overloaded.
Tune swappiness if your server is swapping too aggressively:
```bash
sudo sysctl vm.swappiness=10
```
This change is temporary and resets on reboot. To make it permanent, add `vm.swappiness=10` to `/etc/sysctl.conf` (or a new file in `/etc/sysctl.d/`).
Lower values make the kernel prefer RAM over swap, which usually improves performance on servers with enough memory.
Adjust open file limits for high-traffic services (databases, web servers) in `/etc/security/limits.conf`, since the default limits are often too low for production workloads.
Use `iostat` and `vmstat` to spot disk I/O or memory bottlenecks:
```bash
iostat -x 1
vmstat 1
```
***
### 13. Troubleshooting: A Practical Checklist [#13-troubleshooting-a-practical-checklist]
When something breaks, resist the urge to randomly try fixes. Work through it methodically:
1. **Check the logs first:** `journalctl -xe` or the relevant file in `/var/log/` usually tells you exactly what happened.
2. **Check resource usage:** Is the disk full? Is memory exhausted? `df -h` and `free -h` take five seconds to run.
3. **Check the service status:** `systemctl status ` tells you if it's even running, and often shows the last error.
4. **Check connectivity:** If it's a network issue, work outward: local process, then firewall, then DNS, then external reachability.
5. **Check recent changes:** Did a package update, config change, or deployment happen recently? Grep your shell history or deployment logs.
Keep a simple runbook (even a plain text file) documenting fixes for problems you've solved before. Future-you, debugging the same issue at 1 AM six months from now, will thank present-you.
**Bottom line:** An [AI terminal with live server context](/docs/modules/ai-terminal) can compress this entire checklist into a single question: "Why is my server slow?" It runs the diagnostic commands, reads the output, and surfaces the root cause - with every command shown for your approval before execution.
***
## Why Do Linux Server Management Best Practices Matter? [#why-do-linux-server-management-best-practices-matter]
If you have ever suddenly woken up at 3 AM because a server ran out of disk space, or spent a stressful afternoon explaining to your boss why a production box got compromised through an open SSH port, you already know that managing Linux servers is equal parts discipline and muscle memory.
It's not glamorous work. Nobody writes movies about the sysadmin who quietly kept 200 servers patched and backed up for five years straight. But that quiet reliability is exactly the goal.
This guide covered the practices that separate a server that "just works" from one that becomes a liability: security, updates, monitoring, backups, and a lot of the day-to-day plumbing - user accounts, permissions, firewalls, cron jobs, systemd, and troubleshooting with real commands you can run today.
Whether you are a freelance developer managing client VPS instances, a startup CTO keeping production reliable as the fleet grows, or a sysadmin responsible for hundreds of machines, these 13 Linux server management best practices apply to your stack right now. Every command in this guide is written for Ubuntu 22.04/24.04, with the RHEL/CentOS equivalents noted where they differ.
***
## Bringing It All Together [#bringing-it-all-together]
None of this is complicated in isolation - the challenge is doing all of it, consistently, on every server you're responsible for. Good Linux server management best practices aren't a one-time setup. They're a routine.
Lock down SSH and firewalls. Keep patches current. Automate your backups and maintenance. Watch your logs and resource usage. Document what you learn along the way.
Servers that are well-managed tend to be boring, in the best possible sense - no drama, just quiet reliability. That's the goal.
The gap between knowing these practices and actually applying them across 5, 10, or 20 servers is where most teams fall behind. Manual repetition across a growing fleet is where mistakes compound. For a practical breakdown of how to organize and automate server operations at that scale, read our guide on [DevOps automation tools](/blog/devops-automation-tools) that actually fit small teams.
***
## Frequently Asked Questions [#frequently-asked-questions]
The most critical practices are disabling root SSH login, switching to key-based authentication, configuring a deny-by-default firewall, automating security updates, and testing backup restores monthly. These five steps eliminate the overwhelming majority of common server compromises and data loss scenarios on any Linux distribution.
Disable root login (`PermitRootLogin no`), switch to ed25519 key authentication, disable password auth entirely, change the default port, use `fail2ban` to block brute-force attempts, and set idle timeouts with `ClientAliveInterval`. Test new key-based login in a separate terminal before closing your current session.
No. `chmod 777` gives every user on the system full read, write, and execute access to the file. On a web server, this allows anyone to upload and run malicious scripts. Instead, identify the actual owner/group mismatch with `ls -l` and set the correct permissions - typically `644` for files and `755` for executable scripts.
Security patches should be applied automatically using `unattended-upgrades` (Ubuntu/Debian) or `dnf-automatic` (RHEL/CentOS). Hold off on full version upgrades until tested in staging. A patched CVE protects you immediately. A kernel upgrade that breaks your application creates a new incident.
Keep 3 copies of your data, on 2 different types of storage, with 1 copy off-site. This protects against hardware failure, ransomware, and human error like `rm -rf` on the wrong directory. Crucially, backups must be versioned (for example `rsync` with `--backup-dir`, or snapshot tools like Restic and Borg). A simple sync/mirror (`rsync --delete`) is not a backup, because it will propagate ransomware encryption or deletions to your destination on the next run. The most overlooked step: test restoring from your backup once a month. A backup you've never restored is an assumption, not a safety net.
CtrlOps is a local-first desktop application that brings SSH management, a visual file manager, infrastructure monitoring, an approval-based AI terminal, and automated backups together in a single interface. Read more about [why CtrlOps](/why-ctrlops) was built to replace 4-5 separate tools and reduce deployment time from 30-45 minutes to under 5 minutes. It costs $7/user/month after a 1 month free trial - no credit card required.
For small teams managing under 25 servers, CtrlOps's built-in monitoring covers CPU, memory, disk, and running processes without installing or maintaining a separate stack. For teams at scale needing custom metrics, PromQL queries, and long-term data retention, Prometheus + Grafana is still the right choice. CtrlOps handles the 80% case with zero setup overhead.
Avoid full automation for production database migrations, credential rotation, server scaling or termination, and any destructive filesystem operations. These should be human-gated: automate the process, but require a human trigger and review before execution. Monitoring, backups, log rotation, and SSL renewal are safe to automate fully.
Both schedule recurring tasks. systemd timers offer better logging (via `journalctl`), dependency handling, and missed-run recovery (`Persistent=true` runs a missed task when the server comes back online). Cron is simpler to set up for basic scheduling. For production servers, systemd timers are the modern, more reliable choice.
Run `sudo ss -tulnp` to see every listening port and the process behind it. Cross-reference with your firewall rules (`sudo ufw status` or `sudo firewall-cmd --list-all`). Any port that's listening but not needed should be closed. Every open port is one more surface an attacker can probe.
Lock or delete their user account (using `sudo usermod -L` and disabling shell access with `sudo usermod -s /usr/sbin/nologin`, or deleting the user and their home directory entirely with `sudo userdel -r`), remove or back up their SSH keys from `~/.ssh/authorized_keys`, and rotate any shared credentials they had access to. This should happen the same day they leave, not "when someone remembers."
No. Termius and PuTTY are SSH connection tools. They handle terminal access but don't provide infrastructure monitoring, backup scheduling, AI-assisted diagnostics, or deployment automation. For those capabilities in a single app, CtrlOps is built for that use case at $7/user/month after a 1 month free trial - no credit card required.
---
# How to Manage Multiple Servers in 2026: Developer Guide (/blog/manage-multiple-servers-without-losing-control)
Author: Daxesh Italiya | Role: Co-Founder & CTO, TST Technology | Published: 2026-05-13 | Updated: 2026-06-11 | Tags: server management, ssh, devops, multi-server, developer workflow | Reading Time: 28 min read
> Managing multiple servers manually breaks down at server five or six. Real tools, SSH workflows, and deployment systems that hold up under production pressure.
## Key Takeaways [#key-takeaways]
Managing multiple servers without losing control comes down to one thing: stop relying on memory and start using a system. Manual setups break down faster than most developers expect - usually around server five or six. The system that holds up from one server to twenty-five combines a named server directory, integrated file management, always-visible monitoring, and standardized deployments.
* **One named directory** for all servers: no raw IPs, no tab guessing
* **Integrated file management** alongside your terminal: no SFTP app switching
* **Live monitoring visible at a glance**: not something you SSH into per server
* **Standardized deployments**: same steps, same outcome, whoever runs them
| Your situation | Best approach |
| -------------------------------------- | ---------------------------------- |
| 1 - 3 personal servers | Native OpenSSH + `~/.ssh/config` |
| Mobile SSH access needed | Termius |
| Free, local, open source | Tabby + Netdata + FileZilla |
| 3 - 25 servers, solo dev or small team | CtrlOps (unified app) |
| 30+ servers, dedicated ops staff | Ansible + Datadog + CI/CD pipeline |
***
## Why You Need a System for Managing Multiple Servers [#why-you-need-a-system-for-managing-multiple-servers]
It was a Friday evening. Eight client servers, one developer, one wrong terminal tab active.
Two hours of incident recovery later, the client was unhappy, and the developer was questioning every tool choice they had made in the past year.
The developer was not careless. The setup was not unusual. The failure was completely predictable. When you manage multiple servers by relying on memory, terminal tabs, and spreadsheets, you are not managing infrastructure. You are managing risk. And risk compounds.
This guide is about replacing that setup with something that actually holds up: the SSH workflows, monitoring habits, and deployment systems that survive the scale from one server to twenty-five.
***
## Why Managing Multiple Servers Becomes Chaos Quickly [#why-managing-multiple-servers-becomes-chaos-quickly]
One server is fine. Three is manageable. By six, something has usually broken once. By ten, you have probably had at least one incident that started with "I thought I was on the staging server."
The chaos does not arrive all at once. It builds up one server at a time, one added tool at a time, one manual workaround at a time.
### The Spreadsheet and Terminal Tab Problem [#the-spreadsheet-and-terminal-tab-problem]
Here is the setup most developers end up with when managing five or more servers:
* A Google Sheet with IPs, usernames, ports, SSH keys, and notes like "restart nginx after deploy"
* A terminal with six tabs open, named things like "server1" or "ubuntu\@45.33.32.156"
* A separate SFTP app that needs its own credentials every session
* A monitoring dashboard in a browser tab that nobody checks unless something already broke
* A Slack thread with deployment commands from three months ago that may or may not still be correct
Each one of these felt like the right solution to a specific problem at the time. Together, they form a system with no clear owner, no consistent truth, and no way to catch mistakes made under pressure.
What breaks first:
* The spreadsheet goes stale within weeks
* Terminal tabs get renamed or closed by accident
* The SFTP app is never open when you actually need it
* The monitoring dashboard gets skipped because opening it takes effort
* The Slack thread is impossible to search mid-incident
When everything is running fine, this works. The moment something goes wrong, it falls apart exactly when you need it most.
**Bottom line:** Every tool you add to patch a gap creates a new gap: another credential to maintain, another context to switch into, another place where information goes stale. The answer is not more tools. There are fewer tools doing more.
### No Visibility Across Your Servers [#no-visibility-across-your-servers]
Here is a direct question: right now, without SSH-ing into each server, do you know the current disk usage across everything you manage?
Most developers do not. They find out:
* A server is low on disk because the app starts throwing 500 errors
* Memory is maxed because response times go from 200ms to 4 seconds
* A process has been dead for six hours because a user filed a support ticket
This is not about being careless. It is the natural result of a setup where checking server health requires individual SSH sessions and manual commands. When every check costs two minutes per server, you only check when you already suspect something is wrong.
By then, you are already in recovery mode.
### Context Switching Kills Productivity [#context-switching-kills-productivity]
Every time you switch between tools, your brain has to rebuild context. [Parnin and Rugaber's analysis of 10,000 programming sessions](https://link.springer.com/article/10.1007/s11219-010-9104-9) found developers spend 15 to 30 minutes reconstructing context before resuming an interrupted task, and [UC Irvine's Gloria Mark](https://www.ics.uci.edu/~gmark/chi08-mark.pdf) measured an average of 23 minutes to fully refocus after an interruption.
Key numbers that put this in perspective:
* Only [10% of interrupted programming sessions](https://link.springer.com/article/10.1007/s11219-010-9104-9) resume productive work in under a minute - the rest lose real time to context rebuilding
* The average knowledge worker [toggles between applications over 1,200 times per day](https://hbr.org/2022/08/how-much-time-and-energy-do-we-waste-toggling-between-applications), per Harvard Business Review research
* [Atlassian's research on context switching](https://www.atlassian.com/blog/productivity/context-switching) identifies tool fragmentation as one of the biggest productivity killers for dev teams
When you are bouncing between a terminal, SFTP app, monitoring tab, and shared doc to complete a single deployment, you are not just losing time. You are increasing the odds of a mistake.
#### Real Example: Managing 8 to 15 Servers Manually [#real-example-managing-8-to-15-servers-manually]
Picture a freelance developer managing infrastructure for four clients:
* Client A: production + staging
* Client B: production + staging + database server
* Client C: one production machine
* Client D: two new servers for a feature launch
That is nine servers. Different SSH keys per client. Three different Linux distros. Mix of Nginx, Caddy, and Apache. Deployments done by SSH-ing in and running commands from a Notion doc that has three versions because three developers each updated their own copy.
A Friday afternoon hotfix deployment looks like this:
1. Open Notion to find the deployment commands for Client B production (context switch 1)
2. Open the spreadsheet to find the correct IP (context switch 2)
3. Open terminal, SSH in, realize you are in Client A's production tab by mistake
4. Close it, open a new tab, SSH into the correct server
5. Run deployment
6. Open SFTP app to verify the config file (context switch 3)
7. Open monitoring tab to confirm the service came back up (context switch 4)
8. Update the deployment log somewhere else (context switch 5)
Five context switches for one deployment. Multiply that by three servers. Add in a config edit. A 15-minute task becomes an hour, with a near-miss already baked in.
**Reality check:** When a client calls at 2 AM because their app is down, you do not need a scavenger hunt through spreadsheets, Slack threads, and terminal tabs. You need instant access. Every second you spend hunting for the right IP or the right key is a second their business is bleeding.
***
## What Actually Breaks When You Manage Multiple Servers at Scale [#what-actually-breaks-when-you-manage-multiple-servers-at-scale]
Scaling from one or two servers to ten does not just multiply your effort. It introduces failure modes that do not exist at the small scale.
### SSH Connection Confusion [#ssh-connection-confusion]
With one server, you always know what you are connected to. With ten, you are one wrong terminal tab away from:
* Running a production restart on staging
* Deleting a directory on the wrong machine
* Pushing a deployment to the wrong environment
The failure mode is subtle because it feels fine right up until it does not.
The technical fix is [SSH config aliases](/tools/ssh-config-generator): readable names instead of raw IPs. The better fix is a system where you see "acme-prod-web" and know exactly what you are connecting to before you run anything.
At midnight, tired, you will run commands on the wrong server. It is not a question of if. It is when. The only protection is a system that makes wrong-server connections visually impossible, not just unlikely.
### Deployment Inconsistency Across Servers [#deployment-inconsistency-across-servers]
Manual deployments look different depending on who runs them:
* One developer does `git pull` then restart. Another restarts, then pulls (brief downtime every time).
* One clears the cache. Another does not.
* One updates environment variables first. Another forgets.
When something breaks in production and the question is "what changed?", the honest answer is: "depends on who deployed it and when."
This inconsistency also creates configuration drift:
* Config files get edited on the server and never committed to the repo
* Environment variables updated on production but not staging
* Dependencies updated on one server, forgotten on three others
This is the root cause of the entire class of bugs that "only reproduce in production."
**Bottom line:** Manual deployments are not a process. They are a series of individual decisions made under varying conditions by different people. That is not repeatable. And things that are not repeatable will eventually fail in ways you cannot predict.
### Monitoring Gaps and Late Detection [#monitoring-gaps-and-late-detection]
Without proactive monitoring, you find out something is wrong from your users, not from your infrastructure:
* User reports the site is slow: you SSH in, find the disk at 98% from two months of unrotated logs
* Feature stops working: background worker has been dead for six hours
* Support tickets spike: Node process crashed when the disk hit 100%
The disk filling from 70% to 95% is entirely observable. It happens slowly and predictably. A monitoring setup that shows you this catches the problem days before it becomes an incident. The reason most small teams skip this is not that monitoring is hard. It is that setting it up properly across multiple cloud providers takes time most teams redirect to product work.
#### Why These Problems Compound Over Time [#why-these-problems-compound-over-time]
Here is the chain that makes this genuinely dangerous over time:
1. SSH confusion causes an incident
2. Incident requires an emergency manual fix under pressure
3. Emergency fix is undocumented
4. Undocumented fix creates configuration drift
5. Drift makes monitoring harder to interpret
6. You miss the next early signal
7. Repeat
The team's most experienced developer gradually becomes the single point of failure. The only one who knows which server is which, which deployment command is current, and where to start at 11 PM when something breaks. That is both a business risk and a path to burnout.
Bottom line: Every problem described above comes from one root cause: decisions stored in memory instead of systems. Move the knowledge into the system and most of these problems will solve themselves.
***
## What Efficient Multi-Server Management Actually Looks Like [#what-efficient-multi-server-management-actually-looks-like]
Efficient multi-server management has four characteristics. Most manual setups achieve none of them consistently.
### Centralized Server Visibility [#centralized-server-visibility]
Every server you manage should be visible in one place:
* Name and environment (not raw IP)
* Connection status
* Last connected timestamp
* At-a-glance health metrics (CPU, RAM, disk)
Not in a spreadsheet that goes stale. Not scattered across tabs. Not in your memory. One view, always current.
When you can see the state of your entire fleet at a glance, you stop being reactive. You start catching patterns before they escalate.
### Named SSH Access With No IP Chaos [#named-ssh-access-with-no-ip-chaos]
Your connection system should use human-readable names:
* `acme-prod-web` tells you exactly what you are connecting to
* `ssh ubuntu@203.0.113.45` requires you to correctly recall which IP, which key, which username
This distinction matters most under pressure. When something is broken and you are moving fast, connecting to the wrong server can make the incident worse. A named system removes this class of mistake by design, not by discipline.
### Integrated File Management [#integrated-file-management]
File management and your terminal should live in the same application. Opening a separate SFTP app to edit a config file on a server you are already SSH-ed into is not just inefficient. It is a context switch with a cognitive cost every time.
Same for monitoring. If checking server health requires opening a different browser tab, you will check it less often. Less often means more missed signals. More missed signals means more incidents.
### Fast Movement Between Servers [#fast-movement-between-servers]
Moving between servers should take seconds. Click the name, connect, work. Not:
1. Find the IP in a spreadsheet
2. Open a new terminal tab
3. Type the SSH command
4. Enter the passphrase
5. Navigate to the working directory
The goal: the server identity is the only variable. Everything else stays consistent and fast.
***
## Traditional Workflow vs Modern Workflow [#traditional-workflow-vs-modern-workflow]
### Traditional Setup [#traditional-setup]
| Task | Tool |
| ------------------- | -------------------------------------------------- |
| SSH access | Terminal with named (or unnamed) tabs |
| File management | Separate SFTP app with its own credentials |
| Server monitoring | Browser-based dashboard, rarely checked |
| Server info | Google Sheet or Notion doc, inconsistently updated |
| Deployment commands | Slack thread or shared doc with multiple versions |
A single deployment with this setup:
1. Open Notion to find the IP and commands (context switch 1)
2. SSH into the server (context switch 2)
3. Run deployment
4. Open SFTP app to verify config (context switch 3)
5. Open the monitoring tab to confirm health (context switch 4)
6. Update the deployment log (context switch 5)
Five context switches. Each one costs 15 to 30 minutes of recovered focus time.
### Modern Setup with CtrlOps [#modern-setup-with-ctrlops]
| Task | What changes |
| ----------------- | ---------------------------------------------------------- |
| SSH access | Click server name in the directory, connect in one click |
| File management | File manager opens alongside the terminal, no separate app |
| Server monitoring | Infra panel visible in the same interface, always |
| Deployment | Wizard handles the process end-to-end with validation |
| AI assistance | Describe the task in plain English, review before running |
The same deployment:
1. Click the server name
2. Run deployment via the built-in wizard
3. Check the infra panel to confirm a healthy status
Three steps. Zero context switches.
### Comparison [#comparison]
| Factor | Fragmented setup | Unified workflow with CtrlOps |
| ------------------------- | --------------------------------- | ------------------------------- |
| Time per deployment | 35 to 60 min | 8 to 12 min |
| Context switches per task | 4 to 5 | 0 |
| Wrong-server risk | High (tab confusion) | Low (named, visual connections) |
| New developer onboarding | Half a day | Under 20 min |
| Mental load | High (tracking info across tools) | Low (one context) |
Five deployments per week: that is roughly 135 minutes per week recovered. Over a year, more than 100 hours.
The risk difference matters more. [Studies of interrupted programming work](https://link.springer.com/article/10.1007/s11219-010-9104-9) consistently find that fragmented attention raises both recovery time and error rates - most interrupted tasks lose 15 to 30 minutes of context rebuilding before productive work resumes.
***
## Best Approaches to Manage Multiple Servers [#best-approaches-to-manage-multiple-servers]
### 1. Manual SSH and Scripts [#1-manual-ssh-and-scripts]
**What it is:** Terminal access, SSH keys, and scripts you have built up over time.
**What works:**
* Maximally flexible, no additional tooling required
* Works well if you are a solo developer who knows the infrastructure deeply
* Good starting point before anything grows
**What breaks:**
* Scripts fail silently when the environment changes
* Infrastructure knowledge lives in people's heads and leaves when they do
* Getting a new team member up to speed requires significant manual setup per server
**Best for:** Solo developers managing two or three stable, personal servers.
***
### 2. SSH Clients with Tabs (iTerm2, Termius) [#2-ssh-clients-with-tabs-iterm2-termius]
**What it is:** A dedicated SSH client with session management, named connections, and multi-tab support.
**What works:**
* Named connections remove the IP memorization problem
* Tabs make multi-session access more organized
* The SSH part of the workflow improves meaningfully
**What it does not solve:**
* File management is still a separate application
* Monitoring is still a separate tab or a manual SSH session
* Deployment is still manual
You organized one piece of a four-part problem. The other three stayed exactly the same.
**Best for:** Developers who primarily need organized SSH access and rarely do file management or deployments.
***
### 3. Monitoring + SSH + File Tools Combination [#3-monitoring--ssh--file-tools-combination]
**What it is:** Best tool for each job: dedicated SSH client, SFTP app, monitoring platform, deployment pipeline.
**What works:**
* Each component does its specific job well
* Powerful at scale with dedicated infrastructure staff
**What breaks:**
* Four tools mean four places to update credentials when a server changes
* Four interfaces to maintain, four configurations that drift out of sync
* High onboarding cost for new team members
* High maintenance overhead for anyone not exclusively working on infrastructure
**Best for:** Teams with dedicated DevOps staff who have time to maintain and evolve a multi-tool setup.
***
### 4. Unified Desktop Tool (CtrlOps) [#4-unified-desktop-tool-ctrlops]
**What it is:** One desktop application handling SSH management, file browsing, infrastructure monitoring, an AI-assisted terminal, and deployment automation.
**What works:**
* One credential store, one interface, one context across every server management task
* [File manager](/docs/modules/file-manager) opens alongside the terminal, no separate SFTP connection needed
* [Infra Details panel](/docs/modules/infra-details) shows live CPU, RAM, disk per server, no agent installation required
* [AI Terminal](/docs/modules/ai-terminal) generates commands from plain English, requires your review before anything runs
* Add Application wizard handles Node.js, React, Next.js [deployments](/docs/modules/deployment) end-to-end (Nginx, PM2, SSL, env vars)
* Everything local, AES-256 encrypted, no cloud sync
**The trade-off:**
* You are in one tool rather than best-in-class specialized tools
* At 30+ servers with dedicated ops staff, specialized tools become more appropriate
**Where CtrlOps doesn't fit (yet):**
No tool works everywhere. CtrlOps is built for traditional server infrastructure - VMs, VPS, dedicated machines. If your stack runs on serverless (AWS Lambda, Cloud Functions) or you're deep into container orchestration (Kubernetes, ECS Fargate), CtrlOps isn't the right tool for those environments. Also, CtrlOps doesn't have an automatic alerting system yet - you can see real-time metrics on the dashboard, but push-based alerts (Slack, email) are on the roadmap. For teams that need proactive alerting today, pairing CtrlOps with a dedicated monitoring tool like Datadog or UptimeRobot fills that gap.
**Best for:** Developers, freelancers, and startup teams managing 3 to 25 servers who want reduced context switching and faster deployments without dedicated infrastructure staff.
Before deciding on tool consolidation, count the number of application switches in your last three server management tasks. If the answer is consistently more than three per task, the context-switching cost alone is likely costing you several hours of productive work every week.
***
## Multi-Server Management Tools That Actually Help [#multi-server-management-tools-that-actually-help]
### SSH Connection Managers [#ssh-connection-managers]
| Tool | Platform | Price | Best for |
| -------------------------------- | --------------- | ----------------- | -------------------------------------------- |
| Native OpenSSH + `~/.ssh/config` | All | Free | Power users comfortable with text config |
| Termius | All + Mobile | $10/mo | SSH access from phone, cross-device sync |
| Tabby | All | Free | Local storage, open source, modern UI |
| CtrlOps | Mac, Win, Linux | $7/mo (1 mo free) | SSH + files + monitoring + deployment in one |
**Native OpenSSH:** Pre-installed everywhere. A well-structured `~/.ssh/config` handles named hosts and key routing automatically. No GUI, no fleet visibility.
**Termius:** Best mobile SSH experience available. Credentials sync through their cloud vault (end-to-end encrypted, but cloud-dependent and account-required). Good if phone access is a real need.
**Tabby:** Free, open source, modern interface. Local credential storage. Solid if you want free and private.
**CtrlOps:** Desktop app integrating SSH, file management, monitoring, and deployment. Local-first. [$7/month flat](/pricing) for unlimited servers, with a 1 month free trial.
Still picking a client? We've tested the options hands-on for every platform: [best SSH clients for Mac](/blog/best-ssh-client-mac-2026), [best SSH clients for Windows](/blog/best-ssh-clients-windows), and [best SSH clients for Linux](/blog/best-ssh-client-linux).
***
### Server Monitoring Tools [#server-monitoring-tools]
| Tool | Type | Price | Agents required |
| --------------------- | -------------------------- | --------------- | --------------------- |
| htop / top | CLI, per-server | Free | No (built into Linux) |
| Netdata | Self-hosted dashboard | Free | Yes, per server |
| Uptime Kuma | Self-hosted uptime monitor | Free | No |
| Datadog / New Relic | Enterprise SaaS | $15 - $30+/host | Yes |
| CtrlOps Infra Details | Built into app | Included | No |
**htop/top:** Good diagnostic tools once you know something is wrong. Require SSH-ing into each server individually. No fleet-level view.
**Netdata:** Good open source dashboards with historical data. Needs installation and maintenance on each server.
**Uptime Kuma:** Excellent for service uptime and alerting. Does not provide detailed resource metrics.
**Datadog/New Relic:** Enterprise-grade. Right call at scale with dedicated ops staff. Too much cost and overhead for small teams under 30 servers.
**CtrlOps Infra Details:** No agent installation needed. Shows [live CPU, RAM, disk, and process table](/features/infra-monitoring) per server from inside the app you are already using for SSH and files.
***
### File Management Tools [#file-management-tools]
| Tool | Platform | Price | Needs separate connection |
| -------------------- | ------------ | ---------- | ------------------------- |
| WinSCP | Windows only | Free | Yes |
| Cyberduck | Mac, Windows | Free / $38 | Yes |
| FileZilla | All | Free | Yes |
| CtrlOps File Manager | All | Included | No |
All standalone SFTP tools require opening a second application and re-establishing a connection to a server you are already SSH-ed into. CtrlOps File Manager opens alongside the terminal with no additional connection or credential entry.
***
#### When to Use Each Approach [#when-to-use-each-approach]
| Situation | Best fit |
| ------------------------------------------------ | --------------------------- |
| 1 to 3 personal servers, no deployments | Native OpenSSH |
| Mobile SSH access needed | Termius |
| Free, local, open source | Tabby + Netdata + FileZilla |
| 3 to 25 servers, small team, regular deployments | CtrlOps |
| 30+ servers with dedicated infrastructure staff | Enterprise stack |
***
## Real DevOps Scenarios: Where Systems Break or Scale [#real-devops-scenarios-where-systems-break-or-scale]
### Managing 5 to 20 Servers Simultaneously [#managing-5-to-20-servers-simultaneously]
**The setup:** A dev agency managing six clients. Each client has production and staging. Two have separate database servers. Fourteen servers total. Four developers with different access levels.
**Where it breaks down:**
* Three developers have been updating the server spreadsheet independently. Three versions exist, each slightly different.
* A developer who did not set up Client D's servers needs to connect on a Saturday. They spend 15 minutes finding credentials.
* One developer stored SSH keys in Dropbox "for convenience." A client security audit catches this six months later.
**What a working setup looks like:**
* All 14 servers added once with consistent naming (acme-prod-web, acme-prod-db, acme-staging-web)
* Any developer can connect in seconds using their own locally stored SSH keys
* New developer onboarding: import configuration file, run SSH wizard, done in under 20 minutes
Softnoesis hit this wall at fifteen to twenty servers across eight-plus active projects, with every credential sitting in one notepad file. [Connecting all of them took a single six-minute setup](/case-studies/softnoesis).
***
### Deploying Updates Across Multiple Servers [#deploying-updates-across-multiple-servers]
**The setup:** A startup pushing a hotfix during high traffic. Three servers need the fix: app server, worker server, API server. Same codebase, different configs per server.
**Where it breaks down:**
* App server: deployed correctly
* Worker server: missed an environment variable that was added manually three weeks ago and never documented
* Worker processes fail silently, with no monitoring on background job failures
* The issue is not caught for 40 minutes until a downstream effect surfaces in user-facing data
* Debugging requires SSH-ing through three servers and checking logs manually
**What a working setup looks like:**
* Parameterized deployment scripts in a shared script directory
* Scripts pull correct environment-specific values per server automatically
* Infra panel shows all three servers returning a healthy status within seconds
* Any failure surfaces immediately, no manual log check required
***
### Debugging Production Issues at Night [#debugging-production-issues-at-night]
**The setup:** Production returning 502 errors at 11:30 PM. On-call developer is not the one who built the server setup. Solid developer, limited Linux admin experience.
**Where it breaks down:**
| Step | Time lost |
| ------------------------------------------------------- | --------------------- |
| Finding the correct server in the spreadsheet | 5 min |
| SSH-ing in with the right key (wrong key first attempt) | 3 min |
| Running diagnostic commands from an outdated Notion doc | 15 min |
| Identifying disk is full | Finally, after 25 min |
| Clearing disk and restarting the process | 15 min |
| Total incident duration | 90+ min |
**What a working setup looks like:**
| Step | Time |
| ---------------------------------------------------------------- | ------------ |
| Open CtrlOps, click production server by name | 10 sec |
| Infra Details: disk at 97%, immediately visible | 10 sec |
| AI Terminal: "Node app throwing 502, disk at 97%, what do I do?" | 30 sec |
| Review AI-generated commands, approve each | 2 min |
| Disk cleared, process restarted, 502 errors stopped | Done |
| Total incident duration | Under 15 min |
***
#### Which Workflows Fail and Which Hold Up [#which-workflows-fail-and-which-hold-up]
The pattern is consistent across every scenario:
* Workflows that depend on implicit knowledge (which server is which, which command is current, what "normal" looks like) fail under pressure
* Workflows that externalize that knowledge into systems, naming conventions, parameterized scripts, and visible dashboards hold up when things are hard
The failure is never a lack of skill. It is always a lack of system.
***
## Monitoring Across Multiple Servers [#monitoring-across-multiple-servers]
### What Metrics Actually Matter [#what-metrics-actually-matter]
Focus on three things. These catch the majority of server failures before they reach users.
**Disk above 85%:**
* Almost always heading toward an incident
* Fills from log accumulation, old deploy artifacts, and database growth
* At 100%, most applications fail in ways that are hard to diagnose
* Catching it at 85%: a 5-minute cleanup task
* Catching it at 100%: a recovery operation
**Memory pressure above 85% sustained:**
* Indicates a memory leak, an under-resourced server, or a rogue process
* Catch it early: restart the process, resize the server, investigate the leak
* Miss it: user-facing slowness that is hard to attribute to a root cause
**Sustained CPU spikes:**
* Legitimate load increase: you need more capacity
* Rogue process: you need to find and stop it
* You can only tell the difference when you can see the CPU alongside the process table
### Alerts vs Manual Checks [#alerts-vs-manual-checks]
| Approach | Posture | When you find out |
| ---------------- | --------------- | -------------------------- |
| No monitoring | Fully reactive | When users report it |
| Manual checks | Partly reactive | When you remember to check |
| Automated alerts | Proactive | Before users are affected |
Setting up alerts requires choosing thresholds, notification channels, and maintaining configuration as your fleet changes. For teams that cannot justify that investment yet, a unified dashboard you actually look at regularly is a meaningful step up from having no visibility at all.
### Why Most Teams Miss Early Signals [#why-most-teams-miss-early-signals]
The answer is friction, not negligence.
If checking disk usage across 10 servers requires 10 SSH sessions and 10 manual commands, most developers will not do it proactively. The effort cost is too high.
If checking disk usage across 10 servers means glancing at a dashboard already open in the same app you use for SSH, developers do it regularly because the cost is nearly zero.
A monitoring system that requires effort to access is a monitoring system that will not be used proactively. And a monitoring system nobody uses proactively provides no better early warning than no monitoring at all.
The simplest monitoring habit that prevents most incidents: a 10-minute fleet health review every Monday morning. Open your server management tool, scan disk and memory across all servers, and note anything trending toward a threshold. Ten minutes per week. The incidents it prevents cost hours.
***
## What Actually Works for Server Management at Any Scale [#what-actually-works-for-server-management-at-any-scale]
### Best Approach for Solo Developers [#best-approach-for-solo-developers]
* Set up a proper `~/.ssh/config` with named hosts for every server you manage
* Use dedicated server management software for developers with named connections, not raw terminal tabs
* Write parameterized deployment scripts and store them somewhere findable under pressure
* If you consistently open more than two tools for a typical server management task, evaluate whether a unified tool recovers enough time to be worth it
### Best Approach for Startup Teams [#best-approach-for-startup-teams]
The most urgent risk for a startup team: the knowledge bus factor. One developer is the only person who knows which server is which and what to do when things break.
Address this before the crisis, because the crisis will be the worst possible time to discover the knowledge that lives in one person's head:
* Use tooling that makes server access shareable through a configuration file, not shared credentials - the right server management software for developers pays for itself the first time you onboard a new engineer in 20 minutes instead of half a day
* Standardize deployments so every team member follows the same steps to the same outcome
* Add basic monitoring before the first major incident, not in response to it
### Managing 5+ Client Servers as a Freelance Developer [#managing-5-client-servers-as-a-freelance-developer]
Freelancers face a version of the multi-server problem that is distinct from teams, and almost entirely unaddressed by standard tooling.
The core tension: you need to manage client servers as a freelancer with the operational discipline of a team, while working as a single person, without the time to build and maintain a multi-tool stack.
**What makes the freelance scenario different:**
* Each client has separate SSH keys, separate credentials, and separate deployment processes
* Context switching between clients is not just between servers - it is between entirely different environments and expectations
* You are the bus factor. There is no second person who knows which server is which
* Billing time spent searching for credentials or context-switching between tools directly reduces the hourly rate
**The specific failure modes that hit freelancers:**
* The client spreadsheet has four versions across three projects and Notion
* SSH keys stored in Dropbox or a shared folder for "convenience" - a security risk that surfaces only when a client asks who has access (the [SSH key storage best practices](/blog/ssh-key-management-best-practices) guide covers the safe alternatives)
* Deployments look different client to client because each was set up differently, six months apart
* A client calls on a Saturday. You spend 12 minutes finding the right credentials before you can even SSH in
**What a clean freelance server management setup looks like:**
The naming convention matters more here than anywhere. Because clients are the organizing unit, not environments:
* `clienta-prod-web`
* `clienta-staging-web`
* `clientb-prod-api`
* `clientc-prod-web`
Each client's servers are immediately identifiable. Zero IP lookups required.
With CtrlOps, a freelancer adds each server once, using the client-based naming convention. Every subsequent connection is one click from the Multi-Server Directory. SSH keys stay local, per-client, never shared. When a client relationship ends: remove their servers from the directory, done.
**The economics are direct.** If you manage client servers as a freelancer and bill at $75/hour:
* 15 minutes recovered per deployment × 3 deployments/week = 45 minutes/week
* 45 minutes × 52 weeks = 39 hours/year recovered
* At $75/hour: $2,925 in billable time recovered annually from a $7/month tool
The tool cost is roughly 3% of what it recovers.
**The freelancer test:** Can any client server you manage be accessed within 30 seconds from a cold start - no spreadsheet lookup, no credential hunting, no terminal tab archaeology? If not, the cost is not just productivity. It is the professional impression you make at 11 PM when a client's site is down, and they are watching how fast you respond.
### Best Approach for Scaling Environments [#best-approach-for-scaling-environments]
At 25+ servers or 8+ developers, the math shifts:
* Dedicated monitoring infrastructure (Datadog, Prometheus + Grafana) becomes a justified investment
* Proper CI/CD pipelines pay back their setup cost clearly
* Specialized tooling for each function makes sense when you have staff to maintain it
For the period between "a handful of servers" and "need enterprise infrastructure," a unified desktop tool covers the gap without requiring you to build and maintain a multi-tool stack.
### Simplest Setup That Still Scales [#simplest-setup-that-still-scales]
These four things together cover most teams up to 25 servers and 10 developers:
1. Named servers in a management tool with one-click connect
2. Integrated file management alongside the terminal
3. A visible monitoring panel is checked regularly
4. Parameterized deployment scripts run the same way every time
Not the most sophisticated setup possible. The one that actually gets used consistently because the friction is low enough that people do not bypass it under pressure.
***
## Common Mistakes When Managing Multiple Servers [#common-mistakes-when-managing-multiple-servers]
### Relying on Memory Instead of Systems [#relying-on-memory-instead-of-systems]
Storing critical infrastructure information in your head: which IP maps to which server, which key goes with which client, which deployment command is current - and it works until it does not.
The failure always happens under pressure: when you are tired, distracted, or moving fast.
What to externalize instead:
* Server names and connection details (not IPs)
* Deployment steps, written and version-controlled
* Environment variable differences between servers, documented
* Runbooks that any developer on the team can follow
The investment is for a few hours. The return is eliminating an entire class of incidents for as long as you use the system.
***
### Using Too Many Disconnected Server Management Tools [#using-too-many-disconnected-server-management-tools]
Every additional tool in your server management workflow is:
* A context switch with a cognitive cost
* A separate set of credentials to maintain when servers change
* Another configuration that drifts out of sync over time
* Another interface that a new team member has to learn
Evaluate tool consolidation based on the total workflow cost, not on whether each individual tool is excellent at its specific job. A tool that handles four jobs at 85% of the capability of four specialized tools is often the better operational choice when the alternative is four context switches per task.
***
### No Standardized Deployment Process [#no-standardized-deployment-process]
"Everyone has their own way of deploying" is a description of a system waiting to fail.
Consequences:
* Incidents are harder to diagnose: was it the code change or how the deployment was executed?
* Senior developers become bottlenecks: they are the only ones who know the full correct process
* Production drifts from staging in ways that create "only reproduces in production" bugs
The fix: standardize the process once, write it down, and use tooling that enforces the standard rather than depending on each developer to remember every step every time.
**Bottom line:** The teams that handle scale well do not have better memories or more discipline. They have systems that prevent these failures by design. Names instead of IPs. Scripts instead of rituals. Dashboards instead of gut checks.
***
## Final System: How to Set Up a Clean Multi-Server Workflow [#final-system-how-to-set-up-a-clean-multi-server-workflow]
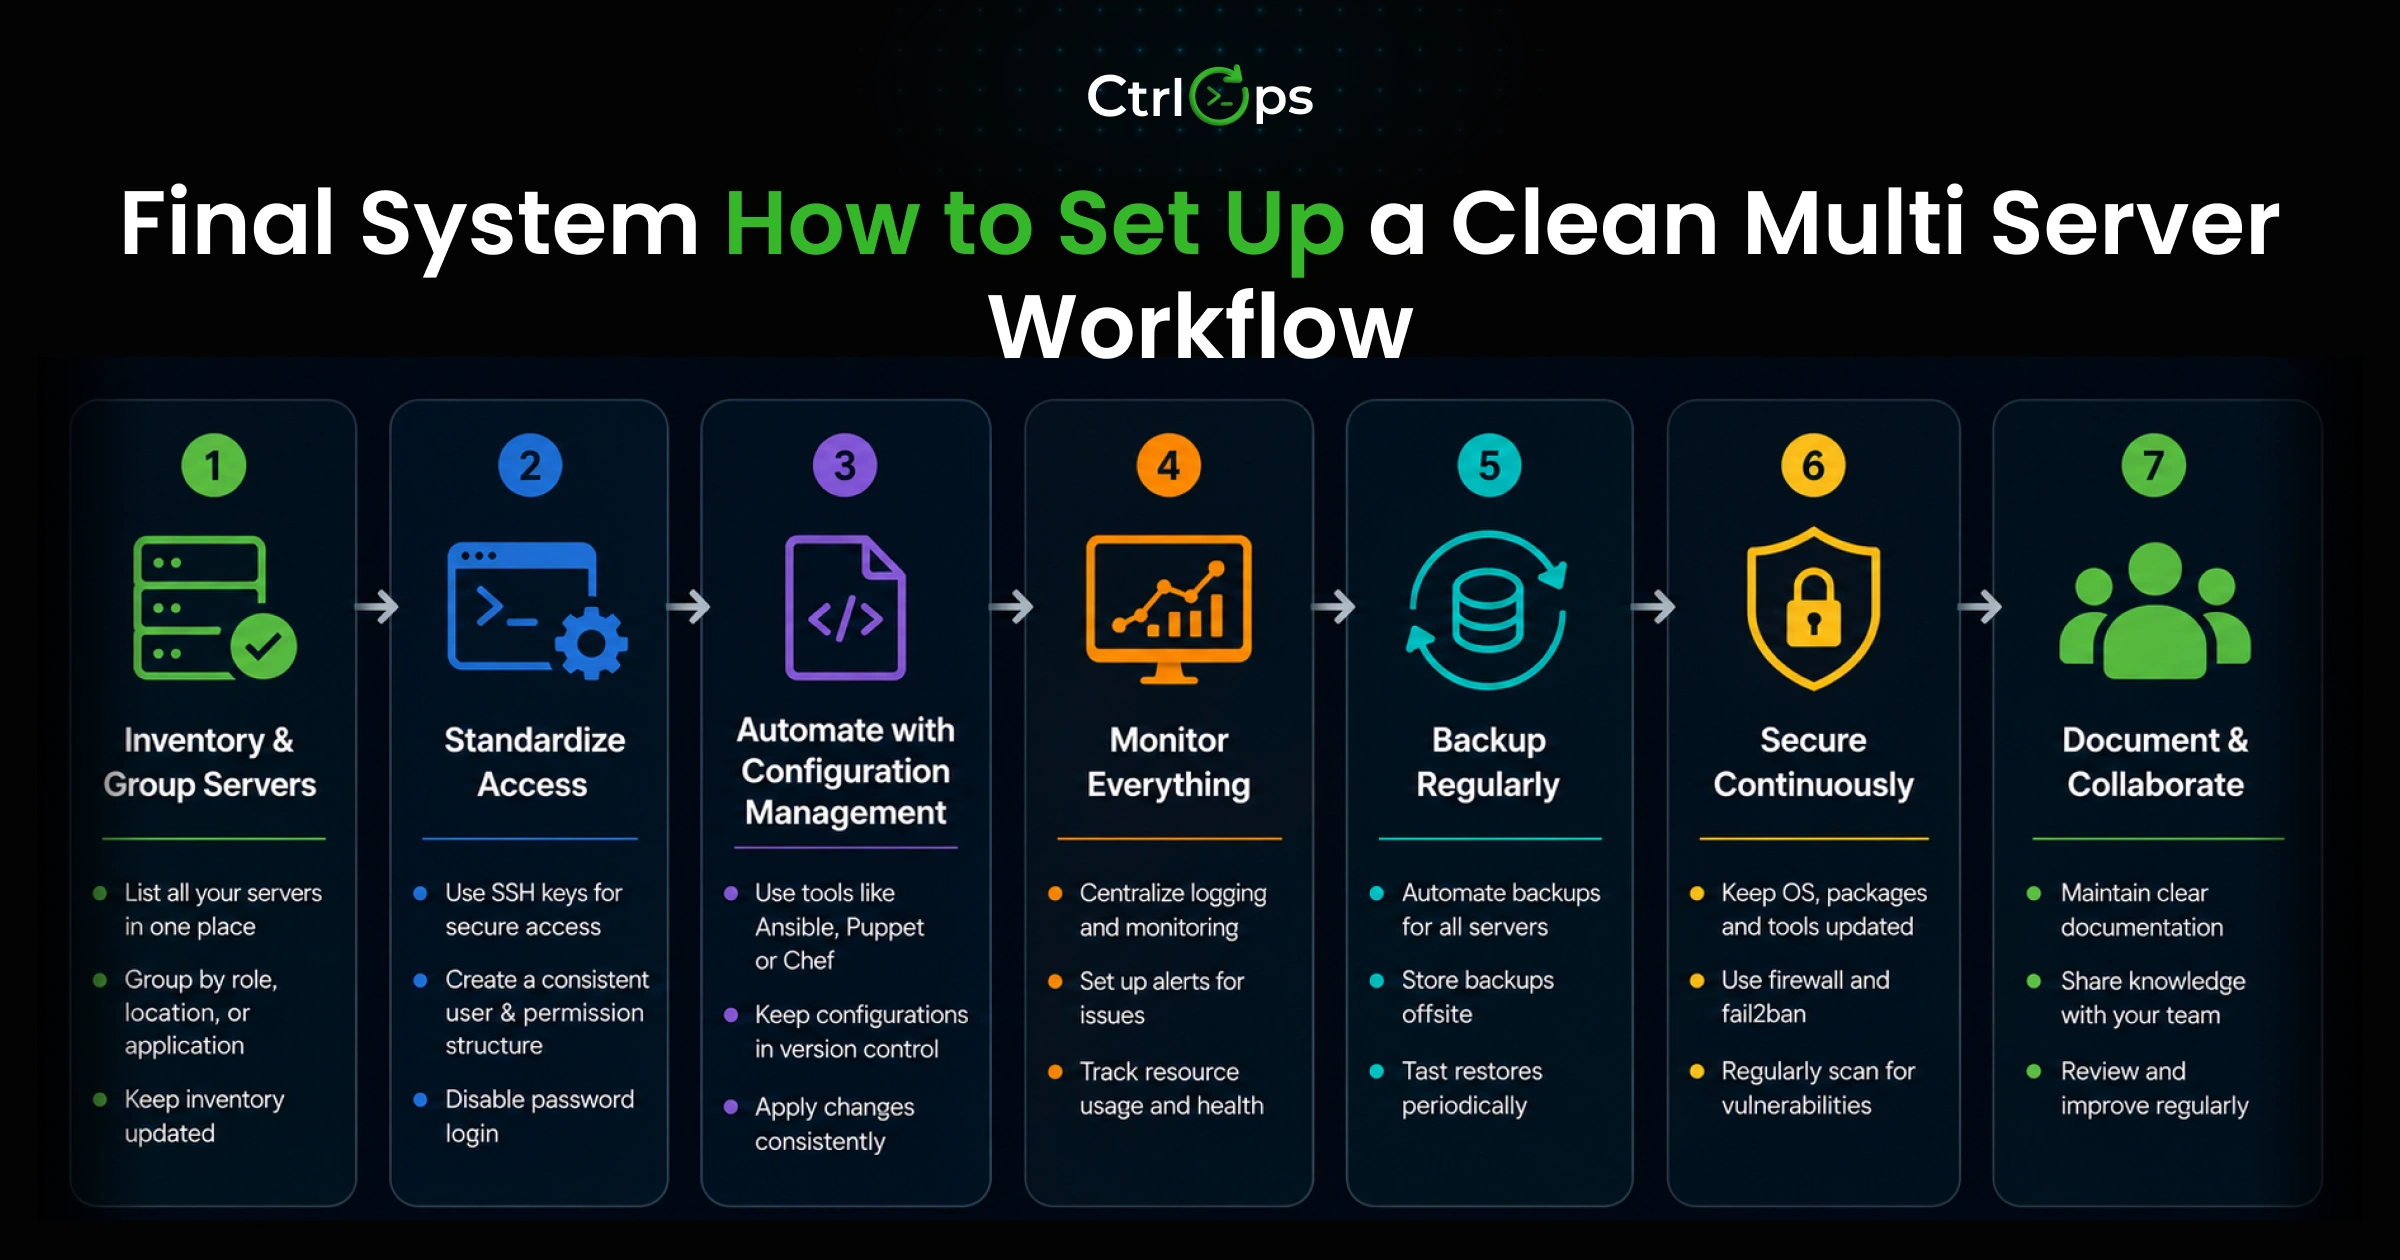
This is the practical setup that works for most developers and small teams managing 5 to 25 servers.
### Step 1: Name Every Server Before You Add It [#step-1-name-every-server-before-you-add-it]
Establish a naming convention and apply it immediately.
A reliable pattern: `[project-or-client]-[environment]-[role]`
Examples:
* `acme-prod-web`
* `acme-prod-db`
* `acme-staging-web`
* `internal-prod-api`
* `clientb-prod-worker`
This naming convention tells you what you are looking at, what environment it belongs to, and what role it plays, before you connect to it.
Retroactively renaming and reorganizing fifteen servers later is painful work. Name them correctly from the start.
***
### Step 2: Centralize All Server Connections in One Place [#step-2-centralize-all-server-connections-in-one-place]
Add every server to a single connection manager using the naming convention from Step 1.
In CtrlOps, this is the [Multi-Server Directory](/features/multi-server-management): add a server once (name, IP, username, SSH key or .pem path), and it is available with one click for any team member who imports the configuration file.
Whether you use an SSH config file or a dedicated tool, the goal is the same: connect to any server without looking up an IP address. And when a hostname doesn't resolve the way you expect, a quick [DNS record lookup](/tools/dns-record-lookup) shows exactly what's pointing where before you start blaming the server.
***
### Step 3: Stop Using a Separate SFTP App [#step-3-stop-using-a-separate-sftp-app]
If your current SSH client does not include a file manager, evaluate what switching to one that does would cost versus what it would recover.
The test: next time you need to edit a config file on a server you are already SSH-ed into, count the steps. If the answer involves opening a second application and re-entering credentials, that workflow has more friction than it needs.
***
### Step 4: Add Basic Monitoring Without Extra Infrastructure [#step-4-add-basic-monitoring-without-extra-infrastructure]
Connect through a tool that shows you CPU, RAM, and disk across your fleet without requiring agents installed on each server.
Check it at least once a week. Build the habit before you need it.
***
### Step 5: Parameterize and Standardize Your Deployments [#step-5-parameterize-and-standardize-your-deployments]
For each application type you deploy regularly:
* Write a script with variable placeholders for the values that differ between servers
* Store it where any team member can find it under pressure
* Test on staging before production
* Run from the same tool every time
Once deployments are standardized, the next bottleneck is usually everything around them - CI, backups, log checks. Our roundup of [DevOps automation tools for small teams](/blog/devops-automation-tools) covers what's worth automating at each stage.
Set up your full server management system for any new server before you deploy anything to it. Add it to the directory with the correct name. Check its initial monitoring metrics. Run a test script. This 15-minute setup investment prevents rebuilding server knowledge under incident pressure months later.
***
## Conclusion: Systems Beat Memory [#conclusion-systems-beat-memory]
Managing multiple servers is not the hard part. Managing them without a system is where the problems start.
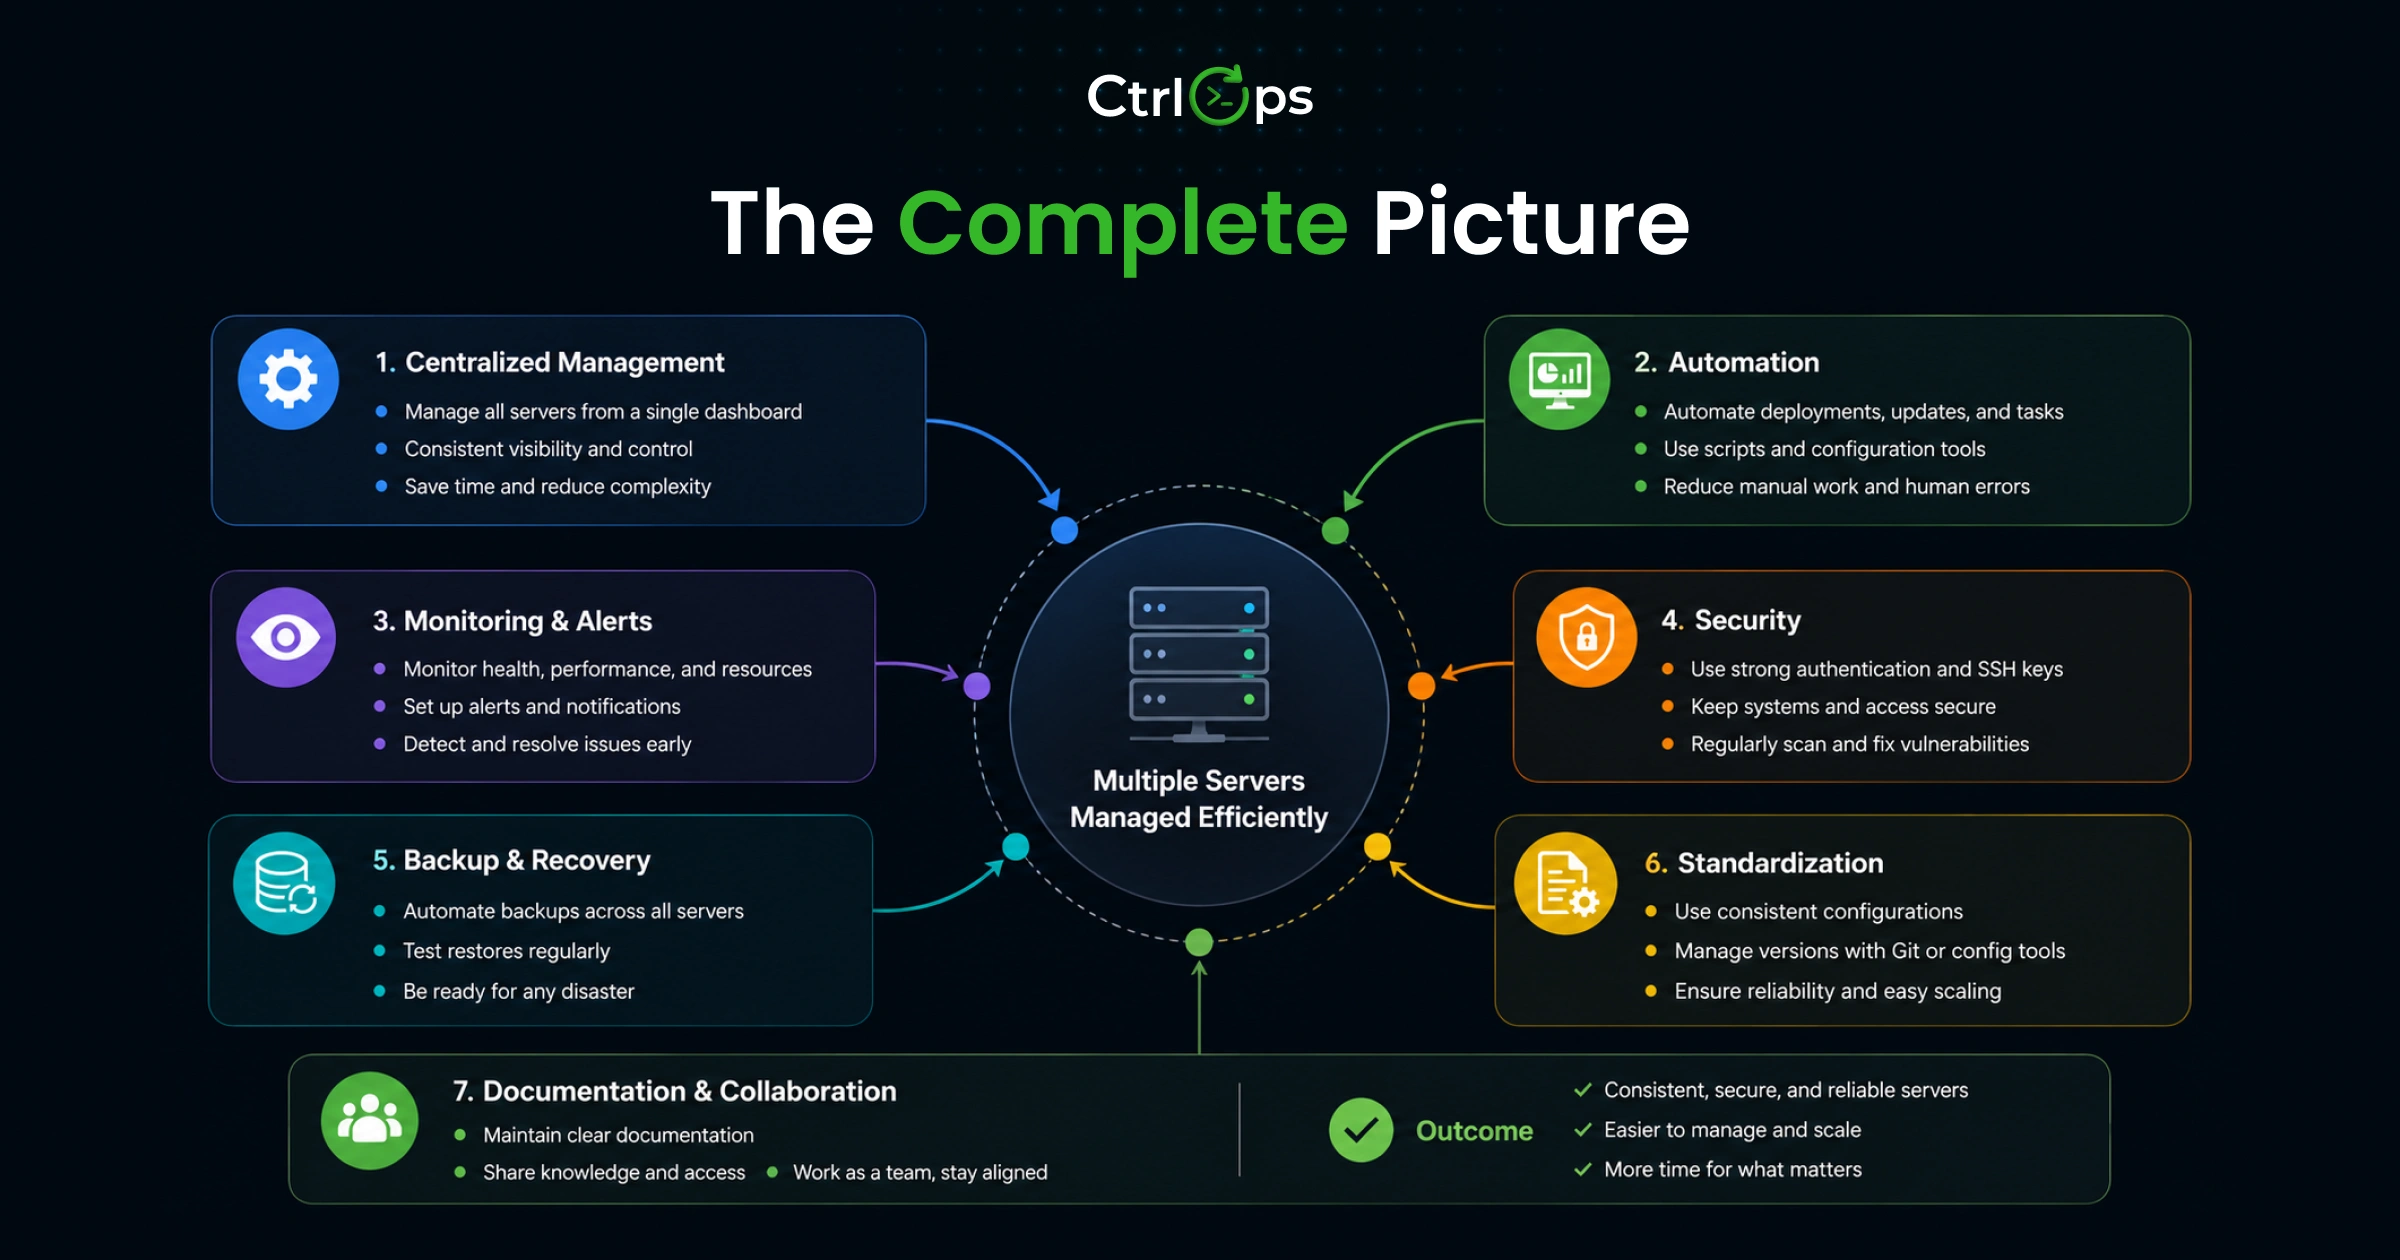
Name your servers. Centralize your connections. Stop switching between four tools to complete one deployment. Write your deployment process down and run it the same way every time.
These are not complicated technical changes. They are system-level decisions. And system-level decisions compound - in your favor - once you make them.
***
## FAQs [#faqs]
The most efficient approach combines three things most manual setups lack:
* A named server connection system that removes raw IP dependency
* A unified tool that handles SSH, file management, and monitoring without switching applications mid-workflow
* A standardized deployment process that any team member can execute correctly
The biggest gains come from reducing context switching. [Research on interrupted programming tasks shows each switch costs 15 to 30 minutes of recovered focus time](https://link.springer.com/article/10.1007/s11219-010-9104-9). A typical multi-tool server management workflow involves three to five switches per task.
Depends on team size and what you need:
* SSH access only: Termius or Tabby
* SSH + files + monitoring + deployment in one tool: CtrlOps ($7/mo flat)
* 30+ servers with dedicated ops staff: Ansible + Datadog or Prometheus + CI/CD pipeline
* Free, local, open source: Tabby + Netdata + FileZilla (with context-switching overhead)
For most developers and small teams managing 3 to 25 servers, consolidation eliminates more friction in practice than specialized tools provide in marginal capability.
Two steps:
1. Set up SSH config aliases. A properly structured `~/.ssh/config` replaces raw IPs with meaningful server names and handles key routing automatically. `ssh acme-prod-web` always connects to the right server with the right key.
2. Use a connection manager that stores named configurations and makes connecting a one-click action.
CtrlOps's Multi-Server Directory does exactly this, shareable with team members through a configuration file.
The practical starting point for small teams: a tool that shows CPU, RAM, and disk across your fleet without agent installation or complex configuration.
CtrlOps's Infra Details panel does this inside the same app you use for SSH and file management.
For teams that need alerting and historical data: [Uptime Kuma](https://github.com/louislam/uptime-kuma) and [Netdata](https://www.netdata.cloud/) are low-overhead self-hosted options. Full stacks (Prometheus + Grafana, Datadog) are the right investment when scale and dedicated ops justify the setup work.
The most important factor is not which tool you use. It is whether checking server health is genuinely frictionless enough to become a regular habit.
The short answer: stop managing servers one at a time.
Effective multi-server management requires three things working together:
1. **A named connection directory.** Every server accessible by a human-readable name - not an IP you recall from memory. `clienta-prod-web` is faster to identify correctly than `203.0.113.45`, especially at midnight under pressure.
2. **A unified interface.** SSH, file management, and monitoring in one tool. Every application switch in your server management workflow has a cognitive cost. Three tools per task means three context switches, every time.
3. **Parameterized deployment scripts.** The same steps, the same outcome, regardless of who runs them or which server they target. This is how you go from "I manage multiple servers" to "I manage multiple servers reliably."
CtrlOps handles all three in a single desktop app. You add a server once, connect with one click, manage files alongside the terminal, and run deployments from a built-in wizard. No credential hunting, no tab confusion.
Depends on scale and team structure:
| Situation | Best fit |
| -------------------------------------------- | ---------------------------------- |
| 1 - 3 personal servers | Native OpenSSH + `~/.ssh/config` |
| SSH access only, mobile included | Termius |
| Free, local, open source | Tabby + Netdata + FileZilla |
| 3 - 25 servers, solo developer or small team | CtrlOps |
| Freelancer managing multiple client servers | CtrlOps |
| 30+ servers, dedicated DevOps staff | Ansible + Datadog + CI/CD pipeline |
For most developers, the best server management software is not the most feature-rich one. It is the one that reduces context switching enough that you actually use it consistently, including during incidents when the alternative is a frantic spreadsheet search at 2 AM.
CtrlOps is purpose-built for Linux server management: SSH directory, integrated file manager, real-time infra monitoring, AI terminal, and application deployment in one desktop app. $7/month flat, unlimited servers, no agent installation required, and a 1 month free trial.
If your stack is serverless (Lambda, Cloud Functions) or container-orchestrated (Kubernetes, ECS), a different tool is the right fit - CtrlOps is built for traditional VM and VPS infrastructure.
Most developers hit the wall between five and eight servers. The clear signals:
* You are not confident that you know the current state of all servers at any given time
* Your deployment process produces different outcomes depending on who runs it
* New team members take hours or days to get up to speed on your infrastructure
* Incidents consistently involve a step where you are searching for information that should be immediately accessible
* Multi-Server Directory supports export and import: add all servers once, share the configuration file with the team
* Each developer uses their own locally stored SSH keys, no shared credentials
* Script Directory stores parameterized scripts that any team member can run against any server they have access to
* AI Terminal gives less experienced developers a safe way to diagnose server issues by reviewing commands before executing them
* $7/month flat for unlimited servers after a 1 month free trial, significantly cheaper than per-user alternatives when managing multiple environments
For a team moving from spreadsheets and terminal tabs to a real system, expect roughly an hour of focused setup for the first 10 servers, then a few minutes per server after that.
A realistic breakdown:
* Naming convention agreed and written down: 15 minutes
* Adding 10 servers to a connection manager with SSH keys and notes: 30 to 45 minutes
* Writing two parameterized deployment scripts and testing on staging: 30 to 45 minutes
* Confirming the monitoring view across all servers: 5 minutes
The longest part is usually the naming convention discussion, not the technical setup. Once the convention is set, every additional server takes under two minutes to add.
Yes for traditional compute instances. No for serverless or container orchestration.
CtrlOps connects to any Linux server over SSH, which covers:
* AWS EC2 instances
* DigitalOcean Droplets
* Linode (Akamai) Compute instances
* Vultr, Hetzner, OVH, Contabo
* On-premises VMs and bare-metal servers
What it does not manage:
* AWS Lambda, Google Cloud Functions, Azure Functions (serverless)
* Kubernetes clusters, AWS ECS Fargate (container orchestration)
* Managed PaaS like Heroku, Render, Vercel (no SSH access)
If your stack is primarily VMs and VPS instances across one or more cloud providers, CtrlOps is built for that. If you are running mostly on serverless or Kubernetes, a different tool is the right fit.
Different problems, different tools.
Ansible is configuration management. It is built for declaring the desired state of fleets of servers (packages installed, files in place, services running) and enforcing that state across hundreds or thousands of machines. It shines when the same configuration needs to be reproduced reliably across a large fleet.
A desktop tool like CtrlOps is operational management. It is built for the day-to-day work of connecting, deploying, monitoring, and debugging a smaller fleet of servers that a developer or small team touches directly.
The honest answer:
* 5 to 25 servers, small team, no dedicated ops staff: a desktop tool removes more daily friction than Ansible adds in setup cost
* 50+ servers, fleet-wide configuration drift is a real problem, dedicated ops staff: Ansible (or Terraform + Ansible together) is the right investment
* Both at once is common at scale: Ansible enforces baseline configuration, the desktop tool handles the human-in-the-loop debugging and deployment work
The two are complementary, not competing. Pick based on which problem is actually costing you time right now.
Server management focuses on the individual machines: SSH access, file edits, deployments, monitoring CPU and disk, restarting services. It is a developer-level discipline.
Infrastructure management is broader: provisioning, networking, load balancing, DNS, autoscaling, IAM policies, multi-region failover, CI/CD pipelines, and observability platforms. It is typically an SRE or DevOps team discipline at scale.
The simple way to tell which you need:
* If you are running 5 to 25 servers and asking, "how do I keep these from breaking?" - that is server management
* If you are running 100+ servers, multi-region, and asking "how do I provision and govern this fleet automatically?" - that is infrastructure management
Most developers and small startup teams need server management done well. Infrastructure management tooling (Terraform, Pulumi, full observability stacks) becomes relevant when the fleet grows beyond what a small team can reason about server-by-server.
---
# Top 5 MobaXterm Alternatives for Mac in 2026 (/blog/mobaxterm-alternatives-mac)
Author: Hiren Kalariya | Role: Co-Founder & CEO, TST Technology | Published: 2026-06-03 | Updated: 2026-09-07 | Tags: MobaXterm Alternatives for Mac, MobaXterm for Mac, Mac SSH Manager, Server Management App Mac | Reading Time: 14 min read
> MobaXterm doesn't run on Mac. We compared CtrlOps, Termius, Royal TSX, Warp & iTerm2 against real tasks. Find the best fit for your workflow.
MobaXterm is Windows-only and has never had a macOS version. The 5 best MobaXterm alternatives for Mac in 2026 are CtrlOps (all-in-one server management), Termius (cross-device SSH sync), Royal TSX (multi-protocol RDP/SSH/VNC), Warp (AI-first coding terminal), and iTerm2 (free open-source terminal).
Here's how each handles real server tasks on Mac:
| Tool | Best For | Price | AI | File Manager | Local Credentials |
| ----------- | -------------------------------- | -------------------------- | ----------------------------------- | -------------- | ---------------------- |
| **CtrlOps** | **All-in-one server management** | **$7/user/mo (1 mo free)** | **✓ Approval-gated** | **✓ Full GUI** | **✓ Local-only** |
| Termius | Cross-device SSH sync | Free / $10/user/mo | ⚠️ Autocomplete (Gloria in preview) | ✓ SFTP | ⚠️ Cloud on paid tiers |
| Royal TSX | Multi-protocol IT work | Free / €49 one-time | ✗ | ✓ SFTP | ✓ Local |
| Warp | AI-first coding terminal | Free / $20/mo | ✓ Auto-run | ✗ | ✗ Cloud required |
| iTerm2 | Free terminal emulator | Free | ✗ | ✗ | ✓ Local |
Prefer to watch instead? The full rundown - why MobaXterm never shipped on Mac, and how all five alternatives handle real server work - in a few minutes:
***
## The 5 Best MobaXterm Alternatives for Mac (2026) [#the-5-best-mobaxterm-alternatives-for-mac-2026]
The best MobaXterm alternative for Mac depends on why you used MobaXterm. For full server management with AI assistance, CtrlOps is the closest match. For cross-device SSH sync, Termius leads. For multi-protocol IT work including RDP, Royal TSX is purpose-built. For a fast modern terminal, Warp. For zero-cost local terminal work, iTerm2.
### Alternative 1: CtrlOps - Best for Developers Who Want More Than SSH [#alternative-1-ctrlops---best-for-developers-who-want-more-than-ssh]
[CtrlOps](https://ctrlops.io/) is a desktop app for macOS, Windows, and Linux that replaces your SSH client, file transfer tool, monitoring dashboard, and deployment system in one local-first interface.
If you managed multiple servers on MobaXterm and want the best [SSH client for Mac](/blog/best-ssh-client-mac-2026), CtrlOps is the closest match. It does things MobaXterm never did.

**What it does well:**
* **Named server cards:** Connect to "Prod-Backend" or "Client-XYZ-Staging" in one click. No IPs to memorize.
* **Full [GUI file manager](https://ctrlops.io/docs/modules/file-manager):** Upload, download, edit remote files with drag-and-drop. No `scp` commands, no separate SFTP tool.
* **Approval-gated [AI terminal](https://ctrlops.io/docs/modules/ai-terminal):** Ask "why is my server slow?" and get diagnostic commands shown before execution. Supports [web search](https://ctrlops.io/docs/modules/ai-terminal/web-search) for live docs and [MCP servers](https://ctrlops.io/docs/modules/ai-terminal/mcps) for repo-aware context.
* **[1-click deployment](https://ctrlops.io/docs/modules/deployment):** Pick your framework, paste GitHub repo, add env variables. CtrlOps handles git clone, dependencies, PM2, Nginx, and SSL.
* **[Infrastructure monitoring](https://ctrlops.io/docs/modules/infra-details):** Live CPU, RAM, disk for every server. No `htop` in a separate window.
* **[Log management](https://ctrlops.io/features/log-management):** Auto-discovers every log file on your server, grouped by source. Search, live tail, and download without terminal commands.
* **[Script Directory](https://ctrlops.io/docs/modules/ai-terminal/scripts):** Save reusable scripts with `{{variable}}` placeholders. Run across servers in one click.
* **[Access management](https://ctrlops.io/docs/modules/access-management):** See who can SSH into every server across your fleet. Onboard or offboard across all servers in one action.
* **[Security audit](https://ctrlops.io/features/security-audit):** Run 25+ agentless security checks on your servers, databases, and Docker configurations. Get a hardening score and AI-assisted remediation.

To see all features, visit the [CtrlOps features page](https://ctrlops.io/features).
**Where CtrlOps falls short:**
* No mobile app, Termius wins for phone-based SSH
* No serverless or Kubernetes support
* No push notifications yet (on roadmap)
**Pricing:** $7/user/month or $70/user/year (unlimited servers). [1 month free trial](https://ctrlops.io/pricing), no credit card required.
**Platforms:** macOS (Apple Silicon + Intel), Windows, Linux.
If you want to [manage multiple servers](/blog/manage-multiple-servers-without-losing-control) without losing track of which tab is which client, CtrlOps is purpose-built for that.

Here's what "everything in one window" actually looks like - adding a server and working with it, start to finish:
***
### Alternative 2: Termius - Best Cross-Device SSH Client [#alternative-2-termius---best-cross-device-ssh-client]
[Termius](https://termius.com/) is a modern SSH client that syncs your servers, keys, and configurations across Mac, Windows, Linux, iOS, and Android.
If the main thing you want from a MobaXterm alternative is clean SSH management with cross-device access, Termius is the most polished option in 2026. It runs natively on Mac, including Apple Silicon. The interface feels like a product designed for developers, not a ported Windows tool.

**What it does well:**
* Cross-device sync - your hosts, keys, and settings work on Mac, iPad, and iPhone without re-entering anything
* Built-in SFTP for file transfers without switching apps
* SSH key management that doesn't involve editing `~/.ssh/config`
* Snippets for saving and reusing commands
* AI autocomplete that suggests commands as you type
* Gloria, an agentic DevOps assistant, is in limited preview - it can take on infrastructure tasks like installing and configuring services, though it's not yet generally available
* Port forwarding with a visual interface
**Where Termius falls short:**
* No one-click deployment
* No infrastructure monitoring dashboard
* SSH keys sync to Termius cloud servers, a hard blocker if client contracts restrict third-party credential storage
**Pricing:**
* Starter: Free - SSH/SFTP, AI autocomplete, port forwarding, local vault (credentials stay on your machine, no cloud sync on this tier)
* Pro: $10/month (billed annually) - personal cloud vault, cross-device sync, snippets, log bookmarks
* Team: $20/user/month (billed annually) - shared team vault, real-time collaboration, consolidated billing
* Business: $30/user/month (billed annually) - multiple vaults, granular access control, SAML SSO add-on
That's $120/year per person on Pro versus $70/year for CtrlOps with significantly more features. For a 5-person team, Termius Team costs $1,200/year.
**Reality check:** On the free Starter plan, credentials stay in a local vault. Upgrade to Pro or above, and SSH credentials move to Termius's cloud. Check client agreements before upgrading. If that trade-off rules Termius out, see [Termius alternatives](/blog/termius-alternatives) across all platforms, or the [Mac-specific breakdown](/blog/termius-alternatives-mac).
***
### Alternative 3: Royal TSX - Best for IT Pros Managing Multiple Protocols [#alternative-3-royal-tsx---best-for-it-pros-managing-multiple-protocols]
[Royal TSX](https://www.royalapps.com/ts/mac) is a Mac-native connection manager that handles SSH, RDP, VNC, SFTP, and web connections from a single interface - the closest thing to MobaXterm's multi-protocol approach on macOS.
If your job involves jumping between SSH sessions, Windows Remote Desktop connections, and VNC consoles all day, Royal TSX is built exactly for that. It's the connection hub IT professionals reach for on Mac.

**What it does well:**
* **Multi-protocol in one app:** SSH, RDP, VNC, SFTP, Telnet, web connections
* Tree-based folder structure for organizing connections cleanly
* Credential management - assigns credentials to connections without exposing them
* Perpetual license model: buy once, own it. No monthly subscription
* Free tier available (up to 10 connections, enough to test)
* No cloud dependency - connections and credentials stay on your machine
**Pricing:**
* Free: Up to 10 connections (personal use)
* Individual User License (Royal TSX for Mac): €49 one-time (includes 1 year of software maintenance)
* Royal TS/X + Royal Server Personal Bundle: €99 one-time
Licenses are perpetual. You pay once and get 1 year of free updates. After that, you can pay \~50% of the license price to extend maintenance - or just keep using the version you bought.
**Where Royal TSX falls short:**
* No AI features of any kind
* No infrastructure monitoring dashboard
* No one-click app deployment
* UI feels heavy for developers used to modern interfaces
* No built-in script automation
**Bottom line:** Royal TSX fits IT pros living in RDP and VNC across a mixed fleet. For developers managing web servers and cloud VPS, it has no AI terminal, no infra dashboard, and no deployment automation. If you're coming from SecureCRT instead, see [SecureCRT alternatives for Mac](https://ctrlops.io/blog/securecrt-alternatives-mac).
***
### Alternative 4: Warp - Best Modern AI Terminal for Local Development [#alternative-4-warp---best-modern-ai-terminal-for-local-development]
[Warp](https://warp.dev/) is a Rust-built terminal emulator for Mac (and Windows/Linux) with a block-based interface, IDE-like editing, and a powerful AI Agent Mode that converts natural language to shell commands.
If what you're really replacing is just MobaXterm's terminal - and you do most of your work locally or on a single server - Warp is one of the most polished terminal experiences available on Mac in 2026. For a direct head-to-head of all three classic tools, see the [PuTTY vs MobaXterm vs Warp comparison](/blog/putty-mobaxterm-warp-alternative).

**What it does well:**
* Built in Rust - fast, no Electron lag
* **Block-based output:** each command and its result stays in a distinct block, making it easy to scan, copy, and share
* **AI Agent Mode:** type a task in natural language, Warp generates the commands (note: Warp's Agent Mode can auto-execute, unlike CtrlOps)
* **Warp Drive:** shared team command library
* **Multi-agent support:** run multiple AI agents in parallel tabs
**Pricing (as of 2026):**
* Free: Core terminal features + 75 AI credits/month (150/month for the first two months)
* Build: $20/month - 1,500 AI credits/month, BYOK support, rollover Reload Credits
* Business: $50/user/month - everything in Build, plus SSO, Zero Data Retention, and shared team credits
Warp restructured pricing in late 2025. Build tier is $20/month, Business is $50/user/month. The terminal remains free without AI credits.
**Where Warp falls short:**
* No multi-server dashboard, Warp is a terminal, not a server management tool
* No GUI file manager
* No infrastructure monitoring
* No one-click deployment
* Requires a Warp cloud account
* AI Agent Mode can auto-run commands, meaningful risk on production servers
**Reality check:** Warp's Agent Mode can execute commands automatically on your server without showing you first. On a staging machine, that's fine. On production, it's a different conversation - one unreviewed command can take down a live service. CtrlOps always shows generated commands before anything runs.
***
### Alternative 5: iTerm2 - Best Free Terminal Emulator for Mac [#alternative-5-iterm2---best-free-terminal-emulator-for-mac]
[iTerm2](https://iterm2.com/) is the most widely used free, open-source terminal emulator for macOS - a powerful upgrade from Apple's default Terminal.app that's been battle-tested by millions of developers [since 2010](https://github.com/gnachman/iTerm2), with over 16,000 stars on GitHub.
If you're on a tight budget or you just need a solid terminal without extra tooling, iTerm2 is the honest answer.

**What it does well:**
* Split panes - divide your terminal window horizontally and vertically for multiple sessions at once
* Hotkey window - summons the terminal from any app instantly
* Tmux integration - manages tmux sessions through a native Mac interface
* Advanced search with regex support across the full scrollback buffer
* Password manager integration (1Password, Bitwarden, Keeper Security)
* Fully local - no cloud account, no subscription, no tracking
* Donationware - free, with an optional donation to support development
**Pricing:** Free (open source, GPL-2.0)
**Where iTerm2 falls short:**
* No AI features
* No graphical file manager, you're back to SCP commands for file transfers
* No server dashboard or multi-server management
* No deployment tooling
* macOS only, if your team uses Windows or Linux, they need something else
**Bottom line:** iTerm2 is the right tool if you want a free, reliable terminal and you're happy managing file transfers and monitoring through separate tools. If tool-switching is killing your productivity, see how [AI is changing DevOps workflows](https://ctrlops.io/blog/ai-in-devops) with approval-gated commands.
***
## Quick Comparison Table [#quick-comparison-table]
| Factor | CtrlOps | Termius | Royal TSX | Warp | iTerm2 |
| ---------------------- | ------------------------------------ | ----------------------------------- | -------------------- | ---------------- | ----------- |
| Price | $7/mo/user · $70/yr/user (1 mo free) | Free / $10/mo / $20/mo | Free / €49 one-time | Free / $20/mo | Free |
| macOS Support | ✓ | ✓ | ✓ | ✓ | ✓ |
| Windows/Linux | ✓ | ✓ | ✗ Mac-only | ✓ | ✗ |
| Mobile App | ✗ | ✓ iOS + Android | ✓ iOS + Android | ✗ | ✗ |
| Multi-Server Dashboard | ✓ Named cards | ⚠️ Host list | ✓ Folder tree | ✗ | ✗ |
| GUI File Manager | ✓ Full GUI | ✓ SFTP | ✓ SFTP | ✗ | ✗ |
| AI Terminal | ✓ Approval-gated | ⚠️ Autocomplete (Gloria in preview) | ✗ | ✓ Auto-run | ✗ |
| Infra Monitoring | ✓ Dashboard | ✗ | ✗ | ✗ | ✗ |
| Log Management | ✓ Auto-discovery | ✗ | ✗ | ✗ | ✗ |
| 1-Click Deployment | ✓ | ✗ | ✗ | ✗ | ✗ |
| Local Credentials | ✓ Local-only | ⚠️ Local on free, cloud on Pro+ | ✓ Local | ✗ Cloud required | ✓ Local |
| Free Trial | 1 month free | Free plan | Up to 10 connections | Free terminal | Always free |
***
## Why You Need a MobaXterm Alternative on Mac [#why-you-need-a-mobaxterm-alternative-on-mac]
It's midnight. You've just switched from a Windows machine to a MacBook, or your team lead hands you a new M3 Pro and says, "Get our 12 servers sorted by tomorrow." You Google "MobaXterm for Mac" and immediately hit a wall: MobaXterm is Windows-only. It always has been.
That's the moment freelance developers, startup CTOs, and agency engineers realize they need to find a **MobaXterm alternative for Mac** fast. And it's a common moment: 31.8% of professional developers work on macOS according to the [2024 Stack Overflow Developer Survey](https://survey.stackoverflow.co/2024/technology), making it the second most popular developer OS - and a steady stream of them arrive from Windows setups built around MobaXterm. And not just any alternative. You want something that handles SSH, maybe file transfers, and ideally doesn't require three extra apps just to do what MobaXterm did on Windows.
We compared five tools against the same real-world tasks - connecting to multiple servers, transferring files, running diagnostic commands, and deploying an app - so you don't have to.
***
## Why Mac Users Keep Getting Sent to MobaXterm? [#why-mac-users-keep-getting-sent-to-mobaxterm]
MobaXterm was built for Windows system administrators and has never had a macOS release in the company's history - [Mobatek](https://www.mobatek.net/) has been building Windows system and network software since 2008, and has not announced plans to change that. Mac users searching for MobaXterm are usually after one of three things: multi-tab SSH sessions, a graphical file browser, or a single app that handles multiple servers. All three are fully covered by the Mac alternatives in this list.

What made MobaXterm worth defending on Windows was the bundle: SSH, X11 forwarding, RDP, VNC, SFTP, and a built-in Unix environment, all in one app. That's genuinely useful - if you live on Windows. The catch is that the X11-server architecture it's built around is Windows-native, which is a big part of why there's never been a Mac port. So every time a developer switches to Mac, or a cross-platform team onboards a new engineer with a MacBook, someone has to explain the "MobaXterm doesn't work on Mac" situation again.
**The good news:** macOS has better native SSH infrastructure than Windows ever did - [OpenSSH ships built into macOS](https://support.apple.com/guide/mac-help/allow-a-remote-computer-to-access-your-mac-mchlp1066/mac), and Apple's own Remote Login feature runs on it. The tools that fill the gap on Mac are actually more capable for developers in 2026 - especially if you want features like AI-assisted terminal commands, GUI file managers, or multi-server dashboards.
What you're really looking for depends on *why* you used MobaXterm:
* You loved the multi-tab SSH sessions - Termius, Royal TSX, or CtrlOps
* You relied on the graphical file browser - CtrlOps or Transmit
* You just want a solid terminal - iTerm2 or Warp
* You managed 5+ servers and needed a dashboard - CtrlOps
**Bottom line:** MobaXterm's core value was "everything SSH-related in one place." On Mac in 2026, CtrlOps comes closest to that - and goes further with an [AI terminal](/features/ai-terminal) and one-click app deployment.
***
## Which One Should You Pick? [#which-one-should-you-pick]
There's no single "best" MobaXterm alternative for Mac - it depends on what you actually used MobaXterm for.

Here's the honest breakdown:
**Choose CtrlOps if** you're a developer or startup CTO managing 3+ servers. You want SSH, file transfers, monitoring, log viewing, and AI diagnostics in one app instead of four. $7/user/month or $70/user/year. [Try CtrlOps free for 1 month](https://ctrlops.io/get-api-key), no credit card needed.
**Choose Termius if** you work across Mac, iPad, and iPhone and want your server list synced across devices. Great for solo developers who need clean SSH management with SFTP. SSH credentials go to Termius's cloud on paid tiers, so review your client agreements first.
**Choose Royal TSX if** you're an IT professional managing Windows RDP connections alongside SSH and VNC. Royal TSX is the only tool here that handles all three protocols well on Mac. A one-time purchase also makes sense if you dislike subscriptions.
**Choose Warp if** you want the most modern, AI-enhanced terminal experience for local development and single-server work. It's a strong MobaXterm alternative if what you mainly used was the terminal - not the multi-server management.
**Choose iTerm2 if** you need zero-cost, zero-cloud, maximum reliability. It's the right foundation if you're comfortable in the terminal and manage everything else through separate tools.
For a deeper look at how the top **SSH clients for Mac** stack up on key features, the [best SSH clients for Mac](/blog/best-ssh-client-mac-2026) breakdown covers the full picture. And if you're curious how AI is changing the way developers manage servers day-to-day, the [AI in DevOps](/blog/ai-in-devops) breakdown is worth reading next.
**Bottom line:** MobaXterm alternatives on Mac have caught up - and in several areas, surpassed what MobaXterm offered on Windows. CtrlOps is the only tool here that combines SSH management, file transfer, an AI-assisted terminal, and deployment in a single local-first desktop app.
***
## How to Migrate From MobaXterm to Your Mac in 10 Minutes [#how-to-migrate-from-mobaxterm-to-your-mac-in-10-minutes]
You've picked a tool. Now you need your MobaXterm sessions on your Mac without redoing everything by hand. Here's the full migration in three steps.
### Step 1: Export your MobaXterm sessions and keys (3 minutes) [#step-1-export-your-mobaxterm-sessions-and-keys-3-minutes]
On your Windows machine, open MobaXterm's session manager and export your saved sessions - or, if you only have a handful, just note the host, port, and username for each. MobaXterm often stores private keys in PuTTY's `.ppk` format, but macOS SSH tools expect standard OpenSSH keys. Convert any `.ppk` file with PuTTYgen (`brew install putty`, then `puttygen yourkey.ppk -O private-openssh -o yourkey`), copy your keys into `~/.ssh/` on the Mac, and lock down permissions with `chmod 600 ~/.ssh/yourkey`.
### Step 2: Recreate your servers in your chosen tool (5 minutes) [#step-2-recreate-your-servers-in-your-chosen-tool-5-minutes]
* **CtrlOps:** Click New Connection, give each server a readable name ("Client-A-Prod"), paste the IP and username, and point it at your `~/.ssh/` key. Moving a whole team? Import a server list instead of adding them one by one.
* **Termius:** Add each host, attach the key from your vault, and - on a paid tier - sync across your devices.
* **Royal TSX:** Create a document, add connections under a folder tree, and assign saved credentials.
* **iTerm2 / Warp:** Add host entries to `~/.ssh/config` (`Host prod` / `HostName 1.2.3.4` / `User deploy` / `IdentityFile ~/.ssh/yourkey`), then connect with `ssh prod`.
### Step 3: Connect and verify (1 minute) [#step-3-connect-and-verify-1-minute]
Connect to one server and confirm the essentials: your key authenticates, you can open a file-transfer/SFTP view, and commands run. If a converted `.ppk` key fails, re-check that permissions are `chmod 600` and that you pointed the tool at the OpenSSH version of the key - not the original `.ppk`.
**Bottom line:** Migrating off MobaXterm isn't a project - it's a 10-minute copy of your servers and keys into a tool that actually runs on your Mac. Nothing changes on the server side: same SSH, same keys, same access. Only the client changes.
***
## Conclusion [#conclusion]
MobaXterm not running on Mac is frustrating, especially if you've built your workflow around it. But the Mac ecosystem in 2026 has caught up and surpassed what MobaXterm offered on Windows.
CtrlOps is the most direct replacement if you need SSH, file transfers, monitoring, and AI diagnostics in one app. Termius wins for cross-device sync. Royal TSX handles mixed-protocol IT work. iTerm2 or Warp cover pure terminal needs.
If you're also evaluating server panels alongside SSH clients, the [aaPanel alternatives](https://ctrlops.io/blog/aapanel-alternatives) guide covers the panel side. For Windows-specific tools, see [PuTTY alternatives for Windows](https://ctrlops.io/blog/putty-alternatives-windows).
Pick the tool that matches your actual workflow. Not the one with the most feature checkboxes.
***
## FAQs [#faqs]
No. MobaXterm is Windows-only software developed by Mobatek, a France-based company. There is no official macOS version and no indication one is planned. Mac users need a separate SSH and server management tool entirely. CtrlOps, Termius, Royal TSX, Warp, and iTerm2 are the strongest alternatives in 2026.
iTerm2 is the best free alternative if you primarily want a powerful terminal emulator - open source, actively maintained, runs on both Intel and Apple Silicon Macs. If you need a free option that also includes SFTP and multi-device sync, Termius has a free plan, though SSH credentials sync to the cloud on paid tiers and the free plan is limited to one device.
CtrlOps is a desktop app for macOS, Windows, and Linux that combines SSH, a GUI file manager, an approval-gated AI terminal, infrastructure monitoring, log management, fleet-wide access control, and one-click deployment in one interface. It organizes servers as named cards, shows real-time infra dashboards, and requires your approval before any AI-generated command runs. $7/user/month or $70/user/year with a 1 month free trial.
Termius encrypts SSH credentials but stores them in its cloud on Pro and Team plans. If your contracts restrict third-party credential storage, this is a hard blocker. CtrlOps and Royal TSX keep all credentials stored locally on your device.
Yes. Warp's Agent Mode can execute commands automatically without requiring approval first. This is efficient for local development but carries real risk on production servers where one unreviewed command can cause downtime.
Not the way dedicated server management tools handle it. Warp is a terminal emulator - you SSH into servers manually and manage them through the command line. There's no visual dashboard, named server directory, or one-click connect for a fleet of servers. For multi-server management, CtrlOps, Termius, or Royal TSX are better suited to that workflow.
CtrlOps is purpose-built for this scenario. You create named server cards per client environment ("Client-A-Prod", "Client-B-Staging"), connect instantly without memorizing credentials, manage files through the GUI without switching to Cyberduck or FileZilla, and diagnose issues through the AI terminal - all without storing credentials in third-party cloud services. Server list import/export means onboarding a new team member takes minutes, not an afternoon.
Yes. CtrlOps runs natively on macOS with both Apple Silicon (M1/M2/M3/M4) and Intel chips. It also runs on Windows and Linux, so teams using mixed hardware can all work from the same tool without platform-specific workarounds or compatibility issues.
MobaXterm has been Windows-only since 2008 and Mobatek has not announced any plans for a macOS version. The app relies on a Windows-native X server architecture that would require a near-complete rewrite to port to macOS. Mac users should not wait for an official release - the alternatives covered here are mature and, in several areas, more capable.
Yes. CtrlOps and Termius both run on macOS, Windows, and Linux. Warp also supports all three platforms. If your team uses mixed operating systems, any of these three tools let everyone work from the same app without platform-specific workarounds or separate license purchases.
---
# 10 Best PuTTY Alternatives for Windows in 2026 (With AI) (/blog/putty-alternatives-windows)
Author: Daxesh Italiya | Role: Co-Founder & CTO, TST Technology | Published: 2026-05-25 | Updated: 2026-08-27 | Tags: PuTTY Alternatives, SSH Client for Windows, AI Terminal, Server Management | Reading Time: 24 min read
> PuTTY still works - but costs you 40 min per incident. Compare 10 PuTTY alternatives for Windows in 2026, including free options and AI-powered tools.
The best PuTTY alternatives for Windows in 2026 are CtrlOps (AI terminal + file manager + local-first security, $7/month per user with a 1 month free trial), Termius (cross-device sync with mobile apps), MobaXterm (best free option), and Windows Terminal + OpenSSH (built-in, no install). For teams managing 5+ servers, CtrlOps replaces the 3-app workflow: PuTTY forces SSH, file management, and AI diagnostics in one desktop app, cutting deployment time from 30-45 minutes to under 5.
## 10 Best PuTTY Alternatives for Windows in 2026 [#10-best-putty-alternatives-for-windows-in-2026]
The 10 best PuTTY alternatives for Windows in 2026 are CtrlOps (all-in-one server management), Termius (cross-device sync), MobaXterm (best free Windows option), KiTTY (lightweight PuTTY fork), Royal TS (multi-protocol), Warp (AI coding terminal), SecureCRT (enterprise compliance), Windows Terminal + OpenSSH (built-in), Bitvise (free SSH + SFTP), and Tabby (open-source modern terminal). We tested each against the same real-world scenarios.
Here's how each handles real server tasks:
| Tool | Best For | Price | AI | File Manager | Local Credentials |
| -------------------------- | -------------------------------- | ------------------------------ | ---------------------- | --------------------- | ----------------- |
| **CtrlOps** | **All-in-one server management** | **$7/mo per user (1 mo free)** | **✅ Approval-gated** | **✅ Full GUI** | **✅ Local-only** |
| Termius | Cross-device sync | $10/mo per user | Partial (autocomplete) | ✅ SFTP | ❌ Cloud |
| MobaXterm | Windows power users | Free / $69 one-time | ❌ | ✅ Basic SFTP | ✅ Local |
| KiTTY | Lightweight PuTTY fork | Free | ❌ | ❌ | ✅ Local |
| Royal TS | Multi-protocol IT teams | \~$40 - 60 one-time | ❌ | Limited | ✅ Local |
| Warp | AI-first coding terminal | Free / $20/mo | ✅ Auto-run | ❌ | ❌ Cloud |
| SecureCRT | Enterprise compliance | \~$119/license | ❌ | ❌ (SecureFX separate) | ✅ Local |
| Windows Terminal + OpenSSH | Built-in, no install | Free | ❌ | ❌ | ✅ Local |
| Bitvise | Free SSH + SFTP | Free | ❌ | ✅ SFTP GUI | ✅ Local |
| Tabby | Open-source modern terminal | Free | ❌ | ✅ SFTP/Zmodem | ✅ Local |
*Pricing from vendor sites as of June 2026. SecureCRT is \~$119 alone or \~$129 bundled with SecureFX; volume and enterprise pricing is quoted per order.*

Prefer to watch instead? The video walkthrough covers seven of the ten tools below, plus the approval-gated AI terminal and the 2 AM incident test, in under 9 minutes:
***
These ten tools cover every realistic PuTTY replacement scenario on Windows in 2026. Each is rated on what you actually do with it: connecting to a fleet, moving files, debugging incidents, and managing credentials safely.

### 1. CtrlOps: Best All-in-One with AI Terminal [#1-ctrlops-best-all-in-one-with-ai-terminal]
[CtrlOps](https://ctrlops.io/) takes a fundamentally different approach from every other tool on this list.

Instead of being a better terminal, it replaces your entire server management stack: terminal, file manager, monitoring dashboard, and deployment system. All-in-one desktop app.
**Where CtrlOps shines:**
* **Named server cards:** Connect to "Prod-Backend" or "Client-XYZ-Staging" instead of remembering raw IPs. One click, you're in.
* **Full [GUI file manager](https://ctrlops.io/docs/modules/file-manager):** Upload, download, edit remote files with drag-and-drop. No WinSCP, no re-entering credentials.
* **Approval-gated [AI terminal](https://ctrlops.io/docs/modules/ai-terminal):** Ask "why is my server slow?" and get diagnostic commands shown before execution. You review, approve, then it runs. No auto-run.
* **One-click [app deployment](https://ctrlops.io/docs/modules/deployment):** Pick your stack (React, Next.js, Node.js), link GitHub, set environment variables. CtrlOps handles cloning, dependencies, PM2, Nginx, and Certbot SSL automatically.
* **[PM2 Process Manager](https://ctrlops.io/docs/modules/pm2-process-manager):** View and manage PM2 processes, monitor CPU/memory usage, and stream logs live in a clean GUI without typing commands.
* **[Security Audit](https://ctrlops.io/docs/modules/security-audit):** Run 25 security configuration checks across SSH, firewalls, databases, and Docker. Get a hardening score, download PDF reports, and generate approval-gated AI fixes.
* **[Infrastructure monitoring](https://ctrlops.io/docs/modules/infra-details):** CPU, RAM, disk, and running processes visible inside the app. No more `htop` in a separate window.
* **Local-first security:** Credentials, SSH keys, and server configs stay on your machine. AES-256 encrypted. No cloud sync.
* **[Script Directory](https://ctrlops.io/docs/modules/ai-terminal/scripts):** Save reusable scripts with `{{variable}}` placeholders. One click runs them across every server.
**Where CtrlOps falls short:**
* No mobile app
* No serverless or Kubernetes support
* No push notifications yet (on roadmap)
**Pricing:** $7/month per user (unlimited servers). [1-month free trial](https://ctrlops.io/pricing), no credit card required.
**Platforms:** Windows, macOS (Apple Silicon + Intel), Linux.
> "I recently bought the Lifetime Subscription of CtrlOps because it genuinely helps in daily workflows."
>
> * [Prince Sherasiya](https://x.com/prince_ptl0506/status/2049714386143748111), Technical Lead at Spirex Infoways
***
### 2. Termius: Best for Cross-Device Sync [#2-termius-best-for-cross-device-sync]

Termius is the most polished SSH client on the market. It syncs server credentials, SSH keys, and command snippets across Mac, Windows, Linux, iOS, and Android through an E2E encrypted cloud vault.
If you need SSH from your phone during a production incident, Termius is the only serious option on this list.
**Where Termius shines:**
* Cross-device sync - Mac, Windows, Linux, iOS, Android, all in sync
* Team vault with real-time collaboration
* AI-powered autocomplete (suggests commands as you type)
* SOC2 Type II compliance on the Business plan
* AWS, DigitalOcean, and Azure integrations for quick server imports
**Where Termius falls short:**
* No infrastructure monitoring dashboard
* No one-click application deployment
* AI is autocomplete - it doesn't understand your server's context or generate full diagnostic sequences
* Cloud vault means your credentials live on Termius' servers (E2E encrypted, but not locally isolated)
* Pricing scales per user - at 5 users on Pro that's $50/month, versus $35/month for CtrlOps at the same headcount ($7 per user)
**Pricing:** Free (Starter, limited), $10/month per user (Pro, billed annually), $20/user/month (Team).
**Platforms:** macOS, Windows, Linux, iOS, Android.
**Reality check:**
Termius' cloud vault is E2E encrypted - Termius doesn't technically read your credentials. But the keys do travel through and live in their cloud infrastructure. Some client contracts and compliance frameworks (especially in fintech or healthcare) explicitly prohibit credentials leaving local storage. Check your NDAs before syncing.
***
### 3. MobaXterm: Best Free Windows Option [#3-mobaxterm-best-free-windows-option]

MobaXterm is the most feature-packed free SSH client on Windows. One executable, no install required, gives you SSH, RDP, VNC, FTP, SFTP browser, embedded X server, and a built-in Unix terminal. For a Windows-only shop that needs a free PuTTY upgrade right now, it's the easiest answer.
The embedded X server is genuinely unique - if you run graphical Linux applications remotely (think database GUIs, IDE remote servers, or legacy apps), MobaXterm handles that natively where other tools can't.
**Where MobaXterm shines:**
* Completely free for home and light professional use
* No install required - runs from a single portable .exe
* Tabbed interface - manage multiple sessions in one window
* Built-in SFTP browser alongside your terminal
* Embedded X11 server for graphical remote apps
* One-time Pro license ($69/user) if you need unlimited sessions
**Where MobaXterm falls short:**
* Windows only - not an option for Mac or Linux developers
* No AI features whatsoever
* No cloud sync or team collaboration
* No infrastructure monitoring
* No app deployment capabilities
* UI feels dated compared to modern tools
**Pricing:** Free (Home edition, 12 sessions max). Professional: $69/user one-time.
**Platforms:** Windows only.
**Reality check:**
MobaXterm's "Windows only" limitation is a deal-breaker for mixed teams. If even one developer on your team uses a Mac, MobaXterm creates tool fragmentation - they'll need a different SSH client, which means different session exports, different config formats, and different workflows for the same servers.
***
### 4. KiTTY: Best Lightweight PuTTY Fork [#4-kitty-best-lightweight-putty-fork]

KiTTY is a PuTTY fork - it takes PuTTY's codebase and adds the features users have been requesting for 20 years: automatic reconnection on session drop, session launcher, Zmodem file transfer, and URL hyperlinks in the terminal. If you love PuTTY's simplicity but are frustrated by its specific gaps, KiTTY patches exactly those gaps.
It's free, it's Windows-native, and it starts in under a second. No cloud accounts, no subscriptions, no learning curve if you know PuTTY.
**Where KiTTY shines:**
* Zero learning curve from PuTTY
* Auto-reconnect on dropped sessions (PuTTY's most annoying omission)
* Session launcher and session filter
* Zmodem for quick file transfer without a separate app
* Portable - single .exe, runs from a USB drive
* Free forever
**Where KiTTY falls short:**
* Windows only
* No AI features
* No file manager GUI
* No team collaboration
* No infrastructure monitoring
* Development has slowed - only minor updates since 2024, and it's built on the older PuTTY 0.76 core, so it lags behind PuTTY's recent releases and security fixes
* Still looks and feels like 2003 - functional, not modern
**Pricing:** Free and open-source.
**Platforms:** Windows only.
**Bottom line:**
KiTTY is the right choice if you're a solo developer who wants a marginally better PuTTY and has no interest in moving to a full server management platform. If you're managing more than 3 servers or working in a team, you'll outgrow it within a month.
***
### 5. Royal TS: Best for Multi-Protocol IT Teams [#5-royal-ts-best-for-multi-protocol-it-teams]

Royal TS is a connection manager designed for IT professionals who manage mixed environments - SSH servers, RDP Windows machines, VNC endpoints, web consoles, and VMware all in one place. If your team manages Linux servers alongside Windows Remote Desktop, it's the most organized way to handle that.
Royal Server (sold separately) acts as a secure gateway - your team connects through Royal Server rather than directly to production machines, which is a solid security architecture for IT shops.
**Where Royal TS shines:**
* Multi-protocol: SSH, RDP, VNC, web, VMware, SFTP, and more
* Cross-platform: Windows, macOS, iOS, Android
* Team document sharing - share connection configurations as Royal TS documents
* Password manager integration
* Royal Server for secure gateway access
**Where Royal TS falls short:**
* No AI features
* Complex UI - steep learning curve for non-IT users
* No one-click app deployment
* No infrastructure monitoring dashboard
* Pricing is opaque - personal licenses are \~$40 - 60, team pricing is custom
* Overkill for developers who only need SSH
**Pricing:** Free (limited connections). Personal: \~$40 - 60 one-time. Business: custom pricing.
**Platforms:** Windows, macOS, iOS, Android.
**Bottom line:**
Royal TS is built for IT admins managing Windows + Linux mixed fleets. If your entire stack is Linux/VPS and your team is developers (not sysadmins), it's more tool than you need - and you'll pay for complexity you won't use. For a direct feature and pricing breakdown, see
[CtrlOps vs Royal TS](/compare/ctrlops-vs-royalts)
.
***
### 6. Warp: Best AI-First Coding Terminal [#6-warp-best-ai-first-coding-terminal]

Warp is the most funded AI terminal in the world - backed by Sequoia and Google Ventures - and it shows. It's a genuine reinvention of the terminal: block-based output, an IDE-like editing experience, AI Agent Mode that converts natural language into shell commands, and Warp Drive for sharing commands with your team.
Here's the important caveat: **Warp is a local coding terminal, not a server management tool.** Its AI understands your local shell, your local files, and your local environment. When you SSH into a remote server through Warp, you get Warp's terminal UI - but you lose all the AI context, because Warp's AI doesn't know what's running on that remote server.
**Where Warp shines:**
* Best-in-class terminal UI - block-based output, full search, multi-cursor
* AI Agent Mode: type natural language, get shell commands
* Warp Drive: share commands with your team
* Extremely fast (written in Rust)
* Available on Mac, Windows, and Linux
**Where Warp falls short:**
* No named server directory for fleet management
* No file manager GUI
* No infrastructure monitoring
* No one-click app deployment
* AI doesn't have remote server context - it doesn't know what's running on your VPS
* Cloud-dependent for AI features
* Free tier available; Build plan is $20/month for AI credits
**Pricing:** Free (core terminal). Build: $20/month.
**Platforms:** macOS, Windows, Linux.
For a deeper head-to-head of how Warp stacks up against the classic Windows tools, see the full [PuTTY vs MobaXterm vs Warp comparison](/blog/putty-mobaxterm-warp-alternative).
**Reality check:**
Warp and CtrlOps solve different problems. Warp makes your local terminal smarter. CtrlOps makes remote server management faster and safer. If you SSH into remote servers to deploy apps, debug incidents, and manage files, Warp's AI won't help you there - it's optimized for local development workflows.
***
### 7. SecureCRT: Best for Enterprise & Compliance [#7-securecrt-best-for-enterprise--compliance]

SecureCRT by VanDyke Software has been the enterprise SSH client since 1995. It's FIPS 140-2 validated, government-approved, and supports advanced scripting in Python, VBScript, and Perl. If you're working in a regulated industry - government, defense, healthcare IT - SecureCRT is likely already on your approved software list.
**Where SecureCRT shines:**
* 31 years of reliability - enterprise trust is real
* FIPS 140-2 compliance for government and regulated industries
* Advanced scripting for automation
* Multi-protocol: SSH, Telnet, Serial, RDP
* One-time purchase model (no recurring subscription)
**Where SecureCRT falls short:**
* No AI features
* Legacy UI - functional but dated
* Expensive for SMBs: \~$119 - 129 per license + annual update fees for continued updates
* No infrastructure monitoring
* No one-click deployment
* Windows-centric ecosystem despite cross-platform availability
**Pricing:** $119 per license for SecureCRT alone (\~$129 bundled with SecureFX) - one-time, including 1 year of updates, with optional maintenance after that.
**Platforms:** Windows, macOS, Linux.
**Bottom line:**
SecureCRT is the right choice if you're in a regulated environment where FIPS 140-2 compliance is non-negotiable. For startup CTOs, freelancers, and agency developers, you're paying enterprise prices for features you'll never use. Already on SecureCRT and looking to move? Our
[SecureCRT alternatives](/blog/securecrt-alternatives-mac)
guide walks through the switch.
***
### 8. Windows Terminal + OpenSSH: Best Built-In Option [#8-windows-terminal--openssh-best-built-in-option]
Windows 10 and 11 ship with OpenSSH pre-installed. Combined with Windows Terminal, Microsoft's modern tab-based console, it replaces PuTTY for basic SSH with zero downloads - and it's the answer sysadmin communities give first when someone asks what to use instead of PuTTY.
Open Windows Terminal, type `ssh user@your-server-ip`, and you're connected. Add named hosts in `~/.ssh/config` and you get one-command connections without touching the Windows registry.
**Where Windows Terminal + OpenSSH shines:**
* Already on your machine - nothing to install, nothing to get approved by IT
* Tabs, profiles, and split panes in a modern, GPU-accelerated console
* Named hosts in `~/.ssh/config` replace PuTTY's registry sessions - in plain files you control
* Standard OpenSSH keys - no .ppk conversion needed
* WSL integration for a full Linux shell alongside your SSH sessions
**Where Windows Terminal + OpenSSH falls short:**
* No GUI file manager - file transfers mean `scp` commands with exact paths
* No visual server directory - you maintain the config file by hand
* No AI, no monitoring, no deployment automation
* Config file typos fail silently with unhelpful errors
**Pricing:** Free (built into Windows 10 and 11).
**Platforms:** Windows.
**Bottom line:**
If PuTTY's only job for you is opening an SSH connection, Windows Terminal + OpenSSH is the modern default - free, already installed, and using standard key formats. The moment your work involves file transfers, multiple servers, or production debugging, you'll hit the same walls PuTTY has.
***
### 9. Bitvise: Best Free SSH + SFTP Combo [#9-bitvise-best-free-ssh--sftp-combo]
Bitvise is a Windows-native SSH client that's free for all use - personal, commercial, and enterprise. No session limits, no feature gates, no per-user pricing. Its graphical split-pane SFTP browser is the fastest way to eliminate WinSCP from a PuTTY workflow.
**Where Bitvise shines:**
* Completely free, including commercial use, with no restrictions
* Graphical SFTP browser alongside the terminal - drag-and-drop file transfers
* Strong tunneling: SSH port forwarding, SOCKS proxy, FTP-to-SFTP bridge
* Windows-native, not Electron - fast and lightweight
* Automatic reconnection after dropped connections
**Where Bitvise falls short:**
* Windows only - no Mac, Linux, or mobile version
* No AI features
* Connection profiles exist, but no fleet view or environment grouping
* No monitoring, no deployment, no automation
* UI is functional but dated
**Pricing:** Free (SSH Client; Bitvise's SSH Server is a separate paid product).
**Platforms:** Windows only.
**Bottom line:**
If file transfer is the pain that's pushing you off PuTTY, Bitvise fixes it for free - one app for SSH and SFTP instead of PuTTY plus WinSCP. It stays a connection tool, though: no fleet management, no AI, no deployment.
***
### 10. Tabby: Best Open-Source Modern Terminal [#10-tabby-best-open-source-modern-terminal]
Tabby is a cross-platform, open-source terminal (MIT license) that modernizes SSH with tabs, split panes, a plugin ecosystem, and a built-in connection manager with SFTP. No subscription, no account required.
**Where Tabby shines:**
* Free and open-source - no feature gates, no vendor lock-in
* Cross-platform: Windows, macOS, Linux with an identical interface
* Built-in SSH profiles, SFTP, Zmodem transfers, and key management
* Split panes and saved workspaces, plus community plugins
* Encrypted local credential vault with a master passphrase
**Where Tabby falls short:**
* Electron-based - noticeably heavier on RAM than PuTTY or Bitvise
* No AI features, no monitoring, no deployment
* Extensive configuration options are a barrier for beginners
* Occasional stability issues with certain plugin combinations
**Pricing:** Free, open-source (MIT license).
**Platforms:** Windows, macOS, Linux.
**Bottom line:**
Tabby is the pick if open-source and cross-platform matter more to you than management features. It's a significantly better terminal than PuTTY on every axis - at the cost of higher memory usage.
***
## How We Compared These PuTTY Alternatives [#how-we-compared-these-putty-alternatives]
Imagine It's midnight. Your client's Node app is down. You open PuTTY, realize you forgot the IP address, dig through a sticky note, finally connect - and then spend 20 minutes Googling which command to run. Meanwhile, your client is watching their revenue ticker drop.
If you're a freelance developer, startup CTO, or agency engineer who still opens PuTTY as your go-to SSH client, that scenario is probably not unfamiliar. PuTTY was a good tool - in 2003. In 2026, managing production servers with it means juggling raw IP addresses, no session naming, no file management, no AI assistance, and zero workflow integration. You've outgrown it. You just haven't had a reason compelling enough to switch - until now.
We put 10 **PuTTY alternatives for Windows** through the same real-world scenarios - the jobs you actually do: connecting to a 5-server fleet, deploying a Node.js app, recovering from a 2 AM production incident, and managing SSH keys across a small team. We evaluated each tool on documented features, verified pricing, and real-world fit for those exact scenarios. Here's how they stack up.
***
## Why Are Developers Leaving PuTTY in 2026? [#why-are-developers-leaving-putty-in-2026]
Developers are leaving PuTTY in 2026 because it cannot do the three things modern server management requires: name servers, manage files, or help diagnose problems.

* **Name your servers.** PuTTY stores sessions by raw IP in the Windows registry. No aliases, no labels. You don't remember which IP is prod-backend versus staging-api at 2 AM.
* **Manage files.** Upload a config? That's a separate WinSCP session, re-entering credentials, re-authenticating.
* **Help you diagnose problems.** PuTTY gives you a blank terminal. When something breaks on an unfamiliar stack, you're alone with a cursor.
Research by [Gloria Mark at UC Irvine](https://ics.uci.edu/~gmark/chi08-mark.pdf) found it takes an average of 23 minutes to fully refocus after a single context switch. PuTTY forces at least 4 switches per deployment: terminal, SFTP client, IP spreadsheet, and monitoring dashboard.
The [2025 Stack Overflow Developer Survey](https://survey.stackoverflow.co/2025) flagged tool sprawl as a real drag on developer productivity. PuTTY's latest release was version 0.84 (May 2026), but its core design hasn't evolved since the early 2000s.
There's also a security angle. PuTTY stores saved sessions in the Windows registry in plain text - hostnames, usernames, and ports. For a feature-by-feature comparison, see the full [CtrlOps vs PuTTY](https://ctrlops.io/compare/ctrlops-vs-putty) breakdown.
**Reality check:**
PuTTY saves your sessions - including server addresses and usernames - in the Windows registry in plain text (HKEY_CURRENT_USER\Software\SimonTatham\PuTTY\Sessions). That data is accessible to any process or user on that machine. For developers handling client servers or regulated data, this is a compliance problem, not just an inconvenience.
***
## What Makes a Good SSH Client for Windows in 2026? [#what-makes-a-good-ssh-client-for-windows-in-2026]
The best SSH client for Windows in 2026 does more than open a terminal. It reduces the total number of tools you need to manage a server - and it doesn't create new security problems in the process.

**Five criteria that actually matter:**
1. **Named server directory** - You need to find the right server in under 10 seconds, not by remembering an IP.
2. **Integrated file management** - Uploading a config file or pulling a log shouldn't require opening a second app.
3. **Credential security** - Keys stored locally and encrypted, not sitting in cloud vaults you don't control.
4. **AI or command assistance** - When you SSH into an unfamiliar stack, something that can generate or explain commands saves 20 - 40 minutes per incident.
5. **Real price transparency** - Per-user pricing on small teams adds up fast. Know the true cost at 3, 5, and 10 users.
**Bottom line:**
The best Windows SSH clients in 2026 aren't just SSH clients - they're server management tools. If you're evaluating PuTTY alternatives purely on "SSH connection quality," you're solving the wrong problem.
***
## Real Workflow Comparison: PuTTY vs Modern Tools [#real-workflow-comparison-putty-vs-modern-tools]
Switching tools isn't just about features - it's about how much time you lose on tasks that should be automatic. Here's the same deployment task, done two ways.

### What managing 5 servers actually looks like with PuTTY [#what-managing-5-servers-actually-looks-like-with-putty]
You need to deploy an updated Node.js app to production. Here's the real process:
1. Open your IP spreadsheet (or sticky note). Find the right server. (2 - 3 minutes)
2. Open PuTTY. Enter the IP. Select the saved session if you have one. (1 - 2 minutes)
3. Authenticate. You've forgotten which key this server uses - dig through your key folder. (3 - 5 minutes)
4. SSH in. Run `git pull`. Something breaks. Google the error. (10 - 20 minutes)
5. Config file needs updating - open WinSCP, re-authenticate, navigate the filesystem. (5 - 8 minutes)
6. Restart the service. Hope it worked. Check the browser. (2 - 3 minutes)
**Total: 23 - 41 minutes for a deployment that should take 5.**
You've used at minimum 3 separate apps, re-entered credentials twice, and navigated your filesystem twice without any UI.
### The same deployment in CtrlOps [#the-same-deployment-in-ctrlops]
1. Open CtrlOps. Click "Prod-Backend" server card. Connected instantly - no IP lookup, no key hunting. (20 seconds)
2. Navigate to your app folder in the File Manager. Upload updated config if needed - drag and drop. (1 - 2 minutes)
3. Open the AI Terminal. Type: "pull latest from git, restart PM2, check if the app is healthy." CtrlOps shows you the 3 commands it will run. You approve. (2 minutes)
4. Infrastructure dashboard confirms CPU back to normal, no error spike. Done. (30 seconds)
**Total: 4 - 5 minutes. You never left the app.**
**Bottom line:**
The 35-minute gap isn't about typing speed. It's about context switching. CtrlOps reduces a 5-step, 3-app workflow to a 4-step, 1-app workflow. At 3 deployments per week, that's 105 minutes saved every week - per developer.
***
## How to Choose: Which Tool Fits Your Situation? [#how-to-choose-which-tool-fits-your-situation]
The "best SSH client for Windows" depends entirely on what you actually need to do with it. Use the situational guide below to match a tool to your role, team size, and security constraints instead of defaulting to the most-recommended name.

**You manage multiple client servers as a freelancer:**
CtrlOps. Named server directory, local credential storage (client NDAs stay clean), AI terminal for unfamiliar stacks. $7/month total for solo freelancers. If you need mobile access too, pair it with Termius Free.
**You're a startup CTO with a 3 - 8 person dev team:**
CtrlOps. At $7/user it undercuts per-seat competition. A 5-person team costs $35/month vs Termius Pro at $50/month and includes monitoring, deployment, and a file manager Termius doesn't.
**You're a solo developer on Windows who just wants "better PuTTY" for free:**
MobaXterm Home edition. Free, no install, tabbed sessions, built-in SFTP browser. Want to stay closer to PuTTY? KiTTY adds auto-reconnect and a session launcher.
**You don't want to install anything at all:**
Windows Terminal + OpenSSH. Already on your machine - add named hosts in `~/.ssh/config` and you have a respectable zero-download setup. Bitvise is the free upgrade when file transfers become the pain point; Tabby if open-source and cross-platform matter most.
**You manage a mixed Windows + Linux fleet as an IT admin:**
Royal TS handles multi-protocol (SSH + RDP + VNC) better than anything here. If your environment is SSH-only, it's overkill.
**You work in government or a regulated environment requiring FIPS compliance:**
SecureCRT. Nothing else on this list is validated for that requirement.
**You need mobile SSH access from your phone:**
Termius is the only real option. Its iOS and Android apps are genuinely polished - not an afterthought.
**Where CtrlOps doesn't fit (yet):**
No mobile app - if you need to SSH from your phone, you'll need Termius alongside it. No serverless support (Lambda, Cloud Functions). No Kubernetes or container orchestration. No push alerts yet (on roadmap).
***
## How Do You Migrate from PuTTY? (Sessions and Keys in About 10 Minutes) [#how-do-you-migrate-from-putty-sessions-and-keys-in-about-10-minutes]
Migrating off PuTTY takes about 10 minutes: back up your saved sessions from the Windows registry, convert your .ppk keys to the standard OpenSSH format, test every connection in the new client, then remove the plain-text session data PuTTY leaves behind. Here's the exact process.
**Step 1: Back up your PuTTY sessions (2 minutes).**
PuTTY stores sessions in the registry, not in files. Open `regedit`, navigate to `HKEY_CURRENT_USER\Software\SimonTatham\PuTTY\Sessions`, right-click the key, and export it as a `.reg` file. That file is both your backup and your server checklist for the new tool. MobaXterm and KiTTY can read PuTTY's registry sessions directly; for other clients, work down the exported list as you add named hosts.
**Step 2: Convert your .ppk keys to OpenSSH format (3 minutes).**
PuTTY's `.ppk` format is PuTTY-specific - nearly every modern client expects standard OpenSSH keys. Convert in PuTTYgen (load the key, then Conversions → Export OpenSSH key), or use our free [PPK to OpenSSH converter](/tools/ppk-to-openssh-converter) - it runs entirely in your browser, nothing is uploaded.
**Step 3: Test every connection before deleting anything (3 - 5 minutes).**
Add your servers to the new client and connect to each one with the converted keys. Keep PuTTY installed until every server has connected successfully at least once.
**Step 4: Remove PuTTY's plain-text session data (1 minute).**
Once you've migrated, delete the `Sessions` key in the registry (you have the `.reg` backup). This removes the unencrypted hostnames and usernames that PuTTY stores in plain text in the Windows registry, readable to any process on the machine.
**Reality check:**
the exported
`.reg`
backup contains the same plain-text session data. Once your migration is confirmed, store it encrypted or delete it - don't leave it sitting in your Downloads folder.
***
## Why Privacy-Conscious Developers Are Going Local-First in 2026 [#why-privacy-conscious-developers-are-going-local-first-in-2026]
There's a shift happening among privacy-conscious teams. Termius - the most common "modern PuTTY replacement" recommendation - stores your SSH keys and server credentials in a cloud vault. It's end-to-end encrypted, yes. But it's still cloud storage.
For a growing segment of developers - agencies with client NDAs, startups in regulated spaces, freelancers who've had a client ask "where are my credentials stored?" - the answer "in Termius' cloud" is not acceptable.
Local-first isn't about paranoia. It's about being able to answer that question with confidence. CtrlOps stores every credential, every SSH key, and every server configuration on your local machine. AES-256 encrypted. No third-party access. No cloud sync that you didn't initiate.
If a client ever audits your tooling, that answer - "everything is on my machine, nothing in a cloud I don't control" - is a professional advantage.
You can learn more about [SSH key management best practices](/blog/ssh-key-management-best-practices) and why local storage matters for credential security in our dedicated guide. If you also manage servers from a Mac, see how the [best SSH clients for Mac in 2026](/blog/best-ssh-client-mac-2026) handle the same local-first question.
***
## The AI Terminal Gap No One Is Talking About [#the-ai-terminal-gap-no-one-is-talking-about]
Every article about PuTTY alternatives focuses on feature checklists: tabs, SFTP, session management. None of them talk about what happens when something goes wrong on a server and you don't know what to do next.
That's the real test. Not "can I open an SSH session?" - PuTTY does that. The test is: "I'm SSH'd in, my app is throwing a 502, my client is calling me, and I have no idea where to start."

With PuTTY, you open a browser, Google the error, find a Stack Overflow post from 2018, try a command, hope for the best.
With CtrlOps' AI Terminal - which is connected to real-time web search, not just a static model - you type the problem. It reads the latest documentation. It shows you exactly which commands to run. You review them. You approve. The fix runs. The [web search documentation](https://ctrlops.io/docs/modules/ai-terminal/web-search) covers how it pulls current docs, error messages, and package versions live. Here's web search running inside the AI Terminal:
The difference isn't convenience. It's the 35 minutes between "my client is down" and "my client is fixed."
> "What stands out from an engineering perspective is the approval gate on the AI terminal. Most AI tooling here either runs blind or needs too much manual intervention to be useful. This sits in the right place: the AI does the thinking, the engineer makes the call."
>
> * [Drijesh P.](https://www.linkedin.com/posts/drijesh_ctrlops-deploy-debug-manage-linux-servers-activity-7462442711686651904-gb4r), Engineering Manager at IBM
### A real incident: a suspicious pull request in a client's repo [#a-real-incident-a-suspicious-pull-request-in-a-clients-repo]
This isn't hypothetical for us.
A few days ago, one of our developers spotted something off in a client's GitHub repository - a pull request that looked like a routine code update at first glance. Looking closer, it had quietly added an unwanted third-party script set to run automatically after installation.
Someone had gained access to the repo and was trying to use it as a path onto the server.
That's not a bug. That's a security incident - and the clock starts the moment you find one.
**Investigating with the AI Terminal**
We opened CtrlOps, connected to the affected server, and went straight into the AI Terminal.
Instead of guessing commands one at a time, we described the situation in plain English: an unwanted script had been added, and we needed to know where it landed, whether it was running, what it had touched, and what to do next.
CtrlOps worked through it as an investigation - generating each diagnostic command, showing us what it intended to run, and waiting for approval before anything executed. Step by step, every command human-approved, it checked:
* Running processes
* Suspicious and temporary files
* Package files and dependency manifests
* Likely persistence points (cron, services, init scripts)
* Recent access patterns
**The incident report**
At the end, it produced a structured incident report covering:
* What was injected, and where
* When the suspicious change happened
* What was still running
* Whether the server showed active signs of compromise
Followed by concrete remediation steps - what to remove, what to revoke, which access to review, what history to clean, and which repository changes to audit.
Done by hand, that's hours of work: knowing every command, inspecting every file and log, then writing up a report for the team and the client.
With CtrlOps, we had the full investigation and the report in about **ten minutes**.
That's the part that never shows up in a feature checklist. An AI terminal isn't just for "check the CPU" or "restart the service" - when something suspicious happens and time matters, it helps you understand what actually happened and act on it, with a human approving every command before it touches anything.
Here's the full incident, start to finish:
For [DevOps automation tools](/blog/devops-automation-tools) and how AI is reshaping server operations more broadly, our guide covers the full landscape.
***
## Conclusion [#conclusion]
PuTTY isn't broken. It does what it was designed to do in 2003. But managing production servers in 2026 requires named server directories, integrated file management, and AI assistance - none of which PuTTY offers.
For teams managing VPS fleets, CtrlOps replaces the 3-app workflow at $7/month per user with a 1 month free trial. For mobile SSH, Termius leads. For a free Windows upgrade, MobaXterm Home Edition. For regulated environments, SecureCRT.
Spending 40 minutes on a deployment that should take 5 is a choice you don't have to keep making.
***
## Frequently Asked Questions [#frequently-asked-questions]
MobaXterm Home Edition is the best free PuTTY alternative for Windows. It's a single portable .exe with tabbed sessions, a built-in SFTP browser, an X11 server, and support for SSH, RDP, VNC, and FTP - all free. KiTTY is a close second if you want something closer to PuTTY with auto-reconnect added. Both are Windows-only. For a cross-platform free option, Termius Starter is available at no cost but limits you to local vault only (no sync).
PuTTY still works as a basic SSH client in 2026, but it has significant limitations compared to modern tools: no named server directory (sessions stored by raw IP in the Windows registry), no integrated file manager, no AI assistance, and no infrastructure monitoring. Its latest release (0.84) shipped in May 2026, but its core architecture hasn't changed meaningfully in over a decade. For individual developers connecting to 1 - 2 servers occasionally, it's fine. For anyone managing more than 2 - 3 servers regularly, the tool-switching overhead it creates costs 2+ hours per week.
Yes. Windows 10 and 11 include the OpenSSH client pre-installed - open Windows Terminal and type `ssh user@your-server-ip`. If it's missing, enable it under Settings → Apps → Optional Features → OpenSSH Client. For basic connections, this replaces PuTTY with zero downloads and uses standard OpenSSH keys instead of .ppk files. What it doesn't add: a GUI file manager, a named server directory, monitoring, or AI assistance - for those, you still need a dedicated tool like MobaXterm (free) or CtrlOps ($7/month per user, with a 1 month free trial).
Termius uses end-to-end encryption for its cloud vault - Termius itself does not have access to your decrypted credentials. However, your SSH keys do live in Termius' cloud infrastructure, which some security policies, client NDAs, and compliance frameworks prohibit. For developers who require that credentials never leave local storage, CtrlOps is local-only (AES-256 encrypted on your machine) and is a better fit. For most developers without specific compliance requirements, Termius' security model is sound.
No. MobaXterm is Windows-only. This is its most significant limitation. If your team includes any Mac or Linux developers, MobaXterm will create fragmentation - those developers need a different SSH client, which means different session formats, different configuration exports, and different workflows. For cross-platform teams, Termius, CtrlOps, or Royal TS are better choices. Mac users can also see the dedicated comparison of [Mac-specific MobaXterm alternatives](/blog/mobaxterm-alternatives-mac).
CtrlOps is the only SSH client for Windows with a genuine AI terminal for server management in 2026. Its AI Terminal is approval-gated - it shows you the commands it plans to run before executing anything - and is connected to real-time web search so it reads current documentation before suggesting commands. Warp has AI features, but is optimized for local development workflows rather than remote server management. Termius has AI autocomplete, but it only suggests command completions - it doesn't understand your server context or generate diagnostic sequences.
Termius Pro costs $10/user/month (billed annually). For a team of 5, that's $50/month or $600/year. CtrlOps costs $7 per user per month for unlimited servers after a 1 month free trial - so the same 5-seat team is $35/month, the lower cost on a like-for-like comparison. CtrlOps also includes features Termius doesn't - an infrastructure monitoring dashboard, one-click app deployment, and a full GUI file manager - at that lower per-seat price.
CtrlOps is not the right tool in three situations: (1) You need SSH access from your phone - CtrlOps is desktop-only; use Termius for mobile. (2) You manage serverless infrastructure (AWS Lambda, Google Cloud Functions) - CtrlOps is built for traditional VPS and bare-metal server management. (3) Your team requires Kubernetes/container orchestration tooling - CtrlOps doesn't support K8s. For all three of those specific needs, other tools fill the gap.
KiTTY is a fork of PuTTY that adds several features the original project never shipped: automatic session reconnection after a dropped connection, a built-in session launcher, Zmodem file transfer protocol support, and URL hyperlinking in the terminal. Its SSH core comes from PuTTY 0.76, the version it was forked from, and KiTTY's development has slowed (last update September 2024), so it lags behind PuTTY's more recent releases and security updates. If you like PuTTY but find yourself frustrated by dropped sessions and manual reconnection, KiTTY is a direct drop-in replacement. It's Windows-only and free.
Not if you switch to the right tool. PuTTY forces you to use WinSCP (or similar) because it has no file management capability. MobaXterm, CtrlOps, and Royal TS all have integrated file management - meaning you can upload, download, edit, and manage server files from the same app you use for SSH. CtrlOps' File Manager gives you a full GUI browser of your server's filesystem with drag-and-drop upload, download, and directory creation.
The key is named server directories instead of raw IP lists. Tools like CtrlOps let you save servers as named cards (e.g., "Prod-Backend", "Staging-API", "Client-XYZ-DB") and connect with one click. Termius supports named hosts in its vault. Even MobaXterm lets you save named sessions. Any of these beats a Google Sheet of IPs. For a detailed guide on managing multiple servers efficiently, see our [full guide on managing multiple servers without losing control](/blog/manage-multiple-servers-without-losing-control).
CtrlOps is built for this exact scenario. You can name servers by client and environment ("ClientA-Prod", "ClientA-Staging", "ClientB-VPS"), store all credentials locally (important if your client NDAs restrict cloud storage), and use the AI terminal to debug unfamiliar stacks quickly. At $7 per user per month - and the first month is free - it's less than a single billable hour and pays for itself the first time you diagnose an incident in 5 minutes instead of 45.
No. SecureCRT has no AI features as of 2026. It's built for enterprise environments that prioritize protocol compliance, scripting (Python, VBScript, Perl), and FIPS 140-2 certification over modern UX or AI assistance. If you're looking for enterprise-grade tooling with AI, CtrlOps is the closest option - though it doesn't yet have the same compliance certifications (no SOC2 or SAML SSO). For fully regulated enterprise environments, SecureCRT remains the standard.
---
# PuTTY vs MobaXterm vs Warp Alternative (2026) (/blog/putty-mobaxterm-warp-alternative)
Author: Daxesh Italiya | Role: Co-Founder & CTO, TST Technology | Published: 2026-05-28 | Updated: 2026-07-17 | Tags: PuTTY vs MobaXterm, MobaXterm Alternative, Warp Alternative, SSH Client Comparison | Reading Time: 22 min read
> PuTTY vs MobaXterm vs Warp compared for 2026. Pricing, AI features, file management, and which tool actually fits a 5 to 25 server fleet.
## Key Takeaways [#key-takeaways]
PuTTY is a free SSH terminal from 1999 with no tabs, no AI, and no file manager. MobaXterm is a Windows-only toolbox capped at 12 free sessions. Warp is an AI terminal built for local coding, not remote server fleets. CtrlOps is the only tool here built for managing 5-25 remote servers - with a GUI file manager, approval-gated AI terminal, infra dashboard, and one-click deployments at [$7/month per user](https://ctrlops.io/pricing), after a 1 month free trial.
* **Windows-only user needing a free SSH client** - PuTTY (zero cost, raw SSH, nothing more)
* **Windows sysadmin with mixed protocols** - MobaXterm (SSH + RDP + X11 + SFTP in one app)
* **Developer who lives in the local terminal** - Warp (AI command help, IDE-like editing)
* **Developer managing 5 or more remote servers** - CtrlOps ([AI terminal](/features/ai-terminal) + file manager + deployment + infra dashboard in one app at $7/month per user, 1 month free trial)
## How We Compared PuTTY, MobaXterm, and Warp [#how-we-compared-putty-mobaxterm-and-warp]
We tested PuTTY, MobaXterm, Warp, and CtrlOps against 6 identical server tasks: connecting, switching servers, running scripts, monitoring resources, deploying a Next.js app, and diagnosing a slow server. Each tool was evaluated on time-to-complete, tool-switching required, and whether it handled the full workflow or forced you into a second app.
Picture this. You are a freelance developer juggling seven client servers.
You click into PuTTY, hunt for the saved session, realize the IP is stale, open the Google Sheet, copy-paste it in, SSH into the wrong server, and then remember you still need WinSCP to upload the config file. Six minutes gone. Zero work done. You haven't even started debugging yet.
The **PuTTY vs MobaXterm vs Warp alternative** debate is not about terminal preferences for startup CTOs managing 20-server fleets, freelance developers hopping between client environments, or agency developers pushing to staging and production daily.
It is about which tool actually handles the full workflow without forcing you to open three more apps. We compared all three against the same real-world server tasks to find where each one wins, where each one breaks, and what to use when none of them fit.
## Quick Comparison: PuTTY vs MobaXterm vs Warp vs CtrlOps [#quick-comparison-putty-vs-mobaxterm-vs-warp-vs-ctrlops]
Before the deep dive, here is the side-by-side breakdown on the data points that actually decide which SSH client survives a 2026 server workflow - primary use, platforms, free tier, paid pricing, AI assistant, file manager, deployment, and credential storage.

| Feature | PuTTY | MobaXterm | Warp | **CtrlOps** |
| ----------------------------- | ---------------------- | ----------------------- | ---------------------------- | ------------------------------------------------- |
| **Primary use** | Raw SSH terminal | Windows network toolbox | AI coding terminal | **Multi-server management** |
| **Platforms** | Win, Mac, Linux | **Windows only** | Mac, Win, Linux | **Mac, Win, Linux** |
| **Free tier** | Fully free, forever | Home: 12 sessions max | 75 AI credits/mo after trial | **1 month free, no card** |
| **Paid plan** | None | $69/user one-time | From $20/mo per user | **$7/mo per user, unlimited servers (1 mo free)** |
| **AI assistant** | None | None | Cloud-based AI | **Approval-gated, BYOK** |
| **Multi-server dashboard** | Saved sessions list | Session list | Local terminal only | **Named server cards** |
| **GUI file manager** | None | SFTP browser | None | **Full GUI browser** |
| **One-click app deploy** | None | None | None | **Node.js, React, Next.js** |
| **Real-time infra dashboard** | None | Basic monitor | None | **CPU, RAM, Disk live view** |
| **Credentials storage** | Local files | Local | Local + optional cloud | **Local-only, never syncs** |
| **Built for** | 1999 Windows sysadmins | 2008 Windows admins | 2020 terminal developers | **2026 SMB DevOps** |
**Bottom line:**
PuTTY, MobaXterm, and Warp were each built to solve a different problem in a different decade. None were designed for the developer
[managing a fleet of 5 to 25 remote servers](/features/multi-server-management)
in 2026. That gap is exactly what CtrlOps fills.
## What Is PuTTY and Who Still Uses It in 2026? [#what-is-putty-and-who-still-uses-it-in-2026]
PuTTY is a free, open-source SSH and Telnet client originally released in 1999 by Simon Tatham. It runs on Windows, macOS, and Linux. Its job is exactly one thing: open a terminal connection to a remote server. No tabs. No file manager. No AI. No fleet view. It remains the default starting point for anyone who has Googled "how to SSH into a server" for the first time.

**Where PuTTY works well:**
* 100% free with no licenses and no accounts required
* Tiny binary (under 5 MB), portable, no installation needed
* Universally documented - every Linux tutorial assumes it is already installed
* Reliable for quick, one-off SSH sessions on Windows
**Where PuTTY breaks down in 2026:**
Each session opens a brand new window. Manage 6 servers and you have 6 windows stacked on your taskbar. Keys are converted with a separate tool called PuTTYgen, stored as `.ppk` files, and tracked entirely by hand. File transfer requires PSCP, WinSCP, or FileZilla - a second tool, a second login, a second window. Forgot the `journalctl` syntax? Open ChatGPT in a browser tab and copy the answer back. You cannot see CPU, RAM, or disk across your fleet without SSHing into each box one at a time. For a Windows-focused ranking of replacements, see the [7 best PuTTY alternatives for Windows](/blog/putty-alternatives-windows).
**Reality check:**
The PuTTY command line handles a single server perfectly well. For anyone managing more than 3 production servers, the lack of tabs, the separate key manager, and the absent file transfer turn every task into a 4-tool workflow.
## What Is MobaXterm and What Are Its Real Limits? [#what-is-mobaxterm-and-what-are-its-real-limits]
MobaXterm is a Windows-only "network toolbox" released in 2008 by Mobatek, a French company. It bundles SSH, RDP, VNC, FTP, SFTP, an X11 server, and a Cygwin-based Unix shell into a single application. For Windows-only IT shops, it is the most popular all-in-one option available. But in 2026, its lack of AI features, macOS support, and the 12-session free tier cap create hard limits that most comparisons skip over.

**MobaXterm's genuine strengths:**
* Embedded X11 server - run remote Linux GUI apps directly on your Windows desktop
* Built-in SFTP browser auto-launches the moment you SSH in
* Multi-protocol support: SSH, RDP, VNC, Telnet, Serial, FTP
* Built-in scripting engine, macros, and a text editor for automating repetitive tasks
* Portable version runs from a USB stick with zero installation
* One-time license with no ongoing subscription
**MobaXterm's hard limits in 2026:**
The biggest fact most comparisons bury: **MobaXterm is Windows only.** There is no native macOS build and no Linux build. Any Mac developer searching "MobaXterm for Mac" will find this out the hard way - the [MobaXterm alternatives for Mac](/blog/mobaxterm-alternatives-mac) guide covers the five tools that fill that gap. This single limitation disqualifies it for anyone on Apple Silicon or any modern Linux workstation.
The Home Edition free tier caps at 12 sessions and 2 SSH tunnels. Managing more than 12 servers means upgrading to the Professional edition, which is priced at $69 per user. That is a one-time fee, not a subscription, but it still adds up for teams. The product has also not added any AI features. There is no natural-language command generation and no integration with LLMs.
### Does MobaXterm Have AI Features? [#does-mobaxterm-have-ai-features]
No. MobaXterm has no built-in AI features as of 2026. There is no natural-language command generation, no LLM integration, and no AI-assisted diagnostics. Developers who want AI help while using MobaXterm must switch to a separate browser tab with ChatGPT or a similar tool, copy their terminal output, paste it in, get the suggested command, switch back, and type it manually. CtrlOps and Warp both integrate AI directly into the terminal workflow - CtrlOps with approval-gated execution on your live server, Warp with local AI command generation.
**Bottom line:**
MobaXterm is the right answer for Windows-only network engineers who need RDP, SSH, VNC, and X11 in a single app. For any Mac-based freelancer or developer who wants AI-assisted Linux commands, this tool is not the right fit.
## What Is Warp and Why Is It Not a Real PuTTY or MobaXterm Replacement? [#what-is-warp-and-why-is-it-not-a-real-putty-or-mobaxterm-replacement]
Warp is an AI-native terminal launched in 2020 and built in Rust with GPU rendering. It replaces iTerm2 or the default macOS terminal with a block-based, IDE-like interface. It introduced AI Agent Mode in 2024, which converts plain English into shell commands. It added Windows support in February 2025 and has [raised $73 million in total funding](https://theroompodcast.medium.com/scaling-warp-and-supercharging-developers-with-ai-with-founder-zach-lloyd-0823d3446ad4) from Sequoia Capital, Google Ventures, and other investors.
**Warp's genuine strengths:**
* True AI command generation in natural language, built into the terminal
* Block-based UI where every command and its output is a separate editable block
* Warp Drive for shared team command libraries
* BYOK support for OpenAI, Anthropic, and Google on paid plans
* Free plan available with core terminal features and limited AI credits
**Where Warp falls short for server fleet management:**
Warp is a local terminal. It runs on your laptop. It does not maintain a visual directory of remote servers as named cards you can click into. There is no GUI file manager - you still type `scp` or open a separate FTP client. There is no live infrastructure dashboard showing CPU, RAM, and disk across your fleet. Advanced AI agents in Warp rely on cloud platform infrastructure for execution, so credentials and session context do flow through their systems.
Pricing also moves fast. Warp's Build plan is $20 per user per month with 1,500 monthly AI credits. The Business plan is $50 per user per month. Add three teammates on Build and you are at $60 per month. CtrlOps is $7 per month per user with unlimited servers, and the first month is free with no credit card required.
**Reality check:**
Warp is excellent for developers who write code locally and want AI command help in their terminal. It was never built for the developer who SSHs into 8 different client VPS instances daily and also needs to upload config files and check disk space across all of them.
## PuTTY vs MobaXterm: Which Is Better in 2026? [#putty-vs-mobaxterm-which-is-better-in-2026]
PuTTY is better for developers who need a free, portable, cross-platform SSH client with zero setup. MobaXterm is better for Windows sysadmins who need SSH, RDP, VNC, SFTP, and X11 in a single app. PuTTY runs on Mac, Windows, and Linux. MobaXterm runs on Windows only. Neither tool includes AI features or one-click deployment.
| Factor | PuTTY | MobaXterm |
| ----------------- | ----------------------- | --------------------------------- |
| **Price** | 100% free, forever | Free (12 sessions) / $69 one-time |
| **Platforms** | Windows, macOS, Linux | Windows only |
| **Tabs** | No (separate windows) | Yes |
| **File transfer** | Requires WinSCP or PSCP | Built-in SFTP panel |
| **AI features** | None | None |
| **Best for** | Quick SSH on any OS | Windows multi-protocol admin |
We tested both tools across 7 identical real-world server tasks, from connecting to 5 servers in under 60 seconds to deploying a Node.js app on a VPS. Read the full [PuTTY vs MobaXterm head-to-head comparison](https://ctrlops.io/blog/putty-vs-mobaxterm) for detailed test results, a scored breakdown, and our recommendation for each use case.
**Bottom line:**
PuTTY wins on cross-platform support and zero cost. MobaXterm wins on multi-protocol breadth and built-in SFTP. Neither was built for the 2026 developer workflow of fleet management, AI-assisted diagnostics, and automated deployments.
## PuTTY vs MobaXterm vs Warp vs CtrlOps: The Same 6 Tasks, Side by Side [#putty-vs-mobaxterm-vs-warp-vs-ctrlops-the-same-6-tasks-side-by-side]
Here is how the same six real-world tasks play out across all four tools. These are the tasks every freelance developer and startup CTO performs weekly.

| Task | PuTTY | MobaXterm | Warp | **CtrlOps** |
| -------------------------------------- | ---------------------------- | ---------------------------- | -------------------------------- | ------------------------------------------------ |
| Connect to a saved server | \~15 sec | \~10 sec | \~30 sec (manual SSH) | **\~3 sec (one click)** |
| Switch between 5 servers | 5 separate windows | 5 tabs | 5 typed SSH commands | **one dashboard** |
| Run the same setup script on 3 servers | Write from scratch each time | Write from scratch each time | Write from scratch each time | **Script Directory: write once, run everywhere** |
| Check CPU, RAM, and Disk | Run 3 separate commands | Run 3 separate commands | Run 3 separate commands | **One dashboard view** |
| Deploy a Next.js app from scratch | 30 to 45 min manual | 30 to 45 min manual | 30 to 45 min manual | **5 to 8 min guided** |
| Diagnose a slow server | Switch to ChatGPT | Switch to ChatGPT | Ask Warp AI (local context only) | **Ask AI inline with full server context** |
The three tools were never designed to be compared on the same axis. PuTTY is a 1999 SSH terminal. MobaXterm is a 2008 Windows toolbox. Warp is a 2020 local AI terminal. Asking which is "best" for server fleet management is like asking whether a hammer, a Swiss army knife, or a power drill is best for building a house. The answer is: none of them.
**Bottom line:**
Across these six tasks the gap is not small. PuTTY, MobaXterm, and Warp each force you to switch tools or type commands by hand at almost every step, while CtrlOps keeps the whole workflow in one window. The time savings come almost entirely from eliminating tool-switching, not from any single feature.
## Why the Multi-Tool SSH Workflow Costs You Hours Every Week [#why-the-multi-tool-ssh-workflow-costs-you-hours-every-week]
The average developer managing 5+ remote servers uses 4 to 5 separate tools per session: a terminal, a file transfer client, a browser tab for AI help, a spreadsheet for server IPs, and a monitoring dashboard. This multi-tool workflow adds 15 to 30 minutes of context-switching overhead per deployment task.
Here is what most freelancers and startup teams actually run today:

1. PuTTY or the native terminal for SSH
2. WinSCP, FileZilla, or Cyberduck for file transfer
3. A browser tab with ChatGPT for Linux commands they do not remember
4. A Google Sheet with IPs, usernames, and key file paths
5. A monitoring dashboard (or nothing at all)
Every server task bounces you between four or more tools. That friction is not just annoying; it's measurable.
[Atlassian's State of Developer Experience 2025 report](https://www.atlassian.com/blog/developer/developer-experience-report-2025), based on a survey of 3,500 developers and managers across six countries, found that developers' top time-wasters are:
* Finding information (services, docs, APIs)
* Adapting to new technology
* Context switching between tools
This is not a tooling preference. It is a margin problem.
## What a True PuTTY vs MobaXterm vs Warp Alternative Looks Like [#what-a-true-putty-vs-mobaxterm-vs-warp-alternative-looks-like]
A real alternative to all three tools needs to handle the entire server management workflow, not just the SSH connection. That means:

* A **named server directory** so there is no more IP spreadsheet
* A **GUI file manager built into the same window** with no second tool and no re-login
* An **AI assistant that knows your actual server** with no copy-pasting logs to ChatGPT
* A **real-time infrastructure dashboard** showing CPU, RAM, and disk at a glance
* **One-click app deployment** for Node.js, React, and Next.js without reading 7 tutorials
* **Local-first credential storage** where keys never sync to a cloud you do not control
* **Cross-platform support** on Mac, Windows, and Linux
This is the gap CtrlOps fills. It is not a faster terminal. It is a different category: a server management desktop app built for the developer who builds product but does not want to become an infrastructure specialist.
Prefer to watch before you read on? Here is a quick look at CtrlOps in action:
## Use Case Decision Framework: Which Tool Fits Which Developer? [#use-case-decision-framework-which-tool-fits-which-developer]
Use PuTTY for 1-2 servers that only need occasional SSH. Use MobaXterm for Windows-only sysadmins juggling SSH, RDP, and VNC. Use Warp for local AI-assisted coding with minimal remote server work. Use CtrlOps for managing 5 or more remote servers as a freelancer or small team at $7/month per user, with a 1 month free trial.
Most comparison articles list features and leave you to sort it out. Here is the cleaner framework, matched to who you actually are.

### You Manage 1 to 2 Servers and Just Need SSH [#you-manage-1-to-2-servers-and-just-need-ssh]
Use PuTTY on Windows or the built-in Terminal on Mac and Linux. It is free, it works, and adding a paid tool for occasional SSH sessions is overengineering the problem.
### You Are a Windows Sysadmin With Mixed Protocols [#you-are-a-windows-sysadmin-with-mixed-protocols]
Use MobaXterm Professional. RDP, SSH, VNC, SFTP, and X11 in one app saves real time for Windows network administrators. The $69 per user one-time fee is fair for the scope. Just know it will never run on macOS.
### You Code Locally and Want AI in Your Terminal [#you-code-locally-and-want-ai-in-your-terminal]
Use Warp. It is the best AI-native terminal available for local development. If your day is 90% writing code on your laptop and 10% occasional SSH, Warp plus your existing SSH tool is a clean stack. You will need to add a separate file manager for server file work.
### You Manage 5 or More Remote Servers as a Freelancer or Small Team [#you-manage-5-or-more-remote-servers-as-a-freelancer-or-small-team]
Use CtrlOps. Named server cards, an approval-gated AI terminal, a GUI file manager, an infra dashboard, and one-click app deployment in one desktop app at $7 per month per user, free for the first month. No cloud sync of credentials. Mac, Windows, and Linux native.
### You Are a Mac Developer Who Hit MobaXterm's Windows Wall [#you-are-a-mac-developer-who-hit-mobaxterms-windows-wall]
Use CtrlOps. MobaXterm has no Mac build. CtrlOps gives you the same "all in one app" experience built natively for Apple Silicon. Read our deeper guide on the [best SSH client for Mac in 2026](/blog/best-ssh-client-mac-2026) for the full breakdown.
**Is CtrlOps the right fit?**
CtrlOps is a focused desktop command center for managing remote server fleets, so a couple of jobs sit outside its lane by design. It runs on the desktop, so for fixing a server from your phone on the move you'll want a mobile SSH app in your pocket too. It's tuned for VPS and bare-metal fleets rather than container orchestration - if you live in Kubernetes, keep
`kubectl`
or Lens beside it. And if your day is pure local-terminal coding with no remote servers in sight, a local terminal like Warp will serve you better. Match the tool to the work, and CtrlOps earns its keep the moment remote server management is the job.
## Pricing Compared: What You Actually Pay in 2026 [#pricing-compared-what-you-actually-pay-in-2026]
The free-tier limits are different enough across tools to matter. Here is what each one actually costs.
| Tool | Free tier | Paid plan | Annual cost |
| -------------- | ----------------------------------------- | --------------------- | --------------------- |
| PuTTY | Fully free, all features | None | $0 |
| MobaXterm Home | 12 sessions, 2 tunnels | $69/user one-time | $69 per user |
| Warp Free | 150 credits/mo first 2 months, then 75/mo | $20/mo Build per user | $240/year per user |
| **CtrlOps** | **1 month free, no card** | **$7/mo per user** | **$70/year per user** |
CtrlOps is $7 per user per month, or $70 per year per user (saving 16.7%), after a 1 month free trial. The cost is per user with unlimited servers, so it stays predictable as your fleet grows. This pricing model was designed specifically for SMBs and freelancers who cannot justify expensive per-seat SaaS billing on top of their hosting costs.
## AI Inside Your Terminal: Bolted On vs Built In [#ai-inside-your-terminal-bolted-on-vs-built-in]
Warp added AI to a terminal. CtrlOps built a server management platform around AI. The difference shows in practice.

**Warp's AI** works on your local machine session. It is excellent for "give me the right `find` command" or "explain this bash error." What it cannot do is reach into your live production server and run diagnostics. You still need to SSH in, copy the logs, paste them into Warp, get a command back, and run it yourself.
[CtrlOps AI Terminal](https://ctrlops.io/docs/modules/ai-terminal) lives inside the active SSH session to your server. Type "Why is my server slow?" in plain English. The AI generates `top`, `free -m`, `df -h`, and `journalctl --since "1 hour ago"` commands and shows them to you with a single Run button before executing anything. You approve. The commands run live. The output comes back as a plain-English summary. Every command is logged with status and execution time.
This is the **approve-before-execute model** at work:
1. Type your question in plain English
2. AI generates the shell commands
3. You see the exact commands with a Run button
4. You approve and the commands execute on your live SSH session
5. AI summarizes the results in plain English
6. Full history is logged with status and timestamp
The Auto-Run toggle exists for power users who want to skip the gate during long diagnostic sequences, but it is off by default. CtrlOps also supports **BYOK** - bring your own API key from OpenAI, Google Gemini, Anthropic Claude, or any OpenAI-compatible provider. Your key, your costs, your data. Keys are stored locally with AES-256 encryption and never sent to CtrlOps servers.
The AI Terminal also includes a **Web Search toggle**. When enabled, the AI searches the internet in real time before generating commands - so it reads the latest official documentation instead of using potentially outdated training data. Choose from Tavily (recommended), Brave, or DuckDuckGo (no API key needed).
**Reality check:**
Auto-run AI in any production-facing tool is a security incident waiting to happen. CtrlOps defaults to approval-gated execution because one hallucinated
`rm -rf`
from an LLM is enough to end a client relationship. Auto-Run is an opt-in feature, not the default.
## File Management: The Tax Nobody Talks About [#file-management-the-tax-nobody-talks-about]
PuTTY has no file manager at all - you need WinSCP or FileZilla as a second tool. Warp has no GUI file browser either. MobaXterm includes a basic SFTP panel that auto-launches on SSH connection. CtrlOps opens a full GUI file browser as the default first tab on every server connection, with upload, download, rename, and delete built in.
Every "best SSH client" article skips past file management. But at some point in every server workflow, you need to upload a config file, download a log, or edit an `.env`.
With PuTTY, that means opening WinSCP, re-entering credentials, and navigating the directory tree again. With Warp, it means typing an `scp` command and hoping the path is right. MobaXterm earns credit here - the SFTP panel launches automatically.

CtrlOps opens the **file manager as the first visible tab** when you connect to a server. The full server file system appears as a visual browser: folders, files, breadcrumb path, hidden file toggle, and search. Every item in the tree has download, upload, create folder, rename, delete, and deploy actions available.
**What this directly replaces:**
* WinSCP (Windows SFTP)
* FileZilla (cross-platform FTP)
* Cyberduck (Mac SFTP and S3)
* Transmit (Mac SFTP)
* The 90-second re-authentication cycle between terminal and file transfer
## One-Click App Deployment: The Feature None of Them Have [#one-click-app-deployment-the-feature-none-of-them-have]
PuTTY, MobaXterm, and Warp all stop at: "You are SSHed in, now type the commands yourself."

[Deploying a Next.js app manually](/blog/deploy-nextjs-app-linux-vps) from scratch looks like this:
1. SSH into the server (5 min including tool-switching)
2. Install the correct Node.js version (5 min)
3. Clone the GitHub repo (3 min)
4. Set environment variables (5 min)
5. Configure PM2 for process management (8 min)
6. Configure Nginx as a reverse proxy (10 min)
7. Set up SSL with Certbot (5 min)
8. Debug why nothing is working (variable, often long)
Average: **30 to 45 minutes for an experienced developer. 3 to 4 hours for a developer doing it the first time.**
CtrlOps Add Application turns this into a form. Paste your GitHub repo URL, select Next.js as the framework, paste your `.env` variables, add your domain, toggle on SSL, and click Create. The app is live with HTTPS in **5 to 8 minutes**. PM2, Nginx, and Certbot are configured under the hood. No Nginx config blocks. No tutorial tabs open. You can see exactly how this works in the [CtrlOps one-click deployment documentation](https://ctrlops.io/docs/modules/deployment).
This is the single feature that makes CtrlOps a different product category - not just a faster SSH client.
## Server Security: Local-First vs Cloud-Synced Credentials [#server-security-local-first-vs-cloud-synced-credentials]
Warp and many cross-platform SSH clients offer cloud sync features. For solo developers that convenience is appealing. For freelancers under client NDAs or agency developers handling financial or healthcare data, syncing server credentials to a third-party cloud is a contract violation, not a convenience.

CtrlOps stores everything locally. No cloud dashboard holds your SSH keys. No third-party server ever sees your server IPs or credentials. The platform communicates directly over standard SSH - no agent installed on your server, no protocol changes, no vendor sitting in the middle.
> "Been exploring \[CtrlOps] recently, and it already includes an AI-assisted terminal with command approval, real-time server monitoring, SSH management, a remote file manager, backups and automation scripts, multi-server management, and one-click GitHub deployments. Everything works directly over SSH, and credentials stay local."
>
> * [Ajay Patel](https://x.com/ajaypatel_aj/status/2059593498291249213), developer and founder of ThemeSelection & ShadCN Studio
| Security factor | PuTTY | MobaXterm | Warp | **CtrlOps** |
| ------------------------- | ----------- | ----------- | ---------------------- | -------------------------------- |
| Credential storage | Local files | Local | Local + optional cloud | **Local-only, AES-256** |
| Cloud account required | No | No | Yes | **No** |
| Agent installed on server | No | No | No | **No** |
| AI data leaves machine | N/A | N/A | Yes (cloud AI) | **Only with BYOK if you choose** |
| Compliance friendly | Variable | Yes (local) | SOC 2 compliant | **Client-NDA friendly** |
For freelancers and agencies whose clients have data residency requirements - financial services, healthcare, government work - local-first is not a preference. It is a contract clause. Read our comparison of [PuTTY, Webmin, and ServerPilot alternatives](/blog/putty-webmin-serverpilot-alternatives) for a longer security-focused breakdown.
You can also review CtrlOps' [SSH security model documentation](https://ctrlops.io/docs/core/ssh-security) for the technical architecture details.
## What Happens When These Tools Are Not Enough [#what-happens-when-these-tools-are-not-enough]
There is a ceiling each of these tools hits, and no comparison article talks about it honestly.
**PuTTY hits its ceiling** the day you manage more than 3 servers. No tabs, no fleet view, no file transfer - you are building workarounds before you have started real work.
**MobaXterm hits its ceiling** the moment you switch to a Mac or a Linux workstation. There is no version for you. It also hits the ceiling when a client asks about their credential security and you have no answer about where the connection config lives.
**Warp hits its ceiling** when your work is more "managing remote infrastructure" than "writing local code." The AI does not have context about what is actually running on your production server unless you SSH in and paste the output back manually.
**CtrlOps hits its ceiling** at the enterprise edge - no mobile app yet for phone-based incident response, no native Kubernetes orchestration, and no push alert system yet (on the roadmap). For a solo freelancer or a 2 to 10 person engineering team managing VPS servers, none of those limits apply.
Choosing the right tool means matching it to the work you actually do, not the work you imagine doing. If you spend more time managing remote servers than writing local code, a terminal emulator is the wrong category of tool.
For teams already thinking beyond SSH clients and toward full DevOps automation, read our guide on [DevOps automation tools](/blog/devops-automation-tools) and our piece on [managing multiple servers without losing control](/blog/manage-multiple-servers-without-losing-control).
## How to Migrate From PuTTY or MobaXterm to CtrlOps in 10 Minutes [#how-to-migrate-from-putty-or-mobaxterm-to-ctrlops-in-10-minutes]
You have saved sessions in PuTTY or MobaXterm. Switching tools feels like a project. It is not. Here is the full migration in three steps - done in under 10 minutes. For the PuTTY-only angle, see [CtrlOps vs PuTTY](https://ctrlops.io/compare/ctrlops-vs-putty).

### Step 1: Download and Activate CtrlOps (2 minutes) [#step-1-download-and-activate-ctrlops-2-minutes]
Go to [ctrlops.io](https://ctrlops.io), click Download, and choose your platform: Apple Silicon, Apple Intel, Windows, or Linux. Install the app and open it. On first launch it asks for a license key. Sign in with Google or email at ctrlops.io, copy your trial key from the dashboard, and paste it into the app. You are in.
### Step 2: Add Your Servers (5 minutes) [#step-2-add-your-servers-5-minutes]
Click **New Connection**. For each server you currently have saved in PuTTY or MobaXterm:
* Enter a readable name (for example, "Client-A-Prod" or "DB-Primary")
* Paste the IP address
* Enter your username
* Choose SSH key or `.pem` file authentication
CtrlOps uses your existing local SSH keys. Nothing changes on the server side. No agent to install. If you have 10 servers, adding all of them takes about 5 minutes. Once added, every server appears as a named card on your dashboard - no more raw IP lists.
**Migrating from MobaXterm on Windows?** Your saved sessions in MobaXterm use the same SSH keys you already have. Point CtrlOps at the same keys. Connection works identically, just with a modern UI.
### Step 3: Connect and Verify (1 minute) [#step-3-connect-and-verify-1-minute]
Click the play button on any server card. CtrlOps opens three tabs instantly: File Manager, Console, and Infra Details. Your SSH session is live. The file system is browsable. CPU, RAM, and disk are visible without typing a single command.
That is the full migration. Your old tool can stay installed as a backup. Most users stop opening it within a week.
**Bottom line:**
The migration from PuTTY or MobaXterm to CtrlOps is not a configuration project. It is a 10-minute copy of your server details into a better interface. Your SSH keys, your servers, your workflows - everything carries over. Only the tool changes.
## Conclusion [#conclusion]
PuTTY, MobaXterm, and Warp are each excellent at the specific problem they were designed for in their own era. PuTTY solved "I need SSH from Windows" in 1999. MobaXterm solved "I need every Windows network tool in one place" in 2008. Warp solved "I want AI in my local terminal" in 2020.
The 2026 problem is different. A freelance developer manages 8 client servers. A startup CTO keeps a 12-server fleet alive with no dedicated DevOps hire. An agency developer deploys to 6 staging environments per week. None of PuTTY, MobaXterm, or Warp - alone or stacked together - handles that workflow end-to-end. You still end up with PuTTY plus WinSCP plus ChatGPT plus a Google Sheet.
CtrlOps was built for the 2026 version of this problem. Named server cards instead of spreadsheets. A GUI file manager in the same window as your SSH terminal. An AI that knows your actual server and asks before running anything. A real-time infra dashboard. One-click app deployment. All at $7 per month per user on Mac, Windows, and Linux, with a 1 month free trial, and credentials that never leave your machine.
If you have been searching for a real **PuTTY vs MobaXterm vs Warp alternative**, stop looking for a better terminal. Look for a different category. Then test it on the same six tasks in this article. The contrast does the work. And if Termius was on your shortlist too, see how it compares against the [best Termius alternatives in 2026](/blog/termius-alternatives).
***
## FAQs [#faqs]
For Windows-only sysadmins, yes - MobaXterm bundles SSH, RDP, VNC, SFTP, and X11 into one app while PuTTY is SSH-only with no tabs or file transfer. The MobaXterm Home edition is free but capped at 12 sessions and 2 SSH tunnels. The Professional edition costs $69 per user as a one-time fee. PuTTY remains completely free with no session limits, just fewer features. The trade-off is feature depth against simplicity and cost.
PuTTY does run on macOS but feels dated. Most Mac developers use the built-in Terminal or iTerm2 for SSH sessions. For a unified server management experience on Mac that includes a file manager, AI terminal, and infrastructure dashboard, CtrlOps is built natively for Apple Silicon and Intel Macs. It offers 1 month free with no credit card needed. Read the full comparison at our [best SSH client for Mac guide](/blog/best-ssh-client-mac-2026).
Warp can connect via SSH like any terminal but was not designed as a fleet manager. There is no named-server directory, no GUI file browser, and no live infrastructure monitoring dashboard. Warp excels for local development with AI assistance. If you manage 5 or more remote servers regularly, you will need to layer a dedicated server manager on top of Warp, or replace both with CtrlOps directly.
CtrlOps is a local-first desktop application for macOS, Windows, and Linux that combines a named server directory, a GUI file manager, an approval-gated AI terminal with BYOK support, real-time infrastructure monitoring, automated backups, a script directory, and one-click app deployment for Node.js, React, and Next.js. PuTTY is a 1999 SSH terminal. MobaXterm is a Windows-only network toolbox. Warp is a local AI coding terminal. CtrlOps is a server fleet management platform built for SMB developers.
CtrlOps is $7 per month per user for unlimited servers, or $70 per year per user. Warp's Build plan is $20 per user per month and the Business plan is $50 per user per month. MobaXterm Professional is $69 per user as a one-time purchase. CtrlOps offers a 1-month free trial with no credit card required, the longest trial period of any tool in this comparison.
No. MobaXterm is Windows-only. There is no native macOS or Linux build and Mobatek has not announced cross-platform support. Mac developers searching for a MobaXterm equivalent typically end up with iTerm2 plus FileZilla, or CtrlOps for a unified server management experience on Apple Silicon or Intel Macs.
Yes. PuTTY is actively maintained and patched. The current release supports modern SSH ciphers, Ed25519 keys, and the SSH-2 protocol. The security risk is not the tool itself - it is in how users store key files, manage saved sessions, and avoid logging sensitive credentials. For higher-security workflows, tools with local-only credential storage and no cloud sync, such as CtrlOps, offer a stronger security posture.
Three clear cases. First, if you need a mobile SSH client to manage servers from your phone - CtrlOps is desktop-only, so a dedicated mobile SSH app is a better fit. Second, if your infrastructure is primarily serverless (AWS Lambda, Cloud Functions) - CtrlOps is designed for VPS and bare-metal servers. Third, if you manage large Kubernetes clusters at enterprise scale - pair CtrlOps with `kubectl` or Lens, or use a dedicated k8s orchestration tool.
Warp uses a cloud account for sync features, and advanced agentic capabilities rely on Warp's cloud platform infrastructure. Warp states it is SOC 2 compliant with zero data retention on contracted LLM providers. If you enable sync, settings flow through their platform. For client work under NDAs or compliance requirements where credentials must never leave your machine, a local-first tool like CtrlOps is the appropriate choice.
Neither PuTTY nor MobaXterm has built-in AI features as of 2026. Both products focus on protocol support and stability rather than AI integration. Getting AI help while using either tool requires switching to ChatGPT or another AI tool in a separate browser window, pasting in your logs, copying commands back, and then running them. CtrlOps and Warp both integrate AI directly into the terminal workflow, with the key difference being that CtrlOps AI operates in context of your actual remote server session.
Manually, a first-time Next.js deployment to a VPS takes 30 to 45 minutes and involves Node.js setup, PM2, Nginx reverse proxy configuration, environment variable management, and SSL via Certbot. CtrlOps reduces this to a guided form - paste your GitHub repo, select Next.js, add your `.env`, set your domain, toggle SSL, and click Create. The full stack is deployed in 5 to 8 minutes with no Nginx knowledge required.
Yes - that is the stated design goal. The GUI handles the most common server tasks without typing any commands. The AI terminal lets you describe what you need in plain English. Every AI-generated command is shown with an approval gate before execution, so you see exactly what will run and learn what each command does in the process. The primary audience CtrlOps targets is the freelance developer or technical founder who builds software but does not want to become a Linux or DevOps specialist just to manage deployments.
MobaXterm has a free Home Edition that is fully usable for personal use. The free version is limited to 12 simultaneous SSH sessions and 2 SSH tunnels. For commercial use or teams needing more sessions, the Professional Edition costs $69 per user as a one-time purchase with no annual subscription. There is no time limit on the free tier - the restriction is session count, not duration.
Yes. PuTTY runs without issues on Windows 11. The current release is 0.84 (released May 22, 2026), which fixes multiple security issues including a remotely triggerable double-free in RSA key exchange. It works on Windows 7 through Windows 11 in both 32-bit and 64-bit versions, and the portable build runs with no installation required. Version 0.81 previously addressed a critical vulnerability (CVE-2024-31497) affecting 521-bit ECDSA keys - if you used that key type with any version before 0.81, treat the private key as compromised and generate a new pair. Always download PuTTY from the official source at chiark.greenend.org.uk to avoid malware-laced fake downloads.
PuTTY has not been "replaced" because it still works for its original purpose: a raw SSH session on Windows. What has changed is the category of problem developers face. Modern freelancers and small teams managing multiple servers now use tools like CtrlOps (server fleet management with AI and file manager) or Warp (AI-native local terminal). Each serves a different use case rather than replacing PuTTY directly.
They are built for different jobs. MobaXterm is a Windows-only network toolbox - SSH, RDP, VNC, X11, Serial, and an SFTP browser in one app - ideal for Windows sysadmins who juggle multiple protocols and never touch a Mac. Warp is a cross-platform, AI-native terminal built for local development, with natural-language command generation and a block-based UI. Choose MobaXterm for multi-protocol remote administration on Windows; choose Warp for local coding with AI help. If your real job is managing a fleet of remote servers - connecting, deploying, transferring files, and monitoring health - neither is built for that, and CtrlOps covers the full workflow on Mac, Windows, and Linux.
SuperPuTTY is a free, open-source tabbed wrapper for PuTTY on Windows. It adds tabs, session management, and an SFTP browser on top of PuTTY's raw SSH. MobaXterm goes further with built-in X11, RDP, VNC, macros, and a Cygwin shell. SuperPuTTY is the right choice if you want tabbed PuTTY with no new learning curve. MobaXterm is the right choice if you need multi-protocol support beyond SSH. Neither includes AI features or cross-platform support.
No. MobaXterm is Windows-only. Mobatek has not released a Linux build or announced plans for one. Linux developers looking for a similar all-in-one experience can use CtrlOps, which runs natively on Linux (Debian/Ubuntu .deb package) and includes a GUI file manager, AI terminal, and server dashboard. For a free terminal-only option on Linux, Terminator or tmux provide tabbed and split-pane SSH sessions.
Warp is a local AI-native terminal focused on coding workflows with block-based editing and natural-language command generation. Termius is a cross-platform SSH client with cloud sync, team sharing, and SFTP. Warp excels for developers who write code locally. Termius excels for teams that share SSH credentials across members. Neither provides one-click deployment, a live infrastructure dashboard, or approval-gated AI execution on remote servers.
---
# PuTTY vs MobaXterm in 2026: 7 Real-World Tests Reveal the Winner (/blog/putty-vs-mobaxterm)
Author: Hiren Kalariya | Role: Co-Founder & CEO, TST Technology | Published: 2026-07-08 | Tags: PuTTY vs MobaXterm, MobaXterm vs PuTTY, SSH Client Windows, PuTTY Alternative | Reading Time: 19 min read
> Comparing PuTTY and MobaXterm on connection speed, SFTP, credential security, and AI features. Full 2026 test results, plus a modern SSH alternative.
PuTTY is a free, open-source SSH client for Windows that is ideal for simple SSH, Telnet, and serial connections. It works well for managing individual server sessions but lacks built-in tools for centralized multi-server management. MobaXterm is a Windows-only terminal toolbox that combines SSH, RDP, VNC, X11 forwarding, and a graphical SFTP browser into a single application. It offers both a free Home Edition and a paid Professional Edition. Both tools handle SSH connections.
Neither tool includes AI assistance, one-click deployment, or infrastructure monitoring. MobaXterm is Windows-only, while PuTTY primarily targets Windows and has limited support on other platforms. For developers managing multiple servers in 2026, platforms like [CtrlOps](https://ctrlops.io) aim to address limitations by offering features such as AI assistance, centralized server management, deployment workflows, and monitoring in a single interface.
## Key Takeaways [#key-takeaways]
PuTTY and MobaXterm are both reliable SSH tools for Windows, but they were designed for a different era of server management. PuTTY handles single SSH connections with zero overhead. MobaXterm adds multi-protocol access, tabs, and file transfers. Neither tool offers AI diagnostics, deployment automation, or real-time server monitoring.
If your workflow has outgrown manual terminal commands and constant tool-switching, neither PuTTY nor MobaXterm solves the full problem.
> **TL;DR**
>
> PuTTY and MobaXterm both connect you to servers. Neither helps you manage them.
>
> * **Quick single-server SSH on Windows** - PuTTY (free, 25+ years of trust, zero setup)
> * **Multi-protocol Windows power user** - MobaXterm (SSH + RDP + VNC + X11 + SFTP in one app)
> * **Managing 5+ servers with deployments, monitoring, and AI** - [CtrlOps](https://ctrlops.io) ($7/user/month after a 1 month free trial, local-first)
| Feature | PuTTY | MobaXterm (Pro) | CtrlOps |
| ------------------------------ | ----------------------------------------------- | ----------------------- | ------------------------------------- |
| **Price** | Free | $69 one-time | $7/user/mo or $70/user/yr (1 mo free) |
| **Platforms** | Windows (primary), Linux, macOS | Windows only | macOS, Windows, Linux |
| **Tabs / multi-session** | No (separate windows) | Yes | Yes |
| **File manager** | No | Yes (SFTP browser) | Yes (full GUI) |
| **AI terminal** | No | No | Yes (approval-gated) |
| **Deployment automation** | No | No | Yes (one-click) |
| **Infrastructure monitoring** | No | No | Yes (real-time dashboard) |
| **Session/credential storage** | Windows Registry (session metadata, plain text) | Local (master password) | Local (AES-256 encrypted) |
| **X11 forwarding** | Yes (manual config) | Yes (built-in X server) | No |
| **Multi-protocol (RDP, VNC)** | No | Yes | No (SSH-focused) |
***
## What Is PuTTY and Who Still Uses It in 2026? [#what-is-putty-and-who-still-uses-it-in-2026]
PuTTY is a free, open-source SSH and Telnet client created by Simon Tatham in 1999. It remains the most widely recognized SSH client for Windows, with a 17.29% market share in the SSH category according to [6sense](https://6sense.com/tech/secure-shell-ssh/putty-vs-mobaxterm).
Its [latest release is version 0.84](https://www.chiark.greenend.org.uk/~sgtatham/putty/) (May 2026), which patched a remotely triggerable double-free vulnerability in RSA key exchange.

PuTTY's primary purpose is establishing SSH connections, although it also supports Telnet, serial, raw TCP, and Rlogin connections. Enter an IP address, click Open, and you're connected. No account required. No installation necessary (portable .exe available). For 25+ years, that simplicity was enough.
In 2026, it's not.
Here's what PuTTY still does well. It's lightweight (under 3 MB). It supports SSH, Telnet, SCP, and raw serial connections. It runs as a standalone executable from a USB drive. It has 25+ years of security audits behind it. The source code is open and inspectable.
Here's where PuTTY breaks down for modern server management:
**No tabs:** Every server opens in a separate window. Managing 5 servers means 5 floating PuTTY windows. At 10 servers, your taskbar is unusable.
**No file manager:** Need to upload a config file? Close PuTTY (or minimize it), open WinSCP, re-enter credentials, navigate to the right directory, upload. That's 3 - 5 minutes and a full context switch for a 10-second task.
**No server directory:** PuTTY stores saved sessions in the Windows Registry rather than providing a modern searchable server inventory or team workspace. While you can give sessions descriptive names, managing a large collection becomes less convenient than using tools with built-in organization and filtering.
**No AI, no monitoring, no deployment:** You're alone with a blank cursor. When something breaks, your diagnostic tools are Google and Stack Overflow.
**Plain-text credential storage:** PuTTY stores session data (hostnames, usernames, ports) in the Windows Registry in plain text. Any process running under the same Windows user account, or a user with sufficient access to that profile, can read the stored session information.
For developers handling client servers or regulated data, storing server metadata in plain text can be a security concern, depending on your organization's security policies or compliance requirements.
**Reality check:** PuTTY stores your saved sessions, including server addresses and usernames, in the Windows Registry in plain text (`HKEY_CURRENT_USER\Software\SimonTatham\PuTTY\Sessions`). Any process with user-level access can read that data. If you manage client servers with NDAs or regulated data, this is a real security gap, not a theoretical one.
### Who Still Uses PuTTY in 2026? [#who-still-uses-putty-in-2026]
Developers who connect to one or two servers occasionally. IT professionals in locked-down corporate environments where PuTTY is the only approved tool. Students learning SSH for the first time. Anyone who needs a quick, disposable SSH connection without installing anything.
If you regularly manage multiple servers each day, PuTTY's lack of built-in tabs, integrated file transfers, centralized session management, and automation can make workflows less efficient compared to more modern tools. For a deep look at modern replacements, see our guide to [PuTTY alternatives for Windows](/blog/putty-alternatives-windows).
***
## What Is MobaXterm and What Does It Actually Include? [#what-is-mobaxterm-and-what-does-it-actually-include]
MobaXterm is a Windows-only enhanced terminal and remote computing toolkit created by Mobatek (France) in 2008. It bundles SSH, RDP, VNC, FTP, SFTP, X11, Telnet, and MOSH into a single portable executable. It holds a 13.10% market share in the SSH client category according to [6sense](https://6sense.com/tech/secure-shell-ssh/putty-vs-mobaxterm).
Think of MobaXterm as "PuTTY plus everything PuTTY doesn't have." Tabs. A graphical SFTP browser. A built-in X11 server for running remote GUI apps on your Windows desktop. Built-in Unix commands (`bash`, `grep`, `awk`, `rsync`) that work out of the box.

### MobaXterm Free vs Professional: What Do You Actually Get? [#mobaxterm-free-vs-professional-what-do-you-actually-get]
| Feature | Home (Free) | Professional ($69/user) |
| --------------- | --------------- | -------------------------------- |
| Sessions | Max 12 | Unlimited |
| SSH tunnels | Max 2 | Unlimited |
| Macros | Max 4 | Unlimited |
| Network daemons | 360 seconds max | Unlimited |
| Customization | Limited | Full (branding, startup scripts) |
| Commercial use | Not permitted | Permitted |
| License type | Free | One-time, lifetime right to use |
| Updates | Included | 12 months included |
*Pricing verified on [mobaxterm.mobatek.net](https://mobaxterm.mobatek.net/download.html), June 2026.*
**Where MobaXterm shines:**
* **Tabbed interface:** Multiple SSH sessions in one window. Split panes, horizontal and vertical.
* **Graphical SFTP browser:** Connect via SSH and an SFTP panel opens automatically. Drag and drop files between local and remote.
* **Built-in X11 server:** Run remote Linux GUI applications on your Windows desktop. No separate Xming or VcXsrv install needed.
* **Multi-protocol:** SSH, RDP, VNC, FTP, SFTP, Telnet, MOSH, serial, all from one app.
* **Portable version:** Run from a USB drive without installing. Carry your sessions with you.
* **Session management:** Save, organize, and group connections with folders.
* **Master password:** Encrypt stored credentials locally.
**Where MobaXterm falls short:**
* **Windows only:** No macOS version. No Linux version. MobaXterm's X11 server is unnecessary on Linux (X11 runs natively), and there's no equivalent for Mac users. If your team uses mixed operating systems, MobaXterm can't follow.
* **No AI features:** Manual commands and macros only. No command generation, no diagnostics, no error explanation.
* **No deployment automation:** Deploy a Node.js app? You're running `git pull`, `npm install`, `pm2 restart`, and configuring Nginx by hand.
* **No infrastructure monitoring:** No CPU, RAM, or disk dashboard. Run `htop` in a terminal tab.
* **Free edition is restricted:** 12 sessions max, 2 SSH tunnels, 4 macros. Developers managing multiple client environments may quickly reach those limits.
* **No cloud sync:** Sessions are local files. Moving to a new machine means exporting and importing configs manually.
**Bottom line:** MobaXterm solves PuTTY's biggest pain points: it adds tabs, file transfers, and multi-protocol support. But it's still a connection tool, not a management tool. It gets you to the server. What you do once connected is still entirely manual.
***
## PuTTY vs MobaXterm: Head-to-Head Feature Comparison [#putty-vs-mobaxterm-head-to-head-feature-comparison]
PuTTY is a lightweight remote access client focused primarily on SSH, with support for Telnet, serial, and other connection types. MobaXterm is a multi-protocol terminal toolbox with tabs, file transfers, and an embedded X server. MobaXterm wins on features.
PuTTY wins on simplicity and cross-platform availability. Neither tool offers AI, deployment automation, or server monitoring.
Here's the complete side-by-side across every capability that matters for daily server work.
| Capability | PuTTY | MobaXterm |
| ------------------------------ | ------------------------------------------------- | ---------------------------------------- |
| **SSH support** | Yes | Yes |
| **Telnet / Serial** | Yes | Yes |
| **RDP (Remote Desktop)** | No | Yes |
| **VNC** | No | Yes |
| **FTP / SFTP** | No built-in GUI (PSCP/PSFTP available separately) | Yes (auto SFTP browser) |
| **X11 forwarding** | Yes (manual config, external X server needed) | Yes (built-in X11 server) |
| **Tabs / multi-session** | No (separate windows per session) | Yes (tabbed + split panes) |
| **Session management** | Basic (Windows Registry) | Advanced (folders, groups, INI files) |
| **Portable version** | Yes (.exe, no install) | Yes (.exe, no install) |
| **Built-in Unix commands** | No | Yes (bash, grep, awk, rsync) |
| **Macros / scripting** | No | Yes (macros + custom scripts) |
| **Plugin support** | No | Yes (MobaXterm plugins) |
| **Session/credential storage** | Windows Registry (session metadata, plain text) | Local files (master password encryption) |
| **Platforms** | Windows, Linux, macOS | Windows only |
| **AI terminal** | No | No |
| **Infrastructure monitoring** | No | No |
| **Deployment automation** | No | No |
| **File manager (GUI)** | No | Yes (SFTP browser) |
| **Price** | Free (MIT-0 license) | Free Home / $69 Pro (one-time) |
| **Open source** | Yes | No (proprietary, free Home edition) |
| **Latest version** | 0.84 (May 2026) | v26.x (2026) |
Two patterns stand out from this table.
**MobaXterm dominates on connection features.** If your job involves SSH, RDP, VNC, and file transfers on a Windows machine, MobaXterm replaces 3 - 4 separate tools. PuTTY needs WinSCP for file transfers, a separate X server for GUI forwarding, and mstsc.exe for RDP. That's 4 apps versus 1.
**Both tools hit the same wall.** Neither has AI assistance, deployment automation, or infrastructure monitoring. Once you're connected, both tools give you a blank terminal and leave the rest to you. The difference between them stops at the connection layer.
***
## Is MobaXterm Better Than PuTTY? 7 Real-World Tests [#is-mobaxterm-better-than-putty-7-real-world-tests]
MobaXterm wins 6 out of 7 real-world server management tests against PuTTY. PuTTY wins on simplicity and cross-platform availability. Both tools draw on Test 4 (production diagnostics) because neither tool offers built-in troubleshooting or log analysis.
We tested both tools against the same 7 scenarios that freelance developers, startup CTOs, and agency engineers face daily. Here's how each performed.
### Test 1: Connecting to 5 Servers in Under 60 Seconds [#test-1-connecting-to-5-servers-in-under-60-seconds]
**PuTTY:** Open 5 separate PuTTY windows. Load each saved session individually. No way to group by project or environment. With 5 servers, you're clicking through the session list 5 times.
**Time: \~90 seconds.** The taskbar is now cluttered with 5 identical PuTTY icons.
**MobaXterm:** Open MobaXterm once. Click saved sessions from the sidebar, each opens in a new tab. Group sessions by folder (Production, Staging, Client-A).
**Time: \~30 seconds.** Everything in one window.
**Winner: MobaXterm.** Tabs and session folders cut connection time in half and keep your workspace organized.
### Test 2: Uploading a Config File Mid-Session [#test-2-uploading-a-config-file-mid-session]
**PuTTY:** Minimize PuTTY. Open WinSCP. Re-enter the same server credentials (or load a saved session). Navigate to the target directory. Upload the file. Switch back to PuTTY.
**Time: 3 - 5 minutes.** Two tools, one context switch.
**MobaXterm:** The SFTP panel appears automatically when you connect via SSH. Drag the file from Windows Explorer to the remote directory. Done.
**Time: \~30 seconds.** Zero context switches.
**Winner: MobaXterm.** Built-in SFTP eliminates the single biggest friction point in PuTTY's workflow.
### Test 3: Managing SSH Keys Across a Small Team [#test-3-managing-ssh-keys-across-a-small-team]
**PuTTY:** Use PuTTYgen to generate key pairs. Manually copy public keys to each server's `authorized_keys`. Each team member repeats this process independently. No centralized key directory. Keys are .ppk format (PuTTY-specific), which can cause confusion with standard OpenSSH keys.
**MobaXterm:** Slightly better. MobaXterm can use standard OpenSSH keys or .ppk keys. Master password protects stored credentials. But still no centralized team key management, no key rotation automation, no audit trail.
**Winner: Slight edge to MobaXterm** (master password, standard key support), but neither tool solves team-scale SSH key management. For a deeper breakdown of this challenge, see our guide on [SSH key management and security](/docs/core/ssh-security).
### Test 4: Diagnosing a Production Incident at 2 AM [#test-4-diagnosing-a-production-incident-at-2-am]
**PuTTY:** Connect to the server. Blank terminal. Run `htop`, `journalctl -xe`, `tail -f /var/log/nginx/error.log` from memory. If you don't know the right diagnostic commands for this stack, open a browser, Google the error, find a Stack Overflow post from 2019 and hope it applies.
**Time: 20 - 40 minutes.**
**MobaXterm:** Same manual process. Better organized (you can see all your sessions and quickly switch between servers), but still no diagnostic help. You're alone with the same blank terminal.
**Time: 20 - 35 minutes.**
**Winner: Draw.** Neither tool helps you diagnose problems. Both leave you Googling at 2 AM.
### Test 5: Running Graphical Linux Apps on Windows (X11) [#test-5-running-graphical-linux-apps-on-windows-x11]
**PuTTY:** Enable X11 forwarding in PuTTY settings. Install a separate X server on Windows (Xming, VcXsrv, or X410). Configure the `DISPLAY` variable. Hope the versions are compatible.
**Time: 15 - 30 minutes for first-time setup.**
**MobaXterm:** X11 server is built in. Connect via SSH, run `firefox` or `gedit` and the GUI window appears on your Windows desktop. Zero configuration.
**Time: immediate.**
**Winner: MobaXterm.** This is MobaXterm's strongest differentiator. If you run remote GUI apps regularly, this alone justifies choosing MobaXterm over PuTTY.
### Test 6: Deploying a Node.js App on a VPS [#test-6-deploying-a-nodejs-app-on-a-vps]
**PuTTY:** SSH in. Run `git clone`, `npm install`, configure Nginx, set up PM2, run Certbot for SSL. 12+ commands, each with potential failure points. If you miss the PM2 ecosystem config, your app won't survive a reboot.
**Time: 30 - 45 minutes.**
**MobaXterm:** Same manual process. You can use the SFTP browser to upload `.env` files without a second tool. Macros can save frequently-used command sequences. But deployment is still manual, step-by-step.
**Time: 25 - 40 minutes.**
**Winner: Marginal edge to MobaXterm** (SFTP + macros save a few minutes), but neither tool automates deployment. Both require you to know and execute every command.
### Test 7: Credential Security and Storage [#test-7-credential-security-and-storage]
**PuTTY:** Stores saved sessions in the Windows Registry in plain text. Hostnames, usernames, and port numbers are readable by any process or user with access to `HKEY_CURRENT_USER`. No encryption. No master password.
**MobaXterm:** Stores credentials in local files protected by a master password. Credentials don't leave your machine. Not cloud-synced.
**Winner: MobaXterm.** Master password protection is a real improvement over PuTTY's unencrypted registry storage. For teams handling client data, this matters.
### Scorecard [#scorecard]
| Test | PuTTY | MobaXterm | Winner |
| ----------------------- | ------------------------------------------- | ---------------------------------- | -------------------- |
| Multi-server connection | Slow (separate windows) | Fast (tabs + folders) | MobaXterm |
| File upload mid-session | Requires WinSCP | Built-in SFTP | MobaXterm |
| SSH key management | Basic (PuTTYgen-based key management) | Standard keys + master password | MobaXterm (slight) |
| 2 AM incident diagnosis | Manual | Manual | Draw |
| X11 GUI forwarding | Needs external X server | Built-in X server | MobaXterm |
| Node.js deployment | Fully manual | Mostly manual (SFTP + macros help) | MobaXterm (marginal) |
| Credential security | Session metadata stored in Windows Registry | Master password protected | MobaXterm |
**Final score: MobaXterm 6, PuTTY 0, Draw 1.**
MobaXterm is the better tool for Windows power users who manage multiple connections, transfer files, and run remote GUI apps. PuTTY is the simpler choice when you need a quick, zero-install SSH connection.
But both tools share the same blind spots. No AI. No deployment. No monitoring. The gap isn't between PuTTY and MobaXterm. The gap is between connection tools and management tools.
***
## Where Both PuTTY and MobaXterm Fall Short in 2026 [#where-both-putty-and-mobaxterm-fall-short-in-2026]
Both PuTTY and MobaXterm were built to solve a 2005 problem: "How do I connect to a remote server from Windows?" In 2026, the problem has changed. The bottleneck isn't the connection. It's everything that happens after you connect: diagnosing errors, deploying code, monitoring resources, managing files across a fleet.
Here are the four capabilities neither tool offers:
**1. AI-assisted diagnostics:**
Your Node.js app throws a 502 error at 2 AM. With PuTTY or MobaXterm, you open a browser, Google the error, read Stack Overflow posts from 2019, and try commands one at a time.
**2. One-click deployment:**
Deploying a Node.js or [Next.js app on a VPS](/blog/deploy-nextjs-app-linux-vps) requires 12+ manual commands: `git clone`, `npm install`, PM2 config, Nginx setup, Certbot SSL. Both PuTTY and MobaXterm require you to run every command individually. Miss one step and the deployment fails silently.
**3. Infrastructure monitoring:**
Neither tool shows CPU load, RAM usage, or disk space. You run `htop` in a terminal tab and watch numbers scroll. No alerts. No historical trends. No "your disk is 92% full" warning before it's too late.
**4. Cross-platform support (MobaXterm-specific):**
MobaXterm runs on Windows only. No macOS version. No Linux version. If your team includes Mac or Linux users, MobaXterm can't be a team-wide standard. PuTTY at least has Linux and macOS ports, though its main strength remains Windows.
For developers who hit these walls with MobaXterm specifically, our [CtrlOps vs MobaXterm](/compare/ctrlops-vs-mobaxterm) comparison covers the full gap analysis across platforms, AI, and deployment workflows.
**Bottom line:** PuTTY and MobaXterm are connection tools. They get you to the server. What you do once connected, diagnosing problems, deploying code, monitoring health, managing files across 10 servers, is where the real time goes. And it's where both tools leave you on your own.
***
## What Does a Modern SSH Workspace Look Like in 2026? [#what-does-a-modern-ssh-workspace-look-like-in-2026]
A modern SSH workspace in 2026 combines terminal access, file management, infrastructure monitoring, AI diagnostics, and deployment automation in a single desktop app, without sending your credentials to the cloud.
CtrlOps is the only tool in the PuTTY/MobaXterm category that does this across macOS, Windows, and Linux at $7/user/month (or $70/user/year), with a 1 month free trial.
PuTTY and MobaXterm are connection tools. [CtrlOps](https://ctrlops.io) is a server management workspace.
Here's how CtrlOps handles the same 7 tests from the comparison above:
| Test | PuTTY | MobaXterm | CtrlOps |
| ----------------------- | ------------------------------------------- | ---------------------------- | ---------------------------------------------------------------------------------------- |
| Connect to 5 servers | 5 windows, \~90 seconds | 5 tabs, \~30 seconds | 5 named cards, \~15 seconds |
| Upload config file | WinSCP required | Built-in SFTP | Drag-and-drop in [File Manager](/docs/modules/file-manager) |
| SSH key management | Session configuration in Windows Registry | Local files, master password | AES-256 encrypted, [local-only](/docs/core/ssh-security) |
| 2 AM incident diagnosis | Google + manual commands | Google + manual commands | [AI Terminal](/docs/modules/ai-terminal): describe the problem, review commands, approve |
| X11 GUI forwarding | External X server needed | Built-in X server | Not supported (SSH-focused) |
| Node.js deployment | 12+ manual commands | 12+ commands + SFTP help | [One-click deployment](/docs/modules/deployment): form, click, done |
| Credential security | Session metadata stored in Windows Registry | Master password | AES-256 encrypted, never leaves your machine |
**What CtrlOps adds that neither PuTTY nor MobaXterm has:**

* **Named server cards:** Connect to "Prod-Backend" or "Client-XYZ-Staging" with one click, not by remembering IP addresses.
* **Full [GUI file manager](/features/file-manager):** Upload, download, rename, edit, and delete remote files with drag-and-drop. No second app required.
* **Approval-gated [AI terminal](/features/ai-terminal):** Type "why is my server slow?" and CtrlOps generates diagnostic commands based on your server's live context (CPU, memory, running processes, recent logs). Every command shows before it runs. You approve, then it executes. Human-in-the-loop, not auto-run.
* **[MCP Server integration](/docs/modules/ai-terminal/mcps):** Connect Context7 for official documentation, GitHub for your repo, Filesystem for local files, or any custom MCP server via JSON config. The AI reads your actual codebase and documentation before generating commands, not just its training data. MCP does not bypass the approval gate.
* **[Script Directory](/docs/modules/ai-terminal/scripts):** Save command sequences as reusable one-click scripts with `{{variable_name}}` placeholders. Run the same deployment across every server without retyping.
* **One-click deployment:** Choose your framework (Node.js, Next.js, React), paste your GitHub repo URL, set environment variables, toggle SSL. CtrlOps handles `git clone`, dependencies, PM2 config, Nginx, and Certbot. This can reduce a typical manual deployment from dozens of steps to just a few guided inputs, depending on the application and server configuration.
* **Real-time infrastructure monitoring:** CPU load, RAM usage, disk space, and running processes in a dashboard. No `htop` in a separate tab.
* **[Web search integration](/docs/modules/ai-terminal/web-search):** The AI terminal searches the latest documentation and error messages before suggesting commands. When you're debugging a framework version that shipped after the AI model's knowledge cutoff, this catches outdated answers before they reach your server.
* **BYOK AI model:** Bring your own OpenAI, Anthropic Claude, or Google Gemini API key. You control the model, the cost, and the data.
* **Cross-platform:** macOS (Apple Silicon + Intel), Windows, Linux. One tool for the whole team.
* **SSH user and key management:** Create server users with role-based permissions (root, standard, read-only). Add or rotate SSH keys per server. Give a contractor read-only access to debug, revoke it with one click when the contract ends.
* **Fleet-wide Access Management:** Scan your entire server fleet to see who can log in to every server, from one screen. Onboard a new developer to 10 servers at once, or offboard a departing contractor from all 19 servers in a single confirmed action. Export audit snapshots for compliance records. No more checking `authorized_keys` server by server.
* **Automated server backups:** Schedule backups to AWS S3, Cloudflare R2, Backblaze B2, DigitalOcean Spaces, Wasabi, or MinIO. Live progress tracking from the backup tab. No cron scripts needed.
**Pricing:** $7/user/month or $70/user/year. Unlimited servers. All features included. [1 month free trial](/pricing), no credit card required.
**Platforms:** macOS (Apple Silicon + Intel), Windows, Linux.
For teams evaluating broader [DevOps automation tools](/blog/devops-automation-tools) alongside SSH clients, CtrlOps fits as the deployment and monitoring layer. For a direct breakdown against other modern tools, see our comparisons: [CtrlOps vs Termius](/compare/ctrlops-vs-termius), [CtrlOps vs Warp](/compare/ctrlops-vs-warp), and [CtrlOps vs SecureCRT](/compare/ctrlops-vs-securecrt).
***
## Which Tool Should You Pick? (Decision Framework) [#which-tool-should-you-pick-decision-framework]
The right SSH tool depends on your daily workflow, team size, and operating system. PuTTY fits lightweight SSH workflows, especially on Windows. MobaXterm fits multi-protocol Windows power users. CtrlOps fits developers managing 5 - 25 servers who need deployment, monitoring, and AI in one cross-platform app.
Here's a quick decision matrix by role.
**You need a quick SSH connection on Windows, nothing else:**
PuTTY. Free, portable, zero setup. Connect, do your work, close. Don't overthink it.
**You manage multiple remote protocols (SSH + RDP + VNC) on Windows:**
MobaXterm. The built-in X11 server and multi-protocol support are among its biggest strengths on Windows. If you also need file transfers, the auto SFTP browser saves real time.
**You manage 5+ servers, deploy apps, and need AI diagnostics:**
CtrlOps - Named servers, one-click deployment, approval-gated AI, infrastructure monitoring, and cross-platform support. The workflow advantage shows up the first time you deploy in 5 minutes instead of 45, which can significantly reduce deployment time by automating common setup tasks.
**You work on macOS or Linux:**
MobaXterm is Windows-only, while Linux and macOS already include OpenSSH clients. As a result, many users on those platforms rely on the built-in SSH tools or choose modern cross-platform alternatives. PuTTY works on Linux but adds nothing over built-in OpenSSH.
**You need cross-device sync (phone + laptop + desktop):**
Neither PuTTY nor MobaXterm syncs across devices. Termius is the strongest option for mobile SSH. See how it compares in our [CtrlOps vs Termius](/compare/ctrlops-vs-termius) breakdown.
| Your Situation | Best Pick | Why |
| ---------------------------------------- | -------------------------- | ------------------------------------------------------------------------------------------------------------- |
| Quick SSH on Windows, 1 - 2 servers | PuTTY | Free, zero install, zero learning curve |
| Windows power user, SSH + RDP + VNC | MobaXterm Pro ($69) | Multi-protocol, tabs, X11 server |
| Freelancer, 5 - 15 client servers | CtrlOps ($7/user/mo) | Named servers, AI, deployment, monitoring |
| Startup CTO, team of 3 - 5 | CtrlOps ($7/user/mo) | Cross-platform, local credentials, one-click deploy |
| Agency engineer, 10+ client environments | CtrlOps ($7/user/mo) | Server organization, script reuse, fleet monitoring |
| Enterprise / compliance requirement | SecureCRT (\~$116/license) | FIPS 140-2, advanced scripting, 31-year track record |
| Mac or Linux primary OS | CtrlOps or OpenSSH | MobaXterm is Windows-only. Most Linux users already have OpenSSH available, so PuTTY is less commonly needed. |
The cost math is straightforward. PuTTY is free, but workflows that rely on multiple companion tools for file transfers, deployments, and monitoring can introduce additional manual steps. MobaXterm Pro is $69 one-time and cuts file transfer friction, but deployment and monitoring are still manual.
CtrlOps is $7/user/month after a 1 month free trial and replaces your terminal, SFTP client, monitoring dashboard, and deployment workflow with one app.
For a look at how [AI is changing DevOps workflows](/blog/ai-in-devops) beyond just SSH, we break down the full approval-gated model and where human oversight fits in production operations.
***
## Conclusion [#conclusion]
**PuTTY vs MobaXterm** in 2026 comes down to simplicity versus features, but both tools share the same ceiling.
PuTTY is free, portable, and connects you to a server in 10 seconds. It's the right choice for a quick SSH session on Windows when you don't need anything else. Twenty-five years of trust behind it.
MobaXterm wraps SSH, RDP, VNC, X11, and SFTP into one Windows app. It replaces 3 - 4 separate tools. For Windows power users managing mixed protocol environments, it's the better choice.
But neither tool helps you deploy code, monitor server health, or diagnose problems with AI. Neither provides the same cross-platform experience as tools designed specifically for Windows, macOS, and Linux together. Neither provides the integrated credential management, deployment workflows, and monitoring available in CtrlOps. Neither saves your team 30 - 40 minutes of tool-switching overhead per session.
For developers and teams managing 5 - 25 servers who need SSH, file management, monitoring, deployment, and AI diagnostics in one local-first app, CtrlOps fills the gaps both tools leave open. $7/user/month (or $70/user/year). [1 month free trial](/pricing), no credit card required. If you're also evaluating Termius as a modern upgrade, see the full [Termius alternatives](/blog/termius-alternatives) comparison.
Pick the tool that matches your biggest friction today. Outgrow it? Switch. The best SSH client is the one you stop fighting.
***
## Frequently Asked Questions [#frequently-asked-questions]
For most Windows users managing multiple servers, yes. MobaXterm adds tabbed sessions, a built-in SFTP browser, an embedded X11 server, and multi-protocol support (SSH, RDP, VNC). PuTTY is better when you need a quick, zero-install SSH connection and nothing else. Neither tool offers AI, deployment automation, or infrastructure monitoring.
For occasional single-server SSH connections on Windows, PuTTY still works fine. Its latest release (version 0.84, May 2026) patched critical security vulnerabilities. But PuTTY stores sessions in the Windows Registry in plain text, has no tabs, no file manager, and no AI. For anything beyond basic SSH, modern tools like MobaXterm or CtrlOps are more capable.
Several. MobaXterm adds tabs, SFTP, and X11 on Windows. Termius adds cross-device sync and mobile apps. CtrlOps adds AI diagnostics, one-click deployment, infrastructure monitoring, and a full GUI file manager at $7/user/month, with a 1 month free trial. For a full breakdown, see our guide to [PuTTY alternatives for Windows](/blog/putty-alternatives-windows).
On Windows, yes. MobaXterm does everything PuTTY does (SSH, Telnet, serial) and adds tabs, SFTP, X11, RDP, VNC, macros, and session folders. The Free Home Edition has a 12-session limit; the Professional Edition ($69 one-time) removes that cap. On macOS and Linux, MobaXterm is unavailable, while most users rely on the built-in OpenSSH client or other native SSH tools instead of PuTTY.
No. MobaXterm is a Windows-only application. There is no native macOS or Linux version. On Mac, alternatives include iTerm2, Termius, or CtrlOps. On Linux, OpenSSH is pre-installed on most distributions, and CtrlOps offers full cross-platform support. See our [CtrlOps vs MobaXterm](/compare/ctrlops-vs-mobaxterm) comparison for the cross-platform breakdown.
PuTTY stores saved session data (hostnames, usernames, port numbers) in the Windows Registry under `HKEY_CURRENT_USER\Software\SimonTatham\PuTTY\Sessions` in plain text. Any process with user-level access can read this data. PuTTY itself doesn't store passwords, but session metadata is unencrypted. For client work or regulated environments, this is a real security gap.
Two tools offer AI command generation for server management: CtrlOps (approval-gated, shows commands before execution) and Warp (auto-run, executes commands immediately). CtrlOps also connects to MCP servers like Context7 and GitHub so the AI works from your real documentation and codebase, not just training data. Both support BYOK (bring your own API key).
Skip MobaXterm if your team uses macOS or Linux (it's Windows-only), if you need AI-assisted server diagnostics, if you need automated deployment, if you manage infrastructure monitoring, or if you need to sync sessions across devices. MobaXterm is a connection tool, not a management platform. It excels at getting you to the server. What you do once connected is still entirely manual.
CtrlOps replaces the terminal, SFTP client, monitoring dashboard, and deployment workflow with one desktop app. It adds named server cards, a full GUI file manager, approval-gated AI terminal, one-click deployment, real-time infrastructure monitoring, and AES-256 encrypted local credential storage. It costs $7/user/month (or $70/user/year) after a 1 month free trial, and runs on macOS, Windows, and Linux. PuTTY and MobaXterm handle the connection. CtrlOps handles the connection plus everything after it.
MobaXterm adds tabs, a built-in file browser, and one-click X11 support - things PuTTY doesn't have at all. You get more done without switching between apps. PuTTY still wins on simplicity and cross-platform use, but for daily multi-server work, MobaXterm is the easier tool.
Yes. MobaXterm adds tabs and file transfers. Termius adds mobile access. CtrlOps adds AI diagnostics, one-click deployment, and server monitoring for teams managing multiple servers. The best pick depends on what you need beyond a basic SSH connection.
MobaXterm includes its own SSH client and does not require PuTTY. However, MobaXterm can import PuTTY saved sessions from the Windows Registry, so you don't lose your existing server configurations when switching. MobaXterm also supports standard OpenSSH key formats alongside PuTTY's .ppk format.
---
# Best Alternatives to PuTTY, Webmin & ServerPilot for 2026 (/blog/putty-webmin-serverpilot-alternatives)
Author: Daxesh Italiya | Role: Co-Founder & CTO, TST Technology | Published: 2026-04-14 | Updated: 2026-06-11 | Tags: PuTTY alternatives, SSH client, Webmin, ServerPilot, server management | Reading Time: 16 min read
> Compare modern alternatives to PuTTY, Webmin, and ServerPilot. Find the right tools for SSH access, server management, and deployment workflows.
## Key Takeaways [#key-takeaways]
PuTTY, Webmin, and ServerPilot each solved a real problem - in 1999, 1997, and 2012. None of them aged into modern workflows. The strongest replacements in 2026 are **Termius** or **MobaXterm** for SSH, **Cockpit** or **Plesk** for browser-based server administration, and **RunCloud** or **Forge** for PHP/WordPress deployment - and **CtrlOps** if you want all three workflows (SSH, files, monitoring, and AI-assisted deployment) in a single app.
* **PuTTY replacement** - Termius (cross-device), MobaXterm (Windows-only), or CtrlOps (SSH + files + monitoring + AI in one app)
* **Webmin replacement** - Cockpit (free, lightweight), Plesk (full hosting panel), or CtrlOps (modern desktop UI)
* **ServerPilot replacement** - RunCloud (direct PHP swap), Forge (Laravel-first), or CtrlOps (flexible, AI-assisted)
* **If you want all three in one tool** - that's the gap CtrlOps was built to fill, at $7/user/month with a 1 month free trial
| Tool you're replacing | Direct replacement | All-in-one option |
| ------------------------- | -------------------- | ----------------- |
| PuTTY (SSH terminal) | Termius or MobaXterm | CtrlOps |
| Webmin (browser admin) | Cockpit or Plesk | CtrlOps |
| ServerPilot (PHP deploys) | RunCloud or Forge | CtrlOps |
***
## Why Teams Are Replacing PuTTY, Webmin, and ServerPilot [#why-teams-are-replacing-putty-webmin-and-serverpilot]
If you've been managing servers for a while, you've probably used PuTTY for SSH, Webmin for browser-based admin, or ServerPilot for PHP deployments. They work. But they also feel dated: scattered workflows, no centralization, and zero AI assistance.
The problem isn't that these tools don't function. The problem is that modern DevOps workflows have outgrown them. [Atlassian's State of Developer Experience 2025 report](https://www.atlassian.com/blog/developer/developer-experience-report-2025), surveying 3,500 developers and managers across six countries, lists context switching between tools among developers' top time-wasters - and [Getcoherence research](https://getcoherence.io/blog/context-switching-productivity) puts the cost of each interruption at an average of 23 minutes to fully refocus.
This guide covers the strongest alternatives that solve actual problems: too many tabs, fragmented credentials, manual command execution, and constant context-switching between tools.
***
## What does this guide cover? [#what-does-this-guide-cover]
### SSH Access, Server Management, and Hosting Workflows [#ssh-access-server-management-and-hosting-workflows]
We're looking at three categories of tools:
* **PuTTY alternatives** - for teams that primarily need SSH terminal access with better session management
* **Webmin alternatives** - for teams that want browser-based server administration
* **ServerPilot alternatives** - for teams deploying and managing PHP/WordPress applications
Some tools fit one category. A few fit all three. We'll make that clear.
### Who is this comparison for? [#who-is-this-comparison-for]
DevOps engineers are tired of juggling multiple tools. System administrators want a modern UI. Developers deploy to their own servers. SaaS teams build internal tools.
If you've ever thought, "There has to be a better way to manage servers," this is for you.
## How We Compared the Tools [#how-we-compared-the-tools]
### Real-World Workflow Criteria [#real-world-workflow-criteria]
We didn't just read feature lists. We compared each tool against the workflows that actual teams run daily:
* Connecting to multiple servers without re-entering credentials
* Transferring files without opening a separate SFTP client
* Monitoring CPU, memory, and disk without SSH-ing in
* Running commands safely with audit trails
* Deploying code changes without logging into a control panel
### Setup, Usability, Monitoring, and Security [#setup-usability-monitoring-and-security]
Each tool was evaluated on:
| Criteria | What We Evaluated |
| ---------- | --------------------------------------------------------- |
| Setup time | How long from download to the first successful connection |
| Usability | UI clarity, learning curve, and workflow efficiency |
| Monitoring | Real-time visibility into server health |
| Security | Credential storage, command approval, and audit logs |
## Best PuTTY Alternatives for Modern SSH Workflows [#best-putty-alternatives-for-modern-ssh-workflows]

PuTTY has been around since 1999. It's reliable, but it's stuck in the past. No tabs. No saved credentials across sessions. No file browser. No monitoring. Each server is a separate window.
If you're still using PuTTY, you're doing more work than necessary. Windows users can find a dedicated ranking in the [PuTTY alternatives for Windows](/blog/putty-alternatives-windows) guide; the tools below cover the broader cross-platform picture.
**Bottom line:** PuTTY still works in 2026 the same way it worked in 1999 - and that's the problem. Every modern alternative below adds at least one of: tabbed sessions, saved credentials, built-in file transfer, monitoring, or AI-assisted commands. If you're managing more than two servers, the upgrade pays for itself in the first week.
### CtrlOps for SSH and terminal workflows [#ctrlops-for-ssh-and-terminal-workflows]
**Best for SSH + UI-based file management + AI-assisted workflows**
[CtrlOps](https://ctrlops.io/) isn't trying to be a better terminal. It's trying to be a complete server workspace. You get SSH access, a file browser, real-time monitoring, and an AI terminal that suggests commands, all in one interface.
What makes it different:
* **Centralized credentials:** Add server details once, use them everywhere
* **[UI file operations](/docs/modules/file-manager):** Drag, drop, edit files without the command line
* **[AI terminal](/docs/modules/ai-terminal):** Ask "show me nginx logs from the last hour" and get the command
* **Approval gates:** AI suggests commands, you approve before execution
* **[Real-time monitoring](/docs/modules/infra-details):** CPU, memory, disk, processes visible on dashboard
Strengths:
* Replaces 3-4 tools (terminal, SFTP client, monitoring dashboard)
* Native desktop app for Mac, Windows, and Linux. No browser needed.
* Built for teams with shared server access
* Security-first design with command approval workflows
Limitations:
* More features than needed if you only want SSH
* Requires initial setup to add servers
**Pricing:** $7/user/month or $70/user/year for unlimited servers. Every account starts with a [1 month free trial](/pricing), no credit card required.
**Workflow fit:** Best for teams [managing 3+ servers](/blog/manage-multiple-servers-without-losing-control) who want everything in one place. If you're constantly switching between PuTTY, WinSCP, and a monitoring tool, CtrlOps consolidates that.
### MobaXterm [#mobaxterm]
**Best for all-in-one SSH and remote admin**
[MobaXterm](https://mobaxterm.mobatek.net/) is what PuTTY users often upgrade to. It bundles SSH, SFTP, RDP, VNC, and X11 into a single Windows application.
What makes it different:
* Tabbed interface for multiple sessions
* Built-in SFTP browser (opens automatically with SSH)
* Supports remote desktop protocols
* Macro recording for repetitive tasks
Strengths:
* Familiar interface for PuTTY users
* No need for separate file transfer tools
* Portable version available (no installation)
* Good documentation and community
Limitations:
* Windows only
* The free version has session limits
* UI can feel cluttered with all the features
* No cloud sync for settings
**Workflow fit:** Best for Windows users who want SSH plus file transfer without switching apps. Great for individual administrators, less ideal for team collaboration.
### Termius [#termius]
**Best for cross-device session management**
[Termius](https://termius.com/index.html) syncs your servers across desktop and mobile. Start a session on your laptop, continue on your phone. It's built for engineers who move between devices.
What makes it different:
* Cross-platform: Windows, Mac, Linux, iOS, Android
* Syncs hosts, credentials, and snippets across devices
* Built-in SFTP client
* SSH key management
Strengths:
* Smooth device switching
* Clean, modern UI
* Strong mobile app (actually usable for quick fixes)
* End-to-end encryption for synced data
Limitations:
* Free tier has no cross-device sync - the local vault keeps everything on one device
* No AI assistance beyond command autocomplete
* Monitoring features are basic
* Team features require a premium plan
**Workflow fit:** Best for solo engineers who work across multiple devices. If you need to check servers on your phone or switch between a laptop and a desktop regularly, Termius handles that well.
### SecureCRT [#securecrt]
**Best for advanced terminal users and enterprises**
SecureCRT is the enterprise choice. It's not flashy, but it's rock-solid for organizations with strict security requirements.
What makes it different:
* Advanced scripting with Python, Perl, VBScript
* Tabbed sessions with saved layouts
* Smart card and PKI support
* Detailed session logging
Strengths:
* Rock-solid reliability
* Extensive protocol support
* Granular access controls
* Integrates with VanDyke's file transfer tools
Limitations:
* Expensive (per-seat licensing)
* Dated interface
* Steep learning curve for advanced features
* Overkill for simple SSH needs
**Workflow fit:** Best for enterprises with compliance requirements and teams that need detailed audit trails. If you're in a regulated industry, SecureCRT is a safe bet.
**Reality check:** Some "modern" SSH and AI-powered terminals auto-execute commands without an approval gate. On a production server, one auto-run command is one incident away. If a tool runs things without asking, treat it as a developer-machine tool, not a server-management tool.
## Best Webmin Alternatives for Server Administration [#best-webmin-alternatives-for-server-administration]

[Webmin](https://webmin.com/) has been the go-to for browser-based server admin since 1997. It works, but the UI feels like a time capsule. Finding settings takes too many clicks. Mobile support is nonexistent. And modern monitoring? Not really.
If you want browser-based admin without the 1990s experience, these alternatives are worth a look.
### CtrlOps for browser-free server administration [#ctrlops-for-browser-free-server-administration]
**Best for centralized server management, monitoring, and file operations in one workspace**
[CtrlOps](https://ctrlops.io/) gives you what Webmin promised: full server control from a native desktop app. But with a modern interface, real-time monitoring, and AI assistance.
What makes it different:
* [Real-time dashboard](/features/infra-monitoring): See CPU, memory, disk, and processes at a glance
* [File browser](/features/file-manager): Navigate, edit, upload, and download files visually
* AI terminal: Describe what you want, get the right command
* Multi-server view: All your servers in one dashboard
Strengths:
* Modern, responsive UI (works on mobile)
* No agent installation uses SSH credentials
* Team collaboration with shared access
* Audit logs for all operations
Limitations:
* Not designed for email/DNS management (use Plesk for that)
* Requires SSH access (doesn't work with local-only servers)
**Workflow fit:** Best for teams that want Webmin's centralized management convenience, with a modern UX and monitoring. If you're tired of Webmin's clunky interface, CtrlOps is the upgrade you're looking for.
Olbuz made this trade for the same reason. Its tech lead wanted infrastructure details visible without running a panel on the VPS at all, and [ended up consolidating four servers into one local app](/case-studies/olbuz) covering terminal, file transfers, deployments, and backups.
### Cockpit [#cockpit]
**Best for lightweight Linux server administration**
Cockpit is an open-source project from Red Hat. It's lean, focused, and comes pre-installed on many Linux distributions.
What makes it different:
* Pre-installed on Fedora, RHEL, CentOS
* Terminal built into the UI
* Storage, networking, and container management
* Multi-server support
Strengths:
* Free and open source
* Very lightweight (runs in browser, minimal resources)
* No vendor lock-in
* Good for single-server management
Limitations:
* UI feels sparse compared to alternatives
* Limited monitoring and alerting
* No AI features
* Team features are basic
**Workflow fit:** Best for Linux administrators who want a simple, free tool without vendor dependencies. If you're managing a handful of servers and don't need AI assistance, Cockpit is solid.
### Plesk [#plesk]
**Best for multi-site hosting and UI-driven operations**
[Plesk](https://www.plesk.com/) is the modern alternative to cPanel. It's designed for hosting providers and agencies managing dozens of websites.
What makes it different:
* Website and domain management
* Email server configuration
* One-click CMS installations (WordPress, Joomla)
* Customer account management for resellers
Strengths:
* Complete hosting control panel
* Excellent WordPress toolkit
* Built-in security features
* Extension marketplace
Limitations:
* Overkill if you're not hosting websites
* Licensing costs add up
* Resource-heavy compared to lighter alternatives
* Steep learning curve for non-hosting use cases
**Workflow fit:** Best for agencies, hosting providers, and teams managing multiple client websites. If you need email, web hosting, and DNS in one panel, Plesk covers it. Budget-conscious teams often shortlist aaPanel in this category too - our [CtrlOps vs aaPanel](/compare/ctrlops-vs-aapanel) breakdown covers when a browser panel makes sense and when it doesn't, and the [7 best aaPanel alternatives](/blog/aapanel-alternatives) guide compares the free panels worth switching to.
### CloudPanel [#cloudpanel]
**Best for modern cloud server management**
[CloudPanel](https://www.cloudpanel.io/) is the newer, lighter alternative to Plesk. It's designed specifically for cloud servers running PHP applications.
What makes it different:
* Focused on PHP/Node.js/Python apps
* Built for cloud providers (AWS, DigitalOcean, etc.)
* Let's Encrypt SSL automation (and when a renewal misbehaves, our [SSL certificate decoder](/tools/ssl-certificate-decoder) shows the cert's expiry and chain in seconds)
* Clean, modern UI
Strengths:
* Free for basic use
* Fast and lightweight
* Good documentation
* One-click application deployment
Limitations:
* Limited to specific tech stacks
* No email hosting
* Smaller community than Plesk
* Less mature feature set
**Workflow fit:** Best for developers deploying PHP or Node.js apps to cloud servers. If you're running Laravel, WordPress, or Node apps on DigitalOcean, CloudPanel is worth a look. It also lands near the top of our [aaPanel alternatives comparison](/blog/aapanel-alternatives) if you're leaving a heavier panel behind.
## Best ServerPilot Alternatives for Deployment and Hosting [#best-serverpilot-alternatives-for-deployment-and-hosting]

[ServerPilot](https://serverpilot.io/) made it easy to deploy PHP apps on your own servers. But development has slowed, and users are looking for alternatives with active development and better features.
### CtrlOps for app deployment without lock-in [#ctrlops-for-app-deployment-without-lock-in]
**Best for deployment + live server operations + AI-assisted workflows**
[CtrlOps](https://ctrlops.io/) isn't just for server management. The AI terminal can help with [deployment tasks](/features/deployment), suggesting commands for Git pulls, restarts, and log checks.\
What makes it different:
* SSH-based: Works with any server you have access to
* AI assistance: "Deploy the latest code from main branch" generates the commands
* Real-time logs: See deployment output live
* No lock-in: Use your own Git, your own servers
Strengths:
* Not tied to a specific hosting provider
* AI helps with deployment commands
* Works alongside existing CI/CD pipelines
* File browser for quick config edits
Limitations:
* Not a full CI/CD platform (use it alongside GitHub Actions, etc.)
* Requires SSH access to servers
**Workflow fit:** Best for teams that want ServerPilot's simplicity but with more flexibility. If you deploy to your own servers and want AI-assisted workflows, CtrlOps is a good fit.
### RunCloud [#runcloud]
**Best for managed PHP and WordPress servers**
[RunCloud](https://runcloud.io/) is the most direct ServerPilot alternative. It's actively developed and focused on PHP/WordPress deployments.
What makes it different:
* Server management via API and UI
* One-click WordPress installation
* Automatic security updates
* Git deployment integration
Strengths:
* Active development and updates
* Good documentation
* Integrates with cloud providers
* Team management features
Limitations:
* Pricing per server adds up
* Limited to PHP/WordPress use cases
* No AI features
* Requires agent installation
**Workflow fit:** Best for teams that want a direct ServerPilot replacement for PHP/WordPress hosting. If you're currently on ServerPilot, RunCloud is the smoothest transition. Torn between RunCloud's panel approach and a desktop workspace? See [CtrlOps vs RunCloud](/compare/ctrlops-vs-runcloud) for a side-by-side look.
### Forge [#forge]
**Best for developers who want simple server provisioning**
Forge is from the Laravel team. It's designed for PHP deployments but works well for any stack that uses Nginx. (Still hand-writing those server blocks on your own boxes? Our free [nginx config generator](/tools/nginx-config-generator) gives you a production-ready starting point.)
What makes it different:
* Provision servers directly from cloud providers
* Zero-downtime deployments
* Database management
* SSL certificate automation
Strengths:
* Excellent for Laravel deployments
* Clean, simple interface
* Good integration with cloud providers
* Active development
Limitations:
* Laravel-focused (other stacks are secondary)
* No AI assistance
* Pricing can be confusing
* Limited monitoring features
**Workflow fit:** Best for Laravel developers who want simple server provisioning. If your stack is Laravel, Forge is purpose-built for you.
### SpinupWP [#spinupwp]
**Best for WordPress-focused workflows**
SpinupWP is the WordPress-specific alternative to ServerPilot. It's built by the Delicious Brains team (makers of popular WordPress plugins).
What makes it different:
* WordPress-specific optimizations
* One-click staging sites
* Automatic backups
* Git-based deployments
Strengths:
* WordPress expertise built-in
* Good for agencies managing multiple sites
* Integrates with popular backup services
* Active community
Limitations:
* WordPress only
* No AI features
* Limited to non-WordPress stacks
* Smaller feature set than Plesk
**Workflow fit:** Best for WordPress agencies and freelancers. If 90% of your work is WordPress, SpinupWP handles it well.
## Feature Comparison by Workflow [#feature-comparison-by-workflow]
### Best for SSH Access [#best-for-ssh-access]
Terminal usability and session handling:
| Tool | Tabbed Sessions | Saved Credentials | Cross-Device | AI Assistance |
| :-------: | :-------------: | :---------------: | :----------: | :-----------: |
| CtrlOps | ✅ | ✅ | ✅ | ✅ |
| MobaXterm | ✅ | ✅ | ❌ | ❌ |
| Termius | ✅ | ✅ | ✅ | ❌ |
| SecureCRT | ✅ | ✅ | ❌ | ❌ |
### Best for File Management [#best-for-file-management]
Visual navigation vs command-line work:
| Tool | Visual File Browser | Drag & Drop | Edit in App | SFTP Built-in |
| :-------: | :-----------------: | :---------: | :---------: | :-----------: |
| CtrlOps | ✅ | ✅ | ✅ | ✅ |
| MobaXterm | ✅ | ✅ | ❌ | ✅ |
| Termius | ✅ | ✅ | ❌ | ✅ |
| Cockpit | ✅ | ❌ | ✅ | ❌ |
### Best for Monitoring [#best-for-monitoring]
CPU, memory, disk, and process visibility:
| Tool | Real-time Dashboard | Process List | Alerts | Multi-Server View |
| :-----: | :-----------------: | :----------: | :----: | :---------------: |
| CtrlOps | ✅ | ✅ | ✅ | ✅ |
| Cockpit | ✅ | ✅ | ❌ | ✅ |
| Plesk | ✅ | ✅ | ✅ | ✅ |
| Webmin | Basic | Basic | ❌ | ❌ |
### Best for Security [#best-for-security]
Approval-based command execution and credential handling:
| Tool | Command Approval | Audit Logs | Team Access Controls | 2FA |
| :-----------: | :--------------: | :--------: | :------------------: | :---: |
| **CtrlOps** | **✅** | **✅** | **✅** | **✅** |
| **SecureCRT** | **❌** | **✅** | **✅** | **✅** |
| **Termius** | **❌** | **❌** | **✅** | **✅** |
| **Plesk** | **❌** | **✅** | **✅** | **✅** |
**Bottom line on security:** Approval-based command execution is the single biggest differentiator on this list. Most SSH clients and admin panels run whatever you click; few ask before executing. For regulated industries (SOC2, HIPAA, PCI), an audit-trailed approval gate isn't a nice-to-have - it's the difference between a usable tool and a compliance liability.
## CtrlOps: The Perfect Alternative if You Need All Three [#ctrlops-the-perfect-alternative-if-you-need-all-three]

### Why CtrlOps Replaces PuTTY, Webmin, and ServerPilot in One Workspace? [#why-ctrlops-replaces-putty-webmin-and-serverpilot-in-one-workspace]
If you're currently using PuTTY for SSH, Webmin for admin, and ServerPilot for deployments, you're switching between three tools, each with a different interface.
CtrlOps consolidates all three workflows.
Centralized credentials, UI file operations, AI terminal, and real-time monitoring:
Instead of:
* PuTTY window for SSH
* WinSCP window for file transfers
* Browser tab for Webmin
* Another tab for ServerPilot
You get:
* One app with SSH terminal, file browser, and monitoring dashboard
* AI that helps generate commands (you approve them before execution)
* Real-time server health across all connected servers
Security-first with user-approved commands:\
The AI doesn't auto-execute. It suggests. You review and approve. This prevents the "AI went rogue" scenario that keeps security teams up at night.
⚠️
**Where CtrlOps doesn't fit (yet):**
CtrlOps replaces the daily server-operations layer - SSH, files, monitoring, deployment commands. It doesn't replace full hosting control panels with email/DNS/customer management (Plesk and cPanel still win there), it doesn't replace dedicated CI/CD pipelines (GitHub Actions, GitLab CI), and it doesn't ship a built-in push-alerting system yet - you'll see live metrics on the dashboard, but Slack/email alerts are on the roadmap. Pair it with those tools, or pick one of the alternatives above if your primary need is hosting-panel features.
### Real Workflow Wins Over Fragmented Tools [#real-workflow-wins-over-fragmented-tools]
Less tool-switching, faster operations, better control:
A typical DevOps workflow might involve:
1. SSH in to check disk space
2. Open SFTP to download logs
3. Open a monitoring tool to see CPU trends
4. Open the deployment tool to push code
CtrlOps handles all four through a single interface - the time savings compound when you do this dozens of times a day.
For teams exploring the broader [DevOps automation landscape](/blog/devops-automation-tools), consolidating tools is often the first step toward efficiency.
## Which Tool Should You Choose? [#which-tool-should-you-choose]
### Choose PuTTY Alternatives If You Mainly Need SSH [#choose-putty-alternatives-if-you-mainly-need-ssh]
* CtrlOps if you want SSH + file management + monitoring in one workspace - compare them directly in [CtrlOps vs PuTTY](https://ctrlops.io/compare/ctrlops-vs-putty)
* MobaXterm, if you're on Windows and want a familiar upgrade from PuTTY
* Termius, if you need to access servers from multiple devices
* SecureCRT if enterprise compliance is non-negotiable
### Choose Webmin Alternatives If You Want Unified Server Management [#choose-webmin-alternatives-if-you-want-unified-server-management]
* CtrlOps if you want modern UI + AI assistance + monitoring
* Cockpit is free, open-source, and lightweight
* [Plesk](https://www.plesk.com/) if you're managing hosting for multiple clients
* CloudPanel, if you're running PHP/Node apps on cloud servers
### Choose ServerPilot Alternatives If You Deploy and Manage App Servers [#choose-serverpilot-alternatives-if-you-deploy-and-manage-app-servers]
* CtrlOps if you want flexibility and AI-assisted deployment commands - if you are weighing a self-hosted PaaS, see [CtrlOps vs Dokploy](https://ctrlops.io/compare/ctrlops-vs-dokploy)
* RunCloud if you want the closest ServerPilot replacement
* Forge if Laravel is your primary stack
* SpinupWP if WordPress is your focus
### Choose CtrlOps If You Want One Workspace for Everything [#choose-ctrlops-if-you-want-one-workspace-for-everything]
If you checked multiple boxes above, SSH access, server management, and deployments, CtrlOps is the only tool that covers all three. It's designed for teams that don't want to switch contexts.
For more context on choosing [DevOps management tools](https://tsttechnology.io/blog/devops-management-tool), the key is to match features to actual workflows, not just pick the most popular option.
## Final Recommendation [#final-recommendation]
### Why Choose CtrlOps as Best Overall? [#why-choose-ctrlops-as-best-overall]
Perfect for teams seeking the ultimate 3-in-1 replacement:\
CtrlOps isn't the best at any single category. SecureCRT has deeper enterprise features. Plesk has more hosting tools. RunCloud has tighter WordPress integration.
But CtrlOps is the only one that offers SSH, file management, monitoring, and AI assistance in a single workspace, for teams that don't want to manage three different tools, which matters.
Outshines others in centralization, AI assistance, and security:
* **Centralization:** One login, one interface, all your servers
* **AI assistance:** Describe what you want, get the right command
* **Security:** Commands don't execute without your approval
### Best by Workflow [#best-by-workflow]
| Your Primary Need | Best Tool | Why |
| ----------------- | ------------------- | ------------------------------------------- |
| SSH-focused | CtrlOps or Termius | Modern UX, cross-device access |
| Server admins | CtrlOps or Cockpit | Desktop app, real-time monitoring |
| Deployment | CtrlOps or RunCloud | Flexible, AI-assisted or WordPress-specific |
| All-in-one | CtrlOps | SSH + files + monitoring + AI in one place |
## Conclusion [#conclusion]
PuTTY, Webmin, and ServerPilot each solved specific problems. But modern DevOps workflows demand more: centralization, AI assistance, and tools that work together.
The right choice depends on what you actually do daily:
* If SSH is 90% of your work, Termius or MobaXterm handles it well
* If you're managing hosting for clients, Plesk or CloudPanel fits
* If you deploy WordPress specifically, SpinupWP or RunCloud makes sense
* If you want SSH + files + monitoring + AI in one place, CtrlOps is the answer
The best tool isn't the one with the most features. It's the one that matches how you actually work.
## FAQs [#faqs]
It depends on your needs. For modern workflows, **CtrlOps** and **MobaXterm** offer better experiences than PuTTY with tabbed sessions, saved credentials, and **built-in file transfer**. **Termius** is better for **cross-device access**.
For most users, yes. **Termius** has a **modern UI**, syncs across devices, and includes **SFTP**. PuTTY is reliable but **hasn't meaningfully evolved in decades**. However, Termius requires a **paid plan for cross-device sync and snippets** - the free Starter tier keeps everything in a local vault on one device.
They serve different purposes. **Webmin is free** and gives **low-level server control**. cPanel (and Plesk) are designed for **web hosting with email, DNS, and customer management**. For system administration, **Webmin is more flexible**.
Webmin works reliably for basic server administration. The main complaints are the **dated interface** and the lack of **real-time monitoring and mobile support**. If you want the same functionality with better UX, **CtrlOps** or **Cockpit** are modern alternatives.
For modern workflows that include **file management and monitoring** alongside SSH, **CtrlOps is the best choice**. For pure SSH with modern UI, **Termius** works well. For Windows users wanting a direct upgrade, **MobaXterm** is the answer.
Yes. **CtrlOps** provides a **native desktop app** with **visual file browsing and AI-assisted commands**, making it accessible for users who prefer not to work in a terminal. **Plesk** is another option for users managing web hosting.
**RunCloud** is the closest direct replacement with **team features**. **CtrlOps** offers more flexibility if you're managing **diverse server types** beyond PHP/WordPress. Both have active development and good documentation.
**Yes.** CtrlOps combines **SSH terminal access**, **visual file management**, **real-time monitoring**, and **AI-assisted command generation** into a **single workspace**. It's designed specifically for teams tired of switching between multiple tools.
**Yes.** CtrlOps uses **approval-based command execution**: AI suggests commands, but **humans must approve them** before execution. It stores credentials **securely** and provides **audit logs** for compliance.
---
# 7 Best SecureCRT Alternatives for Mac in 2026 (With AI) (/blog/securecrt-alternatives-mac)
Author: Hiren Kalariya | Role: Co-Founder & CEO, TST Technology | Published: 2026-06-22 | Tags: SecureCRT Alternatives for Mac, SecureCRT for Mac, Mac SSH Client, Server Management App Mac | Reading Time: 18 min read
> SecureCRT on Mac has no AI, file manager, or monitoring. We tested 7 alternatives - CtrlOps, iTerm2, Termius, Warp, Royal TSX, Tabby, DartShell.
The best SecureCRT alternatives for Mac in 2026 are CtrlOps, iTerm2, Termius, Warp, Royal TSX, Tabby, and DartShell. For developers managing multiple servers, CtrlOps is the top pick: it replaces SecureCRT, a separate SFTP client, and a monitoring dashboard with one local-first desktop app at $7/user/month after a 1 month free trial, keeping every credential on-device and every AI command approval-gated.
Which one fits depends on the job. **CtrlOps** is best for all-in-one server management with AI diagnostics, file management, monitoring, and one-click deployment. **iTerm2** is the strongest free, keyboard-centric Mac-native terminal for `.ssh/config` power users. **Termius** leads when you need the same setup synced across Mac, iPhone, and Android. **Warp** is the best AI coding terminal for local development, though it auto-runs commands. **Royal TSX** is the only option here that handles RDP, SSH, and VNC together natively on macOS. **Tabby** is the best open-source, cross-platform terminal with no vendor lock-in. **DartShell** is a lightweight, Mac-native multi-protocol tool for occasional remote access. SecureCRT still connects reliably, but it offers no AI, no file manager, and no monitoring at enterprise pricing, which is why Mac developers are switching.
## Key Takeaways [#key-takeaways]
SecureCRT still connects to servers reliably, but it is a single-purpose terminal: no AI, no built-in file manager, no monitoring, at enterprise pricing. The seven alternatives below add what Mac developers expect in 2026, and most cost less than a single SecureCRT license. Here is the quick comparison:
| Tool | Best For | Price | AI | File Manager | Local Credentials |
| ----------- | -------------------------------- | -------------------------- | ---------------------- | -------------- | ----------------- |
| **CtrlOps** | **All-in-one server management** | **$7/user/mo (1 mo free)** | **✓ Approval-gated** | **✓ Full GUI** | **✓ Local-only** |
| iTerm2 | Free Mac power terminal | Free | ✗ | ✗ | ✓ Local |
| Termius | Cross-device sync + mobile | $10/user/mo | Partial (autocomplete) | ✓ SFTP | ✗ Cloud |
| Warp | AI-first coding terminal | $20/mo | ✓ Auto-run | ✗ | ✗ Cloud |
| Royal TSX | Multi-protocol (RDP/SSH/VNC) | €49 one-time | ✗ | Limited | ✓ Local |
| Tabby | Open-source modern terminal | Free | ✗ | ✓ SFTP | ✓ Local |
| DartShell | Lightweight Mac-native SSH | Free / $9.99 | ✗ | ✓ SFTP | ✓ Local |
Prefer to watch instead? The full comparison - all seven tools tested across SSH, file management, AI assistance, monitoring, and deployment - in under 6 minutes:
***
## How We Evaluated 7 SecureCRT Alternatives for Mac [#how-we-evaluated-7-securecrt-alternatives-for-mac]
You just moved your main development machine to a MacBook. Your SecureCRT license still works, technically. But every interaction feels off.
The UI renders like a cross-platform afterthought. The settings panel looks like it was designed for Windows XP. Session management works, but nothing about it feels like a Mac app.
Then you realize you're paying $119+ for a terminal emulator with no AI, no monitoring, no file manager, and no deployment automation. A 31-year-old tool that hasn't shipped a major UX update in years.
If you're a **freelance developer managing 5 to 15 client VPS instances**, a **startup CTO who deploys Node.js apps to production weekly**, or an **agency engineer switching between staging and production across multiple projects**, you've already started searching for something better.
We compared 7 **SecureCRT alternatives for Mac** against the same real-world server management tasks:
* Connecting to a multi-server fleet on macOS
* Deploying a Node.js application to a VPS
* Debugging a 2 AM production incident
* Transferring config files without leaving the terminal
* Managing SSH keys across environments

This guide covers how each tool handles those scenarios. Not feature-list marketing. Actual workflow comparisons.
***
## Why Are Mac Users Switching Away from SecureCRT in 2026? [#why-are-mac-users-switching-away-from-securecrt-in-2026]
SecureCRT still connects to servers reliably. That part works.
The problem is everything around the connection: the interface, the missing features, and the price relative to what modern tools offer.
Five specific pain points push Mac users to look for **SecureCRT alternatives**:

**1. The UI is not Mac-native:**
SecureCRT runs on macOS, but it does not feel like macOS. No native toolbar, no Spotlight integration, no drag-and-drop that matches Finder conventions. After 8 hours in a Mac environment, SecureCRT feels like a foreign app.
**2. No AI assistance:**
When you SSH into an unfamiliar server at 2 AM, SecureCRT gives you a blank cursor. No command suggestions. No diagnostics. No error interpretation. You Google everything manually. That loop costs 20 to 40 minutes per incident, according to research from [Getcoherence](https://getcoherence.io/blog/context-switching-productivity) on context-switching costs.
**3. No built-in file management:**
Need to upload a config file? SecureFX is a separate product, sold separately. On macOS, most developers expect file transfer built into their SSH tool, not bolted on as a second purchase.
**4. No infrastructure monitoring:**
Checking CPU, RAM, or disk usage means running `htop`, `free -m`, and `df -h` manually. Every time. On every server. Modern tools show this data in a dashboard without typing a single command.
**5. Expensive for what you get:**
SecureCRT costs $119 to $190 per license, plus annual maintenance fees for updates. That buys a lot of terminal, but no AI, no monitoring, no deployment, and no [file manager](/features/file-manager). At that price, you're paying enterprise rates for a single-purpose tool.
**Bottom line:** SecureCRT's core SSH engine is still reliable. But Mac users increasingly need AI diagnostics, visual file management, and infrastructure monitoring alongside their terminal. SecureCRT doesn't offer any of these, and charges enterprise pricing anyway.
***
## 7 Best SecureCRT Alternatives for Mac in 2026 [#7-best-securecrt-alternatives-for-mac-in-2026]
The 7 best SecureCRT alternatives for Mac are CtrlOps (all-in-one server management with AI), iTerm2 (free Mac power terminal), Termius (cross-device sync), Warp (AI coding terminal), Royal TSX (multi-protocol RDP/SSH/VNC), Tabby (open-source), and DartShell (lightweight Mac-native). We compared each against identical scenarios: connecting to multiple servers, deploying code, debugging under pressure, and transferring files on macOS.
Here's how all seven compare.
### 1. CtrlOps: Best for AI-Powered Server Management on Mac [#1-ctrlops-best-for-ai-powered-server-management-on-mac]
[CtrlOps](https://ctrlops.io/) is not a terminal replacement. It replaces your entire server management workflow: terminal, file manager, monitoring dashboard, and deployment system, combined in one desktop app.

Where SecureCRT gives you a connection and a blank cursor, CtrlOps gives you a complete operations platform. Every credential stays local on your Mac. Every AI command requires your approval before execution. For a side-by-side comparison, see [CtrlOps vs SecureCRT](https://ctrlops.io/compare/ctrlops-vs-securecrt).
**Pros of CtrlOps:**
* **[Named server cards](/features/multi-server-management).** Connect instantly to "Prod-Backend" or "Client-Staging" in a single click. Say goodbye to memorizing IP addresses and navigating complex session trees.
* **Full GUI file manager.** Upload, download, edit, and delete remote files with drag-and-drop. No SCP commands. No separate SFTP tool.
* **Approval-gated AI terminal.** Type "why is my server slow?" and CtrlOps generates diagnostic commands. It shows every command before execution. You approve, then it runs. Human-in-the-loop, not auto-run.
* **MCP server integration.** Connect external documentation, code repositories, and local files directly to the AI Terminal using the Model Context Protocol. Predefined servers include Context7 (official docs), GitHub (your repos), and Filesystem (local files). Add your own MCP server via JSON config or manual entry over HTTP, SSE, or a local process. The AI reads your actual codebase and current documentation before suggesting commands, not just its training data. MCP does not bypass the approval gate.
* **One-click app deployment.** Pick your stack (Node.js, React, Next.js), input your GitHub repository link, and configure your environment variables. CtrlOps automatically manages the git clone, npm installation, PM2 configuration, Nginx setup, and Certbot SSL provisioning. [Deployment tasks that typically take 30 to 45 minutes](https://ctrlops.io/docs/modules/deployment) of manual effort are finished in less than 5 minutes.
* **Real-time infrastructure monitoring.** Live CPU, RAM, disk usage, and top processes for every connected server. No `htop` needed. Spot a disk at 94% before it causes downtime.
* **Local-first security.** Every SSH key, password, and server config stays on your Mac. AES-256 encrypted. No cloud sync. No vendor-side storage. Your credentials never leave your device.
* **[Script Directory](https://ctrlops.io/features/script-directory).** Save reusable command sequences with `{{variable_name}}` placeholders. Run the same deployment script across every server without retyping a single command.
* **Web Search integration.** The [AI Terminal connects to real-time web search](https://ctrlops.io/docs/modules/ai-terminal/web-search) via Tavily, Brave, or DuckDuckGo. It reads the latest documentation before suggesting commands, not just the model's training data.
* **Rust-based performance.** Built in Rust as a lightweight native desktop app, not Electron. Faster startup and lower memory use than Electron-based tools.
**CtrlOps Limitations:**
* No mobile app
* No serverless or Kubernetes support
**Pricing:** $7/user/month or $70/user/year (unlimited servers). 1 month free trial, no credit card required.
**Platforms:** macOS (Apple Silicon + Intel), Windows, Linux.
| What you do with SecureCRT today | With CtrlOps |
| ----------------------------------------- | --------------------------------------------------------- |
| Look up server IP in a spreadsheet | Click named server card (10 seconds) |
| Buy SecureFX separately for file transfer | Drag-and-drop in the built-in File Manager |
| Run `htop`, `df -h`, `free -m` manually | Glance at the monitoring dashboard |
| Google error messages at 2 AM | Ask the AI Terminal, approve commands before execution |
| Run 12 commands to deploy a Next.js app | Fill a form, click Create (under 8 minutes) |
| Paste docs into ChatGPT for context | Connect Context7 or GitHub via MCP, AI reads real sources |
> "the file manager sounds boring, I know. But I was doing everything through a separate SFTP client before this. separate login, separate window, separate headache. now i just open it inside CtrlOps and edit configs directly. for someone managing multiple client servers, this is honestly the feature i use the most."
>
> * Gabriel, [Product Hunt review](https://www.producthunt.com/products/ctrlops?comment=5380575)
***
### 2. iTerm2: Best Free Terminal for Mac Power Users [#2-iterm2-best-free-terminal-for-mac-power-users]
[iTerm2](https://iterm2.com/) is the Mac terminal most developers already have installed. It is free, open-source, and built specifically for macOS.

iTerm2 is not an SSH client in the traditional sense. It is a terminal emulator that runs macOS's built-in OpenSSH. But for developers who configure `.ssh/config` files and live in the command line, iTerm2 is the most capable free option on the platform.
**Pros of iTerm2:**
* **Truly Mac-native.** Built for macOS from scratch. Spotlight integration, Finder services, native notifications, proper Retina rendering.
* **Split panes and tabs.** View multiple SSH sessions side by side. Save window arrangements and restore them with one shortcut.
* **Hotkey window.** Summon the terminal with a global hotkey, even while using other apps. Instant access from any workspace.
* **Autocomplete and search.** Search across all open sessions. Autocomplete commands from your shell history.
* **Trigger automation.** Define regex patterns that execute actions when matched in terminal output. Highlight errors, send notifications, run scripts automatically.
* **tmux integration.** Native tmux support lets you detach and reattach sessions without losing state.
* **100% free.** No feature gates. No account required. No subscription.
**iTerm2 Limitations:**
* **No GUI file manager.** File transfers require SCP, rsync, or a separate SFTP tool.
* **No server directory.** You maintain SSH config files manually. No visual grouping, no one-click connect cards.
* **No AI features.** Same blank cursor as SecureCRT, just in a nicer window.
* **No monitoring dashboard.** You run diagnostic commands manually every time.
* **No deployment automation.** Every `git pull`, `npm install`, `pm2 restart` is manual.
* **macOS only.** Team members on Windows or Linux need a different tool.
**Pricing:** Free, open-source (GPL v2).
**Platforms:** macOS only.
iTerm2 is the best free SecureCRT alternative for Mac if you're comfortable with `.ssh/config` and command-line workflows.
Once you scale to managing more than five servers, regularly moving files, or troubleshooting new software stacks, you will hit its constraints. While iTerm2 serves as an excellent terminal emulator, it lacks native server management features. If you are looking for a Mac-native terminal that includes built-in server administration capabilities, explore our comprehensive [best SSH clients for Mac 2026](https://ctrlops.io/blog/best-ssh-client-mac-2026) guide for better alternatives.
***
### 3. Termius: Best for Cross-Device Sync and Mobile SSH [#3-termius-best-for-cross-device-sync-and-mobile-ssh]
[Termius](https://termius.com/) is the most polished dedicated SSH client available. It syncs servers, credentials, and command snippets across Mac, Windows, Linux, iOS, and Android with end-to-end encryption.

If you need to SSH into a server from your phone during a production incident, Termius is the only serious option on this list.
**Pros of Termius:**
* **Cross-device sync.** Servers and credentials follow you across every device. E2E encrypted vault keeps data protected in transit.
* **Mobile apps.** Fully functional SSH client on iOS and Android. Not a stripped-down companion app.
* **Streamlined connection management.** Organizes your connections with named hosts, custom tags, and groups for quick one-click access - offering a much cleaner alternative to SecureCRT's complex session hierarchies.
* **Integrated SFTP.** Move files securely between environments without buying or launching external file transfer utilities.
* **AI-assisted command autocomplete.** Predicts and suggests commands in real-time as you type, referencing your command history and local environment context.
* **Team vault.** Shared server access with role-based controls and consolidated billing.
**Termius Limitations:**
* **SSH keys sync to Termius's cloud.** E2E encrypted, yes, but your credentials live on third-party infrastructure. Some client contracts and compliance frameworks prohibit this.
* **No infrastructure monitoring.** You SSH in and run `htop` manually. No dashboard.
* **No one-click deployment.** Manual repo cloning, PM2 setup, Nginx configuration.
* **AI is autocomplete, not diagnostics.** Suggests command completions but doesn't understand your server's current state.
* **Per-user pricing scales fast.** Pro costs $10/user/month. Team costs $20/user/month. A 5-person Team plan runs $100/month ($1,200/year).
**Pricing:** Free (Starter, local vault only). Pro: $10/user/month. Team: $20/user/month. Business: $30/user/month.
**Platforms:** macOS, Windows, Linux, iOS, Android.
Termius wins if you need the same SSH setup on your MacBook, your iPhone, and your Linux workstation. For a deeper head-to-head breakdown, see [CtrlOps vs Termius](https://ctrlops.io/compare/ctrlops-vs-termius).
The trade-off is cloud credential storage and per-user pricing that gets expensive at team scale. At $7/user/month vs Termius's $10 to $20/user/month, [CtrlOps](https://ctrlops.io/) offers more features (monitoring, deployment, AI diagnostics) at a lower price, but without mobile apps. And if Termius's cloud credential model isn't a fit either, our [Termius alternatives](/blog/termius-alternatives) guide covers the local-first options across every platform, with a [Mac-specific breakdown](/blog/termius-alternatives-mac) that goes deeper on that exact question.
***
### 4. Warp: Best AI-Powered Coding Terminal [#4-warp-best-ai-powered-coding-terminal]
[Warp](https://www.warp.dev/) is a modern AI terminal built in Rust with GPU-accelerated rendering. It reimagines the terminal with block-based output and an AI Agent Mode that converts natural language into shell commands.

While Warp looks and feels like the future of terminals, it is designed primarily as a coding terminal rather than a server management tool. For a detailed feature comparison, see [CtrlOps vs Warp](https://ctrlops.io/compare/ctrlops-vs-warp).
**Pros of Warp:**
* **AI Agent Mode.** Type natural language, get shell commands generated and executed. Powerful for local development workflows.
* **Block-based output.** Each command and its output is a selectable, searchable, shareable block. Copy results without line-number noise.
* **IDE-like editing.** Select, copy, and edit previous commands like text in VS Code. Cursor navigation works naturally.
* **Rust-based performance.** GPU-accelerated rendering. No Electron. Noticeably faster than any Electron-based terminal.
* **Warp Drive.** Create, store, and distribute command workflows across your engineering team to enable reusability without writing custom scripts.
* **BYOK support.** Bring your own OpenAI, Anthropic, or Google API key. AI requests routed through BYOK don't consume Warp credits.
**Warp Limitations:**
* **Not a server manager.** No server directory, no file manager, no monitoring, no deployment wizard.
* **AI auto-runs commands by default.** On a production server at 2 AM, one misinterpreted prompt can escalate an incident. No approval gate like CtrlOps.
* **Cloud account required.** You cannot use Warp without signing in to their service.
* **Free tier is limited.** 150 AI credits for 2 months, then 75/month. Build plan costs $20/month for 1,500 credits.
* **No server context awareness.** Warp's AI doesn't know your server's CPU, RAM, or running processes. It generates commands generically.
**Pricing:** Free (75 to 150 AI credits/month). Build: $20/month (1,500 credits). Business: $50/user/month.
**Platforms:** macOS, Windows, Linux.
Warp is the best AI terminal experience on Mac for writing and running code locally.
For managing remote servers, Warp's AI doesn't have your server's context. And auto-executing commands on production is a risk most teams shouldn't accept. CtrlOps's approval-gated approach shows every command before execution, which is the difference between a convenient tool and a safe one.
**Reality check:** Any AI terminal that auto-runs commands without a review step is a development-machine feature, not a server-management feature. On a production server with real traffic, the approval gate in CtrlOps stops 2 AM mistakes from becoming outages.
> "The preview step is the whole game when AI touches live infra. CtrlOps gets it right: ask in plain English, see the exact command before it runs, approve."
>
> * Vivek Chand, [Product Hunt review](https://www.producthunt.com/products/ctrlops?comment=5381393)
***
### 5. Royal TSX: Best for Multi-Protocol Mac Environments (RDP + SSH + VNC) [#5-royal-tsx-best-for-multi-protocol-mac-environments-rdp--ssh--vnc]
[Royal TSX](https://www.royalapps.com/ts/mac) is the Mac version of Royal TS, built specifically for IT professionals who manage mixed-protocol environments.

If your workflow involves SSH to Linux servers, RDP to Windows machines, and VNC to headless systems from the same Mac, Royal TSX is the only tool on this list that handles all three natively.
**Pros of Royal TSX:**
* **Multi-protocol support.** SSH, RDP, VNC, Apple Remote Desktop, Telnet, Web, VMware, all in one app with tabbed connections.
* **Mac-native design.** Built for macOS. Native toolbar, proper window management, Retina display support.
* **Connection organization.** Folders, groups, and tags. Save credentials per connection or per folder.
* **Royal Server integration.** Centralized gateway for secure access management across teams.
* **Password management integration.** Connects to 1Password, KeePass, LastPass, and other vaults.
* **One-time pricing.** €49 individual license. No subscription. Includes 1 year of software maintenance.
**Royal TSX Limitations:**
* **No AI features.** Manual command execution only. No suggestions, no diagnostics.
* **No infrastructure monitoring.** No dashboard. You run system commands manually.
* **No one-click deployment.** No automation for app setup.
* **Complex UI.** Powerful, but the learning curve is steeper than simpler SSH clients. Beginners may find it overwhelming.
* **Limited file management.** Basic SFTP through plugins, not a full GUI file manager.
* **Maintenance costs.** Major version upgrades require a new license purchase.
**Pricing:** Free (limited connections). Individual: €49 one-time. Site: €849. Includes 1 year of updates.
**Platforms:** macOS, Windows, iOS, Android.
Royal TSX is the right SecureCRT alternative if you work across Linux, Windows, and macOS systems and need one tool for all of them.
For pure SSH-to-Linux server management with AI and monitoring, CtrlOps is more focused. For mixed-protocol IT administration, Royal TSX wins. If you're comparing the two head-to-head, see [CtrlOps vs Royal TS](/compare/ctrlops-vs-royalts) for a feature-by-feature breakdown.
***
### 6. Tabby: Best Open-Source Modern Terminal [#6-tabby-best-open-source-modern-terminal]
[Tabby](https://tabby.sh/) is a cross-platform, open-source terminal that modernizes SSH with tabs, split panes, a plugin ecosystem, and a built-in connection manager.
No subscription. No account. No vendor lock-in. MIT-licensed.

**Pros of Tabby:**
* **Free and open-source.** MIT license. No feature gates, no accounts, no usage limits.
* **Cross-platform.** macOS, Windows, Linux with an identical interface. Team members on different operating systems use the same tool.
* **Built-in SSH client.** Connection profiles, SFTP, Zmodem transfers, SSH key management included out of the box.
* **Plugin ecosystem.** Extend with community-built plugins for additional functionality.
* **Split panes and workspaces.** Save complex window layouts as reusable profiles.
* **Encrypted password manager.** Local storage with master passphrase protection.
* **Modern UI.** Themes, font ligatures, GPU-accelerated rendering.
**Tabby Limitations:**
* **Resource-heavy.** Electron-based. Uses noticeably more RAM than iTerm2 or native terminals.
* **Lacks AI capabilities.** Does not provide automated command suggestions, server diagnostics, or error analysis.
* **No monitoring or deployment.** Terminal only, no server management capabilities.
* **Learning curve.** Extensive configuration options are a strength for power users but a barrier for beginners.
* **Occasional stability issues.** Some plugin combinations cause crashes or rendering glitches.
**Pricing:** Free, open-source (MIT license).
**Platforms:** macOS, Windows, Linux.
Tabby is the best choice for developers who want a modern, cross-platform terminal without vendor lock-in or subscription fees.
It is significantly more capable than SecureCRT's UI. The trade-off is higher memory usage, no AI, and no server management features beyond basic SSH. If you're also looking at [alternatives to PuTTY, Webmin, or ServerPilot](https://ctrlops.io/blog/putty-webmin-serverpilot-alternatives), Tabby fits the SSH layer but not the management layer.
***
### 7. DartShell: Best for Lightweight Mac-Native Remote Access [#7-dartshell-best-for-lightweight-mac-native-remote-access]
[DartShell](https://dartshell.com/) is a macOS-native remote connection tool that bundles SSH, RDP, VNC, and SFTP in a single lightweight app.

It focuses on being a clean, Mac-first alternative to heavier cross-platform tools. No AI. No monitoring. Just smooth, native remote connections.
**Pros of DartShell:**
* **Mac-native design.** Feels like a macOS app, not a ported Windows utility. Fast startup, clean interface.
* **Multi-protocol.** SSH, RDP, VNC, SFTP, and FTP in one app. Covers more remote access scenarios than a pure SSH client.
* **Low friction.** Minimal setup. No account required for basic use.
* **Available on the Mac App Store.** Install with a click. Apple-reviewed.
**DartShell Limitations:**
* **macOS only.** No Windows, Linux, or mobile. Teams with mixed operating systems need a second tool.
* **No AI features.** Manual command execution only.
* **No infrastructure monitoring.** No server dashboards.
* **No deployment automation.** Every deployment step is manual.
* **Newer product.** Smaller community and fewer integrations than established tools.
* **Limited documentation.** Fewer guides and tutorials available compared to iTerm2 or Termius.
**Pricing:** Free download with premium features via in-app purchase.
**Platforms:** macOS only (requires macOS 11.5+).
DartShell is the right pick if you want a lightweight, Mac-native tool for occasional remote connections across multiple protocols.
For daily server management at scale, it lacks the depth of CtrlOps (AI, monitoring, deployment) or the ecosystem of Termius (cross-platform sync, team features).
***
## SecureCRT Alternatives: Feature-by-Feature Comparison [#securecrt-alternatives-feature-by-feature-comparison]
Here is the full side-by-side comparison across every capability that matters for daily server management on macOS. Not marketing features. Things you actually do every day.
| Feature | CtrlOps | iTerm2 | Termius | Warp | Royal TSX | Tabby | DartShell |
| ------------------------- | ------------------- | ------ | -------- | ---------- | --------------- | -------- | --------- |
| Named server directory | ✓ | ✗ | ✓ | ✗ | ✓ | ✓ | ✓ |
| One-click connect | ✓ | ✗ | ✓ | ✗ | ✓ | ✓ | ✓ |
| Built-in file manager | ✓ Full GUI | ✗ | ✓ SFTP | ✗ | Limited | ✓ SFTP | ✓ SFTP |
| Infrastructure monitoring | ✓ Dashboard | ✗ | ✗ | ✗ | ✗ | ✗ | ✗ |
| AI command generation | ✓ Approval-gated | ✗ | Partial | ✓ Auto-run | ✗ | ✗ | ✗ |
| MCP server integration | ✓ | ✗ | ✗ | ✗ | ✗ | ✗ | ✗ |
| One-click deployment | ✓ | ✗ | ✗ | ✗ | ✗ | ✗ | ✗ |
| Local credential storage | ✓ AES-256 | ✓ | ✗ Cloud | ✗ Cloud | ✓ | ✓ | ✓ |
| Multi-protocol (RDP/VNC) | ✗ SSH only | ✗ | ✗ | ✗ | ✓ | ✗ | ✓ |
| Mobile app | ✗ | ✗ | ✓ | ✗ | ✓ iOS | ✗ | ✗ |
| Mac-native UI | ✓ | ✓ | ✓ | ✓ | ✓ | Electron | ✓ |
| Price (individual/mo) | $7/user (1 mo free) | Free | $10/user | $20 | \~€49 one-time | Free | Free |
| 5-user team (monthly) | $35 | $0 | $100 | $250 | \~€245 one-time | $0 | N/A |
The pricing gap matters at team scale.
**Termius and Warp charge per user.** Costs grow linearly with headcount. A 5-person Termius Team plan costs $1,200/year.
**CtrlOps at $7/user/month** ($70/user/year, after a 1 month free trial) includes monitoring, deployment, file management, MCP integration, and AI diagnostics that you'd otherwise pay for separately or build with 3 to 4 additional tools.
**SecureCRT at $119 to $190 per license** gives you none of these extras. At 5 licenses, that's $595 to $950 upfront, plus annual maintenance, for a pure terminal emulator.
For more on how different [Windows SSH clients](https://ctrlops.io/blog/best-ssh-clients-windows) compare on similar criteria, we've done the same deep-dive there.
***
## Which SecureCRT Alternative Should You Pick? [#which-securecrt-alternative-should-you-pick]
The best SecureCRT alternative for Mac depends on what you actually need to do with it. No single tool wins every scenario.

**You're a developer managing multiple client servers and need AI terminal that actually works:**
CtrlOps.
Named servers keep client environments organized. Local credentials satisfy NDAs.
> "The 'bash (2)' tab hit too close to home. We literally had a sticky note on the monitor saying which terminal was which. Absolute chaos. What you built is what everyone needed but nobody sat down to actually make."
>
> * Deep Boda, [Product Hunt review](https://www.producthunt.com/products/ctrlops?comment=5380571)
The [AI Terminal](https://ctrlops.io/docs/modules/ai-terminal) diagnoses unfamiliar stacks without Googling. Connect Context7 or GitHub via MCP and the AI reads your actual documentation and codebase before suggesting a single command.
One-click deployment turns a 30 to 45 minute process into under 8 minutes. At $7/user/month - with the first month free - it pays for itself the first incident you resolve in 5 minutes instead of 45. To understand how AI fits into modern server management, read our guide on [AI in DevOps workflows](https://ctrlops.io/blog/ai-in-devops).
**You're a CLI power user who configures everything in dotfiles:**
iTerm2.
Free, Mac-native, 100% keyboard-driven. With `.ssh/config` and tmux, you have a complete SSH workflow. When you outgrow manual file transfers and need monitoring, add CtrlOps alongside it.
**Your team needs the same setup on every device, including mobile:**
Termius.
Cross-device sync across Mac, Windows, Linux, iOS, Android. Accept the cloud credential trade-off, or verify it meets your security requirements first.
**You manage a mixed Linux + Windows environment from a Mac:**
Royal TSX.
SSH, RDP, VNC in one app. The only tool here that handles Windows remote desktop alongside Linux SSH natively.
**You want open-source with zero vendor lock-in:**
Tabby.
Free, MIT-licensed, cross-platform, plugin ecosystem. Heavier on RAM, but more capable than SecureCRT's UI out of the box.
**You live in the terminal writing code locally:**
Warp.
AI Agent Mode and block-based output are the best available for local development. Be careful with Agent Mode on production servers though, since there is no approval gate.
**You just want a light Mac-native SSH/RDP tool:**
DartShell.
Clean, fast, multi-protocol. No AI or monitoring, but zero setup friction.
| Your Situation | Best Pick | Runner-Up |
| ----------------------------------- | --------- | --------- |
| Freelancer, 5 to 15 client servers | CtrlOps | Termius |
| CLI power user, dotfile workflow | iTerm2 | Tabby |
| Cross-platform team with mobile SSH | Termius | CtrlOps |
| Mixed Linux + Windows from Mac | Royal TSX | DartShell |
| Open-source advocate | Tabby | iTerm2 |
| AI-first terminal power user | Warp | CtrlOps |
| Lightweight Mac remote access | DartShell | Royal TSX |
***
## What Does Switching from SecureCRT Actually Look Like? [#what-does-switching-from-securecrt-actually-look-like]
Feature tables help. But the real question is this: how much time do you lose on tasks that should be faster?
Same deployment. Two approaches.
### Deploying with SecureCRT on Mac [#deploying-with-securecrt-on-mac]
1. Open your server list. Find the right session in the tree. (1 to 2 minutes)
2. Connect. Enter passphrase for your SSH key. (1 minute)
3. Run `git pull`. A dependency error appears. Google the error, find a Stack Overflow thread from 2021. (10 to 20 minutes)
4. Config file needs updating. Open SecureFX (separate app, separate license). Navigate to the right directory. (5 to 8 minutes)
5. Upload the fix. Restart the service. Check the browser. (2 to 3 minutes)
**Total: 19 to 34 minutes.** Two apps. Two license costs. Multiple context switches.
### The Same Deployment in CtrlOps [#the-same-deployment-in-ctrlops]
1. Click the server card. Connected instantly. (10 seconds)
2. Open [File Manager](https://ctrlops.io/docs/modules/file-manager). Upload the updated config with drag-and-drop. (1 minute)
3. Open AI Terminal. Type: "pull latest, rebuild, restart PM2." Review the generated commands. Approve. (2 minutes)
4. Check the [infrastructure dashboard](https://ctrlops.io/docs/modules/infra-details). CPU normal. No error spikes. (30 seconds)
**Total: 4 to 5 minutes.** One app. Zero context switches.
***
## Conclusion [#conclusion]
The best **SecureCRT alternatives for Mac** in 2026 are the tools that consolidate workflows into fewer apps.
SecureCRT still connects to servers. But connecting was never the hard part. The hard part is deploying code, debugging production at 2 AM, managing files across servers, and monitoring infrastructure without opening 4 separate tools.
CtrlOps does all of that at $7/user/month ($70/user/year) with a 1 month free trial. The workflow speaks for itself the first time you deploy in 5 minutes instead of 34.
> "Started using CtrlOps a few weeks ago. Honestly didn't expect much. But my DevOps workflow has genuinely shifted: AI Terminal that understands plain English, server management without SSH juggling, backups, deployments, file manager all in one place. I'm doing in 10 minutes what used to take an hour."
>
> * Chintan P., [LinkedIn](https://www.linkedin.com/posts/chintan-poriya_product-review-started-using-ctrlopsai-activity-7467179106200260609-Uoht)
Pick the tool that matches your biggest pain point today. Switch if it stops fitting. The best SSH client is the one you actually use without fighting it.
***
## Frequently Asked Questions [#frequently-asked-questions]
Yes. SecureCRT by VanDyke Software runs on macOS, Windows, and Linux. VanDyke added Mac support in 2010 with version 6.6. The same license key works across platforms. However, the macOS version uses a cross-platform interface that doesn't feel Mac-native. It also lacks AI features, built-in file management, and infrastructure monitoring that newer Mac SSH tools like [CtrlOps](https://ctrlops.io/) and iTerm2 offer.
macOS includes OpenSSH built into Terminal, so you can SSH without installing anything. For a graphical experience similar to PuTTY, iTerm2 is the most popular free option. For a fuller server management experience with AI, file management, and monitoring, [CtrlOps](https://ctrlops.io/) combines everything PuTTY does and adds the features Mac users expect in 2026. You can also check our full list of [PuTTY alternatives for Windows](https://ctrlops.io/blog/putty-alternatives-windows) if you work across both platforms.
**iTerm2** is the best free SecureCRT alternative for Mac if you want a powerful terminal with split panes, hotkey window, and tmux integration. **Tabby** is the best free option if you also need Windows and Linux support with a modern UI. Both are free and open-source. Neither includes AI, monitoring, or deployment features.
Yes. CtrlOps runs natively on macOS (Apple Silicon and Intel) and covers everything SecureCRT does: SSH connections, session management, key-based authentication. It also includes features SecureCRT lacks: a GUI file manager, real-time infrastructure monitoring, an approval-gated AI terminal with MCP server integration, and one-click app deployment. At $7/user/month ($70/user/year) with a 1 month free trial, it costs less annually than a single SecureCRT license. See the full [CtrlOps vs SecureCRT](https://ctrlops.io/compare/ctrlops-vs-securecrt) comparison.
Yes. CtrlOps supports unlimited server connections with named server cards, visual grouping, and one-click connect. Unlike SecureCRT's session tree, CtrlOps also shows live CPU, RAM, and disk metrics for every connected server without running manual commands. The [Script Directory](https://ctrlops.io/docs/modules/ai-terminal/scripts) lets you execute the same command sequence across multiple servers with variable placeholders. For a full guide on multi-server management workflows, see [how to manage multiple servers without losing control](https://ctrlops.io/blog/manage-multiple-servers-without-losing-control).
For Mac users who need cross-device sync and mobile SSH access, Termius is a stronger choice than SecureCRT. It has a modern UI, syncs credentials across Mac, iOS, and Android, and offers team collaboration features. The trade-off is that Termius stores credentials in the cloud (E2E encrypted), while SecureCRT stores everything locally. For users who need local-only credential storage plus AI and monitoring, CtrlOps offers both without cloud dependency. Compare the details in our [CtrlOps vs Termius](https://ctrlops.io/compare/ctrlops-vs-termius) breakdown.
Keep SecureCRT if you need FIPS 140-2 validated encryption for government or defense compliance. Keep it if your workflow depends on advanced scripting in Python, VBScript, or Perl that runs inside the terminal emulator. Keep it if you've invested heavily in SecureCRT session configurations and scripts that would take significant time to migrate. For these enterprise-specific requirements, no current alternative fully matches SecureCRT.
SecureCRT provides a native Apple Silicon (ARM64) build; VanDyke ships a dedicated ARM64 installer alongside the Intel one.
**CtrlOps** at $7/user/month ($70/user/year, after a 1 month free trial) is the lowest-cost SSH tool for Mac with AI command generation. It includes approval-gated AI diagnostics, MCP server integration, web search, and BYOK support for OpenAI, Anthropic Claude, and Google Gemini. **Warp** offers AI at $20/month (Build plan) but auto-runs commands without an approval step. **Termius** has basic AI autocomplete at $10/month but doesn't generate diagnostic commands.
No. SecureCRT scripts cannot run directly on other terminal emulators because they rely on a proprietary scripting API (specifically the `crt` object). If your existing scripts are written in Python, you can run them on SecureCRT for macOS. However, to switch to a different client like CtrlOps, you must rewrite your automation. You can convert your logic into standard shell/Python scripts (using libraries like Netmiko/Paramiko), write native Python scripts using iTerm2's API, or use CtrlOps's built-in **Script Directory** which stores reusable command sequences with variable placeholders.
SecureCRT does not support exporting sessions to a generic CSV or XML format; its built-in `Tools > Export Settings` option generates a proprietary XML backup. SecureCRT stores individual connection settings as separate `.ini` files in its Config directory. To migrate to CtrlOps, you can use a Python or VBScript export script (available on the VanDyke forums) to parse those `.ini` files into a standard CSV, and then copy those columns into the CtrlOps import template to import all your hosts, ports, and credentials in bulk.
iTerm2 does not have a graphical SFTP panel or a side-by-side file tree. However, it does support file transfers. Besides standard command-line tools like `scp`, `rsync`, and `sftp`, iTerm2 allows you to upload files via drag-and-drop and download them with a click if you install iTerm2's **Shell Integration** helper scripts on the remote host (using the `it2ul` and `it2dl` utilities). If you want an integrated graphical file browser next to your terminal window without setup, you will need a client like CtrlOps or Termius.
The most native option is the built-in macOS **Terminal.app**, which acts as a wrapper for standard system-level OpenSSH. For third-party options, **iTerm2** is the most popular terminal emulator written specifically for macOS in Cocoa/Objective-C. If you want a GUI client for managing connections, **Royal TSX** and **DartShell** are designed specifically around macOS visual guidelines, and Swift-native options like **Termy** offer native terminal wrappers. **CtrlOps** is also styled to match modern macOS aesthetics, whereas SecureCRT uses a dated, cross-platform UI.
---
# 14 SSH Key Management Best Practices for Developers (2026) (/blog/ssh-key-management-best-practices)
Author: Hiren Kalariya | Role: Co-Founder & CEO, TST Technology | Published: 2026-06-01 | Updated: 2026-09-07 | Tags: ssh key management, ssh keys, ed25519, ssh security, devops | Reading Time: 38 min read
> 14 SSH key management best practices for 2026 - Ed25519 keys, passphrases, per-user access, instant revocation, and a complete audit checklist.
## Key Takeaways [#key-takeaways]
Most SSH security failures come from poor key hygiene, not sophisticated attacks. The core practices: generate Ed25519 keys, protect every private key with a passphrase, keep private keys local-only (never in cloud-synced folders), manage access per user instead of shared team keys, and revoke access the moment someone leaves. The 14 practices in this guide cover the full key lifecycle - from generation to revocation.
* **Freelancers managing multiple clients** - Use per-client key pairs and local-only credential storage. A compromised laptop should expose one client, not all twelve.
* **Startup CTOs with a growing team** - Implement per-user key pairs with a clear revocation process. "I'll remove their key later" is how ex-employees retain production access for months.
* **Compliance-sensitive teams** - Local-only key storage with no cloud sync. Client NDAs often prohibit third-party credential storage, and most SSH tools sync to cloud by default.
| Practice | Manual CLI | With CtrlOps |
| --------------------------- | -------------------------------------- | ----------------------------------------- |
| Generate Ed25519 key | `ssh-keygen -t ed25519` | SSH Setup Wizard, 3 guided steps |
| Copy key to server | `ssh-copy-id` or manual append | One-click Copy Key button |
| Revoke a key | SSH in, edit authorized\_keys manually | Revoke button, instant, no terminal |
| Audit all keys on a server | Manual `cat authorized_keys` | Visual key registry per server |
| Per-client key organization | Manual `~/.ssh/config` editing | Named server cards, per-server management |
| **Price** | Free (hours of DIY setup time) | **$7/month per user, 1 month free trial** |
Prefer to watch instead? All 14 practices - key generation, passphrases, per-user access, and same-day revocation - walked through end to end:
***
## Why SSH Key Management Is the Security Gap Hiding in Plain Sight [#why-ssh-key-management-is-the-security-gap-hiding-in-plain-sight]
You just onboarded a new client. They hand you server credentials over Slack. You drop the IP into your terminal, generate a key on the spot, paste it into `authorized_keys`, and move on. Six months later the project ends. The key is still there. You never removed it. Neither did the three developers who worked on it before you.
That pattern plays out across thousands of servers every day. For freelance developers juggling 8 to 12 client environments, startup CTOs whose ex-devs still technically have production access, and agency engineers who have never actually looked inside `~/.ssh/` - SSH key management is the security gap hiding in plain sight.
SSH keys are the front door to your entire infrastructure. And most developers manage them the same way they manage browser bookmarks: add when needed, never audit, never clean up. This guide covers real-world SSH key workflows across multi-server setups, CLI-only and GUI-assisted to give you a complete guide, no-fluff reference.
These 14 SSH key management best practices cover the full key lifecycle - from generation to revocation.
***
## The 14 SSH Key Management Best Practices [#the-14-ssh-key-management-best-practices]
These 14 practices walk through the full lifecycle of managing SSH keys - generation, key exchange, distribution, passphrase handling, rotation, audit, and deletion - with the exact commands to use at each step. The first twelve apply to every developer or small team managing remote servers. The last two (FIDO2 hardware keys and SSH certificates) cover advanced setups for teams whose needs go beyond standard per-user key files.
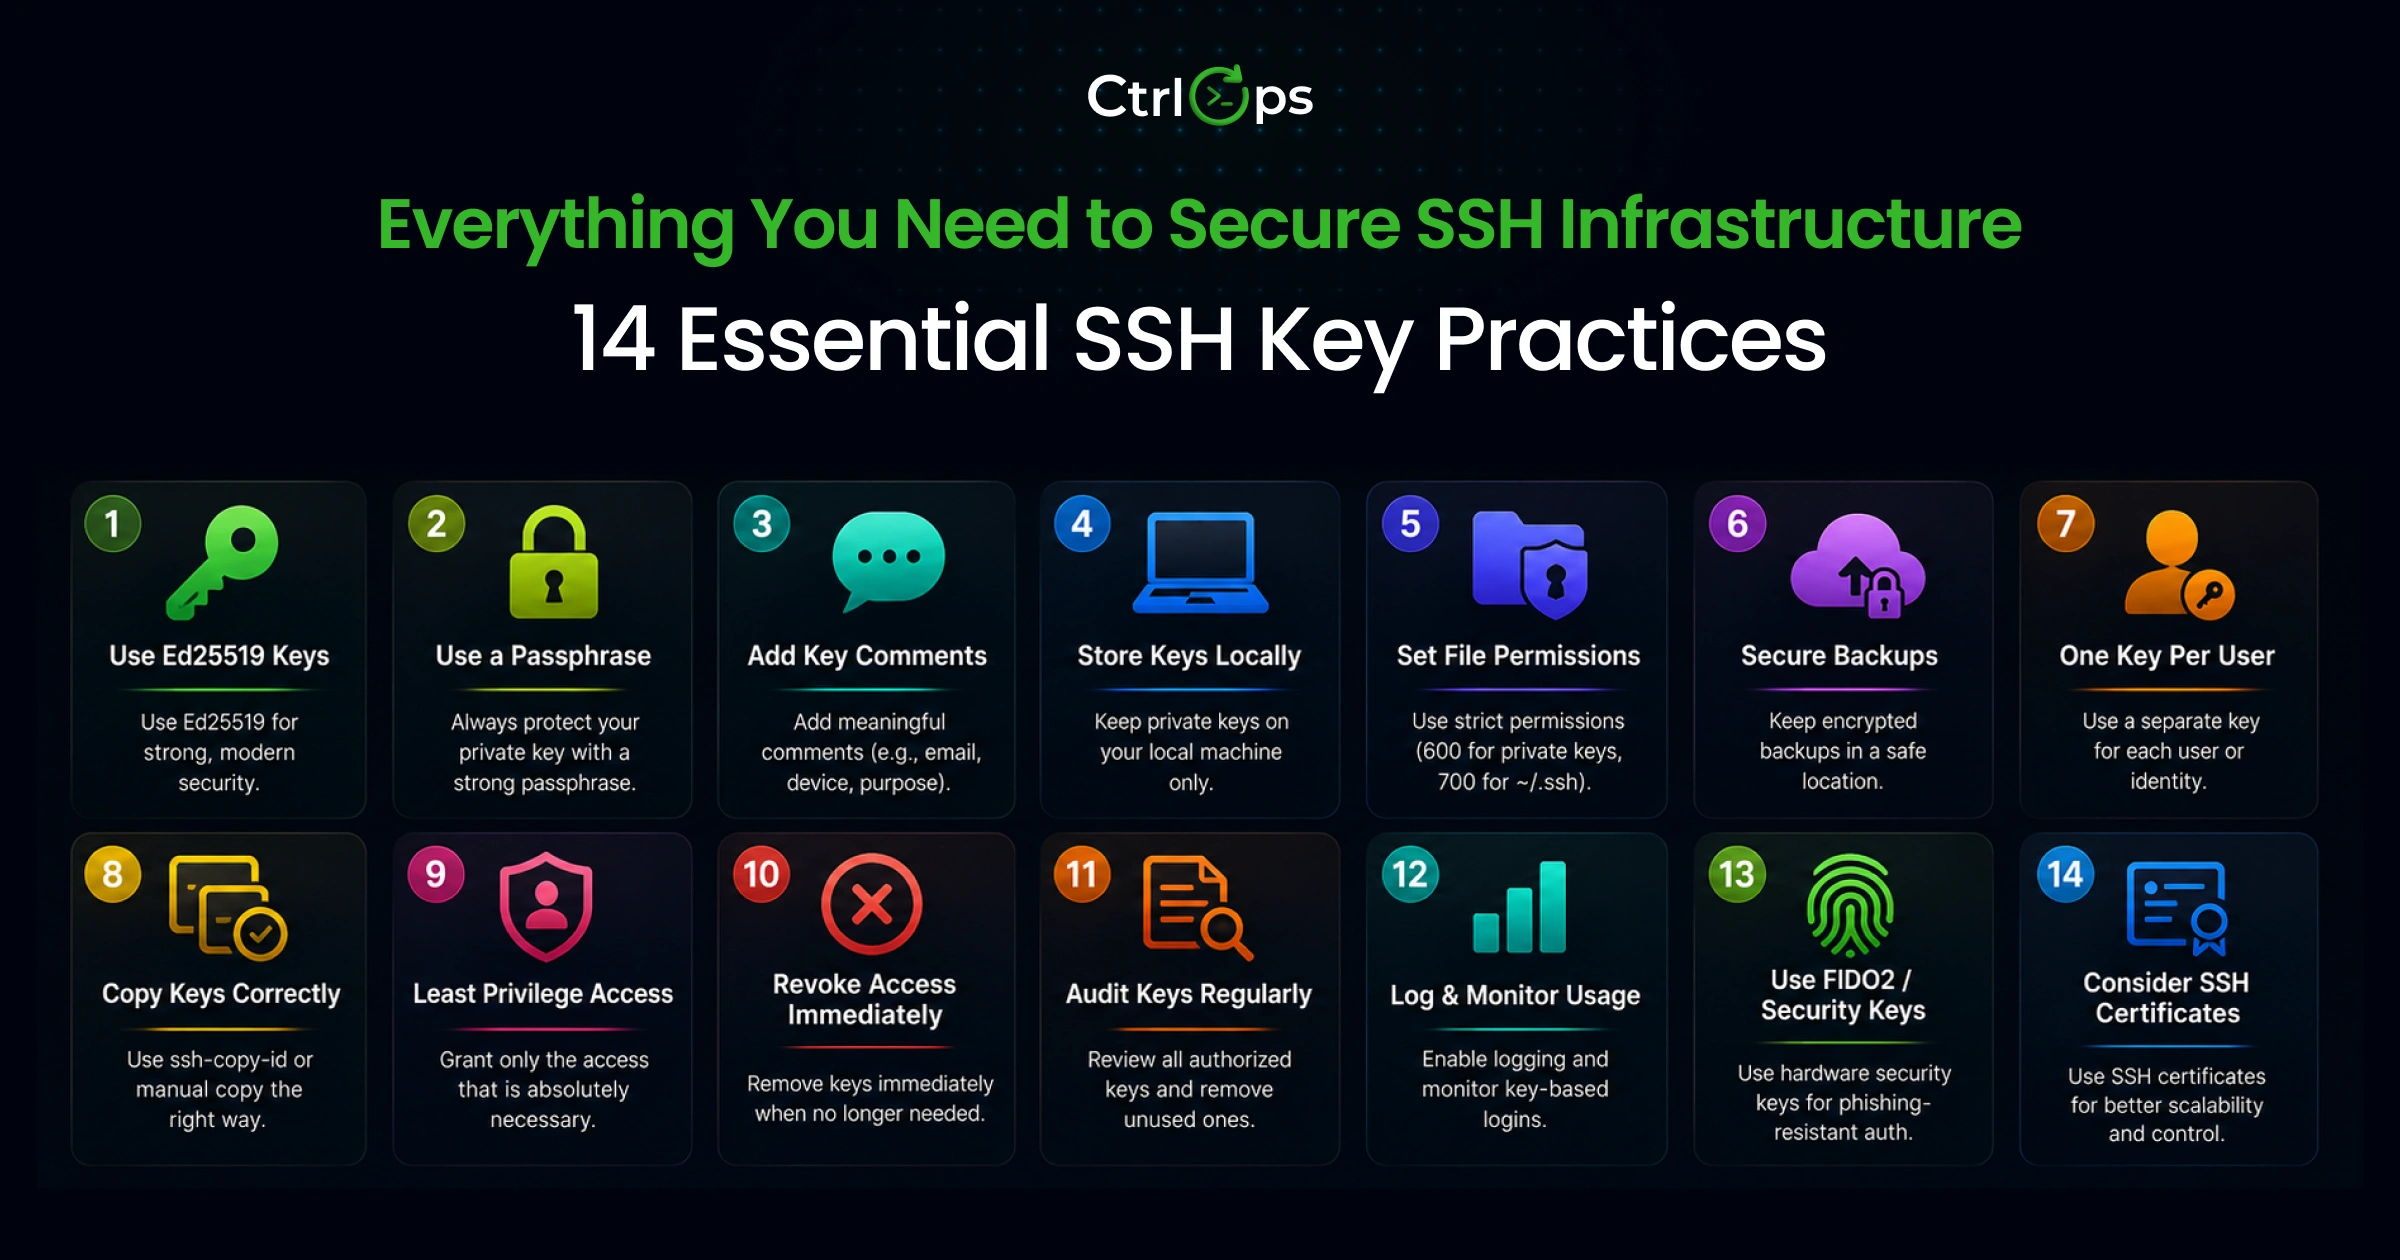
### Practice 1: Always Use Ed25519 Keys, Not RSA 2048 [#practice-1-always-use-ed25519-keys-not-rsa-2048]
Ed25519 is the recommended public-key algorithm for new OpenSSH deployments due to its strong security properties, compact key size, fast signature operations, and resistance to several implementation-level attacks. Use it by default for every new key pair. RSA 2048 is still secure today, but it is no longer the best choice for new keys when Ed25519 is available. Reserve RSA for environments that require it for compatibility or policy reasons, and prefer 4096-bit if you must generate a new RSA key.
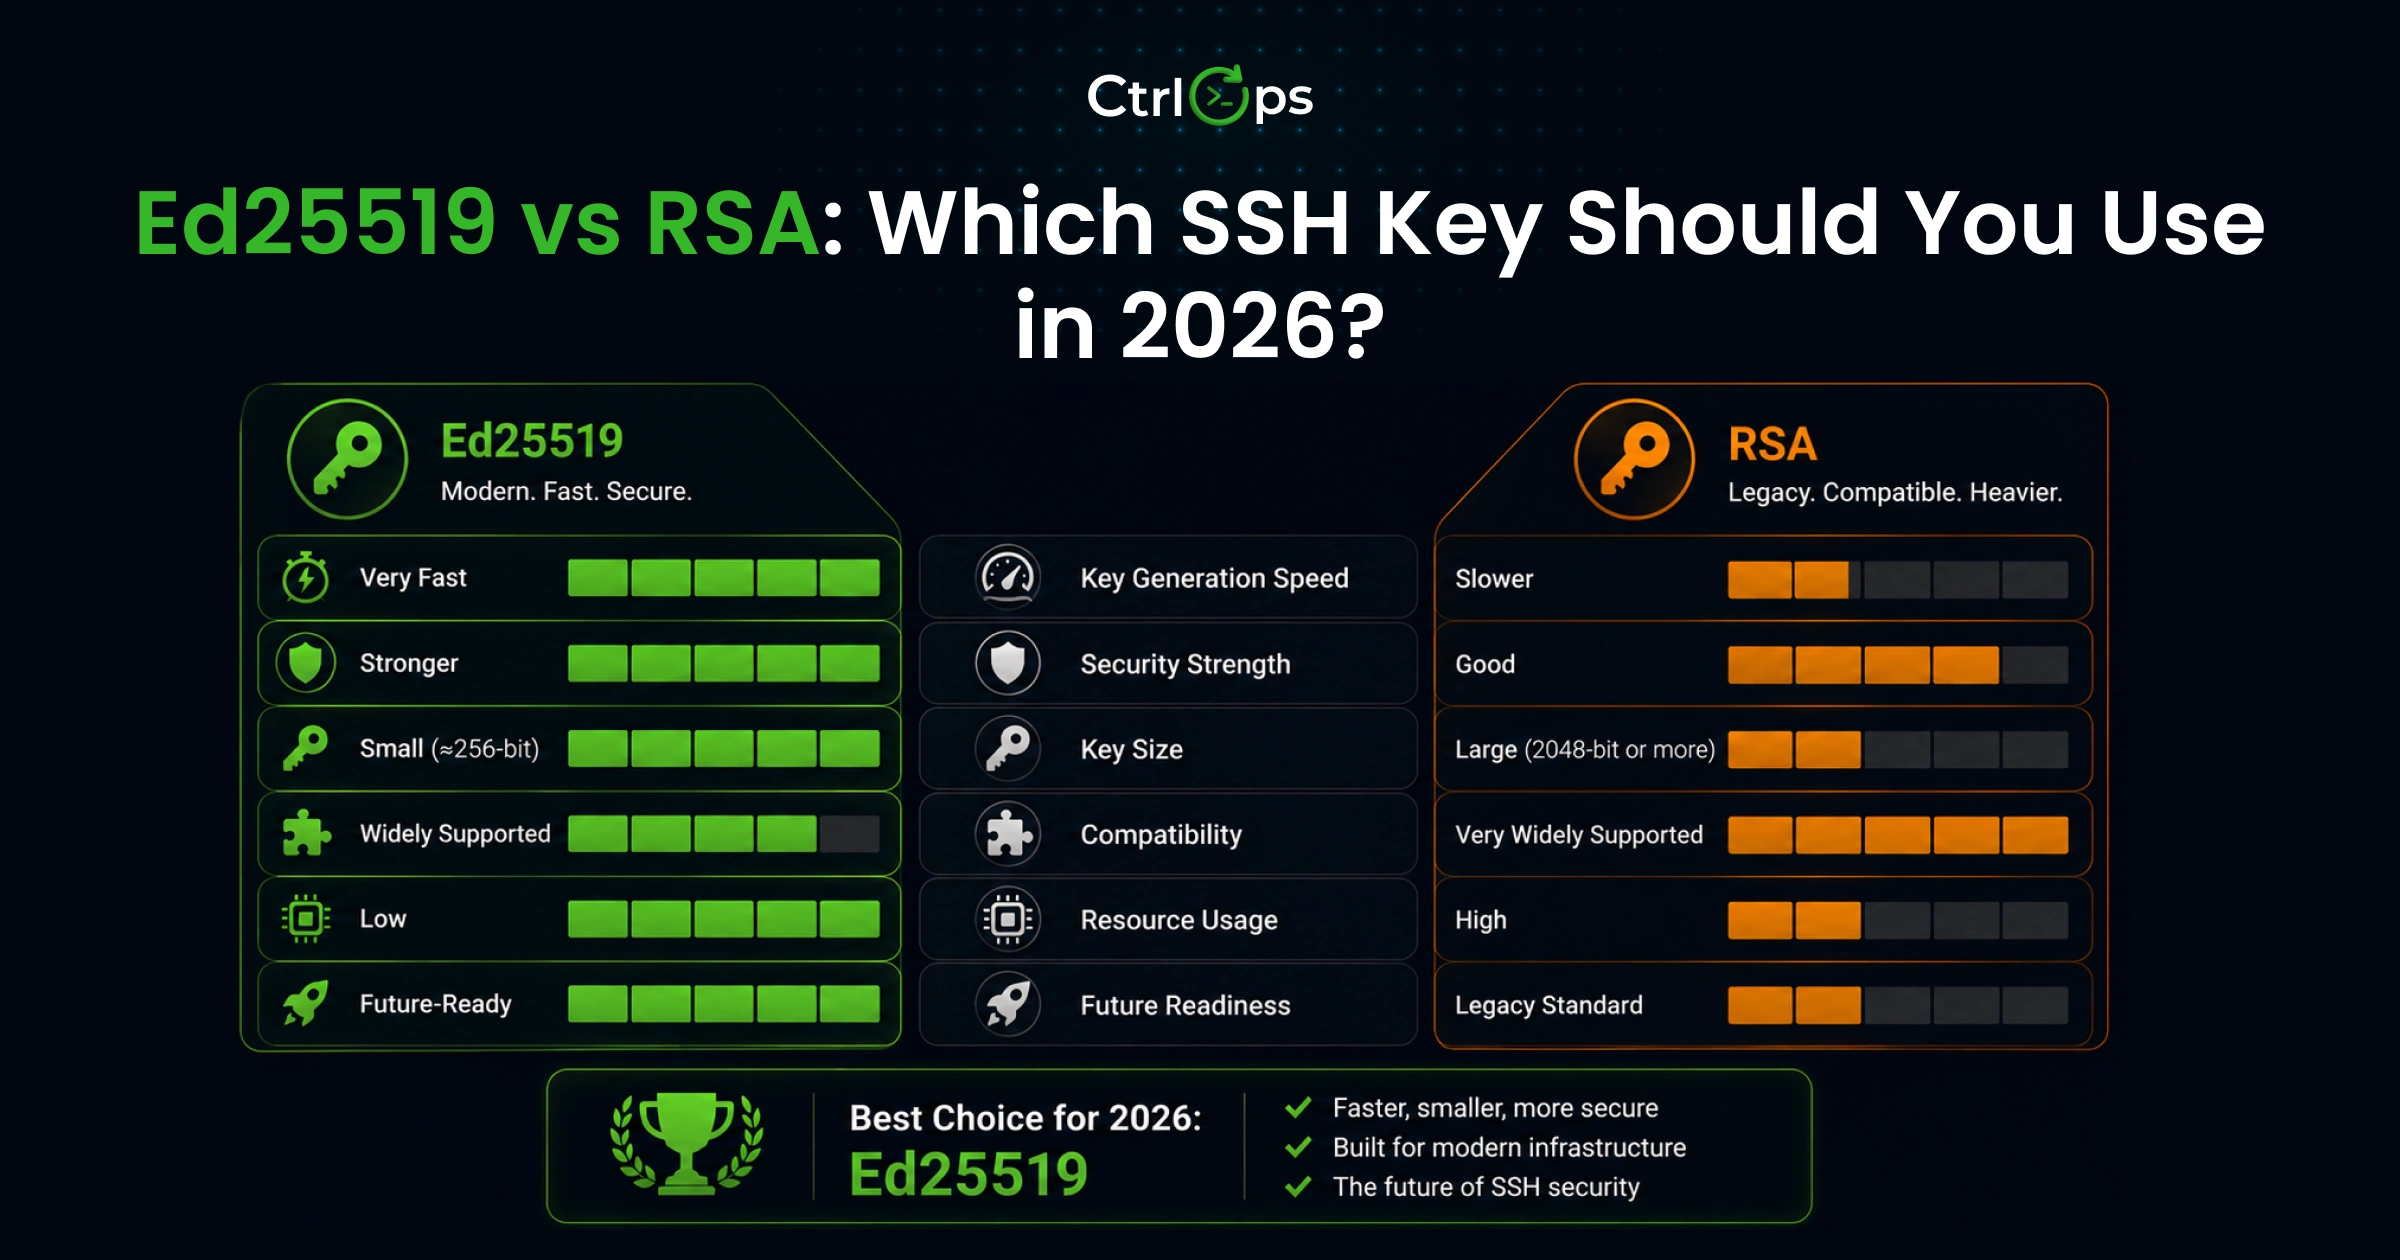
**Why Ed25519 Is Preferred Over RSA For New Deployments:**
| Property | Ed25519 | RSA 2048 | RSA 4096 |
| ----------------------- | ---------------------- | ------------------------------------- | --------------------------- |
| Key size | 256 bits | 2048 bits | 4096 bits |
| Connection speed | Fastest | Slow | Slowest |
| Security level | Equivalent to RSA 3072 | Acceptable for most current use cases | Acceptable |
| Side-channel resistance | High (by design) | Lower | Lower |
| Support | OpenSSH 6.5 and newer | Universal | Universal |
| Verdict | Use this | Avoid for new keys | Only if Ed25519 unsupported |
Ed25519 connections establish significantly faster than equivalent-security RSA keys - a well-documented property of the underlying Curve25519 algorithm that requires fewer CPU operations per handshake. For modern SSH deployments, [Mozilla's OpenSSH Guidelines](https://infosec.mozilla.org/guidelines/openssh) list Ed25519 as the recommended host key algorithm ahead of all RSA variants. For new SSH key generation, Ed25519 is the recommended choice for its superior security design, excellent performance, and compact key size.
Use RSA 4096 only when compatibility with legacy systems is required.
**Generate an Ed25519 key:**
```bash
ssh-keygen -t ed25519 -C "your-comment-here"
```
Replace `your-comment-here` with something meaningful - your name, machine name, or client name. More on comments in Practice 6.
Prefer a GUI? You can [generate an Ed25519 or RSA key pair with our browser-based tool](/tools/ssh-key-generator) - it runs entirely client-side, so the private key never leaves your machine.
For a genuinely old server that predates OpenSSH 6.5, fall back to RSA:
```bash
ssh-keygen -t rsa -b 4096 -C "your-comment-here"
```
Avoid generating new RSA 2048 keys when you can use Ed25519 instead. If you must use RSA for compatibility or policy reasons, prefer 4096-bit over 2048-bit for new keys.
**With CtrlOps SSH Setup Wizard:** In the left sidebar, under TOOLS, click SSH Setup. The wizard recommends Ed25519, generates the pair in one click, and shows your new key ready to copy. No command memorization needed. See the [SSH Setup Wizard documentation](https://ctrlops.io/docs/modules/ssh-management#generate-an-ssh-key-gui-wizard) for step-by-step details.
See how CtrlOps handles SSH access end-to-end - adding, viewing, and removing keys:
**Bottom line:**
Ed25519 is faster, shorter, and more secure than RSA 2048. For nearly all modern SSH deployments in 2026, Ed25519 is generally the preferred choice over RSA 2048, offering stronger performance and better security with broad support across current systems. If a platform says it only supports RSA, check again - most added Ed25519 support after OpenSSH 6.5 launched in 2014.
#### Use Modern SSH Key Exchange Algorithms (Including Post-Quantum) [#use-modern-ssh-key-exchange-algorithms-including-post-quantum]
SSH key exchange (KEX) is not the same as copying a public key to a server. It refers to the cryptographic handshake that happens at the start of every SSH connection - both sides negotiate a session key used to encrypt the entire session. The algorithm used for this handshake is separate from your key type (Ed25519 vs RSA).
This matters in 2026 because weak KEX algorithms are still active on many servers by default, and post-quantum KEX is now the OpenSSH standard.
**What "key exchange" means in practice:**
| KEX Algorithm | Status | Notes |
| ----------------------------- | -------------------- | ---------------------------------------------------- |
| `diffie-hellman-group1-sha1` | ❌ Remove immediately | 1024-bit DH, broken |
| `diffie-hellman-group14-sha1` | ❌ Remove | SHA-1, flagged by all modern scanners |
| `curve25519-sha256` | ✅ Keep | Classical baseline, fast and secure |
| `sntrup761x25519-sha512` | ✅ Keep | Post-quantum hybrid (OpenSSH 9.0+ default) |
| `mlkem768x25519-sha256` | ✅ Preferred | NIST-standardized PQC hybrid (OpenSSH 10.0+ default) |
**The post-quantum context:** Since OpenSSH 9.0 (April 2022), the default key exchange has included `sntrup761x25519-sha512` - a hybrid combining classical X25519 elliptic-curve Diffie-Hellman with a post-quantum key encapsulation mechanism. OpenSSH 10.0 (April 2025) moved `mlkem768x25519-sha256` to the top of the default list. [GitHub followed in September 2025](https://github.blog/engineering/platform-security/post-quantum-security-for-ssh-access-on-github/), enabling post-quantum KEX for all Git-over-SSH connections. Starting with OpenSSH 10.1, connections that fall back to non-post-quantum KEX will display a warning: *"This session may be vulnerable to store now, decrypt later attacks."*
If your server runs OpenSSH 9.0 or newer, the post-quantum defaults are already active. The action item is removing the weak algorithms that may still be enabled as fallback options.
**Harden your KEX configuration in `/etc/ssh/sshd_config`:**
```bash
# Check what KEX your server currently supports
ssh -Q kex
# Add to /etc/ssh/sshd_config to remove weak algorithms
KexAlgorithms mlkem768x25519-sha256,sntrup761x25519-sha512,curve25519-sha256,diffie-hellman-group-exchange-sha256
# Restart SSH daemon
sudo systemctl restart sshd
# Verify the weak algorithms are gone
ssh -oKexAlgorithms=diffie-hellman-group1-sha1 localhost
# Expected: "no matching key exchange method found"
```
Remove `diffie-hellman-group1-sha1` and `diffie-hellman-group14-sha1` entirely. These use SHA-1, are flagged by every modern vulnerability scanner, and have no place in a 2026 server configuration. For authoritative KEX recommendations, see [Mozilla's OpenSSH Guidelines](https://infosec.mozilla.org/guidelines/openssh) and [openssh.org/pq.html](https://www.openssh.org/pq.html).
**Bottom line:**
Your SSH key type (Ed25519) and your SSH key exchange algorithm (KEX) are separate settings. A server using Ed25519 keys but still allowing
`diffie-hellman-group1-sha1`
as a fallback KEX is only half-hardened. Check both. OpenSSH 9.0+ has post-quantum KEX enabled by default - but weak legacy algorithms may still be listed unless you explicitly remove them.
***
### Practice 2: One Key Pair Per Machine, Per Use Case [#practice-2-one-key-pair-per-machine-per-use-case]
Never reuse the same private key across multiple machines or purposes. Create a separate key pair for each laptop, each work context, and each major client relationship.
The logic is simple. If one private key is compromised, it should expose exactly one machine worth of access - not your entire server fleet.
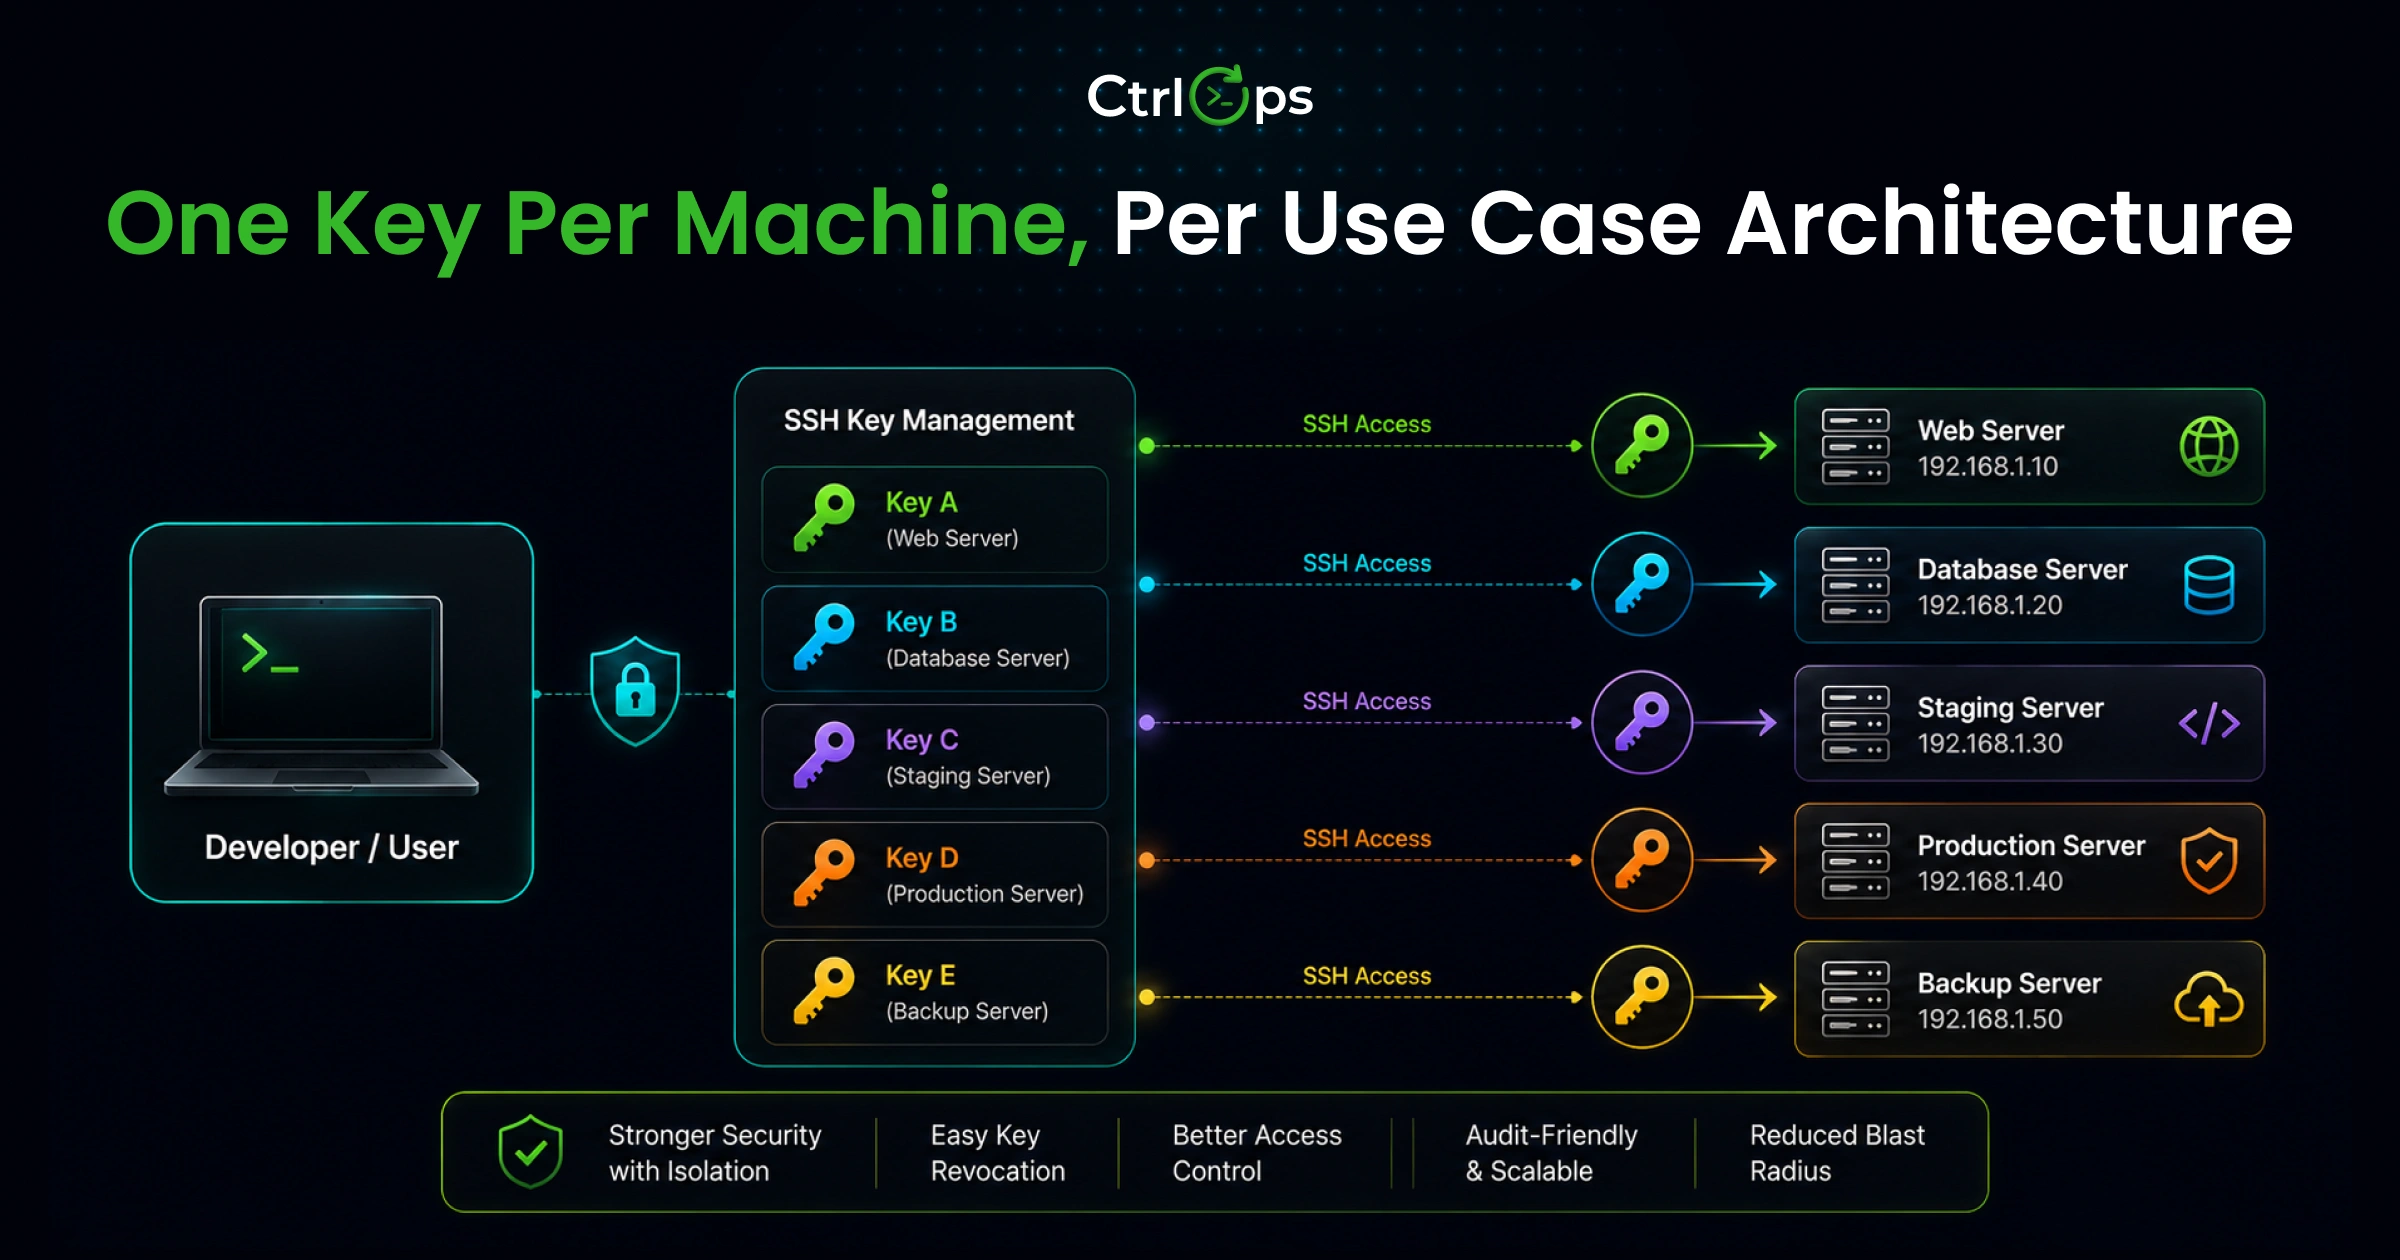
**Common key separation patterns:**
```
~/.ssh/
├── id_ed25519 # Personal default key, home laptop
├── id_ed25519.pub
├── client_acme_ed25519 # Client A, freelance project
├── client_acme_ed25519.pub
├── client_beta_ed25519 # Client B, separate key
├── client_beta_ed25519.pub
├── work_laptop_ed25519 # Office machine, different device = different key
└── work_laptop_ed25519.pub
```
Map each key to the right servers in `~/.ssh/config`:
```
Host acme-prod
HostName 203.0.113.10
User ubuntu
IdentityFile ~/.ssh/client_acme_ed25519
Host beta-staging
HostName 198.51.100.20
User ec2-user
IdentityFile ~/.ssh/client_beta_ed25519
```
This setup takes 15 minutes to configure once. A compromised laptop key then affects only that laptop's servers - not every client you have ever worked with.
**Reality check:**
The "one key for everything" shortcut is the most common SSH security mistake developers make. When your laptop gets stolen, an attacker who cracks that one key has access to every server you ever added it to. Separate keys are damage control, not paranoia.
***
### Practice 3: Protect Every Private Key with a Passphrase [#practice-3-protect-every-private-key-with-a-passphrase]
A passphrase provides an additional encryption layer for the private key material stored on disk. Possession of the key file alone is insufficient without knowledge of the passphrase. Without a passphrase, anyone who gains physical or file-system access to your machine can use your SSH key right away, with no additional authentication required.
Generate a key with a passphrase:
```bash
ssh-keygen -t ed25519 -C "work-laptop-2026"
```
The tool prompts:
```
Enter passphrase (empty for no passphrase): [type a strong passphrase]
Enter same passphrase again: [confirm]
```
Use a real passphrase. Four to six random words, a diceware phrase, not a variation of your login password.
**Avoid re-typing your passphrase dozens of times a day.** Add your key to the SSH agent once per session:
```bash
ssh-add ~/.ssh/id_ed25519
```
On macOS, persist it across reboots:
```bash
ssh-add --apple-use-keychain ~/.ssh/id_ed25519
```
The agent holds your decrypted key in memory for the session. You type the passphrase once. Every subsequent SSH connection uses it silently. The key is never written to disk unencrypted. This is not a security compromise.
**Bottom line:**
A passphrase-protected key that gets stolen is useless without the passphrase. An unprotected key is an instant compromise. Adding a passphrase costs you one
`ssh-add`
call per day. Not adding one costs you an incident response.
***
### Practice 4: How to Remove a Passphrase When You Actually Need To [#practice-4-how-to-remove-a-passphrase-when-you-actually-need-to]
Sometimes you need a passphrase-free key - for automated CI/CD pipelines, cron jobs that SSH into servers, or deployment scripts that run unattended. Removing a passphrase is straightforward. Here is how to do it safely.
**Remove a passphrase from an existing key:**
```bash
ssh-keygen -p -f ~/.ssh/id_ed25519
```
The tool prompts:
```
Enter old passphrase: [current passphrase]
Enter new passphrase (empty for no passphrase): [press Enter]
Enter same passphrase again: [press Enter]
Your identification has been saved with the new passphrase.
```
Pressing Enter for the new passphrase sets it to empty, effectively removing it.
**Only do this for dedicated automation keys.** Create a separate key pair specifically for CI/CD use. Never strip the passphrase from your main developer key.
**Correct workflow for automation keys:**
1. Generate a dedicated key: `ssh-keygen -t ed25519 -C "ci-deploy-key" -f ~/.ssh/ci_deploy_ed25519`
2. Remove the passphrase: `ssh-keygen -p -f ~/.ssh/ci_deploy_ed25519`
3. Add only this key's public key to the target server
4. Restrict this key to specific commands on the server using the `command=` prefix in `authorized_keys`
5. Rotate this key every 90 days or when a project ends
**Reality check:**
A passphrase-free key on a shared CI system is an accepted tradeoff - but only when that key is scoped tightly. If your deploy key can
`sudo`
into anything on production, a compromised CI system is a full production breach. Restrict it to exactly what the pipeline needs and nothing more.
***
### Practice 5: Avoid Storing Raw Private Keys In Consumer Cloud Storage [#practice-5-avoid-storing-raw-private-keys-in-consumer-cloud-storage]
Your private key files - `id_ed25519`, `client_acme_ed25519`, anything without a `.pub` extension - should never leave your local machine. Not in Dropbox. Not in Google Drive. Not synced to iCloud. Not pasted into Notion "for backup." And definitely not committed to a Git repository.
According to [Wiz Research's November 2025 investigation of the Forbes AI 50](https://www.wiz.io/blog/forbes-ai-50-leaking-secrets), 65% of leading AI companies had verified secret leaks on GitHub - with exposed material including API keys, tokens, and credentials buried in deleted forks, gists, and commit history that standard scanners never reach.
**Secure local storage rules:**
```bash
# Private key, must be 600
chmod 600 ~/.ssh/id_ed25519
# Public key, 644 is fine
chmod 644 ~/.ssh/id_ed25519.pub
# Directory permissions, must be 700
chmod 700 ~/.ssh
```
**For backup:** Back up your `~/.ssh/` directory to an encrypted local drive or a password manager with secure SSH key storage. Never sync it as plain files to any cloud folder.
**The tool sync problem:** Several SSH client tools sync credentials to the cloud by default. If a client NDA prohibits storing their server credentials on third-party servers, verify that your SSH tool is genuinely local-only. Tools that sync keys to cloud servers without explicit user control create a compliance exposure, not just a security one.
CtrlOps stores all credentials locally on your machine only. Nothing syncs to any cloud service. Your keys stay exactly where you put them. Read more about [CtrlOps' local-first SSH security architecture](https://ctrlops.io/docs/core/ssh-security).
The local-plaintext version of this problem is just as common. Softnoesis kept access for fifteen to twenty servers in a notepad file across eight-plus client projects before it moved. [None of those credentials sit in a text file now](/case-studies/softnoesis).
**Bottom line:**
Cloud-synced private keys are a security and compliance liability. Needing backup access is a legitimate concern, but the safer solution is an encrypted local backup rather than storing sensitive keys in a cloud-synced folder. The security risk introduced by a sync compromise often outweighs the convenience.
***
### Practice 6: Add Meaningful Key Comments [#practice-6-add-meaningful-key-comments]
The `-C` flag when generating a key adds a comment to the public key file. Most developers skip it or use their email address. The result: a server's `authorized_keys` file that looks like this:
```
ssh-ed25519 AAAA...
ssh-ed25519 AAAA...
ssh-ed25519 AAAA...
```
Three keys. Zero idea whose they are, when they were added, or which machine they came from.
**Use descriptive comments instead:**
```bash
ssh-keygen -t ed25519 -C "bhautik-macbook-pro-2025"
ssh-keygen -t ed25519 -C "client-acme-deploy-key"
ssh-keygen -t ed25519 -C "ci-cd-github-actions"
```
Now your `authorized_keys` reads:
```
ssh-ed25519 AAAA... bhautik-macbook-pro-2025
ssh-ed25519 AAAA... client-acme-deploy-key
ssh-ed25519 AAAA... ci-cd-github-actions
```
When you need to revoke a key - especially after someone leaves the team - you know exactly which line to remove without comparing 64-character hex strings.
In CtrlOps' [SSH Management tab](https://ctrlops.io/docs/modules/ssh-management), the key comment appears as the "Name / Identity" column in the key registry. A useful comment means finding and revoking the right key takes seconds.
**Bottom line:**
Comments cost zero security and save significant time during every revocation event. A comment like "dev-laptop-alex-2025" tells you immediately whether to remove it when Alex leaves. A blank comment tells you nothing.
***
### Practice 7: Copy Keys to Servers Correctly, Not by Hand [#practice-7-copy-keys-to-servers-correctly-not-by-hand]
Getting your public key onto a server is a step most developers do once, under pressure, in a way they never document. Here are the three correct methods, from fastest to most manual.
**Method 1 (Recommended): `ssh-copy-id`**
When you already have password access to the server:
```bash
ssh-copy-id -i ~/.ssh/id_ed25519.pub username@your-server-ip
```
This appends your public key to `~/.ssh/authorized_keys` on the server, creates the `.ssh` directory if needed, and sets correct permissions - all automatically.
**Method 2: Manual append**
```bash
# Step 1: Copy your public key
cat ~/.ssh/id_ed25519.pub
# Step 2: SSH into the server
ssh username@your-server-ip
# Step 3: Create .ssh directory
mkdir -p ~/.ssh
chmod 700 ~/.ssh
# Step 4: Append the public key
echo "YOUR_PUBLIC_KEY_HERE" >> ~/.ssh/authorized_keys
# Step 5: Set correct permissions
chmod 600 ~/.ssh/authorized_keys
```
**Method 3: Cloud provider dashboard**
For first-time setup on AWS, DigitalOcean, Hetzner, or Vultr - add your public key through the provider's UI before provisioning the server. Cleanest option for new instances.
**With CtrlOps SSH Setup Wizard:** The wizard shows all three methods with pre-filled commands and a one-click Copy Key button for your public key. You click Copy Key, run one command in a terminal, done. No hunting for the key file path, no typos in a long key string. Follow the [CtrlOps first connection guide](https://ctrlops.io/docs/getting-started/first-connection) to walk through the full process.
See the full server add and key setup flow from zero:
**Reality check:**
The most common SSH failure after key setup is wrong file permissions.
`chmod 600 ~/.ssh/authorized_keys`
and
`chmod 700 ~/.ssh`
are not optional. A world-readable
`authorized_keys`
file causes OpenSSH to silently reject key authentication. The error says "Permission denied (publickey)" - but the actual cause is a permissions mismatch, not a key problem. If octal permission values never quite stick in your memory, our free
[chmod calculator](/tools/chmod-calculator)
translates them both ways.
***
### Practice 8: Manage SSH Access Per User, Not Per Team [#practice-8-manage-ssh-access-per-user-not-per-team]
Every person who needs SSH access to a server should have their own key pair. Their public key goes into `authorized_keys`. No sharing private keys between teammates.
This is the rule most small teams break - and the one that causes the most damage when someone leaves.
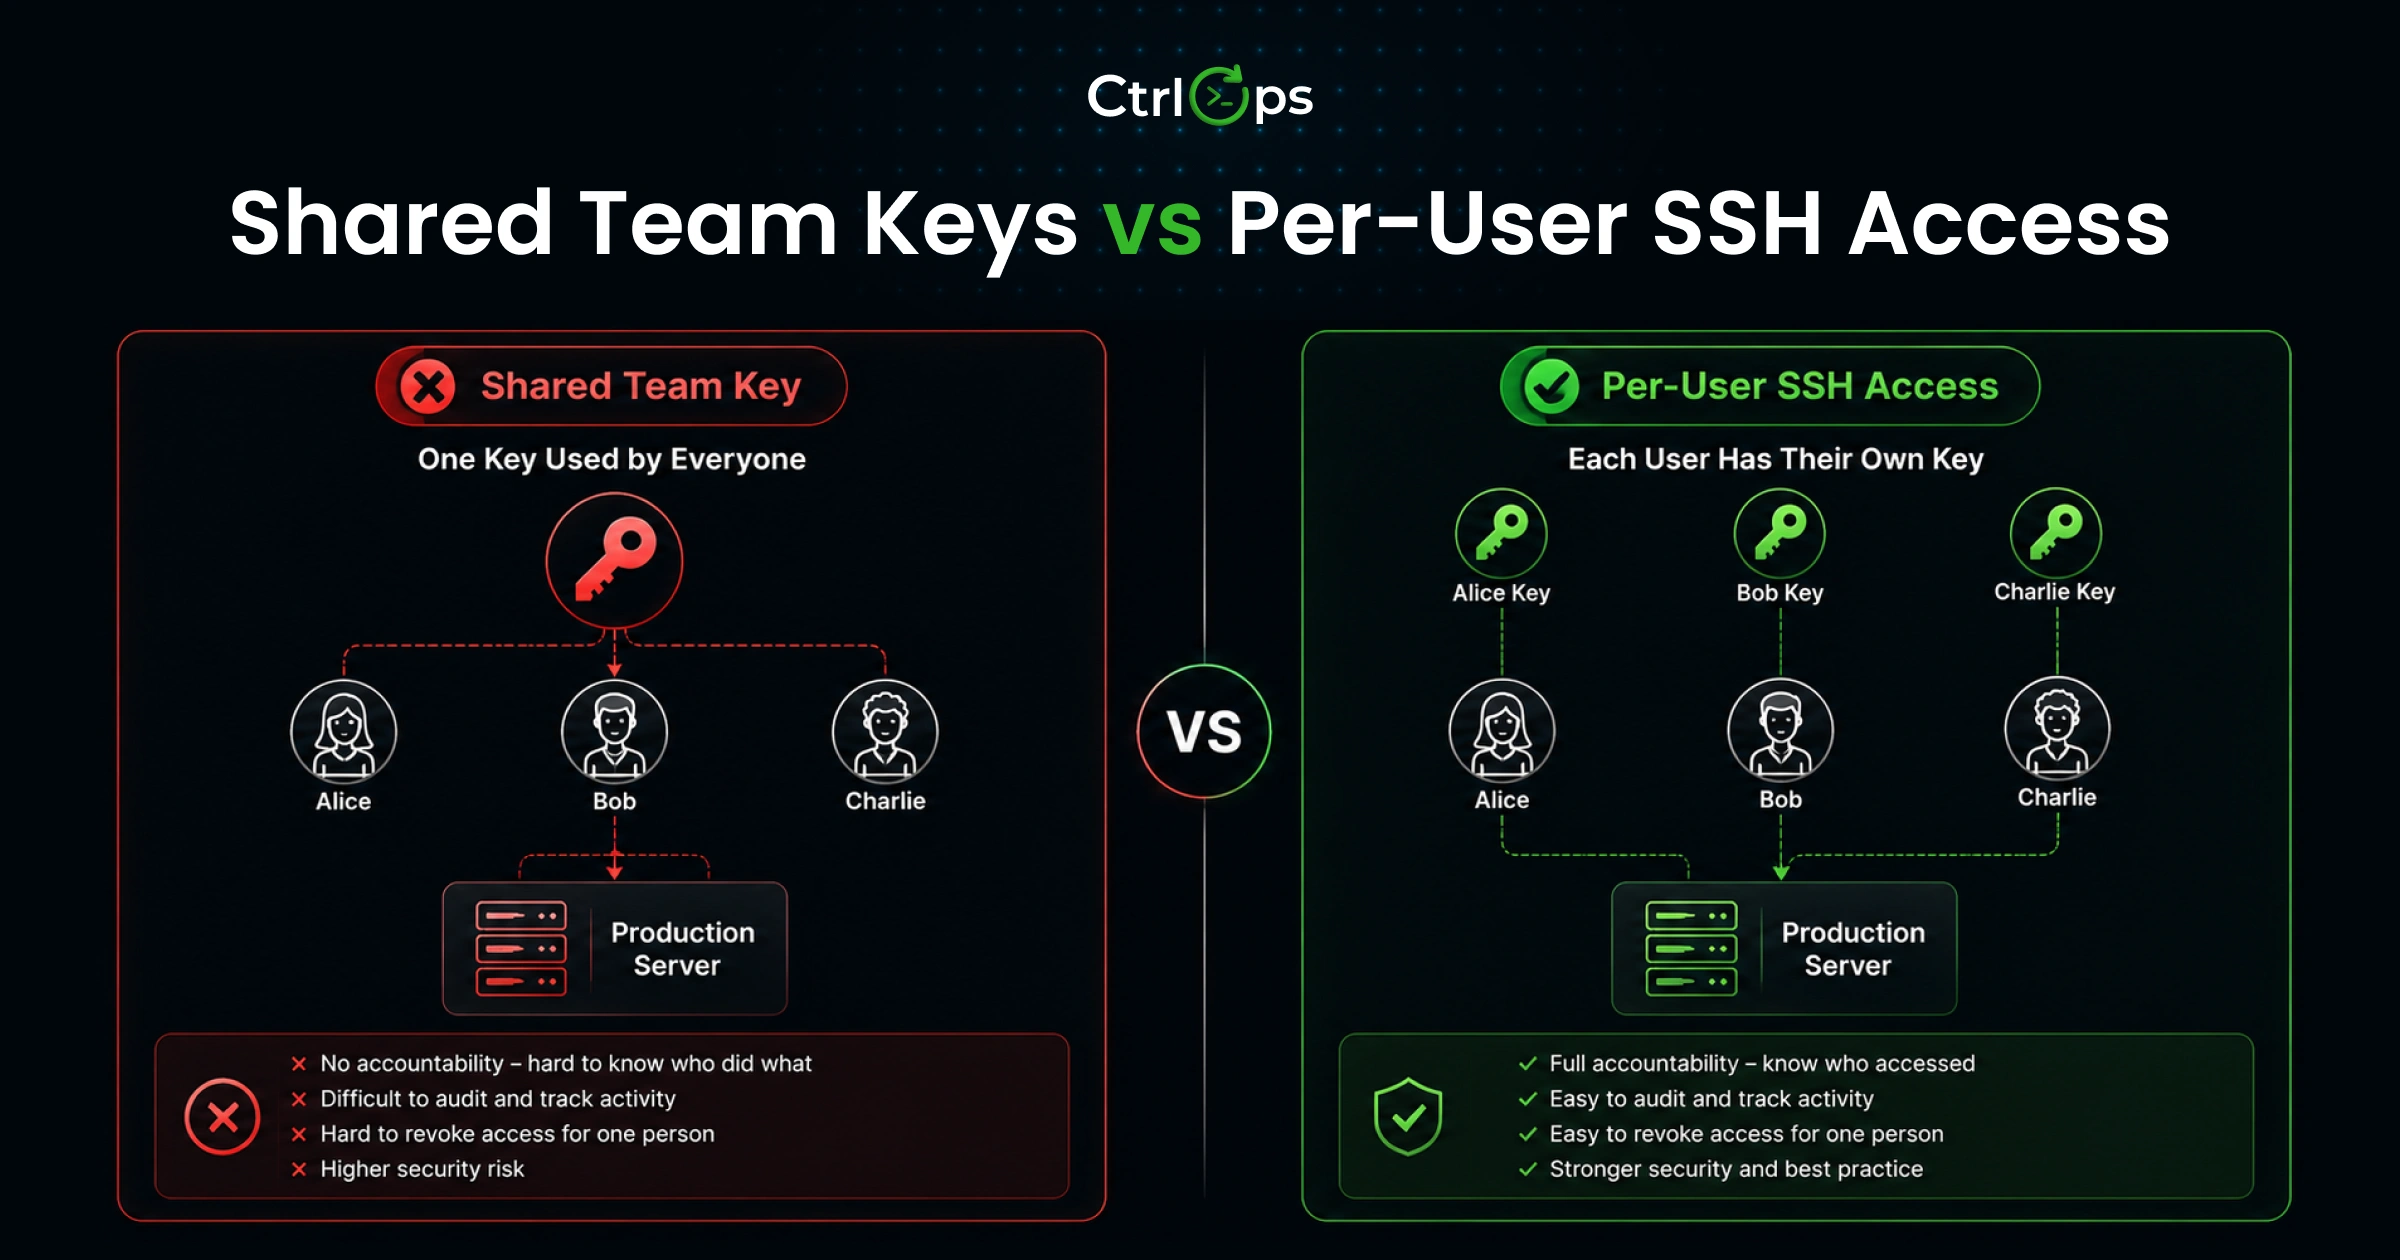
**Shared key scenario (dangerous):**
The team creates one `team_deploy_key`. Everyone uses the same private key. A developer leaves. To be truly safe, you'd need to regenerate and redistribute the key to everyone still on the team. In practice, nobody does this. The old key stays valid for months or years.
**Per-user key scenario (correct):**
Each developer generates their own Ed25519 key pair. Each developer's public key is added to `authorized_keys` on the servers they need access to. A developer leaves - revoke their single entry from `authorized_keys` in 30 seconds. No key redistribution. No disruption for anyone else.
A clean `authorized_keys` file looks like:
```
ssh-ed25519 AAAA... priya-macbook-2025
ssh-ed25519 AAAA... raj-work-laptop
ssh-ed25519 AAAA... ci-deploy-github-actions
```
Removing Raj's access means deleting one line. That is it.
In CtrlOps' [SSH Management tab](https://ctrlops.io/docs/modules/ssh-management), each key appears as a named row with a Revoke button. Managing per-user access across multiple servers takes under 2 minutes - no terminal required.
**Bottom line:**
Per-user keys are your offboarding process. "Revoke one key" is 30 seconds of work. "Regenerate and redistribute a shared key because one person left" is 3 hours that interrupts your entire team.
***
### Practice 9: Revoke Access Immediately When Someone Leaves [#practice-9-revoke-access-immediately-when-someone-leaves]
SSH key revocation is the step that consistently does not happen on time. When someone leaves your team or a project ends, their SSH key is active on every server you gave them access to - until you manually remove it.
Former employees retaining access after leaving an organization remain a significant security risk and are a common, though often underreported, source of breaches in small teams. It does not require malicious intent. The risk exists even when someone leaves on good terms: their laptop can be stolen, their credentials can be phished, or their machine can be compromised through an unrelated vulnerability. According to [DTEX Systems' 2023 Insider Risk Investigations Report](https://www.dtexsystems.com/blog/2023-insider-risk-investigations-report-the-rise-of-employee-attrition-and-data-exfiltration/), 12% of employees take sensitive IP with them when they leave an organization - including customer data, employee data, health records, and sales contracts.
**The manual CLI revocation process:**
```bash
# SSH into each affected server
ssh username@server-ip
# Open authorized_keys
nano ~/.ssh/authorized_keys
# Find and delete the line with their key comment
# Save and close
# Repeat for every server they had access to
```
If someone had access to 8 servers, this is 8 separate SSH sessions, 8 manual file edits, 8 opportunities for mistakes. Realistically it takes 20 to 30 minutes and often gets deprioritized to "I'll do it tomorrow."
**With CtrlOps SSH Management:**
1. Connect to the server and click the [SSH Management tab](https://ctrlops.io/docs/modules/ssh-management)
2. Find the departing developer's key, visible by name and comment
3. Click Revoke
4. Confirm: "Revoke Now"
Done. The key is removed from `authorized_keys` immediately. Repeat per server - each one takes under 30 seconds.
**Reality check:**
"We have former devs whose SSH keys are still on production." This is not hypothetical. It is what most startup CTOs admit when asked directly. If your offboarding checklist does not include "revoke SSH access same day," you have active unauthorized access sitting on production right now.
***
### Practice 10: Set Correct File Permissions Every Time [#practice-10-set-correct-file-permissions-every-time]
OpenSSH is strict about file permissions. If permissions on your key files or `.ssh` directory are too open, SSH silently rejects the connection - and the error message points to "authentication failed," not "wrong permissions." This mismatch sends developers down the wrong debugging path for hours.
**Required permissions:**
```bash
# Your .ssh directory
chmod 700 ~/.ssh
# Your private key
chmod 600 ~/.ssh/id_ed25519
# Your public key
chmod 644 ~/.ssh/id_ed25519.pub
# The authorized_keys file on the server
chmod 600 ~/.ssh/authorized_keys
# The .ssh directory on the server
chmod 700 ~/.ssh
```
**Quick permissions audit:**
```bash
ls -la ~/.ssh
```
Anything showing `rw-rw-rw-` (666) or `rwxrwxrwx` (777) will cause silent auth failures. Correct immediately.
OpenSSH refuses to use a key that is not properly protected because a world-readable private key file means any user on that machine could copy it. This is a security feature, not a quirk.
**On Windows:** If you see "SSH Agent Not Running" errors, run these commands in PowerShell as Administrator:
```powershell
Set-Service -Name ssh-agent -StartupType Automatic
Start-Service ssh-agent
ssh-add $env:USERPROFILE\.ssh\id_ed25519
```
**Bottom line:**
Wrong permissions on
`~/.ssh/authorized_keys`
is the top cause of "key authentication not working even though I definitely added the key." Always run
`chmod 600 authorized_keys`
and
`chmod 700 ~/.ssh`
after any manual key addition on a server.
Key files are not the only permissions worth getting right on a server. The [file system security audit checklist](/security-checklist/vps/filesystem) covers the same discipline applied host-wide: world-writable files outside `/tmp`, set-id binaries in user-writable paths, and the modes on `/etc/shadow`, each with the exact value that passes.
***
### Practice 11: Audit Your SSH Keys Regularly [#practice-11-audit-your-ssh-keys-regularly]
You should know exactly which keys exist on each server and why. Most developers do not - they add keys when onboarding and never look again. Keys accumulate. Old ones from past contractors, decommissioned CI systems, and replaced laptops stay indefinitely.
**Manual SSH key audit on your local machine:**
```bash
# List all key files
ls -la ~/.ssh/*.pub
# Check what is loaded in the SSH agent
ssh-add -l
# Check key fingerprints
ssh-keygen -lf ~/.ssh/id_ed25519.pub
```
**Manual SSH key audit on a server:**
```bash
# SSH in and view all authorized keys
cat ~/.ssh/authorized_keys
# Count entries
wc -l ~/.ssh/authorized_keys
```
For each entry, ask: Do I know whose key this is? Are they still on the team or project? Does this key still need this level of access?
**In CtrlOps SSH Management tab:** Connect to any server and the tab shows [a full visual registry](/features/ssh-management) - key type (Ed25519 in green, RSA in blue), the key identity or comment, and the blurred key string you can reveal by clicking. Total key count, Ed25519 count, and RSA count show as counters at the top of the view. No terminal access required to audit.
Pair SSH key audits with CtrlOps' real-time [infrastructure monitoring dashboard](https://ctrlops.io/docs/modules/infra-details) - CPU, RAM, and disk usage visible per server without running a single command. A server sitting at 91% disk with 5 unknown authorized keys is two separate problems. CtrlOps surfaces both in the same view.
**Bottom line:**
Run a full SSH key audit every 90 days minimum, or after any team change. A manual audit takes 15 minutes per server. A visual audit in CtrlOps takes 2 minutes across your entire fleet.
***
### Practice 12: Use AI to Diagnose SSH Key Errors [#practice-12-use-ai-to-diagnose-ssh-key-errors]
SSH key errors are notoriously cryptic. `Permission denied (publickey)` tells you nothing about whether the problem is the key itself, the permissions, the `authorized_keys` file, the SSH daemon config, or something else entirely. The typical debug loop: search Stack Overflow, find answers from 2015, try three commands, still broken.
**With CtrlOps AI Terminal:**
Open the [AI Terminal](https://ctrlops.io/docs/modules/ai-terminal) tab on your connected server and type exactly what is happening:
> "I'm getting Permission denied (publickey) when connecting. I've added my Ed25519 public key to authorized\_keys but it's still failing."
The AI reads your server's current state and generates targeted diagnostic commands. Those commands identify the actual issue: wrong permissions on `authorized_keys`, `PubkeyAuthentication no` in `/etc/ssh/sshd_config`, or a key that was appended with a trailing space that invalidated it.
Every suggested command appears for your review before anything runs. You approve it. The AI is approval-gated - it never executes commands automatically. For power users who want to skip the approval step, Auto-Run can be enabled in the AI Terminal settings.
For SSH key issues involving recent OpenSSH changes or distribution-specific quirks, enable [Web Search in the AI Terminal](https://ctrlops.io/docs/modules/ai-terminal/web-search). The AI checks current documentation from Tavily, Brave, or DuckDuckGo before generating commands - meaning answers based on what is actually true today, not training data from a year ago.
CtrlOps uses a Bring Your Own AI Key (BYOK) model. Connect OpenAI, Anthropic Claude, Google Gemini, or any OpenAI-compatible provider. Your AI queries never pass through CtrlOps servers - they go directly from your machine to your chosen AI provider.
See the approval-gated workflow in action:
**Bottom line:**
Type "why is my SSH key not working?" in the AI Terminal and get diagnostic commands targeted to your actual server state. The approval gate means you always see exactly what will run before it runs. No blind execution.
***
### Practice 13: Consider FIDO2 Hardware Keys for Production Access [#practice-13-consider-fido2-hardware-keys-for-production-access]
Standard SSH keys live on disk. A FIDO2 hardware key changes the security model entirely - the private key never leaves the physical device.
When you use an `ed25519-sk` key (the `-sk` stands for security key), the private key is generated and stored inside a FIDO2 hardware authenticator like a YubiKey. Your machine only holds a "key handle stub" - a reference file that is useless without the physical device. When you connect to a server, the server sends a challenge, and your YubiKey signs it. You touch the key to confirm presence. No software on your machine ever sees the actual private key.
**Setup (requires OpenSSH 8.2+ and a FIDO2-compatible hardware key):**
```bash
# Generate a hardware-backed SSH key
ssh-keygen -t ed25519-sk -O resident -C "yubikey-prod-2026"
# You'll be prompted to touch your YubiKey during generation
# The .pub file goes to the server as normal - the private key stays on the hardware
# Copy the public key to your server
ssh-copy-id -i ~/.ssh/id_ed25519_sk.pub username@server-ip
```
The `-O resident` flag stores the key handle on the YubiKey itself - so you can use the same key on multiple machines by loading it from the hardware: `ssh-add -K`.
**When to use FIDO2 keys:**
* Any production server where a stolen laptop would otherwise mean immediate access
* Shared workstations or CI runners where multiple people have physical access
* Any environment where "physical presence required" is a meaningful security constraint
This is not a requirement for every developer workflow. Standard Ed25519 keys with passphrases cover most freelance and small-team use cases. But for teams managing critical production infrastructure in 2026, hardware-backed `ed25519-sk` keys are becoming the standard - [as documented by Yubico's OpenSSH integration guide](https://developers.yubico.com/SSH/Securing_SSH_with_FIDO2.html).
**Bottom line:**
A FIDO2 hardware key means a stolen laptop is not a server breach - because the private key was never on the laptop. The
`ed25519-sk`
key type is supported natively in OpenSSH 8.2+ and requires only a physical touch (not a PIN, unless you add
`-O verify-required`
) to authenticate.
***
### Practice 14: Know When SSH Certificates Replace Key Management [#practice-14-know-when-ssh-certificates-replace-key-management]
For teams beyond roughly 15 to 20 people, individual `authorized_keys` management at scale becomes its own problem. SSH certificates offer a different model.
Instead of adding each developer's public key to every server's `authorized_keys`, you configure servers to trust any certificate signed by a central Certificate Authority (CA). A developer requests a short-lived certificate - typically valid for 15 minutes to 8 hours - uses it to connect, and it expires automatically. No standing access. No `authorized_keys` files to maintain per server. No revocation step when someone leaves - their certificate simply expires.
This is worth knowing about, not necessarily worth implementing today. For a solo developer or a team of 5, per-user Ed25519 keys with manual revocation (as covered in Practices 8 and 9) is simpler and sufficient. For a 30-person engineering org managing 80 servers, SSH certificates are the right answer.
The practical signal: if you find yourself regularly forgetting to revoke keys when projects end, or if auditing `authorized_keys` across your fleet feels unmanageable, look at SSH certificate authorities. HashiCorp Vault and AWS Systems Manager Session Manager both offer managed CA implementations that integrate with existing infrastructure. Session Manager also removes SSH keys from the picture entirely by moving access into the browser, a trade-off covered in our [web-based vs. local SSH clients](/blog/web-based-vs-local-ssh-client) comparison.
**Bottom line:**
SSH certificates are the scalable answer to
`authorized_keys`
sprawl at larger team sizes. If you are managing fewer than 20 people across a handful of servers, per-user key pairs with a solid revocation process covers you. If you are beyond that, certificate-based SSH is worth evaluating.
## Why CtrlOps Is the Right Tool for SSH Key Management [#why-ctrlops-is-the-right-tool-for-ssh-key-management]
Every practice in this guide can be done manually through the CLI. The question is whether you will do it consistently - under pressure, at 11PM, when someone just left the team and you are SSHing into 8 servers one by one.
CtrlOps turns the SSH key management practices that developers skip into actions that take less time than skipping them.
**[SSH Setup Wizard](https://ctrlops.io/docs/getting-started/first-connection)** guides you through generating an Ed25519 key pair, verifying SSH is installed on your machine, and getting your public key onto the server using the correct method for your setup. Three steps. No documentation lookup.
**[SSH Management tab](https://ctrlops.io/docs/modules/ssh-management)** shows every authorized key on a connected server in a visual registry. Key type (Ed25519 or RSA) is labeled and color-coded. The key comment shows as the entry name so you can identify ownership at a glance. Add keys by pasting a public key directly. Revoke any key with one click and confirm. The key is removed from `authorized_keys` immediately.
**[AI Terminal](https://ctrlops.io/docs/modules/ai-terminal)** with approval gate diagnoses SSH errors against your actual server state, not generic Stack Overflow answers. Every command is shown for review before execution. For critical servers, this means no accidental wrong `sshd_config` edit. Enable [Web Search](https://ctrlops.io/docs/modules/ai-terminal/web-search) for real-time documentation lookups. Use the [Script Directory](https://ctrlops.io/docs/modules/ai-terminal/scripts) to save reusable server setup commands with variables - write your SSH hardening script once, run it across every server with one click.
**[Automated backups](https://ctrlops.io/docs/modules/backup)** mean that even if a key misconfiguration locks you out of a server temporarily, your data is protected. Set backup schedules once and stop worrying about the day a disk fails or a bad config update corrupts your environment.
**[File Manager](https://ctrlops.io/docs/modules/file-manager)** lets you browse, upload, edit, and download server files from inside CtrlOps - no separate SCP client or FTP tool needed. When fixing SSH permission issues, you can edit `authorized_keys` or `sshd_config` visually without opening a separate app.
**[Local-first security model](https://ctrlops.io/docs/core/ssh-security):** All credentials - SSH keys, server IPs, passwords - stay on your machine only. Nothing syncs to any cloud service. CtrlOps connects to your servers directly over SSH with no cloud bridge in between.
**Multi-server fleet:** Unlimited server connections. Add each server once with a name you recognize - "prod-backend," "staging-api," "client-acme-db" - and connect with one click. No spreadsheet, no copy-pasted IPs. If you want to see how teams handle this at scale, read the guide on [managing multiple servers without losing control](/blog/manage-multiple-servers-without-losing-control).
| What you need | CtrlOps feature | Time with CtrlOps | Time manually |
| ------------------------------- | ------------------------------------ | --------------------- | ------------------------------ |
| Generate Ed25519 key | SSH Setup Wizard | Under 2 minutes | 5 min + docs lookup |
| Copy key to server | Wizard, one-click copy | Under 2 minutes | 10 min including errors |
| Revoke a departing dev's key | SSH Management tab, Revoke button | 30 seconds per server | 5 min per server |
| Audit all keys on a server | SSH Management tab, visual registry | 2 minutes | 10 min per server |
| Diagnose SSH auth errors | AI Terminal, approval-gated commands | Under 5 minutes | 30 to 60 min on Stack Overflow |
| Fix permissions or config files | File Manager, visual editor | Under 2 minutes | 10 min via terminal |
CtrlOps runs on macOS (Apple Silicon and Intel), Windows, and Linux. It connects to any Linux server with SSH enabled - AWS, DigitalOcean, Hetzner, Vultr, bare metal, any VPS. No agents required on your servers.
**Pricing:** $7/month per user for the monthly plan. $70/year per user for the annual plan (saves 16.7%). Both include unlimited server connections and all features. 1 month free trial, no credit card required. [See full pricing details](https://ctrlops.io/pricing).
***
## The Freelancer Multi-Client SSH Key Scenario [#the-freelancer-multi-client-ssh-key-scenario]
You are a freelance developer managing 10 client servers across different hosting providers. Here is exactly how to structure SSH keys without it becoming a liability.
**The problem without a system:**
One key for everything means a stolen laptop exposes all 10 clients at once. Keys stored in a Google Drive folder labeled "server stuff" means credentials are cloud-synced by default. No comments on keys means you cannot identify which entry to revoke when a project ends. No audit means you do not know if keys from 18 months ago are still active.
**The correct structure:**
```
~/.ssh/
├── client_acme_ed25519 # Client A
├── client_acme_ed25519.pub
├── client_beta_rsa4096 # Client B, legacy server requires RSA
├── client_beta_rsa4096.pub
├── client_gamma_ed25519 # Client C
├── client_gamma_ed25519.pub
└── config
```
**`~/.ssh/config` for multi-client management:**
```
Host acme-prod
HostName 203.0.113.10
User ubuntu
IdentityFile ~/.ssh/client_acme_ed25519
AddKeysToAgent yes
Host beta-staging
HostName 198.51.100.45
User root
IdentityFile ~/.ssh/client_beta_rsa4096
Host gamma-backend
HostName 10.0.0.5
User ec2-user
IdentityFile ~/.ssh/client_gamma_ed25519
```
Now `ssh acme-prod` connects with the right key automatically. No flags, no remembering which key goes where.
**When a project ends:** Run `ssh-add -d ~/.ssh/client_acme_ed25519` to remove it from the agent, revoke your public key from the client's `authorized_keys`, and archive or delete the local key pair.
**Client NDA compliance:** Many clients in finance, healthcare, and enterprise SaaS have contracts that prohibit storing server credentials on cloud services. If you use an SSH tool that syncs to cloud by default, that may be a compliance violation regardless of intent. CtrlOps is local-only - credentials stay on your machine, nothing syncs to any third-party service. That is a straightforward answer to a compliance question.
For a deeper look at managing multiple servers across client environments, read the guide on [managing multiple servers without losing control](/blog/manage-multiple-servers-without-losing-control).
If you are specifically looking for a GUI SSH client for Mac that handles per-client key management well, the comparison of [best SSH clients for Mac in 2026](/blog/best-ssh-client-mac-2026) covers your options in detail.
You might also find value in exploring how AI is changing server operations more broadly - the [AI in DevOps guide](/blog/ai-in-devops) covers what these workflows look like for small teams in practice.
***
## SSH Key Audit Checklist [#ssh-key-audit-checklist]
Run this every 90 days, or after any team or project change.
**On your local machine:**
* List all key pairs: `ls -la ~/.ssh/*.pub`
* Check agent contents: `ssh-add -l`
* Verify every key has a meaningful comment
* Confirm `chmod 700 ~/.ssh` and `chmod 600` on all private keys
* Confirm no private keys are in any cloud-synced folder
* Confirm passphrase on all non-automation keys
* Delete or archive keys for projects that ended more than 90 days ago
**On each server:**
* View all authorized keys: `cat ~/.ssh/authorized_keys`
* Count entries: `wc -l ~/.ssh/authorized_keys`
* Confirm you can identify every entry's owner
* Remove any key without a clear owner
* Verify `chmod 600 ~/.ssh/authorized_keys`
* Verify `chmod 700 ~/.ssh`
* Check `PubkeyAuthentication yes` in `/etc/ssh/sshd_config`
**After team or project events - do these immediately, not later:**
* Developer leaves: revoke their key from all servers the same day
* Laptop stolen or lost: revoke all keys associated with that device immediately
* Project ends: remove your key from the client's servers before the final invoice
* Contractor engagement ends: revoke access before or alongside the final payment
***
## Conclusion [#conclusion]
SSH key management is not a one-time setup. It is an ongoing practice - generating the right key type, protecting private keys locally, using passphrases, keeping access per-user, and revoking the moment someone leaves.
The 14 practices in this guide cover the full SSH key lifecycle. Most take under 10 minutes to implement the first time. The audit checklist takes 30 minutes every quarter. The payoff is infrastructure where a stolen laptop, a departed developer, or an ended project does not automatically mean a security incident.
Start with the three highest-impact changes: switch to Ed25519 keys, add passphrases to all developer keys, and put per-user key management in place with a real revocation process. If you want to make that revocation process a 30-second click instead of a 30-minute CLI task, CtrlOps' [SSH Management module](https://ctrlops.io/docs/modules/ssh-management) handles it across every server in your fleet - at $7/month per user with a 1 month free trial.
***
## FAQ [#faq]
Ed25519 is the recommended SSH key type in 2026. It uses the Curve25519 elliptic curve algorithm, which is faster, more secure, and produces shorter keys than RSA 2048. It is specifically designed to resist side-channel attacks. Use RSA 4096 only when a legacy system explicitly does not support Ed25519, which is rare since OpenSSH added support in version 6.5, released in 2014.
Create a separate Ed25519 key pair for each client engagement and name it clearly - for example, `client_acme_ed25519`. Map each key to the correct server in `~/.ssh/config` using the `IdentityFile` directive. This means a compromised key only affects that one client's servers, not your entire portfolio. When a project ends, remove your public key from the client's server and delete or archive the local key pair.
Run `ssh-keygen -p -f ~/.ssh/your_key_name` and press Enter when prompted for the new passphrase to leave it blank, which removes it. Only do this for dedicated automation or CI/CD keys - never for your main developer key. For daily use, add your key to the SSH agent with `ssh-add ~/.ssh/id_ed25519` instead. You type the passphrase once per session and the agent handles every subsequent connection silently.
**From a server**, SSH in and open `~/.ssh/authorized_keys` with a text editor. Find the line containing the key you want to remove - the comment at the end identifies whose it is - and delete that line. Save the file. The key is revoked immediately with no SSH daemon restart needed. In CtrlOps, the SSH Management tab lists every authorized key by name. Click Revoke next to the entry and confirm. Done in under 30 seconds.
**From your local machine**, delete the key files with `rm ~/.ssh/your_key_name` and `rm ~/.ssh/your_key_name.pub`, then remove it from the SSH agent with `ssh-add -d ~/.ssh/your_key_name`. For sensitive keys, use `shred -u ~/.ssh/your_key_name` to overwrite the file before deletion so it cannot be recovered from disk.
Your private key must be `chmod 600`. Your `~/.ssh/` directory must be `chmod 700`. The `authorized_keys` file on the server must also be `chmod 600`. If these permissions are wrong, OpenSSH silently rejects key authentication. The error says "Permission denied (publickey)" but the root cause is a permissions problem, not a key mismatch. This is the most common reason key-based auth fails after a correct setup.
Rotate SSH keys when a developer leaves the team, a laptop is stolen or lost, a contractor engagement ends, or you suspect a key has been exposed. For CI/CD deploy keys, rotate every 90 days as a baseline. For developer keys, annual rotation is a reasonable minimum for most small teams. Always revoke the old key before or immediately after adding the new one so there is no gap in access.
Yes - a password manager with SSH key support like 1Password is a secure backup option. The key is stored encrypted and protected by your master password. What you must never do is store private keys in plain cloud storage such as Dropbox, Google Drive, or iCloud, in a Git repository, or in any unencrypted file. The private key file must always be encrypted at rest.
Password authentication should only be used when you genuinely cannot set up key-based auth - for example, during first-time access to a server before your public key is installed. Once key authentication works, set `PasswordAuthentication no` in `/etc/ssh/sshd_config` to eliminate brute-force attack surface entirely. SSH keys are the correct choice for all regular server access.
Yes. CtrlOps includes a built-in SSH Setup Wizard that guides you through generating an Ed25519 key and copying it to your server in three steps. The SSH Management tab inside each connected server shows all authorized keys with their type, comment, and a one-click Revoke button. You can add new public keys directly from the app. All credentials stay local - nothing syncs to any cloud. The monthly plan is $7/month per user with a 1 month free trial.
If your private keys have no passphrase, every server that trusts those keys is immediately at risk. Connect from another machine and remove the stolen laptop's public key from `authorized_keys` on every affected server as fast as possible. If you use per-machine keys as recommended in this guide, only those specific servers are at risk. If you used one key for everything, you need to revoke access across your entire fleet. This is exactly why per-machine key pairs and passphrases matter - they limit the blast radius to one device's worth of access.
Termius syncs connection details and credentials to its cloud servers by default. CtrlOps is local-first - all credentials stay on your machine and nothing syncs to any external service. For developers working with clients who have NDAs prohibiting cloud storage of server credentials, or for teams in compliance-sensitive environments, the local-only model is a meaningful difference. CtrlOps also includes an AI Terminal with approval-gated command execution, a visual SSH key registry with per-key revocation, automated backup scheduling, real-time infrastructure monitoring, a GUI file manager, and a reusable script library - at $7/month per user with unlimited server connections, after a 1 month free trial.
`ssh-copy-id -i ~/.ssh/id_ed25519.pub username@server-ip` copies your public key to a server's `authorized_keys` file automatically. It handles directory creation, key appending, and permission setting in one command. Use it when you already have password or other auth access and want to add key-based access. It is the fastest and least error-prone method. If it is not available on your system, use the manual method: SSH in, create `~/.ssh/` with `chmod 700`, append the key to `authorized_keys`, and set `chmod 600` on that file.
---
# 7 Best Termius Alternatives for Mac in 2026 (Tested on macOS) (/blog/termius-alternatives-mac)
Author: Hiren Kalariya | Role: Co-Founder & CEO, TST Technology | Published: 2026-07-03 | Tags: Termius Alternatives for Mac, Termius for Mac, Mac SSH Client, Server Management App Mac | Reading Time: 18 min read
> Termius is SSH-only with cloud credentials on paid plans. We tested 7 Termius alternatives for Mac - CtrlOps, iTerm2, Warp, Tabby, Royal TSX, WindTerm, Core Shell.
If you are looking for the best Termius alternatives for Mac in 2026, the leading options on macOS are CtrlOps, iTerm2, Warp, Tabby, Royal TSX, WindTerm, and Core Shell. For Mac teams managing several server instances, CtrlOps is highly recommended. It unites your shell, performance metrics, and deployment pipelines into a single local-first macOS application priced at $7 per user monthly after a 1 month free trial, keeping all keys on your Mac and ensuring no AI commands run without your approval.
**This guide is macOS-only.** Looking across Windows and Linux too? See our full [Termius alternatives](/blog/termius-alternatives) guide.
## Key Takeaways [#key-takeaways]
Although Termius is a popular SSH tool with a modern AI assistant, it focuses purely on connection tunnels. It leaves out critical needs like automated deployments, resource graphs, BYOK custom AI options, and MCP integrations, while also uploading server credentials to remote servers on commercial tiers.
The alternatives discussed here address these gaps for modern workflows, often at a lower price point.
Here is the quick comparison:
| Tool | Best For | Price | AI | File Manager | Local Credentials |
| ----------- | -------------------------------- | -------------------------- | -------------------- | -------------- | ----------------- |
| **CtrlOps** | **All-in-one server management** | **$7/user/mo (1 mo free)** | **✓ Approval-gated** | **✓ Full GUI** | **✓ Local-only** |
| iTerm2 | Free Mac power terminal | Free | ✗ | ✗ | ✓ Local |
| Warp | AI-first coding terminal | $20/mo | ✓ Auto-run | ✗ | ✗ Cloud |
| Tabby | Open-source modern terminal | Free | ✗ | ✓ SFTP | ✓ Local |
| Royal TSX | Multi-protocol (RDP/SSH/VNC) | €49 one-time | ✗ | Limited | ✓ Local |
| WindTerm | Fast free SSH + SFTP | Free | ✗ | ✓ SFTP/SCP | ✓ Local |
| Core Shell | Mac-native SSH manager | Free / $9.99/mo | ✗ | ✗ | ✓ Local |
**The cost gap at team scale:** For a 5-person team, Termius Team runs **$1,200/year** ($20/user/month), while CtrlOps costs **$350/year** on the annual plan ($70/user/year) - and includes monitoring, one-click deployments, automated backups, and AI diagnostics that Termius doesn't offer at any tier. You pay less and get more.
Prefer to watch instead? The full 7-tool comparison - SSH, file management, AI assistance, monitoring, and the deploy race - in under 6 minutes:
## How We Evaluated 7 Termius Alternatives for Mac [#how-we-evaluated-7-termius-alternatives-for-mac]
You open Termius. Connect to your staging server. The deployment needs a config file updated. So you use the built-in SFTP browser. It works, barely.
Then you need to check CPU usage. Termius doesn't show that. You open a browser tab to your cloud provider's dashboard.
Next, a build script crashes. You turn to Termius's AI assistant. While it knows your host list and current sessions, it lacks the context of your specific files or documentation. The output is generic, forcing you to adjust commands by hand before the error resolves.
Whether you are a freelance developer overseeing multiple client servers, a startup CTO pushing Node.js deployments every week, or an agency engineer constantly bouncing between development and staging environments, this is a daily reality.
We compared 7 **Termius alternatives for Mac** against the same real-world server management tasks:
* Connecting to multiple servers on macOS
* Deploying a Node.js application to a VPS
* Debugging a production incident under pressure
* Transferring config files without leaving the terminal
* Managing SSH keys across environments

This guide covers how each tool handles those scenarios. Not feature-list marketing. Actual workflow comparisons.
***
## Why Are Mac Developers Switching Away From Termius in 2026? [#why-are-mac-developers-switching-away-from-termius-in-2026]
Termius is still the most polished dedicated SSH client available. Cross-device sync works well. The mobile apps are genuine. That part isn't the problem.
Five specific pain points push Mac developers to look for **Termius alternatives on macOS**:

**1. Credentials sync to the cloud on paid plans:**
On the free Starter plan, Termius stores credentials locally. Upgrade to Pro or above, and your SSH keys move to Termius's cloud servers. E2E encrypted, yes, but your credentials leave your Mac.
Some client contracts and security rules, especially in finance and healthcare, strictly forbid keys and passwords leaving local storage. Check your NDAs before upgrading.
**2. AI features lack codebase awareness and custom keys:**
Termius includes a confirmation-based AI helper that analyzes your connection parameters, active sessions, and group tags - which is a major convenience.
However, this AI operates over their cloud network. It cannot access your project's configuration files, repository code, or offline documents. It has no way of reading your `package.json`, server configurations, or project documentation to understand your build structure. Additionally, it does not let you supply your own API keys (BYOK) from providers like OpenAI, Anthropic, or Google.
**3. No visual system metrics:**
To monitor CPU, memory, or disk health, you have to SSH in and manually run tools like `htop` or `df -h` on each instance. Modern alternatives display this performance data automatically via visual dashboards.
**4. Manual builds and deployments:**
Pushing updates to a remote app requires logging in and running commands for Git syncs, package installations, process manager restarts, and web server configurations. Doing this by hand on every release is slow and prone to errors.
**5. Expensive subscription costs at scale:**
With seats starting at $10 monthly for the individual tier and scaling to $20 for teams, managing a small squad of 5 can cost $100 monthly ($1,200 annually). While this covers a refined shell client and cross-device sync, it doesn't give you performance dashboards, deployment helpers, deep AI troubleshooting, or advanced file handling.
**Bottom line:** Termius is very good at what it was built for: cross-device SSH. But Mac developers managing production servers increasingly need AI diagnostics, deployment automation, and infrastructure monitoring alongside their terminal. Termius doesn't offer any of these, and per-user pricing makes the gap harder to justify at team scale.
Points 2 and 5 are exactly what pushed Uttam Ughareja to switch. He ran 6 servers on Termius until its AI executed a command without a safety check, then [moved everything across in under 2 minutes](/case-studies/ughareja-infotech) so he could run the AI terminal on his own key, locally.
***
## What Is Better Than Termius for Mac? [#what-is-better-than-termius-for-mac]
The best Termius alternative for Mac depends on what you need beyond SSH. For all-in-one server management with AI, monitoring, and deployment, CtrlOps is the most complete option at $7/user/month, with a 1 month free trial. For a free Mac-native terminal, iTerm2.
For AI-first local coding, Warp. For open-source with no vendor lock-in, Tabby. For connecting to different kinds of systems (RDP + SSH + VNC), Royal TSX.
For a fast free SSH client with SFTP, WindTerm. For a lightweight Mac-native SSH manager, Core Shell.
Here is the full side-by-side:
| Feature | CtrlOps | iTerm2 | Warp | Tabby | Royal TSX | WindTerm | Core Shell |
| ------------------------------ | ------------------- | ------ | ---------- | -------- | --------------- | -------------- | ------------ |
| Named server directory | ✓ | ✗ | ✗ | ✓ | ✓ | ✓ | ✓ |
| One-click connect | ✓ | ✗ | ✗ | ✓ | ✓ | ✓ | ✓ |
| Built-in file manager | ✓ Full GUI | ✗ | ✗ | ✓ SFTP | Limited | ✓ SFTP/SCP | ✗ |
| Infrastructure monitoring | ✓ Dashboard | ✗ | ✗ | ✗ | ✗ | ✗ | ✗ |
| AI command generation | ✓ Approval-gated | ✗ | ✓ Auto-run | ✗ | ✗ | ✗ | ✗ |
| MCP server integration | ✓ | ✗ | ✗ | ✗ | ✗ | ✗ | ✗ |
| One-click deployment | ✓ | ✗ | ✗ | ✗ | ✗ | ✗ | ✗ |
| Automated backups | ✓ S3/R2/B2 | ✗ | ✗ | ✗ | ✗ | ✗ | ✗ |
| Local key and password storage | ✓ AES-256 | ✓ | ✗ Cloud | ✓ | ✓ | ✓ | ✓ |
| Cross-device sync | ✗ | ✗ | Cloud | ✗ | ✗ | ✗ | iCloud |
| Mobile app | ✗ | ✗ | ✗ | ✗ | ✓ iOS | ✗ | ✗ |
| Multi-protocol (RDP/VNC) | ✗ SSH only | ✗ | ✗ | ✗ | ✓ | Telnet/Serial | ✗ |
| Mac-native UI | ✓ | ✓ | ✓ | Electron | ✓ | Cross-platform | ✓ |
| Price (individual/mo) | $7/user (1 mo free) | Free | $20 | Free | \~€49 one-time | Free | Free / $9.99 |
| 5-user team (monthly) | $35 | $0 | $250 | $0 | \~€245 one-time | $0 | N/A |
***
## 7 Best Termius Alternatives for Mac in 2026 [#7-best-termius-alternatives-for-mac-in-2026]
The 7 best Termius alternatives for Mac are CtrlOps (all-in-one server management with AI), iTerm2 (free Mac power terminal), Warp (AI coding terminal), Tabby (open-source cross-platform), Royal TSX (multi-protocol RDP/SSH/VNC), WindTerm (fast free SSH + SFTP), and Core Shell (Mac-native SSH manager).
We compared each against identical scenarios: connecting to multiple servers, deploying code, debugging under pressure, and transferring files on macOS.
Here's how all seven compare.
### 1. CtrlOps: Best All-in-One Server Management for Mac [#1-ctrlops-best-all-in-one-server-management-for-mac]
[CtrlOps](https://ctrlops.io/) is not a Termius replacement. It replaces your entire server management stack: terminal, file manager, monitoring dashboard, backup scheduler, and deployment system, combined in one desktop app.

While Termius focuses on establishing SSH connections and syncing them across devices, CtrlOps handles the connection and manages the entire post-connection workflow. More importantly, all of your sensitive credentials remain stored locally on your Mac.
No AI-generated action runs without your approval. If you want a detailed side-by-side feature analysis, check out the complete [CtrlOps vs Termius](https://ctrlops.io/compare/ctrlops-vs-termius) comparison.
**Pros of CtrlOps:**
* **[Named server cards](/features/multi-server-management).** Connect instantly to "Prod-Backend" or "Client-Staging" in a single click. No memorizing IP addresses. No navigating Termius's host groups to find the right entry.
* **Full GUI file manager.** Upload, download, edit, and delete remote files with drag-and-drop. No SCP commands. No opening Termius's SFTP panel in a separate tab. Edit a config file without leaving the app.
> "The file manager sounds boring, I know. But I was doing everything through a separate SFTP client before this - separate login, separate window, separate headache every time. Now I just open it inside CtrlOps and edit configs directly. For someone managing multiple client servers, this is honestly the feature I use the most, more than the AI stuff even."
>
> * **Gabriel**, verified review on [Product Hunt](https://www.producthunt.com/products/ctrlops?comment=5380575)
* **Approval-gated AI terminal.** Type "why is my server slow?" and CtrlOps generates diagnostic commands. It shows every command before execution. You approve, then it runs. Human-in-the-loop, not auto-run. Warp auto-executes by default. Termius's AI Agent also requires confirmation, but runs through their cloud and lacks MCP integration or BYOK support. CtrlOps keeps everything local and connects to your actual docs and codebase.
> "The approve before execute thing is what sold me. Every other AI tool just runs stuff, and you find out what happened after."
>
> * **Bhautik Kapadiya**, verified review on [Product Hunt](https://www.producthunt.com/products/ctrlops?comment=5381266)
* **Support for MCP servers.** Integrate external developer guides, GitHub repositories, and local directories with the AI Terminal using the [Model Context Protocol](https://ctrlops.io/docs/modules/ai-terminal/mcps). It comes with built-in configurations for Context7 (official documentation), GitHub (your repositories), and the local Filesystem. You can also hook up custom MCP servers using a JSON configuration or connect manually via HTTP, SSE, or a local process. Instead of relying solely on static training data, the AI analyzes your actual codebase and up-to-date documentation prior to suggesting commands. This keeps things secure, meaning MCP suggestions still require manual user approval before running.
* **Streamlined application deployments.** Select your framework (such as Node.js, React, or Next.js), paste your GitHub repository URL, and set your environment variables. The platform automatically handles downloading the code, installing dependencies, configuring PM2, setting up Nginx, and generating SSL certificates with Certbot. What usually takes [30 to 45 minutes of manual configuration](https://ctrlops.io/docs/modules/deployment) is completed automatically in under 5 minutes.
* **Instant server health monitoring.** Track live server usage - like CPU loads, RAM utilization, disk capacity, and active system processes - across all your machines without running terminal commands like `htop`. This visual feedback helps you catch a disk reaching 94% capacity before it impacts production uptime.
* **Hands-off scheduled backups.** Easily configure automated backups to popular cloud destinations like AWS S3, Cloudflare R2, Backblaze B2, DigitalOcean Spaces, Wasabi, or MinIO. Once configured, the application manages the scheduler, tracks backup progress, and maintains execution logs, eliminating the need to write and debug custom cron scripts.
* **Privacy-first key storage.** Keep all server configurations, SSH keys, and passwords saved only on your macOS device. This data is protected locally using AES-256 encryption. There is no cloud sync or remote server storage, ensuring your keys and passwords remain completely under your control.
* **Global template scripts.** Create and save custom command sequences using `{{variable_name}}` placeholders for dynamic values. This allows you to execute uniform scripts across different servers without having to input them again. Any custom scripts added to the [Script Directory](https://ctrlops.io/docs/modules/ai-terminal/scripts) can be accessed from any of your connection profiles.
* **Live web search integration.** The [AI Terminal can search the live web](https://ctrlops.io/docs/modules/ai-terminal/web-search) using engines like Tavily, Brave, or DuckDuckGo. This fetches current manuals and API reference pages to formulate command recommendations, rather than relying on outdated offline training data.
* **Easy user and SSH key control.** Easily create user accounts on servers with defined roles (e.g., standard root, read/write permissions, or read-only access). The tool helps you deploy, manage, and change keys across your servers. It is also designed to give temporary, read-only access to external contractors for troubleshooting sessions and end their access immediately afterwards.
* **Centralized user access control.** Oversee user access permissions across your entire server network from a unified control panel. You can authorize a new engineer on multiple hosts at the same time, or instantly remove a former team member's access from all servers in one click. It also allows you to export access logs for security checks, removing the tedious task of reading `authorized_keys` files on individual servers.
**CtrlOps Drawbacks:**
* Lacks a mobile application, making it impossible to perform remote administration from a smartphone.
* Does not offer native integration or management tools for serverless architectures or Kubernetes deployments.
**Pricing Structure:** Costs $7 per seat monthly or $70 annually for managing unlimited target servers. A 1 month free trial is available without entering payment details.
**Platforms:** macOS (Apple Silicon + Intel), Windows, Linux.
| What you do with Termius today | With CtrlOps |
| ------------------------------------------------------------------- | ------------------------------------------------------------------------------------------- |
| Browse host groups for the right server | Click named server card (10 seconds) |
| Open SFTP panel for file transfers | Drag-and-drop in the built-in File Manager |
| SSH in, run `htop`, `df -h`, `free -m` manually | Glance at the monitoring dashboard |
| Paste errors into Termius AI Agent (no project docs or MCP context) | Ask the AI Terminal with MCP-connected docs and codebase, approve commands before execution |
| Run 12 commands to deploy a Next.js app | Fill a form, click Create (under 5 minutes) |
| Paste docs into ChatGPT for context | Connect Context7 or GitHub via MCP, AI reads real sources |
| No automated backups | Schedule backups to S3/R2/B2, forget about it |
***
### 2. iTerm2: The Premier Free Terminal for Power Users on macOS [#2-iterm2-the-premier-free-terminal-for-power-users-on-macos]
[iTerm2](https://iterm2.com/) is a popular tool that many macOS developers already use daily. It is completely free, open-source, and designed to leverage macOS features.

Technically, iTerm2 is not a dedicated, standalone SSH client; rather, it is a terminal environment that utilizes the operating system's native OpenSSH utility. However, for engineers who manage their connections using custom `.ssh/config` configurations and operate primarily from the CLI, it represents the most robust free solution on Mac.
**Advantages of iTerm2:**
* **Deeply integrated with macOS.** Built specifically for the Apple ecosystem, providing Retina resolution support, Finder integration, native OS notifications, and Spotlight searches.
* **Support for tabs and split layouts.** Run multiple terminal sessions in adjacent panes to keep everything visible, and restore previous screen arrangements with a simple keybinding.
* **Hotkey window overlay.** Configure a global shortcut key to reveal the terminal window over any active application for quick commands.
* **Command search and suggestion.** Query your shell logs to find historical inputs, and leverage built-in autocompletion.
* **Automated triggers.** Specify custom regular expression rules to intercept specific console outputs - allowing you to trigger shell scripts, pop up warnings, or highlight system bugs automatically.
* **Built-in tmux support.** Integrate directly with tmux to manage persistent shell environments without detaching manually.
* **Entirely free to use.** There are no paid features, mandatory cloud profiles, or subscription schemes.
**Limitations of iTerm2:**
* **Lacks a visual file explorer.** You will need to rely on terminal-based utilities like SCP or rsync, or use an external SFTP program to transfer items.
* **No visual connection dashboard.** You must catalog your hosts using static configuration files rather than clicking on cards.
* **No integrated AI assistance.** You are left with a blank prompt without intelligent suggestions or autocompletion shortcuts.
* **No telemetry graphing.** Keeping tabs on CPU or RAM necessitates running commands yourself whenever you check.
* **No built-in pipeline automation.** Manual tasks such as updating Git repositories, building packages, and restarting application managers remain completely unautomated.
* **Limited to macOS.** Any developers on your team running Linux or Windows will need to find another terminal.
**Pricing:** Free, open-source (GPL v2).
**Platforms:** macOS only.
For macOS developers comfortable editing their own SSH configs, iTerm2 represents the strongest free alternative to Termius. It elevates the standard shell experience, though it misses the dedicated remote-management utility features.
As you manage more servers, or when you find yourself frequently copying documents or configuring new software stacks manually, the utility's limits become apparent. To look at other options, take a look at our curated list of [best SSH clients for Mac 2026](https://ctrlops.io/blog/best-ssh-client-mac-2026).
***
### 3. Warp: The Most Advanced AI-Infused Development Terminal [#3-warp-the-most-advanced-ai-infused-development-terminal]
[Warp](https://www.warp.dev/) is a modern terminal utility coded in Rust that utilizes your graphics card for hardware-accelerated rendering. It structuralizes your workspace by separating logs into distinct blocks and comes with an AI agent capable of translating simple text prompts into terminal inputs.

Although Warp has a very modern design, it functions primarily as a local development tool rather than a comprehensive server controller. If you want to check how it fares side-by-side, read the detailed comparison at [CtrlOps vs Warp](https://ctrlops.io/compare/ctrlops-vs-warp).
**Advantages of Warp:**
* **Interactive AI Prompting.** Input normal English sentences to generate and execute shell actions, streamlining local system workflows.
* **Discrete visual blocks.** Each execution and its corresponding output exists inside an isolated segment that you can select, filter, or share easily, bypassing traditional console copy issues.
* **Rich editor controls.** Place cursors, select text blocks, and adjust lines just like you would in a typical code editor.
* **Rust execution speed.** Utilizes GPU processing rather than Electron web wrappers, rendering text much faster than legacy terminal projects.
* **Collaborative workflow sharing.** Use the built-in storage to share standard command books across your team, standardizing repetitive scripts.
* **BYOK capability.** Configure the software to route requests using your private API access keys from Anthropic, Google, or OpenAI, saving your native Warp AI quota.
**Limitations of Warp:**
* **Not built for server fleet administration.** It doesn't feature an address book, graphical file transfer modules, diagnostic metrics, or deployment workflows.
* **Automatic execution risks.** Because it defaults to executing suggestions directly, a misunderstood prompt on a live production node could trigger a service outage or database drop without warning. It does not provide the safety approval flow found in CtrlOps.
* **Compulsory cloud profiles.** You are forced to create a registered account and sign in to their servers before using the terminal.
* **Free tier is limited.** 150 AI credits for 2 months, then 75/month. Build plan costs $20/month for 1,500 credits.
* **No server context awareness.** Warp's AI doesn't know your server's CPU, RAM, or running processes. It generates commands generically.
**Pricing:** Free (75 to 150 AI credits/month). Build: $20/month (1,500 credits). Business: $50/user/month.
**Platforms:** macOS, Windows, Linux.
Warp is the best AI terminal experience on Mac for writing and running code locally. For managing remote servers, Warp's AI doesn't have your server's context. And auto-executing commands on production is a risk most teams shouldn't accept.
CtrlOps's approval-gated approach shows every command before execution, which is the difference between a convenient tool and a safe one. For a closer look at that trade-off, see our [comparison of three AI terminal approaches to server management](/blog/ai-terminal-tools-server-management).
**Reality check:** Any AI terminal that auto-runs commands without a review step is a development-machine feature, not a server-management feature. On a production server with real traffic, one misinterpreted prompt can drop a database or restart the wrong process. The approval gate in CtrlOps shows every command before execution so you catch destructive operations before they run.
***
### 4. Tabby: Best Open-Source Cross-Platform Terminal [#4-tabby-best-open-source-cross-platform-terminal]
[Tabby](https://tabby.sh/) is a cross-platform, open-source terminal that modernizes SSH with tabs, split panes, a plugin ecosystem, and a built-in connection manager.

No subscription. No account. No vendor lock-in. MIT-licensed.
**Pros of Tabby:**
* **Free and open-source.** MIT license. No feature gates, no accounts, no usage limits.
* **Cross-platform.** macOS, Windows, Linux with an identical interface. Team members on different operating systems use the same tool.
* **Built-in SSH client.** Connection profiles, SFTP, Zmodem transfers, SSH key management included out of the box.
* **Plugin ecosystem.** Extend with community-built plugins for additional functionality.
* **Split panes and workspaces.** Save complex window layouts as reusable profiles.
* **Encrypted password manager.** Local storage with master passphrase protection.
* **Modern UI.** Themes, font ligatures, GPU-accelerated rendering.
**Tabby Limitations:**
* **Resource-heavy.** Electron-based. Uses noticeably more RAM than iTerm2 or native terminals.
* **Lacks AI capabilities.** Does not provide automated command suggestions, server diagnostics, or error analysis.
* **No monitoring or deployment.** Terminal only, no server management capabilities.
* **Steeper learning curve.** While power users enjoy the depth of options, the initial setup can feel overwhelming to novices.
* **Plugin compatibility issues.** Certain combinations of third-party plugins can lead to performance hits or visual bugs.
**Pricing:** Free, open-source (MIT license).
**Platforms:** macOS, Windows, Linux.
Tabby remains the premier option for engineers seeking a contemporary, multi-platform console free of recurring bills or closed ecosystems. When compared to the free version of Termius, it provides far more features.
The trade-off is higher memory usage, no AI, and no server management features beyond basic SSH. If you're also looking at [alternatives to PuTTY, Webmin, or ServerPilot](https://ctrlops.io/blog/putty-webmin-serverpilot-alternatives), Tabby fits the SSH layer but not the management layer.
***
### 5. Royal TSX: The Top Choice for Mixed-Protocol Environments on macOS [#5-royal-tsx-the-top-choice-for-mixed-protocol-environments-on-macos]
[Royal TSX](https://www.royalapps.com/ts/mac) is a dedicated macOS version of Royal TS, built for network administrators managing different types of systems.

If you regularly use SSH to interact with Linux instances, connect to Windows systems via RDP, and manage remote desktops with VNC from a single macOS workstation, this is the only client that supports all these methods out of the box.
**Advantages of Royal TSX:**
* **Diverse protocol support.** Consolidate SSH, remote desktop (RDP), VNC, Apple Remote Desktop, Telnet, web views, and VMware connections into a single tabbed workspace.
* **Tailored for macOS.** Designed specifically for the Apple desktop interface, incorporating native menu layouts, window controls, and crisp Retina scaling.
* **Connection organization.** Folders, groups, and tags. Save credentials per connection or per folder.
* **Royal Server integration.** Centralized gateway for secure access management across teams.
* **Password management integration.** Connects to 1Password, KeePass, LastPass, and other vaults.
* **One-time pricing.** €49 individual license. No subscription. Includes 1 year of software maintenance.
**Royal TSX Limitations:**
* **No AI features.** Manual command execution only. No suggestions, no diagnostics.
* **No infrastructure monitoring.** No dashboard. You run system commands manually.
* **No one-click deployment.** No automation for app setup.
* **Complex UI.** Powerful, but the learning curve is steeper than simpler SSH clients. Beginners may find it overwhelming.
* **Limited file management.** Basic SFTP through plugins, not a full GUI file manager.
* **Maintenance costs.** Major version upgrades require a new license purchase.
**Pricing:** Free (limited connections). Individual: €49 one-time. Site: €849. Includes 1 year of updates.
**Platforms:** macOS, Windows, iOS, Android.
Royal TSX is the right Termius alternative for Mac if you work across Linux, Windows, and macOS systems and need one tool for all of them. Termius handles SSH and SFTP. Royal TSX handles SSH, RDP, VNC, and more.
For pure SSH-to-Linux server management with AI and monitoring, CtrlOps is more focused. For managing different types of systems, Royal TSX wins. Curious how the two stack up feature by feature? See [CtrlOps vs Royal TS](/compare/ctrlops-vs-royalts).
***
### 6. WindTerm: Best Free Lightweight SSH Client [#6-windterm-best-free-lightweight-ssh-client]
[WindTerm](https://github.com/kingToolbox/WindTerm) is a cross-platform SSH/SFTP/Shell/Telnet/Serial terminal built in C. It is the #1 ranked Termius alternative on AlternativeTo, and for good reason: it is fast, feature-rich, and completely free.

WindTerm uses dynamic memory compression that [reduces working memory load by 20% to 90%](https://github.com/kingToolbox/WindTerm#terminal-performance) compared to other terminals. According to benchmarks published on its GitHub repository, WindTerm consistently outperforms iTerm2, PuTTY, Alacritty, and Windows Terminal in rendering speed and SFTP transfer rates.
**Pros of WindTerm:**
* **Very fast performance.** Built in C with dynamic memory compression. In official benchmarks, WindTerm used around 107 MB of memory to process 97.6 MB of random text data, while xterm consumed over 3,300 MB and PuTTY used around 733 MB for the same test.
* **Integrated SFTP and SCP.** Upload, download, rename, and manage remote files directly inside the terminal. No separate tool.
* **Deep tmux integration.** Tmux sessions, windows, and panes display natively inside WindTerm's UI. No detach/reattach friction.
* **Session management.** Named sessions, folders, auto-login with password or key-based authentication, SSH ProxyJump support.
* **Cross-platform.** macOS, Windows, Linux with identical functionality.
* **Completely free.** Free for commercial and non-commercial use. Apache-2.0 license on released source code.
* **Port forwarding.** Local, remote, and dynamic (SOCKS) port forwarding built in. (If you ever need the raw command instead, our free [SSH tunnel generator](/tools/ssh-tunnel-generator) builds local, remote, and SOCKS forwarding commands for you.)
**WindTerm Limitations:**
* **No AI features.** Manual command execution only.
* **No infrastructure monitoring.** No dashboards, no health checks.
* **No deployment automation.** Every deployment step is manual.
* **Configuration complexity.** Some settings require manual config file editing. No GUI for every option.
* **Smaller community.** Fewer guides and tutorials compared to iTerm2 or Termius.
* **Cross-platform UI.** Doesn't feel Mac-native the way iTerm2 or Core Shell does.
**Pricing:** Free (Apache-2.0 license).
**Platforms:** macOS, Windows, Linux.
WindTerm is the best free Termius alternative on macOS if raw performance and built-in SFTP matter most. It gives you more features than Termius's free Starter plan: SFTP, port forwarding, session management, and tmux integration, all without paying anything. The trade-off is no AI, no monitoring, and a less polished Mac experience.
***
### 7. Core Shell: Best Mac-Native SSH Manager [#7-core-shell-best-mac-native-ssh-manager]
[Core Shell](https://codinn.com/shell/) is a macOS-native SSH client built on top of OpenSSH. It focuses on being the cleanest, lightweight SSH connection manager for Mac users who want a GUI without giving up terminal power.

Available through Setapp or as a standalone purchase on the Mac App Store.
**Pros of Core Shell:**
* **Mac-native design.** Built in Cocoa for macOS. Feels like a first-class Mac app, not a cross-platform port.
* **OpenSSH-based.** Uses the same OpenSSH you already trust. Full compatibility with `~/.ssh/config`.
* **Auto-reconnect.** Drops and reconnects automatically when your network changes. Useful for laptop users moving between Wi-Fi networks.
* **Color-coded hosts.** Assign colors to servers for quick visual identification. Spot your production server instantly.
* **iCloud sync.** Sync connection settings across multiple Macs via iCloud. Not a third-party cloud, but Apple's own infrastructure.
* **Lightweight.** Minimal resource usage. Opens instantly.
**Core Shell Limitations:**
* **macOS only.** No Windows, Linux, or mobile support.
* **No AI features.** Manual command execution only.
* **No file manager.** File transfers require `scp` or a separate tool.
* **No infrastructure monitoring or deployment.**
* **Limited free tier.** Free version restricts some features. Premium available through Setapp ($9.99/month for 250+ apps) or standalone.
* **SSH only.** No RDP, VNC, or other protocols.
**Pricing:** Free (limited features). Premium via Setapp ($9.99/month) or Mac App Store (one-time purchase).
**Platforms:** macOS only.
Core Shell is the right pick if you want the most Mac-native SSH experience possible. It is simpler than Termius but also more focused: no cross-device sync beyond iCloud, no mobile apps, no team features.
For developers who manage a handful of servers from a single Mac and want a clean, fast connection manager, Core Shell fits perfectly.
***
## Termius vs CtrlOps: A Direct Comparison [#termius-vs-ctrlops-a-direct-comparison]
Termius and CtrlOps solve different problems. Termius is a cross-device SSH client that syncs your connections across Mac, iPhone, and Android, with a cloud-based AI Agent for command generation. CtrlOps is a server management platform that replaces your terminal, file manager, monitoring dashboard, backup scheduler, and deployment system with one local-first app, with BYOK AI and MCP integration.
Here is the head-to-head:
| Capability | Termius | CtrlOps |
| ------------------------- | --------------------------------------------------------------------------------- | ---------------------------------------------------------------------------------------------- |
| SSH connections | ✓ | ✓ |
| Cross-device sync | ✓ (Mac, Windows, Linux, iOS, Android) | ✗ (desktop only) |
| Mobile app | ✓ (iOS, Android) | ✗ |
| File management | SFTP browser | Full GUI file manager (drag-and-drop) |
| AI assistance | AI Agent (confirmation-gated, infrastructure context, cloud-based) + Autocomplete | Approval-gated AI Terminal (BYOK, MCP integration, web search, local-first) |
| MCP integration | ✗ | ✓ (Context7, GitHub, Filesystem, custom servers) |
| Infrastructure monitoring | ✗ | ✓ (live CPU, RAM, disk, processes) |
| One-click deployment | ✗ | ✓ (Node.js, React, Next.js) |
| Automated backups | ✗ | ✓ (S3, R2, B2, Wasabi, DO Spaces) |
| Script library | Snippets (command shortcuts) | [Script Directory](/features/script-directory) (reusable scripts with variables, cross-server) |
| Credential storage | Cloud (E2E encrypted) on paid plans | Local-only (AES-256, never leaves your Mac) |
| Web search in terminal | ✗ | ✓ (Tavily, Brave, DuckDuckGo) |
| Team pricing (5 users/mo) | $100 (Team) / $50 (Pro) | $35 |
| Individual pricing | Free / $10/mo (Pro) | $7/user/mo (1 mo free trial) |
### The manual method versus the CtrlOps shortcut [#the-manual-method-versus-the-ctrlops-shortcut]
Same task: [deploy a Node.js application to a VPS](/blog/deploy-nodejs-app-linux-vps). Two approaches.
**Deploy Node.js Using Termius (13 Steps):**
1. Open Termius, find your server in the host groups, and connect via SSH. (1 to 2 minutes)
2. Update server packages: `sudo apt update && sudo apt upgrade`. (2 to 3 minutes)
3. Install Node.js and Git on the server. (2 to 3 minutes)
4. Clone your Node.js project from GitHub. (1 minute)
5. Navigate to the project directory. (10 seconds)
6. Create and configure your `.env` file with environment variables. (2 to 3 minutes)
7. Install project dependencies with `npm install`. (1 to 2 minutes)
8. Open the required firewall ports using `ufw allow`. (1 minute)
9. Test the application locally on the server to confirm it runs. (1 to 2 minutes)
10. Install PM2 and configure it as a process manager for your app. (2 to 3 minutes)
11. Install and configure Nginx as a reverse proxy. (3 to 5 minutes)
12. Point your domain's DNS to the VPS IP address. (1 to 2 minutes, plus propagation wait)
13. Install Certbot and generate an SSL certificate for HTTPS. (2 to 3 minutes)
**Total: 13 manual steps, 20 to 30 minutes of active terminal work.** Each step runs through separate SSH commands. If a dependency error appears mid-process, Termius's AI helper can suggest a fix, but it lacks access to your project files or docs, so you adjust the output by hand.
**Deploy Node.js Using CtrlOps (3 Steps):**
1. Open CtrlOps and click your named server card to connect. (10 seconds)
2. Click "Add Application" inside the [File Manager](https://ctrlops.io/docs/modules/file-manager). (5 seconds)
3. Fill out the deployment form: paste your GitHub URL, select your Node.js version, add environment variables, enter your domain, and click "Create." (3 to 4 minutes)
**Total: 3 steps, 4 to 5 minutes.** CtrlOps handles the Git clone, dependency install, PM2 setup, Nginx configuration, and SSL certificate generation automatically. Your Node.js application goes live without running a single manual command.
> "I'm a designer, I don't write code. Building websites is easy now, but deployment was always my wall - I'd wait on a friend to handle the server stuff. One day he wasn't available and I was stuck with a finished site and no way to take it live. I opened CtrlOps, asked the AI Terminal in plain English what to do, and it walked me through everything step by step. I deployed my website. By myself. For the first time."
>
> * **Urvesh Kavar**, [UI/UX Product Designer](https://dribbble.com/Urvesh_7970) ([original post on LinkedIn](https://www.linkedin.com/posts/uiuxdesigner-urvesh-kavar_design-nocode-webdeployment-share-7467076744877862912-GL8W/))
For a deeper dive into how AI changes server management workflows, see our guide on [AI in DevOps](https://ctrlops.io/blog/ai-in-devops).
***
## How to Choose the Right Termius Alternative for Your Mac Workflow [#how-to-choose-the-right-termius-alternative-for-your-mac-workflow]
The best Termius alternative for Mac depends on what you actually need to do with it on macOS. No single tool wins every scenario.
**You're a developer managing multiple client servers and need AI diagnostics:**
CtrlOps.
Named server cards keep distinct client platforms separated, and storing your credentials locally ensures compliance with NDAs. The [AI Terminal](https://ctrlops.io/docs/modules/ai-terminal) diagnoses stack issues dynamically. By linking resources like Context7 or GitHub using the Model Context Protocol, the AI is able to read relevant files and developer guides prior to suggesting command syntax.
By automating configuration and deployment, what used to take 30 to 45 minutes is cut down to under 5 minutes. Billed at $7 per seat monthly, the tool pays for itself the very first time you patch a production bug in minutes rather than spending an hour on manual SSH troubleshooting.
**You're a CLI power user who configures everything in dotfiles:**
iTerm2.
Free, Mac-native, 100% keyboard-driven. With `.ssh/config` and tmux, you have a complete SSH workflow. When you outgrow manual file transfers and need monitoring, add CtrlOps alongside it.
**You live in the terminal writing code locally:**
Warp.
Its custom prompts and modular output blocks are highly efficient for local setups. However, using these automated commands on live servers requires caution, as there is no confirmation step to intercept dangerous operations.
**You want open-source with zero vendor lock-in:**
Tabby.
Free, MIT-licensed, cross-platform, plugin ecosystem. Heavier on RAM, but more capable than Termius's free tier out of the box.
**You manage a mixed Linux + Windows environment from a Mac:**
Royal TSX.
Integrates SSH, RDP, and VNC into a single platform. This is the only software on the list that natively handles remote desktop sessions for Windows alongside standard SSH sessions for Linux.
**You want raw performance and free SFTP:**
WindTerm.
Fastest terminal on this list. Built-in SFTP and SCP. Deep tmux integration. Zero cost.
**You just want a clean Mac-native SSH manager:**
Core Shell.
Lightweight, fast, OpenSSH-based. iCloud sync across Macs. No bloat. If you manage fewer than 5 servers and just want clean connections, it handles that without friction.
| Your Situation | Best Pick | Runner-Up |
| ---------------------------------- | ---------- | ---------- |
| Freelancer, 5 to 15 client servers | CtrlOps | Termius |
| CLI power user, dotfile workflow | iTerm2 | WindTerm |
| AI-first terminal power user | Warp | CtrlOps |
| Open-source advocate | Tabby | WindTerm |
| Mixed Linux + Windows from Mac | Royal TSX | Core Shell |
| Raw performance on a budget | WindTerm | iTerm2 |
| Lightweight Mac-native SSH | Core Shell | iTerm2 |
If you're evaluating broader [DevOps automation tools](https://ctrlops.io/blog/devops-automation-tools) beyond just SSH clients, CtrlOps fits as the deployment and monitoring layer that complements your CI/CD pipeline.
***
## Conclusion [#conclusion]
The best **Termius alternatives for Mac** in 2026 are the tools that go beyond cross-device SSH sync.
Termius still connects to servers beautifully. But connecting was never the hard part. The hard part is deploying code, debugging a crashed process on a live server, managing files across servers, monitoring infrastructure, and scheduling backups, without opening 4 separate tools.
CtrlOps does all of that at $7/user/month ($70/user/year) with a 1 month free trial. The workflow speaks for itself the first time you deploy in under 5 minutes instead of 30.
> "Started using CtrlOps a few weeks ago, honestly didn't expect much. But my DevOps workflow has genuinely shifted - AI Terminal that understands plain English, server management without SSH juggling, backups, deployments, and file manager all in one place. I'm doing in 10 minutes what used to take an hour. If you manage servers, just try it."
>
> * **Chintan Poriya**, [Co-founder & CEO of BytezTech](https://byteztech.com) ([original post on LinkedIn](https://www.linkedin.com/posts/chintan-poriya_product-review-started-using-ctrlopsai-activity-7467179106200260609-Uoht))
Pick the tool that matches your biggest pain point today. Switch if it stops fitting. The best SSH client is the one you actually use without fighting it.
Migrating from a different legacy client instead? The same testing methodology is behind our [SecureCRT alternatives for Mac](/blog/securecrt-alternatives-mac) guide.
***
## Frequently Asked Questions [#frequently-asked-questions]
For developers seeking a zero-cost replacement, **iTerm2** is a top option for macOS, offering advanced terminal features like window overlays, split panes, and tmux support. If you require multi-platform compatibility (Windows, Linux, Mac) alongside modern UI tabs and integrated file transfers, **Tabby** is a great choice. If speed and low resource usage are key, **WindTerm** provides robust SFTP/SCP features for free. All of these tools are open-source and free, though they lack AI assistants, visual monitoring, or deployment tools.
If you need a tool that handles broader administration tasks, **CtrlOps** provides a comprehensive environment. It matches standard SSH utilities in organizing connections and keys, but includes features like a graphical file manager, visual server vitals, one-click deployment pipelines, automated remote backups, and a locally-controlled AI terminal that works with MCP servers. Starting at $7 per seat monthly after a 1 month free trial, it offers more utility than Termius's plans for less money, though it doesn't offer a mobile version or cloud-based device sync.
Termius encrypts your credentials end-to-end, but paid subscriptions sync this data to their remote servers. The free tier stores configuration data only on your local system. For compliance-heavy projects (like finance or medicine) or strict NDAs, saving keys in the cloud might violate security policies. If your project mandates local storage, [CtrlOps](https://ctrlops.io/) secures your configuration using local AES-256 encryption without external cloud sync.
Yes, CtrlOps is fully compatible with macOS (both Apple Silicon and Intel chips) and supports essential client features like session directories, keys, and file handling. Furthermore, it integrates live monitoring, a safety-first AI terminal with MCP/web connectivity, deployment tools, scheduled backup schedules, and template scripting. Priced at $7/month (or $70/year) with a 1 month free trial, it is cheaper than Termius Pro. Read our [CtrlOps vs Termius](https://ctrlops.io/compare/ctrlops-vs-termius) summary for more details.
Yes. Termius offers a free Starter plan that includes SSH, SFTP, AI-powered autocomplete, port forwarding, and a local vault. Credentials stay on your machine on this tier. The free plan does not include cloud sync, snippets, or team features. To sync credentials across devices or access the team vault, you need Pro ($10/user/month billed annually) or Team ($20/user/month billed annually).
An individual Termius Pro plan is $10 per user monthly ($120/user annually), and their Team tier is $20 per user monthly ($240/user annually). CtrlOps, by contrast, is priced at $7 per user monthly, or $70/user annually. For a team of five on annual billing, Termius Team costs $1,200/year while CtrlOps costs $350/year - and CtrlOps includes monitoring, automatic deployments, AI diagnostics, backups, and file browsing that Termius doesn't offer.
Keep Termius if mobile SSH access is critical to your workflow. No other tool on this list offers fully functional iOS and Android apps. Keep Termius if your team relies on cross-device credential sync across Mac, Windows, Linux, and mobile. Keep Termius if you've invested heavily in team vaults with role-based access controls and consolidated billing. For these specific use cases, Termius remains the best option in 2026.
Yes, Termius features an AI assistant that uses system metadata (connection lists, host names, groups) to construct commands, requiring your confirmation before running them via their cloud service. While both tools use a review step, CtrlOps adds capabilities like private API key usage (BYOK), direct MCP integration (for local directories, repositories, and documentation), and built-in search engines (Tavily/Brave/DuckDuckGo). This gives CtrlOps a deeper context layer and complete API key privacy.
If you want AI capabilities on macOS, **CtrlOps** and **Warp** are the main options. CtrlOps requires your approval, showing you every proposed command before execution. Warp defaults to running suggestions immediately. For production systems, having a review stage is safer. Both systems support BYOK (private keys from OpenAI, Anthropic, or Google). Termius includes an autocomplete assistant rather than generating complete multi-step command sets.
Yes. **Tabby** (MIT license) is the most feature-rich open-source Termius alternative for Mac. It offers tabs, split panes, built-in SFTP, SSH key management, and a plugin ecosystem. **WindTerm** (Apache-2.0) is the fastest open-source option with integrated SFTP/SCP and deep tmux support. **iTerm2** (GPL v2) is the most popular Mac-native open-source terminal. None of these include cloud sync or mobile apps that Termius offers.
You do not have to re-enter anything. CtrlOps has a built-in Termius importer: on the All Servers screen, click the three-dot menu and choose **Import from Termius** under MIGRATE. Your Mac asks once for permission to read the credentials Termius saved in your keychain, then CtrlOps lists every host it found with its authentication type and imports the ones you select. Hosts, ports, usernames, and SSH keys all come across in about 30 seconds, with no export file. Everything is read locally on your Mac and stored with AES-256 encryption, so nothing is uploaded. Termius snippets, port-forwarding rules, and sync groups do not transfer, since they have no equivalent in the CtrlOps server list. Full walkthrough: [migrate from Termius to CtrlOps](/docs/getting-started/migrate-from-termius).
Yes. CtrlOps supports unlimited server connections with named server cards, visual grouping, and one-click connect. Unlike Termius's host groups, CtrlOps also shows live CPU, RAM, and disk metrics for every connected server without running manual commands. For a full guide on multi-server management workflows, see [how to manage multiple servers without losing control](https://ctrlops.io/blog/manage-multiple-servers-without-losing-control).
---
# 9 Best Termius Alternatives in 2026 (Tested & Ranked) (/blog/termius-alternatives)
Author: Hiren Kalariya | Role: Co-Founder & CEO, TST Technology | Published: 2026-08-06 | Updated: 2026-08-24 | Tags: Termius Alternatives, Termius, SSH Client, Server Management Tool | Reading Time: 19 min read
> Termius stops at SSH. We tested 9 alternatives - CtrlOps, Tabby, Warp, MobaXterm, iTerm2, PuTTY, Royal TS, WindTerm, SecureCRT - on real Ubuntu servers.
The best Termius alternative for developers who need more than SSH is [CtrlOps](https://ctrlops.io), a local-first desktop workspace with one-click deployment automation, live infrastructure monitoring, and an AI terminal at $7/user/month after a 1 month free trial - no credit card required.
For a free open-source option, Tabby offers cross-platform SSH with a plugin ecosystem. Warp is best for AI-native terminal workflows on desktop.
## Why Are Developers Looking for Termius Alternatives in 2026? [#why-are-developers-looking-for-termius-alternatives-in-2026]
Developers search for Termius alternatives because Termius focuses on SSH connections and cross-device sync but lacks deployment automation, infrastructure monitoring, and AI capabilities. Its per-user pricing reaches $20/user/month at team scale, and credentials sync to cloud servers on paid plans.
You connect to your VPS through Termius. The deployment needs a config file updated, so you open the SFTP browser. Then CPU spikes, so you open your cloud provider's console.
A process crashes. Termius's AI autocomplete can't read your `package.json` or server docs. Four tools open. One task half-done.
Whether you're a freelance developer juggling 8 client servers, a startup CTO pushing weekly builds, or an agency engineer bouncing between staging and production, Termius solves the connection problem. It leaves the management problem untouched.
**Reality check:** Trustpilot tells a similar story. As of mid-2026, multiple users report losing saved sessions and credentials after logging out or switching accounts, with one reviewer writing that they lost years of saved data on a simple logout [Termius reviews on Trustpilot](https://www.trustpilot.com/review/termius.com). For a tool that handles SSH keys and server access, data reliability is not optional.
We tested 9 Termius alternatives on Ubuntu 24.04 LTS servers (DigitalOcean droplets) against the same real-world tasks: multi-server connections, Node.js deployment, production incident debugging, config file transfers, and SSH key rotation. Here is what held up.
> **TL;DR: Best Termius Alternatives at a Glance**
>
> Where each tool beats Termius - check the full breakdown below.
| # | Tool | Where It Beats Termius |
| -- | ---------------- | --------------------------------------------------------------------------------------------------------------------------------- |
| 01 | **CtrlOps** | SSH + deployment + monitoring + AI terminal in one local-first app. $7/user/mo (1 mo free), credentials never leave your machine. |
| 02 | **Tabby** | Free open-source SSH with connection manager, SFTP, and plugin ecosystem. No account, no subscription. |
| 03 | **Warp** | GPU-rendered AI terminal with block output and BYOK support. Best for local coding, not server management. |
| 04 | **MobaXterm** | SSH + X11 + RDP + VNC in one Windows app. $69 one-time, no subscription. |
| 05 | **iTerm2** | Free Mac-native terminal with hotkey window, split panes, and tmux integration. |
| 06 | **PuTTY** | 3 MB portable SSH client. Zero install, 25+ years of reliability. |
| 07 | **Royal TS/TSX** | Multi-protocol manager for mixed Linux + Windows environments. SSH, RDP, VNC in one UI. |
| 08 | **WindTerm** | Fastest free terminal. C-based with dynamic memory compression and built-in SFTP. |
| 09 | **SecureCRT** | FIPS 140-2 certified. 31 years of enterprise trust. $119 one-time. |
**Bottom line:** Pricing and plans may change over time. For the latest pricing and feature details, please visit the official websites of the respective providers.
Prefer to watch? All 9 tools ranked, tested on real Ubuntu servers - in about 7 minutes:
***
## 9 Best Alternatives to Termius (In-Depth Review) [#9-best-alternatives-to-termius-in-depth-review]
The 9 best Termius alternatives in 2026 are CtrlOps, Tabby, Warp, MobaXterm, iTerm2, PuTTY, Royal TS/TSX, WindTerm, and SecureCRT, each solving a specific gap that Termius leaves open, from deployment automation and AI diagnostics to free open-source SSH and enterprise compliance.
### 1. CtrlOps: Best Overall Termius Alternative [#1-ctrlops-best-overall-termius-alternative]
CtrlOps is the best overall Termius alternative because it combines SSH, a GUI file manager, live infrastructure monitoring, automated backups, one-click deployment, and an approval-gated AI terminal in a single local-first desktop app at $7/user/month after a 1 month free trial - no credit card required, with all credentials stored on your local machine.
[CtrlOps](https://ctrlops.io) is not a terminal replacement. It replaces your entire server management stack. While Termius stops at the SSH connection, CtrlOps handles what happens after you connect: deploying code, monitoring health, transferring files, scheduling backups, and diagnosing issues with AI.
**What CtrlOps does well:**
* Named server cards with one-click connect (no raw IPs, no host group hunting)
* Approval-gated AI terminal: generates commands, shows each one before execution, waits for your approval.
* MCP server integration: AI reads your project files and docs (Context7, GitHub, Filesystem) before suggesting commands
* One-click deployment for Node.js, React, Next.js: Git clone, npm install, PM2, Nginx, SSL in [4-5 minutes instead of 30-45](https://ctrlops.io/blog/deploy-nodejs-app-linux-vps)
* Live infrastructure monitoring: CPU, RAM, disk, processes across all connected servers
* GUI file manager with drag-and-drop (no separate SFTP client)
* Automated backups to S3, R2, B2, Wasabi, DO Spaces, MinIO
* Local-only credential storage (AES-256, never leaves your machine)
*Beyond these core capabilities, CtrlOps is packed with features like a visual file manager, custom scripts, port forwarding, and more. To explore all features, visit the [CtrlOps Features](https://ctrlops.io/features) page.*
**Where CtrlOps falls short:**
* No mobile app (desktop only: macOS, Windows, Linux)
* No serverless support (Lambda, Cloud Functions)
* No Kubernetes or container orchestration
**Best for:**
* Managing 5-15 client servers under named cards without mixing up environments.
* Developers who want approval-gated AI command generation that doesn't run without permission.
* Speeding up deployment of Node.js, React, and Next.js applications to 4-5 minutes instead of 30-45.
* Teams and individuals looking to replace separate SFTP, monitoring, and backup tools.
**Pricing:** $7/user/month (unlimited servers). $70/user/year. 1 month free trial, no credit card required. A 5-person team pays $350/year vs. $1,200/year on Termius Team.
Ughareja Infotech ran that same math at $70/year against Termius Pro at $120/year, then [moved all six of its servers across in under two minutes](/case-studies/ughareja-infotech).
**Platforms:** macOS (Apple Silicon + Intel), Windows, Linux.
> "I recently bought the Lifetime Subscription of CtrlOps because it genuinely helps in daily workflows."
>
> * **Prince Sherasiya**, Technical Lead at Spirex Infoways ([original post on X](https://x.com/prince_ptl0506/status/2049714386143748111))
*Want a head-to-head comparison? Read our [CtrlOps vs. Termius Comparison](https://ctrlops.io/compare/ctrlops-vs-termius).*
***
### 2. Tabby: Best Free Open-Source Alternative [#2-tabby-best-free-open-source-alternative]
Tabby is the best free Termius alternative because it provides cross-platform SSH with a built-in connection manager, SFTP transfers, split panes, and a plugin ecosystem, all under an MIT license with no account required.
[Tabby](https://tabby.sh/) (formerly Terminus) is a cross-platform terminal emulator built with Electron. It combines local shell, SSH, Telnet, and serial connections in a single tabbed interface with a modern, customizable UI.
**What Tabby does well:**
* Cross-platform support (macOS, Windows, Linux) with identical features
* Built-in SSH client with connection profiles, SFTP, and Zmodem file transfers
* Encrypted local password manager with master passphrase
* Plugin ecosystem for Docker, clickable URLs, enhanced autocomplete
* Split panes and saved workspace layouts
* X11 and port forwarding, jump hosts, agent forwarding
* No account, no subscription, no usage limits
**Where Tabby falls short:**
* Electron-based, so heavier on RAM than native terminals
* No AI command generation or diagnostics
* No infrastructure monitoring or deployment automation
* Some plugin combinations cause performance issues
**Best for:**
* Developers looking for a completely free, MIT-licensed open-source SSH manager.
* Customizing their terminal environment via active community-built plugins.
* Storing keys securely in an encrypted local password manager.
**Pricing:** Free, open-source (MIT license). Optional Tabby Web service has a paid tier.
**Platforms:** macOS, Windows, Linux.
Tabby gives you more out of the box than Termius's free Starter plan: SFTP, port forwarding, session management, and a plugin system, all without paying anything. The trade-off is no AI, no monitoring, and higher memory usage.
***
### 3. Warp: Best AI Terminal (Desktop Only) [#3-warp-best-ai-terminal-desktop-only]
Warp is the best AI-first terminal for developers who live in the command line and want natural language command generation, but it's built for local development, not remote server management.
[Warp](https://www.warp.dev/) is a GPU-rendered terminal built in Rust. It structures output into selectable blocks, includes an AI Agent Mode that translates plain English into shell commands, and supports BYOK for OpenAI, Anthropic, and Google models.
**What Warp does well:**
* AI Agent Mode converts natural language to shell commands
* Block-based output for selecting, filtering, and sharing command results
* GPU-accelerated rendering, significantly faster than Electron terminals
* Warp Drive for team command sharing and workflow standardization
* BYOK support on all plans, including Free
* Cross-platform (macOS, Windows, Linux)
**Where Warp falls short:**
* AI auto-runs commands by default. On a production server, one misinterpreted prompt can restart the wrong process or drop a table. No approval gate
* Requires a cloud account to use the terminal
* No server directory, file manager, monitoring, or deployment features
* Free tier drops to 75 AI credits/month after 2 months
**Best for:**
* Local command-line workflows with GPU-accelerated rendering in Rust.
* Writing normal English prompts to generate commands via AI Agent Mode.
* Standardizing command logs and shared scripts for developers within teams.
**Pricing:** Free (75-150 AI credits/month). Build: $20/user/month (1,500 credits). Business: $50/user/month.
**Platforms:** macOS, Windows, Linux.
**Reality check:** Any AI terminal that auto-runs commands without a review step is a development-machine feature, not a server-management feature. On a production server with real traffic, one misinterpreted prompt can drop a database or restart the wrong service. CtrlOps shows every command before execution. That approval gate is the difference between a convenient tool and a safe one.
***
### 4. MobaXterm: Best for Windows Power Users [#4-mobaxterm-best-for-windows-power-users]
MobaXterm is the best Termius alternative for Windows users who need multi-protocol support, a built-in X11 server, and a tabbed SSH workspace without a subscription.
[MobaXterm](https://mobaxterm.mobatek.net/) packs SSH, RDP, VNC, FTP, X11, and a Unix shell into a single Windows application. The free Home edition supports 12 sessions. The Professional license is a one-time $69 purchase with unlimited sessions.
**What MobaXterm does well:**
* Built-in X11 server for running graphical Linux apps on Windows
* Multi-protocol: SSH, RDP, VNC, FTP, SFTP, Telnet, serial in one app
* Graphical SFTP browser opens automatically with SSH connections
* Portable version runs from a USB drive with no install
* One-time purchase, no subscription
**Where MobaXterm falls short:**
* Windows only. No macOS, Linux, or mobile support
* No AI features of any kind
* No infrastructure monitoring or deployment automation
* Limited to 12 sessions and 2 SSH tunnels on the free edition
* No cloud sync or team collaboration
**Best for:**
* Windows developers who need SSH, RDP, VNC, and FTP in one interface.
* Running graphical Linux desktop applications on Windows with a built-in X11 server.
* Portability: using the client directly from a USB stick without local installation.
**Pricing:** Free Home edition (limited). Professional: $69/user one-time.
**Platforms:** Windows only.
If you're on Windows and want everything in one tool, MobaXterm is hard to beat for $69. The X11 server alone saves you from installing a separate X server.
For cross-platform needs, look at CtrlOps or Tabby. For a deeper look, see our [MobaXterm alternatives for Mac](https://ctrlops.io/blog/mobaxterm-alternatives-mac) comparison.
***
### 5. iTerm2: Best Free Mac Terminal [#5-iterm2-best-free-mac-terminal]
iTerm2 is the best free Termius alternative for macOS power users who configure everything through `.ssh/config` and prefer keyboard-driven workflows over GUI connection managers.
[iTerm2](https://iterm2.com/) is open-source, built natively for macOS, and deeply integrated with the Apple ecosystem. It provides split panes, a hotkey window overlay, tmux integration, and triggers for automated responses to specific terminal output.
**What iTerm2 does well:**
* Mac-native with Retina support, Finder integration, and Spotlight search
* Hotkey window overlay for quick terminal access over any app
* Split panes and saved window arrangements
* Deep tmux integration
* Command history search and autocomplete
* Completely free (GPL v2)
**Where iTerm2 falls short:**
* No visual file manager, connection directory, AI, monitoring, or deployment
* macOS only
* Everything runs through `.ssh/config`, which requires manual setup
**Best for:**
* macOS power users who want deep integration with the Apple ecosystem.
* Developers who prefer running workflows from a custom-configured `.ssh/config` file.
* Keyboard-only execution using shortcuts, split panes, and tmux profiles.
**Pricing:** Free, open-source (GPL v2).
**Platforms:** macOS only.
iTerm2 is the right pick if you're comfortable managing servers from the command line and don't want any GUI wrapper. When you outgrow manual file transfers and need monitoring, pair it with CtrlOps.
For a full comparison, see our guide to the [best SSH clients for Mac 2026](https://ctrlops.io/blog/best-ssh-client-mac-2026), or the dedicated [Termius alternatives for Mac](https://ctrlops.io/blog/termius-alternatives-mac) roundup.
***
### 6. PuTTY: Best Lightweight Windows SSH [#6-putty-best-lightweight-windows-ssh]
PuTTY is the best Termius alternative for developers who need a zero-cost, zero-install SSH client that connects reliably and stays out of the way. It does one thing and does it well.
[PuTTY](https://www.chiark.greenend.org.uk/~sgtatham/putty/) has been the default Windows SSH client since 1999. It supports SSH, Telnet, Serial, and raw TCP connections in a 3 MB executable that requires no installation.
**What PuTTY does well:**
* Extremely lightweight (under 3 MB)
* Zero install, runs as a portable executable
* Reliable SSH, Telnet, Serial, and raw TCP connections
* PuTTYgen for SSH key generation
* Stable: 25+ years of production use
**Where PuTTY falls short:**
* No tabs, no split panes, no modern UI
* No server directory, you re-enter credentials each session or manage saved sessions manually
* No file manager, AI, monitoring, or deployment
* No built-in SFTP (requires separate WinSCP or PSFTP)
* Windows-centric (Linux version exists but adds nothing over native OpenSSH)
**Best for:**
* Minimalists looking for a zero-install, lightweight (under 3 MB) client.
* Connecting to router consoles, hardware boards, or legacy serial setups.
* Teams seeking maximum stability from a utility with 25+ years of active history.
**Pricing:** Free, open-source (MIT license).
**Platforms:** Windows, Linux.
PuTTY still works for quick SSH connections. But every production incident adds extra minutes in tool switching between PuTTY, WinSCP, a monitoring tab, and ChatGPT.
If you're ready to upgrade, check our roundup of [PuTTY alternatives for Windows](https://ctrlops.io/blog/putty-alternatives-windows).
***
### 7. Royal TS/TSX: Best Multi-Protocol Manager [#7-royal-tstsx-best-multi-protocol-manager]
Royal TS (Windows) and Royal TSX (macOS) are the best Termius alternative for IT professionals who manage mixed Linux and Windows environments and need SSH, RDP, VNC, and web-based connections in a single tabbed workspace.
[Royal TS/TSX](https://www.royalapps.com/) by Royal Apps supports over a dozen connection types, password management integrations (1Password, KeePass, LastPass), and team document sharing through Royal Server.
**What Royal TS/TSX does well:**
* Multi-protocol: SSH, RDP, VNC, Telnet, SFTP, web, VMware, Apple Remote Desktop
* Cross-platform: Windows, macOS, iOS, Android
* Password manager integrations
* One-time perpetual license (no subscription)
* Royal Server for centralized team gateway access
**Where Royal TS/TSX falls short:**
* No AI features, no monitoring, no deployment automation
* Complex UI with a steep learning curve
* Major version upgrades require a new license purchase
* Limited SFTP through plugins, not a full file manager
**Best for:**
* IT professionals managing mixed Linux and Windows infrastructure simultaneously.
* Integrating credentials from managers like 1Password, KeePass, and LastPass.
* Purchasing a one-time perpetual license with no recurring subscription fees.
**Pricing:** Free (up to 10 connections). Individual: \~€49 one-time. Includes 1 year of updates.
**Platforms:** macOS, Windows, iOS, Android.
Royal TS/TSX wins when you need one tool for SSH to Linux servers and RDP to Windows machines. Termius only handles SSH and SFTP. For pure SSH-to-Linux server management with AI and monitoring, CtrlOps is more focused.
***
### 8. WindTerm: Best Cross-Platform Free Client [#8-windterm-best-cross-platform-free-client]
WindTerm is the best free cross-platform Termius alternative for developers who prioritize raw terminal performance and built-in SFTP without paying for any subscription.
[WindTerm](https://github.com/kingToolbox/WindTerm) is built in C with dynamic memory compression. In [published benchmarks](https://github.com/kingToolbox/WindTerm#terminal-performance), it uses 107 MB to process 97.6 MB of random text data. xterm consumes over 3,300 MB and PuTTY uses 733 MB for the same test.
**What WindTerm does well:**
* Extremely fast: C-based with dynamic memory compression
* Built-in SFTP and SCP for file transfers
* Deep tmux integration with native UI
* Session management with auto-login, SSH ProxyJump
* Local, remote, and dynamic port forwarding
* Cross-platform with identical features on all OSes
* Free for commercial and non-commercial use
**Where WindTerm falls short:**
* No AI features, monitoring, or deployment automation
* Some settings require manual config file editing
* Smaller community with fewer tutorials
* Partially open source (not all source code released)
**Best for:**
* Users looking for the fastest possible terminal client written in pure C.
* Running split terminal sessions and managing directories on multiple servers smoothly.
* Speeding up remote file access with built-in, lightweight SFTP and SCP tools.
**Pricing:** Free (Apache-2.0 license on released source code).
**Platforms:** macOS, Windows, Linux.
WindTerm delivers more features than Termius's free Starter plan: SFTP, port forwarding, tmux integration, and session management. Zero cost. The trade-off is no AI and no server management features beyond the terminal.
***
### 9. SecureCRT: Best Enterprise SSH Client [#9-securecrt-best-enterprise-ssh-client]
SecureCRT is the best Termius alternative for regulated enterprises that require FIPS 140-2 compliance, advanced scripting, and a 31-year track record of stability.
[SecureCRT](https://www.vandyke.com/products/securecrt/) by VanDyke Software has been shipping since 1995. It supports SSH, Telnet, Serial, and RDP connections with Python, VBScript, JScript, and Perl scripting for automation.
**What SecureCRT does well:**
* FIPS 140-2 compliance for government and regulated industries
* Advanced scripting in Python, VBScript, JScript, Perl
* Multi-protocol: SSH, Telnet, Serial, RDP
* 31 years of stability and enterprise trust
* Cross-platform: Windows, macOS, Linux
* Perpetual license with no recurring fees
**Where SecureCRT falls short:**
* Legacy UI that hasn't modernized
* No AI features of any kind
* No infrastructure monitoring or deployment
* $119 per license plus $48/year for renewal after the first year
* No free tier, only a 30-day evaluation
**Best for:**
* Regulated enterprise teams requiring certified FIPS 140-2 compliance.
* Automating repetitive terminal sequences with Python, VBScript, or Perl scripts.
* Operations managers wanting reliable security support from a 31-year legacy vendor.
**Pricing:** $119 one-time (1 license, includes 1 year of updates). SecureCRT + SecureFX bundle: $129. Renewal after year 1: $48/year.
**Platforms:** macOS, Windows, Linux.
SecureCRT wins on compliance and scripting depth. If your organization requires FIPS certification or government-approved SSH, it's the safest pick at $119 with 31 years of production history behind it. For teams that need modern features alongside SSH, see our [SecureCRT alternatives comparison](https://ctrlops.io/blog/securecrt-alternatives-mac).
***
***
## How Much Does Each Termius Alternative Cost? [#how-much-does-each-termius-alternative-cost]
CtrlOps is the most cost-effective all-in-one option at $7/user/month with unlimited servers after a 1 month free trial, while free tools like Tabby, iTerm2, PuTTY, and WindTerm cover SSH basics at zero cost. Paid tools range from $69 one-time (MobaXterm) to $50/user/month (Warp Business).
| Tool | Free Tier | Paid Price | Pricing Model | Includes |
| ------------ | ------------------------ | ---------------------------- | -------------------- | ------------------------------------------------------------------- |
| **CtrlOps** | **1 month free trial** | **$7/user/month ($70/year)** | **Subscription** | **SSH, AI terminal, monitoring, deployment, backups, file manager** |
| Tabby | Full features | Optional Tabby Web tier | Open-source (MIT) | SSH, SFTP, connection manager, plugins |
| Warp | 75-150 AI credits/month | $20/user/month (Build) | Subscription | AI terminal, block output, Warp Drive |
| MobaXterm | 12 sessions max | $69/user one-time | Perpetual license | SSH, RDP, VNC, X11, SFTP |
| iTerm2 | Full features | Free | Open-source (GPL v2) | Mac terminal, split panes, tmux |
| PuTTY | Full features | Free | Open-source (MIT) | SSH, Telnet, serial connections |
| Royal TS/TSX | 10 connections | \~€49 one-time | Perpetual license | SSH, RDP, VNC, multi-protocol |
| WindTerm | Full features | Free | Apache-2.0 (partial) | SSH, SFTP, SCP, tmux integration |
| SecureCRT | 30-day eval only | $119/license one-time | Perpetual license | SSH, Telnet, serial, scripting, FIPS |
| Termius | SSH + SFTP + local vault | $10-30/user/month | Subscription | SSH, SFTP, cloud sync, mobile apps |
***
## Final Verdict: Which Termius Alternative Should You Pick? [#final-verdict-which-termius-alternative-should-you-pick]
We listed 9 Termius alternatives, each one built to solve a specific gap that Termius leaves open, whether that's AI-assisted debugging, deployment automation, infrastructure monitoring, local credential storage, or cross-platform open-source access.
But if you're looking for one tool that covers everything, SSH connections, file management, live monitoring, automated backups, and AI diagnostics, [CtrlOps](https://ctrlops.io) is the most complete Termius alternative on this list.
Everything you need for server management lives in one local-first desktop app.
* Named server cards with one-click connect across all your servers
* Approval-gated AI terminal with BYOK (OpenAI, Claude, Gemini)
* MCP integration so AI reads your actual project files and docs before suggesting commands
* One-click deployment for Node.js, React, Next.js (4-5 minutes instead of 30-45)
* Live CPU, RAM, disk, and process monitoring across all connected servers
* GUI file manager with drag-and-drop (no separate SFTP client needed)
* Automated backups to S3, R2, B2, Wasabi, DO Spaces, MinIO
* $7/user/month, unlimited servers, 1 month free trial (no credit card required)
## Frequently Asked Questions [#frequently-asked-questions]
Tabby is the best completely free Termius alternative. It's open-source under the MIT license, runs on macOS, Windows, and Linux, and includes SSH with a connection manager, SFTP transfers, split panes, and a plugin ecosystem. WindTerm is another strong free option with better raw performance. For a free trial of a full server management workspace with AI and deployment automation, CtrlOps offers a 1 month free trial with no credit card required at $7/user/month after the trial.
Tabby (formerly Terminus) is the most popular open-source Termius alternative. It runs on macOS, Windows, and Linux with SSH, serial, and Telnet support under an MIT license. WindTerm is another strong option with superior performance benchmarks, though only partially open-source (Apache-2.0 on released code). PuTTY is also open-source under the MIT license but lacks tabs, split panes, and modern UI features.
Termius is frequently misspelled as Terminus, and this guide covers the same tools either way. Terminus is also the former name of Tabby, the open-source terminal ranked second here, so either spelling lands you in the right place.
For all-in-one server management on Mac, CtrlOps is the most complete option: SSH, AI terminal, file manager, monitoring, and deployment in one app at $7/user/month after a 1 month free trial - no credit card required. For a free Mac-native terminal, iTerm2. For AI-first local coding, Warp ($20/month). For multi-protocol work (RDP + SSH + VNC), Royal TSX (\~€49 one-time). For zero-cost open-source, Tabby. For the full Mac-specific breakdown, see our [Termius alternatives for Mac](https://ctrlops.io/blog/termius-alternatives-mac) guide.
Yes. CtrlOps covers SSH connections and adds one-click deployment, live monitoring, a GUI file manager, automated backups, and a BYOK AI terminal with MCP integration. The main trade-off: CtrlOps is desktop-only while Termius has mobile apps for iOS and Android.
Yes. Termius offers a free Starter plan that includes SSH, SFTP, local vault storage, AI autocomplete, and port forwarding. The Starter plan stores credentials locally. Upgrading to Pro ($10/month), Team ($20/user/month), or Business ($30/user/month) adds cross-device sync, team vaults, and enterprise features, but also moves credentials to cloud servers.
Three SSH-capable tools offer AI features in 2026. CtrlOps has an approval-gated AI terminal that shows commands before execution and supports BYOK with OpenAI, Claude, or Gemini, plus MCP integration for project context. Warp has AI Agent Mode that auto-runs commands with BYOK support. Termius has an AI Agent with confirmation prompts and autocomplete. CtrlOps is the only one that combines AI with infrastructure monitoring and deployment automation.
Yes. Termius has no deployment automation at any tier. Deploying a Node.js app through Termius requires 13 manual steps. CtrlOps reduces this to a 3-step form (select framework, paste GitHub URL, set variables) that completes in minutes.
Tabby is the best self-hosted alternative. It's open-source (MIT license) and offers Tabby Web for browser-based terminal access that you can host on your own infrastructure, though a browser terminal adds a proxy hop that a desktop client does not have (see [web-based vs. local SSH clients](/blog/web-based-vs-local-ssh-client)). WindTerm is another option: free, portable, and stores all data locally without any cloud dependency. CtrlOps is local-first by design, storing all credentials and configurations on your machine, though it's not self-hosted in the traditional sense.
CtrlOps has a built-in Termius importer, so there is no export file to generate and nothing to re-type. On the All Servers screen, click the three-dot menu and choose **Import from Termius** under MIGRATE. Your operating system asks once for permission to read the credentials Termius saved, then CtrlOps lists every host it found and imports the ones you select. Hosts, ports, usernames, and SSH keys come across in about 30 seconds, read locally on your machine with nothing uploaded. Termius snippets, port-forwarding rules, and sync groups do not transfer. Full walkthrough: [migrate from Termius to CtrlOps](/docs/getting-started/migrate-from-termius).
Keep Termius if you primarily access servers from your phone or tablet. Termius is the only professional SSH client with genuine iOS and Android apps. Also keep Termius if your team relies on real-time collaboration features like shared vaults and session sharing across devices. CtrlOps, Warp, iTerm2, and most alternatives are desktop-only. If mobile access is a daily requirement, not just a nice-to-have, Termius remains the best option.
Termius Starter is free. Pro costs $10/month per user. Team costs $20/user/month. Business costs $30/user/month. CtrlOps costs $7/user/month ($70/year) after a 1 month free trial - no credit card required, and includes monitoring, deployment, backups, file management, and AI diagnostics at every tier.
Yes. CtrlOps runs on macOS (Apple Silicon and Intel), Windows, and Linux. The interface and features are identical across all platforms. Download the installer for your OS from [ctrlops.io](https://ctrlops.io). The 1 month free trial works on all platforms.
Termius is worth it if you need cross-device SSH access with mobile apps. The free Starter plan covers basic SSH, SFTP, and local credential storage. The Pro plan ($10/month) and Team plan ($20/user/month) add cloud sync and shared vaults, but also move credentials to cloud servers. If your daily work goes beyond SSH, deploying code, monitoring servers, debugging with AI, tools like CtrlOps ($7/user/month, 1 month free) cover those tasks without needing 3-4 separate apps alongside Termius.
---
# Web-Based vs. Local SSH Clients: Which Is Better in 2026? (/blog/web-based-vs-local-ssh-client)
Author: Daxesh Italiya | Published: 2026-08-24 | Updated: 2026-08-24 | Tags: web-based ssh client, local ssh client, browser ssh client, ssh client comparison | Reading Time: 21 min read
> Web-based and local SSH clients compared on latency, key storage, audit logging, and daily workflow, with a decision framework for developers in 2026.
Web-based and local SSH clients use the same protocol, but they differ in where the client runs, how credentials are stored, and what sits between you and the server. Local clients connect directly through a single hop. Web-based clients route through a two-hop proxy. Neither is universally better. Your daily workflow, team size, and security needs decide the right choice.
## Key Takeaways [#key-takeaways]
Neither web-based nor local SSH clients are universally preferred. Local clients win on latency, private key control, and terminal customization. Web-based clients win on device flexibility, centralized access revocation, and built-in audit logging. Most production teams run a local client as the daily driver and keep a web-based path as a documented emergency fallback.
> **TL;DR: which client type fits your situation**
>
> * **Solo developer working hands-on daily** - Local SSH client. Low latency, full key control, deeper customization.
> * **Team that needs high security and granular individual access** - Local SSH client. Keys stay on user devices or hardware tokens, with no third-party web proxy in the connection path.
> * **Large team sharing 2 to 3 servers with moderate security needs** - Web-based SSH client. Browser access for everyone without distributing key files, when proxy latency is acceptable.
> * **Developer managing 3+ servers who wants SSH, file management, monitoring, and AI diagnostics in one tool** - [CtrlOps](https://ctrlops.io), a local-first desktop app at $7/user/month after a 1 month free trial - no credit card required.
| Factor | Local SSH Client | Web-Based SSH Client |
| ----------------------------- | -------------------------------------- | ----------------------------------------- |
| **Installation** | Requires software on your device | None, runs in any browser |
| **Connection path** | Direct to server (1 hop) | Via proxy or backend (2 hops) |
| **Latency** | Low, more responsive | Higher, extra hop adds delay |
| **Private key storage** | Your device or a hardware token | Managed by the provider, or session-based |
| **Centralized audit logging** | Requires separate tooling | Often already in place |
| **Access from any device** | Only devices with the client installed | Any device with a browser |
| **Best for** | Everyday hands-on work | Emergency access, compliance teams |
Prefer to watch? The short version - the two-hop architecture, the seven differences, and how to pick - in under 7 minutes:
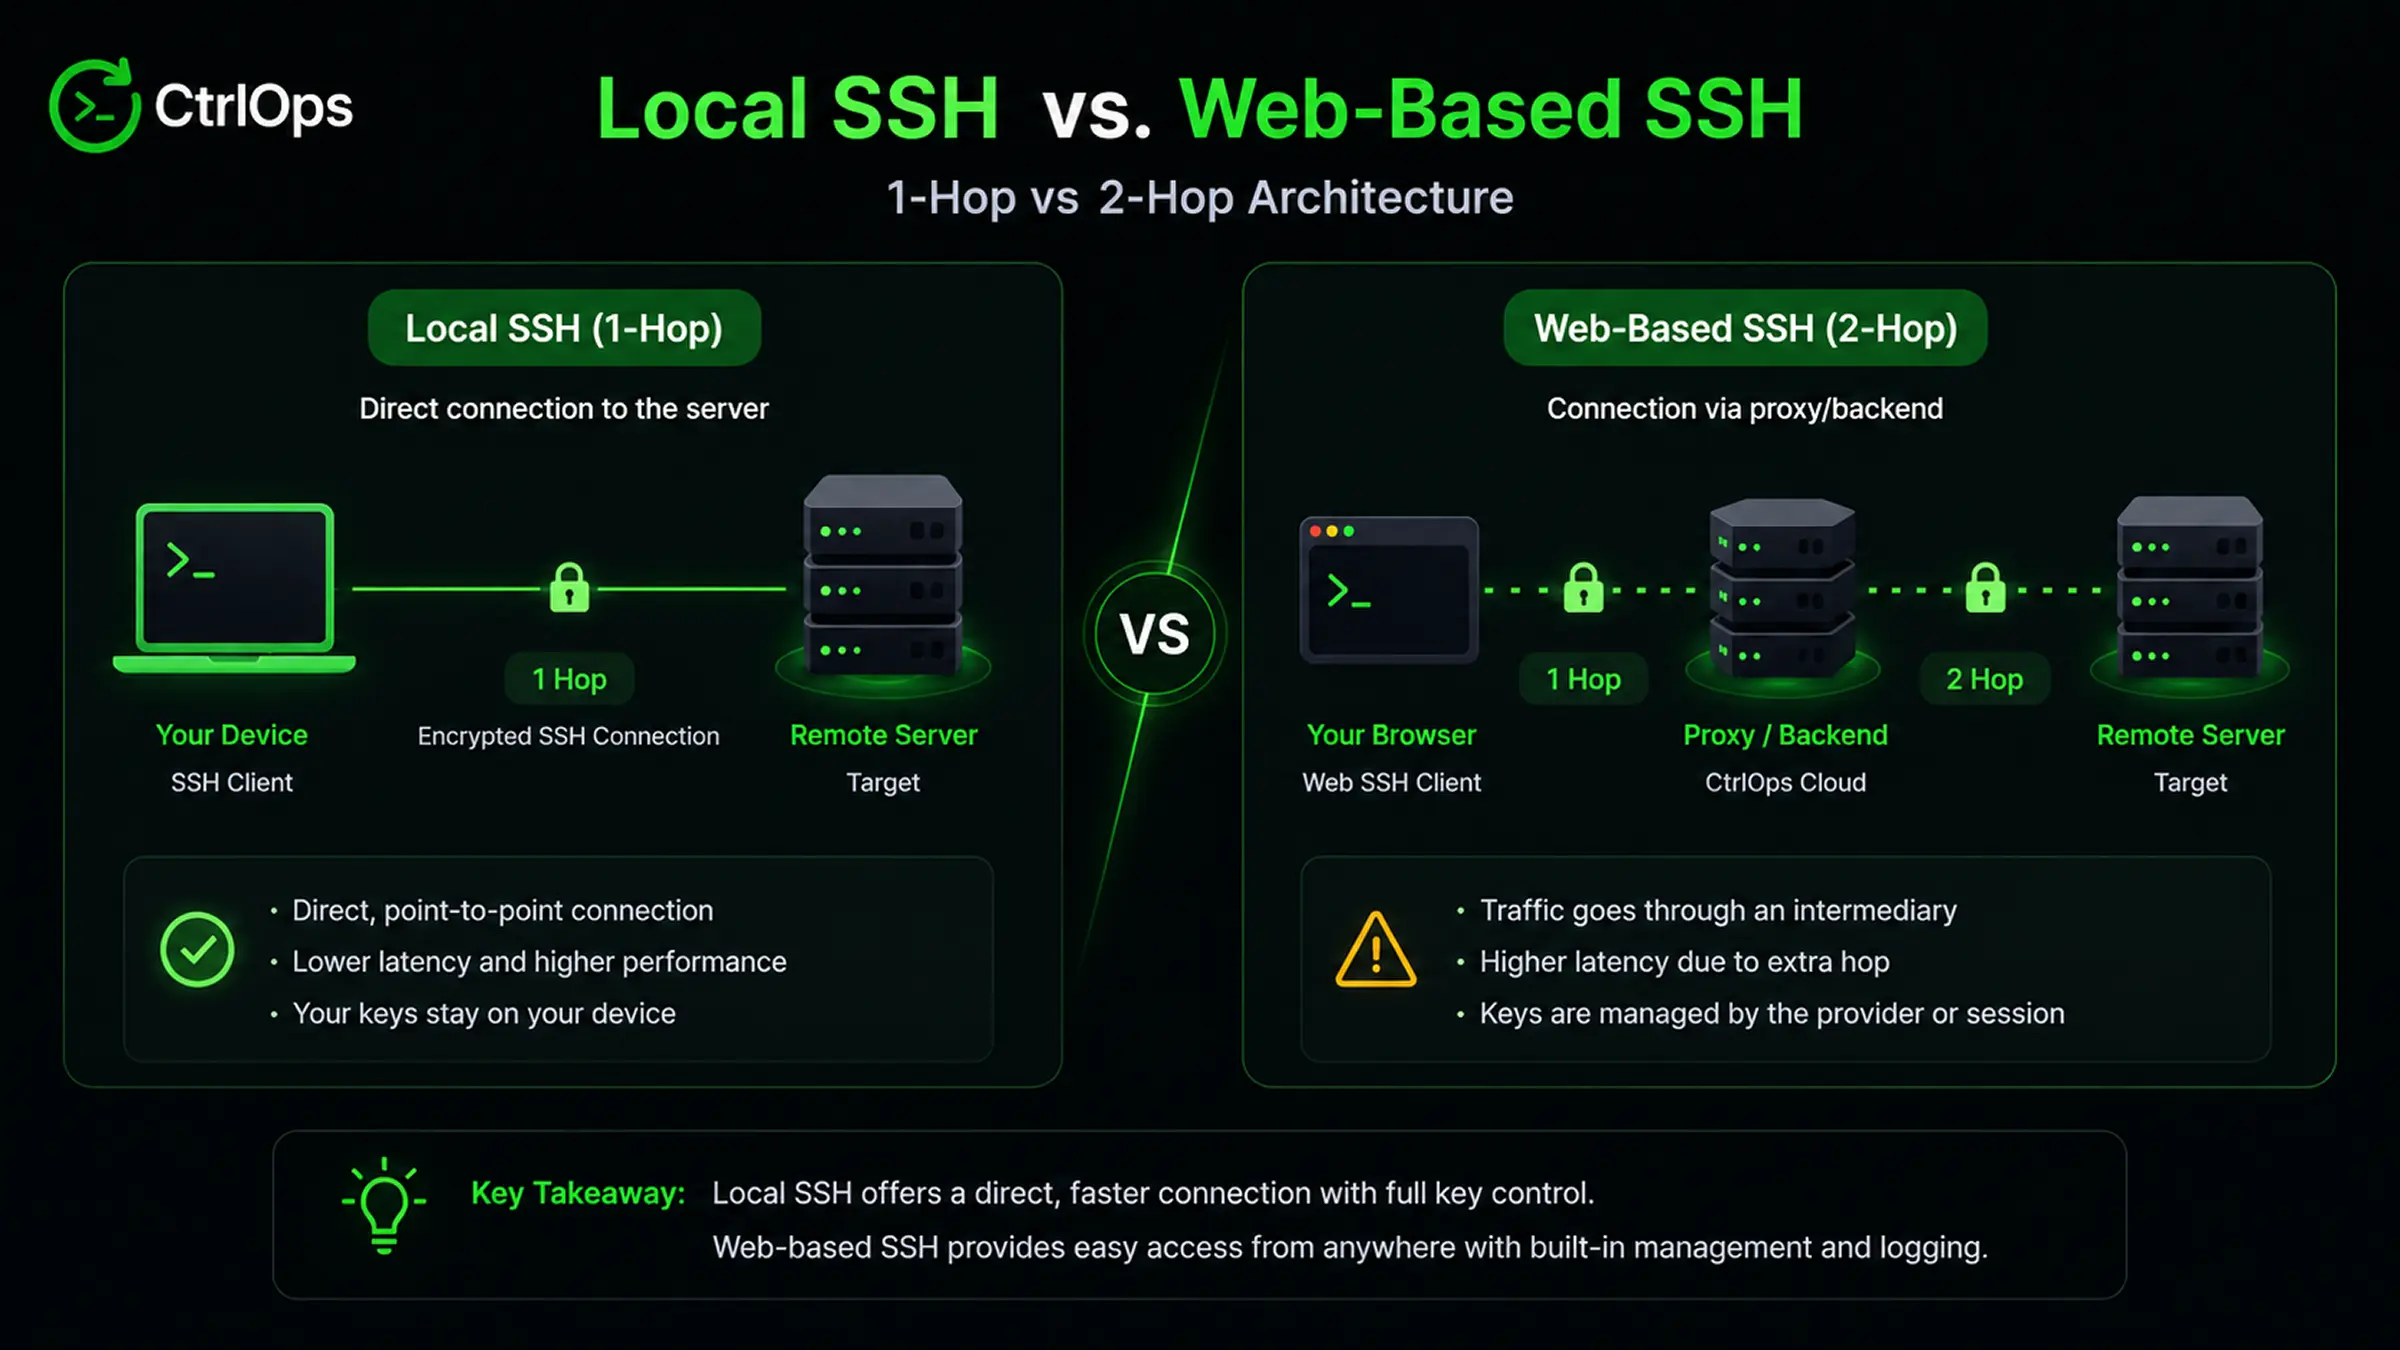
## What Is an SSH Client and Why Does Its Type Matter? [#what-is-an-ssh-client-and-why-does-its-type-matter]
An SSH client is software that initiates an encrypted connection to a remote server. It handles authentication (password or key pair), opens a secure channel, and gives you a shell to run commands, transfer files, or forward ports. Every SSH client performs the same core functions. The difference is where the client runs and what happens between you and the server.
A **local SSH client** is installed on your computer. The connection goes directly from your machine to the server. One hop. Your keys never leave your device.
A **web-based SSH client** runs inside your browser. A backend service translates your keystrokes into SSH commands and streams the output back over HTTPS or WebSocket. Two hops. Your browser talks to a proxy, and the proxy talks to the server.
That architectural difference creates real trade-offs in latency, security, key management, and what happens when something breaks between you and the server.
## How Does a Local SSH Client Work? [#how-does-a-local-ssh-client-work]
A local SSH client connects directly from your device to the target server through an encrypted tunnel. There are no intermediary services in between. Your private key sits on your hard drive (or on a hardware security key like a YubiKey), and the connection is point-to-point.
```
Your laptop --( encrypted SSH )--> Remote server
```
Common local SSH clients include:
* **CtrlOps** - a local-first desktop app combining SSH, file management, monitoring, and AI diagnostics
* **OpenSSH** - the `ssh` command built into macOS, Linux, and modern Windows
* **PuTTY** - long-standing free GUI client for Windows
* **Termius** - a cross-platform native app with an encrypted credential vault and cross-device sync
* **Warp** - a Rust-built AI terminal (coding-focused, not server management)
* **MobaXterm** - a Windows-only SSH client bundled with SFTP, RDP, and X11
A typical connection looks like this:
```bash
ssh -i ~/.ssh/id_ed25519 deploy@203.0.113.10
```
That command tells your local OpenSSH client to authenticate using the private key and connect directly to the server. Nothing passes through a third-party service.
If you are shopping for a local client, we compared the [best SSH clients for Mac in 2026](/blog/best-ssh-client-mac-2026) and the [best SSH clients for Windows](/blog/best-ssh-clients-windows) on real deployment tasks.
**Bottom line:** Local SSH clients offer the lowest latency, complete control over your private keys, and zero dependence on a third-party service being online. The trade-off is that the client must be installed and configured on every device you use.
## How Does a Web-Based SSH Client Work? [#how-does-a-web-based-ssh-client-work]
A web-based SSH client (also called a browser SSH client) runs inside your browser. You open a URL, log in, and a terminal appears on the page, usually rendered with a JavaScript library like xterm.js. But your browser cannot speak raw SSH. A backend proxy handles the actual SSH connection on your behalf.
```
Your browser --( HTTPS / WebSocket )--> Proxy server --( SSH )--> Remote server
```
Common web-based SSH clients include:
* **AWS Systems Manager Session Manager** - built into the AWS console, uses IAM-based credentials instead of SSH keys, and does not require inbound port 22
* **GCP SSH-in-Browser** - Google Cloud's built-in browser terminal for Compute Engine instances
* **Apache Guacamole** - a free, self-hosted gateway supporting SSH, RDP, VNC, and Telnet via browser (Apache License 2.0, latest stable release 1.6.0)
* **Shellngn** - a commercial web-based platform for SSH, SFTP, RDP, and VNC, available as hosted cloud or self-hosted via Docker
* **Wetty, ttyd, WebSSH2** - open-source self-hosted alternatives built on xterm.js
A typical connection works like this: you log in to the AWS console, click "Connect" next to the EC2 instance, select "Session Manager," and a terminal opens directly in your browser tab. No SSH key file on your device. No terminal app required.
**Bottom line:** Web-based SSH clients trade direct control for accessibility. You can connect from any device with a browser, but you are adding a proxy layer, along with its uptime, security practices, and latency, between you and your server.
## What Are the 7 Main Differences Between Web-Based and Local SSH? [#what-are-the-7-main-differences-between-web-based-and-local-ssh]
The architectural gap between browser-based and locally installed SSH clients creates seven measurable differences that show up in daily work. Understanding each one helps you pick the right tool for the situation instead of the one you used last time.
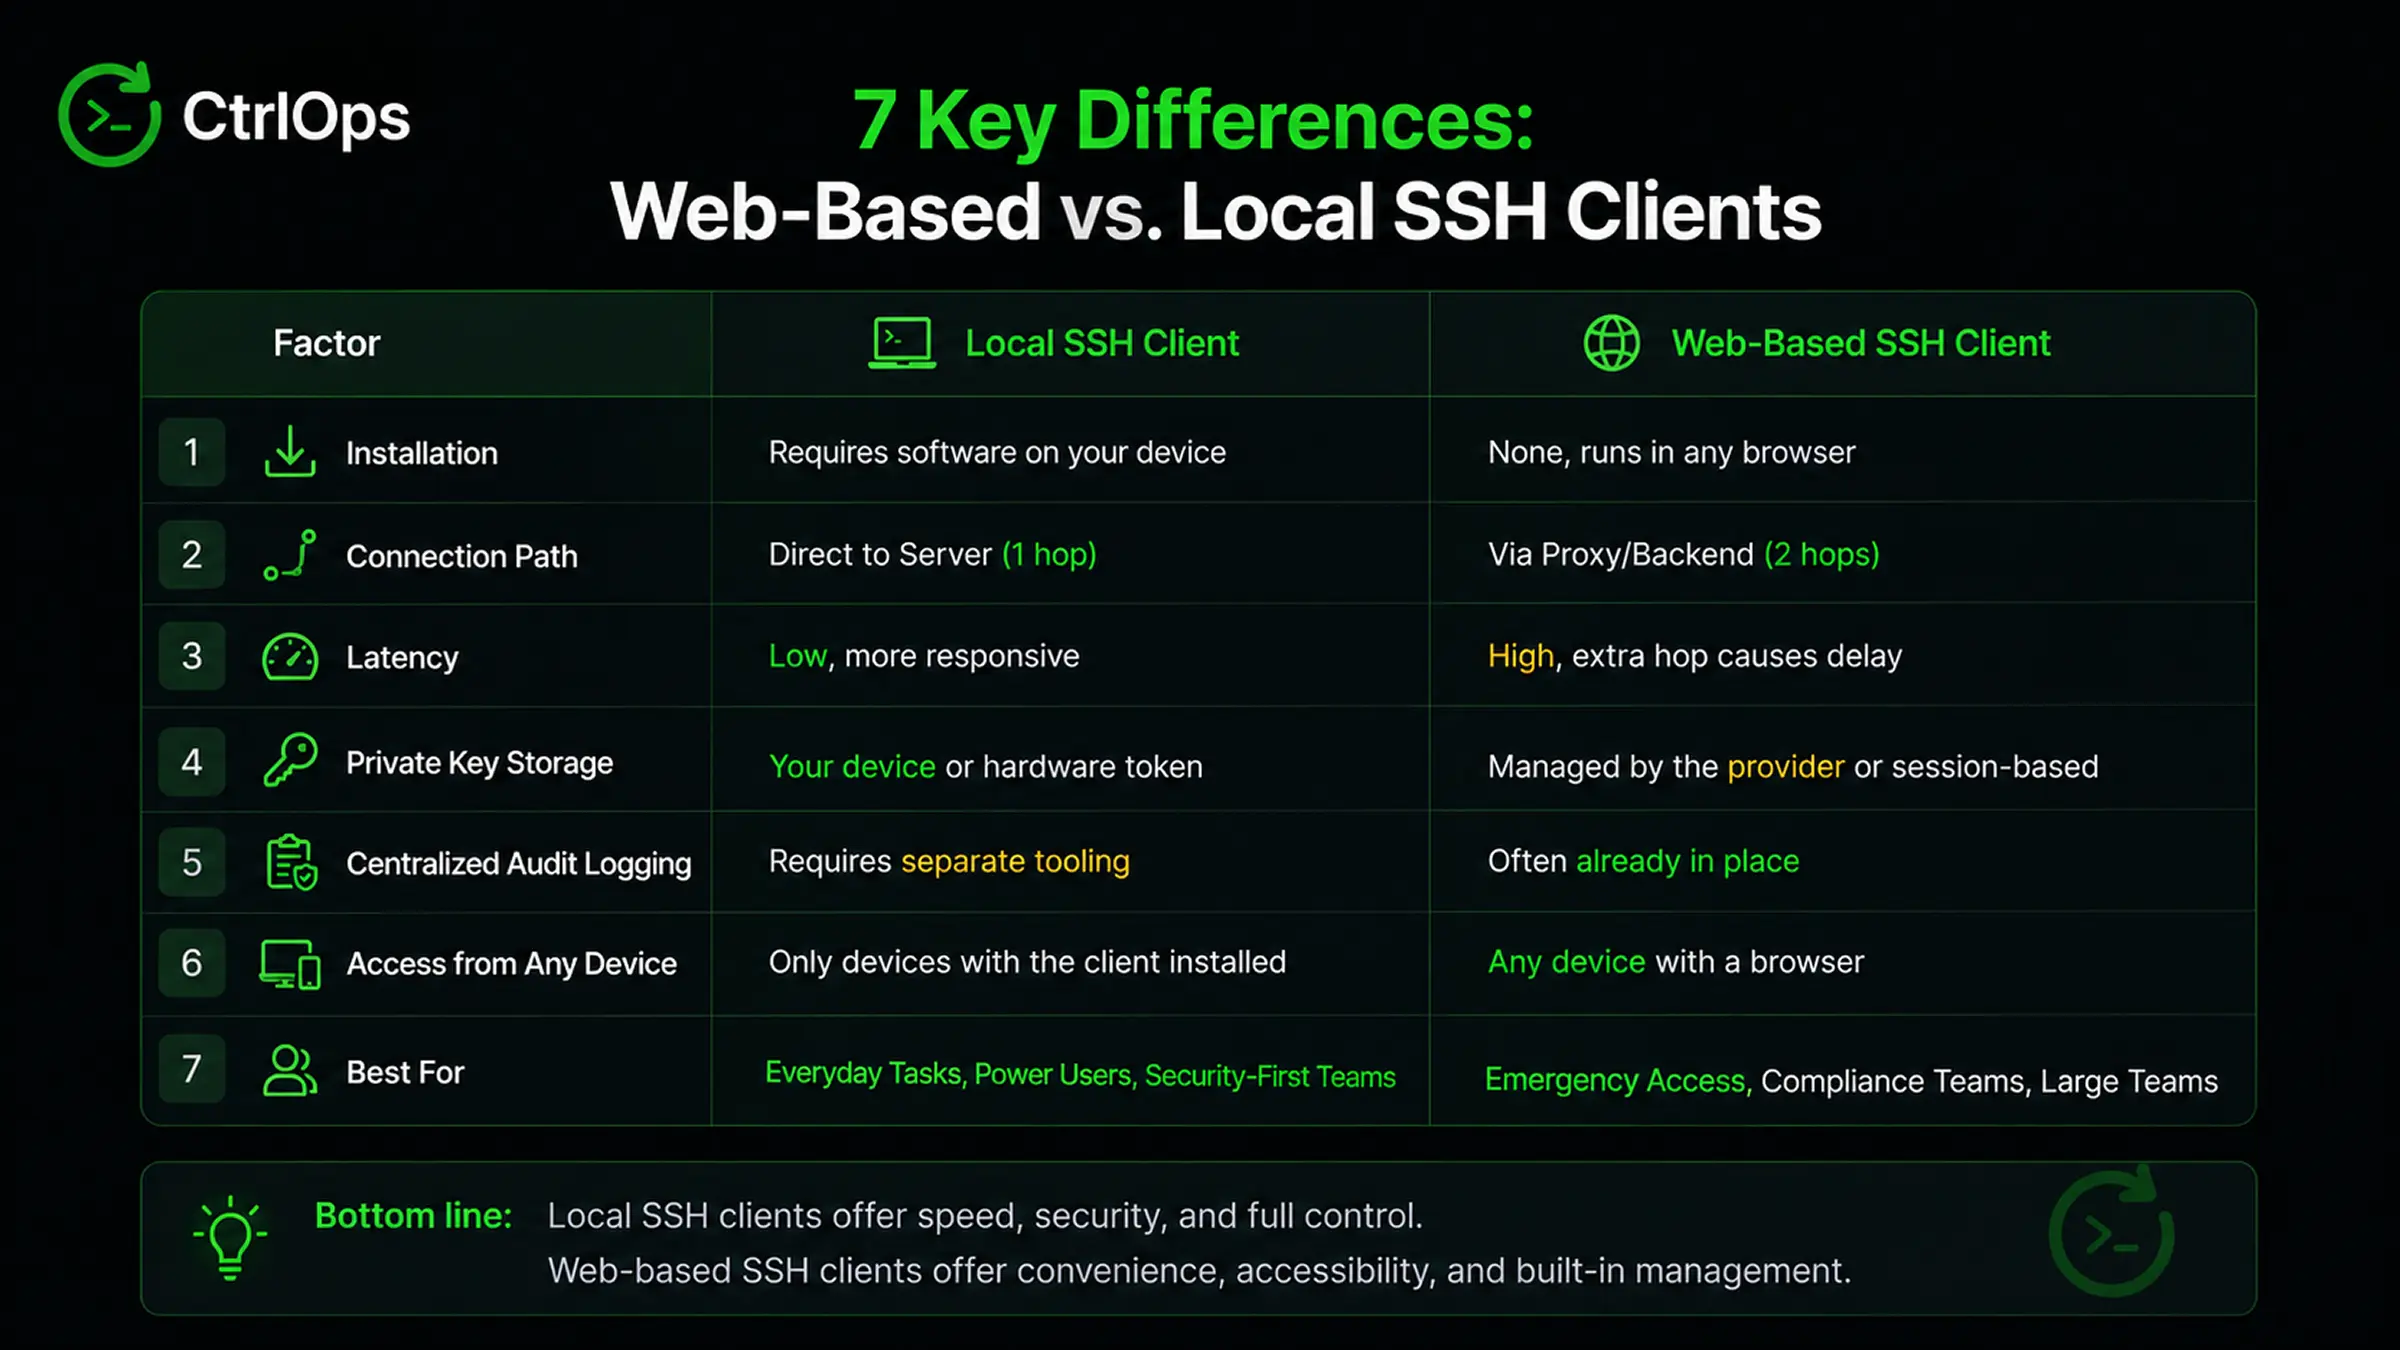
### 1. Connection Path and Latency [#1-connection-path-and-latency]
Local SSH clients connect directly to the server. One network hop. Round-trip latency is the natural distance between you and the host.
Web-based clients add a second hop through a proxy or backend service. For most commands the extra delay is barely noticeable (10 to 50ms). It becomes obvious during interactive work: editing files in `vim`, watching logs scroll with `tail -f`, or typing quickly and expecting immediate feedback.
### 2. Private Key Storage and Control [#2-private-key-storage-and-control]
With a local client, your private key stays on your device. You control the passphrase, the SSH agent, and whether to use a hardware token. No third party ever touches the key.
Web-based clients handle credentials differently. Cloud-native tools like AWS Session Manager skip SSH keys entirely and use temporary, IAM-governed credentials. Self-hosted tools like Apache Guacamole store connection credentials in their own database. Either way, you hand some credential management to another system.
### 3. Installation and Device Access [#3-installation-and-device-access]
A local client requires software installed on every device. Switching to a borrowed laptop, a hotel business-center computer, or a locked-down corporate machine means no SSH access unless the client is already there.
Web-based clients need only a browser and valid login credentials. That makes them appealing for emergency access, contractor onboarding, and restricted environments.
### 4. Offline Flexibility [#4-offline-flexibility]
If the proxy service behind the web-based SSH client goes down, you lose access. Your server can be running fine, but if something breaks in the AWS console or your self-hosted Guacamole instance crashes, you cannot connect.
The local client has no such dependency. If you can reach the server's IP on port 22, you are in.
### 5. Centralized Audit Logging [#5-centralized-audit-logging]
Web-based tools often include session logging out of the box. AWS Session Manager logs every command to CloudTrail, S3, or CloudWatch. Apache Guacamole records sessions for playback. That matters in compliance-heavy environments (HIPAA, SOC 2, PCI DSS).
Local clients provide no centralized audit trail by default. Equivalent logging for local SSH requires extra tooling, such as Teleport or a bastion host with session recording.
### 6. Large-Scale Key Management [#6-large-scale-key-management]
When SSH keys are scattered across every developer's laptop, revoking access after someone leaves means finding every key they hold. According to [Verizon's 2025 DBIR](https://www.verizon.com/business/resources/reports/dbir/), credential abuse accounts for 22% of all data breaches, making it the single most common breach vector. Orphaned SSH keys are a real attack surface.
Web-based access centralizes this. Disable one account and the person loses access everywhere at once. There is no need to hunt through `authorized_keys` files on 19 servers.
For teams on local clients, disciplined [SSH key management practices](/blog/ssh-key-management-best-practices) mitigate the risk, but they depend on that discipline holding.
### 7. Customization and Terminal Experience [#7-customization-and-terminal-experience]
Local clients offer deep customization: themes, keyboard shortcuts, split panes, GPU-accelerated rendering (Warp), multiplexing (tmux), and native clipboard support. The terminal experience is polished and responsive.
Web-based clients are limited by what the browser allows. Copy and paste can be awkward. Scrollback may be capped. Color rendering and font choice depend on the xterm.js configuration.
**Reality check:** Neither approach eliminates risk. Local clients leave you exposed if a laptop holding an unprotected key file is stolen. Web-based clients leave you exposed if the provider's backend is compromised or misconfigured. The right choice depends on which risks you can actually control in your environment.
## Which SSH Client Type Is More Secure? [#which-ssh-client-type-is-more-secure]
Neither web-based nor local SSH clients are inherently more secure. Security depends on how you configure authentication, store credentials, and manage access across your team. Each model offers protections the other lacks.
**Local SSH client security features:**
* Private keys never leave your device (when used correctly)
* No third-party backend in the connection path
* Compatible with hardware security keys (YubiKey, FIDO2)
* Mature, well-audited protocol implementation (OpenSSH has 25+ years of security hardening)
**Web-based SSH client security features:**
* Centralized access revocation (disable one account, lock out everywhere)
* No long-lived SSH keys to manage, distribute, or forget
* Session logging and audit trails already in place
* Can eliminate inbound port 22 entirely (AWS Session Manager uses the SSM agent with outbound connections only)
The overlooked risk with local clients is key proliferation. A developer joins, gets SSH keys for 15 servers, and leaves after six months. Did someone revoke every key from every server? According to [Forbes](https://www.forbes.com/sites/daveywinder/2026/04/30/password-security-286-billion-credential-theft-crimewave-exposed/), 2.8 billion credentials were stolen throughout 2025. Orphaned access credentials, SSH keys included, are a growing attack surface.
The overlooked risk with web-based clients is provider trust. You route every keystroke through a backend service. Well-known cloud providers handle this well. Self-hosted or less mature tools may not isolate sessions properly, may log sensitive output, or may store credentials insecurely.
**Bottom line:** For individual developers, local key-based SSH with Ed25519 keys and a hardware token is the most secure option. For teams of 5+ where people join and leave often, centralized web-based access reduces the surface area for forgotten credentials. Many teams run both.
## Which Gives Better Performance for Daily Work? [#which-gives-better-performance-for-daily-work]
Local SSH clients give the best interactive performance. A direct connection means latency equals the natural round-trip time between your device and the server. That matters for work where you expect immediate keystroke feedback: editing config files in `vim`, running `tail -f` on a production log, or firing off a rapid sequence of diagnostic commands during an incident.
Web-based clients have measurable delay. The extra hop through the proxy adds 10 to 50ms per interaction, depending on the provider and network path. For a one-off command it is invisible. It gets grating at 2 a.m., 45 minutes into debugging a Node.js process that keeps crashing.
Web-based clients also introduce a single point of failure that local clients do not have. If the proxy goes down, you lose access to every server behind it, even servers that are running perfectly. Local SSH has one failure mode: can you reach port 22? Web-based SSH has two: can you reach the proxy, and can the proxy reach the server?
## When Should You Use a Local SSH Client? [#when-should-you-use-a-local-ssh-client]
A local SSH client is the right choice when you need the fastest, most responsive terminal and you are comfortable managing your own keys. Typical scenarios where local pays off:
**Solo developer managing a personal VPS.** Simple, fast, and you have complete control over your one or two keys. OpenSSH with `~/.ssh/config` is all you need.
**An engineer doing heavy hands-on work every day.** Editing configs, tailing logs, running builds, chasing memory leaks. Lower latency and better ergonomics compound over an 8-hour day.
**A developer working across multiple servers at once.** Local clients with multi-tab support keep SSH sessions open on several servers simultaneously. No re-authentication, no session timeouts.
**Security-sensitive environments where keys must never leave the device.** If your compliance requirements forbid passing credentials to third-party services, local key storage is the only option.
The manual multi-server workflow with a traditional local SSH client looks like this:
1. Open Terminal (or PuTTY on Windows)
2. Type `ssh user@server1-ip` and authenticate (30 seconds)
3. Run the diagnostic command, read the output
4. Open another terminal tab, SSH into server 2 (30 seconds)
5. Open a third tab for server 3 (30 seconds)
6. Need a file? Open a separate SFTP client, re-enter credentials (1 to 2 minutes)
7. Need CPU or memory data? Open a browser tab with your monitoring dashboard (1 minute)
8. Context switch between 4 to 5 windows for the next 30 minutes
Total setup time for a 3-server debugging session: 5 to 8 minutes. Total tools open: 4 to 5.
## When Should You Use a Web-Based SSH Client? [#when-should-you-use-a-web-based-ssh-client]
A web-based SSH client is the right choice when accessibility, centralized access control, or compliance logging outweigh the latency trade-off. Typical scenarios where web-based wins:
**Emergency access from an unknown device.** Your laptop died. You are at a coffee shop with a borrowed Chromebook. A web-based client gets you to the server from any browser with nothing to install.
**Enterprise teams with strict compliance requirements.** AWS Session Manager logs every command to CloudTrail. Apache Guacamole records sessions for playback. If auditors need proof of who accessed what and when, built-in session logging saves weeks of tooling work.
**Onboarding a contractor or temporary team member.** Instead of distributing SSH keys and hoping they get revoked later, you create a web-based account with scoped permissions. When the contract ends, you disable the account. Done.
**Servers locked behind private networks with no direct SSH access.** Some infrastructure is deliberately kept off the public internet. A web-based bastion or session manager endpoint may be the only permitted path in.
**Locked-down corporate environments.** If your company laptop blocks outbound connections on port 22 but allows HTTPS, a web-based SSH client tunneled over port 443 is your only option.
**Bottom line:** Many production teams use both: a local client for day-to-day work, and a web-based client as a documented fallback for emergencies, compliance, and restricted environments.
## Can You Get the Best of Both Worlds? [#can-you-get-the-best-of-both-worlds]
The real problem is not "web vs. local." It is the tool sprawl that both paths produce. Even with the best local SSH client, you end up with a terminal in one window, an SFTP client in another, a monitoring dashboard in a browser tab, and a mental map of which server is where.
[CtrlOps](https://ctrlops.io) takes a local-first approach (direct SSH, credentials stored only on your device, no cloud sync) and wraps it in a single desktop app that covers what usually takes 3 to 4 separate tools.
What it actually looks like:
1. Open CtrlOps. Your servers are listed on the dashboard as named cards, not raw IP addresses.
2. Click a server. You get tabbed access to the SSH terminal, file manager, infrastructure monitoring (CPU, memory, disk, processes), and an AI assistant.
3. Need to check another server? Open a second tab. Both stay live. Follow Nginx error logs in one tab while watching memory usage on the database server in the other.
4. Need to upload a config file? Use the built-in file manager. No separate SFTP client. No re-entering credentials.
5. Not sure which command to run? Type the question into the AI terminal in plain English: "Why is memory increasing and not decreasing?" The AI reads your server's actual state, generates the diagnostic commands, shows them to you, and waits for your approval before executing anything.
No web-based SSH client and no traditional local SSH client in the current top search results offers AI-assisted command generation for server management. The standard workflow is still: Google the command, copy it, paste it into the terminal, hope it is correct. CtrlOps is the only local-first SSH tool where you can describe a problem in plain English and get executable commands back, reviewed before anything runs.
The AI terminal is approval-gated by default. It shows each command before execution, explains what it does, flags whether it is safe, and only runs after you click "Run." It supports BYOK (bring your own key) for OpenAI, Anthropic, Google Gemini, or any OpenAI-compatible provider. With MCP server integration it can also pull context from GitHub repositories, local files, or official documentation via Context7 before generating commands.
For teams, CtrlOps includes fleet-wide access management. See everyone logged in across your entire server fleet from a single screen. Onboard a new teammate to multiple servers at once, or offboard a departing one from all servers with a single confirmation. No more checking `authorized_keys` server by server.
Read more about [how AI is changing DevOps workflows](/blog/ai-in-devops) and where approval-gated execution fits in.
## How to Choose: A Decision Framework [#how-to-choose-a-decision-framework]
Your choice between web-based and local SSH comes down to three questions.
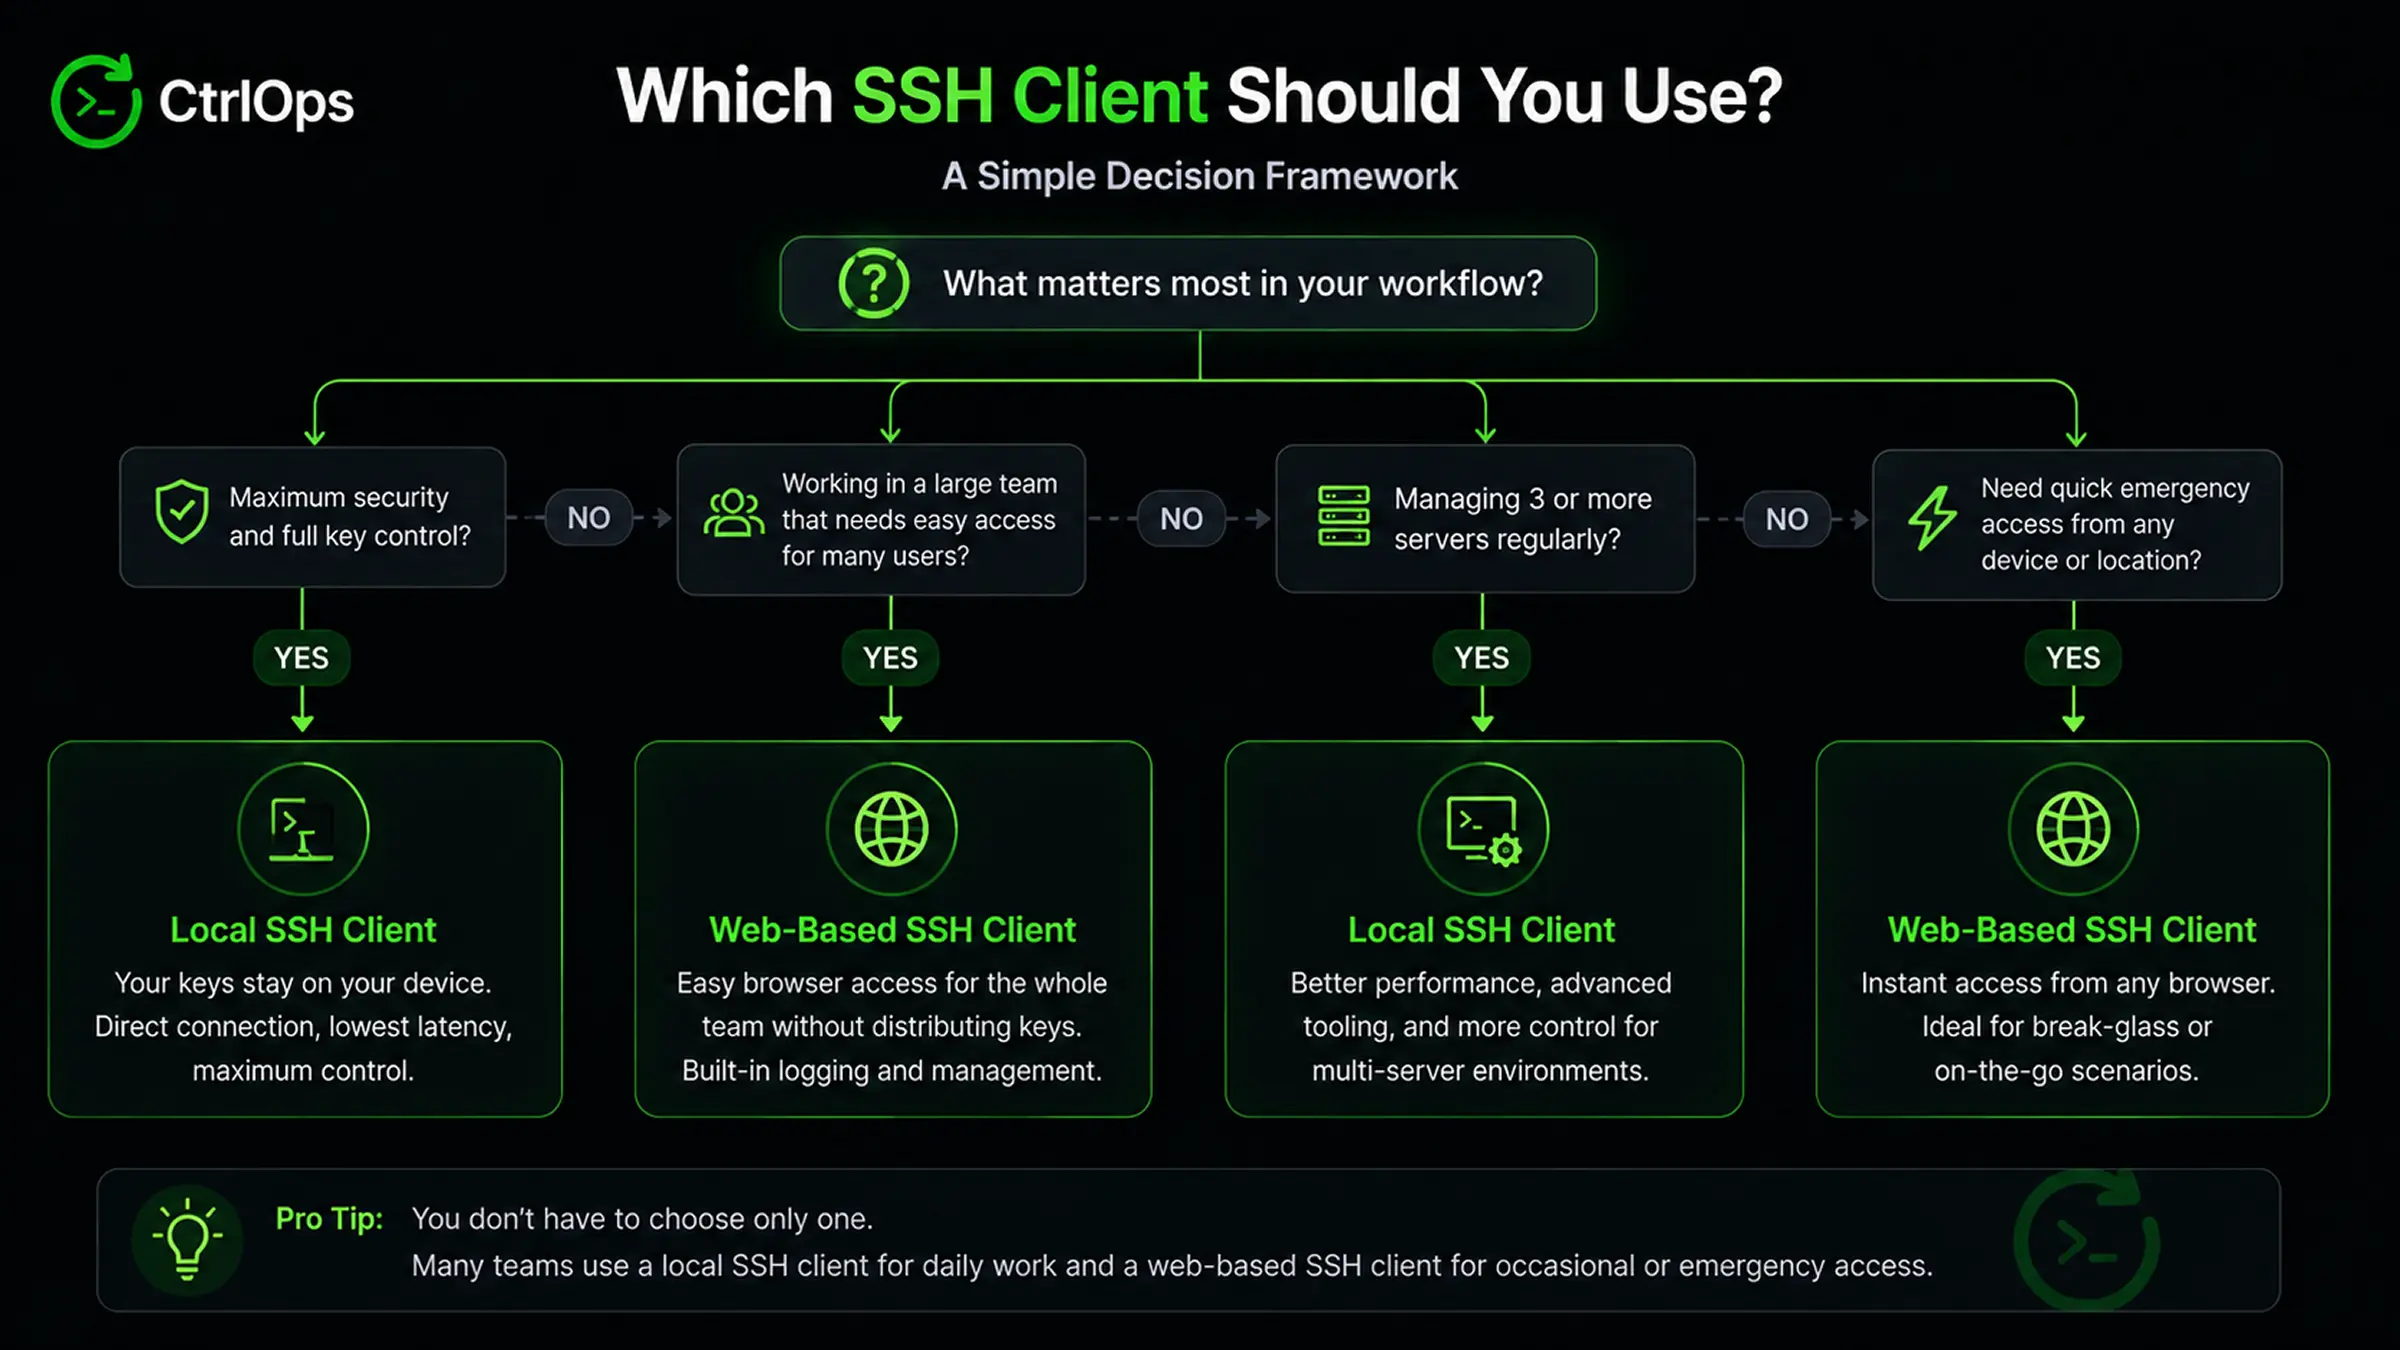
**1. What is your primary daily workflow?**
If you SSH into servers daily for hands-on work (debugging, deploying, editing configs), a local client gives you the speed and customization you need. If you connect occasionally or need an emergency fallback, a web-based client removes the setup burden entirely.
**2. How many people need server access?**
For a solo developer or a team of two, managing local SSH keys is easy. For teams of five or more with regular joiners and leavers, centralized access control prevents orphaned credentials, either through a web-based tool or through a local-first tool like CtrlOps that manages SSH keys across the whole fleet.
**3. What are your compliance requirements?**
If auditors need session recordings and access logs, web-based tools with built-in logging (AWS Session Manager, Apache Guacamole) save a lot of engineering time. If credentials must never pass through third-party infrastructure, local storage is the only path that qualifies.
| Your Situation | Suggested Approach |
| -------------------------------------------------------------------------- | ---------------------------------------------------------------------------------- |
| Solo dev, 1 to 3 servers, daily SSH work | Local client (OpenSSH + `~/.ssh/config`) |
| Developer managing 3 to 15 servers with file transfer and monitoring needs | Local-first all-in-one tool ([CtrlOps](https://ctrlops.io), $7/user/mo, 1 mo free) |
| Enterprise team, 50+ servers, SOC 2 or HIPAA compliance | Web-based (AWS Session Manager) plus a local fallback |
| Emergency access from untrusted devices | Web-based client as a documented backup |
| Contractor or temporary team member | Web-based, with scoped, time-limited accounts |
## Conclusion [#conclusion]
There is no single winner in the web-based versus local SSH client debate. Local clients offer low latency, complete key control, and zero third-party dependencies. Web-based clients offer instant access from any device, centralized audit logging, and one-click access revocation.
For most teams the answer is not one or the other. It is a local client as the daily driver and a web-based option as the safety net. Understanding how each approach handles connections, credentials, and failure modes lets you pick deliberately instead of defaulting to whatever you used last time.
If you manage 3+ servers and you are tired of switching between a terminal, an SFTP client, and a monitoring dashboard, CtrlOps combines local-first SSH with a file manager, live infrastructure monitoring, and an approval-gated AI terminal in one desktop app, at $7/user/month after a 1 month free trial - no credit card required.
It depends on the provider. Well-built platforms like AWS Session Manager use short-lived, IAM-driven credentials and never store long-lived SSH keys, which can be more secure overall than local keys scattered across a dozen laptops. The downside is that you depend on a third-party backend sitting in your connection path, a dependency local clients simply do not have.
Some web-based clients let you import an SSH key, but many use other authentication methods instead. AWS Session Manager relies on IAM policies and the SSM agent rather than traditional SSH keys. Apache Guacamole stores credentials in its own database. The trend is moving toward session-based or identity-provider credentials instead of long-lived key files.
You lose access to that tool even though your servers are running fine. This is the biggest risk of relying on a web-based client as your only access path. Production teams should keep a local SSH fallback for critical systems so a provider outage does not lock them out mid-incident.
Local SSH is faster for interactive work. It connects directly to the server with no extra hop. Web-based clients add 10 to 50ms per interaction through the proxy layer, which compounds during long debugging sessions or file editing. For a quick one-off command or status check, the difference is barely noticeable.
Local clients handle file transfers natively with `scp`, `sftp`, or `rsync`. Web-based clients vary widely. AWS Session Manager has no built-in file transfer, so you need S3 or a separate tool. Apache Guacamole supports drag-and-drop transfers over SSH sessions. Shellngn includes a built-in SFTP panel.
Do not use web-based SSH as the only access method for production servers. If the provider has an outage, you are locked out during an incident. Also avoid it for latency-sensitive interactive work such as editing files in Vim or watching real-time logs for long stretches. The extra proxy hop slows those tasks down noticeably.
CtrlOps is a local-first desktop app for macOS, Windows, and Linux that combines SSH terminal access, a GUI file manager, live infrastructure monitoring, automated backups, and an approval-gated AI terminal in a single interface. Unlike traditional SSH clients, it removes the need to switch between 3 to 4 different tools. It costs $7/user/month after a 1 month free trial - no credit card required - and includes unlimited servers.
No. CtrlOps is a desktop application that connects directly to your server over standard SSH. Credentials are stored locally on your device and never synced to the cloud, which makes it a local-first SSH client rather than a web-based one. If you specifically need browser-based access, AWS Session Manager or Apache Guacamole are the better fit.
AWS Systems Manager Session Manager provides shell access to EC2 instances without SSH keys, open inbound ports, or bastion hosts. Access is controlled through IAM policies. The SSM agent on the instance communicates outbound with the Systems Manager service, so inbound port 22 is not required. Sessions can be logged to CloudTrail, S3, or CloudWatch for compliance.
Apache Guacamole is a free, open-source remote desktop gateway licensed under the Apache License 2.0. It supports SSH, RDP, VNC, and Telnet through the browser using HTML5, and you can host it yourself on your own infrastructure. It includes centralized authentication (LDAP, SAML, TOTP), session recording, and multi-user access control. The latest stable release is 1.6.0.
For personal projects with one or two servers, a single local client is enough. For production teams, keeping both is the safer setup. Use the local client as the daily driver for speed and responsiveness, and keep a web-based client configured as a documented emergency fallback for when your primary machine is unavailable or compromised.
You can manage team SSH keys locally with per-user key pairs, consistent naming conventions, and regular rotation. CtrlOps adds fleet-wide access management, showing every user across all servers on a single screen so you can onboard or offboard across the whole fleet in one action. See our guide to [SSH key management best practices](/blog/ssh-key-management-best-practices) for the full checklist.
---
# How Olbuz Replaced Five Separate Tools With One Local App (/case-studies/olbuz)
Company: Olbuz | Industry: IT Consulting - Web Development & Digital Marketing | Customer: Rakesh Patel, Tech Lead, Olbuz | Published: 2026-08-04
> Olbuz is an IT consulting company running multiple client projects across 4 servers. File transfers ran through Cyberduck and FileZilla, infra checks and backups were manual, and server credentials lived in a Notepad file. Here is how the team moved all of it into one local desktop app.
## The Challenge [#the-challenge]
Olbuz runs multiple client projects at once, each with its own server, its own deployment needs, and its own maintenance routine. Like most growing IT consulting teams, the gaps in the stack grew faster than anyone wanted to admit.
**File transfers ran through two separate tools.** Cyberduck and FileZilla handled moving files to and from servers. They did that job, and nothing else. Anything past a file transfer meant leaving them and picking up something different.
**Infra monitoring and backups had no dedicated tool at all.** Checking server health and running backups were manual tasks, done by hand rather than through any system built for it. The gap was not a bad tool, it was no tool.
**Server credentials were saved in Notepad.** Developers on the team kept IPs and access details in plain text files. It worked, but it was never a convenient or reliable way to manage credentials.
**Backups needed a developer to trigger them.** With no automation in place, someone had to step in and start the process by hand every time, which made backups depend on whoever was free rather than on a schedule.
> "Previously, I had to rely on separate applications to access the terminal and manage server files, which was less convenient and interrupted my workflow. With CtrlOps, everything is available in one place through a clean and user-friendly interface."
>
> **[Rakesh Patel](https://www.linkedin.com/in/rakesh-patel-266a56166/)**, Tech Lead, Olbuz
***
## The Turning Point [#the-turning-point]
Jignesh Gohel, Founder of Olbuz, found CtrlOps through a LinkedIn post. With a 27-person team where only a handful of people touch server infrastructure directly, the appeal was straightforward: one local app that was fast, easy to set up, and did not require a separate panel installed on every VPS.
What stood out early was how quickly it loaded and responded, since everything ran on the local machine instead of round-tripping through a cloud service.
***
## The Solution [#the-solution]
CtrlOps replaced Olbuz's file transfer tools and manual infra and backup work with a single local dashboard covering terminal access, file management, one-click deployment, backups, and infra monitoring.
**One app instead of Cyberduck, FileZilla, and manual work.** Terminal, [file manager](/features/file-manager), deployments, backups, and infra monitoring now run from the same screen, replacing two separate tools and the manual checks that used to fill the rest of the gap.
**PEM key connections that just work.** Server connections and [PEM key setup are straightforward](/features/ssh-management), without the manual back and forth the old tools required.
**Credentials no longer live in Notepad.** Server access is now managed inside CtrlOps directly, instead of a plain text file developers had to maintain by hand.
**Backups that no longer wait on a developer.** What used to be a fully manual process is no longer a recurring interruption for whoever happened to be available, because [backups now run on a schedule](/features/backup).
**Infra visibility without a panel.** Server details are [visible directly inside CtrlOps](/features/infra-monitoring), with no separate panel needed on the VPS itself, and no more manual checks to get the same picture.
**Local-first, and it shows.** Because everything runs on the device rather than through the cloud, the day-to-day experience is simply faster.
> "Earlier there was a need to trigger the developer for backups, but now that's gone. Server connections and PEM key setup are easy, and infra details are visible without needing a panel on the VPS."
>
> **[Rakesh Patel](https://www.linkedin.com/in/rakesh-patel-266a56166/)**, Tech Lead, Olbuz
***
## The Results [#the-results]
Since switching to CtrlOps, the shift at Olbuz has been practical and immediate:
* **4 servers now run from one local app**, replacing Cyberduck and FileZilla for file transfers, and the manual work that used to stand in for infra monitoring and backups
* **Server credentials no longer live in Notepad**, and are managed directly inside CtrlOps
* **Developers handle routine server work themselves**, so the team's infrastructure time goes to the harder problems instead of day-to-day requests
* **Backup scheduling no longer needs a manual trigger** from a developer
* **Day-to-day server work is faster**, since everything runs locally instead of through the cloud
For Rakesh, the bigger shift was not just replacing two tools. It was that infra checks and backups stopped being manual work that fell on whoever was available, and credentials stopped living in a text file no one fully trusted.
***
## Who This Is For [#who-this-is-for]
Based on running CtrlOps across a multi-project, multi-server IT consulting setup, this fits teams in a similar position: multiple client servers, file transfer tools that only cover part of the job, manual infra and backup work filling the rest, and a preference for one local app over that patchwork.
***
## About Olbuz [#about-olbuz]
Olbuz is an IT consulting company based in Ahmedabad, India, providing web development and digital marketing services. The 27-person team, led by Founder Jignesh Gohel with Tech Lead Rakesh Patel, runs 4 servers across multiple client projects through CtrlOps.
---
# How Softnoesis Cut Server Access Time From Minutes to Seconds With CtrlOps (/case-studies/softnoesis)
Company: Softnoesis | Industry: IT Consulting - iOS & Mobile App Development | Customer: Chirag Lukhi, Founder, Softnoesis | Published: 2026-08-05
> Softnoesis is an IT consulting company running 8+ active projects across 15-20 servers. Before CtrlOps, every server credential lived in a notepad file, and just accessing one server took several minutes of searching. Here is how that changed.
## The Challenge [#the-challenge]
Softnoesis runs 8+ active projects, spread across 15-20 servers. With that scale and no dedicated server management tool in place, small inefficiencies added up fast.
**No tool for server management at all.** Most work was done manually. FileZilla came in occasionally, but there was no real system behind how servers were accessed or tracked.
**Every credential lived in a notepad file.** IPs and access details for dozens of servers were written down as plain text, with no structure and no security behind it.
**Accessing a single server took several minutes.** Before doing anything else, someone had to find the right entry in the notepad file, then manually connect. That was the cost just to get started, before any actual work began.
**No visibility into infrastructure or backups.** Checking server health or running a backup meant separate manual commands each time, with nothing showing the bigger picture across servers.
> "I like that CtrlOps helps me easily connect my older DevOps servers all on a single platform, which is super helpful."
>
> **[Chirag Lukhi](https://www.linkedin.com/in/chirag-lukhi/)**, Founder, Softnoesis
***
## The Turning Point [#the-turning-point]
The moment that settled it was a live demo. Rather than connecting one server to try it out, Chirag connected every active, working server in the fleet in a single sitting, in under 6 minutes, skipping the ones that were no longer in use.
Part of what made that possible was that there was nothing to stand up first. No panel to install on each VPS, no per-server configuration, just the app installed on his machine and servers added one after another.
***
## The Solution [#the-solution]
CtrlOps replaced Softnoesis's notepad file and manual process with a single dashboard, connecting every active, working Linux server in one sitting during that demo, in under 6 minutes.
**Every active server connected in one 6-minute setup.** What used to take several minutes just to access a single server turned into all working servers being connected in one sitting, without wasting time on inactive ones.
**Credentials no longer live in a notepad file.** [Server access is now managed inside CtrlOps directly](/features/access-management), closing the gap that manual text-file tracking left open.
**Log management from one screen.** This became the standout feature for Chirag: [reading logs across any server](/features/log-management) without switching tools or hunting through separate access points.
**Infra monitoring for servers that cannot afford downtime.** Several of his servers handle high traffic. Having [infra monitoring built in](/features/infra-monitoring), rather than checked manually, matters directly for those.
**Multi-server management replaced a fragmented process.** Instead of treating each server as a separate manual task, [the full set is now visible and manageable together](/features/multi-server-management).
> "Each server has its own separate monitoring tool for things like CPU status and RAM status. This setup allows me to quickly navigate from one server to another."
>
> **[Chirag Lukhi](https://www.linkedin.com/in/chirag-lukhi/)**, Founder, Softnoesis
***
## The Results [#the-results]
Since switching to CtrlOps, the change for Softnoesis has been immediate:
* **Every active, working server connected in a single 6-minute setup**, down from several minutes just to access one
* **Credentials are no longer tracked in a notepad file**, and are managed directly inside CtrlOps
* **Log management now happens from one screen**, across any connected server
* **Infra monitoring runs continuously** for servers under regular high traffic, instead of manual checks
* **Multi-server management replaced a manual, one-at-a-time process**
For Chirag, the shift was not just speed. It was that server access finally had a real system behind it, and that he now feels more relaxed and productive day to day, instead of losing time and focus to a notepad file every time he needed to connect.
***
## Feature Requested [#feature-requested]
Chirag asked for monitoring alerts and notifications, so that issues on high-traffic servers surface automatically instead of requiring a manual check. This is already in the CtrlOps product pipeline.
***
## Who This Is For [#who-this-is-for]
Based on managing 15-20 servers across 8+ active projects, this fits IT consulting teams at real scale, where credentials were never properly tracked, infra visibility was manual, and connecting to any given server took longer than it should have.
> "the initial setup of CtrlOps was super easy; I just needed to install the software like any other one I'm installing, and that was it."
>
> **[Chirag Lukhi](https://www.linkedin.com/in/chirag-lukhi/)**, Founder, Softnoesis
***
## About Softnoesis [#about-softnoesis]
Softnoesis is an IT consulting company headquartered in Surat, India, building iOS and mobile apps, web platforms, and AI solutions for clients. The 50+ person team, led by Founder Chirag Lukhi, manages 15-20 servers across 8+ active client projects, and now connects to its working servers through CtrlOps.
---
# How Spirex Infoways Cut Deployment Time From 2 Hours to Under 10 Minutes With CtrlOps (/case-studies/spirex-infoways)
Company: Spirex Infoways | Industry: IT Services & Custom Software Development | Customer: Prince Sherasiya, Tech Lead, Spirex Infoways | Published: 2026-07-30
> Spirex Infoways builds web apps, custom CRMs, and mobile apps for clients - and ran 6 servers through 6 separate aaPanel logins, with one person carrying every deployment. Here is how the team cut multi-server changes from 2 hours to under 10 minutes.
## The Challenge [#the-challenge]
Spirex Infoways builds web apps, custom CRMs, and mobile apps for clients. Like most growing IT service companies, their infrastructure grew faster than their tooling did.
**One tool, but one aaPanel per server.** The team ran aaPanel across 6 servers. Every server needed its own aaPanel installation, its own login, and its own separate session. There was no shared view across the fleet, just six disconnected control panels doing the same job in isolation.
**Server credentials lived in Notepad.** IPs, usernames, and passwords were tracked in a plain-text file. Not a password manager, not a shared vault. A Notepad file that one person maintained and everyone else depended on.
**One person carried the entire DevOps load.** On a 9-person team, only one person understood the server setup well enough to manage it. Every deployment, every fix, every server-side change ran through him.
**A single change meant repeating the same work six times.** If a fix needed to go out across 2 or 3 projects, even a small one, it meant logging into each server separately, running the same script by hand, and doing it all over again for the next one. What should have been one change became three or four manual repeats.
> "If I needed to change something in 3 places, that used to take 1.5 to 2 hours. Now it's under 10 minutes with CtrlOps."
>
> **[Prince Sherasiya](https://x.com/prince_ptl0506)**, Tech Lead, Spirex Infoways
***
## The Turning Point [#the-turning-point]
Prince found CtrlOps through a LinkedIn post. At the time, aaPanel was the only tool the team had ever used, so there wasn't much to compare it against directly. What stood out immediately was the AI Terminal.
For a team where only one person was confident touching production, an AI that could explain a command before it ran, and wait for approval before executing it, wasn't a nice-to-have. It was the missing piece that let the rest of the team start participating in server work without the fear of breaking something.
***
## The Solution [#the-solution]
CtrlOps replaced Spirex's six separate aaPanel logins with one screen, and replaced typing the same fix out by hand with a saved script that is one click on whichever server is open.
**One dashboard instead of six logins.** All 6 servers are now [manageable from a single CtrlOps window](/features/multi-server-management). No more separate aaPanel installs, no more switching between 5 or 6 browser tabs per issue.
**The same fix, written once instead of retyped four times.** Prince [saves the command once with the changing part as a variable](/features/script-directory), then runs it on each server with a click. CtrlOps does not broadcast a script to a whole fleet - what changed is that moving between servers became instant, so doing it four times stopped being an afternoon.
**One-click deployment replaced the manual release process.** Deployments that used to involve multiple manual steps per server are [now a single click](/features/deployment), cutting release complexity dramatically for the whole team, not just the one person who used to own it.
**The AI Terminal made critical commands safe to approve.** Every command comes with [a plain-English explanation of what it does before it runs](/features/ai-terminal). For commands that touch production, that context is what makes the team comfortable approving them, instead of blindly trusting or blindly avoiding them.
**Local-first storage meant faster, and it felt safer.** With everything running on the device instead of round-tripping through a cloud service, the team noticed it was simply faster day to day. Keeping data on one device, without routing it externally, also gave the team more confidence in using it on production systems.
> "Mental load is basically gone. No more copying commands by hand. Release complexity is near zero. One person can manage multiple servers and the AI Terminal handles the rest. Running a script across multiple servers is just a daily routine now, not a project."
>
> **[Prince Sherasiya](https://x.com/prince_ptl0506)**, Tech Lead, Spirex Infoways
***
## The Results [#the-results]
Since switching to CtrlOps, the change at Spirex Infoways has been immediate and measurable:
* **Multi-server changes that took 1.5 to 2 hours now take under 10 minutes**
* **6 servers managed from one dashboard**, down from 6 separate aaPanel logins
* **The one-person bottleneck is gone.** Server work is no longer dependent on a single team member being available
* **Workload dropped significantly** on repetitive tasks like deployments and running the same saved script on one server after another
For Prince, the biggest shift wasn't just speed. It was that server management stopped feeling like a specialized, risky skill that only one person on the team could safely perform.
***
## Who This Is For [#who-this-is-for]
Prince's take, based on running CtrlOps daily as a tech lead managing a multi-project, multi-server environment:
> "This is built for IT service companies. Especially ones who are managing multiple servers across multiple clients."
>
> **[Prince Sherasiya](https://x.com/prince_ptl0506)**, Tech Lead, Spirex Infoways
***
## About Spirex Infoways [#about-spirex-infoways]
Spirex Infoways is an IT services and custom software development company based in India. The 9-person team, led by Tech Lead Prince Sherasiya, builds web apps, custom CRM systems, and mobile apps for clients - and now runs its whole 6-server fleet through CtrlOps.
---
# Why Ughareja Infotech Moved From Termius to CtrlOps (/case-studies/ughareja-infotech)
Company: Ughareja Infotech | Industry: IT Consulting - Ecommerce Solutions | Customer: Uttam Ughareja, Founder, Ughareja Infotech | Published: 2026-08-06
> Uttam Ughareja managed 6 servers on Termius for years, until an unsafe AI command execution and a data loss incident made him search for a Termius alternative. He found CtrlOps through a Google search, moved his setup over in under 2 minutes, and has not looked back.
## The Challenge [#the-challenge]
Uttam Ughareja runs an IT consulting company that builds solutions for ecommerce businesses. He relied on Termius for 6 servers, until two problems became impossible to ignore.
**Termius sent AI commands to the cloud.** For a privacy-focused user managing servers for clients running multi-million dollar businesses, that alone was a serious concern.
**He lost data after a missed payment.** With no easy export or backup option, once access was gone, it was gone. For a paying user, that broke trust in a way that was hard to come back from.
**No infra monitoring or one-click deployment.** Every deployment and infra check had to be done manually, or by juggling a separate tool like aaPanel. That meant switching between tools just to get a full picture of server health.
**No option to use his own AI key.** There was no way to bring an existing key or to run anything locally, which left the choice of model out of his hands entirely.
***
## The Turning Point [#the-turning-point]
The breaking point came when the AI terminal ran a command without any safety check, around the same time Uttam lost data from a missed payment with no backup path to recover it.
He searched "Termius alternative" on Google, and found CtrlOps.
***
## The Solution [#the-solution]
Moving from Termius to CtrlOps took Uttam under 2 minutes, with all 6 servers coming across in one sitting.
**AI Terminal that runs locally, with your own key.** CtrlOps lets him attach any AI key he already has, or run models locally. Every command comes with [a description and only runs after his approval](/features/ai-terminal), and nothing is sent to the cloud.
**Infra monitoring and one-click deployment, built in.** What used to mean [manually checking servers](/features/infra-monitoring) or switching to aaPanel is now handled inside CtrlOps directly.
**Backups and scripting, without the risk of losing everything.** Where Termius offered him no real export path, CtrlOps gives him [a way to back up and manage his setup](/features/backup) that does not leave him exposed to another data loss.
**Local-first, which matters most for his clients.** Several of Uttam's clients run multi-million dollar businesses, where security is not optional. Nothing about his setup touches the cloud unless he chooses it to.
> "The AI Terminal shows the command with a description and runs only when I give approval. It also works locally with my own AI keys. That feels so secure."
>
> **[Uttam Ughareja](https://www.linkedin.com/in/uttam-ughareja)**, Founder, Ughareja Infotech
***
## The Results [#the-results]
Since switching from Termius to CtrlOps, the change has been immediate and measurable:
* **Migration took under 2 minutes**, moving all 6 servers over from Termius
* **15-20 minutes saved per infra check and deployment**, tasks that now happen in under a minute
* **AI commands run locally with his own key**, with every command requiring approval before execution
* **Backups and scripting** eliminate the data loss risk he was left exposed to
* **Costing $70/user/year versus Termius Pro at $120/user/year**, while covering infra monitoring and deployment that Termius did not offer at all
For Uttam, the switch was not just about saving money. It was about trusting a tool with client infrastructure, after that trust had already been broken once.
See the full breakdown here: [CtrlOps vs Termius](/compare/ctrlops-vs-termius).
***
## Who This Is For [#who-this-is-for]
Uttam's advice is direct, aimed at exactly the kind of user he used to be: Termius users who are privacy-conscious, tired of juggling separate tools for infra monitoring and deployment, and who want to use their own AI key instead of being locked into one provider.
> "Don't waste your time on Termius, aaPanel, or anywhere else. Move to CtrlOps ASAP to increase your productivity, and save money."
>
> **[Uttam Ughareja](https://www.linkedin.com/in/uttam-ughareja)**, Founder, Ughareja Infotech
***
## About Ughareja Infotech [#about-ughareja-infotech]
Ughareja Infotech is an IT consulting company focused on ecommerce solutions. The 3-person team, led by Founder Uttam Ughareja, manages 6 servers for clients, including several running multi-million dollar businesses, through CtrlOps.